August 26, 2025
Updated: November 4, 2026
A complete 2026 guide to penetration testing methodologies, covering PTES, NIST SP 800-115, OWASP, OSSTMM, and MITRE ATT&CK.

Mohammed Khalil

A penetration testing methodology is a documented, repeatable process that defines what is tested, in what order, how evidence is collected and how findings are reported. Most teams run the engagement lifecycle from PTES or NIST SP 800-115 (scoping, reconnaissance, vulnerability analysis, exploitation, post-exploitation and reporting), use the OWASP Web Security Testing Guide for web and API test cases, and map attacker behavior to MITRE ATT&CK. The methodology matters because it makes results comparable between tests, auditable for requirements such as PCI DSS 11.4, and focused on business impact rather than raw scanner output.
The frameworks below solve different problems. Some define the engagement lifecycle, some catalog technical test cases, and one describes attacker behavior. Most mature programs combine at least two. This table is the landscape at a glance; the four standards buyers ask about most, PTES, OSSTMM, NIST SP 800-115 and the OWASP WSTG, are compared criterion by criterion later in this guide.
| Framework | Type | Structure | Best for | Current version (Nov 2026) |
|---|---|---|---|---|
| PTES | Engagement lifecycle | 7 phases, pre-engagement to reporting | Practitioner-led network and application tests | Original standard; not substantially revised in years |
| NIST SP 800-115 | Engagement lifecycle | 4 phases: planning, discovery, attack, reporting | Federal, regulated and audit-heavy environments | Final version, September 2008 |
| OWASP WSTG | Test-case catalog | Test cases grouped by category (authentication, authorization, input validation and others) | Web application and API testing | v4.2 stable; v5 in development |
| OSSTMM | Operational security measurement | 5 channels: human, physical, wireless, telecom, data networks | Broad assessments that include people and facilities | OSSTMM 3 (2010); OSSTMM 4 released in stages |
| MITRE ATT&CK | Adversary behavior knowledge base | Tactics, techniques and procedures | Threat-informed testing and red teaming | v20 (October 2026) |
| ISSAF | Detailed checklist framework | Phased assessment checklists | Reference material only | No longer actively maintained |
| CREST | Accreditation body, not a methodology | Accredits companies and certifies testers (CRT, CCT) | Checking provider credentials in RFPs | n/a |
Let's get one thing straight: a real penetration testing methodology is more than just a checklist. It's a formal, documented game plan that outlines the scope, phases, and rules for an ethical hacking engagement. Think of it as the strategic blueprint that separates a professional security assessment from an unstructured, ad hoc "hack." It ensures the process is repeatable, thorough, and, most importantly, safe for your environment.
In the early days of cybersecurity, pentesting was often an unguided art form. There were few rules or shared standards, so businesses did not know what to expect and results varied widely from one tester to the next. That's a huge problem. In 2026, with the average cost of a data breach in the U.S. at $11.5 million according to IBM's Cost of a Data Breach Report 2026, businesses can't afford inconsistency.
From my experience leading red team engagements, the choice of methodology is the single most important decision made before any testing begins. It dictates whether we simply find a list of CVEs or if we uncover the multi stage attack chain that could actually take down the business. It’s the core difference between a basic scan and a true security validation, a distinction we'll break down completely by exploring the difference between a vulnerability assessment and penetration testing.
The move toward formal methodologies wasn't an academic exercise; it was a direct market response to the increasing financial and reputational damage caused by data breaches. As the stakes grew, the need for auditable, repeatable, and professional security validation became a business necessity, driving the creation of standards like PTES and the adoption of government frameworks like NIST SP 800 115 to bring order and predictability to the field. Specialized engagements such as wireless penetration testing follow these same structured phases.
Ready to run this on your systems? Get started with our penetration testing services.
No single methodology is a silver bullet. A mature testing provider blends the lifecycle management of PTES or NIST with the technical depth of OWASP and the threat intelligence of MITRE ATT&CK. The sections below explain what each one does; the side-by-side comparison of PTES, OSSTMM, NIST SP 800-115 and the OWASP WSTG follows them.

If you want to know how pentesters actually think, PTES is your guide. It was designed by and for security practitioners to provide a clear, end to end baseline for a high quality pentest. It's less about rigid compliance and more about a practical, real world workflow that mirrors how actual attacks unfold. The standard itself has not been substantially revised in years, so most teams pair its seven phases with current technical references such as the OWASP testing guides and MITRE ATT&CK.
Here's the deal. The PTES methodology is broken down into seven distinct phases:

If PTES is the practitioner's field guide, think of the Technical Guide to Information Security Testing and Assessment (NIST SP 800-115) as the official, government issued manual. Published in September 2008, it is still the current final version of the guide in 2026. It's a formal, structured methodology widely adopted by federal agencies and large enterprises that require a rock solid audit trail and comprehensive documentation of security testing activities.
NIST SP 800-115 breaks a penetration test into four phases:
We often use the NIST framework when a client's primary driver is compliance, such as for FedRAMP penetration testing explained. Its structure is also a great fit for Penetration Testing for DevOps environments.
The WSTG isn't a full lifecycle methodology. Instead, it's the definitive, open source checklist of technical security controls for any web application penetration testing services or API assessment, OWASP Web Security Testing Guide (WSTG). The latest stable release is WSTG v4.2, and OWASP is developing version 5. Its input-validation checks are where classes like template injection get systematically tested.
During the "Vulnerability Analysis" and "Exploitation" phases, my team uses the WSTG as our technical guide. If we're testing for Broken Access Control, which is still ranked first as A01:2025 in the OWASP Top 10:2025, we follow the specific test cases outlined in the WSTG. As threats evolve, so does OWASP, with projects like the OWASP Top 10 for Large Language Models, which tackles emerging AI cybersecurity threats in 2026.
Our OWASP Top 10 2025 guide explains each category and how pentesters test for it.
The Open Source Security Testing Methodology Manual (OSSTMM) from ISECOM focuses on measuring operational security as a whole, going far beyond just digital assets. OSSTMM 3, published in 2010, remains the edition available as a free download; ISECOM is releasing OSSTMM 4 in stages, with early access for its members.
OSSTMM 3 structures its testing across five "channels": Human Security, Physical Security, Wireless Communications, Telecommunications, and Data Networks. Instead of ending with a list of vulnerabilities, it measures the attack surface: the rav balances porosity (the points where an attacker can interact with a target) against controls and their limitations, and results go into a Security Test Audit Report (STAR) signed by the analysts who ran the test.
The Information Systems Security Assessment Framework (ISSAF), published by the Open Information Systems Security Group (OISSG), is an older, very detailed checklist-style framework. It has not been actively maintained for years, so treat it as a reference rather than a primary methodology. CREST is different: it is not a methodology but an international not-for-profit accreditation body that accredits penetration testing companies and certifies individual testers (for example CRT and CCT). When an RFP asks for a CREST-accredited provider, it is asking for evidence that the vendor's processes and testers have been independently assessed, not for a specific set of test phases.
The MITRE ATT&CK framework is not a testing methodology itself. It's a globally accessible knowledge base of adversary tactics, techniques, and procedures (TTPs) based on real world observations. MITRE updates it about twice a year; as of November 2026 the current release is ATT&CK v20 (October 2026), so check which version your provider maps findings to.
We use ATT&CK to make our tests more realistic. Instead of random exploits, we emulate the exact TTPs used by threat actors who target our client's industry, such as specific lateral movement techniques (T1021, Remote Services). This is fundamental to a true red team vs blue team explained engagement.
The lifecycle frameworks predate most of today's attack surface. NIST SP 800-115 was published in 2008, before managed cloud, containers and public APIs became the default, so a modern methodology adds technology-specific references to the same phases.
If these environments are in scope, ask your provider which of these references they test against. See our cloud penetration testing services and LLM and AI penetration testing services.
These four standards come up in almost every RFP and audit conversation, and they are often treated as interchangeable. They are not. PTES and NIST SP 800-115 describe how an engagement runs from scoping to reporting, OSSTMM measures operational security across people, places and networks, and the OWASP WSTG is a catalog of web application test cases. The table below compares them on the points that change how a test is scoped, run and reported. For version status and the wider landscape, including MITRE ATT&CK, see the frameworks overview table near the top of this guide.
| Criterion | PTES | OSSTMM | NIST SP 800-115 | OWASP WSTG |
|---|---|---|---|---|
| Published by | An independent community of security practitioners | ISECOM (Institute for Security and Open Methodologies) | U.S. National Institute of Standards and Technology | OWASP Foundation community project |
| What it defines | The engagement lifecycle in seven sections, from pre-engagement to reporting | A method for testing and measuring operational security, with its own metric and report format | How to plan and run technical security testing and assessment, including a four-phase penetration test | A catalog of test cases for web applications and APIs |
| Coverage | General purpose: network, infrastructure and application engagements | Five channels: human, physical, wireless, telecommunications and data networks | Technical testing of systems and networks; physical and social engineering testing are outside its scope | Web applications and APIs only (12 test categories in v4.2) |
| Scoping and rules of engagement | Dedicated pre-engagement section | Defines scope and its own rules of engagement | Planning phase plus a rules of engagement template (Appendix B) | Not defined; scoping comes from the lifecycle framework you pair it with |
| Technical test depth | Technical guidelines are kept separate from the standard itself | Channel-specific test modules, deliberately not tied to particular security products | Technique families (review, target identification and analysis, vulnerability validation) rather than step-by-step test cases | Detailed test cases with stable IDs such as WSTG-ATHN-01 |
| Output and measurement | Reporting section covering an executive summary and a technical report | An attack surface metric (rav) and a Security Test Audit Report (STAR) | Findings, risk ratings and mitigation recommendations | Reporting chapter; findings can cite the test ID they came from |
| Access and license | Free to read online | OSSTMM 3 is a free download (Creative Commons BY-NC-ND 3.0); OSSTMM 4 modules are being released in stages | Free from NIST | Free under Creative Commons BY-SA 4.0 |
| Main limitation | Not substantially revised in years, so it needs current technical references alongside it | Dense and metric-heavy; more than most standard technical pentests need | Final version dates from 2008, before cloud, containers and modern APIs | No lifecycle, scoping or infrastructure coverage |
| Use it when | You need a practical end-to-end structure for a pentest | You need measurable, repeatable results across people, facilities and networks | Auditors, regulators or federal buyers expect a recognized government reference | A web application or API is in scope |
In practice you rarely pick just one. Choose a lifecycle framework to run the engagement, then add the technical catalog that matches what is in scope. These rules of thumb cover most planning and buying decisions:
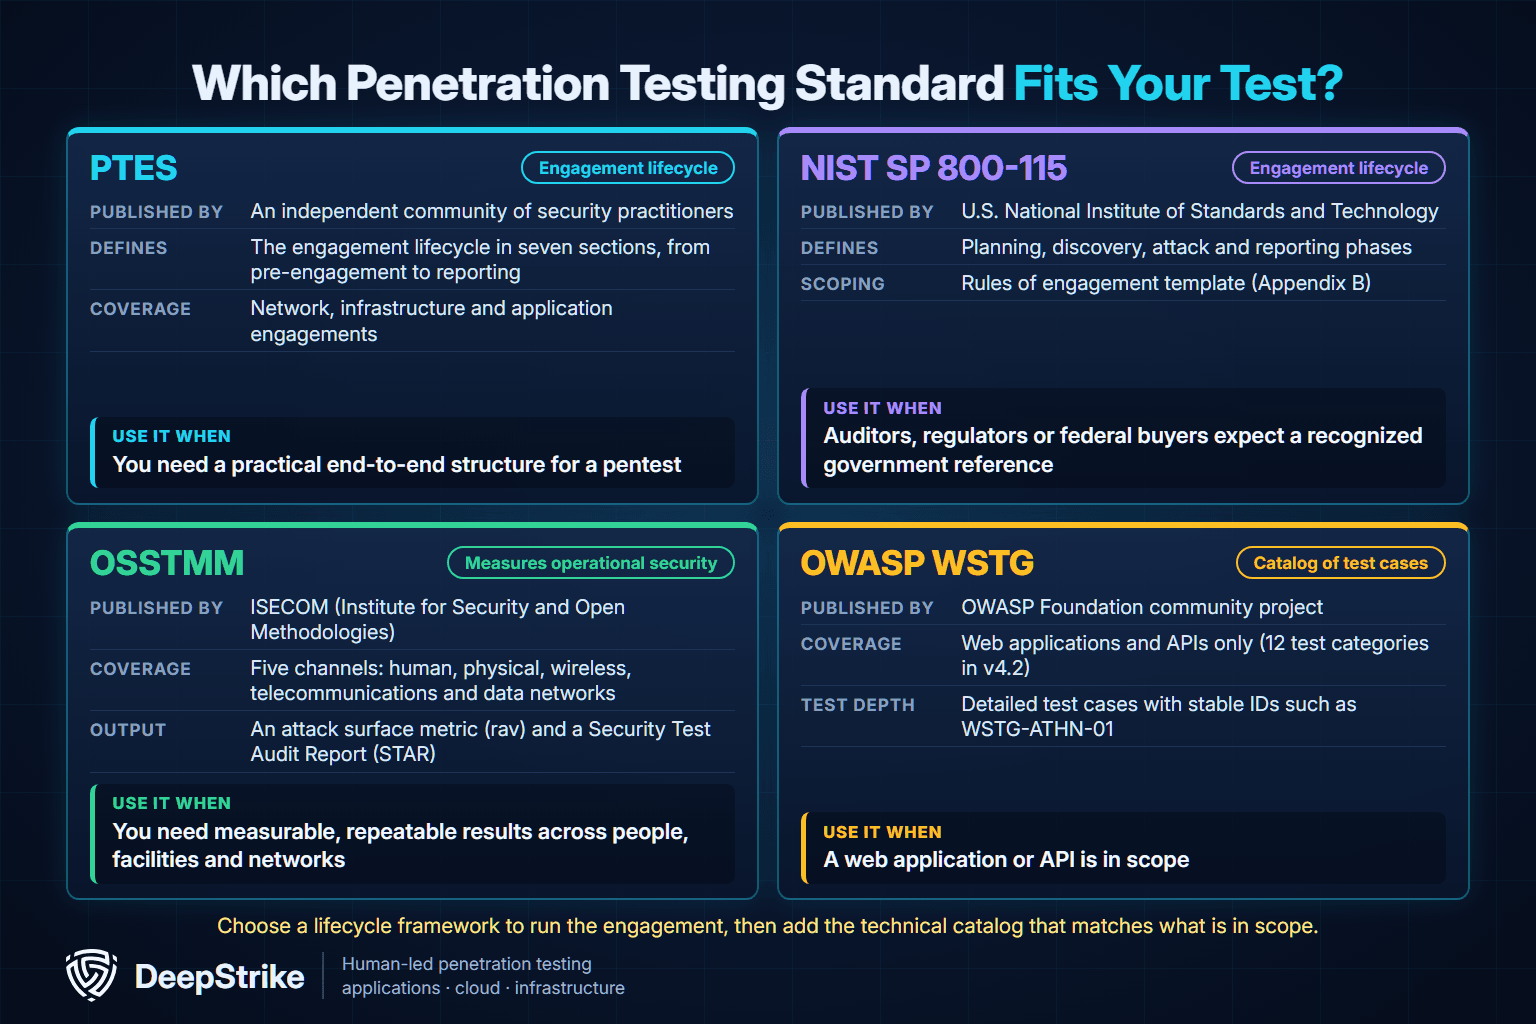
A common combination for a SaaS company is PTES or NIST SP 800-115 for the engagement, the WSTG and the OWASP API Security Top 10 for the application, and MITRE ATT&CK to describe attacker techniques in the report. For a broader assessment that also covers offices, staff and network infrastructure, OSSTMM's five channels make a useful scope checklist even if the final report follows another format.
If a provider describes only a proprietary methodology, ask which of these four it maps to, and which phases, channels or test cases it leaves out. A clear answer to that question tells you more about coverage than the methodology's name.
Here’s a practical, step by step look at how a typical engagement works, combining the best of PTES and NIST.
Search for penetration testing steps and you will find five, six or seven stages. They describe the same work at different levels of detail. This is how the common five-stage model, the seven PTES phases and the four NIST SP 800-115 phases line up with the six steps below:
| This guide (6 steps) | Common 5-stage model | PTES (7 phases) | NIST SP 800-115 (4 phases) |
|---|---|---|---|
| 1. Pre-engagement and scoping | Planning and reconnaissance | Pre-engagement interactions | Planning |
| 2. Intelligence gathering | Planning and reconnaissance | Intelligence gathering; threat modeling | Discovery |
| 3. Scanning and vulnerability analysis | Scanning | Vulnerability analysis | Discovery |
| 4. Exploitation | Gaining access | Exploitation | Attack |
| 5. Post-exploitation | Maintaining access | Post exploitation | Attack |
| 6. Reporting and remediation | Analysis and reporting | Reporting | Reporting |
The step count matters less than what each step produces: a signed scope, a map of the attack surface, validated findings rather than scanner output, proof of business impact, and a report with retest results.
This phase sets the foundation for everything that follows. The goal is to define exactly what will be tested, when, and how, and to get explicit, written permission. We craft the Rules of Engagement (RoE), a document that outlines testing windows, emergency contacts, and what actions are permissible.
The goal here is to collect as much information about the target as possible from public sources. This includes:
Now, we identify specific, potential vulnerabilities.
This is where we prove that a vulnerability is exploitable. We attempt to gain an initial foothold, perhaps using the Metasploit Framework for an unpatched service or exploiting a path traversal in client-side requests.
This phase answers the critical question: "So what?". Key activities include:
The final goal is to deliver a clear, actionable report. A high quality report from a penetration testing provider includes an Executive Summary and detailed Technical Findings with remediation guidance.
The phases are easier to judge when you see them applied. This example comes from a red team engagement DeepStrike has published as a case study, with client details removed. It is summarized here to show how each phase shaped the result.
The methodology lesson: no single scanner check would have flagged this. Each issue looked minor on its own, a duplicate registration, an email-based identity, a trusted header. Only phase-by-phase chaining showed the business impact. Read the full write-up in our JWT account takeover case study.

PCI DSS v4.0.1, the current version of the standard (v4.0 was retired at the end of 2024), covers penetration testing in Requirement 11.4. Requirement 11.4.1 calls for a defined, documented methodology based on industry-accepted approaches that covers the entire CDE perimeter and critical systems, segmentation controls, and both application-layer and network-layer testing. Approaches commonly used to meet it include NIST SP 800-115, PTES, OSSTMM and the OWASP testing guides. Requirements 11.4.2 and 11.4.3 require internal and external testing at least once every 12 months and after any significant upgrade or change, by a qualified tester with organizational independence. For a deep dive, see the PCI Security Standards Council document library and our PCI DSS penetration testing guide.
The Health Insurance Portability and Accountability Act (HIPAA) requires regular risk analysis. While the current Security Rule doesn't explicitly mandate penetration testing, it's strongly advised to meet the requirement for a "thorough assessment of the potential risks and vulnerabilities" to protected health information (ePHI). HHS proposed in January 2025 to require penetration testing at least every 12 months, but as of November 2026 that rule has not been finalized. Our HIPAA penetration testing checklist 2026 can help.
Penetration testing has become a standard expectation for SOC 2 penetration testing requirements 2026 and a critical factor for penetration testing for cyber insurance eligibility. Insurers see regular testing as proof of due diligence and may deny coverage without it. This is especially true for penetration testing for startups and SMBs.

This refers to the Penetration Testing Execution Standard (PTES), which includes: Pre engagement Interactions, Intelligence Gathering, Threat Modeling, Vulnerability Analysis, Exploitation, Post Exploitation, and Reporting.
Most guides list five: planning and reconnaissance, scanning, gaining access (exploitation), maintaining access (post-exploitation), and analysis and reporting. The names vary between sources, and PTES splits the same work into seven phases.
NIST SP 800-115, the Technical Guide to Information Security Testing and Assessment, describes four phases: planning, discovery, attack and reporting. Discovery covers information gathering and vulnerability analysis, and the attack phase can loop back to discovery as testers gain new access. The current version was published in September 2008.
The Open Source Security Testing Methodology Manual (OSSTMM) is ISECOM's methodology for testing and measuring operational security. OSSTMM 3, released in 2010, covers five channels (human, physical, wireless, telecommunications and data networks) and expresses results as an attack surface metric called the rav, reported in a Security Test Audit Report (STAR). ISECOM is releasing OSSTMM 4 in stages.
Use a lifecycle framework, PTES or NIST SP 800-115, to run the engagement, and add the OWASP WSTG whenever web applications or APIs are in scope. Choose NIST SP 800-115 when auditors or federal buyers expect a government reference, and OSSTMM when you need measurable results across people, facilities and networks. Most mature tests combine two or more.
In this context, they are often used interchangeably. A framework (like NIST or PTES) provides the high-level structure, while the methodology is the specific application of that framework, including the tools and techniques used.
For buyers comparing penetration testing services in the UK, timing depends on scope. A small web application test might take one to two weeks, while a full internal and external penetration test for a large enterprise could take a month or more.
Yes for PCI DSS: under PCI DSS v4.0.1, Requirement 11.4 requires internal and external penetration testing at least every 12 months and after significant changes. HIPAA's current Security Rule does not name penetration testing, but it requires a risk analysis and periodic technical evaluation, and many organizations use a pentest as evidence for both. HHS proposed in January 2025 to require penetration testing at least every 12 months; as of November 2026 that rule had not been finalized.
While all are critical, many practitioners agree the Post Exploitation phase delivers the most value. It demonstrates the real world business impact of a breach, moving beyond a simple technical finding.
While you can run tools, a true penetration test requires deep expertise and an outside perspective. Many compliance standards, like PCI DSS, require the tester to be organizationally independent. You can explore the differences in our article on manual vs automated penetration testing.
Costs vary widely based on scope, complexity, and duration. For a detailed breakdown, see our guide on penetration testing cost.
A structured, repeatable penetration testing methodology is the foundation of modern security assurance. It's what transforms security testing from a guessing game into a strategic business function. Frameworks like PTES and NIST provide the roadmap, specialized guides like OWASP WSTG provide the technical depth, and threat intelligence from MITRE ATT&CK ensures the simulation is realistic. The ultimate goal is not to produce a list of CVEs, but to uncover and demonstrate tangible business risk, allowing you to prioritize your defenses effectively. Once the assessment concludes, some teams convert the final report from PDF to flipbook before sharing it with executives, making a dense technical document easier to navigate section by section.
The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements for Fortune 500 companies, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
