June 4, 2025
Updated: November 5, 2026
A practical guide to PCI DSS penetration testing requirements, scope, frequency, segmentation validation, and reporting.

Mohammed Khalil
Yes. PCI DSS requires penetration testing for in-scope environments that store, process, or transmit cardholder data. In practical terms, PCI DSS Requirement 11.4 expects internal and external penetration testing at least annually and after significant changes. If segmentation is used to reduce PCI scope, segmentation controls should also be tested to confirm that non-CDE systems cannot reach the cardholder data environment. PCI DSS v4.0.1 has been the only active version of the standard since v4.0 was retired on December 31, 2024, and the requirements that v4.0 marked as future-dated have applied since March 31, 2025. Quarterly external scans by an Approved Scanning Vendor (ASV) are a separate requirement (11.3.2) and do not replace a penetration test.
• Internal and external penetration testing should be performed for in-scope environments.
• Testing should be repeated after significant changes that could affect CDE security.
• Segmentation controls should be validated when segmentation is used to reduce PCI scope.
• Findings should be remediated and retested, not only documented.
• The testing approach should follow a defined methodology and be performed by qualified, independent testers.
In today’s digital payment landscape, PCI penetration testing has become a non negotiable practice for merchants, payment processors, fintech platforms, and any business handling credit card data. PCI DSS the industry standard for card security doesn’t just suggest penetration testing it mandates it for those in scope. But beyond ticking a compliance box, penetration testing is about protecting high value targets: modern payment systems are hot targets for cybercriminals because they hold the keys to financial gain. Every credit card number in your databases or payment flows is a potential payday for attackers. Merchants on hosted platforms can start with Shopify penetration testing.
This article demystifies PCI focused penetration testing from a practitioner’s perspective. We’ll clarify what it involves, why attackers are drawn to payment environments, and how it aligns with PCI DSS requirements. We’ll also delve into what a proper PCI penetration test should cover from verifying network segmentation to probing cloud configurations and common pitfalls to avoid. Whether you manage a cardholder data environment on premises or in the cloud, understanding PCI penetration testing will help you secure cardholder data and not just comply, but truly protect your business. Indian fintechs and merchants can compare penetration testing companies in India. For cloud-specific scoping and controls, see our PCI compliance in the cloud guide.
PCI penetration testing is a controlled, ethical hacking exercise against systems in your cardholder data environment. In plain language, it means hiring security professionals to act like attackers and attempt to breach your own payment systems within agreed scope and rules. The goal is to find security gaps before malicious actors do. Unlike a vulnerability scan that only identifies potential issues, a penetration test goes further; the tester actually exploits weaknesses to prove they are real and demonstrate the impact. For example, instead of just reporting System X might be vulnerable to SQL injection, a penetration tester will attempt to perform an SQL injection to extract data or gain deeper access, showing what a criminal could achieve.
It’s important to distinguish PCI penetration testing from other security assessments:
PCI DSS emphasizes exploitation, not just detection, because the act of breaking in provides evidence of which vulnerabilities are truly dangerous. A finding confirmed by exploitation is far less likely to be a false positive; it shows that an attacker can actually do this. The PCI Security Standards Council even published guidance noting that penetration testing helps uncover paths to unauthorized access that automated tools might miss. In short, PCI penetration testing is about actively challenging your security controls under real world conditions to ensure cardholder data is adequately protected.
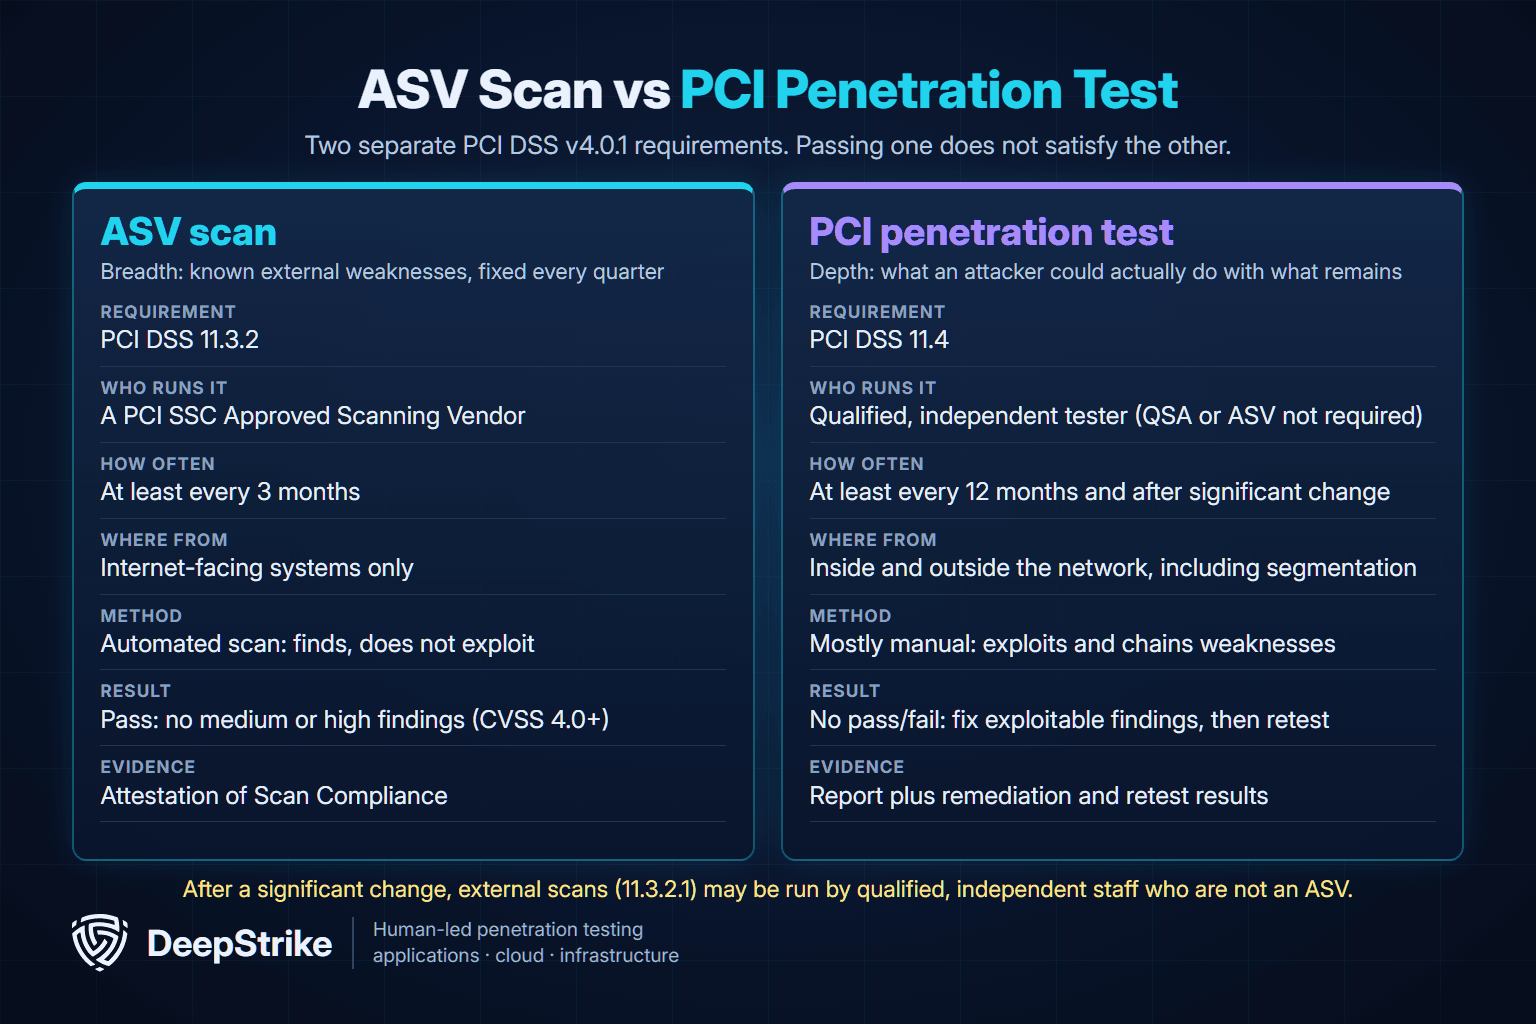
An ASV scan and a PCI penetration test satisfy two different requirements, and neither one can stand in for the other. Requirement 11.3.2 calls for external vulnerability scans at least once every three months, run by a PCI SSC Approved Scanning Vendor (ASV) until the result passes. Requirement 11.4 calls for internal and external penetration tests at least once every 12 months and after significant changes, run by a qualified tester who is organizationally independent of the systems being tested. The scan shows that known external weaknesses are found and fixed on a schedule. The penetration test shows what a skilled attacker could actually do with the weaknesses that remain.
An Approved Scanning Vendor is a company qualified by the PCI Security Standards Council to run external vulnerability scans with an approved scan solution, and the Council publishes the list of Approved Scanning Vendors. ASV scans cover internet-facing systems, such as the web servers, IP addresses and domains that make up your external footprint. Internal vulnerability scans are a separate requirement (11.3.1) and are not run by the ASV program. According to the PCI SSC ASV resource guide, a passing scan is one whose report contains no vulnerabilities ranked "medium" or "high". In the ASV Program Guide’s scoring, that means no finding with a CVSS base score of 4.0 or higher, apart from narrow exceptions such as purely denial-of-service issues. If a scan fails, you fix the findings and rescan until it passes, and the ASV issues an Attestation of Scan Compliance for the passing result.
Two details trip people up. First, the scan customer, not the ASV, is responsible for the scan scope: in the attestation you confirm that every in-scope external component was included and that anything you excluded is properly segmented from the cardholder data environment. Second, not every scan an ASV sells counts. The PCI SSC points out that ASVs also offer other products, including penetration testing, and only scans run with the ASV’s PCI-approved scan solution meet Requirement 11.3.2.
| Criterion | ASV scan | PCI penetration test |
|---|---|---|
| PCI DSS v4.0.1 requirement | 11.3.2 (quarterly external scans); 11.3.2.1 covers scans after significant changes | 11.4.1 to 11.4.4; segmentation tests in 11.4.5 and 11.4.6; multi-tenant support in 11.4.7 |
| Who performs it | A PCI SSC Approved Scanning Vendor, using its approved scan solution | A qualified internal resource or qualified external third party with organizational independence; not required to be a QSA or ASV |
| Minimum frequency | At least once every three months, with a passing scan in every three-month period after the initial assessment | At least once every 12 months and after any significant infrastructure or application upgrade or change |
| Vantage point | External, internet-facing components only | Inside and outside the network: the entire CDE perimeter and critical systems, plus any segmentation and scope-reduction controls |
| Method | Automated scanning that identifies known vulnerabilities but does not exploit them | Mostly manual testing under a documented methodology that attempts exploitation and chains weaknesses together |
| What "done" looks like | A passing result: no vulnerabilities ranked medium or high, confirmed by rescans where needed | No pass or fail. Exploitable findings are corrected based on your risk ranking (Requirement 6.3.1) and the test is repeated to verify the fixes (11.4.4) |
| After a significant change | External scan with CVSS 4.0+ findings resolved; may be run by qualified, independent personnel who are not an ASV (11.3.2.1) | Internal and external tests repeated for the change (11.4.2, 11.4.3) |
| Evidence for the assessor | ASV scan reports with an Attestation of Scan Compliance for each three-month period | Methodology, scope of work, test report, remediation and retest results, kept for at least 12 months (11.4.1) |
The PCI DSS guidance for Requirement 11.4.1 draws the line clearly: running a vulnerability scan is not a penetration test, and a test that only tries to exploit what a scanner already reported is not adequate either. Scanner output is one starting point for the tester, not the test itself.
Which requirements you validate depends on whether you complete a Report on Compliance (ROC) or a Self-Assessment Questionnaire (SAQ), and on which SAQ your acquirer or payment brand accepts. A ROC and SAQ D cover all applicable requirements, so both 11.3.2 and 11.4 apply. The PCI SSC resource guide lists ASV scans in merchant SAQs A, A-EP, B-IP, C and D, and in SAQ D for service providers. For SAQ A, the scan applies only to the merchant system that hosts the webpage that redirects to, or embeds, a PCI DSS compliant third party’s payment page, and SAQ A does not include the 11.4 penetration testing requirements. The PCI SSC’s January 2025 update to SAQ A removed Requirements 6.4.3, 11.6.1 and 12.3.1 from that questionnaire and added an eligibility criterion; the ASV scan requirement was not part of that change. Confirm the exact SAQ with the organization that asks for your compliance evidence.
Payment systems sit at the intersection of money and data, a combination that attracts cybercriminals like moths to a flame. Cardholder data CHD is extremely valuable on the black market; stolen credit card numbers can be sold in bulk or used for fraud, making any system handling them a lucrative target. See our credit card fraud statistics for current loss figures. This financial incentive drives a variety of attacks against organizations that process payments:
In summary, payment systems are prime targets because they deal in data that directly equates to money. The impact of a successful attack is high stolen card data leads to fraud losses, hefty fines, legal liabilities, and reputation damage with customers and banks. That’s why PCI DSS places heavy emphasis on securing these systems and why penetration testing is vital: it helps you find and fix the weaknesses that attackers would eagerly exploit for financial gain.
PCI DSS (currently version 4.0.1) explicitly calls out penetration testing as a requirement; it's not optional if you handle card data. Requirement 11 of PCI DSS is titled Test security of systems and networks regularly, and penetration testing is addressed in sub requirement 11.4. In essence, PCI DSS defines penetration testing as a comprehensive security test of your environment, performed by skilled testers, that goes beyond automated scans to validate the effectiveness of your security controls.
Here are key expectations from PCI’s perspective:
In summary, PCI DSS defines penetration testing as a rigorous, expert driven evaluation of your security, with specific requirements around scope, frequency, and process. It’s about actively testing that your defenses including segmentation work and that you can find and fix vulnerabilities before the bad guys do. Understanding these expectations will help ensure your PCI penetration test meets both the letter and the spirit of the standard.
A PCI focused penetration test isn’t just a general pentest; it has certain must validate objectives rooted in protecting cardholder data. When you engage a PCI penetration test, here are the critical things it should confirm:
In summary, a PCI focused penetration test validates the critical security outcomes: that your CDE is properly isolated, that no easy paths lead to card data, that attackers can’t freely roam your network, and that your apps, APIs, and controls are solid. If the test finds those assumptions hold, you gain confidence and evidence that you’re protecting cardholder data effectively. If not, you gain a clear roadmap of what to fix to fortify your defenses.
Every PCI penetration test starts from a scope decision, and many audit disputes about pen testing are really disputes about scope. PCI DSS v4.0.1 applies to the cardholder data environment (CDE): the people, processes and system components that store, process or transmit cardholder data or sensitive authentication data, plus components with unrestricted connectivity to them. It also applies to anything that could affect the security of that data, even if it never touches a card number. The standard’s own examples include authentication and multi-factor authentication servers, SIEM and logging systems, the network security controls that provide segmentation, name resolution and web redirection servers, virtualization and cloud components such as cloud identity and access management and container orchestration, and the code repositories and deployment tools that push changes into the CDE.
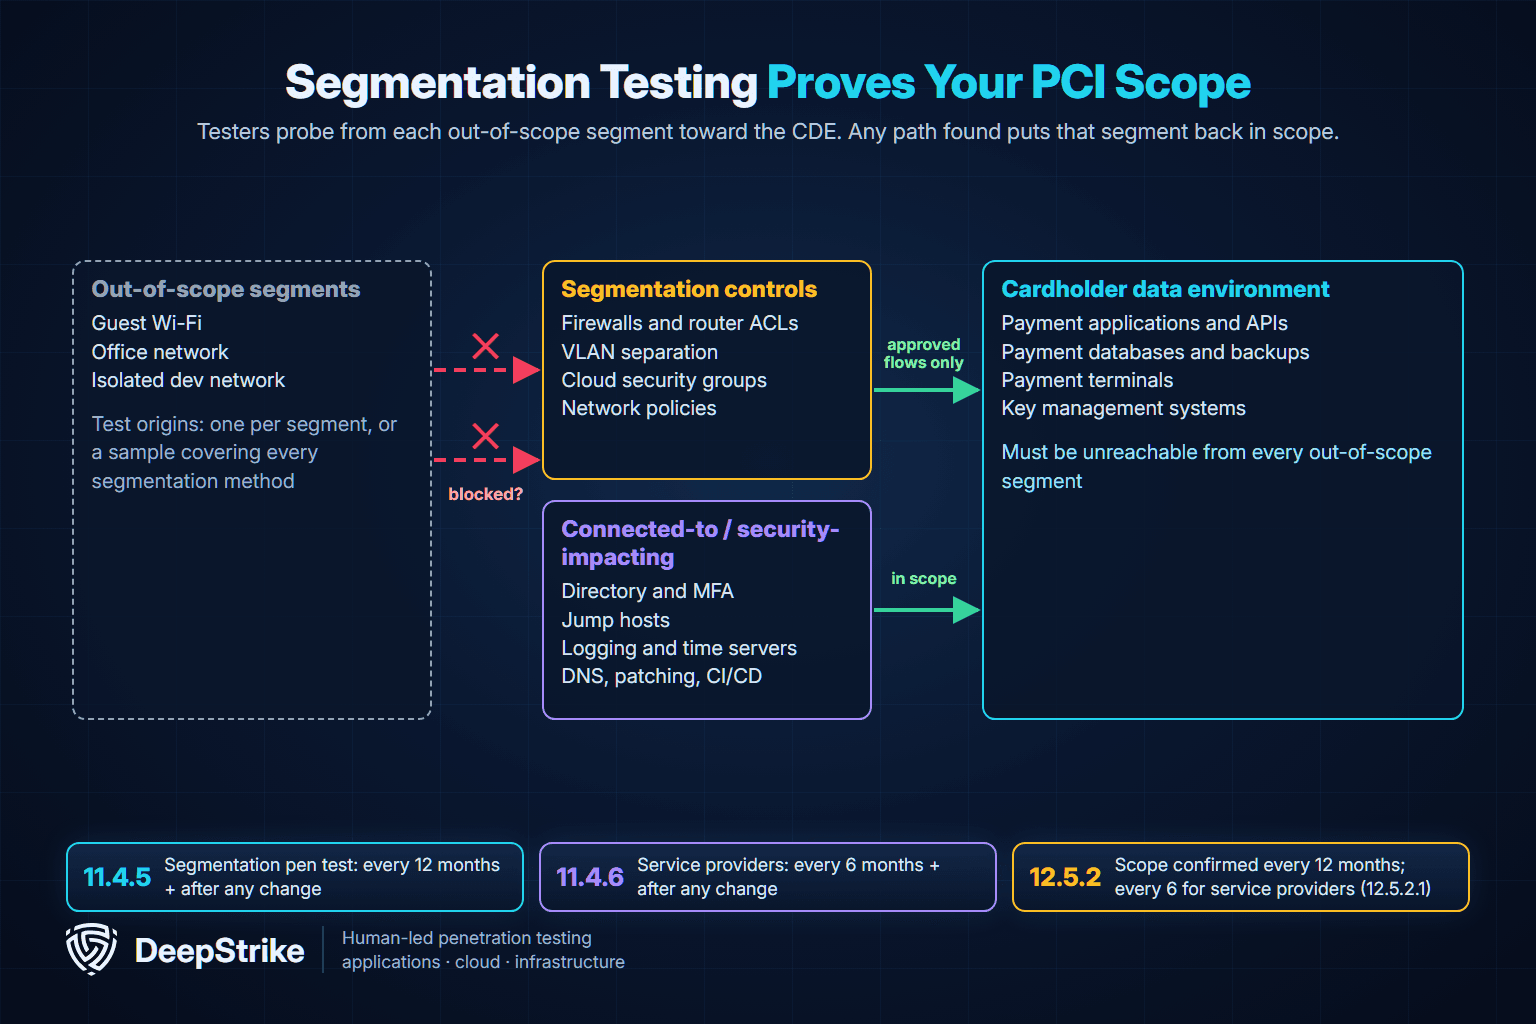
A common way to apply those rules comes from the PCI SSC information supplement Guidance for PCI DSS Scoping and Network Segmentation, which sorts components into three categories. The supplement presents them as an example approach rather than a requirement, and it checks them in order: if a system meets any CDE criterion it is a CDE system, and a system is out of scope only if it meets every out-of-scope criterion. The table shows how each category affects a penetration test.
| Category | What puts a system here | Examples | What the penetration test does with it |
|---|---|---|---|
| CDE systems | Stores, processes or transmits account data, or sits on the same network segment as a system that does | Payment application and database servers, payment terminals, checkout and payment API services | Full network-layer and application-layer testing from inside the CDE and into it |
| Connected-to or security-impacting systems | Can reach the CDE directly or through another system, provides security services to it, supports PCI DSS controls, or provides the segmentation itself | Directory and MFA servers, jump hosts, firewalls that segment the CDE, log storage and time servers, DNS and web redirection servers, patch distribution | Tested as part of the CDE perimeter and critical systems; a weakness here is often the path into the CDE |
| Out-of-scope systems | Does not handle account data, is not on a CDE segment, and cannot reach or affect the CDE, even through an in-scope system | Guest Wi-Fi, an office network with no route to the CDE, an isolated development network | Used as starting points for segmentation testing to prove they really have no path in |
PCI DSS does not require you to segment the CDE. It strongly recommends segmentation because it can reduce the scope, cost and risk of an assessment, and it is explicit about the alternative: without adequate segmentation, the entire network is in scope. A system only counts as out of scope if it is isolated well enough that it could not affect the security of cardholder data even if it were compromised. Once you rely on segmentation to draw that line, PCI DSS expects you to prove it with penetration testing on a fixed schedule.
| Requirement | Applies to | Minimum frequency | What it requires |
|---|---|---|---|
| 11.4.5 | Any entity that uses segmentation to isolate the CDE | At least once every 12 months and after any change to segmentation controls or methods | Penetration tests of all segmentation controls and methods in use |
| 11.4.6 | Service providers that use segmentation | At least once every six months and after any change to segmentation controls or methods | The same segmentation tests on the shorter cycle |
| A1.1.4 | Multi-tenant service providers | At least once every six months | Penetration testing that confirms logical separation between customer environments, in addition to 11.4.6 |
| 12.5.2 | All entities | At least once every 12 months and upon significant change to the in-scope environment | You document and confirm your own PCI DSS scope, including segmentation controls and why each excluded environment is out of scope |
| 12.5.2.1 | Service providers | At least once every six months and upon significant change | The same scope confirmation on the shorter cycle |
| A3.2.4 | Designated entities that a payment brand or acquirer requires to meet Appendix A3 | At least once every six months and after any change to segmentation controls or methods | Segmentation penetration testing that confirms PCI DSS scope |
Requirement 12.5.2 rarely comes up in pen test conversations, but it produces the scope record a segmentation test checks. It asks you to identify all data flows and acceptance channels, update your data-flow diagrams, find every location where account data is stored, processed or transmitted (including outside the defined CDE), identify every component in, connected to or able to affect the CDE, list every segmentation control with a justification for each out-of-scope environment, and identify every third-party connection to the CDE. PCI DSS notes that this is your own exercise and is not replaced by the scoping check your assessor performs.
Requirements 11.4.5 and 11.4.6 set the same content for every segmentation test:
PCI DSS suggests host discovery and port scanning to verify that out-of-scope segments have no access to the CDE, and the PCI SSC Penetration Testing Guidance describes segmentation checks as the discovery stages of a network penetration test. A typical engagement runs in six steps:
Segmentation boundaries usually fail through shared services that quietly connect both sides. Check these before the tester does:
A key step in any PCI penetration test is defining the scope of what systems and components will be tested. PCI DSS scope is determined by the cardholder data environment and anything connected to it. In practice, a PCI pen test scope usually includes the following areas:
This is the heart of the scope. The CDE encompasses all systems that store, process, or transmit cardholder data or sensitive authentication data. In a typical business, this might include databases holding payment transactions, application servers processing payments, point of sale POS terminals, card reader devices, and encryption key management systems. Testers will directly assess these systems because they are the crown jewels; a compromise here means immediate exposure of card data.
For example, if you have a payment database, the penetration test will try to see if an attacker can reach it either through a direct vulnerability like a misconfigured database service accessible on the network or via another component like a web app that interfaces with the DB. In a retail scenario, if POS terminals are in scope, testers might assess how easily those could be attacked though often POS testing is more specialized. The goal in the CDE segment of testing is to ensure that these systems have robust hardening: up to date patches, strong credentials, secure configurations, and that they aren’t directly accessible except through tightly controlled channels. Any weakness in the CDE systems is high severity, so this portion of the test is often thorough including authenticated testing if possible e.g., using a test account to see more of the system to find hidden flaws. Remember, everything in the CDE is by definition in scope for PCI, so nothing here gets a free pass. If it touches card data, it gets tested.
Most cardholder data environments include one or more payment applications for instance, an e-commerce website checkout, a mobile payment app, or back end services that handle card authorizations. These applications and their APIs are a critical part of the scope because they are common entry points for attackers. Here, the penetration test will perform deep application layer testing. This involves looking for issues like SQL injection, cross site scripting XSS, authentication bypass, insecure direct object references IDOR, and other vulnerabilities as catalogued by OWASP. The testers simulate what a malicious user or fraudster might do on the front end: Can they manipulate the payment form? Can they submit unexpected data to the API? Can they retrieve data they shouldn’t like someone else’s card details or personal info?
Special attention is given to how these apps handle cardholder data. For instance, does the web application properly mask card numbers and never store the full PAN unencrypted? Are there any hidden fields or API endpoints that spill sensitive data? Testers also assess the effectiveness of application security controls for example, if you have input validation or a web firewall, can those be evaded with tricky payloads? Given the rise of single page apps and mobile apps, API security is equally important: the test will check that each API endpoint enforces authentication and authorization correctly, no leaking data across accounts, no ability to perform unauthorized actions via the API. Engaging specialized web application security testing for login and session flows can be invaluable here, as it ensures things like session management, password resets, and other auth flows are scrutinized. The bottom line: any software component through which card data flows or is accessed gets a thorough workout in a PCI pen test.
If you use network segmentation to limit PCI scope, testing these controls is mandatory. Segmentation controls include firewalls, routers with access control lists, VLAN separation, software defined network policies, etc., that create a boundary between the CDE and everything else. In the scope, this often appears as segmentation validation testing. What it entails is the penetration tester actively trying to bypass or slip through those network barriers. They might take a system outside the CDE, say, an IT workstation or a server in the corporate network and attempt to ping CDE systems, scan for open ports, or connect to services that should be blocked. They’ll use tools like Nmap to systematically probe the CDE from various points outside it, looking for any crack. Even things like being able to reach a CDE system’s login page from a workstation network when it should be restricted would be a finding.
The expected result is that all such attempts are blocked, essentially testing should show a brick wall around the CDE. If any packet gets through that shouldn’t, the tester will investigate why: maybe a firewall rule was misordered or a network route was forgotten. We often find legacy rules that accidentally allow some access or shadow networks like backup networks or management interfaces that bridge CDE and non CDE. Those are critical to identify because if an attacker finds them, your segmentation is effectively compromised. PCI requires that segmentation testing cover all methods in use so if you have multiple firewalls or both on prem and cloud network controls, each mechanism should be validated. Service providers must repeat it at least once every six months (Requirement 11.4.6), and every entity must retest after any change to its segmentation controls. In summary, the scope covers not just systems, but the gaps between systems ensuring the walls that protect cardholder data have no doors left unlocked.
With many organizations moving CDE components into the cloud or virtualized environments, a PCI penetration test scope often extends to cloud infrastructure like AWS, Azure, GCP and virtualization platforms. The cloud introduces a shared responsibility: the cloud provider manages the underlying hardware and core services, while you, the customer, are responsible for how you configure and use those services. A PCI pen test in the cloud context will focus on the customer controlled aspects, such as:
Engaging in thorough cloud security testing focused on identity and access paths is essential to cover these scenarios. The scope in cloud/virtualized contexts might not be a physical network range but rather all the cloud resources accounts, subscriptions, VPCs/VNETs, instances, containers, etc. that make up your CDE. The pen tester will often need read only access to cloud consoles or APIs to assess configurations in addition to active testing. The outcome should be a confirmation that your cloud setup is as secure as a traditional on prem setup with no inadvertent exposure, no weak credentials, and proper containment of the CDE within the cloud environment.
Modern payment ecosystems are rarely self contained. You may rely on third party services for payment processing, use vendors for support, or integrate outsourced components. While you can’t exactly penetrate test a third party’s systems without permission, the integration points absolutely fall in scope for your penetration test. Key areas include:
In summary, anything that touches your CDE from the outside whether it’s a user’s browser, a vendor’s connection, or a partner’s system gets consideration in the scope. The penetration tester’s job is to think like an attacker: if they can’t break your systems directly, can they break something your system trusts? Testing these integration points often reveals indirect weaknesses for example, acceptance of invalid certificates, lack of verification on callback URLs, etc.. By including third party integration security in scope, you ensure there isn’t an unlocked side door into your cardholder data.
Even with the best intentions, organizations often fall into some pitfalls when approaching PCI penetration testing. Here are common mistakes and why they can be dangerous:
Avoiding these common mistakes comes down to approaching PCI penetration testing as a serious security endeavor. Scope it right, do it regularly, use skilled testers, and follow through on fixing issues. That not only keeps the PCI auditors happy but, more importantly, actually improves your security against real threats.
PCI DSS requires penetration testing at least annually every 12 months and after any significant change. This is the bare minimum for compliance, but there are nuances and best practices to consider:
In summary, at least once a year is the rule, but more often is better from a security standpoint. The cadence should match your organization’s rate of change and risk appetite. Fast moving fintech startups, for example, often test much more frequently than annually because their environment can drastically change in a few months. On the other hand, a very static legacy environment might get by with annual tests though even then, new vulnerabilities in old systems can appear. Always test after major changes, and consider supplementary testing if any critical new threats emerge for example, if a major vulnerability like Heartbleed or Log4Shell comes out, you might do an out of band test of exposure to that issue. The goal is to have as few surprise weaknesses as possible by the time your audit or, worse, a real attacker comes around.
Yes. If your organization is required to comply with PCI DSS generally, if you process, store, or transmit cardholder data, penetration testing is a mandatory requirement. PCI DSS Requirement 11.4 specifically mandates annual internal and external penetration tests, as well as testing after significant changes. There are a few edge cases for example, very simple payment setups that use only point of sale terminals with no stored data might use a lighter self assessment, but service providers and merchants validating with a Report on Compliance or SAQ D must include penetration testing, and some shorter SAQs include parts of Requirement 11.4. Check the SAQ that applies to you. Skipping a required test not only risks non compliance with potential fines or loss of the ability to process cards but also leaves your organization blind to real security weaknesses.
Vulnerability scanning and penetration testing are two distinct but complementary activities required by PCI DSS. Vulnerability scans (Requirement 11.3) are automated checks for known security issues such as missing patches and misconfigurations. Internal scans run at least once every three months (11.3.1), and external scans must be run at least once every three months by a PCI SSC Approved Scanning Vendor, or ASV, until they reach a passing result (11.3.2). Scans report potential problems; they do not exploit them. Penetration testing (Requirement 11.4) is a mostly manual test by a qualified, independent professional, required at least once every 12 months and after significant changes. The tester actually attempts to exploit vulnerabilities and chain them the way an attacker would. In short: scanning is automated and broad, pen testing is human and targeted. The outputs differ too: a scan gives you a list of possible vulnerabilities, which can include false positives, whereas a pen test gives you confirmed, exploitable issues and their impact. Both are necessary: scans catch common issues continually, and penetration tests find the deeper attack paths. The ASV Scan vs PCI Penetration Test section above compares the two side by side.
In scope will be all components of your Cardholder Data Environment CDE and any other system that can connect to or affect the security of the CDE. Concretely, this includes: systems that store card data databases, servers, process it applications, payment terminals, or transmit it network devices, APIs. It also includes systems that don’t handle card data themselves but are on the same network or have access into the CDE often called connected to systems. Examples: a web server in a DMZ that communicates with a database in the CDE, or an internal jump server used by admins to reach CDE servers. Additionally, any security systems that could impact CDE security like authentication servers, DNS servers used by CDE systems, etc. should be in scope. Basically, if compromising System X could in any way lead an attacker to cardholder data in System Y, then X is in scope to test. Note that if strong network segmentation is in place, systems on the other side of a properly isolated network can be considered out of scope but the segmentation itself then must be tested to confirm those systems truly have no access. One way to think of it: draw a boundary around everything that touches CHD directly or indirectly that’s your testing scope. If in doubt, include it. It’s better to show an auditor you tested a few extra systems than to have missed one that should have been included.
Yes. PCI DSS v4.0, now in force as v4.0.1, introduced updates whose future-dated requirements became mandatory on March 31, 2025. These updates raise the bar for penetration testing. The core penetration testing requirements carried over from v3.2.1: annual internal and external tests, a documented methodology based on industry-accepted approaches (formerly 11.3, now 11.4.1), segmentation testing that covers every segmentation method (now 11.4.5), and six-monthly segmentation testing for service providers (now 11.4.6). v4.0 renumbered and clarified them under Requirement 11.4. Another change is the introduction of the Customized Approach in v4.0: if you choose to meet security objectives with alternative controls, you need to do targeted risk analyses and likely more rigorous testing to prove those custom controls work. Additionally, PCI DSS 4.0 has a new requirement for authenticated vulnerability scanning 11.3.1.2 while that’s a scan, not a pen test, it means internally you’ll have more information about vulnerabilities, which typically results in a more informed penetration test testers can use those authenticated scan results to focus their exploits. Also, Requirement 11.4.7, mandatory since March 31, 2025, applies to multi-tenant service providers: they must support their customers’ external penetration testing, either by giving customers prompt access to test or by providing evidence that testing meeting Requirements 11.4.3 and 11.4.4 was performed on the customer’s subscribed infrastructure. In summary, v4.0 doesn’t remove any pen testing it reinforces and clarifies it, expecting organizations to be more structured and perhaps more frequent in their testing, with no stone unturned network, applications, segmentation, all need to be covered.
PCI DSS allows either internal or external personnel to perform the penetration test, but there are strict conditions. The testers must be qualified and independent. Qualified means they have the skills and experience to do a proper job typically this means having a solid background in penetration testing and possibly certifications like OSCP, CEH, GIAC GPEN/GWAPT, etc., or demonstrable experience in similar environments. Independent means the tester is not part of the team that maintains the systems being tested and has no vested interest in the outcome. In practical terms, most organizations choose to hire an external security firm specializing in penetration testing for their PCI tests. External testers have the advantage of broad experience and no internal bias; plus their reports may carry more weight with auditors. If you use internal staff, you need to ensure, for example, that your tester from the security team is free to test the systems without influence and isn’t testing their own work. Many companies with internal red teams still bring in third party testers annually for PCI to get an objective review. Another consideration is that the QSA might ask about the tester’s qualifications; having a well known firm or certified individuals can streamline that conversation. So, while you can do it yourself if you have a skilled internal team separate from IT operations, most opt to use specialized penetration testers to meet PCI requirements and to get the most value out of the test.
Even if you fully outsource payment processing or use tokenization such that you don’t store actual card numbers, you may still need a penetration test. It depends on your setup. If any part of your environment is involved in processing or transmitting card data, that part is in scope for PCI. For example, if your site redirects customers to the provider’s hosted payment page or embeds the provider’s iframe, and every element of the payment page comes only and directly from a PCI DSS-validated provider, you are typically eligible for SAQ A, which does not include Requirement 11.4. The redirecting pages are still in scope and must be protected against tampering. You’d want to test that those pages or scripts can’t be tampered with, imagine an attacker altering your redirect to send customers to a fake page. If you have a mobile app that collects card data and sends it directly to a processor, you need to test that app to ensure it isn’t vulnerable to interception or tampering. In short, outsourcing reduces scope but doesn’t eliminate it. If your own site produces any part of the payment page, for example a direct-post form or JavaScript that sends card data to the processor, SAQ A-EP applies and includes penetration testing items; check the current SAQ for the exact requirements. With SAQ A, your PCI obligations are lighter, but best practice is still to test the interfaces to ensure an attacker can’t change the integration. Also remember, even if a provider handles the heavy lifting, a breach on your site that skims card data as it’s entered before it goes to the provider would be your responsibility. So it’s wise to have a penetration test cover any customer facing components or integrations involved in the payment process, even if you don’t store the data. And if you’re a service provider yourself, you definitely need to test your own infrastructure as part of your PCI compliance.
No. An ASV scan (Requirement 11.3.2) is an automated external vulnerability scan run at least once every three months by a PCI SSC Approved Scanning Vendor, and it must reach a passing result. A PCI penetration test (Requirement 11.4) is a mostly manual exercise, run at least once every 12 months and after significant changes, in which a qualified, independent tester tries to exploit weaknesses from inside and outside the network. If your validation includes both requirements, you need both; a passing ASV scan does not satisfy 11.4.
If you use segmentation to reduce PCI scope, penetration tests of the segmentation controls are required at least once every 12 months and after any change to segmentation controls or methods (Requirement 11.4.5). Service providers must test at least once every six months and after any such change (Requirement 11.4.6). Multi-tenant service providers must also confirm the logical separation between customer environments with penetration testing at least once every six months (Requirement A1.1.4).
No. Requirements 11.4.2, 11.4.3 and 11.4.5 call for a qualified internal resource or a qualified external third party with organizational independence, and state that the tester is not required to be a QSA or ASV. What matters is demonstrable penetration testing skill and independence from the systems being tested.
PCI penetration testing is about security validation, not just compliance checkboxing. By simulating real world attacks on your cardholder data environment, you gain an unvarnished view of where your defenses are strong and where they need improvement. In an era where payment systems are prime cyber targets, this kind of proactive testing is crucial. Remember that the true goal isn’t just to pass a PCI audit, it's to prevent breaches. A thorough PCI pen test, followed by diligent remediation, reduces the risk that your organization will become the next data breach headline. In summary, when done right, penetration testing transforms PCI requirements into real world security outcomes, helping you protect cardholder data and maintain the trust of customers and partners alike. Organizations that also connect to the SWIFT network face a parallel annual obligation, covered in our guide to SWIFT CSP penetration testing.
Ready to Strengthen Your Defenses? Payment security threats demand more than checkbox compliance. If you're looking to validate your PCI DSS scope, test segmentation controls, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business and uncover vulnerabilities before attackers do. Talk to our team about scoping your next PCI penetration test.
About the Author: Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
