August 24, 2025
Updated: November 5, 2026
An updated 2026 analysis of IoT and OT threats, attack volume, breach costs by sector, and the three regulatory regimes now reshaping connected-device security.

Mohammed Khalil
The picture has moved since the 2025 edition of this report. Attackers kept shifting toward industrial targets, manufacturing overtook transportation as the most targeted OT/IoT sector, and three governments now have device-security regimes, two of them mandatory. These are the current figures, each with its source, with the 2025 baseline preserved below for trend comparison.
| Metric | Current figure | What it means |
|---|---|---|
| IoT malware targets | Manufacturing and transportation each took 20.2% of IoT malware attacks; Mirai, Mozi and Gafgyt made up 75% of malicious payloads (Zscaler, Nov 2025) | Industrial sectors carry the heaviest IoT malware load, and old botnet families still dominate |
| Ransomware against industrial operators | +46% from Q4 2024 to Q1 2025 (Honeywell, June 2025) | Attackers keep pivoting to OT, where downtime pressure is highest |
| OT in SEC-reported incidents | 55% (30 of 55) of cyber incidents self-reported on SEC Form 8-K in 2024 were direct attacks on OT (Honeywell) | OT attacks now produce material, disclosable business impact |
| Attacks on home networks | 29 attacks per day on the average home network, which has 22 connected devices (Bitdefender and NETGEAR, Oct 2025) | Consumer devices face continuous, automated probing |
| Most targeted OT/IoT sectors | Manufacturing #1, transportation #2, energy and utilities #3 (Nozomi Networks, June to August 2026) | Attackers focus where operational continuity matters most |
| Costliest breach sector | Healthcare, $6.64M average, the highest for the 15th consecutive year (IBM, 2026) | Connected medical devices add life-safety stakes to breach costs |
| Connected devices | An estimated 21.1 billion in 2025, forecast to reach 39 billion by 2030 (IoT Analytics) | A vast, expanding and poorly secured attack surface |
| Regulation | UK PSTI in force, US Cyber Trust Mark live, EU CRA reporting from 11 Sept 2026 | Security-by-design is becoming a legal requirement, not a differentiator |
The single takeaway: the IoT attack surface is still growing faster than it is being secured, and the damage has shifted decisively from data loss to physical and operational disruption.
What changed since the 2025 edition: figures from earlier versions that could not be traced to a primary source have been replaced with sourced data; Nozomi Networks now ranks manufacturing as the most targeted OT/IoT sector; IBM's healthcare breach average moved to $6.64M and remains the highest for the 15th year; and the regulatory picture went from one law (the UK's PSTI Act) to three overlapping regimes across the UK, US and EU. Each of those is covered in full below.
The most critical internet of things hacking statistics paint a stark picture: a world of unprecedented convenience built on a dangerously fragile foundation. IoT Analytics estimated 21.1 billion connected IoT devices by the end of 2025 and forecasts 39 billion by 2030, and cybercriminals are exploiting that vast and vulnerable attack surface with alarming efficiency.
However, the conversation has moved far beyond stolen data. The threat is now physical. A compromised medical device can endanger patient safety, a hacked water treatment plant can threaten public health, and a disabled power grid can cause widespread chaos. This convergence of digital and physical risk means that IoT security is no longer just an IT problem; it is a fundamental issue of business resilience and public safety.
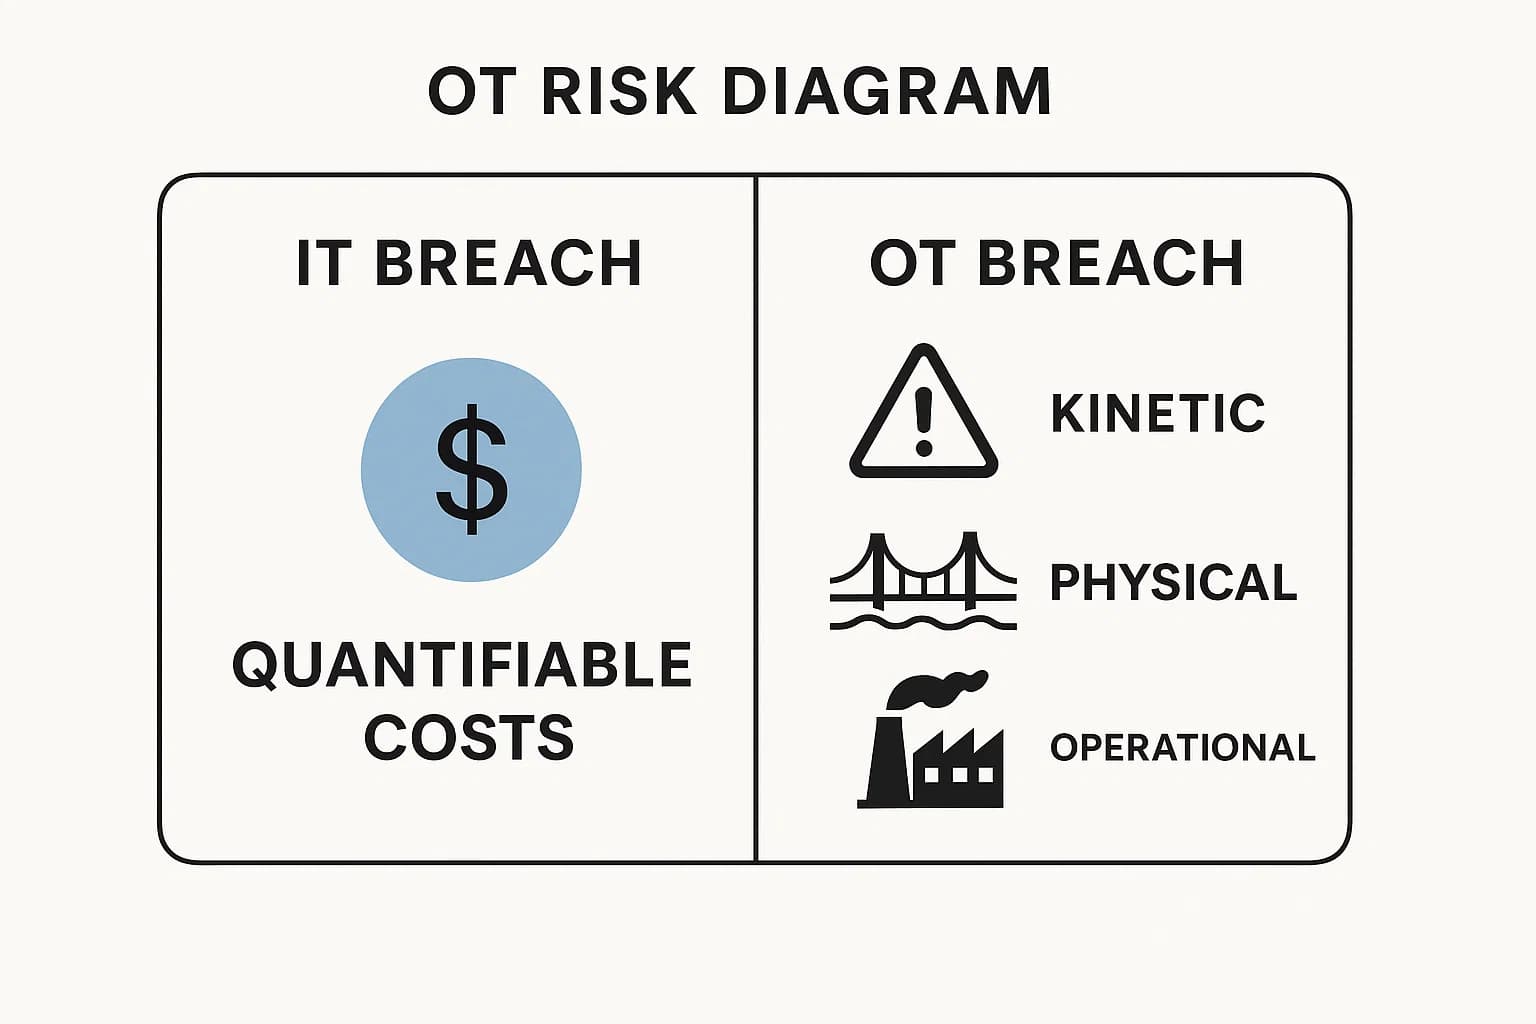
This shift has fundamentally altered the risk calculus for corporate boards and executives. The "cost" of a traditional IT breach, while significant, is often quantifiable in terms of data recovery, regulatory fines, and reputational damage. The cost of an OT breach, however, is kinetic. As detailed in recent threat reports, successful attacks on manufacturing sites and water utilities lead to immediate and complete operational shutdowns. This operational stoppage has a direct, immediate, and often uncapped impact on revenue and, in the case of critical infrastructure, public safety. This gives attackers immense leverage. They are not merely threatening data; they are threatening the core function of the business or public service. This new reality explains the aggressive pivot by sophisticated ransomware actors toward OT environments, where the pressure to pay for decryption keys is highest.
The sheer volume of malicious activity targeting IoT devices is staggering, although no one publishes a reliable global count of attacks per day. The best measured figure comes from home networks: Bitdefender and NETGEAR found the average home network faces 29 attacks per day across its 22 connected devices. For any internet-facing device, that is a constant, automated hum of malicious activity.
This is part of a much larger wave of cyber threats. In the first quarter of 2025 alone, Kaspersky blocked 629,211,451 attacks launched from online resources, demonstrating the scale of the infrastructure used to find and exploit vulnerable endpoints.
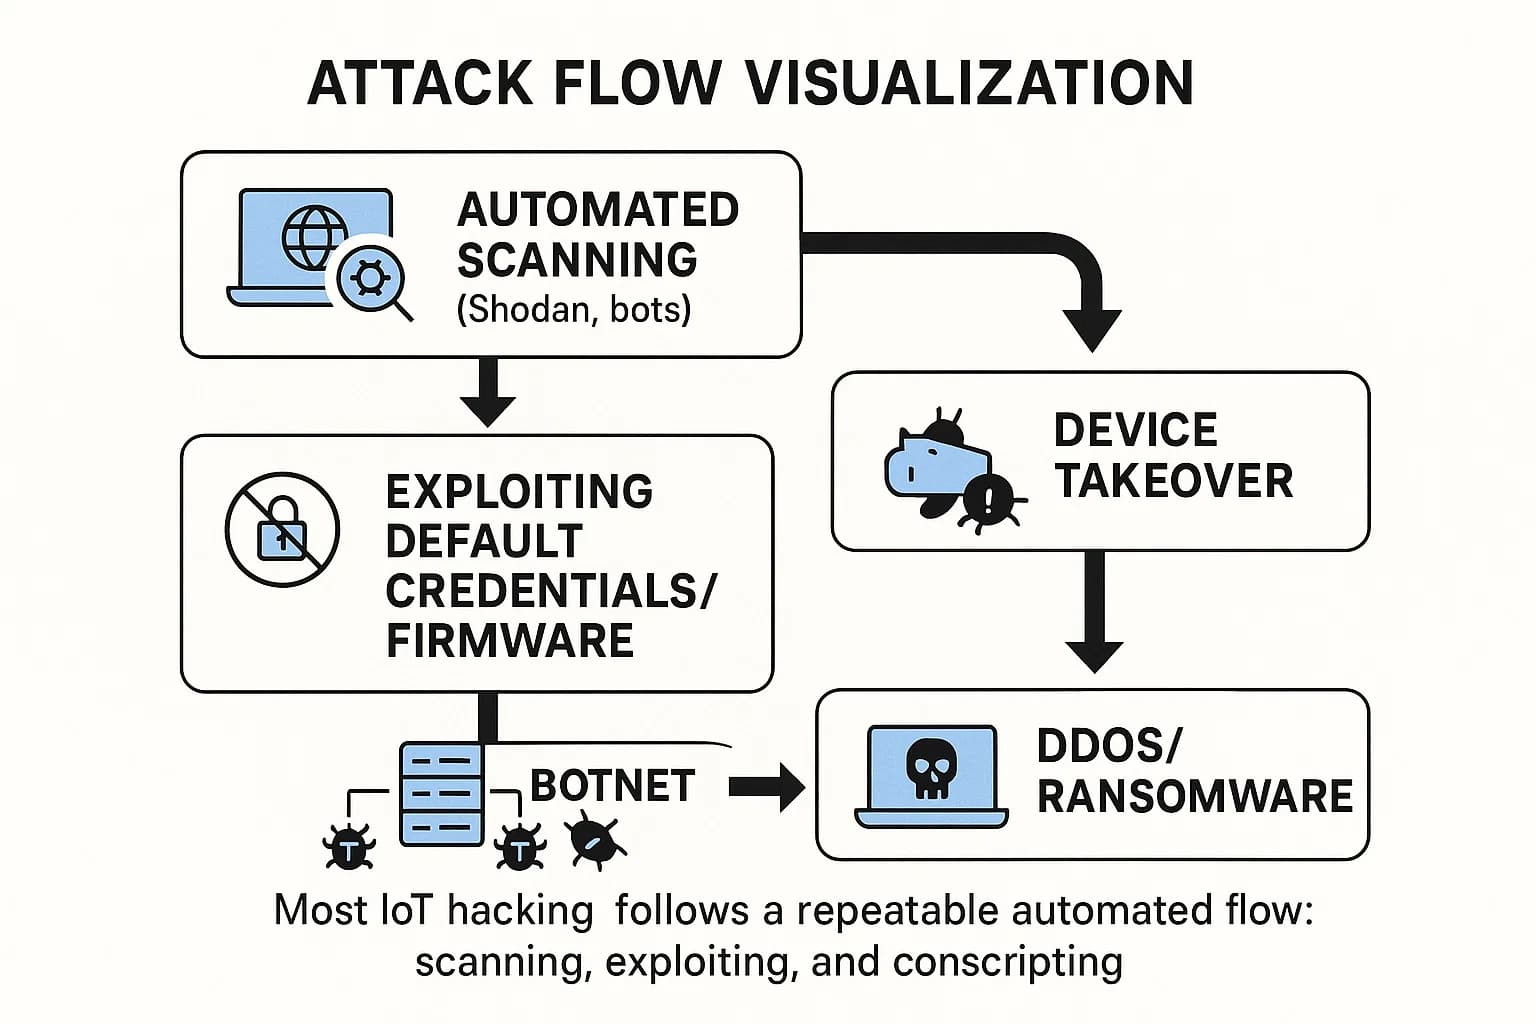
It is crucial to understand the nature of these "attempts." The vast majority are not targeted, human driven efforts. Instead, they represent the output of a global, automated reconnaissance machine. Threat intelligence from Fortinet's 2025 Global Threat Landscape Report reveals a 16.7% worldwide rise in active scanning, as adversaries deploy automated tools to create a near real time map of the internet's attack surface. These scans relentlessly probe for open ports, outdated firmware, and default credentials, the low hanging fruit of the IoT world.
This high volume of unsuccessful daily attacks should not be interpreted as a sign of effective security. Rather, it is a measure of the adversary's investment in intelligence gathering. By the time a sophisticated, targeted attack is launched, the adversary has often already completed their mapping and identified the weakest points of entry. This reality underscores the futility of a purely reactive defense posture. Proactive strategies, such as attack surface reduction and continuous security validation, are the only logical response to an adversary that is always watching.
DeepStrike's Mobile Application Penetration testing targets the companion apps that control IoT devices, where the credentials and API keys usually live.
The financial consequences of an IoT security failure are severe and escalating, particularly when operational technology is involved. Back in 2019, an Irdeto survey of 700 firms already put the average financial impact of an IoT-focused attack at more than $330,000, and these incidents often serve as the initial entry point for much larger, more devastating enterprise breaches.
Sector-specific breach costs show where attackers find the most leverage:
These multi million dollar incidents add up quickly. For a deeper analysis of these financial trends, explore our complete report on data breach statistics and trends.
The escalating cost of IoT/OT breaches is creating powerful secondary effects that are reshaping cybersecurity investment. The clear, quantifiable financial risk associated with an OT compromise provides the actuarial basis for insurance carriers to charge significantly higher premiums for organizations with insecure industrial environments. Simultaneously, new regulations, such as the SEC's requirement for public companies to disclose material cybersecurity incidents, make the financial impact of these attacks transparent to investors and regulators. This creates a pincer movement of market and regulatory pressure, compelling organizations to adopt stronger security controls not merely for protection, but as a non-negotiable cost of doing business and securing liability coverage.
The most unsettling aspect of the IoT threat landscape is that the vast majority of successful attacks do not rely on sophisticated, nation state level capabilities or complex zero day exploits. Instead, they prey on a handful of fundamental, systemic security failures that are baked into devices from the factory floor. For more on advanced threats, see our Zero day exploit lifecycle and prevention.
The core problems plaguing IoT security have been well documented for years. These foundational statistics, while older, remain critical for understanding the scale of the "security debt" the industry has accumulated:
The latest threat intelligence from 2025 confirms that these fundamental flaws remain the primary vectors for compromise:
These persistent failures map directly to the OWASP IoT Top 10, a project that catalogs the most critical security risks to Internet of Things devices. The issues of default credentials and unencrypted traffic fall squarely under categories like "I1 Weak, Guessable, or Hardcoded Passwords" and "I7 Insecure Data Transfer and Storage".
Ultimately, the IoT security crisis is not a technological failure but an economic one. For years, manufacturers have been economically incentivized to prioritize speed to market and low production costs over robust security. Implementing features like encryption chips, unique credential generation, and secure update servers adds to the bill of materials and can delay product launches. Because the manufacturer does not directly bear the cost when one of their devices is conscripted into a botnet, security has been treated as an externality. The collective cost of millions of insecure devices is borne by society at large the victims of massive DDoS attacks or enterprise ransomware campaigns. This fundamental market failure is the true root cause of the problem and is precisely what new government regulations are now attempting to correct.
These statistics represent real world attacks with tangible consequences. The following case studies illustrate the modern threats facing IoT and OT environments.
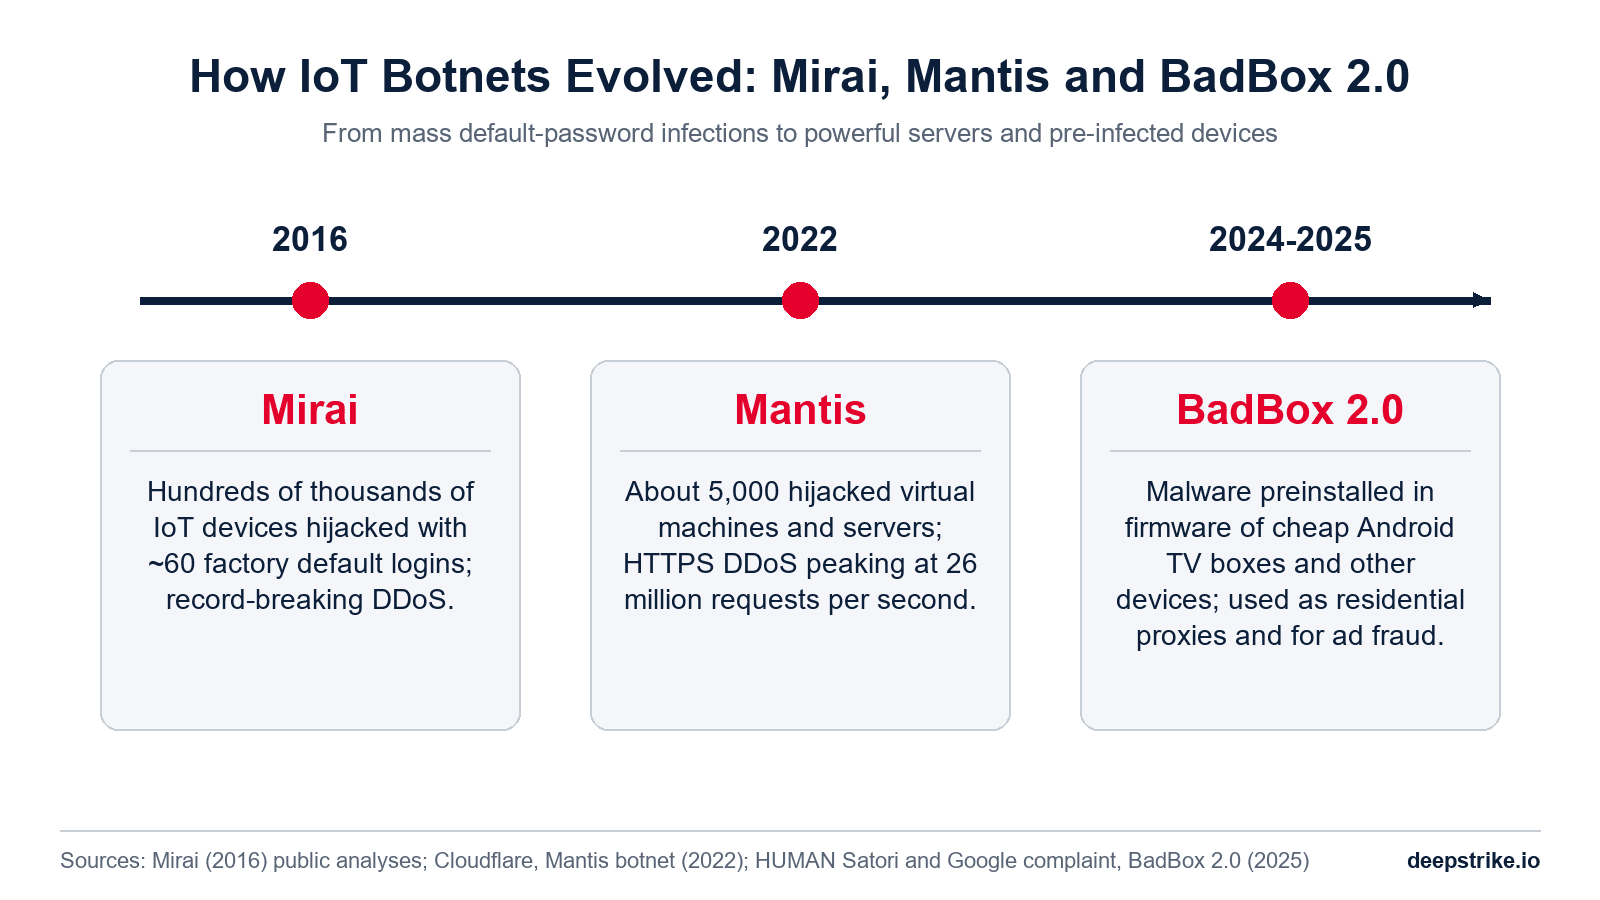
To understand the current threat landscape, it is essential to look at the evolution of IoT botnets.
This evolution from Mirai to Mantis signifies a critical change in adversary tactics, moving from "brute force" (quantity of bots) to "precision strike" (quality of bots). Mirai's strength was its sheer scale, and mitigation often involved blocking huge ranges of residential IP addresses. Mantis's strength is its power density, with each bot possessing high bandwidth and CPU resources. This enables complex application layer attacks that are harder to distinguish from legitimate traffic and originate from seemingly trustworthy sources like cloud providers and data centers. This shift demands more sophisticated, behavior based detection and mitigation strategies.
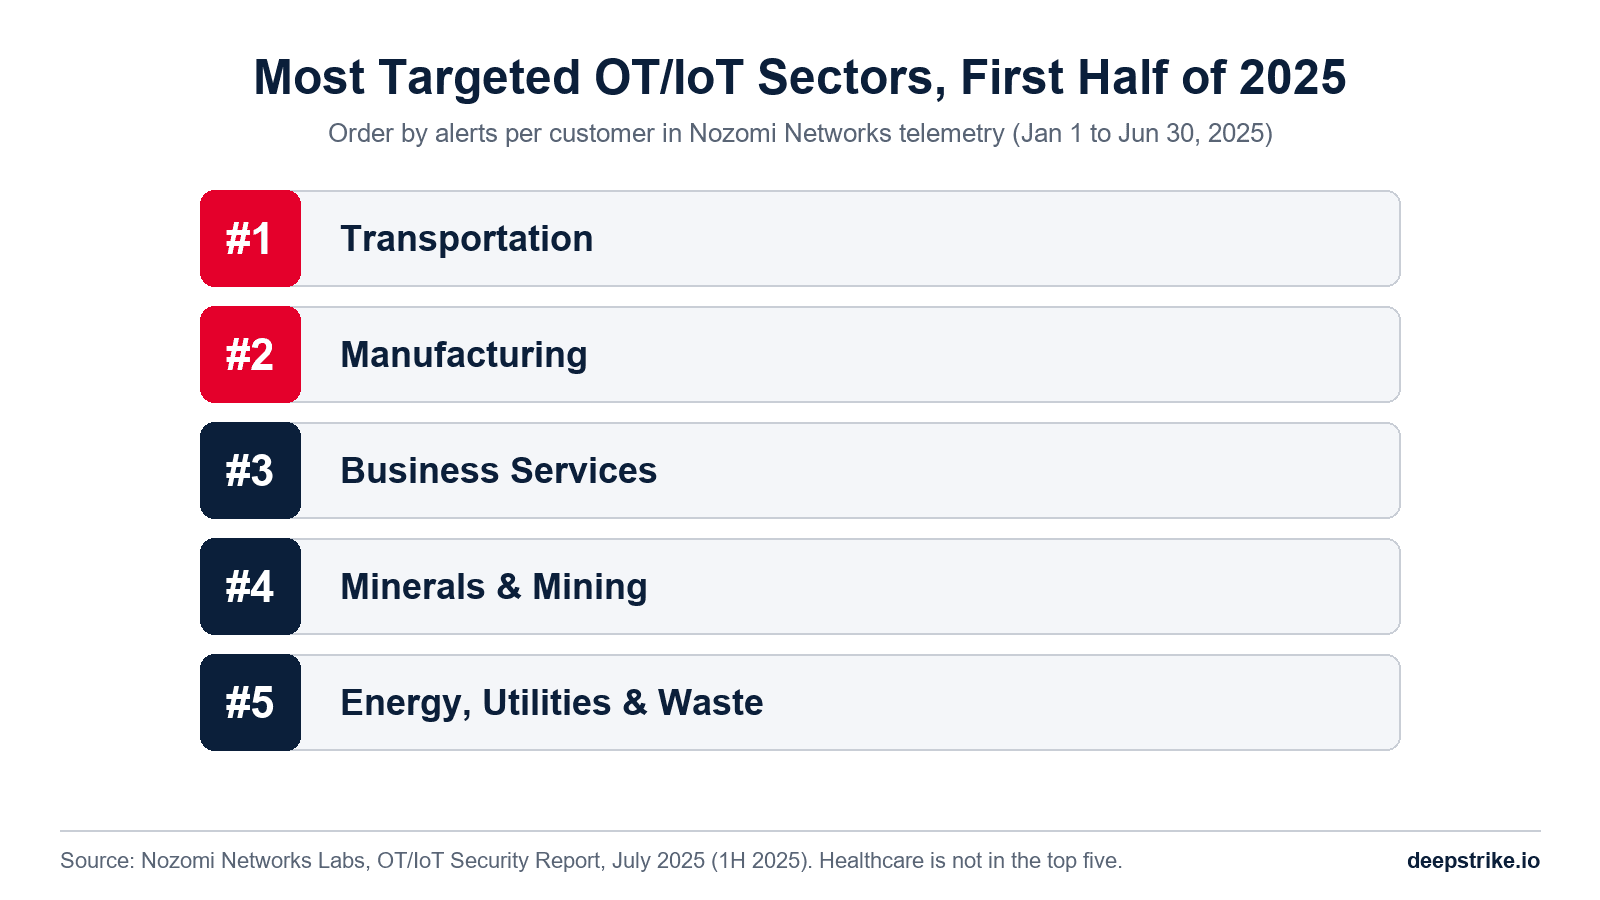
While all sectors are at risk, attackers are increasingly focusing their efforts on high value targets where a successful breach can cause maximum disruption and yield the largest payouts. The latest data from 2025 reveals a clear focus on industrial and critical infrastructure sectors.
Nozomi Networks telemetry from OT environments placed transportation and manufacturing first and second throughout 2025. In its June to August 2026 data, manufacturing overtook transportation and energy and utilities moved into third place. This reflects a strategic choice by adversaries to target industries where operational continuity is paramount and the potential for disruptive leverage is highest.
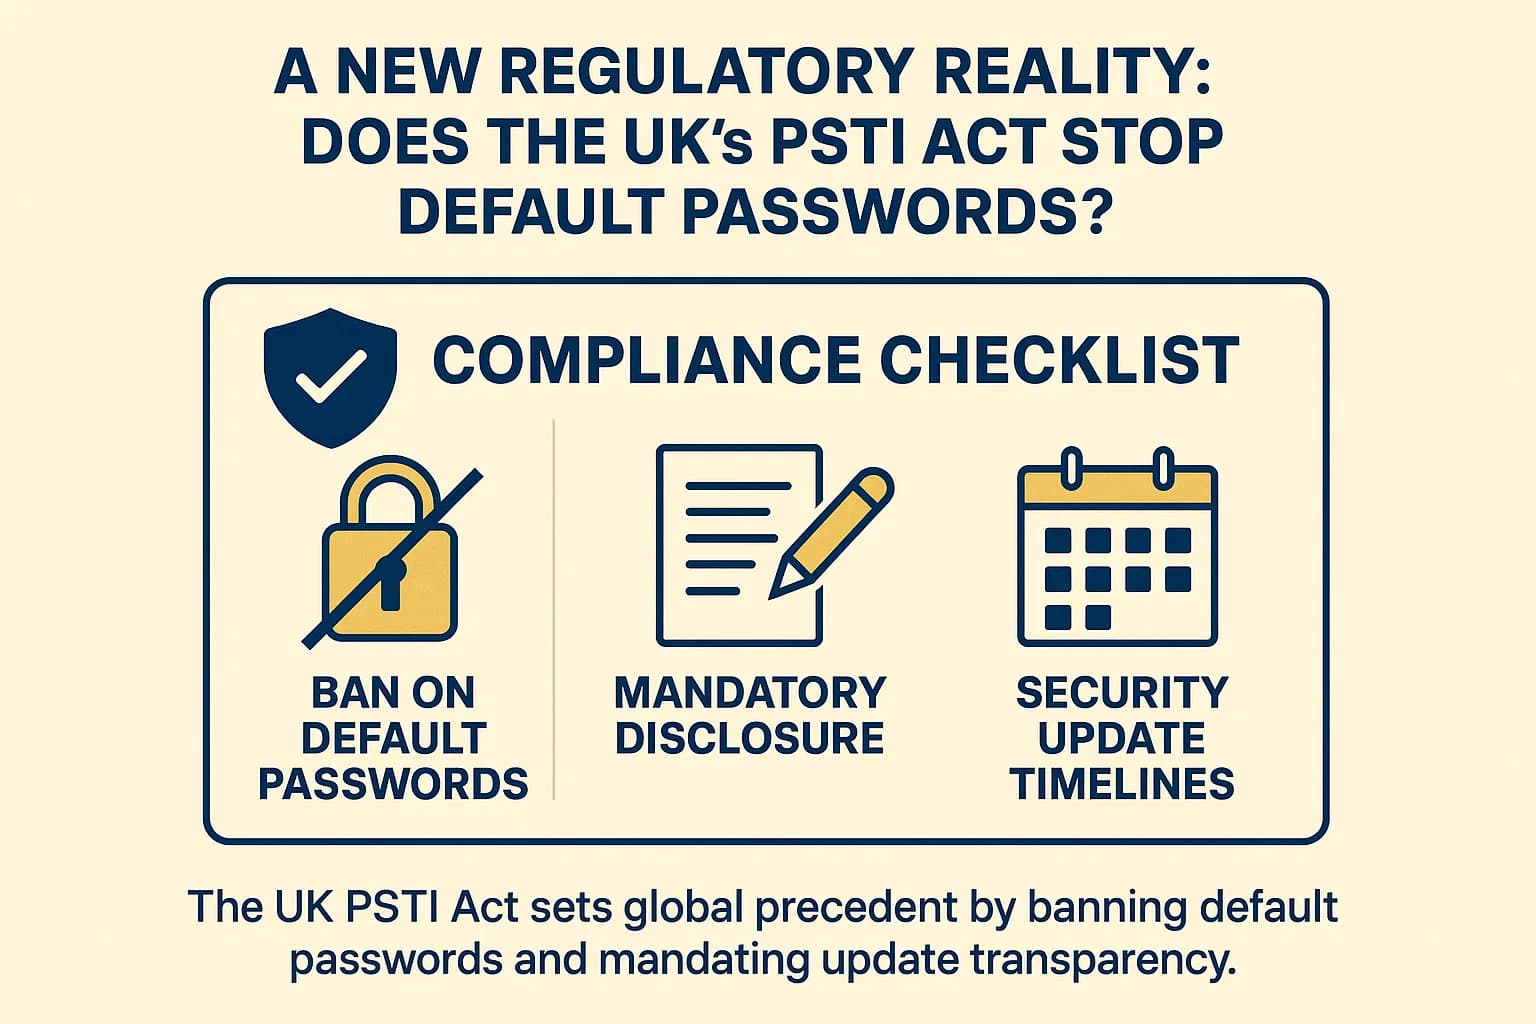
In response to the crisis of "insecurity by design," governments are beginning to intervene. The most significant development is the United Kingdom's Product Security and Telecommunications Infrastructure (PSTI) Act, which came into full effect on April 29, 2024. This landmark legislation is the first of its kind to legally mandate baseline cybersecurity standards for consumer connectable products.
For UK manufacturers, importers, and distributors (see our UK penetration testing services), the PSTI Act imposes three core requirements on smart devices sold in the UK:
Enforcement is robust, with the UK's Office for Product Safety and Standards (OPSS) empowered to issue fines of up to £10 million or 4% of a company's global revenue, whichever is higher, for non compliance.
The PSTI Act represents a direct legislative attempt to correct the economic market failure that has fueled the IoT security crisis. By imposing a significant financial penalty for insecure practices, the law fundamentally alters the economic calculation for manufacturers. A global device maker now faces a choice: create a separate, more secure (and potentially more expensive) product line just for the UK market, or elevate the security baseline of their entire global product line to meet PSTI standards. Given the immense logistical complexity and cost of managing separate SKUs, firmware branches, and supply chains, it is often more efficient to adopt the strictest standard as the global default. Consequently, this UK specific law is expected to have a significant ripple effect, improving the security of IoT devices sold worldwide.
The UK's PSTI Act was the opening move, not the whole game. Two further regimes have since followed, and together they push "security by design" from a slogan toward a market-access requirement. Manufacturers selling into the UK must meet PSTI now; those selling into the EU must meet CRA reporting duties from 11 September 2026 and its essential requirements from 11 December 2027; in the US the Cyber Trust Mark is voluntary, except that federal buyers are directed to require it for consumer IoT from January 2027.
| Regulation | Region | Status | Core requirement |
|---|---|---|---|
| PSTI Act | UK | In force since April 2024 | Bans default and universal passwords; mandatory vulnerability-disclosure policy; declared minimum security-update period. Fines up to £10M or 4% of global revenue |
| US Cyber Trust Mark | USA | Launched Jan 2025; ioXt Alliance named Lead Administrator 13 April 2026 | Voluntary consumer-IoT security label. Executive Order 14306 directs a federal procurement requirement for the mark by 4 January 2027 |
| Cyber Resilience Act (CRA) | EU | In force 10 Dec 2024; reporting obligations from 11 Sept 2026; full application 11 Dec 2027 | Mandatory security requirements for all products with digital elements: secure defaults, vulnerability handling, security updates, supply-chain accountability |
The FCC's Cyber Trust Mark is a consumer-facing security label, conceptually an Energy Star for connected devices, covering smart-home products, cameras and trackers. It launched in January 2025 and had a turbulent first year: UL Solutions withdrew as Lead Administrator in December 2025, and after an application window the FCC named the ioXt Alliance as Lead Administrator effective 13 April 2026.
The detail that matters commercially is the procurement deadline. The label is voluntary for the general consumer market, so retailers and private buyers can still sell and buy uncertified devices. But Executive Order 14306 (June 2025) directs the FAR Council to require, by 4 January 2027, that vendors selling consumer IoT products to the federal government carry the mark. Given that federal agencies are among the largest institutional buyers of connected devices, and that major retailers have signalled they will surface certified products, the practical pull extends well beyond the mandatory scope. Note the exclusions: medical devices, personal computers, smartphones and routers sit outside the programme.
The CRA (Regulation (EU) 2024/2847) is the most sweeping of the three because it is not limited to consumer IoT. It applies to essentially any product with digital elements placed on the EU market, hardware or software, across its whole lifecycle, with sector-specific carve-outs such as medical devices, vehicles and aviation. It entered into force on 10 December 2024.
The deadline most teams have wrong: full application is 11 December 2027, but the reporting obligations under Article 14 bite far earlier, on 11 September 2026. From that date manufacturers must report actively exploited vulnerabilities and severe incidents through the CRA Single Reporting Platform: an early warning within 24 hours, a full notification within 72 hours, and a final report within 14 days of a corrective measure for exploited vulnerabilities, or within one month of the notification for severe incidents. Critically, those reporting duties apply to products already on the market, not just new ones.
Our guide to the Cyber Resilience Act explains who must report, what counts as reportable and how security testing produces the evidence the technical file needs.
That timing creates a dependency teams routinely miss: to report on an exploited component you must first know which components are in your products, which means SBOMs and automated vulnerability tracking need to be operational before the reporting date, not before the 2027 one. Non-compliance with the essential requirements can draw fines up to €15 million or 2.5% of worldwide annual turnover. Our vulnerability management and patch management guides cover the processes this assumes you already run.
Read together, the three regimes point the same direction. The economics that produced insecure devices, where manufacturers captured the savings and users bore the botnet risk, are being corrected by law in the UK and EU, and by a voluntary label backed by federal procurement in the US. And because maintaining separate secure SKUs, firmware branches and supply chains per region is expensive, the rational response for a global manufacturer is the same one PSTI already encouraged: adopt the strictest standard as the global default. For buyers, these labels and conformity requirements are becoming a legitimate procurement filter, and a reasonable question to put to any vendor is which of the three they can already evidence.
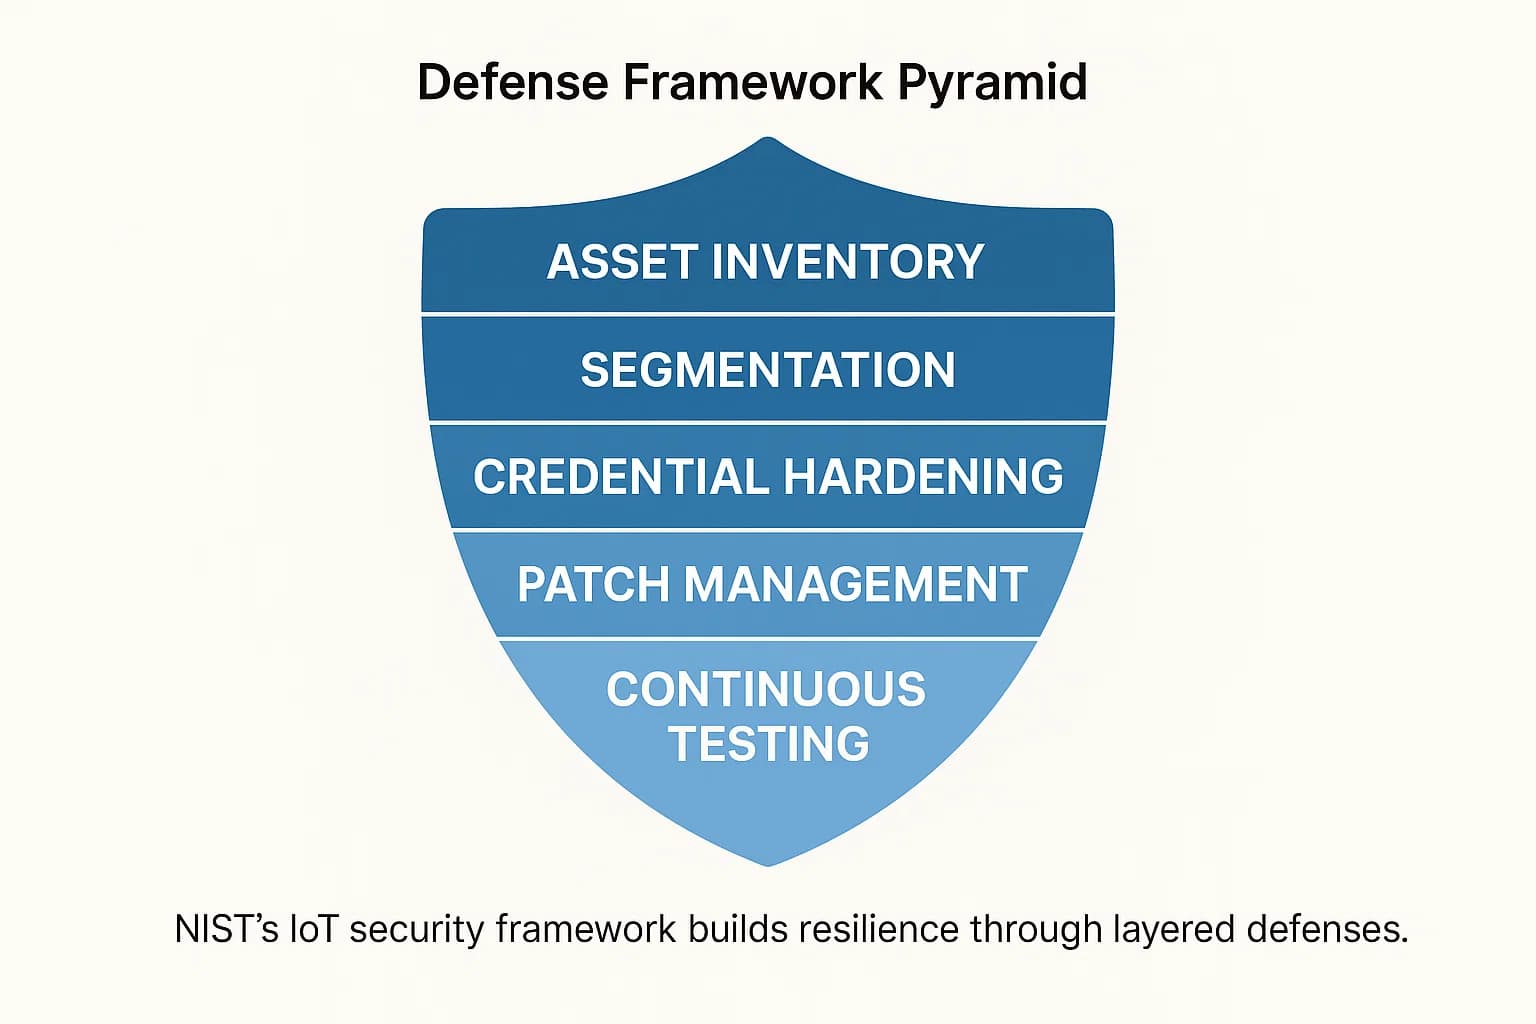
Defending against these evolving threats requires a structured, proactive approach. NIST's IoT guidance (the NISTIR 8259 series and SP 800-213) and the broader NIST Cybersecurity Framework support a risk-based approach. The following steps are our practical summary for any organization deploying IoT and OT devices.
You cannot protect what you do not know you have. The first and most critical step is to conduct a thorough discovery process to create a complete and accurate inventory of every connected device on your network. This inventory is the foundation of any effective risk management program.
Never allow your IoT and OT devices to share the same network as your critical IT systems (e.g., file servers, domain controllers). By creating separate, isolated networks (VLANs), you can contain a potential breach. If a smart camera gets compromised, segmentation prevents the attacker from "pivoting" into your core corporate network. This is a core tenet of a defense in depth strategy.
This is non-negotiable. Immediately change all default passwords on every device. Implement a policy that requires strong, unique passwords and enable multi factor authentication (MFA) wherever it is supported. Access should be granted on a principle of least privilege, ensuring users and devices only have the permissions absolutely necessary to function.
The fundamental weakness of passwords is a primary driver of IoT compromise. A powerful modern solution is FIDO2/WebAuthn, an open authentication standard that enables passwordless logins. It uses public key cryptography to create unique, unphishable credentials that are bound to a user's physical device (like a laptop's fingerprint reader or a hardware security key). When a user registers with a service, their device creates a private key (which never leaves the device) and a public key (which is sent to the server). To log in, the server sends a challenge, which the device signs with the private key. This process is immune to credential stuffing, phishing, and password theft, directly countering the attack vectors used in breaches like the 2024 Roku incident.
With a significant percentage of breaches exploiting unpatched firmware, a formal, repeatable process for tracking, testing, and deploying security updates is essential. This cannot be an ad hoc activity; it must be a core operational security function with clear ownership and accountability.
Assuming your security controls are effective is a critical mistake. To ensure resilience against evolving threats like OT targeted ransomware, organizations must proactively validate their defenses. The key difference between a vulnerability assessment and a penetration test is that the latter actively tries to exploit weaknesses to simulate a real world attack. Industrial environments need a tailored approach: OT/ICS penetration testing uses passive, safety-first techniques so live control systems are not disrupted.
For U.S. organizations, continuous testing through our U.S. penetration testing services can simulate real-world attack chains and uncover hidden vulnerabilities that automated scanners miss. Because most IoT devices are provisioned and controlled through a phone, What Is Mobile Application Penetration Testing covers the companion-app half of that chain. For organizations with dynamic IT/OT environments, a continuous testing model is crucial for staying ahead of attackers. Learn more in our guide to Penetration Testing for DevOps.
The most common attacks are automated and opportunistic, leveraging fundamental weaknesses. Brute force attacks that try thousands of common or default passwords against unencrypted protocols like Telnet are the primary method of infection. Once compromised, devices are often absorbed into botnets to conduct large scale DDoS attacks.
Hackers use automated scanning tools (like Shodan) that constantly probe the entire internet for devices responding on specific network ports, such as Telnet port 23 or SSH port 22. When a device responds, malware like Mirai automatically attempts to log in using a predefined list of common default credentials.
Absolutely. If your smart TV is on the same Wi Fi network as your work laptop and personal phone, an attacker who compromises the TV can use it as a "pivot point." From there, they can scan your internal network to find and attack more valuable targets. This is precisely why network segmentation is a critical security control.
The biggest risks stem from a combination of factors: manufacturers rushing products to market with little to no security built in ("insecurity by design"), users failing to change weak default passwords, and the lack of a consistent, automated mechanism for security updates. This creates a perfect storm for widespread, automated attacks.
Warning signs can include a sudden increase in network traffic from the device, unusually sluggish performance, device settings changing without your input, or the device rebooting unexpectedly. However, many infections are designed to be stealthy. Proactive security measures are far more effective than waiting for obvious symptoms.
Encryption is fundamental. It scrambles data so that it cannot be read or understood by anyone who might intercept it. Unit 42's 2020 research found 98% of IoT device traffic was unencrypted, so sensitive information like video feeds from a security camera, login credentials, or commands sent to a device can travel in plain text, making them trivial for an attacker to steal or manipulate.
They can be, but their safety is a shared responsibility. It depends on both the manufacturer's commitment to security and the user's diligence. To use these devices safely, you must change default passwords, enable MFA, apply updates promptly, and secure your home Wi Fi network. It is also crucial to purchase devices from reputable manufacturers that have a track record of supporting their products with security patches.
Industrial sectors. Zscaler's November 2025 report found manufacturing and transportation each accounted for 20.2% of observed IoT malware attacks, and that the Mirai, Mozi and Gafgyt families made up 75% of malicious IoT payloads. Zscaler's 2023 report had recorded a 400% year-over-year increase in IoT malware. The growth is driven by cheap insecure devices, the ransomware-as-a-service economy, and automated scanning that turns any exposed, unpatched device into a target soon after it comes online.
Healthcare. IBM's 2026 report puts the average healthcare breach at $6.64 million, the highest of any industry for the 15th consecutive year, driven by life-safety stakes, highly sensitive records, and the growth of connected medical devices (IoMT). Industrial and manufacturing breaches also run into the millions once operational downtime is counted, and in OT environments that downtime component often exceeds the data-recovery cost.
They are starting to. The UK PSTI Act legally banned default passwords in April 2024, the US Cyber Trust Mark gives consumers a security label and, from January 2027, gates federal procurement of consumer IoT, and the EU Cyber Resilience Act imposes mandatory security requirements on connected products with reporting duties from September 2026. None of them fixes the installed base of already-deployed insecure devices, but they attack the root economic cause, and because global manufacturers avoid region-specific product lines, the effect is expected to raise device security worldwide.
The statistics for 2025 and 2026 are unequivocal: IoT and OT threats keep growing, fueled by basic, preventable security failures with multi million dollar consequences. The industrialization of attacks against cyber physical systems, the economic incentives that perpetuate insecure by design products, and the new regulatory response all point to a landscape of increasing complexity and risk.
The sheer scale of the problem can feel overwhelming, but the path forward is not about finding a single, complex solution. It is about a consistent, disciplined commitment to foundational security hygiene. Moving from a state of passive awareness to one of proactive readiness is the only viable strategy. This means implementing the fundamentals of strong credential management, rigorous network segmentation, and timely patching. Most critically, it means rigorously validating those defenses through continuous, expert led testing. In the hyper connected world of 2026, assuming you are a target is the first and most essential step toward building a truly resilient defense.
Ready to Strengthen Your Defenses?
Today's IoT threats demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
About the Author
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
