August 24, 2025
Updated: November 4, 2026
A 2026 guide to embedding penetration testing and DevOps security practices in CI/CD, using the OWASP CI/CD risks, SLSA and NIST SP 800-204D.

Mohammed Khalil

Penetration testing for DevOps means building security testing into the CI/CD pipeline: automated scans run on every change, human-led pentests cover high-risk releases, and the pipeline itself is tested as an attack target, because it holds the keys to production. In short:

Penetration testing for DevOps is the practice of embedding automated and continuous security validation across the entire Software Development Lifecycle (SDLC). This approach augments, not replaces, human led pentests: automation covers breadth on every build, while experts probe complex business logic and chained exploits that scanners miss. It also works best alongside threat modeling at design time, so the highest-risk flaws are caught before code exists rather than after deployment. As development teams scale their projects, partnering with a software development company like Binary Studio can provide additional engineering expertise while keeping security considerations integrated throughout the software development lifecycle.
In 2026, this is non-negotiable. The CI/CD pipeline itself is a prime target. The XZ Utils upstream backdoor (CVE-2024-3094) showed how a sophisticated, patient attacker could compromise a core dependency and ripple into production systems worldwide. For U.S. DevOps teams protecting CI/CD pipelines, breach costs averaging $11.5M in IBM's 2026 report (up from $10.22M in 2025) make proactive security a financial necessity.
DeepStrike's Continuous Security Testing adds manual testing of newly deployed features, which can find logic flaws that automated SAST and DAST gates typically miss.

A modern DevSecOps program aligns with key industry standards that provide a battle tested roadmap for security.
You can start integrating security into your pipeline by following a clear, five step process. This checklist provides a structured way to begin shifting security left without overwhelming your development teams.

Each type of security scan plays a specific role at a different stage of the pipeline, providing a defense in depth strategy.
Other helpful entities to be aware of for a comprehensive security posture include CISA, ENISA, CERT-In, MFA, and infostealer malware.

Poisoned Pipeline Execution (PPE) is an attack where malicious commands are injected into a pipeline's configuration file and run with the CI system's permissions. It's identified as CICD-SEC-4 in the OWASP Top 10 CI/CD Security Risks.
A strong PPE playbook includes these countermeasures:
GitLab Enable SAST on Every Merge Request You can enable SAST with a simple template include, then enforce a gate using Merge Request approval policies (GitLab Ultimate).
#.gitlab-ci.yml
include:
  - template: Jobs/SAST.gitlab-ci.yml

# Then add a merge request approval policy (Secure > Policies, GitLab Ultimate)
# that requires approval when SAST reports High or Critical findings.
This configuration ensures SAST runs before code is merged, and an enforced approval policy requires approval before merge requests with High or Critical SAST findings reach your main branch.
GitHub ZAP Baseline Action as a DAST Gate This GitHub Action runs an OWASP ZAP scan against a staging URL and can be configured to fail the build if it finds vulnerabilities.
#.github/workflows/zap.yml
name: ZAP baseline
on: [push, pull_request]
jobs:
  zap:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - name: ZAP baseline scan
        uses: zaproxy/action-baseline@v0.14.0
        with:
          target: https://staging.example.com
          fail_action: true
          rules_file_name: '.zap/rules.tsv'   # Ignore tuned false positive rules
          cmd_options: '-a'                   # Also run alpha passive rules (baseline scans are passive only)
The fail_action: true parameter is what turns this scan into a practical security gate. Baseline scans are passive; use the ZAP full scan action against a dedicated test environment if you need active testing.
Cryptographically signing your artifacts provides a verifiable guarantee of their integrity. Sigstore's Cosign tool enables "keyless" signing, which is ideal for automated CI/CD environments.
# Build & push image first, then:
cosign sign --yes $IMAGE_DIGEST
trivy image --format spdx-json -o sbom.json $IMAGE
cosign attest --yes --predicate sbom.json --type spdxjson $IMAGE_DIGEST
This workflow signs a container image digest and attaches an SBOM as a verifiable attestation, using short lived certificates instead of manually managed keys.
DevOps security is the set of practices that protect the code, pipelines, build systems, credentials and environments a team uses to ship software, so that faster delivery doesn't open new ways in. The scanners above check the application. DevOps security also has to protect the pipeline, because a CI/CD system holds production credentials, decides what gets deployed and runs code from many sources. Penetration testing is how you find out whether those protections actually hold.
These practices sit inside a wider secure software development lifecycle (SSDLC), which also covers requirements, design and code review. For pipeline-specific government guidance, CISA and the NSA published joint guidance on defending CI/CD environments in June 2023, which lists common pipeline risks and recommended mitigations.
The OWASP Top 10 CI/CD Security Risks is the most useful shared vocabulary for pipeline threats. The table lists all ten risks, how each one tends to show up, and what a tester checks during a pipeline-focused assessment.
| Risk | How it shows up | What a pentest checks |
|---|---|---|
| CICD-SEC-1: Insufficient Flow Control Mechanisms | One person or one compromised account can push code or artifacts to production without review | Whether branch protection, required reviews and approval rules can be bypassed by an admin, a bot token or a direct push |
| CICD-SEC-2: Inadequate Identity and Access Management | Stale accounts, shared logins and over-broad roles across source control, CI and registries | Account inventory, MFA and SSO coverage, and whether former staff or unused service accounts still have access |
| CICD-SEC-3: Dependency Chain Abuse | A malicious or hijacked package is pulled into a build through typosquatting, dependency confusion or a compromised maintainer | How package sources are resolved, whether internal package names can be claimed on public registries, and whether lockfiles are enforced |
| CICD-SEC-4: Poisoned Pipeline Execution (PPE) | Someone who can change a pipeline file, or a script it calls, runs commands with the pipeline's permissions | Which branches and forks can trigger privileged jobs, and whether pull request builds can reach secrets |
| CICD-SEC-5: Insufficient PBAC (Pipeline-Based Access Controls) | Every job gets the same broad access to secrets, networks and hosts | Whether each job's token, secrets and network reach match what that job needs |
| CICD-SEC-6: Insufficient Credential Hygiene | Long-lived keys in CI variables, secrets printed to logs, tokens committed to repositories | Secrets in repository history, build logs and artifacts; credential lifetime and rotation |
| CICD-SEC-7: Insecure System Configuration | Unpatched CI servers, default settings, exposed admin consoles, shared self-hosted runners | Versions and hardening of CI, source control and registry systems, and runner isolation between jobs |
| CICD-SEC-8: Ungoverned Usage of 3rd Party Services | Third-party apps, actions and integrations hold access that nobody reviews | OAuth app and integration permissions, and whether third-party actions are pinned and approved |
| CICD-SEC-9: Improper Artifact Integrity Validation | An artifact can be swapped or modified between build and deploy without anyone noticing | Whether signatures and provenance are verified before deployment, not only produced |
| CICD-SEC-10: Insufficient Logging and Visibility | Pipeline and source control changes are not logged or not monitored | Whether audit logs exist, are retained, and would show a malicious pipeline change |
These risks are not theoretical. In March 2025, CISA warned that the widely used GitHub Action tj-actions/changed-files had been compromised (CVE-2025-30066), exposing secrets such as access keys, GitHub personal access tokens, npm tokens and private RSA keys from affected workflows. CISA's alert on the tj-actions compromise told affected organizations to treat those secrets as compromised and rotate them. One incident touched three risks at once: third-party services (CICD-SEC-8), the dependency chain (CICD-SEC-3) and credential hygiene (CICD-SEC-6).
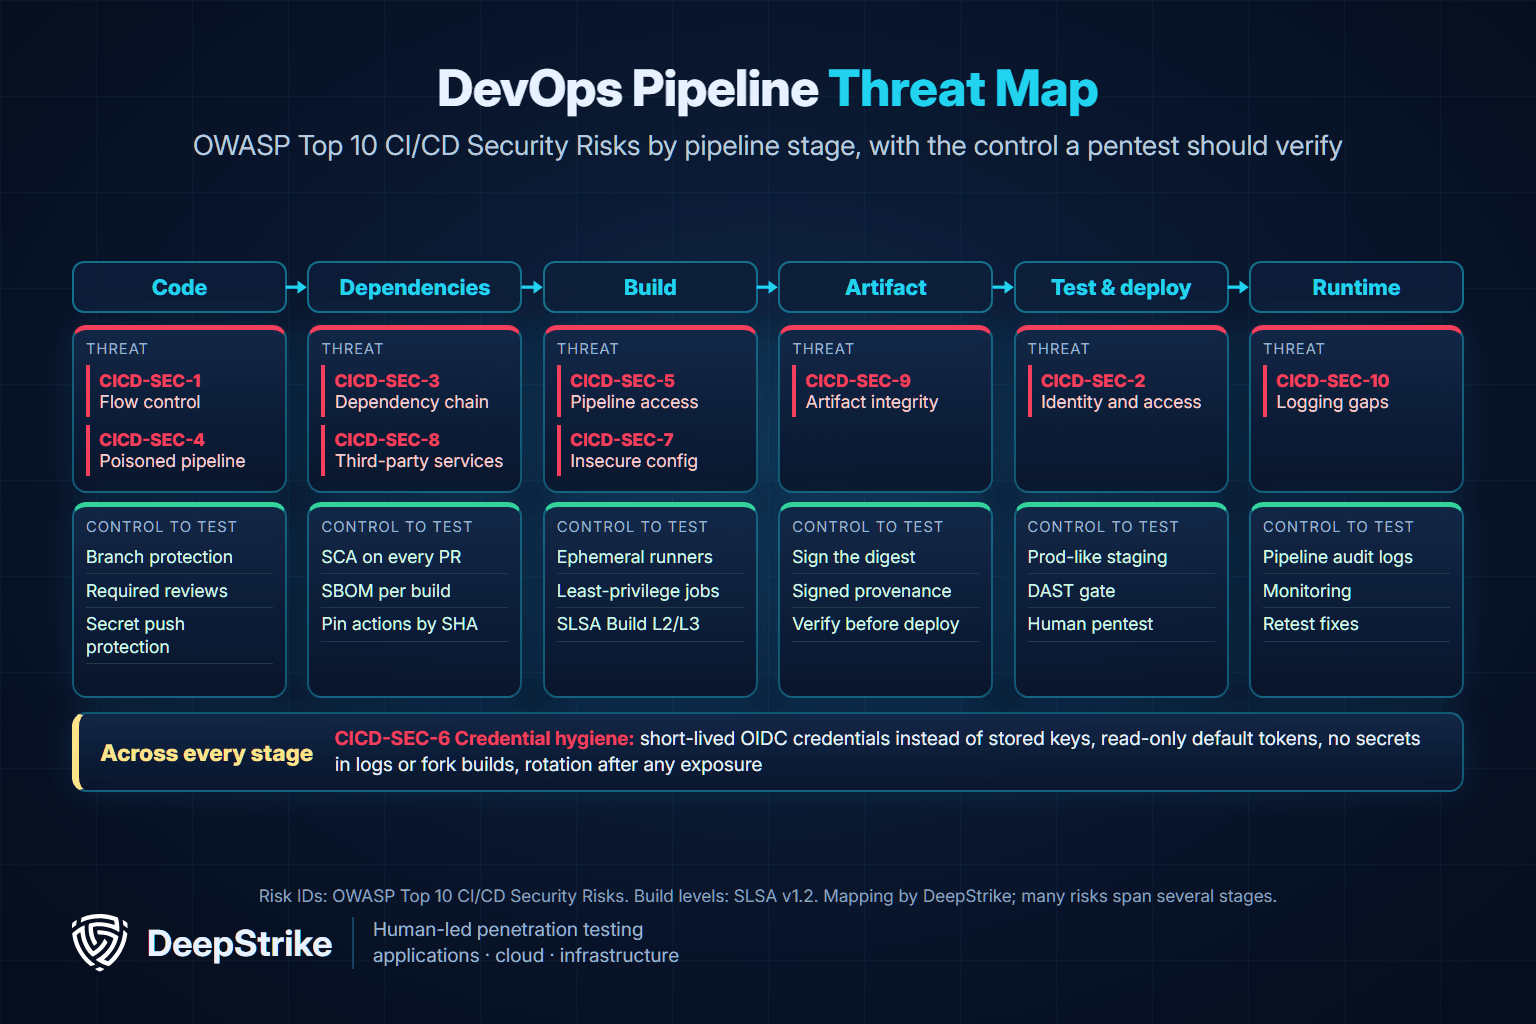
Pipelines need credentials to deploy, but every stored credential is something an attacker can lift from a log, a fork build or a compromised dependency. The goal is fewer secrets, shorter lifetimes and narrower scope:
In a pentest, secrets are often the shortest path from a pipeline weakness to real impact. A DevOps-focused test should cover repository history, build logs, artifacts and container image layers, not only the running application.
SLSA (Supply-chain Levels for Software Artifacts) defines how far you can trust that an artifact was built from the expected source by the expected process. The current specification, v1.2, has a Build track with four levels:
| Level | What it adds | What it protects against |
|---|---|---|
| Build L0: No guarantees | Nothing; L0 is the absence of SLSA | Nothing |
| Build L1: Provenance exists | A consistent build process, with provenance that describes how the artifact was built | Mistakes and missing documentation; easy to bypass or forge |
| Build L2: Hosted build platform | Builds run on a hosted platform that generates and signs the provenance; consumers verify it | Tampering after the build |
| Build L3: Hardened builds | Runs can't influence each other, and signing secrets are kept away from user-defined build steps | Tampering during the build, including by insiders, compromised credentials or other tenants |
Build L2 is a realistic first target for most teams, and the Sigstore Cosign signing and attestation workflow shown earlier is one way to produce what it needs. Aim for L3 on the artifacts that matter most, such as release builds of customer-facing services. The step teams most often skip is verification: provenance only helps if the deploy stage, or an admission controller in Kubernetes, rejects artifacts whose signature or provenance doesn't match. That is CICD-SEC-9 in practice.
Testers check this by trying to deploy an unsigned or re-tagged image through the normal path and seeing whether anything stops it. Our Kubernetes penetration testing guide covers how admission controls are assessed in a cluster.
CI/CD vulnerability scanning means checking code, dependencies, container images and infrastructure definitions automatically inside the pipeline, so known vulnerabilities are caught before release. Dependencies deserve particular attention, because most of a modern application is third-party code and software supply chain attacks target exactly that layer. A practical setup:
Scanners find known issues in known components. They don't tell you whether a vulnerable function is reachable, whether a finding chains with a misconfiguration, or whether a business rule can be abused. For what each automated method can and can't find, see our comparison of SAST vs DAST vs IAST vs RASP.
A DAST scan or a pentest is only as trustworthy as the environment it runs against. If staging uses a different identity provider, skips the WAF, runs older images or has debug settings switched on, its findings won't match production in either direction. You get false alarms for issues production doesn't have, and false confidence about controls production relies on. To keep test results meaningful:
Some checks still belong in production, such as external exposure, TLS and DNS. Run those with written authorization, agreed time windows and rate limits. The same rule applies to pipelines: a CI/CD assessment can touch source control, build systems and cloud accounts, so name each one in the rules of engagement.
Automated gates cover known issues. A periodic human review of the pipeline itself covers the rest: flow-control bypasses, privileged fork builds, over-scoped tokens and unverified artifacts. If you want that review to keep pace with your releases, DeepStrike's continuous penetration testing services pair comprehensive penetration tests twice a year with testing of newly deployed features, functions and APIs.

To demonstrate the ROI of your DevSecOps program, track these key metrics:
Key KPI Definitions
These are illustrative examples, not client results.
For UK software teams embedding pentesting into CI/CD, routine SAST/DAST/SCA scans can run on each change, while human-led pentests should be scheduled for high-risk releases. Our comparison of PTaaS vs. Traditional Penetration testing covers which delivery model keeps up with a weekly release cadence
Your pipeline should align with NIST SSDF (SP 800-218) for process maturity, NIST SP 800-204D for supply chain controls, OWASP Top 10 CI/CD for pipeline threats, and aim for SLSA Build Level 2 (signed provenance generated by a hosted build platform).
Tune your rulesets. Start by only blocking on High/Critical findings. Use per-repository baseline or ignore lists (e.g., ZAP's rules.tsv or Semgrep's --baseline flag) to manage accepted risks and false positives.
Follow the OAuth 2.0 Security Best Current Practice and ensure your DAST tool is configured to handle token based authentication flows.
DevOps security is the practice of protecting the whole software delivery process, including source code, CI/CD pipelines, build systems, secrets, dependencies and deployment environments, without slowing delivery down. It combines automated checks in the pipeline, such as SAST, SCA, secret scanning and IaC scanning, with pipeline hardening against the OWASP Top 10 CI/CD Security Risks, build integrity controls such as SLSA, and periodic human-led penetration testing.
CI/CD vulnerability scanning is automated security scanning that runs inside the build and release pipeline. Typical scans are SAST on source code, SCA on open source dependencies, container image scanning, IaC scanning and DAST against a staging environment. Results feed security gates that block High or Critical findings before deployment. It finds known issues quickly but doesn't replace manual testing for business logic flaws and chained attacks.
Integrating penetration testing into DevOps is the definitive way to build secure software at modern speeds. It’s a strategic shift from reactive, end-of-cycle security to a proactive, continuous, and developer-centric model. By leveraging automation, aligning with modern standards like NIST SSDF and SLSA, and fostering a culture of shared responsibility, you can transform your CI/CD pipeline into your strongest security asset.
The journey starts with small, iterative steps: add one scanner, tune the results, and automate a single gate. Over time, these incremental improvements compound to create a resilient, secure, and efficient software delivery process that doesn't just meet compliance requirements (see our PCI DSS 11.3 penetration testing guide); it builds trust with every release.

Ready to Strengthen Your Defenses?
The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements for Fortune 500 companies, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
