June 23, 2025
Updated: November 5, 2026
How zero-day attacks work in 2026 and why they demand behavioral detection, proactive threat hunting, and Zero Trust security strategies.

Mohammed Khalil

A zero-day exploit is code or a technique that abuses a software, hardware, or firmware flaw the vendor does not yet know about or has not yet patched. The name reflects the vendor’s position: it has had zero days to fix the problem before attackers use it. Because no patch or signature exists yet, traditional defenses usually miss early attacks. Once a fix ships, the flaw becomes an n-day vulnerability.
In 2026, understanding zero-day security exploits isn't just for security analysts; it's a critical business imperative. The threat landscape is evolving at an unprecedented pace, as detailed in the latest cybersecurity statistics for 2026. Attackers are weaponizing vulnerabilities faster than ever: Mandiant estimates the mean time to exploit fell to -7 days in 2025, meaning exploitation routinely begins before a patch is released (Mandiant M-Trends 2026). Google tracked 90 zero-days exploited in the wild in the same year (Google Threat Intelligence Group).
This isn't about theoretical risks. These are real-world attacks happening now, targeting everything from your web browser to the critical infrastructure that powers our daily lives. This guide starts with the core vocabulary of vulnerability, exploit, threat, risk and attack, then breaks down what a zero-day exploit is, why it matters in 2026, and provides an actionable playbook for detection, prevention, and response, backed by insights from leading authorities like NIST, CISA, Google, and Mandiant.
Before getting into zero-days, it helps to pin down five words that security teams often use interchangeably. A vulnerability is a weakness. An exploit is the code or technique that takes advantage of that weakness. A threat is a person, group or event with the potential to cause harm through it. Risk is how likely that harm is and how bad it would be for your organization. An attack is the actual attempt. "Zero-day" is not a sixth category: it is a timing label that can describe a vulnerability, an exploit or an attack while no fix is available.
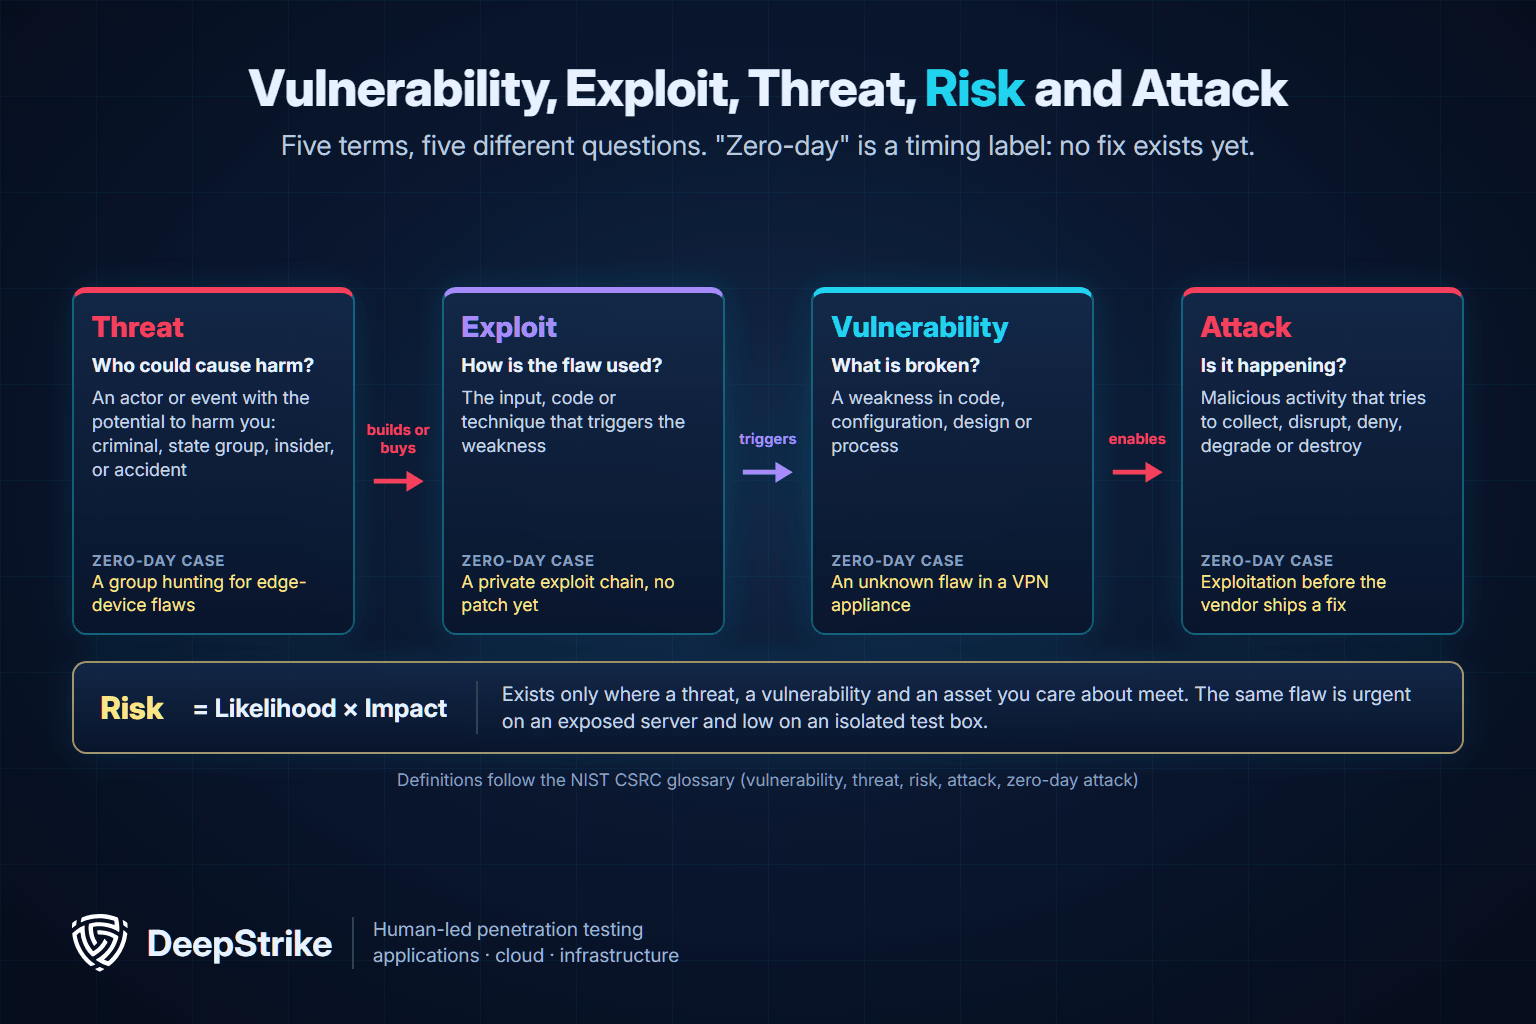
NIST defines a vulnerability as a "weakness in an information system, system security procedures, internal controls, or implementation" (NIST CSRC glossary: vulnerability, citing FIPS 200 and SP 800-53 Rev. 5). The weakness can sit in code, configuration, design or process. Common examples include an outdated library with a published flaw, a default administrator password, an API endpoint that skips an authorization check, and a firewall rule that exposes a management interface to the internet. Our roundup of the most common web vulnerabilities covers the application-layer versions in depth.
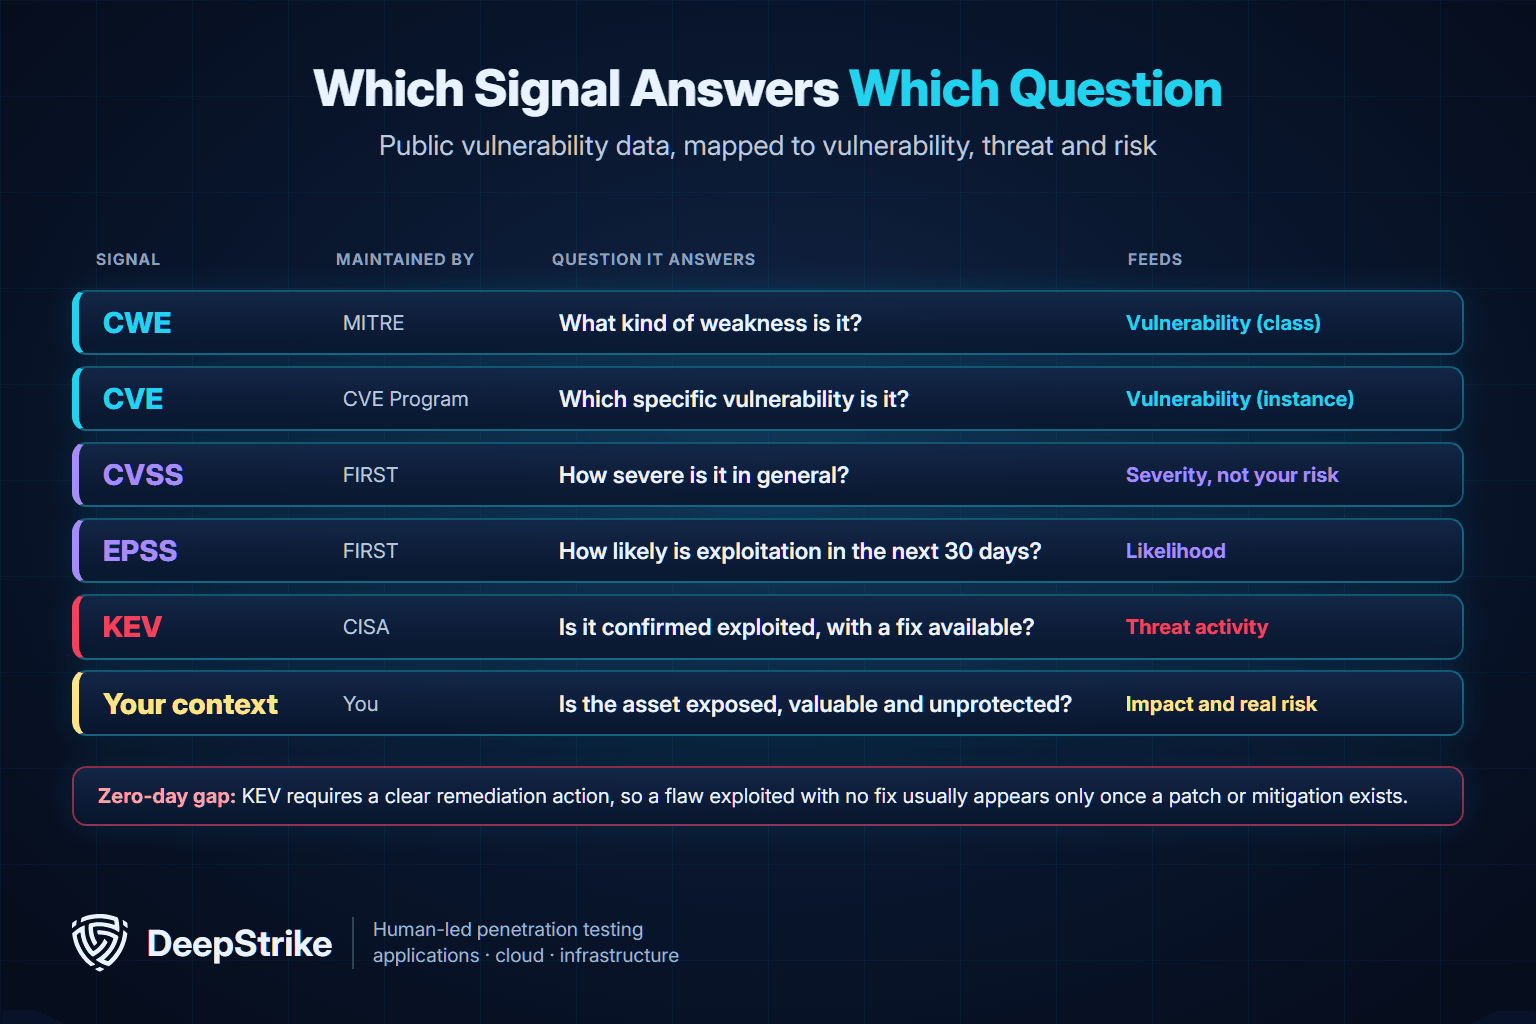
Two public catalogs keep the language precise. MITRE's Common Weakness Enumeration (CWE) lists types of weakness that "could contribute to the introduction of vulnerabilities," such as improper input validation. A CVE Record identifies one specific vulnerability in one product. CWE-79 (cross-site scripting) is a class of bug; a CVE ID points to one real instance of it.
An exploit is the specific input, code or sequence of steps that triggers a vulnerability to produce an effect the attacker wants, such as running code, escalating privileges or reading data they should not see. The NIST CSRC glossary has no standalone entry for "exploit," but its definition of a threat source describes the same idea: "the intentional exploitation of a vulnerability."
Three distinctions matter when you prioritize. A proof of concept shows that a flaw can be triggered; a weaponized exploit is reliable enough to use in real intrusions. An exploit existing is not the same as exploitation in the wild, which requires evidence of real use. And many vulnerabilities never get a working public exploit at all, which is why exploitation evidence is a stronger signal than severity alone.
NIST describes a threat as "any circumstance or event with the potential to adversely impact organizational operations," assets or individuals through an information system, by way of unauthorized access, destruction, disclosure, modification of information or denial of service. The source can be adversarial, such as a ransomware affiliate, a state-sponsored group or a malicious insider, or non-adversarial, such as an administrator's mistake or a power failure.
The practical difference is control. You can find and fix vulnerabilities, but you cannot fix a threat. You can only understand it through threat intelligence and threat modeling, then reduce what it can reach.
NIST defines risk as "a measure of the extent to which an entity is threatened by a potential circumstance or event," typically a function of the adverse impact if the event occurs and the likelihood that it will (CNSSI 4009-2022). Risk exists only where a threat, a vulnerability and an asset you care about meet. Take away any one of the three and the risk drops sharply.
That is why the same CVE can carry very different risk in two places. A critical flaw on an internet-facing server that holds customer data is urgent. The identical flaw on an isolated test machine with no sensitive data, behind controls that block the attack path, may be a scheduled fix rather than an emergency.
NIST defines an attack as "any kind of malicious activity that attempts to collect, disrupt, deny, degrade, or destroy information system resources or the information itself." An attack is a threat put into action, and it can fail. Exploiting a software vulnerability is only one route: phishing for credentials, password spraying and abusing legitimate remote access tools need no software flaw at all. Our overview of the types of cyber attacks covers the wider set.
A zero-day attack is the narrow case NIST describes as "an attack that exploits a previously unknown hardware, firmware, or software vulnerability" (NIST CSRC glossary: zero-day attack).
The table puts the five terms side by side, with the question each one answers and what each looks like in a zero-day case.
| Term | What it is | Question it answers | Who controls it | Zero-day example |
|---|---|---|---|---|
| Vulnerability | A weakness in a system, procedure, control or implementation | What is broken? | The vendor fixes it; you patch, reconfigure or compensate | A flaw in a VPN appliance that no patch addresses yet |
| Exploit | The input, code or technique that triggers the weakness | How can it be used? | Whoever builds or buys it, attacker or researcher | A working exploit chain for that flaw, held privately |
| Threat | A circumstance, event or actor with the potential to cause harm | Who or what could use it? | No one fully; you monitor it and limit exposure | A state-sponsored group targeting edge devices |
| Risk | The likelihood of harm combined with its impact | How much should we worry, here? | You, through exposure, controls and asset value | High for an internet-facing appliance in front of sensitive networks |
| Attack | Malicious activity that tries to collect, disrupt, deny, degrade or destroy | Is it happening? | The attacker starts it; you detect and contain it | The group exploiting the flaw before the vendor ships a fix |
Definitions for vulnerability, threat, risk, attack and zero-day attack follow the entries in the NIST CSRC glossary. "Exploit" has no glossary entry, so the table uses the plain meaning consistent with NIST's threat-source definition.
Public vulnerability data maps neatly onto these terms, as long as each source is used for the question it actually answers.
The third KEV criterion matters for zero-days. A flaw that is being exploited but has no fix yet does not meet the remediation threshold, so a true zero-day usually reaches KEV only once a patch or mitigation exists. KEV is the right tool for closing n-day exposure quickly; it cannot warn you about a zero-day in advance. Risk comes from combining these signals with what only you know: which assets are exposed, what data they hold and which controls stand in the way. That combination is the core of a working vulnerability management program.
Log4Shell (CVE-2021-44228), covered as a case study later in this guide, shows how the five terms separate in a real incident.
The pattern generalizes. Fix the vulnerability, but rank the work by risk, and confirm whether exposure is real instead of trusting a score alone. A penetration test answers the question no score can: whether a vulnerability can actually be exploited in your environment, and what an attacker reaches if it is.
The terms surrounding zero-days can be confusing, but they break down into a simple cause-and-effect chain. Getting this right is the first step to building a solid defense.
Applied to zero-days, the same chain looks like this:
The key difference is whether a fix exists when exploitation starts. Google and Mandiant count a zero-day as a vulnerability exploited in the wild before a patch is publicly available. Many zero-days receive a Common Vulnerabilities and Exposures (CVE) ID once they are reported, so a CVE ID alone does not mean a patch exists. For a zero-day, there is no patch, making traditional defenses like signature-based antivirus largely ineffective. This is why they are considered such a severe threat. Once a patch is released for a zero-day, it becomes a known, "n-day," or "one-day" vulnerability. However, attackers continue to exploit it against organizations that are slow to apply the update, a common problem highlighted in numerous data breach statistics.
Every zero-day follows a predictable lifecycle. It begins with the Discovery, where a threat actor or researcher finds a previously unknown flaw. The attacker then moves to Exploitation, weaponizing the vulnerability and delivering it through vectors like phishing. Eventually, the vendor learns of the issue through Disclosure and Patch Development. This window keeps shrinking: Mandiant now estimates the mean time to exploit at about -7 days, so attackers often strike before a fix ships. Even after a patch is released, the threat continues with Post-Patch Exploitation, as attackers target organizations that are slow to apply the update. This entire period represents a critical "window of exposure" where systems are at risk.
Zero-day exploits are high-value commodities traded in a sophisticated market. This market includes a White Market for responsible disclosure (bug bounties), a lucrative Gray Market where brokers sell exploits to governments for millions, and a Black Market for cybercriminals. Published broker prices, with top mobile exploit chains listed at up to $7 million, reflect their power and mean that zero-day attacks in 2026 are often highly targeted campaigns by well-funded adversaries.
Zero-Day Exploit Pricing: maximum acquisition prices published by broker Crowdfense (checked November 2026):
Treat these as advertised maximums, not proof of what any single exploit sold for. Zerodium, long the other widely cited public price list, removed its acquisition program from its website in early 2025 and appears to have closed, so its older figures should not be read as current prices.
Reducing zero-day exposure starts with finding and fixing the weaknesses you can already know about. Our web app penetration testing services can help you identify exploitable flaws in your applications so you can fix them before attackers chain them with a zero-day.
Intelligence from Google, Mandiant, and CISA reveals several critical trends defining the current landscape.
One of the most significant trends is the shift in targets. While browsers and mobile operating systems are still in the crosshairs, attackers are increasingly focusing on enterprise-specific technology. In 2024, 46% (36) of zero-days targeted enterprise products (GTIG's revised count; first reported as 44%), particularly security and networking appliances, firewalls, VPNs, and gateways from vendors like Ivanti, Cisco, and Fortinet. In 2025 that share rose to 48% (43 zero-days), and about half of those (21) hit security and networking products, with 14 affecting edge devices (Google Threat Intelligence Group, 2026).
This pivot is a direct response to improved defenses on traditional endpoints. Widespread Endpoint Detection and Response (EDR) has made attacking user workstations riskier. In response, adversaries have moved to the network edge, which often represents a blind spot for security teams as these devices typically lack EDR agents. This makes securing network vulnerabilities on edge devices a top priority.
Artificial intelligence is a true double-edged sword in the fight against zero-days. Attackers use it for hyperrealistic phishing, automated vulnerability discovery, and evasive malware. Defenders use AI for behavior-based detection, threat hunting, and automated response (SOAR), which are essential for identifying the anomalous behavior of a zero-day exploit without a pre-existing signature.
Historically the domain of nation-state espionage, zero-day exploits are now increasingly used as the entry point for high-impact ransomware attacks. In 2025, Google tracked nine zero-days exploited by likely or confirmed financially motivated groups, including two used in operations that led to ransomware deployment. Threat actors use a zero-day to gain initial access, move silently through the network, steal data, and then deploy ransomware. This "double extortion" tactic maximizes their leverage and poses a direct threat to business operations.
Case studies make the threat tangible. Analyzing past and present attacks shows how attacker TTPs (Tactics, Techniques, and Procedures) have evolved.

While you can’t stop a zero-day vulnerability from existing, you can build a resilient defense that detects and contains an attack before it causes catastrophic damage, then validate those layers with penetration testing.
Signatures usually miss a zero-day's first use, because nobody has seen it yet. Look for the behavior of an attack in progress.
Prevention focuses on reducing your attack surface and making it harder for an attacker to succeed.
When a zero-day attack hits, a well-rehearsed plan is the difference between controlled response and chaos.
Step-by-Step Zero-Day Incident Response Checklist:

Misconceptions about zero-days can lead to a false sense of security or a feeling of helplessness. Here are the facts.
Firewalls and antivirus remain baseline controls, but they are not enough on their own. The 2026 threat landscape, defined by exploitation that often begins before a patch exists and by well-funded adversaries, demands a fundamental shift in mindset from reactive compliance to proactive resilience.
Zero-day exploits are a core component of the modern cybercrime ecosystem. Winning against this threat isn't about achieving perfect, impenetrable security. It's about building a system that can withstand an attack, detect it quickly, and respond effectively. It requires integrating advanced technology, adopting a modern architectural framework like Zero Trust, and hardening your human defenses.
The clock is always ticking. The question is no longer if a zero-day will target your systems, but when. Your readiness will determine the outcome.
What is a simple definition of a zero-day exploit?
A zero-day exploit is the code or technique an attacker uses to abuse a vulnerability the vendor does not know about or has not yet patched. Using it against a target is a zero-day attack. Because no fix exists yet, early attacks often succeed.
What is a real-world example of a zero-day attack?
A famous example is the Stuxnet worm (2010), which used four different zero-day vulnerabilities in Windows to physically damage Iran's nuclear centrifuges. Log4Shell (2021) is a borderline case: the earliest known activity, on December 1, 2021, looked like testing of the proof of concept, and widespread attacks began only after public disclosure on December 9.
How are zero-day exploits discovered?
Zero-day exploits are discovered in several ways. Security researchers and threat actors can find them through methodical processes like fuzzing (bombarding a program with invalid data), reverse engineering software, or performing source code analysis. Sometimes, they are found by accident during a routine penetration test.
How do you protect against zero-day attacks?
Protection requires a multilayered strategy. Key defenses include:
What is the difference between a zero-day exploit and a known vulnerability?
A zero-day exploit targets a vulnerability that is exploited before the vendor has released a fix, whether or not the vendor already knows about it. A known (n-day) vulnerability already has a patch or vendor fix available, and attackers exploit it in systems that have not applied it. Both types usually carry a CVE ID, so a CVE number alone does not mean a patch exists. Zero-days work even against fully patched systems because no fix exists yet.
Why are zero-day attacks so dangerous?
They are dangerous because of the element of surprise (no pre-existing defenses), their high success rate against initial targets, and the significant time gap (window of vulnerability) between the first exploit and when a patch is widely deployed.
How much is a zero-day exploit worth?
The price varies dramatically based on the target. Exploit broker Crowdfense lists up to $5-7 million for an iPhone zero-click full chain and $2-3 million for a one-click Google Chrome full chain. The high prices are primarily paid by government agencies and their contractors.
What is the difference between a vulnerability, an exploit and a threat?
A vulnerability is a weakness in a system, procedure, control or implementation. An exploit is the code or technique that takes advantage of that weakness. A threat is the person, group or event with the potential to cause harm by using it. Risk combines how likely that harm is with how much damage it would do, and an attack is the actual attempt.
Is a high CVSS score the same as high risk?
No. A CVSS Base score rates a vulnerability's severity from its intrinsic characteristics and assumes a reasonable worst case. Risk also depends on whether the flaw is being exploited, which EPSS estimates and CISA's KEV catalog confirms, and on your environment: whether the asset is exposed, what data it holds and which controls block the attack path.
Got questions? Need expert insights on zero-day defenses? Reach out, always happy to chat.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
