May 12, 2025
Updated: November 12, 2026
A data-driven look at password reuse, credential theft, breach costs, and the transition toward passwordless authentication in 2026.

Mohammed Khalil
Despite decades of security awareness, passwords remain a weak link in the global cybersecurity chain. This report analyzes recent password statistics covering 2024 through 2026 to illustrate the scale of the problem. We face a paradox: while authentication technology has advanced biometrics, hardware keys, passkeys, human password habits have stagnated. Users are overwhelmed by the number of accounts they maintain, leading to risky shortcuts like reusing simple passwords. Attackers are exploiting this at a massive scale, armed with billions of stolen credentials and ever faster cracking tools.
We’ll explore key findings such as the prevalence of weak passwords and reuse, the eruption of credential stuffing attacks, the impact of emerging threats like infostealer malware, and the changing economics of breaches. The data reveals a password crisis driven not by lack of technology, but by human factors, memory limits, fatigue colliding with the exponential offensive capabilities available to cybercriminals. Finally, we discuss how organizations are responding from updated password policies e.g. NIST SP 800-63B-4 to the adoption of multi factor and passwordless authentication marking the transition to a post password era.
Within broader cybersecurity statistics, password statistics refer to aggregate data and metrics that shed light on how people create, use, and manage passwords and how attackers abuse them. These stats encompass things like common password choices, password-strength distribution, reuse rates, and credential exposure. In essence, password statistics measure the real-world state of password hygiene and the resulting security risks.
To illustrate, think of passwords as the keys to hundreds of locks on your online accounts. Password statistics examine how often people are using the same key for many locks, how simple those keys are like a blank key that fits anything, and how many of those keys have been lost or copied by thieves. For example, if we learn that about two in three people reuse passwords across sites (65% in the 2019 Google/Harris Poll), and that 123456 still tops breach-derived password lists, we get a quantitative picture of why breaches occur so frequently via weak or stolen credentials. These numbers help security teams and policymakers craft better defenses such as enforcing stronger password rules, detecting reuse, or promoting multi factor authentication based on actual user behavior and threat patterns, rather than theory.
In practical terms, password stats serve as a report card on the state of authentication security. They highlight if awareness efforts are working, are fewer people using password123?, show emerging threats e.g. spike in credential stuffing attacks per month, and inform where to focus mitigations. For instance, seeing that only 24% of respondents in the 2019 Google/Harris Poll used a password manager (see also this roundup of password statistics) tells us convenience is still a barrier, and alternative solutions like passkeys or single sign on may be needed. Overall, these statistics translate the abstract concept of password risk into tangible data points that organizations can act upon.
To understand the 2026 landscape, it’s useful to compare the latest editions of key reports with the previous ones:
| Metric | Earlier data | Latest data | Source |
|---|---|---|---|
| Password reuse (different measures) | Self-reported: 65% reuse, 13% one password everywhere (Google/Harris, 2019 survey) | Observed in exposed accounts: 65% consumer, 42% corporate (SpyCloud 2026) | Google/Harris; SpyCloud |
| Most common password | 123456 | 123456 again #1 in 2025; admin #2 | NordPass |
| Stolen passwords analyzed | 1B+ malware-stolen passwords (2024 data) | 6B+ stolen passwords (2025 data) | Specops Breached Password Reports |
| Recaptured identity records | 53.3B (2025 report, +22%) | 65.7B (2026 report, +23%) | SpyCloud |
| Infostealer credentials | 548M from 18M+ logs (2024) | 642.4M from 13.2M infections (2025) | SpyCloud |
| Workforce MFA adoption | 66% (Jan 2024) | 70% (Jan 2025) | Okta |
| Passkey share of sign-ins | 26% (2025 index) | 36% (2026 index) | FIDO Passkey Index |
| Average breach cost, global | $4.88M (2024); $4.44M (2025) | $4.99M (2026, record) | IBM |
| Credential abuse as initial access vector | 22%, #1 vector (DBIR 2025) | 13% initial, 39% at any stage (DBIR 2026) | Verizon DBIR |
The data above paints a mixed picture. Reuse remains widespread in both survey and breach data, and the most common passwords are still laughably weak, with 123456 and its numeric cousins as popular as ever. Password complexity rules have not stopped users from choosing basic patterns, keeping the door open for credential stuffing attacks.
Meanwhile, attacker capabilities and exposure of credentials are accelerating. SpyCloud recaptured 3.1 billion exposed passwords in 2024, a 125% increase on the previous year, and in November 2025 Have I Been Pwned loaded a Synthient dataset containing about 1.96 billion unique email addresses and 1.3 billion unique passwords, 625 million of them never seen before. Automated attacks are correspondingly rampant: Akamai's figure of 193 billion credential stuffing attacks in 2020 showed this is a continuous, worldwide onslaught, and Microsoft reports identity-based attacks rose 32% in the first half of 2025 as attackers target websites, APIs and mobile logins.
On the defensive side, adoption of multi factor authentication MFA continues to grow, reaching 70% of workforce users in Okta's data, up from 66% a year earlier. The net effect is that while more logins are protected by a second factor, attackers are concentrating on the weakest links including the millions of accounts that still rely on just a password, especially in the consumer space and smaller orgs. Fully passwordless logins are no longer rare in consumer services, where passkeys now carry over a third of sign-ins at the services in the FIDO Passkey Index, but only 28% of organizations surveyed by FIDO in 2026 have gone fully passwordless for their workforce.
In summary, the global overview reveals stubborn human behavior combined with ramped up attacker aggression. Incremental improvements in password hygiene are not yet enough to counter the explosion in credential theft and cracking power. This sets the stage for why organizations must rethink password policies and invest in stronger authentication layers to mitigate these trends.
Poor password practices have a cascade of negative impacts on security outcomes. Weak and reused passwords don’t just put individual accounts at risk, they actively contribute to large-scale breaches, fraud, and organizational costs. Below we break down several key risk indicators and their estimated impact:
| Indicator | Impact on Security | Trend | Notes |
|---|---|---|---|
| Password reuse (65% of respondents in the 2019 Google/Harris Poll) | Fuels credential stuffing: widespread reuse means one breach can become many breaches, as a single leaked password often unlocks other accounts. | Still pervasive (survey and breach data; different measures) | SpyCloud's 2026 report finds reuse in 65% of exposed consumer accounts and 42% of exposed corporate accounts. |
| Weak/simple credentials e.g. 123456 | Enables instant or very fast compromise via guessing. Many attacks don’t even need to crack anything: attackers simply log in with known weak creds from leaked lists. | → No improvement | 123456 topped NordPass's 2025 list again. In the 2025 DBIR, about 88% of Basic Web Application Attacks breaches involved stolen credentials. Default passwords like admin persist in IoT/enterprise gear. |
| Credential stuffing and spraying success | Directly causes account takeovers ATO and data breaches. Credential abuse was the #1 initial access vector in the 2025 DBIR (22%); in the 2026 DBIR it was 13% as an initial vector but present at some stage in 39% of breaches. | ↑ Growing attacker ROI | Akamai saw 193B credential stuffing attacks in 2020. Microsoft says more than 97% of identity attacks are password attacks. The 2024 Snowflake-related attacks showed how stolen passwords on accounts without MFA can lead to major data exfiltration. |
| Help desk load password resets | Significant operational cost and security risk. Frequent resets also degrade user productivity during lockouts. | → Consistently high | 35% of organizations that deployed passkeys report fewer password reset tickets (FIDO, 2026). Users frustrated by strict policies may choose weaker passwords. |
| Incident severity when creds used | Breaches involving stolen credentials tend to be slow to detect. IBM found they took 292 days to identify and contain in 2024 (the longest vector that year) and 246 days in 2025, still above the 241-day global mean. Attackers with valid credentials blend in as legitimate users. | ↓ 292 days (2024) → 246 days (2025) | Breaches starting with compromised credentials averaged $4.67M in IBM's 2025 report, above the $4.44M global average. Highlights need for monitoring of login anomalies. |
In essence, password reuse and weakness act as force multipliers for attackers. A single compromised password can be tried against dozens of sites, and given the reuse statistics, there is a good chance of a successful login. This is why credential stuffing patterns are so problematic: billions of stolen credentials allow attackers to scale account-takeover attempts. Penetration testing can validate whether compromised credentials enable authentication bypass, privilege escalation, unauthorized access, or lateral movement. Organizations can otherwise suffer breaches in which the attacker simply logs in successfully, without requiring malware or a software exploit.
From an economic standpoint, the failure of password security is extremely costly. Data breaches stemming from compromised credentials averaged $4.67M in IBM's 2025 Cost of a Data Breach report, and in sectors like finance or healthcare the costs run far higher due to regulatory fines and data sensitivity. But even outside of headline making breaches, companies bleed money in the day to day friction caused by passwords, the help desk overhead, lost productivity, and user frustration. Self-service password reset analyses show how much IT time manual resets consume, which is essentially a tax on poor authentication practices.
Finally, weak and reused passwords undermine investments in other security controls. You can have firewalls, intrusion detection, etc., but if an admin’s password is Password2023 and it was leaked in a breach, an attacker can simply walk in through the front door. It’s telling that credential abuse was the top initial access vector in 22% of breaches in the 2025 Verizon DBIR, no exploit required, and that stolen credentials still featured at some stage in 39% of breaches in the 2026 DBIR. In summary, the persistence of weak credentials keeps the floodgates open for threat actors, translating to higher breach likelihood, greater blast radius through lateral movement or reuse across systems, and costly aftermath in both dollars and reputational damage.
Digging into the specifics of how users create passwords in 2025 and 2026 reveals several predictable and risky patterns. Despite increased awareness, many people still choose passwords that are easy to remember which often means easy to crack. Here are some prevalent behaviors and trends:
In summary, user behavior in password creation hasn’t fundamentally changed in the last decade. People choose convenience and familiarity over entropy. Attackers know the collective psyche of users that we like sequences, names, pop culture references, and predictable substitutions. The 2025 and 2026 data from breach analyses by NordPass, Specops, SpyCloud, etc. confirms that the content of passwords reflects human psychology more than any improved security mindset. The myth that younger digital native users would inherently use better passwords has been dispelled, they might not use 123456 as often, but they’ll use skibidi or Pokemon or taylorSwift, which are just as guessable with targeted dictionaries. Until we remove the onus from users through tech like password managers or moving beyond passwords, these common patterns will persist, and attackers will continue to reap the benefits.
The password problem does not affect all industries equally, certain sectors face higher exposure and costs from weak or stolen credentials. Here’s a look at how password related risks vary across industries in 2025 and 2026:
In all industries, one pattern stands out: smaller organizations are at higher relative risk from poor passwords. Large enterprises in any sector now typically enforce stronger controls MFA, SSO with SAML, etc. so even if a password is stolen, it’s not the single point of failure. However, mid-sized and small businesses from a local medical clinic to a regional retail chain often rely on passwords alone, and many SMBs still do not implement MFA. Attackers know this and have shifted focus accordingly. The 2025 DBIR found ransomware in 88% of SMB breaches, compared with 39% at larger organizations. Cybercriminals target the path of least resistance.
Overall, the concentration of risk is higher in industries dealing with consumer accounts retail, finance and those with valuable data healthcare, govt. But any organization that hasn’t adapted its password requirements and protections is likely to be compromised eventually via an account breach. The data shows it’s not a matter of if but when, given the millions of stolen credentials in circulation and automated attack bots constantly probing.
While this analysis is global, there are some regional nuances in password security and related regulations worth noting:
In summary, while the human weaknesses in passwords are universal, the degree of mitigation MFA, policy enforcement and consequences regulatory fines, etc. differ by region. Developed regions with strict laws and strong customer authentication rules are pushing organizations to up their game, which in turn slowly improves user habits or at least forces users into better security through MFA. Regions without such pressures see the raw effects of password insecurity more plainly, more frequent mass account compromises and local cybercrime leveraging credentials. But the interconnected nature of the internet means a password leaked in one country can be used to attack a service in another. The fight against password related threats is truly global, and progress in one region helps others. For instance, when a large platform like Microsoft globally enforces a ban on common passwords, everyone benefits.
The past year has seen several significant credential exposure events and recurring patterns that illustrate how passwords are being compromised at scale:
In summary, the major patterns of credential exposure in 2024 to 2026 are about scale and aggregation. Whether it’s billions of creds compiled from past breaches, millions siphoned quietly by malware, or credentials indirectly exposed via third parties, the pool of compromised passwords keeps growing. According to SpyCloud, its database of recovered identity records grew 22% to 53.3 billion records in its 2025 report and another 23% to 65.7 billion in its 2026 report. That’s roughly eight records for every person on the planet. Of course, many are duplicates or old, but the scale means attackers almost always have some credential data to try when targeting an organization or user. We’ve effectively lost the arms race of keeping passwords secret, too many have leaked. This underpins the push toward new paradigms like zero trust assumptions, verify explicitly even if credentials are correct, and ultimately, passwordless auth. Until those are fully in place, organizations must operate under the assumption that many of their user passwords are already known to attackers, and defense must be built accordingly with monitoring, MFA, anomaly detection on logins, etc.
MFA statistics in 2026 tell two stories. Adoption is still incomplete: 70% of workforce users at Okta customers used MFA in January 2025, and only 41% of Microsoft Entra ID monthly active users at enterprise customers signed in with MFA in 2024. Where MFA is turned on, it works: a Microsoft study found it lowered the risk of account compromise by 99.22%. The weak spot attackers now target is phishable MFA, through push fatigue, adversary-in-the-middle (AiTM) phishing and stolen session tokens.
The figures below come from different populations and years, so compare each one only with its own source. The table summarizes them, and the sections after it explain what each one measures.
| Metric | Figure | Scope and date | Source |
|---|---|---|---|
| Workforce MFA adoption | 70% (66% a year earlier) | Okta customers, January 2025 | Okta Secure Sign-in Trends Report 2025 |
| Entra ID users signing in with MFA | 41% (0.7% in 2014) | Microsoft enterprise customers, monthly active users, 2024 | Microsoft Digital Defense Report 2024 |
| MFA adoption by industry | 87% technology; 52% retail; 42% transportation and warehousing | Okta customers, January 2025 | Okta Secure Sign-in Trends Report 2025 |
| Phishing-resistant authenticators | 14.0% of users (8.6% a year earlier) | Okta customers, January 2025 | Okta Secure Sign-in Trends Report 2025 |
| Reduction in compromise risk with MFA | 99.22% overall; 98.56% with leaked credentials | Microsoft Entra ID accounts, study published May 2023 | Meyer et al., Microsoft |
| Effect of security defaults | 80% fewer compromises | Entra tenants using security defaults vs not, 2024 | Microsoft Digital Defense Report 2024 |
| Targeted attacks blocked | 76% with SMS codes; 90% with on-device prompts | Google accounts, year-long study published May 2019 | Google, NYU and UC San Diego |
| MFA fatigue attempts | About 6,000 per day | Microsoft, by the end of June 2023 | Microsoft Digital Defense Report 2023 |
| AiTM phishing attacks | Up 146% in a year | Microsoft, year covered by the 2024 report | Microsoft Digital Defense Report 2024 |
| Token theft incidents | About 39,000 per day | Microsoft detections, 2024 | Microsoft Digital Defense Report 2024 |
Sources for the table: Okta's Secure Sign-in Trends Report 2025, the Microsoft Digital Defense Report 2024, the Microsoft Digital Defense Report 2023, the Microsoft MFA effectiveness study and Google's account hijacking research.
Microsoft has tracked MFA use on its identity platform since it first offered MFA in 2014, when 0.7% of monthly active users signed in with it. By 2024, the share of Entra ID monthly active users signing in with MFA had reached 41% among Microsoft enterprise customers, according to the Microsoft Digital Defense Report 2024. Defaults make a measurable difference: Microsoft says tenants that use security defaults, which turn MFA on and switch off legacy authentication, experience 80% fewer compromises than tenants that don't. That is why Microsoft began requiring MFA for the Azure portal, Entra admin center and Intune admin center in October 2024, with command-line and infrastructure-as-code tools following from early 2025.
Okta's customer data gives a second view. Its Secure Sign-in Trends Report 2025 puts workforce MFA adoption at 70% in January 2025, but the spread between sectors and regions is wide:
Read together, the two datasets say the same thing: MFA is close to universal where a platform makes it mandatory and well short of it where it is optional. The accounts that still sign in with a password alone are the ones exposed to password spraying and the credential stuffing described earlier in this report.
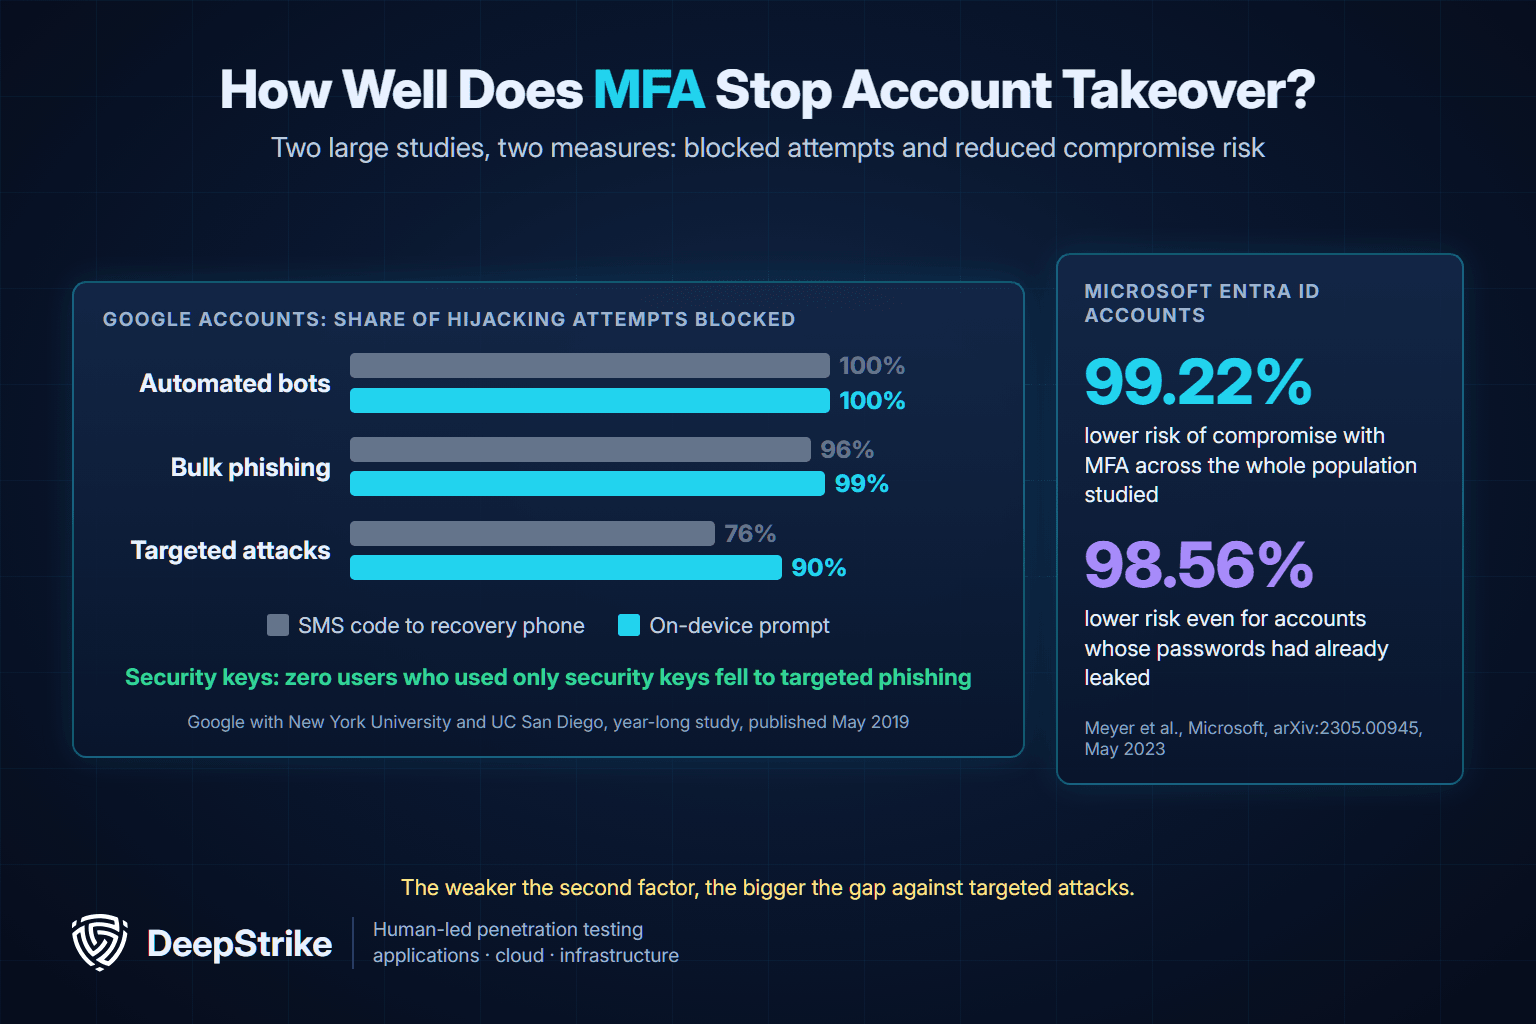
The most cited MFA figure comes from a 2023 Microsoft study of Entra ID accounts by Lucas Augusto Meyer, Alex Weinert and colleagues. Using a large set of Microsoft Entra ID (then Azure AD) accounts that showed suspicious activity, the researchers found MFA lowered the risk of compromise by 99.22% across the whole population and by 98.56% for accounts whose credentials had already leaked. More than 99.99% of MFA-enabled accounts stayed secure during the study period, and authenticator apps performed better than SMS.
Google measured something different: how often each type of challenge blocked a hijacking attempt. In a year-long study with New York University and the University of California, San Diego, published in May 2019, an SMS code sent to a recovery phone blocked 100% of automated bots, 96% of bulk phishing attacks and 76% of targeted attacks. On-device prompts blocked 100%, 99% and 90%. No user who relied only on security keys fell victim to targeted phishing during the study.
The pattern matters more than any single number. Every form of MFA stops nearly all automated, credential-based attacks, but the gap widens against a skilled, targeted attacker, and only security keys closed it completely in Google's data. That is the case for phishing-resistant authenticators such as passkeys on high-value accounts.
Attacks on MFA itself are still a small slice of identity attacks. In the Microsoft Digital Defense Report 2024, more than 99% of the 600 million identity attacks Microsoft sees per day are password-based, and SIM swapping, MFA fatigue and AiTM attacks combined account for less than 1%. That slice is growing, though, and it is aimed at the organizations that have already deployed MFA:
The common thread is that each bypass defeats a factor the user can be tricked into handing over or approving. None of them works against a FIDO2 credential that is bound to the real site's domain, which is the core of CISA's guidance.
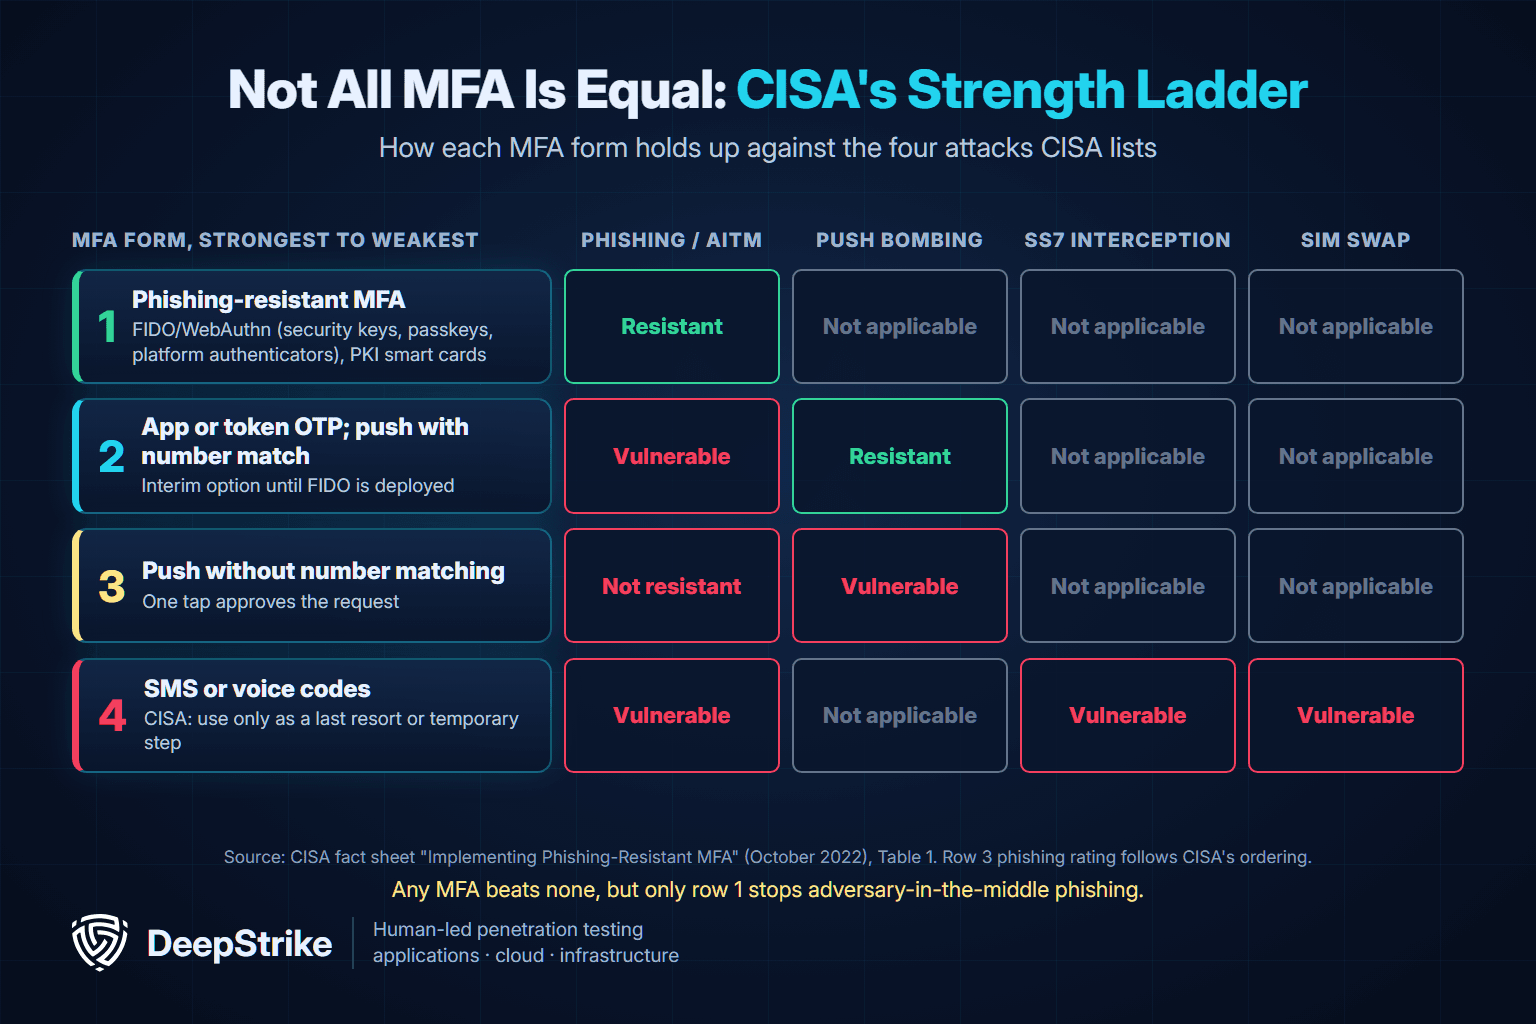
CISA's Implementing Phishing-Resistant MFA fact sheet (October 2022) ranks MFA forms from strongest to weakest by how they hold up against phishing, push bombing, SS7 interception and SIM swapping. CISA calls phishing-resistant MFA the gold standard, and the U.S. Office of Management and Budget requires federal agencies to adopt it. The ranking runs:
CISA's public More than a Password campaign makes the same point for everyone else: any MFA is better than none, FIDO/WebAuthn is the only widely available phishing-resistant option, and number matching is the fallback where FIDO isn't possible yet. CISA also recommends that organizations list the systems that can't support MFA and either upgrade or replace them, escalating that risk to senior leadership in the meantime.
For security teams, these MFA statistics come down to three checks. First, measure coverage per application and per sign-in path, not per user, because legacy protocols, VPNs and service accounts are where single-factor access survives. Second, move administrators and other high-value users to FIDO2 security keys or passkeys first, and turn on number matching everywhere else. Third, test the result: an authorized assessment from our penetration testing services can check whether MFA is enforced on every entry point and whether fallback or recovery methods let an attacker around it.
Several emerging trends in 2025 and 2026 are shaping how organizations think about password security and authentication:
In sum, the trends of 2025 and 2026 point to a gradual but definitive shift away from treating passwords as the sole secret that protects us. The ecosystem is moving toward layered defenses, user friendly but secure alternatives biometrics, passkeys, and smarter detection of attacks. We are likely witnessing the last decade where passwords alone are a primary authentication method on the internet. The transition period, however, is fraught with challenges during which attackers are exploiting both the legacy weaknesses and the gaps as new tech rolls out. The organizations that stay ahead of these trends implementing passwordless where possible, tightening password policies and monitoring, and deploying phishing resistant MFA will significantly reduce their risk of being the next headline breach. Those that don’t will continue to be low hanging fruit in the vast credential theft orchard that cybercriminals harvest.
The data and trends discussed aren’t just trivia they carry important implications for how organizations and individuals should approach security:
In essence, these statistics collectively argue that the status quo of passwords cannot be our future. They guide us to specific actions: update policies, ban Summer2023 etc., deploy MFA everywhere now, plan for passwordless, educate users on using tools not tricks, and constantly watch for credential abuse. Organizations that internalize these lessons will significantly reduce their risk profile. Those that don’t will continue to be over represented in next year’s breach reports as victims of stolen and weak credentials. The numbers really do speak loudly, it's on security leaders to listen and adapt accordingly.
To improve security in light of these findings, organizations and users should adopt a multi pronged strategy. Below are best practices that directly address the weaknesses and attack patterns highlighted by the statistics:
1. Enforce Strong, Unique Passwords with Screening: Implement technical controls so that users must choose passwords that are hard to guess and never used elsewhere. Specifically, enable blocklists of common passwords and breached passwords. Leverage services like Have I Been Pwned’s API to reject passwords known to be compromised. This one step forces users away from 123456, password, etc. Allow and encourage passphrases for example, let users set long phrases like sunshine coffee blue elephant spaces included if possible. The added length exponentially increases cracking difficulty, as the Hive Systems password table shows: each extra character multiplies the work an attacker must do. Meanwhile, discourage the old practice of arbitrary complexity: no need to mandate symbols if the password is long and screened against weak choices. Also, do not enforce routine password expirations instead, require change only on evidence of compromise. This aligns with NIST SP 800-63B-4 and avoids the predictable rotation issues. Many organizations have already updated group policies accordingly. In short, systematize good password choices so users don’t slip into bad habits, don’t rely purely on the user honor system.
2. Implement Universal Multi Factor Authentication: As stressed earlier, MFA should be enabled for all accounts and applications possible. This includes internal admin interfaces, VPNs, email, privileged accounts, and customer facing logins where feasible. Opt for the most secure form factor users can handle: TOTP apps or push notifications at a minimum, or physical security keys for high risk users. Yes, SMS is better than nothing, but given the vulnerabilities SIM swaps, etc., try to migrate away from SMS where possible. Educate users about MFA fatigue for instance, teach employees that if they get an unexpected MFA prompt at 2 AM, it could be an attack and they should deny it and report it. Some companies are configuring MFA apps to limit automatic prompt spam e.g. Microsoft added number matching to Azure MFA to combat blind approval. Furthermore, consider using adaptive MFA only prompts for MFA when a login is deemed suspicious by the risk engine. This can improve user acceptance because they aren’t prompted every single time for example, no prompt when on a corporate network and known device, but prompt when off network or new device. This balance maintains security while reducing annoyance, which helps keep MFA enabled widely. Ultimately, MFA is your safety net coupled with strong passwords, it forms a two layer defense where if one fails, the other stops the adversary.
3. Deploy Password Managers or SSO for Users: To alleviate the cognitive burden that leads to reuse, organizations should provide and encourage password managers for staff. Enterprise password managers or browser based managers with enterprise policies can ensure employees have unique, complex passwords without memorization. Many companies do training on the corporate password manager and even make it default installed on company devices. For customers or general users, promoting password manager use in your security guidance is also beneficial. Another approach for organizations is to reduce the number of passwords in use via Single Sign On SSO solutions. By integrating apps into one SSO portal with one strong credential or federated login, you remove the need for users to juggle dozens of passwords. Less passwords = less chance of reuse and less weak link accounts. The goal is to move toward an identity centric model where a few central credentials protected heavily by MFA and monitoring replace many scattered ones. Most organizations already use SSO for at least some resources, and that’s a trend to continue. By using SSO, you also position yourself better for a passwordless future as those central identity providers are the first to adopt passkeys, etc., which then seamlessly flow to all connected apps. Remember, user convenience and security are not at odds here password managers and SSO improve both by making it easier to be secure than to be insecure.
4. Strengthen Detection of Credential Attacks: Given the volume of credential stuffing and brute force attempts, invest in tools that can detect and block these in real time. Web application firewalls WAFs and bot management services are key if you run public facing logins they can spot when someone is attempting thousands of logins and throttle or block them. Use techniques like rate limiting, IP reputation, device fingerprinting to distinguish legitimate users from botnets. Also, monitor for account lockout trends a spike in locked accounts might indicate a password spraying campaign where attackers try one password like Password123! across many accounts. Internally, implement user behavior analytics: for example, an alert if an employee account suddenly logs in from an IP in Russia after months of only US logins, or if an account accesses an unusual number of files potential data theft after takeover. Many SIEM and SOAR solutions now incorporate such analytics, often branded as UEBA User Entity Behavior Analytics. Because stolen credentials can be used by attackers while impersonating valid users, these behavioral tells are sometimes the only way to catch them. Regularly review login success/failure logs, perhaps weekly reports of top 10 IPs by login failures, etc. It’s not the most glamorous task, but it can reveal an ongoing slow burn attack that might otherwise go unnoticed. In essence, assume credentials will be tried and sometimes used successfully by bad actors, and have a means to catch that activity quickly. Pair this monitoring with continuous penetration testing that checks whether stolen or weak credentials, missing MFA and weak lockout controls would let an attacker in, so you can close those gaps before they are abused.
5. Have Incident Response Plans for Credential Compromises: Not every organization had a playbook for what if an employee’s password is discovered in a breach or what if hundreds of customer accounts get taken over in a stuffing attack. Today, you absolutely need those plans. For employees, define a process: use services to receive breach notifications, if any employee’s corporate email appears in a breach dataset, force a password reset and investigate if that account showed anomalous access. Also, be ready to cycle all credentials if a major compromise happens e.g. if your Active Directory got dumped, do you have a rapid way to enforce org wide password reset or disablement?. For customer accounts, implement protections like account lockout or step up verification after a certain number of failed attempts with careful balance to avoid enabling DoS via lockout abuse. Also, consider enabling MFA for customers or at least providing it as an opt-in. Some will use it, and it will reduce ATO fraud for those who do. If an ATO incident occurs, say 1000 customer accounts brute forced successfully, have a plan: detect the anomalous access, trigger password resets for those accounts, notify the users, and possibly freeze any suspicious transactions. IBM’s finding that stolen-credential breaches took 292 days to identify and contain in 2024 (246 days in 2025) warns us that if you don’t respond swiftly, the cost and damage escalates significantly. Drilling incident response for credential theft scenarios even tabletop exercises can reveal gaps. For instance, do you have contact info to rapidly reach consumers in case you need to secure their accounts? Do you have a penetration testing program that validates authentication controls so you know whether an attacker could move laterally with a stolen password?. Covering these bases in advance is crucial, as credential incidents are not a matter of if but when.
6. Transition Toward Passwordless Where Possible: Finally, start planning the phased rollout of passwordless authentication in your ecosystem. For the workforce, this might mean rolling out hardware security keys or platform authenticators Windows Hello for Business, etc. and allowing users to enroll them as primary auth. Vendors are moving this way: Microsoft made new consumer accounts passwordless by default in 2025, and identity providers like Okta offer passwordless options for workforce apps. Even if you can’t eliminate passwords entirely for all systems, legacy apps are often the blocker, you can significantly reduce their use. Less password use = less password compromise risk. For customer facing implementations, consider offering passkey login for example, users scanning a QR or using FaceID instead of typing a password as browsers have made it simple. The stats about hundreds of millions of passkeys being created by users of Google, Amazon, etc. shows that once available, a sizable chunk of users will opt in for convenience. It’s a win-win situation because it’s both easier and more secure. Keep an eye on usability ensure fallback options are secure if someone loses their device, how to recover account?. But the quicker you gain experience with passwordless tech, the better positioned you’ll be as it becomes the norm. Consider running a pilot: maybe a department in your company goes passwordless for their VPN using certificates or FIDO, and gather feedback. The password statistics clearly indicate that human managed passwords are a losing battle, investing in solutions that remove humans from the loop passwordless is ultimately the most robust fix.
By implementing these best practices, organizations address the root causes illuminated by the statistics: reliance on human memory solved by managers and passkeys, exploitation of reused or weak passwords solved by screening and MFA, and slow detection solved by vigilant monitoring and response. Each practice above is essentially a direct answer to a data point we’ve discussed. For instance, we know roughly two in three people reuse passwords, so we institute unique password requirements plus tools to manage them, we know billions of attacks happen, so we deploy anti automation defenses. Adopting these measures will significantly reduce the risk of account compromise and breaches, moving the security posture from reactive dealing with incidents after they happen to proactive making those incidents much less likely in the first place. Ultimately, the goal is to break the Password123 cycle that has plagued security for too long, and these steps are the way forward.
Extremely common. In a Google/Harris Poll of 3,000 U.S. adults (fielded December 2018, published February 2019), 52% reused one password across multiple accounts and another 13% used the same password for every account, meaning about 65% reuse; only 35% used unique passwords. Measuring something different, SpyCloud's 2026 Identity Exposure Report found password reuse in 65% of exposed consumer accounts and 42% of exposed corporate accounts in its breach data, so work credentials are no exception. This widespread reuse means if any one website is breached, those credentials can unlock accounts elsewhere. It’s a major driver of credential stuffing attacks.
Yes in practice, password managers significantly improve security for most users. A password manager creates and stores unique, long, random passwords for each account, something humans won’t reliably do on their own. Surveys show only about a quarter to a third of people use these tools (24% in a 2019 Google/Harris Poll, 34% in Bitwarden's 2022 global survey), but those who do avoid reuse tend to have stronger passwords. While there’s a theoretical risk if a manager itself is compromised, reputable managers use strong encryption so that even if their data is stolen, the passwords remain encrypted. The likelihood of being hacked due to a reused or weak password is far higher than the chance of a password manager breach. NIST SP 800-63B-4 even requires verifiers to allow password managers and autofill. So for most users, a manager is absolutely safer. It's a way to outsource the memory and ensure every account has a unique key. Just make sure to use a strong master password for the manager and enable 2FA on it.
It’s true that if you have robust multi factor authentication on an account, the password is no longer the sole barrier. However, strong passwords still matter for a few reasons. First, many accounts, especially consumer accounts, do not have MFA enabled, so they rely entirely on the password. Second, even with MFA, passwords can be leveraged in other ways like password spraying to find accounts with no MFA, or using the password to bypass MFA via less secure backup channels. Also, a weak password could be brute forced or guessed, giving an attacker the first factor and potentially more opportunities to attempt social engineering the second factor. Ideally, you want defense in depth: a strong password and MFA. That said, if one had to choose, enabling MFA on a weak password account provides more benefit than having a strong password with no MFA. But there’s no need to choose to do both. One scenario to note: in corporate environments, if an attacker gets a weak admin password that isn’t MFA protected, maybe on a legacy system, they could cause damage. So continuing to enforce decent password practices alongside MFA is important. In summary, MFA greatly reduces reliance on password strength, but strong passwords are still a best practice as part of an overall secure posture.
The best approach is to use a passphrase, a sequence of random words or a sentence that is 15+ characters long but easy for you to remember; 15 characters is also NIST's minimum for passwords used without MFA. For example, amulet honey battery river or a nonsensical phrase like CorrectHorseBatteryStaple famous from an XKCD comic. These are strong because of length and randomness, yet easier to recall than a short complex string like 5%ftY2. Another tip is to add a memorable twist that isn’t obvious e.g. an inside joke or a pattern only you know. But avoid common quotes or phrases from literature or pop culture attackers do use lists of those. Also avoid simple modifications of a common base like Password >Password1 >Password2, that’s predictable. A passphrase of four or five truly random, unrelated words is far beyond practical brute-force reach with today’s hardware and doesn’t require special characters to be strong. One should not rely on personal data, no names, birthdays, etc. those are easily guessed via social engineering dictionaries. If memorability is tough even with passphrases, that’s where a password manager comes in. You only have to remember one master passphrase, and let it generate gibberish for everything else. So in summary: use length over complexity, a random phrase that isn’t published anywhere, etc. that’s the sweet spot between security and usability.
It depends on the password and on how the site stored it. Using rigs of multiple GPUs, attackers can attempt billions of guesses per second against weak, fast hashes like MD5 or SHA-1, where any short password falls almost immediately. Against a strong, slow hash the picture changes: Hive Systems' 2026 Password Table, which assumes 16 RTX 5090 GPUs attacking bcrypt (work factor 10) and a randomly generated password, puts an 8-character lowercase-only password at about 2 weeks and an 8-character password mixing numbers, upper and lowercase letters and symbols at about 132 years. Hive also found a $30,000 NVIDIA H200 AI accelerator was generally no better than an RTX 5090 at this job. Those are worst-case figures for random passwords. If the password is in a dictionary, a breach list or follows a known pattern, cracking tools get it in seconds regardless of length. In practice, most attackers go after low hanging fruit, short or common passwords and reused credentials from breach lists. So the safe mindset: use long, unique, random passwords or passphrases, and rely on other controls like MFA rather than thinking a password alone will hold forever.
Biometric login fingerprint, facial recognition like Face ID, iris scan, etc. are a form of authentication that can replace passwords on the device level, and they are very convenient. However, most biometric systems today actually just unlock a key or token that then authenticates you. For example, Windows Hello uses your face or PIN to unlock a stored credential that logs you into Windows. That credential, under the hood, might be a certificate or asymmetric key. Biometrics are great for user experience and phishing resistance. You can’t phish a fingerprint easily, but they have their own considerations: false negatives/positives, need for fallback e.g. you still need a PIN or password backup if the sensor fails, and privacy concerns. They also aren’t secrets you can change your fingerprint on for life. So if compromised through say a stolen fingerprint database, you can’t exactly get a new finger. That’s why most systems store only a protected representation of biometrics and keep it local. In the context of passwordless, biometrics often pair with something like FIDO2 e.g. your fingerprint unlocks a private key in a secure enclave which then authenticates you with the service no password transmitted. That is exactly how passkeys work, and the FIDO Alliance estimates 7 billion passkeys were in use by October 2026. In effect, biometrics can replace the act of password entry for the user, which is fantastic for convenience. So yes, biometrics are a key part of replacing passwords, but usually as part of multi factor or passwordless strategies rather than a silver bullet alone. They should be used alongside device possession or another factor for high security, to avoid issues where a biometric could be spoofed or forced. All in all, expect more biometric logins, but they work best when integrated into a broader authentication framework.
We are headed in that direction with passkeys, etc., but eliminating passwords system wide is easier said than done. The legacy of decades of systems built around password auth means that companies and websites can’t just flip a switch to remove them overnight. Compatibility is one issue not all user devices or client software may support the new methods yet. User readiness is another reason some users are not tech savvy enough or comfortable with alternative methods initially, and you need fallback options which often end up being passwords or one time codes. There’s also an ecosystem problem: going passwordless often requires an investment in new tech like FIDO2 infrastructure, issuance of security keys, etc. That said, many leading organizations are in transition: Microsoft made new consumer accounts passwordless by default in 2025, and Google, Amazon and others offer passkeys at scale. So the answer is: it’s happening gradually. In the FIDO Alliance's 2026 research, passkeys carried 36% of successful sign-ins at participating consumer services, yet only 28% of organizations surveyed had achieved fully passwordless authentication for their workforce and 57% still relied on phishable methods for primary sign-in. Realistically, we’ll be dealing with passwords as a backward compatible method for some years. In the meantime, focusing on mitigating their weaknesses as we discussed: MFA, monitoring, etc. is crucial. Eventually we might get to a point where passwords are rarely used just as we phased out things like dial up modems over time. But it requires a critical mass of services and users to support the alternatives, a process actively underway, but not instantaneous.
It depends on whose data you use. Okta's Secure Sign-in Trends Report 2025 found 70% of workforce users at its customers used MFA in January 2025, up from 66% a year earlier, ranging from 87% in technology to 42% in transportation and warehousing. Microsoft's Digital Defense Report 2024 put MFA use at 41% of Entra ID monthly active users among its enterprise customers. Either way, a large share of workforce accounts, from about 30% to more than half depending on the platform, still sign in with a password alone.
Very effective against credential-based attacks, and less so against targeted phishing unless the factor is phishing-resistant. A 2023 Microsoft study found MFA lowered the risk of compromise by 99.22%, and by 98.56% even when the password had already leaked. Google's 2019 research found SMS codes blocked 76% of targeted attacks and on-device prompts 90%, while no user relying only on security keys was phished. Attackers now work around phishable MFA with push fatigue and adversary-in-the-middle kits, so CISA recommends FIDO/WebAuthn as the gold standard.
The state of password security in 2026 underscores a critical inflection point in cybersecurity. On one hand, we face a password fatigue crisis. Users are overwhelmed by password overload, leading to insecure behaviors like reuse and simplistic choices that persist year after year. On the other hand, attackers have never been more equipped to exploit these weaknesses, armed with billions of stolen credentials, cheap rented GPU power, and automation tools to wage credential stuffing attacks at internet wide scale. This paradox of advanced technology versus human limitations means that clinging to 20th century password practices is increasingly untenable.
The statistics we’ve examined paint a sobering picture: about two in three people reusing passwords in the 2019 Google/Harris Poll, 123456 topping the 2025 lists again, credential abuse leading initial access in 22% of breaches in the 2025 DBIR and appearing in 39% of breaches in the 2026 DBIR, and more than 97% of identity attacks Microsoft sees being password attacks. The cost of these failures is measured not only in the $4.44M average breach cost of 2025, the record $4.99M global average in IBM’s 2026 study or the $11.5M U.S. average, but also in the invisible drain of productivity and user frustration. The data unmistakably signals that the old approach to passwords complexity theater and user training alone is not working. It’s time for a new paradigm.
Encouragingly, that paradigm is emerging. Standards and policies are shifting to screen out known bad passwords and emphasize length over composition. Multi factor authentication has gone from a niche to a must have, closing the door on many attacks. And the rapid rise of passkeys, an estimated 7 billion in use by October 2026, shows a collective will to finally transcend the password, leveraging public key cryptography and devices to do what humans cannot. The road ahead involves continued investment in these solutions and a commitment to secure authentication design treating identity as the new perimeter and passwords as just one eventually replaceable piece of that puzzle.
In practical terms, organizations should take these statistics as a mandate to act. Implement the best practices discussed: ban the Summer2023! type passwords, roll out MFA everywhere, monitor for abnormal login patterns, and foster a company culture that supports using password managers and new login methods. At the same time, start phasing in passwordless authentication pilots the sooner you learn and integrate, the smoother the transition when passwords truly phase out in the coming years. As the saying goes, the best time to fix the roof is when the sun is shining. Don't wait for a breach to make these changes. The data is already a flashing warning light.
Ultimately, the goal is to reduce reliance on human memory and static secrets. The era of remembering dozens of complex strings is ending, the era of combining something you have a device or key and something you are biometric is beginning. Until that transition completes, we must shore up the existing system as much as possible. The statistics speak to us telling us where the gaps are. By heeding their message, we can drastically cut down on preventable attacks like account takeovers and move toward an authentication ecosystem that is both more secure and user friendly. In the meantime, if one finds it amusing or alarming that the most advanced digital networks are still protected by password123, realize that this is a transitional phase. With collective effort from the security community, by the time we analyze 2030’s password stats, we aim to find that such anecdotes are a thing of the past.
About the Author
Mohammed Khalil is a Cybersecurity Architect at DeepStrike. Specializing in advanced penetration testing and offensive security operations, he holds certifications including CISSP, OSCP, and OSWE. Mohammed has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
