August 9, 2025
Updated: November 5, 2026
A deep dive into the strengths, weaknesses, and best use cases for manual and automated penetration testing, and why 2026 demands a hybrid of automation, AI, and human depth.

Mohammed Khalil
Quick answer: the difference in manual vs automated penetration testing is who does the work and what gets proven. Automated testing uses software to check systems for known vulnerabilities and misconfigurations quickly and repeatedly. Manual testing uses a skilled human tester to prove what is actually exploitable and to find what tools miss: business-logic flaws, broken authorization and chained attack paths. Automation gives you breadth and frequency; manual testing gives you depth and proof. Most organizations need both: automated coverage between engagements, plus a human-led test at least once a year and after any major change.
The 2026 best practice is a three-layer model: automated breadth, AI-assisted triage in the middle, and human depth on what matters.
Updated: November 2026. Adds a direct answer up front, what a manual penetration test involves in practice, a side-by-side of DAST, breach and attack simulation, PTaaS and AI agents, and what PCI DSS and NIST actually require. Earlier updates covered AI-assisted and autonomous testing, the PTaaS delivery model and compliance expectations for human-led testing.
Start with a sobering fact. The Verizon 2025 Data Breach Investigations Report found that exploitation of vulnerabilities as an initial access vector grew 34% year over year and now accounts for roughly 20% of breaches, with edge devices and VPNs a particular focus. The 2026 DBIR puts exploitation at 31% of initial access, now the most common vector. In that landscape, simply "finding bugs" is not enough. The goal is to stop attackers before they get a foothold, and that requires a smarter approach to security testing.
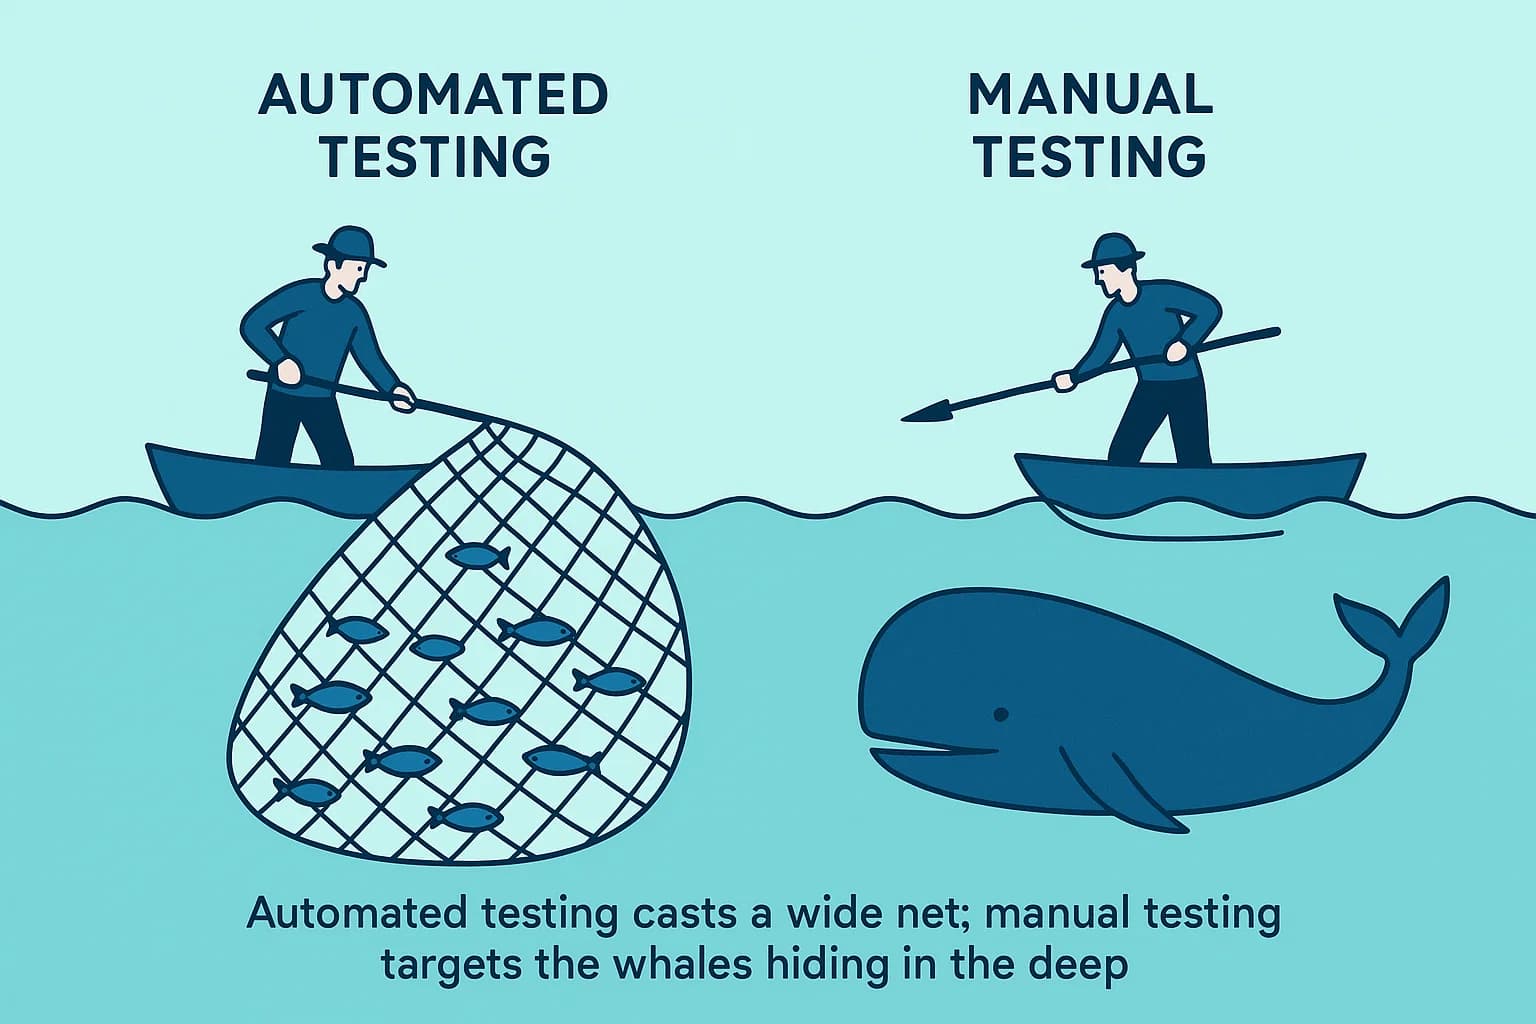
The choice between manual vs automated penetration testing isn't about picking a "better" option; it's about understanding you're choosing between two different tools for two very different jobs. One is a wide net designed to catch common fish; the other is a spear for hunting the whales hiding in the deep. A related choice is in-house vs outsourced penetration testing.
Why does this distinction matter more than ever? In an era of complex, multi-layered cloud applications and AI-accelerated attacks, relying on a single testing method is a critical mistake. Understanding the strengths and weaknesses of each approach is crucial for effective risk management, smart budget allocation, and achieving meaningful compliance rather than just checking a box.
The biggest misconception in cybersecurity testing is confusing automated scanning with true penetration testing. Let's clear that up right now.
Manual penetration testing supplies what automation cannot: judgment. A skilled tester models your specific application, reasons about what a user should and should not be able to do, and chains weaknesses toward a goal the way an adversary would. Crucially, every finding is reproduced by hand before it is reported, so what reaches you is verified and exploitable, not a maybe. The trade-off is that a manual test is a point-in-time assessment: a flaw introduced two weeks after the engagement stays unfound until the next cycle, which is precisely the gap automation and a continuous cadence exist to close.
At its core, manual penetration testing is a human-led, objective-driven engagement where a skilled ethical hacker simulates a real-world attack to uncover and exploit vulnerabilities. It's not just about finding a flaw; it's about demonstrating its real-world impact. This involves chaining exploits, pivoting through systems, and thinking creatively like an adversary would. This is precisely what the National Institute of Standards and Technology (NIST) defines as mimicking real-world attacks to circumvent security features.
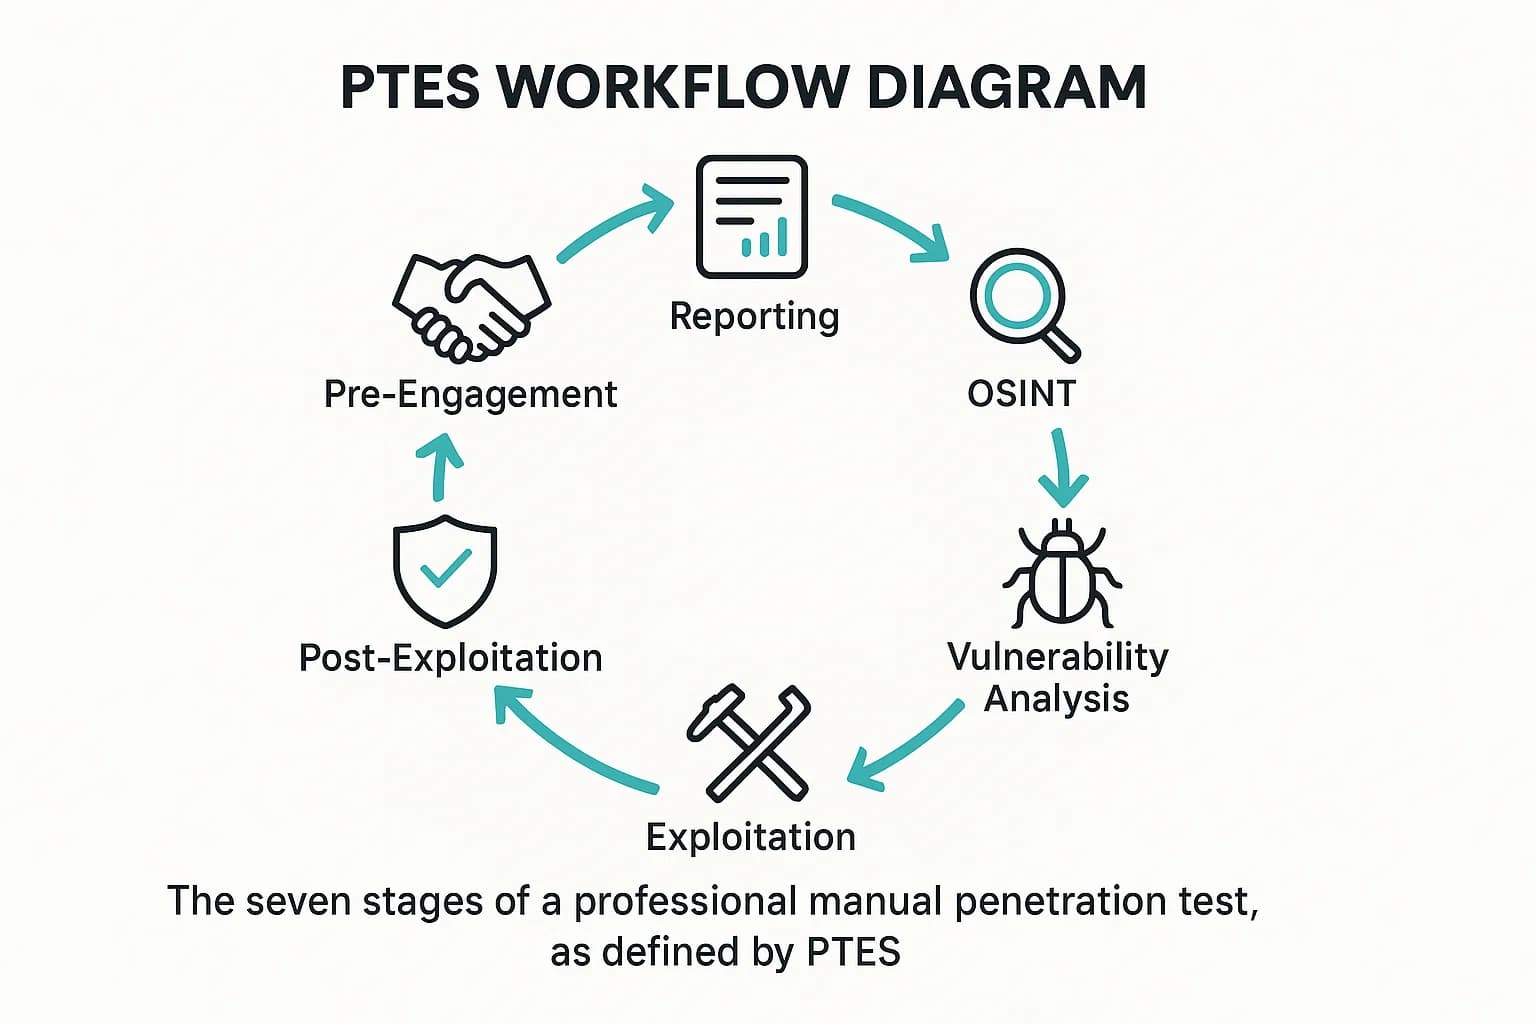
This isn't random, chaotic hacking. Professional engagements follow structured frameworks to ensure the assessment is comprehensive, methodical, and repeatable. The most respected of these is the Penetration Testing Execution Standard (PTES), which outlines seven distinct stages:
This structured approach is what separates professional from ad hoc efforts.
A manual penetration test is a scoped, authorized engagement in which a person, not a tool, decides what to test next. Tools still do the repetitive work, but the tester reads the responses, forms a hypothesis about how the application or network is meant to behave, and then tries to break that assumption. NIST's SP 800-115 technical testing guide notes that penetration testing is labor-intensive and requires great expertise to avoid harming the systems under test, which is why it is scoped and time-boxed rather than left running.
For a web application or a mid-size network, expect one to three weeks of active testing, broken into five parts:
Who does the work matters as much as the method. Ask for testers with hands-on, exam-based certifications such as OSCP or OSWE, a sample report, and a documented penetration testing methodology. A tester who cannot explain why they chose each test is running a scan with extra steps.
Scanners are genuinely good at what they are good at, and dismissing them is as wrong as over-trusting them. They reliably find known CVEs in third-party components, weak TLS configuration and missing security headers, default credentials on common services, simple payload-discoverable injection and cross-site scripting, exposed admin interfaces, and common cloud misconfigurations. For breadth-first inventory work this is irreplaceable: running a human over a thousand hosts to check for outdated SSH versions would be slow and a waste of expert time. Automation is how you keep coverage current across an estate that changes weekly, and how you instantly re-test a fix. It is the backbone of continuous vulnerability management.
Automated penetration testing is the use of specialized software to rapidly scan for known security weaknesses and misconfigurations across a wide range of systems. These tools operate by comparing the state of a target system against a massive, constantly updated database of predefined vulnerability signatures, think outdated software versions, common configuration errors, or known Common Vulnerabilities and Exposures (CVEs).
Here’s the deal, though: the term "automated penetration testing" is often a marketing misnomer. A true penetration test, by definition, involves attempting to exploit vulnerabilities to achieve a specific objective, which requires context and creativity. Most tools marketed as "automated pentesting" platforms are actually advanced vulnerability scanners with some limited, scripted exploitation capabilities. They check for signatures; they don't model threats or adapt their strategy based on what they find.
This confusion is expensive. It leads organizations to buy a scanning tool believing they have satisfied a real pentesting requirement, such as PCI DSS Requirement 11.4 (note the numbering: it was 11.3 under the retired v3.2.1). That creates a false sense of security and leaves them exposed to the very threats they thought they were covered against. If a human expert is not validating findings and attempting to chain them together, it is not a penetration test.
This brings us to a crucial distinction. A vulnerability scan and a penetration test are not the same thing, and using the terms interchangeably is a recipe for disaster.
Relying on a vulnerability scan when you need a penetration test, for example to meet SOC 2 penetration testing requirements or to qualify for cyber insurance, can lead to compliance failures and, worse, unmitigated critical risks.
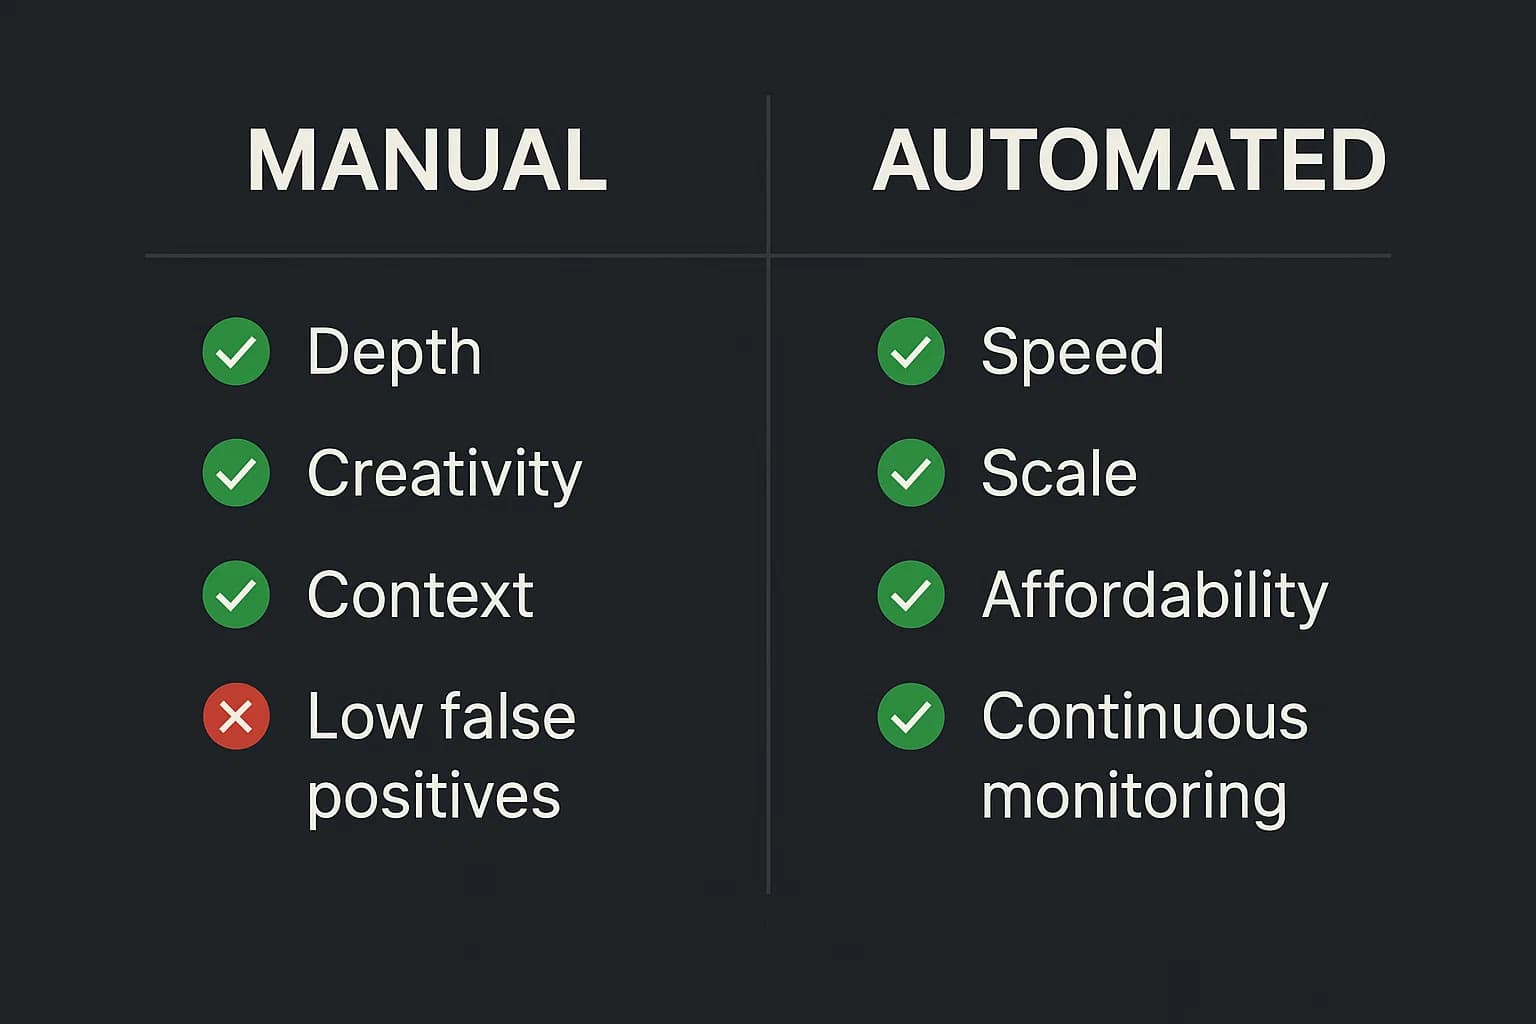
For UK organizations evaluating manual vs automated penetration testing, the practical pros and cons of each approach help determine which model fits the situation.
| Manual penetration testing | Automated testing / scanning | |
|---|---|---|
| Strength | Depth: business logic, authorization, chained exploits | Breadth: known CVEs, misconfigurations, missing patches, across everything |
| Speed | One to three weeks of active testing | Minutes to hours |
| Coverage | Scoped, point-in-time, deep | Wide, repeatable, shallow |
| False positives | Low (findings verified by hand) | Higher (needs triage) |
| Finds business-logic flaws | Yes | Rarely (no model of intended behavior) |
| Chains low-severity issues | Yes | No (evaluates findings in isolation) |
| Compliance sign-off | Required by PCI DSS 11.4 and FedRAMP; commonly used as audit evidence for SOC 2, ISO 27001 and HIPAA risk analysis | Rarely sufficient alone |
| Cost | Industry estimates commonly start around $5,000 for a web app, scaling with scope | Subscription or per-scan, lower |
The line to hold onto: automated testing tells you where the known problems are; manual testing tells you how an attacker would actually break in.
The Case for Manual Testing: Depth, Accuracy, and Real World Insight
The primary advantage of manual testing is the human brain. A skilled tester brings creativity, intuition, and contextual awareness that no tool can replicate.
The Limitations of Manual Testing: Cost, Speed, and Scale
Despite its strengths, manual testing isn't a silver bullet. It has practical limitations.
The Power of Automated Testing: Unmatched Speed and Breadth
Where manual testing is deep, automated testing is wide. Its power lies in its efficiency and scale.
The Blind Spots of Automated Testing: False Positives and Lack of Context
The greatest strength of automation, its reliance on predefined rules is also its greatest weakness.
Only humans reliably find business-logic flaws because these are flaws in what an application is supposed to do, not in its inputs and outputs. A scanner sees requests, responses and status codes; it cannot know that a withdrawal should reject negative amounts or that a coupon should not stack. A tester who understands the intended workflow can.
Three categories of flaw are largely out of reach for signature-based scanners:
This is why a purely automated report gives false comfort. The systems it certifies as clean are often exactly where the serious findings live.
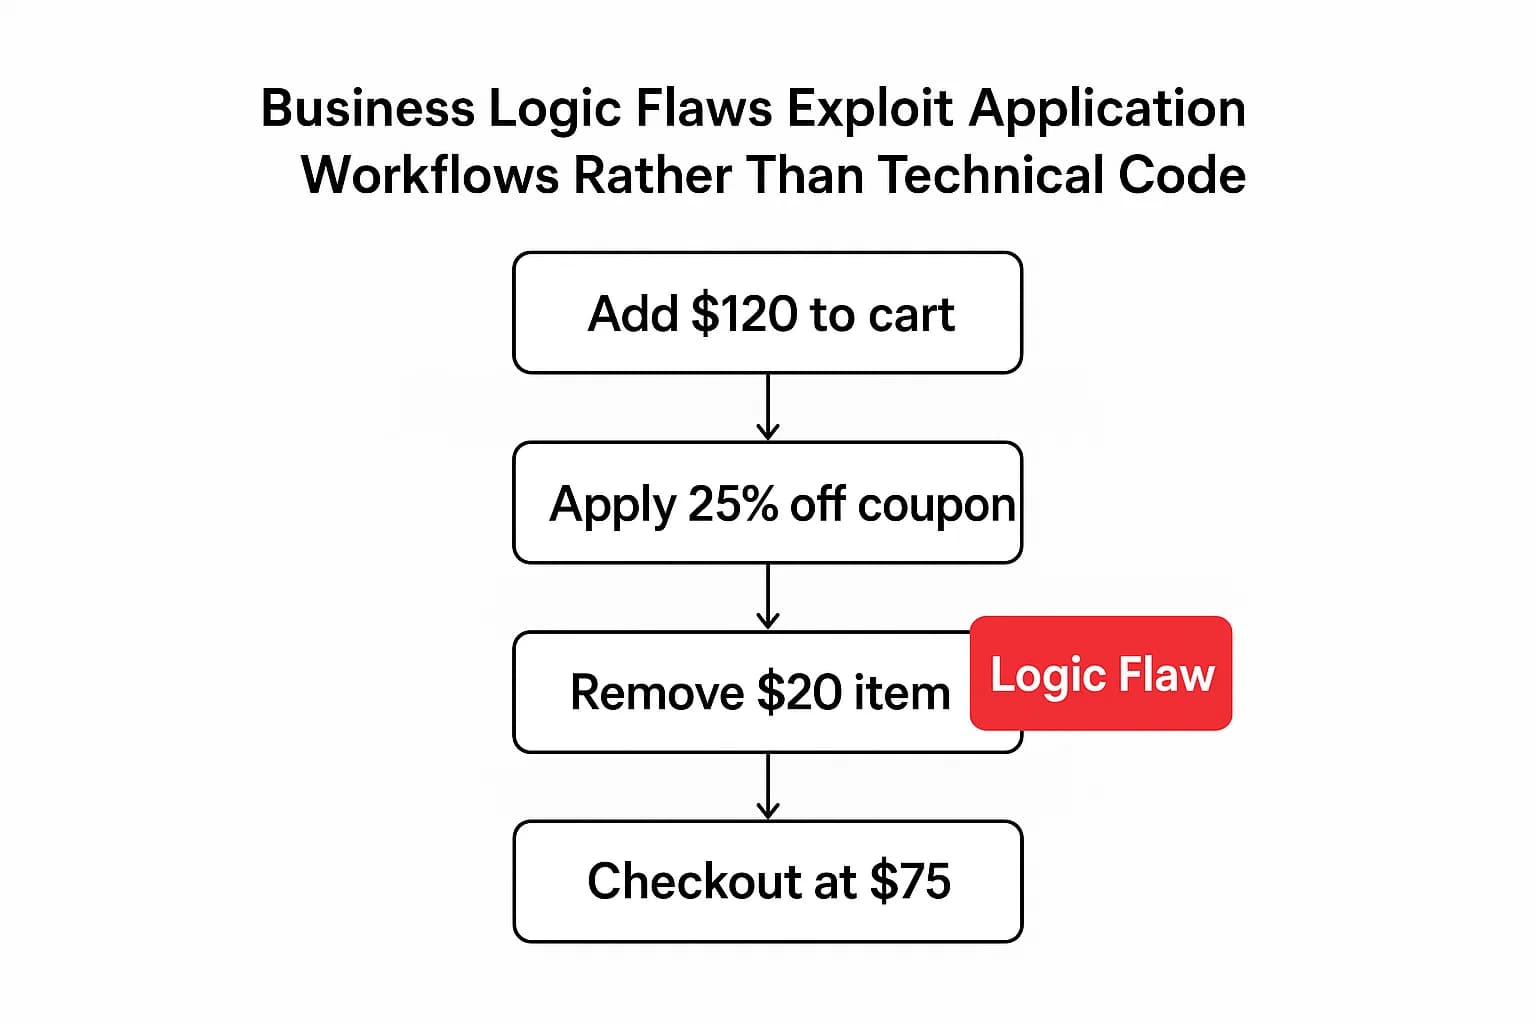
This lack of context is most apparent when it comes to business logic flaws. These are vulnerabilities not in the technical code itself, but in the rules and workflows of an application. The application works exactly as it was coded to, but its design allows for unintended, harmful outcomes that an attacker can exploit.
Here’s an illustrative example: an e-commerce site offers a "25% off orders over $100" coupon. An attacker adds $120 worth of items to their cart, applies the coupon, and the price drops to $90. Then, they remove a $20 item from the cart. The system fails to re-validate the coupon's conditions, and the attacker checks out, paying just $75 for $100 worth of goods. This is a flaw in the process, not a technical bug a signature-based scanner would find.
This is why business logic flaws represent such a significant risk. They attack the very core of a company's unique processes and value propositions. A company's competitive advantage often lies in its proprietary logic, a unique pricing engine, a complex user permission model, and a specific transaction workflow. Automated scanners are designed to find common, generic vulnerabilities like those in the OWASP Top 10 across all applications. By definition, they cannot understand the unique, specific business context of an individual application.
An attacker using manual techniques can therefore target the heart of a business's operations, causing financial or reputational damage that is disproportionately high compared to a generic technical bug. For any business with custom, critical applications, relying solely on automated scanning is a dangerous oversight, as it leaves their most valuable digital assets completely untested for this entire class of threat. This is how many real-world attacks, like those detailed in our Real world account takeover case study, are carried out.
Understanding the theory is one thing; putting it into practice is another. Here’s a look at the tools we actually use and a guide to help you choose the right approach.
Manual Testing Arsenal: The Craftsman's Tools
A manual pentester uses a suite of tools not as a crutch, but as an extension of their own expertise. The workflow often looks like this:
Automated Scanning Platforms: The Dragnet
Automated tools are designed for speed and breadth, casting a wide net to catch common issues.
| Your situation | Reach for |
|---|---|
| Continuous coverage of a fast-changing estate | Automated scanning plus AI triage |
| Instantly re-testing a fix | Automated / autonomous |
| A new app with complex business logic | Manual (human depth) |
| Compliance or customer security sign-off | Manual, independent third party |
| Modeling a specific adversary | Manual red team |
| A quote needing only a URL and a card | Neither, that is a red flag |
Reach for automation when currency and scale are the point. Reach for humans when judgment is the point. Most real programs need both, sequenced.
The right choice depends entirely on your objective.
Choose Manual Testing For...
Compliance mandates: when PCI DSS Requirement 11.4 requires penetration testing, when your risk analysis under the HIPAA Security Rule calls for it (the current rule has no explicit penetration testing requirement; a January 2025 proposal to add one is not yet final), or when FedRAMP requires it, manual testing is non-negotiable. Auditors expect to see proof of human validation, not a tool export.
Choose Automated Testing For...
The manual-versus-automated frame is now a triangle, because AI has landed in the middle, and it is widely misrepresented. Used honestly, AI augments the human tester rather than replacing them:
Two warnings matter. First, AI tooling invents findings, producing confident, well-written vulnerabilities that do not exist. Ship those unverified and a client's security team will fail to reproduce one and rightly discount the whole report, so every AI-surfaced finding still needs human validation. Second, "AI-powered" has become the fashionable label for the same old scan-in-a-box. The autonomous approach is real and useful, but it is a complement to human depth, not a replacement for it, and buyers should verify which one they are actually getting.
Vendors now use "automated pentesting" for at least five different things, and buyers often compare a manual test with the wrong one. The table below compares each option on the questions that decide whether it can stand in for a human-led test.
| Approach | What drives it | Proves exploitability? | Finds logic and authorization flaws? | Typical cadence | Best use |
|---|---|---|---|---|---|
| Vulnerability scanner | Signature checks against hosts and services | No, it reports likely issues | No | Weekly to quarterly, or continuous | Patch and configuration hygiene across every asset |
| DAST | A crawler sends test requests to a running web app or API | Sometimes, for simple injection | Rarely | Every build or release | Catching common web flaws in CI/CD |
| Automated pentest platform | Scripted attack chains against networks and identity systems | Yes, for well-documented techniques | Limited | Monthly to continuous | Checking internal network and Active Directory exposure between human tests |
| Breach and attack simulation (BAS) | Safe simulations of known attacker techniques | No, it tests whether controls detect or block | No | Continuous | Confirming that EDR, SIEM and email controls still work |
| AI agents (agentic pentesting) | LLM-driven agents that plan and adapt tests | Partly, findings need human confirmation | Some IDOR and simple logic cases | Continuous or on demand | Extra coverage on fast-changing apps, with human review |
| PTaaS | Human testers plus a platform for findings and retests | Yes | Yes, within the scoped effort | On demand or subscription | Spreading human testing across the year |
| Manual penetration test | A human tester, scoped and time-boxed | Yes, every finding reproduced | Yes | Annually and after major changes | Compliance, critical apps, new releases and attack-path proof |
Three distinctions do most of the work. DAST is a testing technique, not a penetration test; our SAST vs DAST vs IAST vs RASP comparison covers where it fits in a pipeline. Breach and attack simulation measures whether your defenses notice an attack, which is a different question from whether a system can be broken into. Automated pentest platforms, explained in our automated penetration testing guide, are strongest on networks and identity, where attack techniques are well documented, and weakest on custom web applications.
AI agents sit closest to manual testing and are improving quickly, but they share the false-finding problem described above. Treat an agent's output the way you treat a scanner's: as candidates that a human confirms before anyone acts on them. Testing AI features themselves, such as LLM chat and agents inside your product, is a different discipline; see AI red teaming.
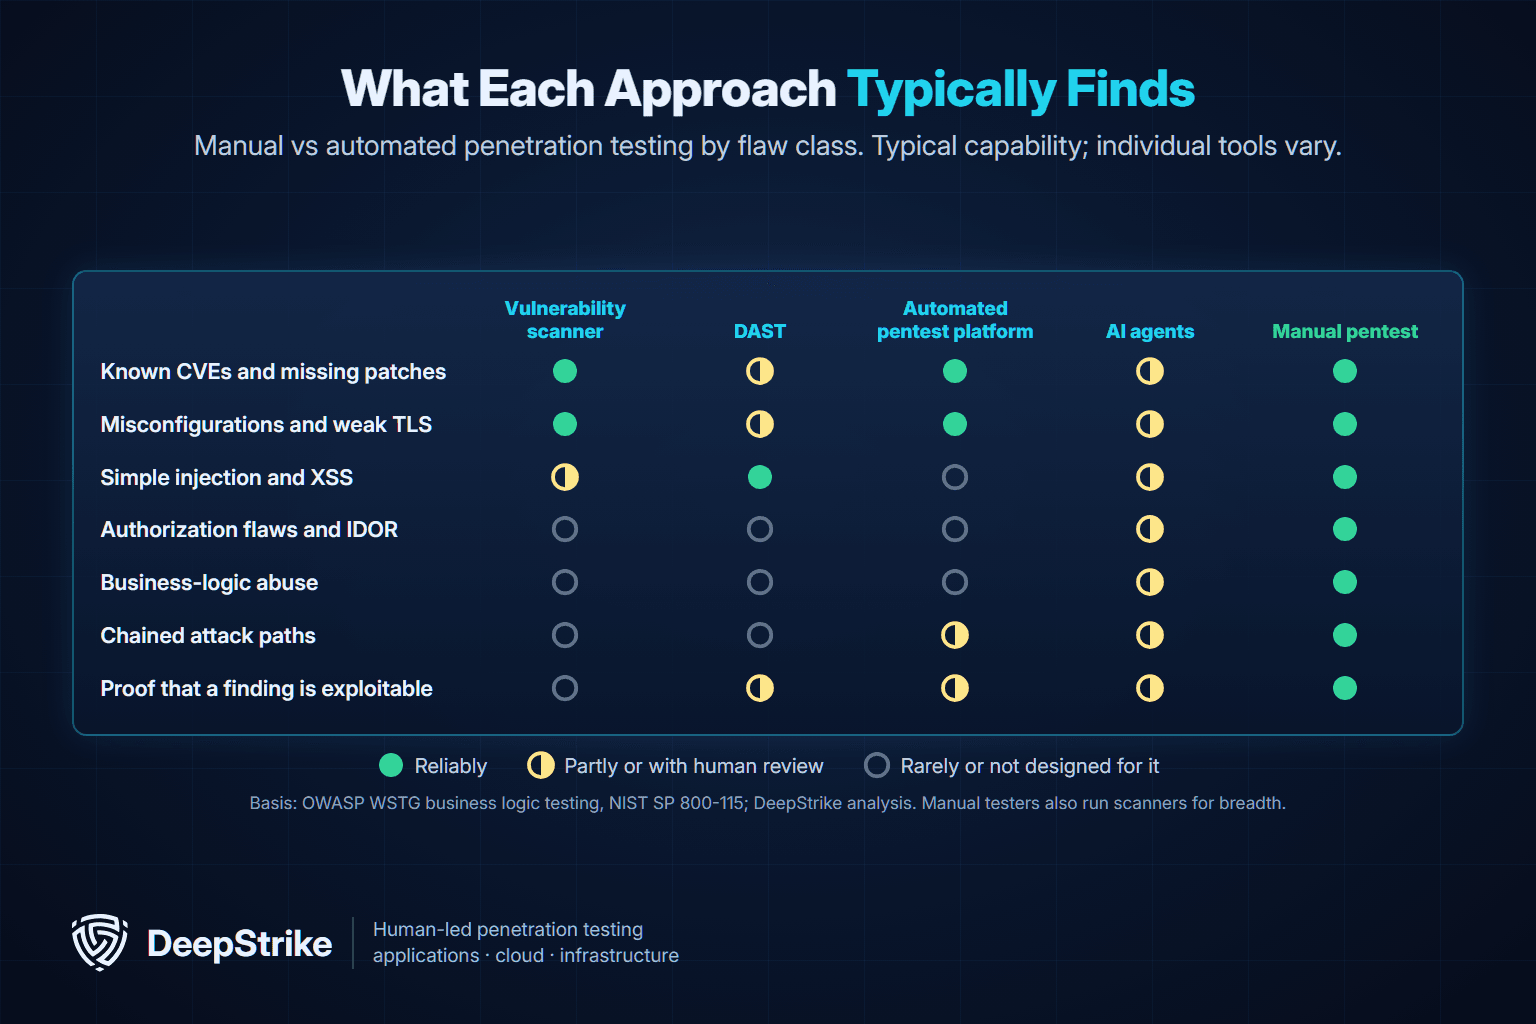
Compliance frameworks settle the manual-versus-automated question by requiring both, on different schedules. PCI DSS v4.0.1, the current card-industry standard, splits them into two requirements:
NIST SP 800-115 draws the same line. It groups vulnerability scanning with discovery techniques and places penetration testing among the techniques that validate whether vulnerabilities are real, and it recommends regularly scheduled scanning interspersed with periodic penetration testing. If an auditor, customer questionnaire or cyber insurer asks for a penetration test, read it as a human-led test with a methodology and reproduction evidence, not a scheduled scan. Our PCI DSS penetration testing guide walks through the requirement in detail.
Mature teams have stopped arguing "versus" and moved to a hybrid: continuous automated testing for breadth and currency, plus periodic human-led testing for depth on what matters most. The two feed each other: automated data informs where humans dig, and human discoveries tune the automated rules. The PTaaS delivery model packages this as subscription access to human testers, findings in a portal in near real time, and one-click retests, spreading cost across the year instead of one heavy annual bill. What the pieces cost is covered in our penetration testing cost guide.
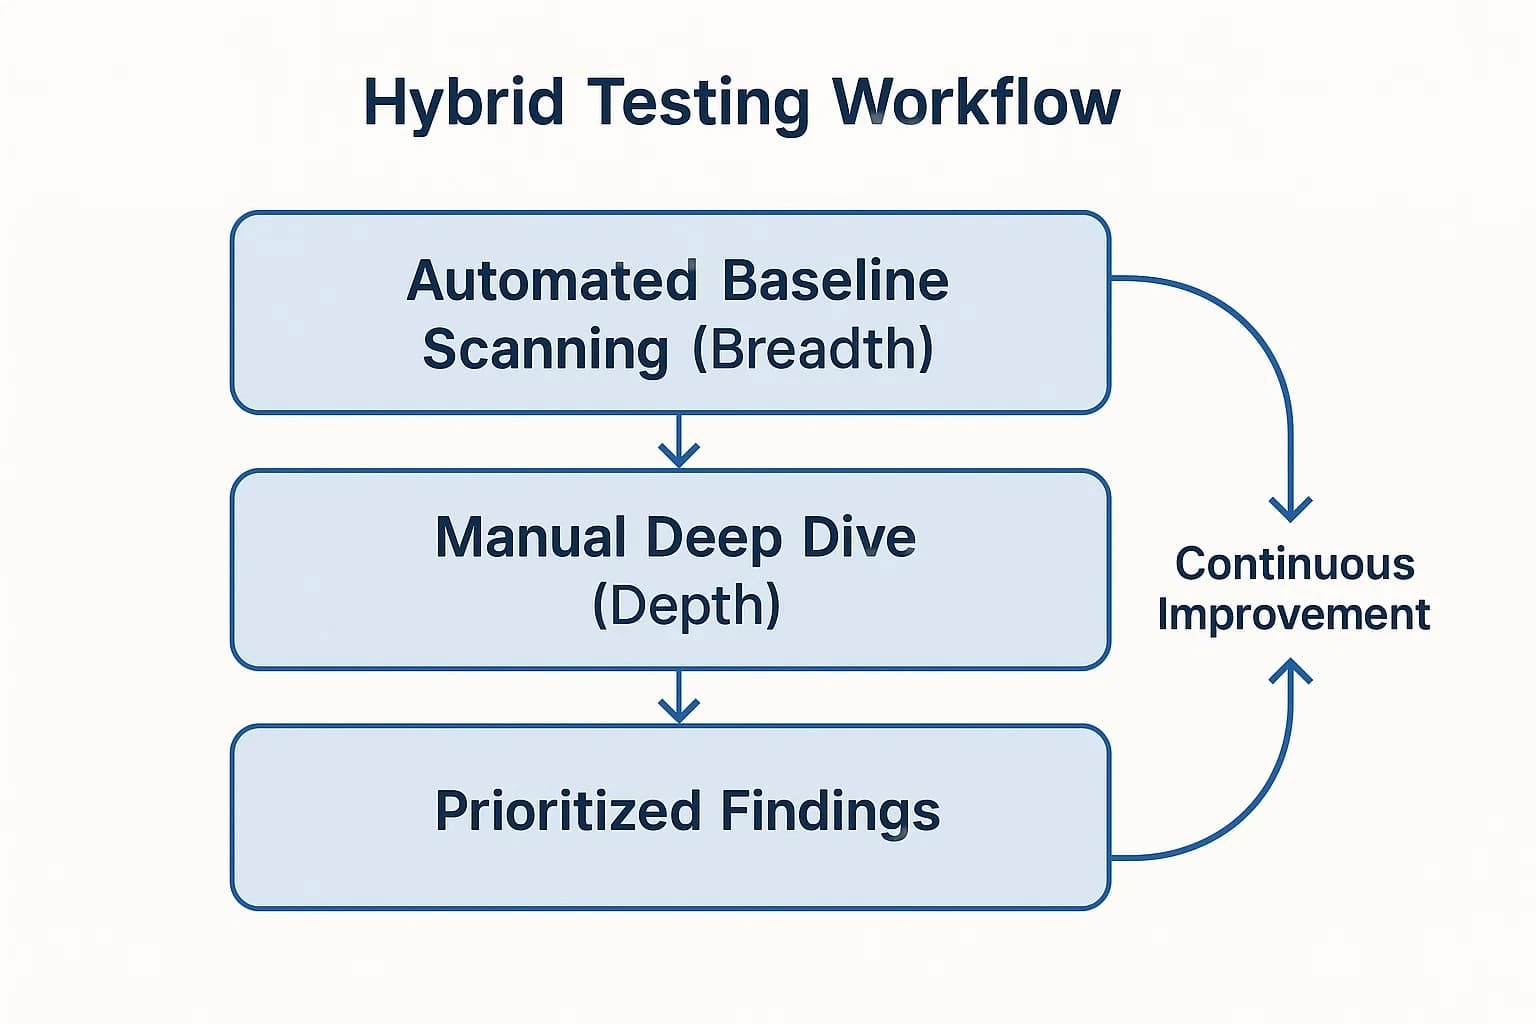
The "manual vs automated" debate is ultimately a false dichotomy. The modern, resilient organization doesn't choose one or the other; it strategically integrates both into a hybrid model.
The goal of a hybrid strategy is to create a continuous feedback loop. You use automation for its breadth and frequency, and you use manual testing for its depth and validation. Crucially, the findings from manual tests should be used to create custom rules and refine your automated scans, making the entire program smarter over time. A growing trend in this space is the adoption of PTaaS platforms, which blend ongoing automated scanning with on-demand access to human experts — see PTaaS vs. Traditional Penetration testing for how the two models differ, though they still cannot fully replace the deep, creative analysis of a dedicated manual engagement.
How To: A Step by Step Guide to a Hybrid Penetration Test
Here’s how a practical hybrid engagement works:
Illustrative Scenario: Securing a Cloud-Native App with a Hybrid Model
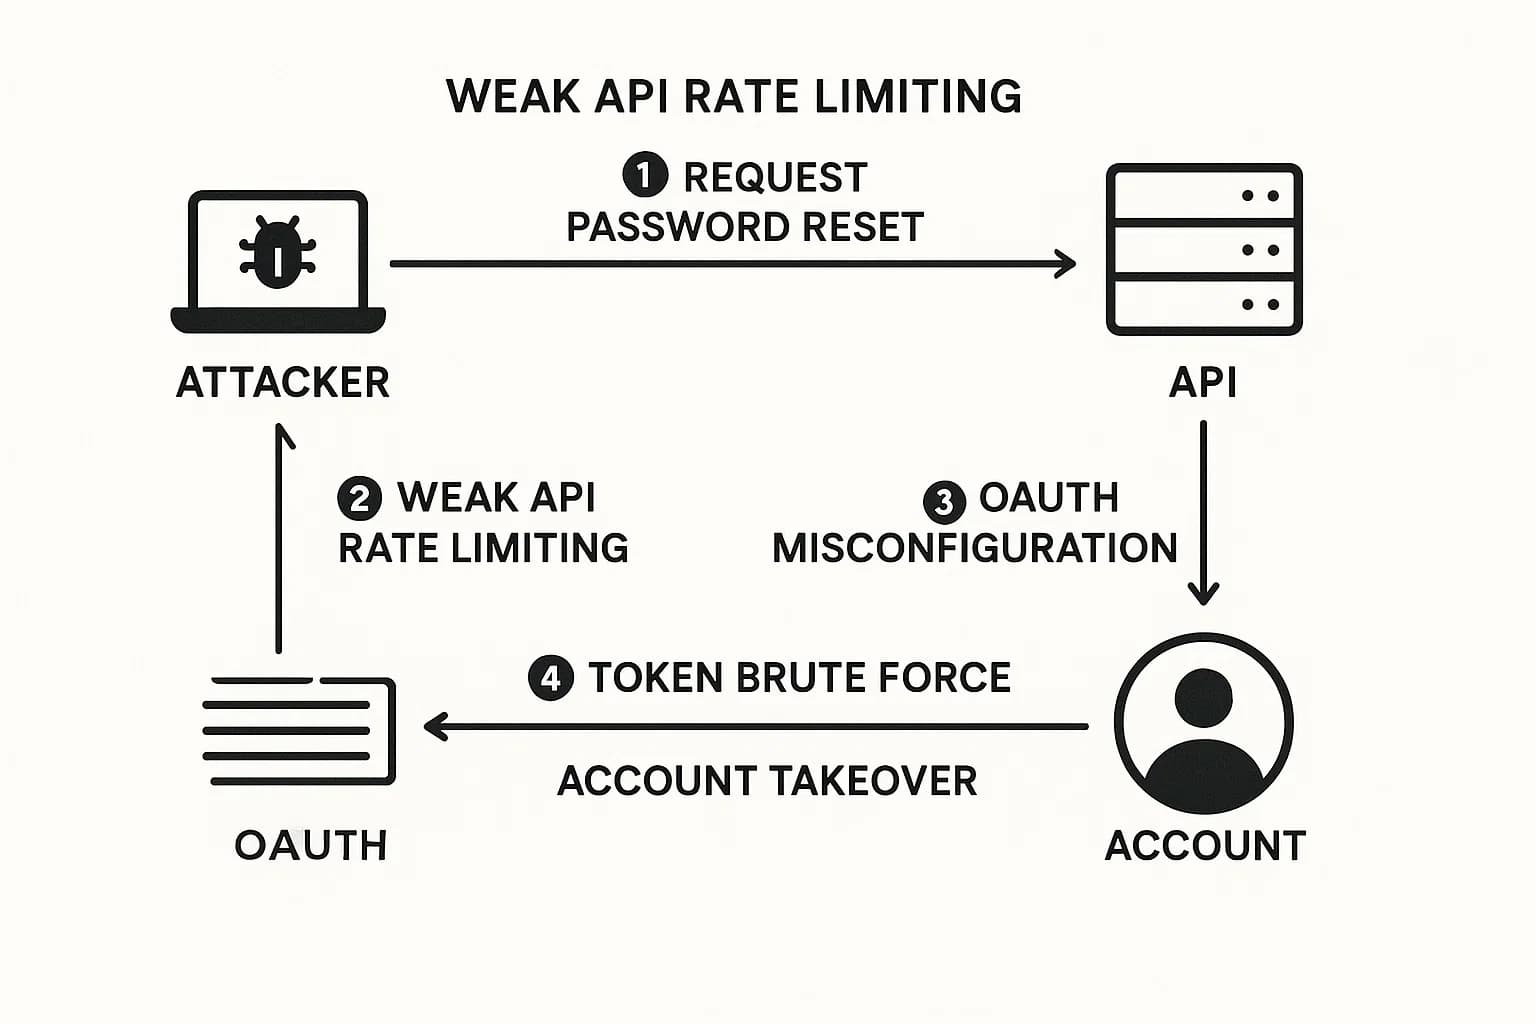
Consider a fintech company deploying a new payment application on AWS, built with microservices and numerous APIs.
The outcome: the automated tools provided essential, continuous coverage and caught dozens of common bugs. But only the manual test found the "death by a thousand cuts" vulnerability that could have led to a massive breach, the kind tracked in our data breach statistics.
How This Approach Helps with Cyber Insurance and Compliance
Securing penetration testing for cyber insurance eligibility keeps getting tougher. Some underwriters now ask for more than a clean automated scan report: they want evidence of rigorous, manual testing that validates security controls against realistic attack scenarios. A hybrid report, showing both broad automated coverage and deep manual validation, provides exactly that evidence, and the same principle applies to any compliance-focused penetration testing engagement.
If a vendor is quoting purely on hours of scanning, ask hard questions. The tells of a scan-in-a-box are consistent:
Both, across three layers. Automated scanning gives breadth across everything you own, AI assistance handles high-volume work in the middle such as mapping attack surface, triaging findings, and reading code, and manual testing supplies depth: business logic, authorization, and chained exploits. A test using only one layer misses what the others catch, which is why the modern standard is a hybrid of all three.
Not yet. AI has no model of what your application is for, so it cannot reliably identify business-logic flaws or chain issues into a real compromise, and it produces confident findings that are not real. Used well it augments human testers by mapping attack surface, triaging noise, and reading code at volume, but every finding it surfaces still has to be reproduced by hand before it is reported.
Ask which findings the tester reproduced by hand, and how; a scan-based provider cannot answer. Other tells: turnaround in hours rather than one to three weeks, scoping that needs only a URL, findings that read like a tool export, and no business-logic findings at all. "AI-powered" is often just the current label for the same automated scan.
Scanners cannot reliably find business-logic flaws, authorization flaws across user contexts such as IDOR and cross-tenant access, or chained attack paths that combine several low-severity issues into a real compromise. These have no signature to match, so finding them requires a human who understands what your application is supposed to permit.
Manual penetration testing is a security assessment in which a skilled human tester, working under written authorization and an agreed scope, simulates a real attacker to find and prove exploitable weaknesses. Tools support the work, but the tester chooses what to test, reproduces every finding by hand, and looks for flaws scanners cannot see, such as broken authorization, business-logic abuse and chained attack paths.
No. DAST is an automated technique that sends test requests to a running web application or API and reports likely flaws such as injection or missing security headers. Automated pentest platforms usually focus on networks and identity and try to chain known techniques. Neither replaces a manual penetration test, because neither understands what your application is supposed to permit.
No. AI agents can plan and adapt tests and sometimes find IDOR or simple logic flaws, but they still report findings that are not real and have no model of your business rules. Treat agent output as candidates for a human tester to confirm, and keep a human-led test for compliance, critical applications and major releases.
The main difference is the "who" and the "how." Automated testing uses software tools to quickly scan for a large number of known vulnerabilities based on predefined signatures. Manual testing uses a skilled human expert who leverages creativity, context, and intuition to find unknown and complex vulnerabilities, like business logic flaws, that tools can't detect.
No. Automated scanning is part of PCI DSS, but Requirement 11.4 (11.3 under the retired v3.2.1) requires penetration testing of both the application and network layers, and the PCI SSC's penetration testing guidance describes a penetration test as a largely manual process that confirms whether vulnerabilities are exploitable. An automated scan alone will not meet the requirement.
The cost varies dramatically. Automated scanning tools can range from a few hundred to a few thousand dollars per month. Manual penetration tests are priced based on scope and complexity; industry estimates commonly range from about $5,000 for a very small application to over $100,000 for a large, complex enterprise environment. Our penetration testing cost guide explains what drives those figures.
Absolutely not. A vulnerability scan identifies potential weaknesses. A penetration test confirms if they are exploitable and determines the potential business impact. They are complementary security activities, not interchangeable ones. A scan gives you a list of possibilities; a pentest gives you confirmed, exploitable findings within the tested scope.
Best practice is to conduct a manual penetration test at least annually, and always after any significant changes to your applications or infrastructure. Automated vulnerability scanning should be performed much more frequently ideally on a continuous basis within a CI/CD pipeline, or at least weekly or monthly.
It refers to the level of knowledge given to the tester. In black box vs white box testing explained, black box means the tester has no prior knowledge of the system, just like an external attacker. White box means the tester has full knowledge, including access to source code and architecture diagrams. Gray box is in the middle, where the tester has some limited knowledge, like user level credentials.
Because business logic is unique to each application's purpose and workflows. Automated scanners rely on universal signatures to find common technical bugs (e.g., a specific pattern indicating an SQL injection). They lack the contextual understanding to recognize that a sequence of valid actions in a custom checkout process is actually a flaw that can be abused. SSTI shows the limit from another angle: scanners can flag many template-injection points, but proving impact, such as safely reaching code execution through the template engine, usually takes a human.
The "manual vs automated" debate is outdated. The modern, resilient organization doesn't choose one or the other; it strategically integrates both. Automation provides the constant vigilance and scale needed to manage the high volume of common threats that make up the bulk of today's attacks. Manual testing provides the critical, deep insight needed to find the unique, high impact flaws that automated tools will forever miss the ones that can bring a business to its knees.
Your security posture is only as strong as the sum of its parts. That means combining the relentless breadth of a machine with the insightful depth of a human mind, and using AI for the high-volume work in between. Neglecting any of the three leaves a critical gap for attackers to exploit.
Today's threats demand more than awareness; they require readiness. If you are looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
