October 14, 2025
Updated: November 5, 2026
A practical enterprise guide to black box, white box, and gray box penetration testing for modern identity-, API-, and cloud-driven environments.

Mohammed Khalil
Black box vs white box testing comes down to visibility. Black box testing evaluates a system from the outside, with no knowledge of its code or internal design. White box testing uses full access to source code, architecture and documentation. Gray box testing sits between them, usually with credentials and partial documentation. In software QA, the terms describe test-design techniques. In penetration testing, they describe how much the tester knows before attacking. That is the real question behind black box vs white box penetration testing: the model you pick changes attacker realism, coverage depth and time to findings.
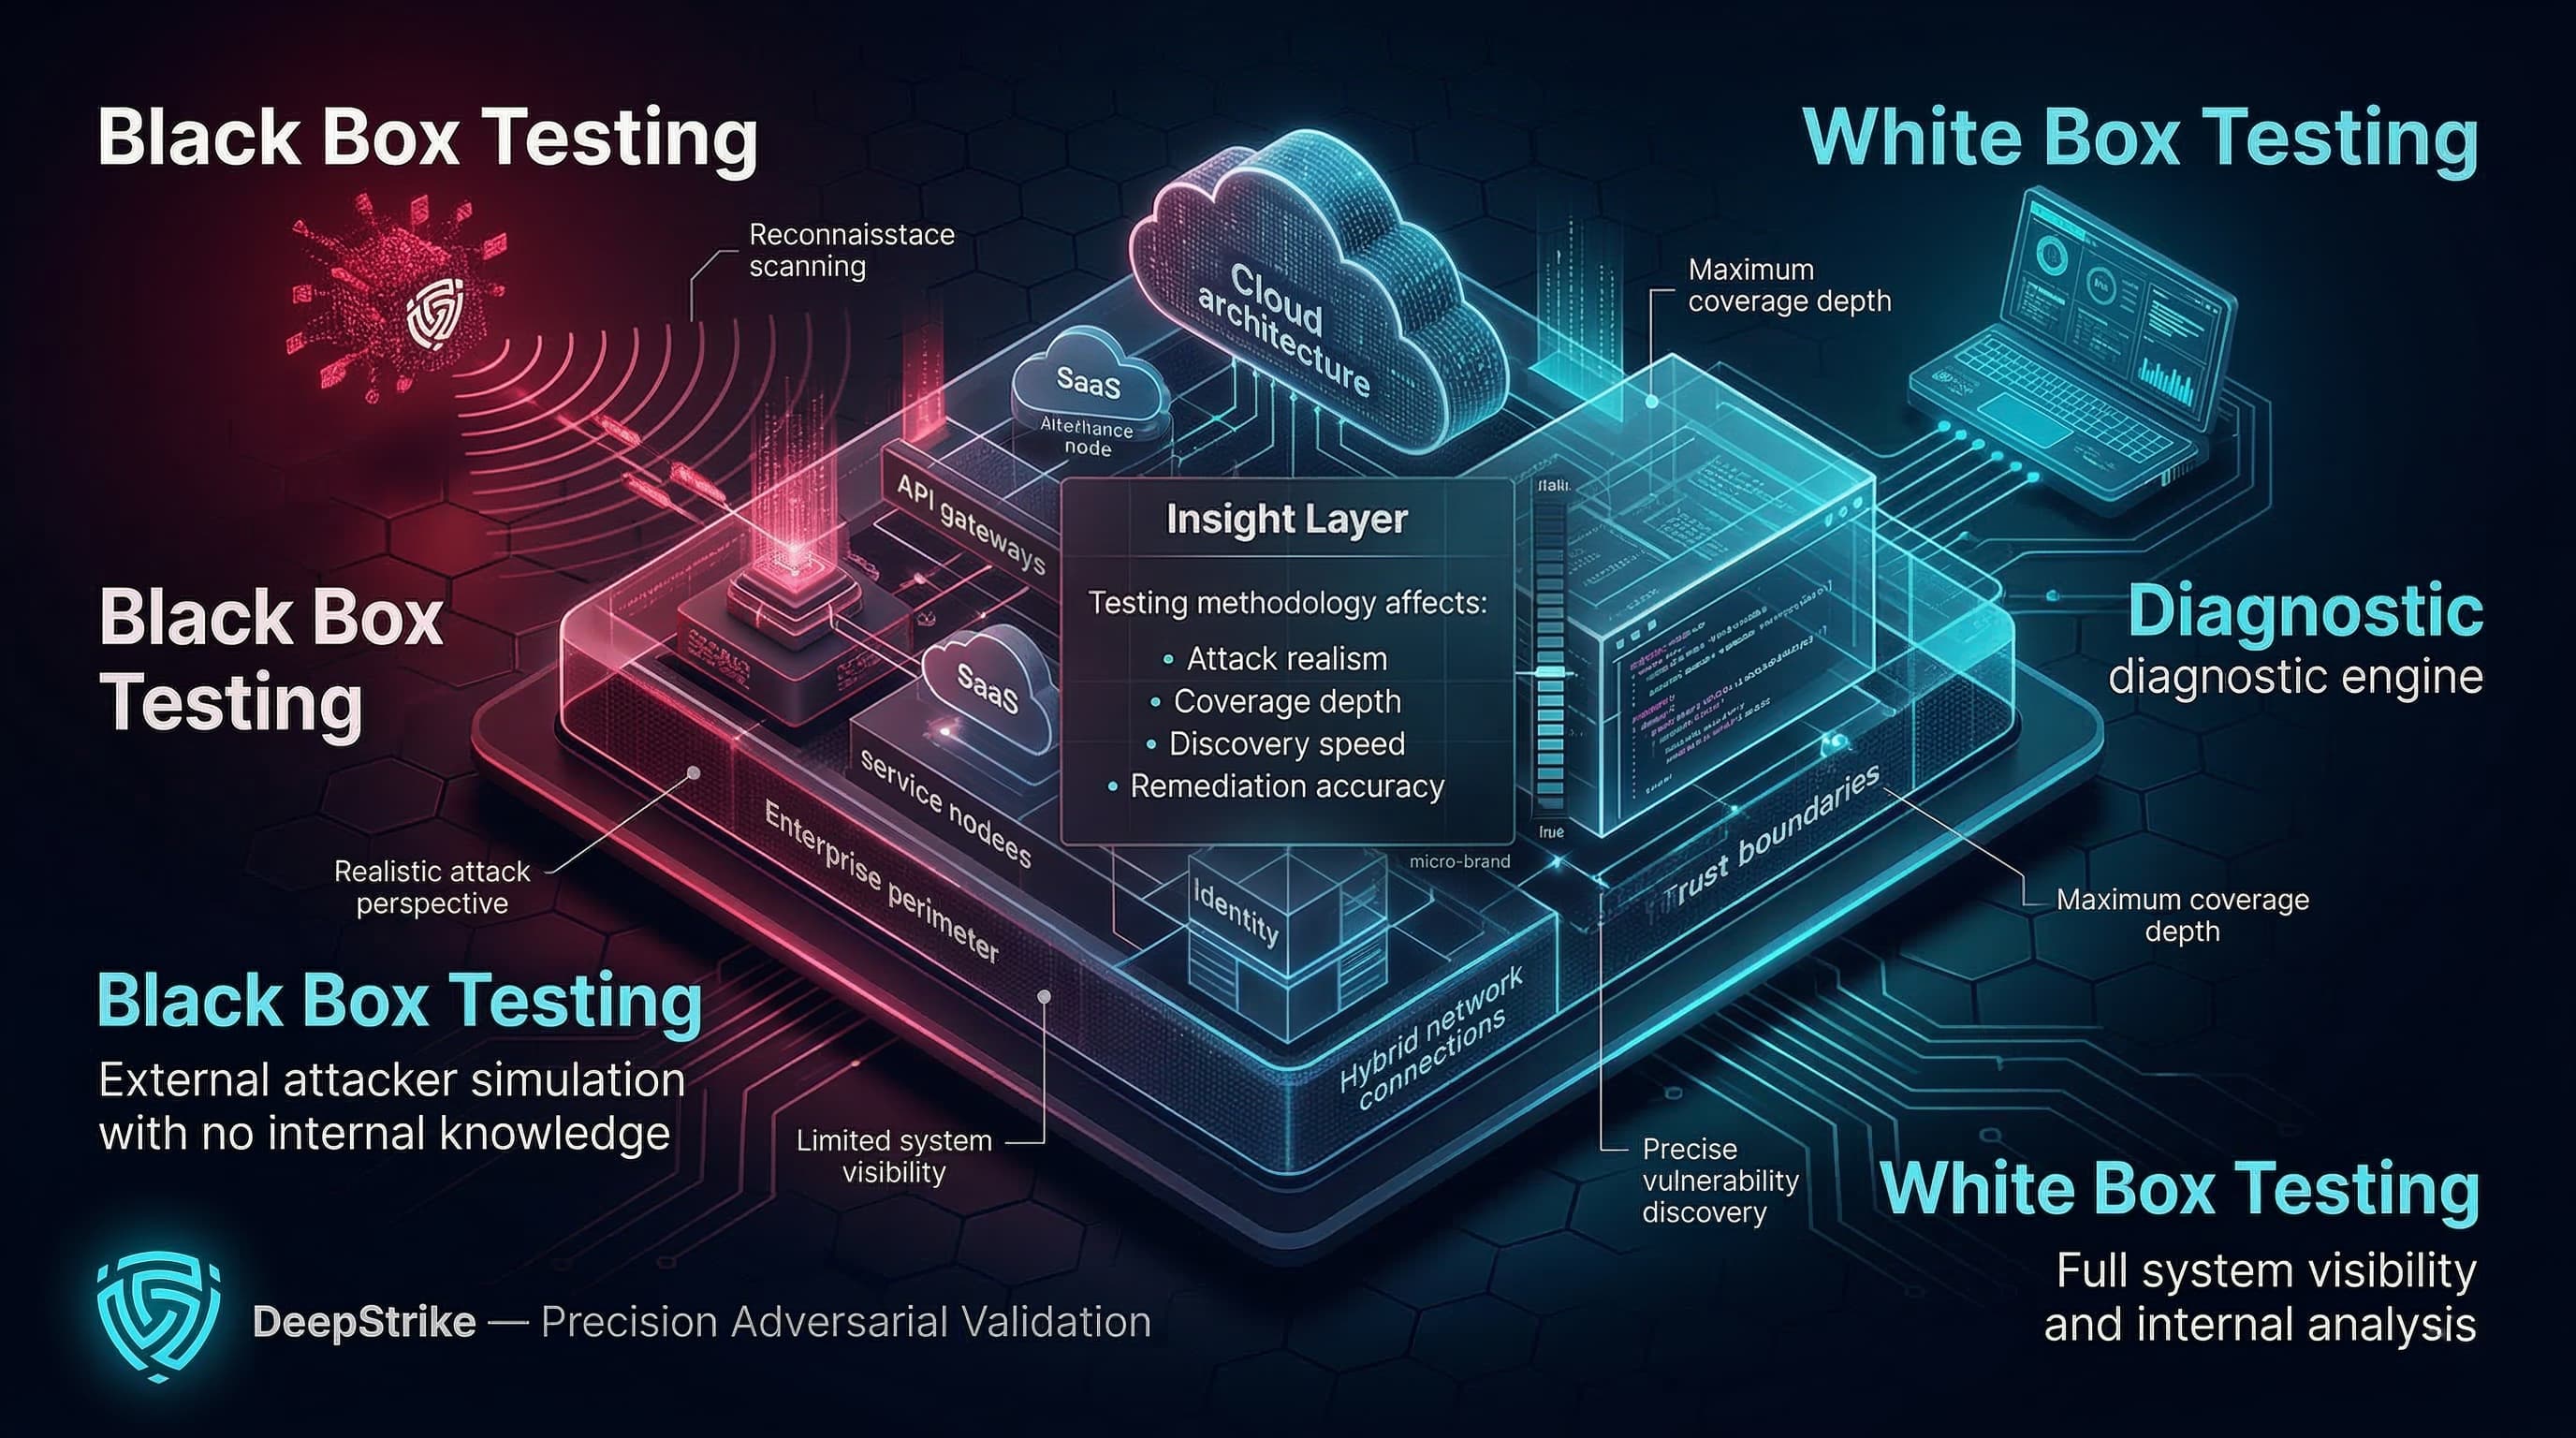
The box model you select changes the realism of attacker simulation, the depth of coverage, the speed of discovery and, most importantly, how actionable the remediation guidance is.
Modern attack surfaces are no longer a single web app behind a perimeter. They span cloud control planes, SaaS integrations, APIs, human and machine identities, hybrid networks and fast-moving delivery pipelines. Method selection should follow a clear objective and a defined assurance outcome, rather than the shortcut that "black box is realistic and white box is thorough."
This guide uses primary testing and security guidance from the National Institute of Standards and Technology (NIST), ISTQB, OWASP, the Penetration Testing Execution Standard (PTES) and MITRE ATT&CK, and maps the models to common audit and regulatory expectations. For a broader baseline on how penetration testing fits into planning, execution and reporting, see our guide on penetration testing methodology.
The same terms mean slightly different things to a QA team and to a penetration tester. Both meanings share one idea: how much of the system's internals the tester can see.
| Context | Black box means | White box means | Typical goal |
|---|---|---|---|
| Software QA | Designing tests from requirements and observable behavior, without looking at code | Designing tests from the code structure, measuring which statements and branches were exercised | Find functional defects and measure test coverage |
| Security / penetration testing | Attacking with no prior knowledge, as an outsider would | Testing with source code, architecture and documentation in hand | Find exploitable weaknesses and prove impact |
The ISTQB Certified Tester Foundation Level (CTFL) v4.0 syllabus names four common black-box techniques:
NIST's glossary notes that black box testing can be applied at virtually every level of software testing: unit, integration, system and acceptance.
White-box techniques derive tests from the code itself. The CTFL v4.0 syllabus covers two:
Stronger criteria such as condition and path coverage exist for safety-critical code, but statement and branch coverage are the common baseline. White-box testing is most often done by developers at the unit and integration level, where the code is directly visible.
Consider a sign-up form whose age field accepts 18 to 65.
That last point is where QA and security meet. The rest of this guide focuses on the security meaning: how much a penetration tester knows before the engagement starts. For how these ideas show up in application security tooling, see our comparison of SAST vs DAST vs IAST vs RASP and manual vs automated code review.
Enterprise security validation is increasingly identity-first and API-first. NIST SP 800-207 (Zero Trust Architecture) describes zero trust as a response to remote users, BYOD and cloud-based assets outside the enterprise network boundary. These trends weaken the assumptions behind network-location trust, which pushes security programs to validate access controls, authentication strength and authorization boundaries more rigorously.
The API layer keeps expanding as well. APIs expose object identifiers and actions that depend on correct object-level authorization and authentication controls. This matters for black box vs white box testing because authorization and business logic flaws are often context-dependent. The testing model determines how quickly testers can authenticate into real user roles, enumerate privilege paths and validate trust boundaries across services and integrations.
Enterprises also expect results they can act on: reproducible findings, clear exploit conditions and remediation guidance developers can apply without guesswork. This fits CISA’s Secure by Design guidance, which favors building and validating security earlier and more continuously across the product lifecycle, rather than relying only on late-stage testing.
The core definitions of black box, white box and gray box testing have not changed. The environment those models must validate has:
As a result, "black box equals realism" and "white box equals depth" is an incomplete framing. In many enterprise programs, gray box becomes the operational default for meaningful coverage of authenticated attack paths, while black and white box methods remain essential for specific objectives and control evidence.
DeepStrike's Continuous Security Testing monitors API documentation, product release change logs and GraphQL schema changes, and alerts the testing team to test new functionality as it ships, which helps catch role and permission drift between scheduled assessments.
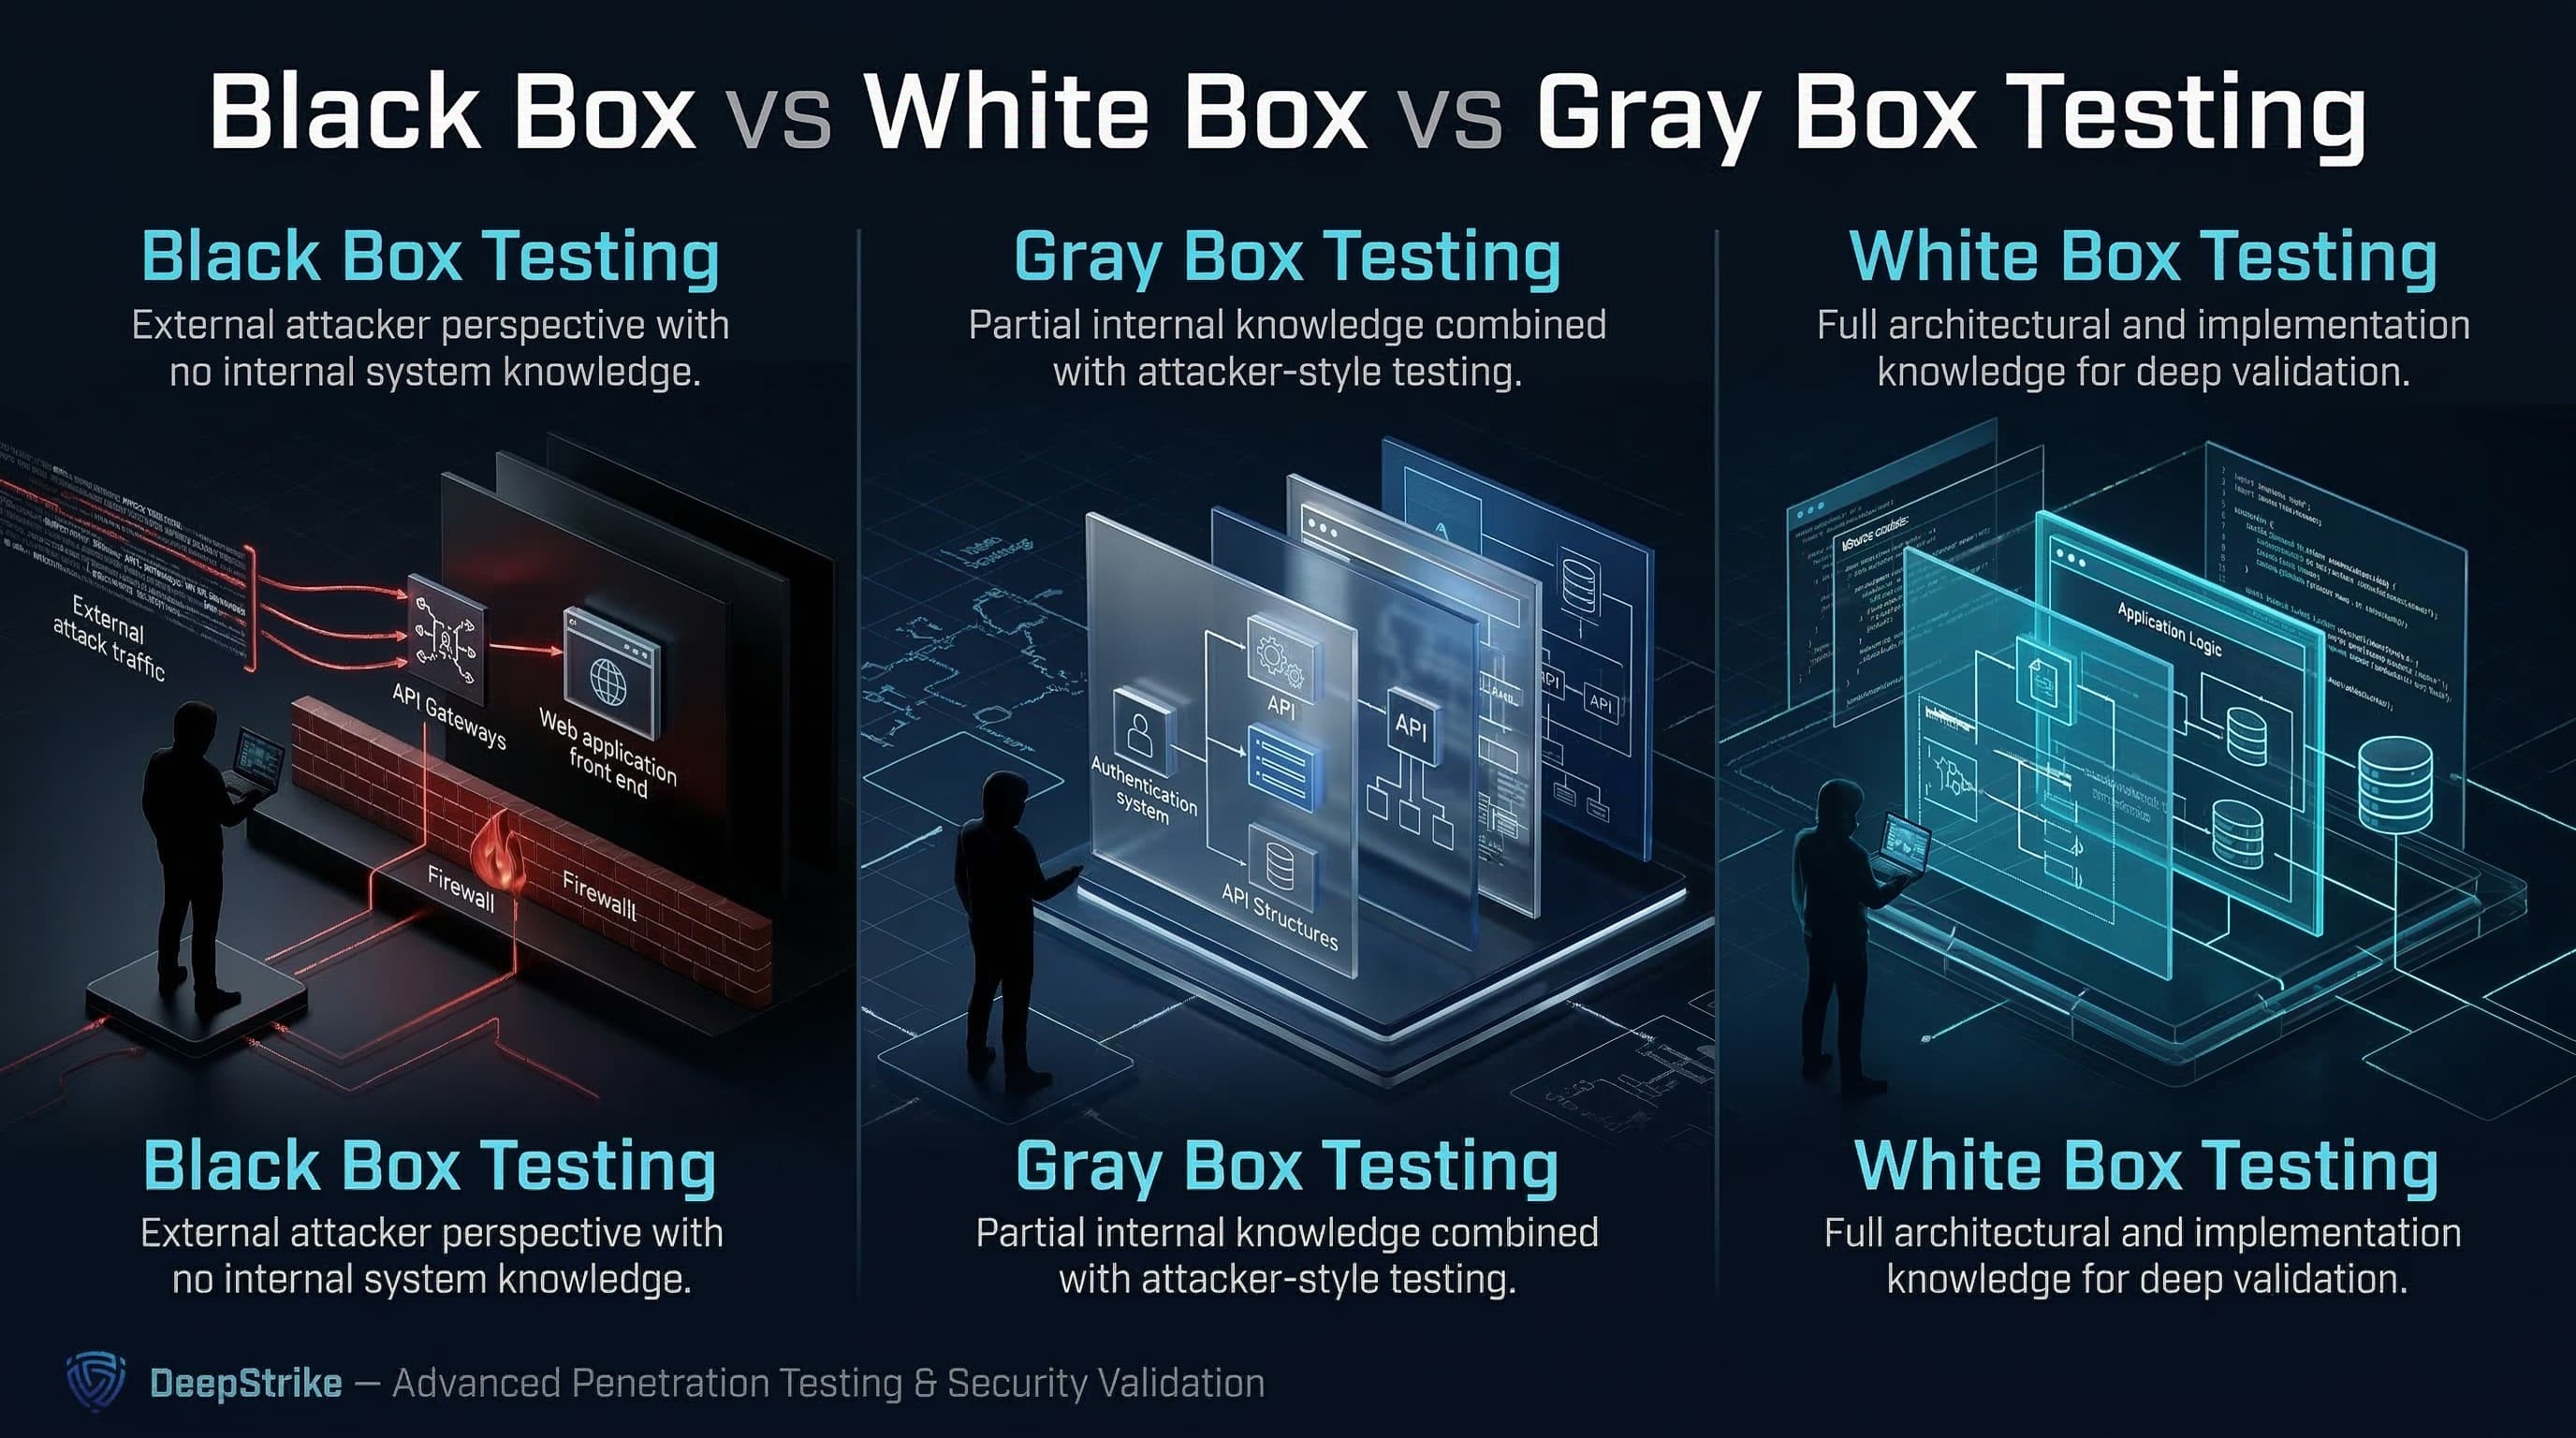
Black box penetration testing is a test methodology that assumes no knowledge of the internal structure and implementation details of the assessment object. It simulates an attacker limited to externally observable behavior and accessible interfaces.
White box penetration testing is a test methodology that assumes explicit and substantial knowledge of the internal structure and implementation details of the assessment object, such as architecture information, documentation and source code. That knowledge enables deeper and more targeted validation.
Gray box penetration testing assumes some knowledge of the internal structure and implementation details, combining partial internal context with attacker-style testing to balance realism, depth and efficiency.
These definitions follow the wording NIST uses in its glossary for black box ("basic") and white box ("comprehensive") testing.
Black box penetration testing is an authorized assessment in which the tester starts with only the agreed scope, such as a company name, a domain or an IP range, and receives no credentials, code or diagrams. It measures what an external attacker could discover and exploit, so most of the effort goes into reconnaissance and attack-surface mapping before exploitation.
Black box tests tend to under-report flaws that sit behind login. Broken object level authorization, which the OWASP API Security Top 10 2023 ranks first, usually needs at least one valid account to find, which is why black box results alone are a weak signal for authenticated applications.
Because much of the budget goes into discovery, a black box test of a large footprint in a short window trades depth for breadth. For a deeper look at the perimeter use case, see our guide to external penetration testing.
Illustrative example (not a client engagement): a software company wants to know what an outsider can reach before a funding round. In scope: the primary domain and all subdomains, the marketing site, the customer login page and two published IP ranges. Out of scope: third-party SaaS providers and denial-of-service testing. Testers receive no accounts. Expected outputs: a verified inventory of exposed assets, exploitable findings with reproducible evidence, and a list of assets that could not be tested and why.
White box penetration testing is an authorized assessment in which the tester receives full internal context: typically source code, architecture and data-flow diagrams, API specifications and accounts for every role. Testers use that knowledge to target trust boundaries and hidden code paths directly, then confirm exploitability against a running environment instead of reporting code review observations alone.
White box testing often reaches high-confidence findings faster per hour of testing because direct targeting replaces discovery, but total effort grows with the amount of code and architecture in scope. Structured threat modeling before the engagement helps focus that effort on the components that matter most.
Illustrative example (not a client engagement): a fintech team is about to release a new payments API. In scope: the API service and its authorization middleware, the OpenAPI specification, the deployment's infrastructure-as-code and IAM roles, and a staging environment with customer, support-agent and administrator accounts. Out of scope: the third-party card processor. Objectives: confirm that no role can read or modify another customer's payment records, that refund workflows cannot be abused, and that no secrets are exposed in code or configuration.
Gray box penetration testing gives the tester partial knowledge, usually accounts for selected roles and some documentation such as API specifications or high-level diagrams, but not source code. It simulates an attacker who already has a foothold, such as a compromised user account or a malicious insider, and concentrates effort on post-login attack paths and authorization boundaries.
Gray box usually spends less time on discovery than black box and avoids the code review effort of white box, which is why it is often the efficient default for authenticated applications and APIs.
Illustrative example (not a client engagement): a B2B SaaS provider needs evidence for a customer's security review. In scope: the web application and public API in a staging environment, with standard user, team administrator and read-only auditor accounts in two separate tenants, plus the API specification. Out of scope: source code and the corporate network. Objectives: prove tenant isolation, test every role transition and confirm that administrator-only API functions reject lower-privileged tokens. Our guide to penetration testing scope explains how to write these boundaries down.
The practical difference is not only how much you know. It is how that knowledge changes the path to reliable, high-impact findings.
Black box testing increases the need for discovery (reconnaissance, enumeration and trial and error). That can improve realism, but it can also lengthen time to coverage and reduce confidence that deep, role-dependent business logic was tested.
White box testing compresses discovery time and increases targeting precision. Testers can focus on critical trust boundaries, risky flows and likely failure points in design and implementation.
Gray box testing often improves practical coverage in enterprise environments. Partial internal knowledge, especially credentials and role definitions, enables direct validation of authenticated attack paths, authorization boundaries and business logic that are hard to reach in purely black box workflows.
NIST SP 800-115 states that many tests use both white box and black box techniques, and that this combination is known as gray box testing.
| Attribute | Black Box Testing | White Box Testing | Gray Box Testing |
|---|---|---|---|
| Initial knowledge | Minimal or none | Extensive (code, architecture, documentation) | Partial (credentials, diagrams, limited docs) |
| Who typically performs it | QA testers; external penetration testers | Developers and QA engineers; code-aware security testers | Penetration testers with provisioned test accounts |
| Typical test level (QA) | System and acceptance, but usable at any level | Unit and integration | Integration and system |
| Attacker realism | High for the external perspective | Lower for initial access; higher for internal chain analysis | Balanced: real attacker techniques with operational access |
| Coverage depth | Variable; often limited by discovery time | High for targeted paths and trust boundaries | High for authenticated and role-based paths |
| Testing efficiency | Lower at the start because of discovery | Higher because of direct targeting | Balanced; avoids blind discovery while keeping attacker workflows |
| Business logic visibility | Limited unless reachable through UI or API behavior | Strong (design- and code-aware validation) | Moderate to strong, especially with role context |
| Likelihood of finding chained weaknesses | Moderate; depends on time and surface visibility | High; can prioritize chainable weaknesses and hidden paths | High; often best for privilege and authorization chains |
| Best fit | External footprint: what can an outsider do? | Deep internal assurance: where are we structurally weak? | Practical enterprise validation: what can an attacker do with partial access? |
The table above mixes software QA and security attributes. This one compares the three models only as penetration testing engagements.
| Attribute | Black box pentest | Gray box pentest | White box pentest |
|---|---|---|---|
| Simulated attacker | External attacker with no foothold | Attacker with stolen credentials or a malicious insider | Well-informed attacker or insider with design knowledge |
| What the tester receives | Scope and rules of engagement only | Accounts for selected roles, API specifications, high-level notes | Source code, diagrams, API specifications, accounts for all roles, infrastructure-as-code |
| Where the effort goes | Reconnaissance and attack-surface discovery | Authenticated workflows and authorization boundaries | Targeted review of trust boundaries and code paths, then exploit validation |
| Typical findings | Exposed assets, outdated software, pre-login authentication flaws, public injection points | Object-level authorization flaws, privilege escalation, tenant isolation failures, logic abuse | Hidden endpoints, server-side validation gaps, hard-coded secrets, reachable vulnerable dependencies, IAM misconfiguration |
| Main blind spot | Flaws behind login and in internal logic | Code-level issues not visible through the running application | Realistic discovery of what an outsider can see |
| Main cost and time drivers | Footprint size, exploitation depth, defensive controls | Number of roles, tenants and workflows; quality of access | Codebase size, documentation quality, environment readiness |
| Customer preparation effort | Low | Moderate | High |
| Strongest evidence for | External exposure and independent assurance | Authenticated application and API risk, customer security reviews | Pre-release assurance, high-impact systems, technical due diligence |
Whichever model you choose, judge the result by the report: reproducible evidence, clear exploit conditions and remediation steps. Our guide to the penetration testing report explains what a useful one contains.
Well-run penetration tests follow a defined process and reporting discipline. The Penetration Testing Execution Standard (PTES) describes a seven-phase structure, from pre-engagement through reporting, and the OWASP Web Security Testing Guide references this kind of structure for penetration testing workflows. The box model influences how you execute those phases, not whether you execute them.
In a security context, black box testing emphasizes external discovery and attack-surface validation:
Black box testing is strongest at answering what is exposed and exploitable from an attacker's constrained viewpoint. It can under-test deep role-based authorization and internal misconfiguration unless time and access are expanded.
White box security validation uses internal knowledge to increase precision and depth:
White box testing is not unrealistic. It answers a different question, what is structurally wrong or fragile, and it can reduce false negatives by exposing hidden code paths and internal assumptions.
Gray box testing is deliberately hybrid:
In enterprise programs, gray box is commonly the most efficient route to validating identity-centric and authorization-centric attack paths. For practical scope in modern environments, see web application penetration testing and cloud penetration testing.
Poor scoping wastes test days whichever model you choose. Use this checklist when preparing an engagement:
| Item | Black box | Gray box | White box |
|---|---|---|---|
| In-scope targets (domains, IP ranges, apps) and exclusions | Required | Required | Required |
| Rules of engagement, testing windows and emergency contacts | Required | Required | Required |
| Test accounts for each relevant role | Not provided | Required (at least two roles to test horizontal and vertical access) | Required |
| API specifications (OpenAPI/Swagger, GraphQL schema) | Not provided | Recommended | Required |
| Architecture and data-flow diagrams | Not provided | Optional, high level | Required |
| Source code or repository access | Not provided | Not provided | Required for code-aware testing |
| Infrastructure-as-code and cloud IAM policies | Not provided | Optional | Recommended for cloud scopes |
| Known issues and previous reports | Usually withheld to keep discovery independent | Recommended, to avoid re-reporting | Recommended |
If you cannot safely share an item, say so during scoping and agree how the tester should compensate, for example by extending discovery time.
Choosing the right model is mainly an objectives-and-constraints problem: what you are trying to prove, what you can realistically provide, and what evidence you need at the end.
Black box strengths: black box testing gives the cleanest view of how exposed and exploitable your public attack surface is when the tester starts without insider knowledge. It is also useful for independent verification where internal teams may have blind spots.
Black box limitations: it can miss issues that require knowledge of hidden endpoints, conditional logic or nuanced role permissions, especially in distributed systems and APIs where the most severe flaws often sit behind authentication and data-level authorization checks.
White box strengths: white box testing supports deeper targeting and higher-confidence coverage where implementation detail matters, such as authorization rules, trust boundaries and hidden code paths. It strengthens development-stage assurance by enabling earlier and more precise defect identification, in line with secure-by-design principles.
White box limitations: it can be resource-intensive because it requires skilled reviewers and time to analyze architecture and implementation. It can also drift away from attacker realism if the engagement becomes documentation-driven without validating exploitability through realistic execution paths.
Where gray box fits best: gray box is strongest when you need both realism and depth: real attacker workflows, with enough internal context (especially credentials and role definitions) to cover the attack paths that matter in identity- and API-heavy systems.
No model is universally best. The appropriate approach depends on objectives, scope and how the system actually fails under realistic attack conditions.
Choose black box testing when:
Choose white box testing when:
Choose gray box testing when:
Do not treat cost as a proxy for value. Treat it as the result of specific drivers:
For budgeting and planning, see penetration testing cost and vulnerability assessment vs penetration testing. For programs that run more continuously, see continuous penetration testing and our comparison of PTaaS vs. traditional penetration testing.
Auditors, regulators and customers review testing through the lens of evidence, and it is rarely correct to say that one box model is universally required. Align scope, evidence and frequency to the standard first, then choose the model that produces credible validation artifacts.
PCI DSS: PCI DSS v4.0.1 Requirement 11.4 requires penetration testing against a defined methodology, covering internal and external testing and validation of segmentation controls. The PCI Security Standards Council's penetration testing guidance (an information supplement published in 2017) explains scoping and methodology. The emphasis is on a documented, repeatable methodology and meaningful validation outcomes, not the black box label. For more detail, see our PCI DSS penetration testing guide.
SOC 2: the AICPA defines SOC 2 as an examination reporting on controls relevant to security, availability, processing integrity, confidentiality or privacy, assessed against the Trust Services Criteria. SOC 2 does not prescribe a single testing method; properly scoped penetration testing is commonly used as evidence that security controls are evaluated and monitored, when aligned to the system description and risk profile. For audit alignment, see SOC 2 penetration testing requirements.
ISO/IEC 27001: the International Organization for Standardization describes ISO/IEC 27001 as defining requirements for establishing, implementing, maintaining and continually improving an information security management system (ISMS). Penetration testing can support ISO 27001 risk treatment and evidence needs, but the standard works through risk-based control selection rather than a universal requirement to test a particular way.
NIS2: the European Union Agency for Cybersecurity (ENISA) provides NIS2 technical implementation guidance to support cybersecurity risk management measures, including evidence and mappings that help entities demonstrate implementation. Many organizations treat penetration testing, often gray box for authenticated coverage, as one way to generate evidence of control effectiveness.
DORA: the Digital Operational Resilience Act (Regulation (EU) 2022/2554) has applied to EU financial entities since 17 January 2025. It requires a digital operational resilience testing program, and selected entities must carry out advanced threat-led penetration testing (TLPT). For DORA-aligned programs, the box-model discussion shifts toward how black, white and gray methods support repeatable, scoped, intelligence-informed validation rather than one-off perimeter checks.
Misconception: black box testing is always the most realistic and therefore always best.
Reality: black box is the cleanest simulation of no prior knowledge, but real attacks often include credential theft, token abuse and post-login exploitation. Gray box frequently validates these scenarios more realistically because it enables authenticated, role-based testing.
Misconception: white box testing is just code review.
Reality: code analysis can be part of white box testing, but the defining feature is substantial internal knowledge that enables deeper validation: architecture-aware targeting, trust-boundary testing and verification of security assumptions.
Misconception: white box testing is unrealistic and therefore less valuable.
Reality: white box methods are designed to reduce false negatives and increase assurance depth for high-impact systems. They answer "where are we structurally weak?" and complement black box validation focused on "what can an outsider do?"
Misconception: gray box is a compromise rather than a deliberate strategy.
Reality: NIST recognizes that combining black and white box techniques is common and calls the result gray box testing. It is often a deliberate choice to balance time, coverage and realism.
Misconception: more access always means better testing.
Reality: more access changes what you validate. If the objective is independence and external exploitability, too much context can reduce the realism of discovery. If the objective is deep assurance, too little context increases the risk of blind spots.
Black box, white box and gray box penetration testing are usually components of a broader security validation strategy, not mutually exclusive options. Many mature programs use several models across the year:
Threat-informed validation can be strengthened by mapping test objectives to adversary behaviors documented in MITRE ATT&CK, a knowledge base of tactics and techniques based on real-world observations that is widely used for threat models and testing methodologies. This helps teams test realistic behaviors rather than generic vulnerability checklists.
For organizations moving toward more continuous validation, complementary practices such as automated scanning, regression security tests and periodic deep manual testing can be combined with outcome-driven guidance that treats testing as part of maintaining security effectiveness.
Choose the model by the question you need answered. Pick black box to measure what an outsider can find and exploit, gray box to test what an attacker holding a valid account can reach, and white box to find structural weaknesses in code and design. Many mature programs rotate all three across the year instead of relying on one.
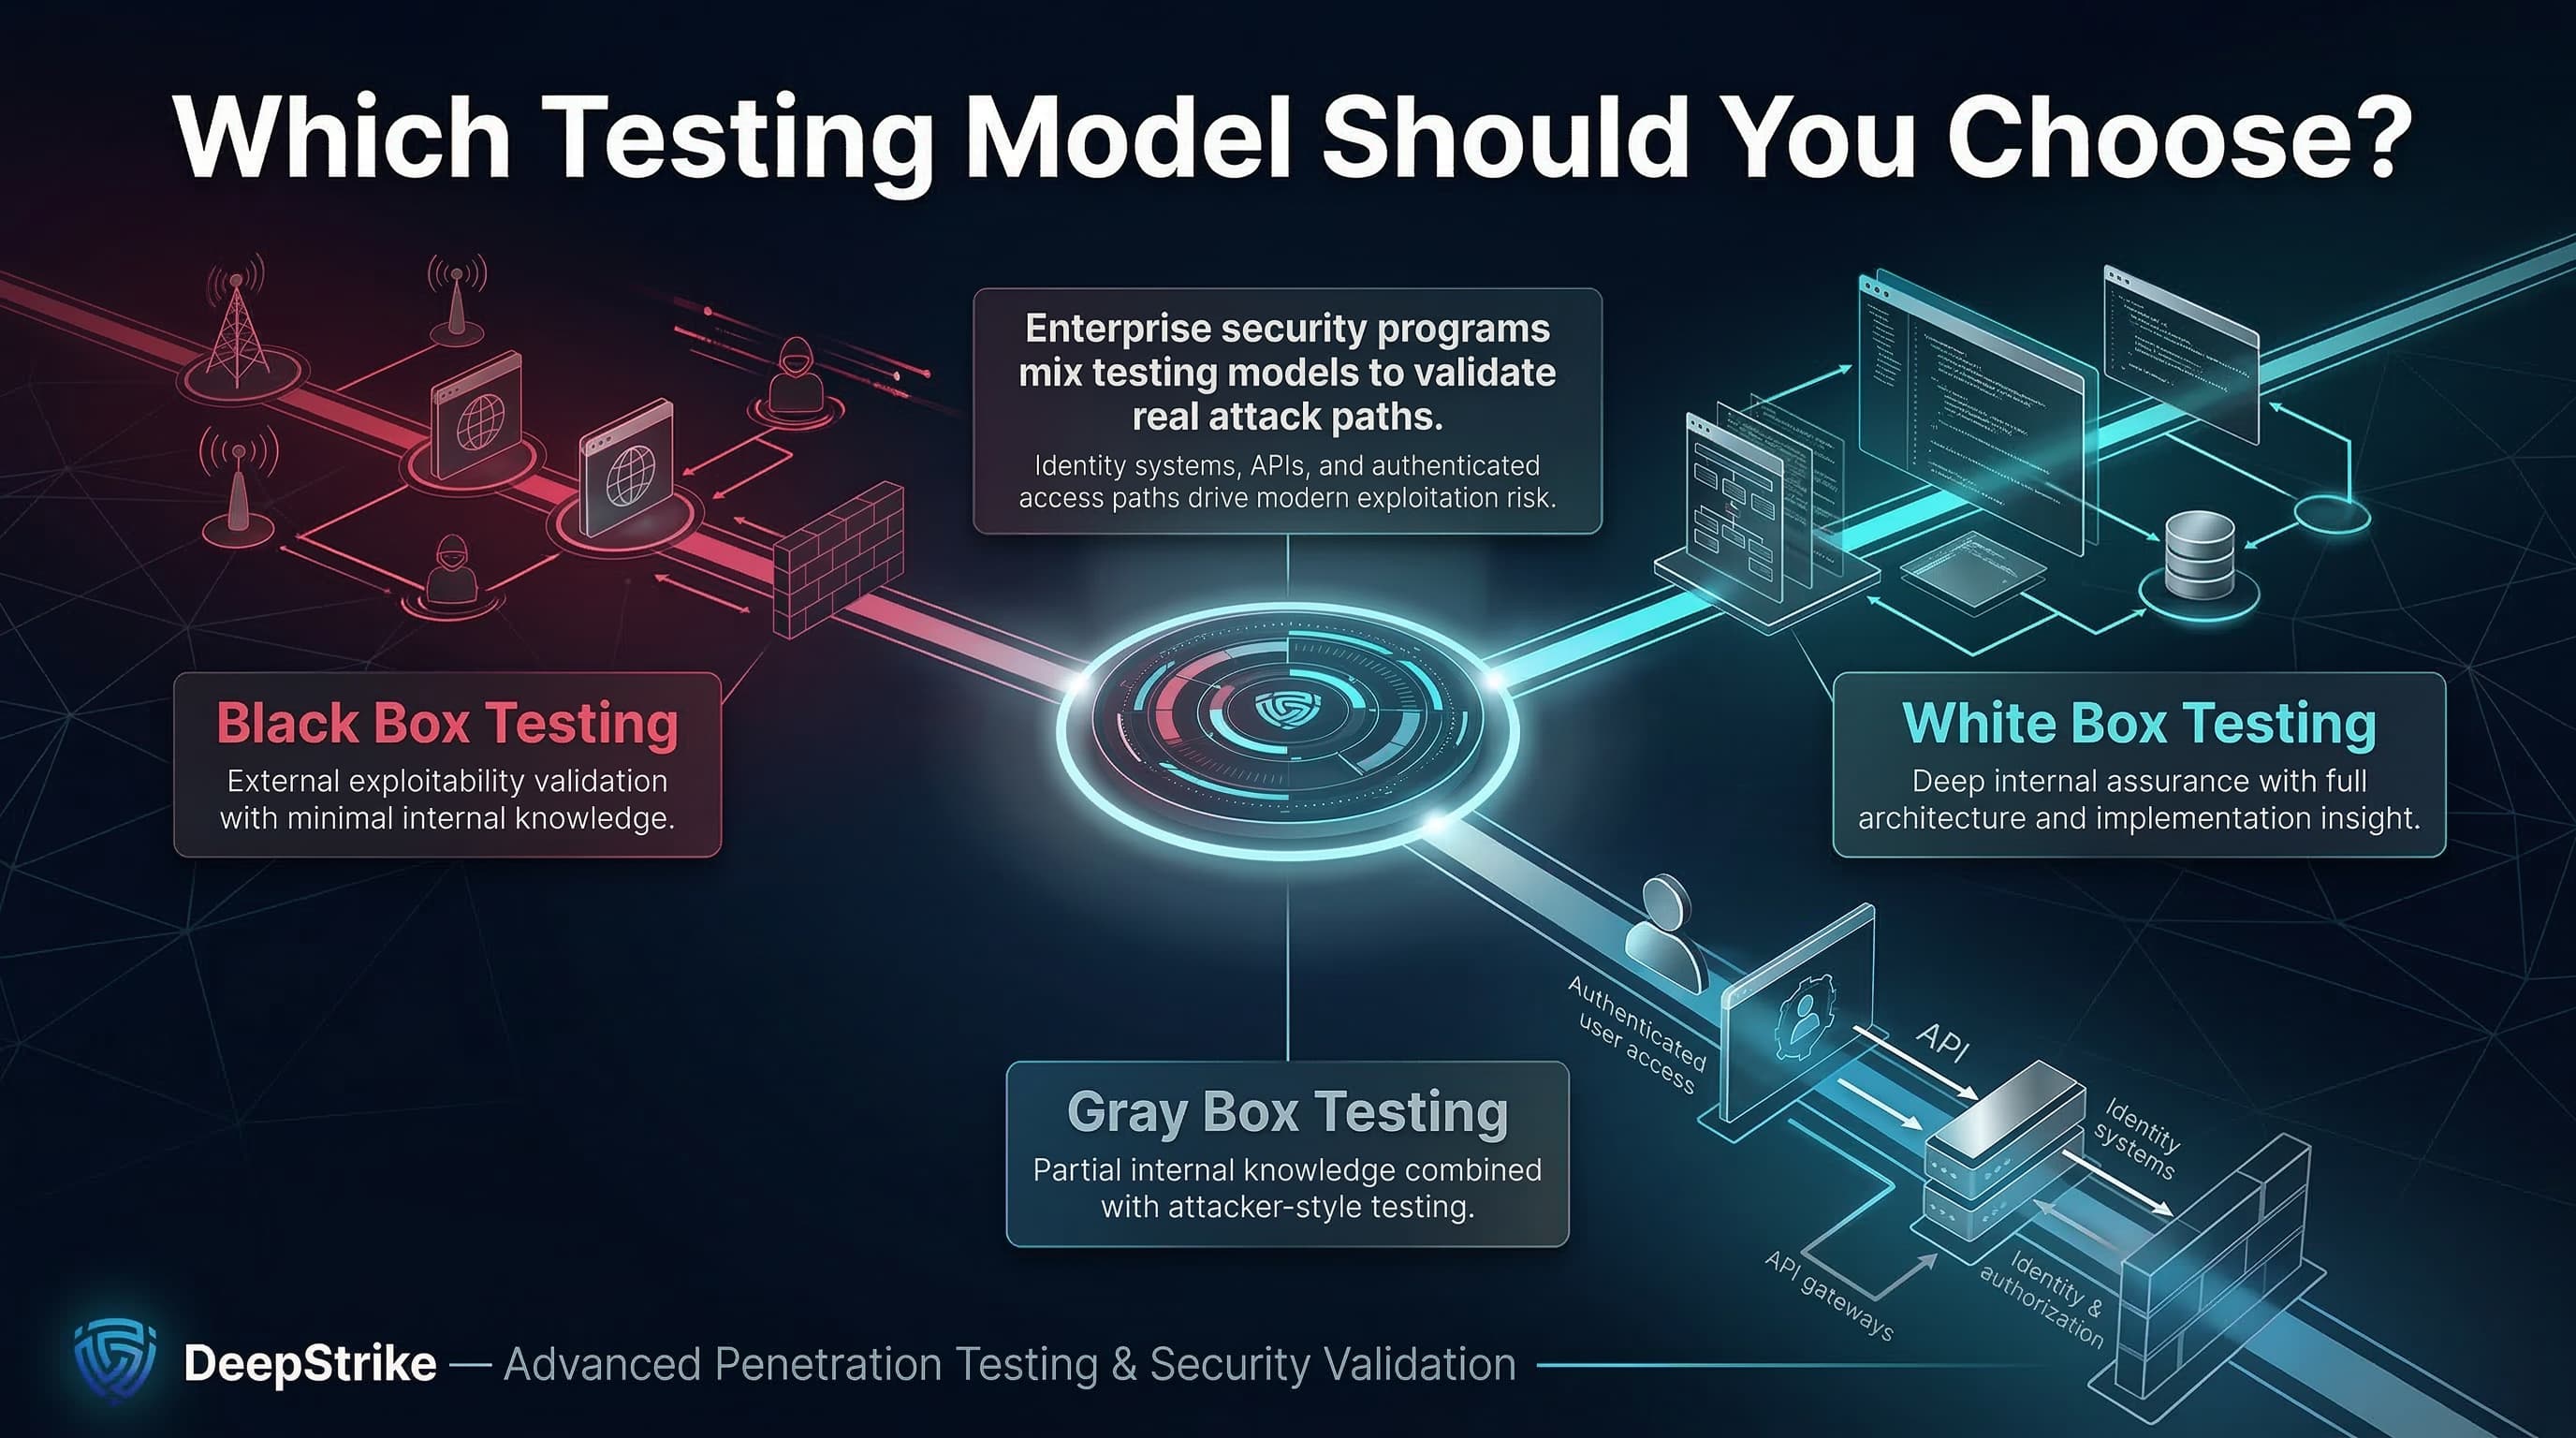
Prioritize method selection by the attack paths that matter (especially identity and authorization), the evidence required for assurance and the pace of change in your environment, then mix models over time rather than forcing one approach into every scope.
If you are ready to scope an engagement, compare options on our penetration testing services in the U.S. page or, for UK-based teams, our UK penetration testing services page.
The difference is how much internal knowledge the tester has. Black box testing assumes none and works only from external behavior; white box testing assumes substantial knowledge, including code and architecture. In QA this changes which test-design techniques you use; in penetration testing it changes discovery effort, coverage depth and how quickly high-confidence findings appear.
Black box penetration testing is a method where the tester begins with no knowledge of the target's internal structure or implementation and validates what can be discovered and exploited through externally observable interfaces. The tester typically receives only the agreed scope and rules of engagement, with no accounts, code or diagrams.
White box penetration testing is a method where the tester has substantial internal knowledge, such as architecture details and source code, enabling deeper, more targeted validation of trust boundaries and implementation paths. Findings are still confirmed against a running environment, so the result shows exploitable risk rather than a list of code review observations.
Gray box penetration testing assumes some internal knowledge, typically credentials and partial documentation, and combines black and white box techniques to balance attacker-style realism with efficient coverage of authenticated paths. It simulates an attacker who already holds a valid account, which makes it well suited to testing authorization and business logic.
Neither is universally better. Black box is better for external realism and independent discovery; white box is better for deep assurance and implementation-driven risk. The correct choice depends on objective, scope and evidence needs. If authenticated workflows and APIs carry most of your risk, gray box is often the practical middle ground.
Choose gray box testing when post-login workflows, role permissions, business logic and authorization boundaries are central to risk, and you need reliable coverage without spending most of the engagement on blind discovery. Typical cases include multi-tenant SaaS platforms, customer portals and APIs where one user must never reach another user's data.
White box can be more effective for internal assurance because it enables targeted testing of hidden paths and trust boundaries. Black box can be more effective for validating external exploitability and discovery realism. Effectiveness depends on the question you need answered, so judge each model against its objective rather than by the number of findings.
Compliance rarely requires a single box model. It requires credible scope, repeatable methodology and evidence that controls were evaluated appropriately. Many enterprise programs mix models across the year to satisfy both external realism and internal assurance evidence needs. Confirm the expected scope and method with your auditor or assessor before the engagement starts.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
