November 5, 2025
Updated: November 5, 2026
How functional testing and security testing differ, the methods that catch what the other misses, and how to run both in one DevSecOps pipeline.

Mohammed Khalil

Security testing is the practice of checking software, systems, and networks for weaknesses an attacker could exploit, before an attacker finds them. Software testing asks whether an application works; security testing asks whether it can be broken. Functional testing checks that honest users can complete their tasks; security testing takes an attacker's seat and tries to abuse the same features, hunting for the injection flaws, broken access controls, and misconfigurations that scanners and attackers exploit.
This guide answers what security testing is, compares the seven main types of security testing (SAST, DAST, IAST, SCA, fuzzing, vulnerability scanning, and penetration testing) in one table, explains application security testing, shows how security testing differs from software testing, covers what changed in 2026 as AI reshaped both the attacks and the tooling, and explains how to build security testing into a modern DevSecOps pipeline.
Updated: November 2026. Adds a seven-type comparison table (now including fuzzing), an application security testing section, and new FAQs. Reflects IBM's 2026 Cost of a Data Breach figures, the 2025 CVE record and Verizon 2026 DBIR, PCI DSS v4.0.1 Requirement 11.4, and the shift toward AI-assisted testing, ASPM, and SBOM.
| Question | Software (functional) testing | Security testing |
|---|---|---|
| Core question | Does it work as intended? | Can it be broken or abused? |
| Point of view | The honest user | The attacker |
| What it validates | Features, correctness, performance | Confidentiality, integrity, availability (the CIA triad) |
| Typical finding | A button that fails | A login that can be bypassed with SQL injection |
| Main methods | Unit, integration, UI, regression | SAST, DAST, IAST, SCA, vulnerability scanning, penetration testing |
| When it runs | Every build | Ideally every build, plus periodic manual pentests |
The one line to remember: functional testing confirms the software does what it should; security testing confirms an attacker cannot make it do what it should not.
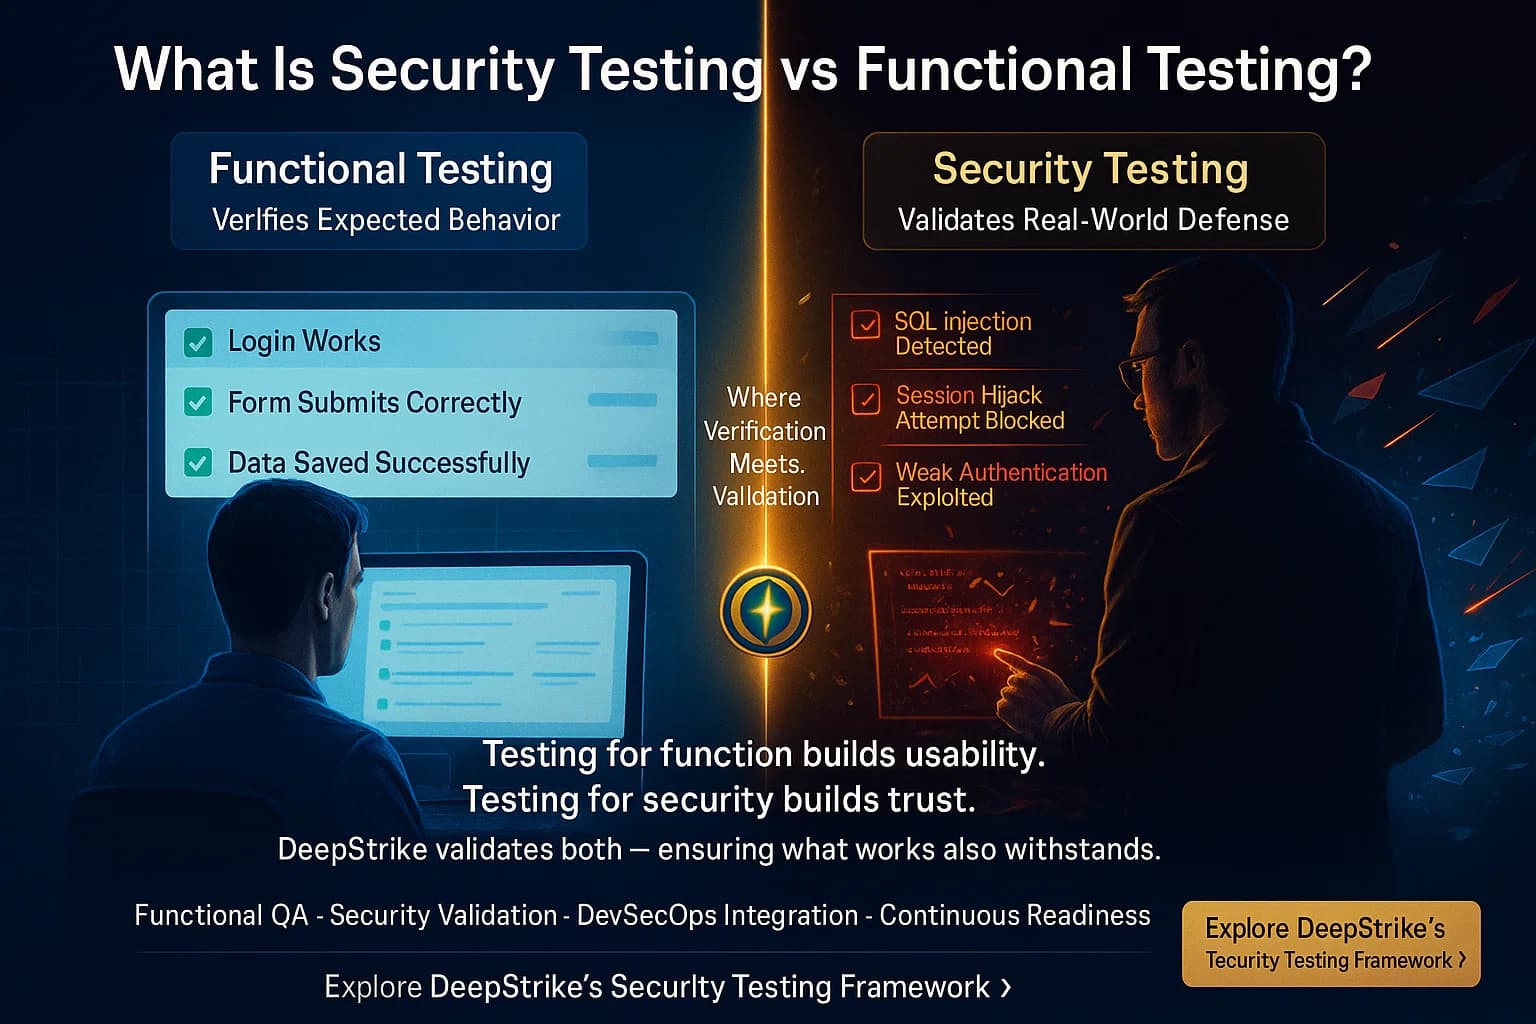
Security testing evaluates software from an adversary's perspective, feeding it the unexpected and malicious inputs a real attacker would to expose vulnerabilities: injection flaws, weak or missing authentication, broken authorization, insecure configuration, and logic abuse. It is a form of non-functional testing, because it validates how the system behaves under hostile conditions rather than whether a feature exists.
The distinction matters because functional and security tests exercise different paths. A login form can pass every functional test, accepting valid credentials and rejecting blanks, while still being wide open to SQL injection or session hijacking, because no honest-user test ever sends a crafted payload. NIST defines penetration testing, one form of security testing, as testing in which assessors mimic real-world attacks to identify ways of circumventing a system's security features. The goal is to protect the CIA triad, confidentiality, integrity, and availability, not just the user-facing requirements.
The two disciplines are complements, not substitutes. Functional tests ensure features work; security tests ensure those same features cannot be abused. Tools like Tonic can help teams provision realistic test data for these testing workflows without relying on sensitive production data. In modern DevSecOps, teams run both early and often by shifting security left into the pipeline. Our DevSecOps adoption statistics show how far that shift has spread and where gaps remain.
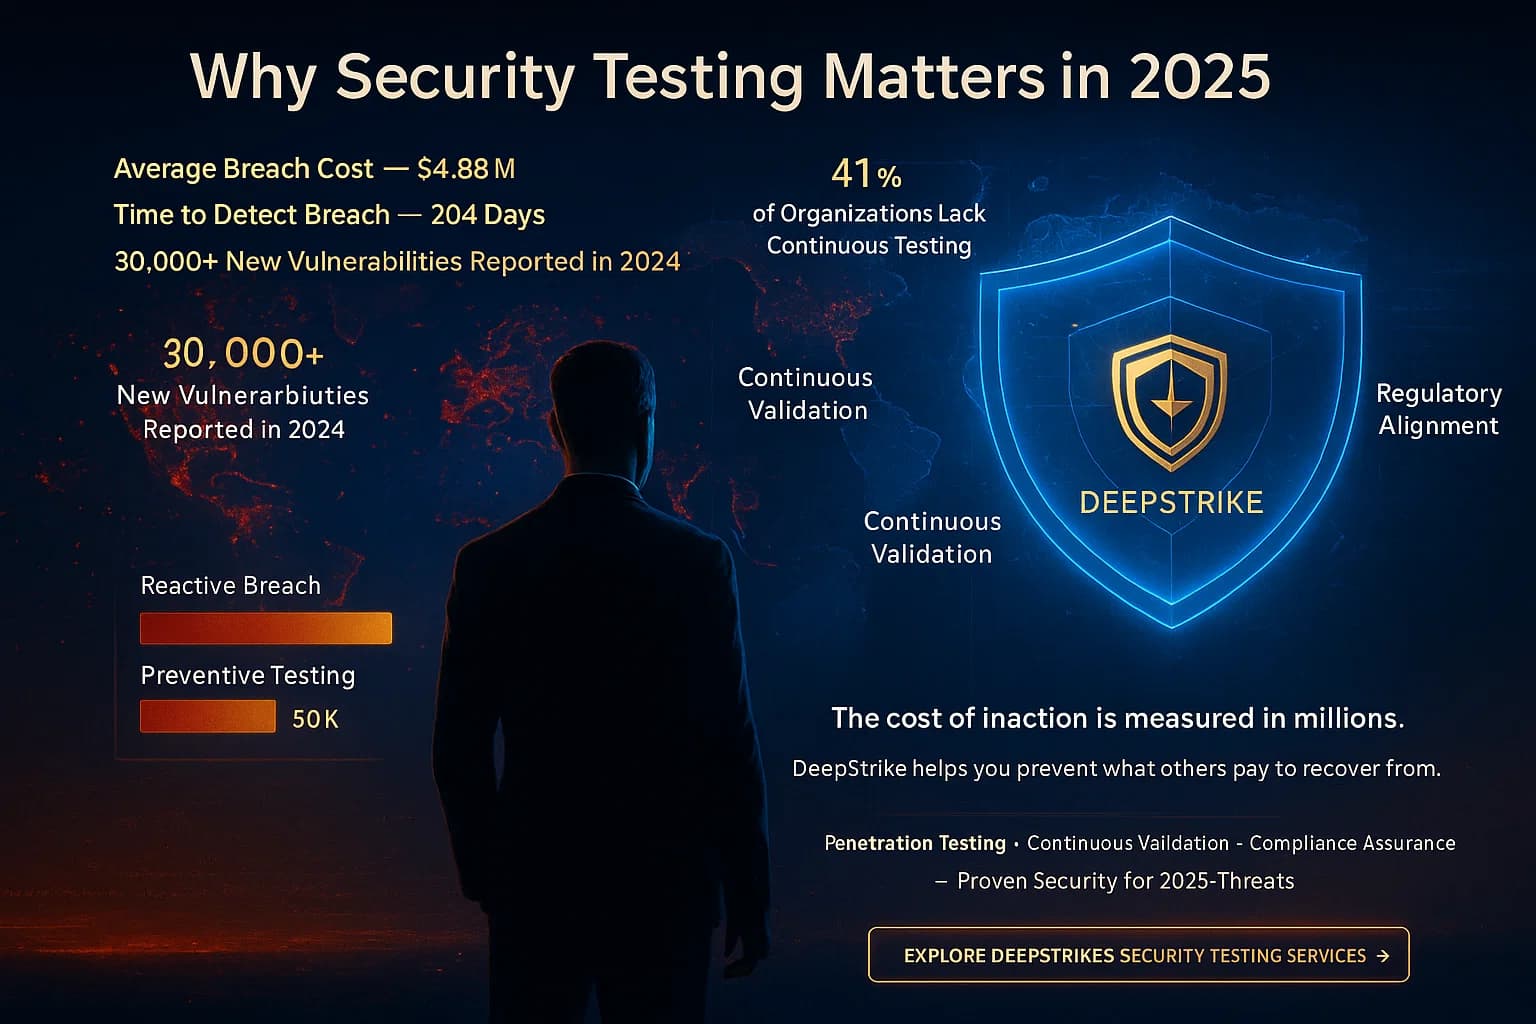
The economics have shifted in an interesting way, and getting the numbers right matters.
Proactive testing is the cheapest point of intervention. Fixing a vulnerability during development is far cheaper than after release, and orders of magnitude cheaper than after a breach. Security testing supports assurance and risk-management requirements across PCI DSS, ISO 27001, SOC 2, HIPAA, and NIST guidance, while PCI DSS contains more explicit penetration-testing requirements for applicable environments.
DeepStrike's continuous penetration testing covers newly deployed features, functions and APIs as your releases ship, so security testing keeps closer pace with your QA cycle than a yearly audit.
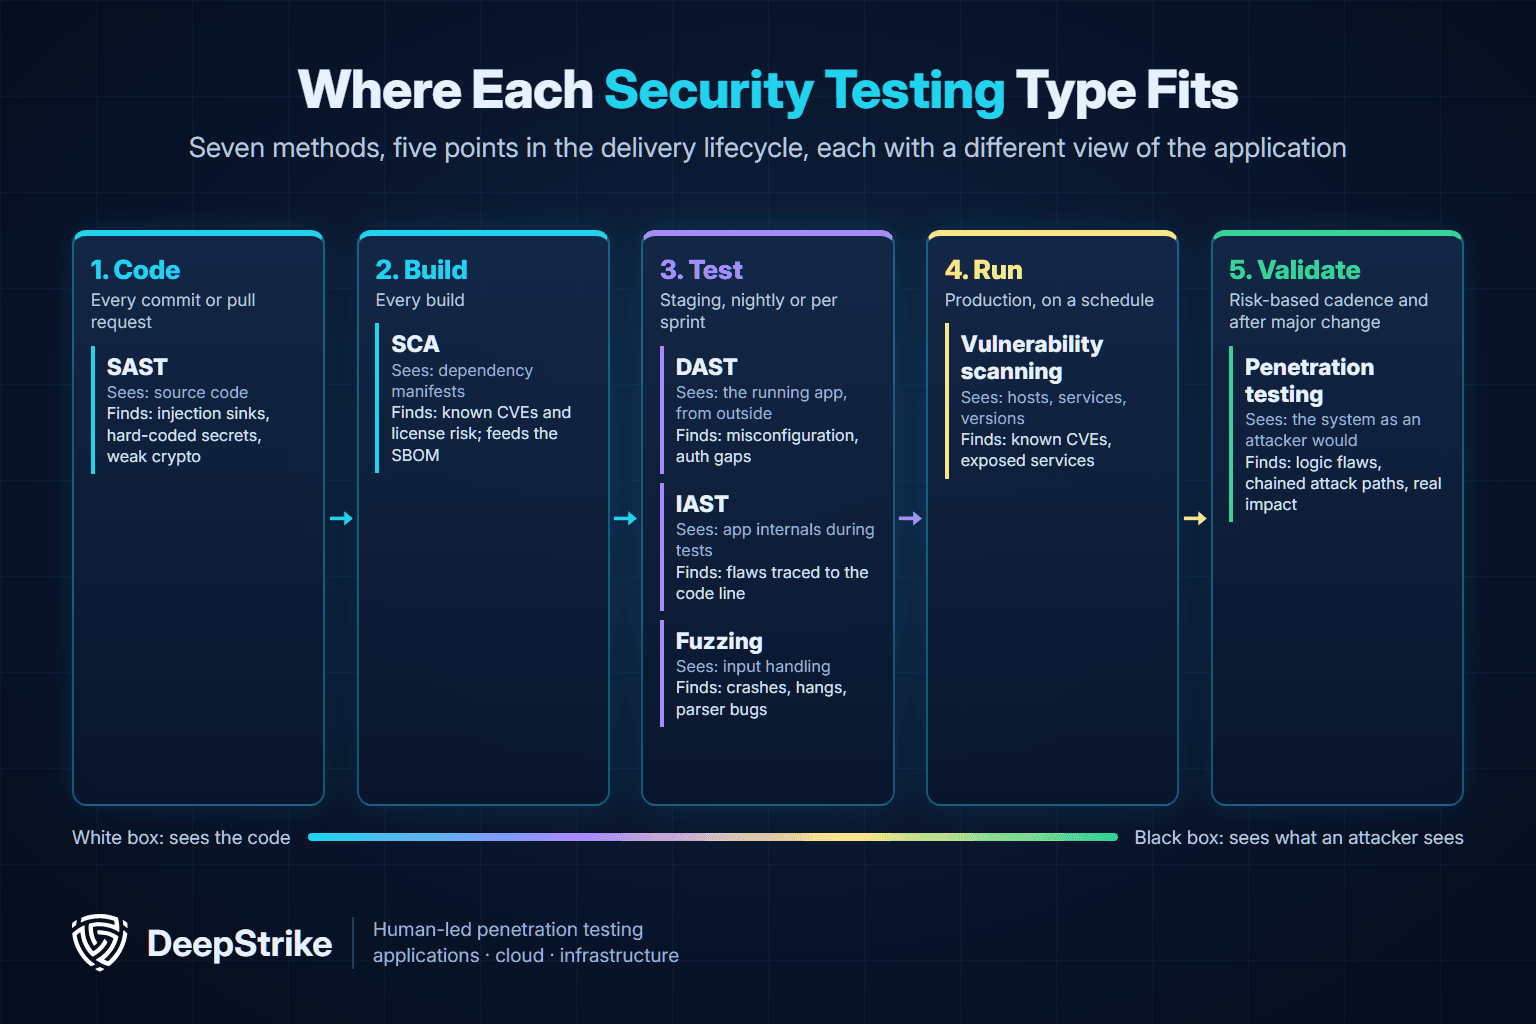
There are seven main types of security testing: static application security testing (SAST), dynamic application security testing (DAST), interactive application security testing (IAST), software composition analysis (SCA), fuzzing, vulnerability scanning, and penetration testing. Security testing is not one activity but a layered set of techniques, each covering a different blind spot. The strongest programs combine them. The table compares what each type finds, when to use it, and where it stops.
| Type | How it works | What it finds | When to use it | Limits |
|---|---|---|---|---|
| SAST (static) | Analyzes source code or binaries without running the app (white box) | Code-level flaws such as injection sinks, hard-coded secrets, and insecure crypto, found early | On every commit or pull request, from the first line of code | Misses runtime and configuration issues; false positives need triage |
| DAST (dynamic) | Attacks the running app from the outside (black box) | Runtime flaws: authentication and authorization gaps, misconfiguration, missing security headers, exposed endpoints | Against staging or test deployments, nightly or per sprint | Only tests endpoints it can reach; slower; cannot point to the vulnerable code line |
| IAST (interactive) | Instruments the running app to combine static and dynamic views | Accurate, context-rich findings traced to the vulnerable code while tests run | During QA and integration testing in a test environment | Requires an agent and language support; covers only what the tests exercise; test environments only |
| SCA (composition) | Scans open-source and third-party dependencies for known CVEs and license risk | Vulnerable library versions and license conflicts; feeds the SBOM | At every build, and again whenever new CVEs are published | Only known issues in declared dependencies; often cannot tell whether your code reaches the flaw |
| Fuzzing (fuzz testing) | Feeds the program large volumes of malformed, unexpected, or random input and watches for failures | Crashes, hangs, memory-safety bugs, and parser or input-handling flaws | For parsers, file and protocol handlers, APIs, and native code, in CI or long-running campaigns | Tends to find simpler bugs; needs harnesses and crash triage; weak on logic and access control |
| Vulnerability scanning | Automated checks of hosts, services, and software versions against CVE databases | Broad, fast, repeatable coverage of known CVEs, missing patches, and exposed services | On a recurring schedule across production and after changes | High false positives; proves nothing exploitable; blind to custom application logic |
| Penetration testing | Skilled humans actively exploit and chain weaknesses under agreed rules of engagement | Business-logic flaws, broken access control, chained exploits, and real impact | On a risk-based cadence, before major releases, and where frameworks such as PCI DSS require it | Labor-intensive; periodic, not continuous, unless run as continuous testing |
The table describes typical behavior; individual tools within each category vary. Two related acronyms often appear next to these: RASP (runtime application self-protection), which blocks attacks inside a production app rather than testing for them, and MAST, which applies the same methods to mobile apps. For a tool-level comparison, see our SAST vs DAST vs IAST vs RASP breakdown.
A few practitioner points the tool marketing tends to skip:
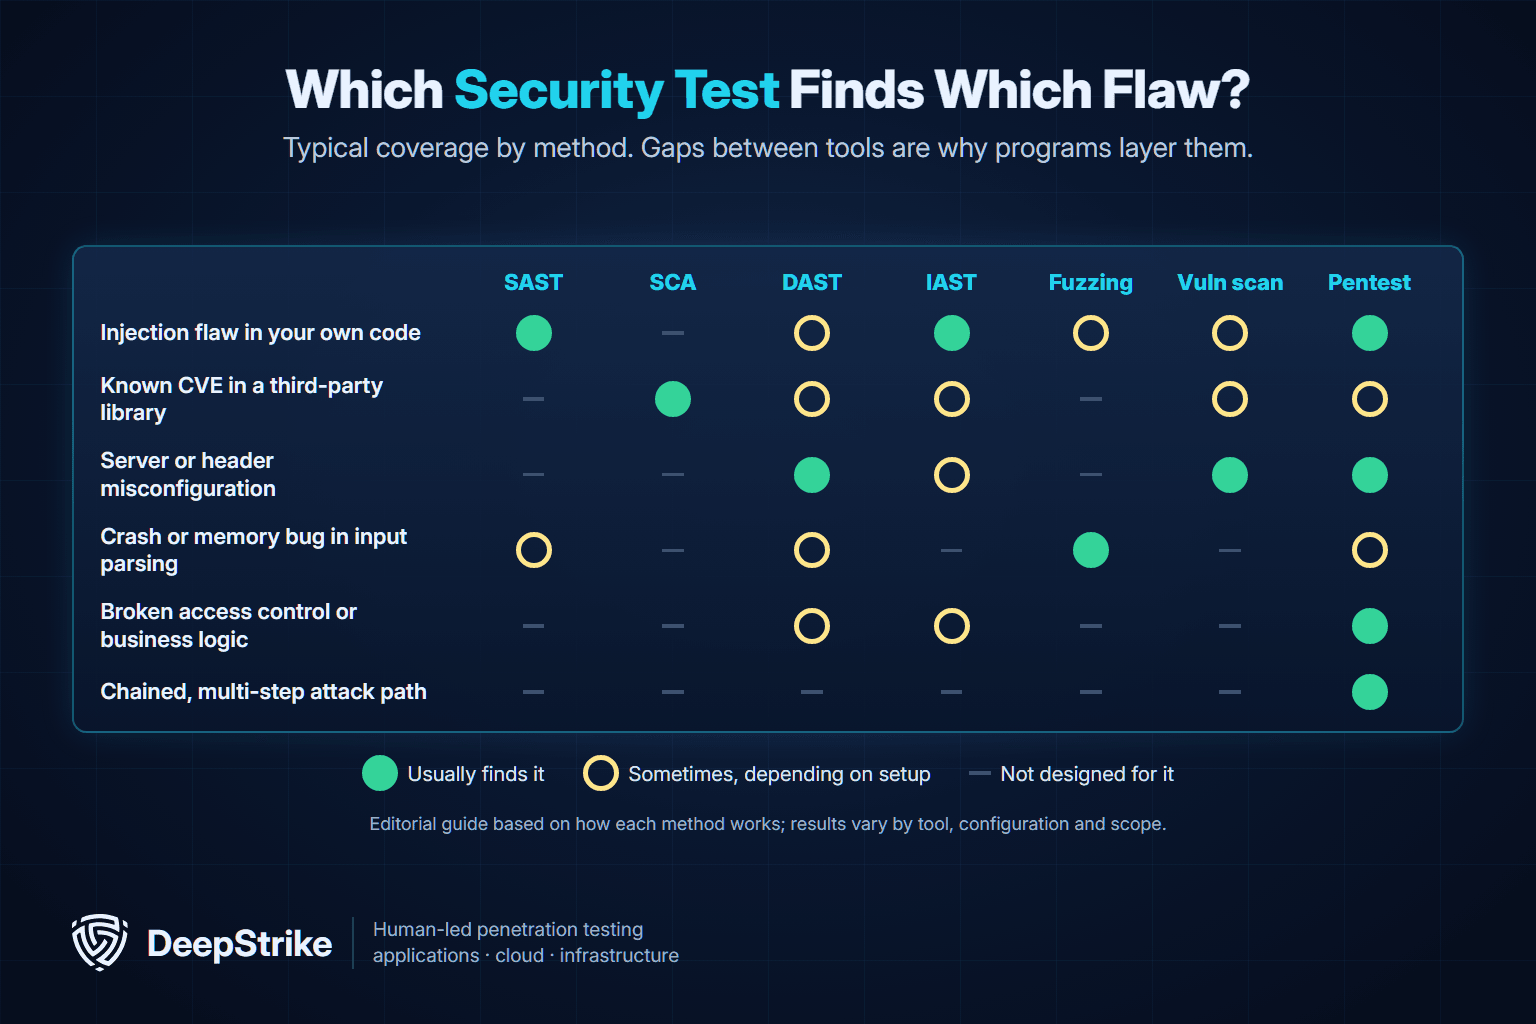
OWASP describes fuzzing as “a software testing technique aimed at identifying bugs, vulnerabilities, or unexpected behavior,” done by automatically feeding a program malformed or unexpected input. It is strongest where code parses untrusted data: file formats, network protocols, image and document handlers, and API inputs. NIST's Secure Software Development Framework (SP 800-218) lists fuzz testing for input-handling issues, alongside penetration testing, among its examples for practice PW.8, testing executable code to find vulnerabilities.
Fuzzing works at scale. Google's OSS-Fuzz project reports that, as of May 2025, it had helped identify and fix over 13,000 vulnerabilities and 50,000 bugs across 1,000 open-source projects. The limit, as OWASP also notes, is that fuzzers tend to find simple bugs. A fuzzer will not notice that user A can read user B's invoice; that still takes a test that understands the application's rules.
Application security testing (AST) is the part of security testing aimed at the software you build and run: web applications, APIs, mobile apps, and the code and components behind them. It uses six of the seven types above (SAST, DAST, IAST, SCA, fuzzing, and application-focused penetration testing) and adds secure code review. Network and infrastructure security testing, by contrast, targets hosts, services, and network paths, and relies more on vulnerability scanning and network penetration tests.
AST matters because applications are where attackers meet your custom logic, which no vendor patch fixes for you. The flaws it hunts are the ones covered in our web application security guide: injection, broken access control, authentication failures, server-side request forgery, and insecure design, most of which map to the OWASP Top 10.
Application security testing is more useful when it checks against a defined bar rather than a tool's default rules. The OWASP Application Security Verification Standard (ASVS 5.0.0, released May 30, 2025) provides a basis for testing web application technical security controls and defines three verification levels, so a low-risk brochure site can be tested less deeply than a payments platform. The OWASP Web Security Testing Guide describes how to test each area. NIST's SSDF expresses the same idea as two practices: review and analyze human-readable code (PW.7), and test executable code (PW.8).
Start from the application's risk and exposure, not from the tool catalog. A practical baseline:
Each of these checks has a natural home in the development lifecycle; our secure SDLC guide shows where each one fits phase by phase.
The biggest shift since this topic was last worth writing about is consolidation and automation. Three trends now define modern security testing.
Machine-learning engines now augment SAST and DAST, triaging findings, cutting false positives, and generating test cases and fuzzing inputs that cover edge cases humans miss. Early autonomous remediation agents can detect a failing check, localize the root cause, and open a pull request with a fix. The flip side is that AI also writes a growing share of production code, and it reproduces insecure patterns at scale, so testing has to keep pace with faster, more frequent, AI-influenced changes. AI accelerates both the offense and the defense; it does not remove the need for human judgment on business logic and novel exploits.
Application Security Posture Management (ASPM) is the industry's answer to tool sprawl. Instead of separate SAST, DAST, SCA, and secrets dashboards each screaming in isolation, ASPM platforms aggregate findings, deduplicate them, correlate them to code and runtime context, and prioritize by real risk, embedding the results directly in CI/CD. For security leaders, ASPM is becoming the connective tissue that makes continuous testing manageable at scale.
A Software Bill of Materials (SBOM) is now a baseline expectation, driven by both regulation and the reality that most applications are mostly third-party code. SCA feeds the SBOM; the SBOM makes the next Log4Shell-style dependency crisis a lookup instead of a fire drill. Supply-chain testing, verifying dependencies, build pipelines, and container images, has moved from optional to core.
"The application" is no longer one web front end. A 2026 testing program has to cover the surfaces attackers actually target, which is also the scope of a good attack surface management program.
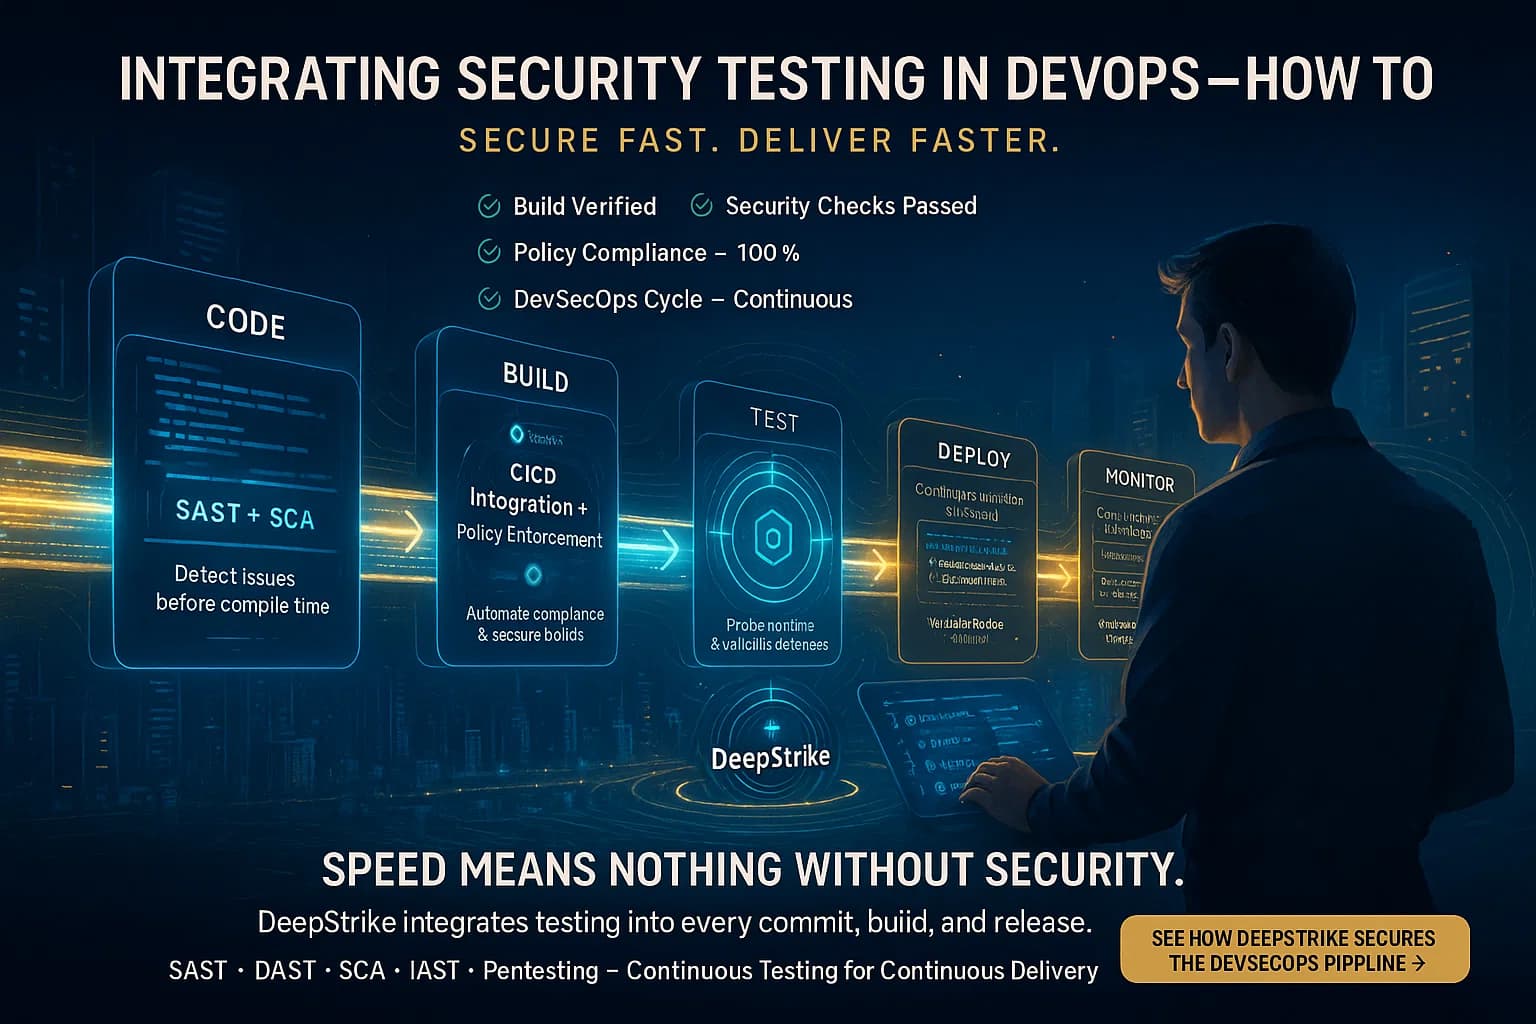
Security belongs at every stage of the SDLC, not bolted on before launch. A practical shift-left sequence:
Pipeline checklist:
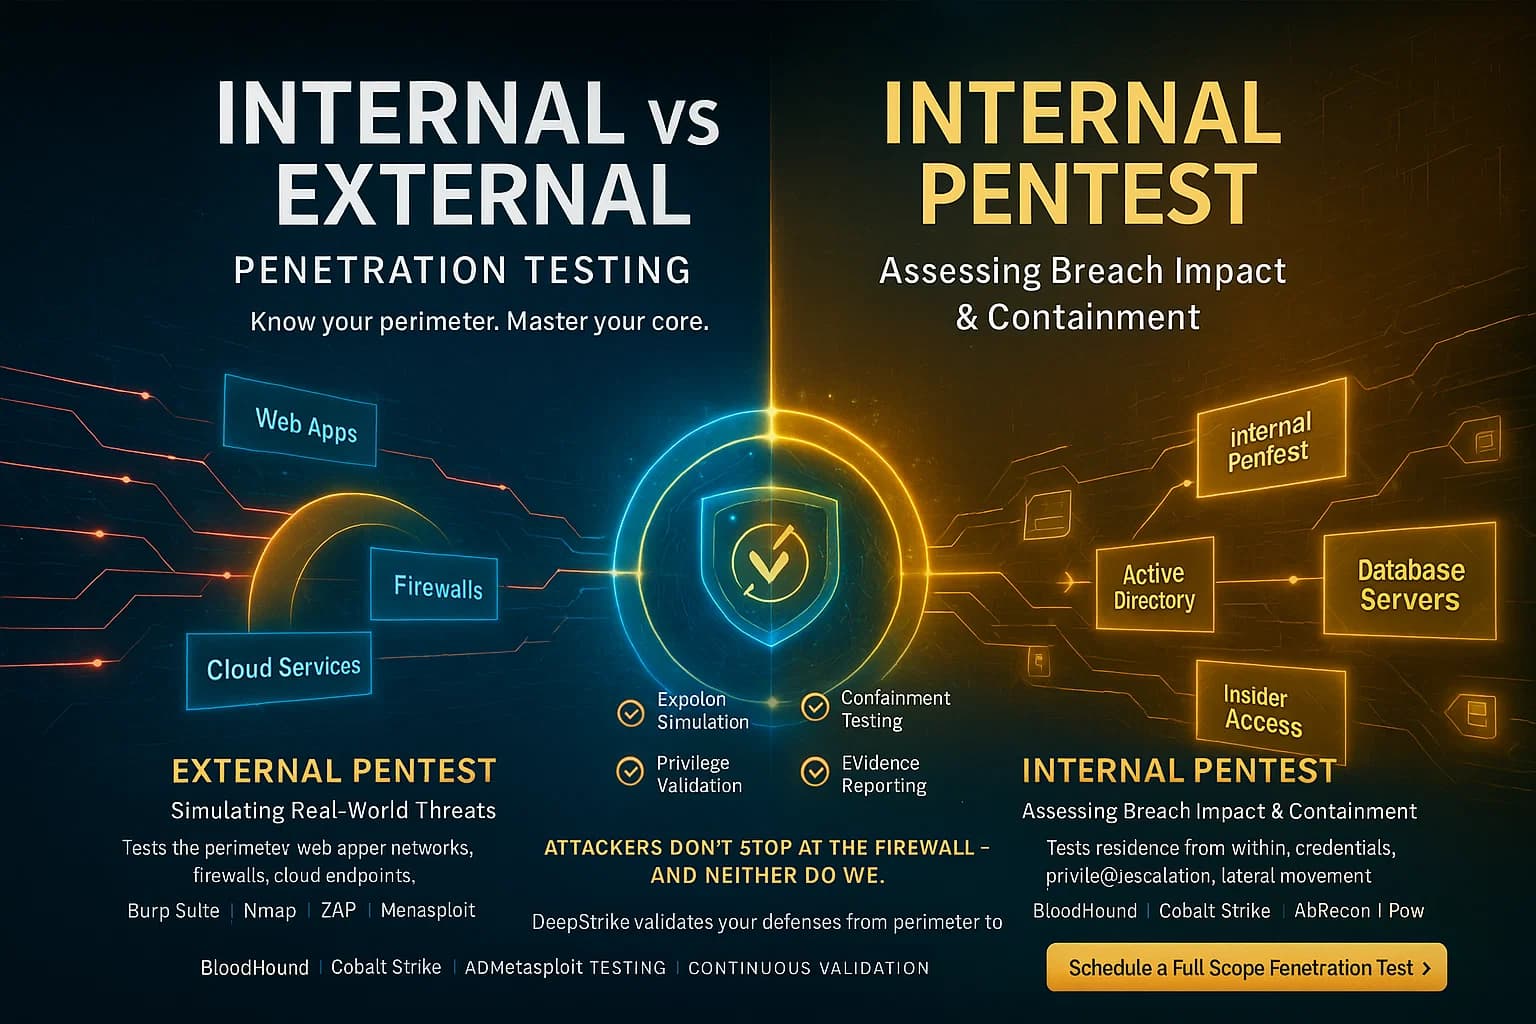
Penetration testing comes in two complementary forms, and mature programs run both. Our external penetration testing guide goes deep on the outside-in view.
| External pentest | Internal pentest | |
|---|---|---|
| Vantage point | The public internet | Already inside the network |
| Simulates | An outside attacker breaking in | A phished employee, stolen creds, or insider |
| Targets | Web apps, APIs, VPNs, email, exposed cloud | Lateral movement, privilege escalation, sensitive data |
| Answers | "Can they get in?" | "How bad is it once they're in?" |
External tests find open ports and vulnerable web apps; internal tests reveal weak privileges and over-shared file access. Together they give the full picture. A common cadence is an annual external test plus a periodic internal one, adjusted to your risk and compliance needs.
Compliance is a major driver of security testing, but the details change between framework versions, so cite the current one. Our SOC 2 penetration testing guide covers what auditors actually accept as evidence.
| Framework | What it expects | Note |
|---|---|---|
| PCI DSS v4.0.1 | Internal and external penetration testing at least every 12 months and after significant change (Req 11.4) | Sub-reqs: 11.4.1 methodology, 11.4.2 internal, 11.4.3 external, 11.4.4 remediation/retest, 11.4.5/11.4.6 segmentation, service providers test segmentation every 6 months |
| SOC 2 | Evidence of a vulnerability management and testing program | No universal "annual pentest" mandate; scoped to your controls, our SOC 2 pentest guide explains what auditors accept |
| ISO 27001 | Technical vulnerability management and regular testing | Aligns with a risk-based testing cadence |
| HIPAA | Risk analysis and safeguards for PHI | Testing supports the required risk assessment |
| NIST SSDF / SP 800-115 | Secure development practices and a testing methodology | The reference methodology for scoping tests |
Note the common error the old guidance carried: PCI's penetration-testing requirement moved from 11.3 (v3.2.1) to 11.4 in v4.0/v4.0.1. Quoting the retired number is an instant credibility tell.
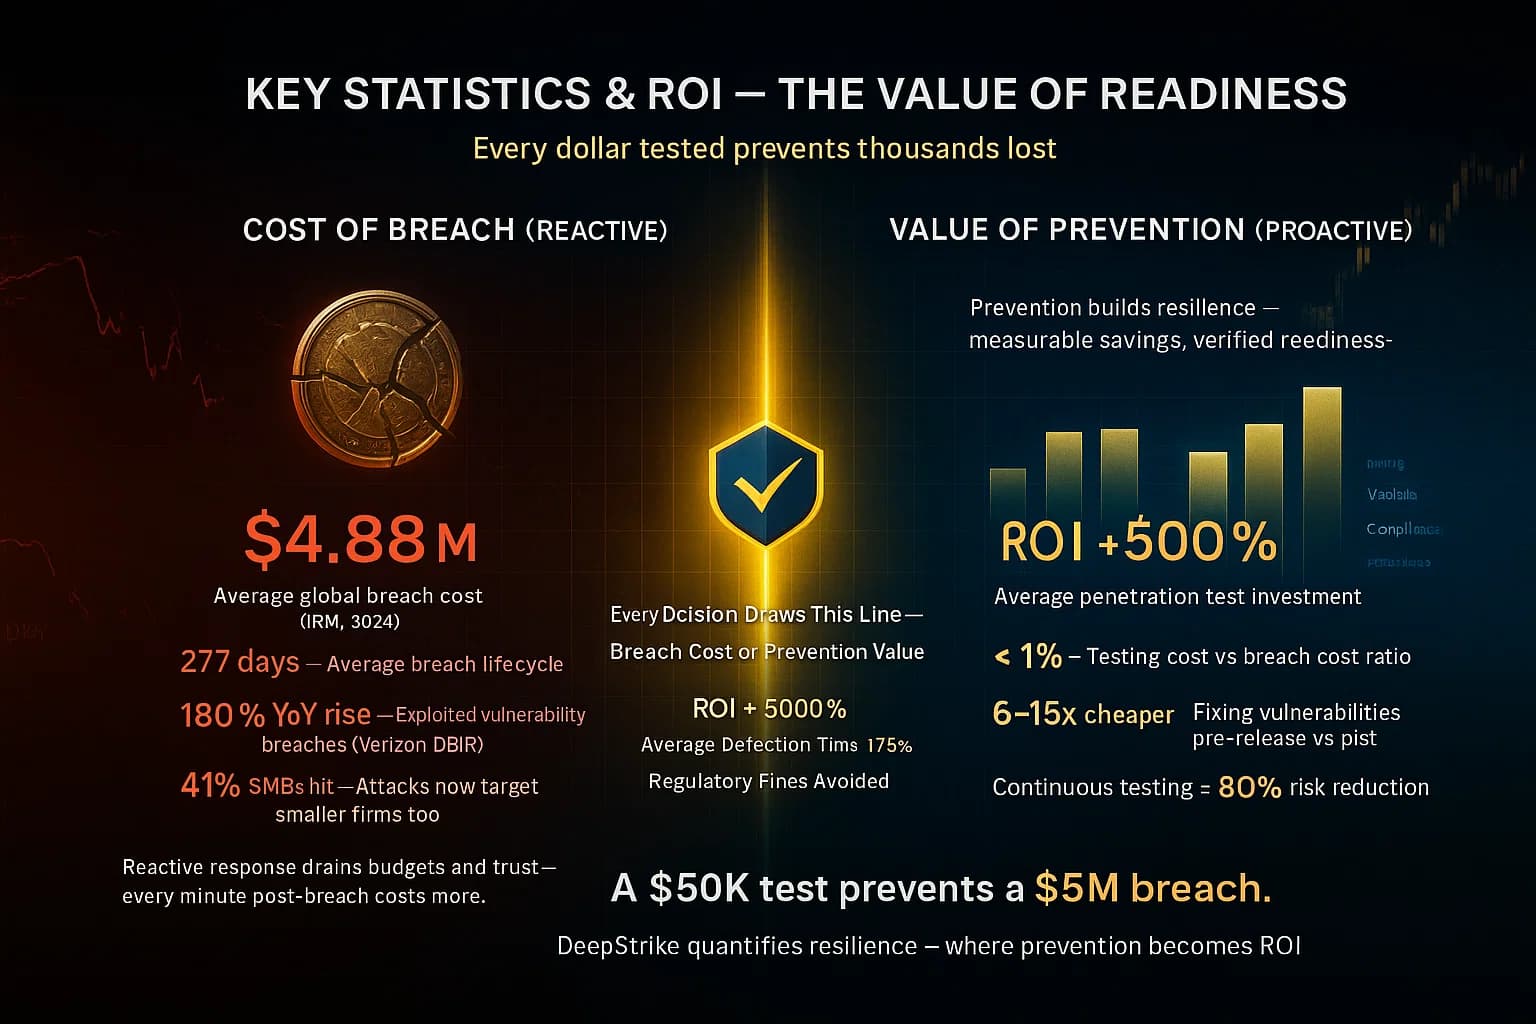
The ROI argument is simple: the annual cost of a solid testing program is small compared with the potential impact of a major breach, and proactive testing helps reduce exploitable paths while improving the effectiveness of the controls that support faster detection and containment.
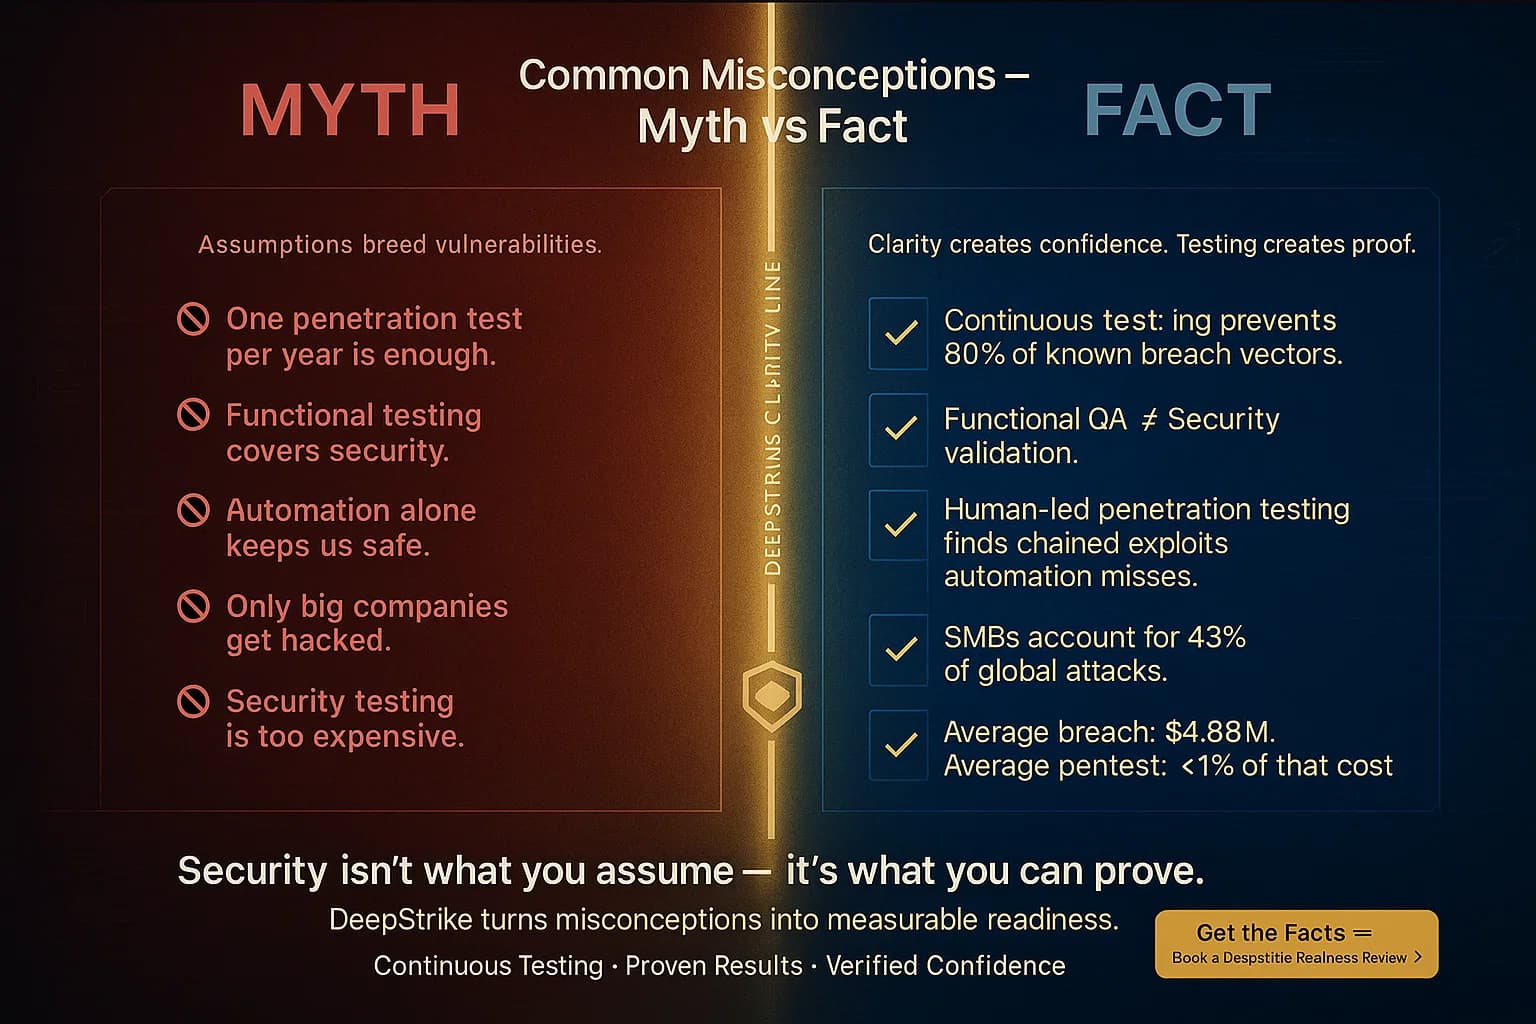
"Functional testing covers security." No. Functional tests assume honest usage and never exercise the malicious paths an attacker takes. Security testing is a distinct discipline.
"One pentest a year is enough." A single test is a snapshot of one moment. Code changes daily, new CVEs land at roughly 132 per day, and attacker techniques evolve. Continuous automated testing plus periodic manual pentests is the modern standard.
"Automated tools are enough." Scanners catch known and pattern-based issues but miss business-logic flaws, chained exploits, and novel attacks. Human testers find the creative paths. Combine both.
"Only big companies get attacked." Attackers target any exploitable system, and a large share of breaches hit small and mid-size businesses precisely because they assume they are too small to matter.
"Security testing is too expensive." Skipping it is the expensive option. Proactive testing costs a fraction of one breach and shortens the detection window that now drives breach cost.
"AI will replace security testing." AI accelerates testing and triage, but it also generates more code and more flaws, and it cannot own judgment on business logic or novel exploits. It changes the work; it does not remove it.
Security testing ensures your software not only works but survives contact with a real attacker. In 2026 that means layering static, dynamic, interactive, composition, and manual testing across the whole pipeline, consolidating the findings with ASPM, tracking dependencies with an SBOM, and keeping pace with AI-generated change. Functional testing runs on every build; security testing that runs once a year is out of step with it. Closing that gap is exactly what PTaaS versus traditional penetration testing is about.
Ready to strengthen your defenses? DeepStrike's penetration testing uncovers the exploitable, chained risks that scanners miss, validates that your controls actually hold, and gives you the fixes before attackers find them. For US-based teams, see our US penetration testing services.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
Software (functional) testing verifies that features work as intended for legitimate users. Security testing takes an attacker's perspective and checks whether those features can be abused, for example bypassing a login or injecting a payload. Functional testing asks "does it work?"; security testing asks "can it be broken?"
The seven core types are SAST (static code analysis), DAST (dynamic testing of the running app), IAST (instrumented, interactive testing), SCA (open-source dependency scanning), fuzzing (malformed-input testing), automated vulnerability scanning, and penetration testing (manual, human-led exploitation). Strong programs combine several, since each covers different blind spots.
Continuously. Run SAST and secret scanning on every commit, SCA at build, DAST against staging deployments, and recurring vulnerability scans in production, then commission manual penetration tests at least annually and before major releases. The earlier a flaw is caught, the cheaper it is to fix.
Yes. Vulnerability scanning provides broad, automated coverage of known issues but proves nothing exploitable. Penetration testing actively exploits and chains weaknesses to show real business impact. Scanning gives visibility; pentesting gives validation. They are complementary, not interchangeable.
AI now augments SAST and DAST with better triage and fewer false positives, generates test and fuzzing inputs, and powers early autonomous remediation. But AI also writes a growing share of code, reproducing insecure patterns at scale, so testing must run faster and more often. AI assists testers; it does not replace human judgment on logic and novel exploits.
Under PCI DSS v4.0.1, Requirement 11.4 mandates internal and external penetration testing at least every 12 months and after significant changes, covering methodology (11.4.1), internal (11.4.2), external (11.4.3), remediation and retest (11.4.4), and segmentation testing (11.4.5/11.4.6, every six months for service providers). Note this moved from the old Requirement 11.3 in v3.2.1.
Automation handles routine checks, SAST, DAST, SCA, container and IaC scanning, and increasingly AI-assisted triage. But automated tools miss complex business-logic flaws, chained exploits, and novel attacks. Skilled penetration testers are still required to probe those creatively. The best practice for critical systems is automated plus manual testing.
Security testing is checking software for weaknesses an attacker could use, before an attacker does. Testers and tools review the code and its dependencies, feed the running application unexpected and malicious input, and try to bypass its controls, then report what they found and how to fix it.
Application security testing is security testing focused on applications and their code: web apps, APIs, and mobile apps. It combines SAST, DAST, IAST, SCA, fuzzing, secure code review, and application penetration testing, usually checked against a standard such as OWASP ASVS.
Fuzz testing, or fuzzing, automatically feeds a program large volumes of malformed or unexpected input and watches for crashes, hangs, and memory errors. It is most effective on parsers, file handlers, protocols, and native code. It does not find business-logic or access-control flaws, so it complements penetration testing rather than replacing it.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
