December 14, 2025
Updated: November 5, 2026
2026’s ultimate guide to the best U.S. cybersecurity firms, published by DeepStrike (listed first for penetration testing), alongside Palo Alto Networks, CrowdStrike, Fortinet, Cisco, and others.

Mohammed Khalil
The top cybersecurity companies in the USA for 2026 include Palo Alto Networks, CrowdStrike, Fortinet, Cisco, Zscaler, SentinelOne, IBM and Rapid7, plus ESET and Heimdal, which serve US buyers from US offices. Together they cover network and SASE security, endpoint and XDR, zero trust access, managed detection, threat intelligence and offensive testing. DeepStrike, the publisher of this guide, is listed for human-led penetration testing. No single company leads every category, so shortlist by the problem you need solved, the rules you must meet, such as FedRAMP or PCI DSS, and whether you are buying a product or a service.
Choosing the right cybersecurity provider in 2026 can make or break your security strategy. The stakes are higher than ever as organizations face AI driven cyber threats and deepfake attacks, alongside increasing regulatory and compliance pressures. The market is also crowded and mature. This means buyers have many options from giant all in one providers to niche specialists and must navigate vendor consolidation and marketing hype to find true quality.
For providers outside the United States, see our worldwide list of penetration testing companies.
Country-specific cybersecurity company lists are available for the UAE, Germany, Singapore, Brazil, the Netherlands, France, Poland, Spain, Canada, Australia and the UK.
Why does this matter? Cyber breaches now cost U.S. companies about $11.5M on average according to IBM’s 2026 Cost of a Data Breach report, and compliance standards from SEC cyber disclosures to HIPAA updates are tightening. Picking a credible, capable security partner is critical to protect your business and meet obligations. The right provider will not only have technical prowess but also fit your organization’s needs in terms of scale, industry experience, and support. This research-driven shortlist, published by DeepStrike (which is also listed), describes each provider against the criteria explained later in this guide, whether you need a full-service enterprise partner or a specialized testing firm. List order is not a quality ranking; DeepStrike is listed first because it is the publisher of this guide.
The table groups the 11 listed companies by what you would buy from them. Product vendors sell platforms your team runs; service providers deliver testing, monitoring or response with their own people; several do both. Each row restates facts from the company's profile below, last checked on 3 November 2026. Order follows the profiles and is not a ranking.
| Company | Main category | What you buy | US base | Choose it if |
|---|---|---|---|---|
| DeepStrike | Penetration testing | Service: human-led application, cloud and infrastructure testing | Newark, Delaware | You need an independent test with remediation support |
| Heimdal | Unified endpoint, patching and PAM | Platform plus MXDR managed service | St. Petersburg, Florida office (main office Copenhagen, Denmark) | You are a mid-market team or MSP cutting the number of agents and consoles |
| ESET | Threat intelligence and endpoint | Products, threat intelligence feeds and MDR | San Diego, California (global HQ Bratislava, Slovakia) | You need research-led intelligence for threat hunting and investigations |
| Palo Alto Networks | Network, SASE, cloud and SOC platforms | Products plus Unit 42 incident response and MDR | Santa Clara, California | You want firewall, SASE, cloud and SOC tooling from one vendor |
| Fortinet | Firewalls, SD-WAN and SASE | Products plus incident response and MDR | Sunnyvale, California | You want firewall, SD-WAN and SASE on one operating system |
| Cisco | Security built into networking, plus Splunk SIEM | Products backed by Talos research | San Jose, California | You already run Cisco networking and want security integrated with it |
| CrowdStrike | Endpoint, XDR, identity and cloud | Falcon platform plus Falcon Complete MDR | Austin, Texas | You want endpoint-led detection and response, optionally fully managed |
| SentinelOne | Endpoint, XDR and AI-SIEM | Singularity platform plus Wayfinder MDR | Mountain View, California | You need SaaS, on-premises or air-gapped deployment |
| Zscaler | Zero trust access (SSE) | Cloud service plus Red Canary MDR | San Jose, California | You are replacing VPNs and perimeter controls for a distributed workforce |
| IBM | Consulting, managed security and offensive testing | Services plus products such as Verify and Guardium | Armonk, New York | You are a large or regulated enterprise that wants one global provider |
| Rapid7 | Exposure management, SIEM and MDR | Command Platform plus MDR and penetration testing services | Boston, Massachusetts | You want exposure management and SIEM with managed services |
Looking only for penetration testing firms? Our list of the top penetration testing companies in the US compares 19 specialist and enterprise testing providers. This page covers the wider security vendor market.
Below is our curated list of the leading cybersecurity companies operating in the United States, covering a mix of service providers and security product vendors. Most profiles set out the company's public offering, US relevance, official sources, buyer fit, and documented strengths and buying considerations. DeepStrike publishes this list and lists itself first; list order is not a quality ranking.
Public offering: DeepStrike's penetration testing services describe human-led testing across applications, cloud environments, and infrastructure, supported by a findings and collaboration platform. Its public process covers planning, reconnaissance, vulnerability discovery, controlled exploitation, reporting, and technical support. Published reports include reproduction steps, remediation guidance, and root-cause information; the proposal should define exact coverage and commercial terms.
US relevance: Founded in 2016, DeepStrike LLC is headquartered in Newark, Delaware, has 11–50 employees, and also publishes a business address in Dubai, UAE (IFZA Business Park). Define tester locations, permitted subcontracting, and data-handling restrictions in the engagement agreement.
Team certifications: OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate, as shown on DeepStrike's services page.
Official sources: Pricing , Contact Us
Buyer fit: Engineering teams that need application, cloud, or infrastructure testing with direct remediation collaboration.
| Documented strengths | Limits and buying considerations |
|---|---|
| Human-led testing with reproduction evidence, root-cause information, and remediation guidance. | The service description is not an independently measured quality comparison. Assess the assigned team and a relevant sample report. |
| The published Basic plan lists Slack collaboration, customizable reports, and 12 months of remediation retesting. | No numeric price is displayed on the pricing page. Basic is a one-shot test; recurring coverage belongs to a different plan, with contract-specific terms. |
| Team certifications shown on the services page include OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate. | These are individual tester credentials, not a company-level accreditation; ask which certified testers will be assigned to your engagement. |

Headquarters: St. Petersburg, FL (USA office); Copenhagen, Denmark (EU main office)
Founded: 2014
Company Size: Mid-sized vendor; third-party headcount estimates vary, so confirm current size with Heimdal
Primary Products/Services:
XDR platform combining Patch & Asset Management, Threat Prevention (DNS security), Next-Gen Antivirus, Privileged Access Management (PAM), Application Control, Email Security, and Managed Extended Detection & Response (MXDR) services.
Industries Served:
Mid-market enterprises, managed service providers (MSPs), and organizations in healthcare, finance, manufacturing, tech, and retail that want a consolidated security stack without a large in-house SOC.
Why They Stand Out:
Heimdal built its platform around a single idea: most organizations run too many disconnected security tools, and that sprawl itself becomes a risk. Heimdal presents its modules as one Unified Security Platform managed from a single dashboard, covering everything from patching to privileged access to email security.
This unified architecture appeals strongly to MSPs and mid-sized IT teams that need enterprise-grade coverage but don't have the headcount to run a dozen separate consoles. Heimdal has also leaned into managed services, offering 24/7 SOC coverage through its MXDR offering so that smaller teams can offload triage and response rather than staffing a round-the-clock security team themselves.
Key Strengths:
Potential Limitations:
Best For:
Mid-market companies and MSPs that want to shrink the number of vendors and agents they manage without sacrificing depth in patching, endpoint protection, or access control. Heimdal is a strong fit for lean IT teams that need enterprise-style coverage, including patch management, PAM, antivirus, and email security, under one roof, and for MSPs managing many small clients who want to adopt modules gradually. It's also a good option for organizations that want the option to add managed detection and response later without switching platforms.
What sets it apart in the US market: Unlike the US-headquartered vendors on this list, Heimdal is a Danish company that serves US customers from its St. Petersburg, Florida office. US buyers should confirm where support staff and MXDR analysts are located and where telemetry is stored.
Headquarters: Bratislava, Slovakia; North American headquarters in San Diego, California, USA
Founded: 1992
Company Size: Multinational cybersecurity vendor with a global research and development network.
Primary Products/Services: ESET Threat Intelligence, ESET PROTECT, endpoint protection, extended detection and response (XDR), and managed detection and response (MDR).
Industries Served: Healthcare, education, manufacturing, government, critical infrastructure, and enterprises seeking stronger threat visibility and proactive cybersecurity.
Why They Stand Out: ESET combines cybersecurity software and security services with in-house threat research, giving organizations both preventive controls and deeper visibility into the attackers, malware, and campaigns that may affect their operations. Its threat intelligence service brings together global telemetry, curated indicators of compromise, APT research, and expert analysis to help security teams enrich investigations, prioritize threats, and strengthen defenses beyond what they can observe within their own networks. The combination of machine-readable feeds and explanatory reporting also supports both operational workflows and higher-context threat hunting.
Key Strengths:
Potential Limitations:
Best For: ESET is a strong fit for enterprises, public-sector organizations, and security operations teams that need curated external intelligence to support threat hunting, investigations, and response prioritization—particularly when understanding advanced threat actors matters alongside day-to-day endpoint and XDR protection.
What sets it apart in the US market: ESET is headquartered in Bratislava, Slovakia, and serves North American customers from San Diego, California. Its case here rests on research-led threat intelligence rather than US federal authorizations, so public-sector buyers should confirm FedRAMP or GovRAMP status for the specific service they plan to buy.
Public offering: Palo Alto Networks sells security platforms rather than a testing service: Strata network security (next-generation firewalls and cloud-delivered security subscriptions), Prisma SASE (Prisma Access, Prisma SD-WAN, and Prisma Browser), Cortex security operations (XSIAM, XDR, XSOAR, and Xpanse), Cortex Cloud and Prisma Cloud for cloud security, and Idira identity security, which came from its CyberArk acquisition. Its Unit 42 team provides threat intelligence, incident response, retainer services, and managed detection and response.
US relevance: Palo Alto Networks is headquartered in Santa Clara, California. CREST's public marketplace lists Palo Alto Networks with penetration testing, incident response, cyber audit, and cyber advisory accreditation, with the United States among its countries; confirm which entity and team will deliver any service engagement.
Official sources: https://www.paloaltonetworks.com/; https://www.paloaltonetworks.com/unit42
Buyer fit: Mid-size and large enterprises that want to consolidate network, cloud, SASE, and SOC tooling with one vendor.
What sets it apart in the US market: Palo Alto Networks pairs its platforms with Unit 42 services, and CREST lists the company for penetration testing and incident response with the United States among its countries. GSA's FedRAMP data lists Palo Alto Networks Government Cloud Services as authorized at the Moderate level; federal buyers should confirm which products sit inside that boundary.
| Documented strengths | Limits and buying considerations |
|---|---|
| Platforms span network security, SASE, security operations, cloud, and identity, with Unit 42 incident response and MDR. | Platform breadth adds licensing and integration complexity; scope the modules you actually need. |
| Identity security was added through the CyberArk acquisition and is now branded Idira. | Product consolidation does not replace independent testing of your applications and configurations. |
Public offering: Fortinet's Security Fabric is built on its FortiOS operating system and FortiGate next-generation firewalls, with unified SASE (SSE, secure SD-WAN, and ZTNA), switching and wireless LAN, a security operations portfolio (SIEM, SOAR, EDR, NDR, deception, and SOC as a service), cloud and application security, and FortiGuard AI-powered security subscriptions. Fortinet also lists incident response, managed detection and response, consulting, and training services.
US relevance: Fortinet is headquartered in Sunnyvale, California. Its products are sold directly and through partners; confirm who will deploy, manage, and support the solution and where any managed-service data is processed.
Official sources: https://www.fortinet.com/; https://www.fortinet.com/corporate/about-us/contact-us
Buyer fit: Organisations from small business to enterprise that want firewall, SD-WAN, and SASE capabilities on one operating system.
What sets it apart in the US market: In April 2025 Fortinet announced GovRAMP (formerly StateRAMP) authorization at the moderate level for its FortiGuard AI-Powered Security Services and FortiCare Services, which is relevant to US state and local government buyers. Federal buyers should confirm FedRAMP status for any cloud-delivered component they plan to use.
| Documented strengths | Limits and buying considerations |
|---|---|
| One operating system across firewalls, SD-WAN, LAN/WLAN, and SASE, with FortiGuard security subscriptions. | Value depends on adopting several Fabric components; compare total cost against best-of-breed alternatives. |
| Incident response and MDR services are available alongside the products. | Fortinet's FortiGuard team also offers a penetration testing service. If you want testing that is independent of your firewall vendor, use a separate provider. |
Public offering: Cisco's security portfolio includes Cisco Firewall and Hybrid Mesh Firewall, Cisco Hypershield for data centre and cloud segmentation, Cisco Secure Access (SSE) and single-vendor SASE, Cisco Duo and Identity Services Engine for identity and access, Splunk Enterprise Security for detection and response, and Cisco AI Defense for AI applications. Cisco Talos provides threat intelligence research.
US relevance: Cisco is headquartered in San Jose, California, and completed its acquisition of Splunk in March 2024. CREST's public marketplace lists Cisco with penetration testing, incident response, and vulnerability assessment accreditation for the United Kingdom only; confirm the delivering team for any US service engagement.
Official sources: https://www.cisco.com/site/us/en/products/security/index.html
Buyer fit: Large enterprises and public-sector organisations that already run Cisco networking and want security integrated with it.
What sets it apart in the US market: For federal and public-sector buyers, GSA's FedRAMP data lists Duo Federal and Webex for Government as authorized at the Moderate level, while Cisco Umbrella for Government is listed as in process. Check the status of the exact Cisco service before procurement.
| Documented strengths | Limits and buying considerations |
|---|---|
| Networking, access, identity, and Splunk-based detection from one vendor, backed by Talos research. | Integration benefits are greatest in Cisco-heavy environments; assess fit for multi-vendor networks. |
| A broad firewall and SASE portfolio for hybrid environments. | A large catalogue can mean overlapping products; confirm which offering covers each requirement. |
Public offering: CrowdStrike's Falcon platform covers endpoint protection and EDR, cloud security, identity security, Next-Gen SIEM, SaaS and data security, exposure management, and threat intelligence and hunting, with Charlotte AI and agentic SOAR for automation. Its services include Falcon Complete managed detection and response, incident response, cybersecurity consulting, and a services retainer.
US relevance: CrowdStrike is headquartered in Austin, Texas. Confirm where managed-service analysts are located and where telemetry is stored if you have data-residency requirements.
Official sources: https://www.crowdstrike.com/; https://www.crowdstrike.com/en-us/contact-us/
Buyer fit: Mid-size and large organisations that want endpoint-led detection and response, optionally fully managed.
What sets it apart in the US market: CrowdStrike announced FedRAMP High authorization for its Falcon platform for government in March 2025 and for Falcon for XIoT in March 2026, which makes it a frequent option for federal and defense-adjacent buyers. Confirm that each module you need is inside the authorized boundary.
| Documented strengths | Limits and buying considerations |
|---|---|
| A single-agent Falcon platform spanning endpoint, cloud, identity, and SIEM. | The number of modules can raise subscription cost; license only the modules you need. |
| Falcon Complete MDR and incident response services. | CrowdStrike also lists penetration testing and red team/blue team services. If you want testing that is independent of your endpoint vendor, use a separate provider. |
Public offering: SentinelOne's Singularity Platform covers endpoint protection, XDR, identity threat detection, cloud security (CNAPP), AI-SIEM, and AI security through Prompt Security, with Purple AI as an analyst assistant. Its Wayfinder services include managed detection and response, threat hunting, and incident readiness and response. Since April 2026 they also include Wayfinder Frontier AI Services, which pair frontier AI models with SentinelOne's offensive and defensive experts to find vulnerabilities and validate which ones are exploitable.
US relevance: SentinelOne is headquartered in Mountain View, California. Confirm the deployment model (SaaS, on-premises, hybrid, or air-gapped) and data location for regulated workloads.
Official sources: https://www.sentinelone.com/; https://www.sentinelone.com/contact/
Buyer fit: Organisations that want AI-driven endpoint and XDR protection with flexible deployment options.
What sets it apart in the US market: SentinelOne's federal page states FedRAMP High authorization covering EDR, AI SIEM, CNAPP, and Wayfinder threat detection and response on AWS GovCloud, and the platform can also be deployed on premises or air-gapped. Confirm the current authorization scope for the modules you plan to buy.
| Documented strengths | Limits and buying considerations |
|---|---|
| Endpoint, identity, cloud, and AI-SIEM on one platform, deployable as SaaS, on-premises, hybrid, or air-gapped. | Compare detection coverage and pricing against other XDR platforms in a proof of concept. |
| Wayfinder MDR, threat hunting, incident response, and (since April 2026) Wayfinder Frontier AI Services for AI-assisted discovery and expert validation of exploitable vulnerabilities. | Wayfinder Frontier AI Services provide exposure validation; confirm whether they meet your penetration testing scope, or plan independent testing separately. |
Public offering: Zscaler's Zero Trust Exchange includes Secure Internet Access (ZIA), Secure Private Access (ZPA), Digital Experience (ZDX), Zero Trust Branch and Zero Trust Cloud, Zero Trust Firewall, Cloud Sandbox, Privileged Remote Access, and data security. Red Canary, a managed detection and response provider, is now part of Zscaler.
US relevance: Zscaler is headquartered in San Jose, California. As a cloud-delivered service, confirm which data centres will process your traffic and logs.
Official sources: https://www.zscaler.com/; https://www.zscaler.com/company/contact
Buyer fit: Organisations with distributed workforces that want to replace VPNs and legacy perimeter controls with zero trust access.
What sets it apart in the US market: GSA's FedRAMP data lists the government versions of Zscaler Internet Access and Zscaler Private Access as authorized at the High level, which makes Zscaler a common candidate for agencies replacing VPNs and Trusted Internet Connection (TIC) perimeter controls.
| Documented strengths | Limits and buying considerations |
|---|---|
| Cloud-delivered zero trust access for internet traffic, private apps, branches, and workloads. | Migrating from VPNs and perimeter firewalls takes planning; phase the rollout. |
| Managed detection and response is available through Red Canary. | Zscaler secures access paths; it does not replace endpoint protection or independent testing. |
Public offering: IBM's security portfolio includes cybersecurity and managed security services, risk consulting, X-Force threat intelligence, and products such as IBM Verify for identity, Guardium for data protection, and MaaS360 for endpoint management. Its X-Force Red offensive security services cover expert-led penetration testing of applications, networks, cloud, hardware, and AI systems, adversary simulation, and social engineering, with findings tracked in its Red Portal.
US relevance: IBM is headquartered in Armonk, New York. CREST's public marketplace lists IBM with penetration testing, incident response, and vulnerability assessment accreditation, with the United States among its countries; confirm the delivering team and tester locations.
Official sources: https://www.ibm.com/security; https://www.ibm.com/services/offensive-security
Buyer fit: Large and regulated enterprises that want consulting, managed security, and offensive testing from one global provider.
What sets it apart in the US market: IBM combines X-Force Red offensive testing with managed security and consulting, and CREST lists it for US penetration testing. GSA's FedRAMP data lists IBM Cloud for Government (High) and MaaS360 Enterprise Mobility Management (Moderate) as authorized, which matters if you also buy IBM-hosted services.
| Documented strengths | Limits and buying considerations |
|---|---|
| Consulting, managed security, X-Force threat intelligence, and X-Force Red testing in one portfolio. | Enterprise engagements can involve longer procurement; agree scope, named testers, and timelines up front. |
| CREST's marketplace lists IBM for penetration testing, incident response, and vulnerability assessment. | IBM sold its QRadar SaaS assets to Palo Alto Networks; confirm the SIEM tooling behind any managed service. |
Public offering: Rapid7's Command Platform combines attack surface and exposure management, vulnerability management (InsightVM), next-gen SIEM, threat intelligence, cloud security (InsightCloudSec), and application security (InsightAppSec). Its services include managed detection and response, managed vulnerability management, continuous red teaming, and penetration testing, and Rapid7 maintains the Metasploit framework.
US relevance: Rapid7 is headquartered in Boston, Massachusetts. Confirm where MDR analysts and penetration testers are located and how evidence is stored.
Official sources: https://www.rapid7.com/services/penetration-testing/; https://www.rapid7.com/contact/
Buyer fit: Mid-market and enterprise security teams that want exposure management, SIEM, and MDR alongside penetration testing services.
What sets it apart in the US market: Rapid7's InsightGovCloud Platform received FedRAMP Moderate authorization in July 2025, covering vulnerability management, CNAPP, and SOAR capabilities, and Rapid7 maintains the open-source Metasploit framework that many US testing teams use. Federal buyers should check which Command Platform features are available in InsightGovCloud.
| Documented strengths | Limits and buying considerations |
|---|---|
| Exposure management, SIEM, MDR, and penetration testing services from one vendor, plus Metasploit. | When the same vendor supplies your tooling and your testing, agree how testing independence will be maintained. |
| Continuous red teaming is listed alongside point-in-time penetration testing. | Compare service scope and tester experience with dedicated testing providers before choosing. |
| Company | Specialization | Best For | Region HQ | Compliance Support | Ideal Company Size |
|---|---|---|---|---|---|
| DeepStrike | Human-led penetration testing | Application, cloud, and infrastructure testing with remediation collaboration | USA Newark, Delaware | Testing scoped to client requirements such as SOC 2, ISO 27001, or HIPAA; team certifications include OSCP and OSWE | SMB to mid enterprise |
| ESET | Cyber threat intelligence, endpoint protection, XDR, and MDR | Research-backed threat intelligence and proactive defense | Slovakia, Bratislava; North American HQ in San Diego, USA | Supports threat-informed risk assessment and security monitoring; compliance depends on implementation | Mid-market to large enterprise; government and critical infrastructure |
| Heimdal | Unified platform: patching, DNS security, NGAV, PAM, email security, MXDR | Consolidated security stack for mid-market teams and MSPs | Denmark, Copenhagen; US office in St. Petersburg, FL | Compliance depends on implementation | Mid-market and MSPs |
| Palo Alto Networks | Next Gen Firewalls & SASE | Network & cloud security platform Best for unified enterprise security | USA Santa Clara | Certifications: FedRAMP, Common Criteria; Compliance mappings in Prisma | Mid to Large Enterprise |
| Fortinet | Unified Threat Management | Cost effective security for distributed orgs Best for SMB value | USA Sunnyvale | PCI DSS device hardening, NSS tested; compliance logging | Small Business to Large Enterprise scales broadly |
| Cisco | Secure Networking & Zero Trust | Secure SD WAN and Zero Trust access Best for large networks | USA San Jose | Supports NIST and FIPS requirements; FedRAMP status varies by product (Duo Federal authorized, Umbrella for Government in process) | Large Enterprise & Government |
| CrowdStrike | Endpoint Protection & XDR | Advanced threat detection & hunting | USA Austin | FedRAMP High authorized; maps to MITRE tactics for compliance audits | Mid to Large including Fortune 100 |
| SentinelOne | Autonomous Endpoint Security | Automated endpoint defense AI driven | USA Mountain View | MITRE ATT&CK reporting; compliance via rollback logs PCI, etc. | Mid to Large Enterprise |
| Zscaler | Cloud Security SWG, ZTNA | Secure cloud access & zero trust remote workforce | USA San Jose | SOC 2 Type II, ISO 27018; assists with HIPAA, GDPR via DLP controls | Mid to Large Enterprise |
| IBM Security | Managed Security & Compliance | Full service, compliance focused programs Best for regulated enterprise | USA Armonk, NY | Extensive ISO 27001 certified, helps with PCI, HIPAA, etc. | Large Enterprise & Critical Sectors |
| Rapid7 | SIEM, XDR & Vulnerability Mgmt | Unified threat detection & risk management Best for compliance driven mid market | USA Boston | PCI, HIPAA reporting; aligns vulns to CVSS/regs; auditor friendly logging | Mid Enterprise also upper SMB |
Compliance Support cells summarize vendor-published claims and certifications, which change over time; confirm current authorizations (for example FedRAMP status) with each vendor before relying on them.
Choosing the right security vendor depends on your environment and priorities. Many enterprises adopt a layered defense: for example, pairing a network/security platform like Palo Alto or Fortinet for perimeter and cloud, an endpoint solution like CrowdStrike or SentinelOne for host level defense, and a cloud access platform like Zscaler for remote access. They then integrate these with managed services or SIEM from providers such as IBM or Rapid7 for 24/7 monitoring and compliance support. Crucially, organizations should also validate their defenses through independent testing. This is where DeepStrike’s proactive penetration testing complements the above platforms; its human-led testing is designed to find logic flaws and chained attack paths that automated scanning can miss. DeepStrike’s published Basic plan lists 12 months of remediation retesting, and its audit ready reports help verify that vulnerabilities are fixed properly, which is often required for compliance.
In summary, 2026 demands both robust security platforms and rigorous validation. The vendors listed above include established options in each category, from Palo Alto’s integrated network defense to CrowdStrike’s AI powered endpoint protection to Zscaler’s zero trust cloud gateway. Enterprises should consider analyst recognized solutions in their respective domains e.g. Palo Alto in SASE, CrowdStrike in endpoint, Zscaler in SSE, IBM in managed services and reinforced them with expert human led testing. The best security strategy blends state of the art tools and continuous human validation to stay ahead of threats. In this integrated model, DeepStrike’s manual pentesting and red teaming add a critical layer of assurance that you’re not relying solely on automation.
By selecting vendors aligned to each of your use cases network, endpoint, cloud, compliance and augmenting them with human-led testing such as DeepStrike’s, your organization can achieve a stronger, more resilient cybersecurity posture in 2026.
Searches for cybersecurity companies, cyber security firms and cybersecurity providers mix very different businesses. Decide the category first: a network security vendor, a managed detection provider and a penetration testing firm answer different questions, and each is bought and judged differently.
Many US organizations combine categories: a network or SASE platform, an endpoint or XDR tool, a managed detection service for nights and weekends, and an independent test at least once a year or after major changes. Testing is most useful when the tester is not the same vendor whose controls are being tested.
How this US list was built: We started from companies with US headquarters or established US operations that American buyers commonly shortlist across network security, endpoint and XDR, zero trust access, security operations, threat intelligence, and offensive testing, and selected providers so that each of those needs is covered. For each entry we checked the company's own product and service pages, CREST's public marketplace for US testing accreditation, GSA's FedRAMP Marketplace data and vendor announcements for federal and state authorizations, and investor releases for acquisitions. Checks were last run on 3 November 2026. This is desk research, not hands-on product testing, and the criteria below describe what we looked for rather than a scored ranking.
Our Evaluation Methodology: To keep this shortlist high quality and procurement friendly, we reviewed companies across multiple dimensions of E-E-A-T (Experience, Expertise, Authoritativeness, Trustworthiness):
Using the above methodology, we selected the U.S.-based cybersecurity providers profiled earlier in this guide.
The United States has no single national cybersecurity or penetration testing law. Requirements come from sector regulators, states, and government contracts, so the right provider depends on which rules apply to you. As of 3 November 2026:
There is no national US accreditation scheme for commercial penetration testing providers comparable to the UK's CHECK scheme, so buyers usually rely on CREST membership, individual tester certifications, and references. CISA, the national cyber defense agency, offers free vulnerability and web application scanning to US government bodies and critical infrastructure organizations; that complements, but does not replace, a scoped penetration test.
Match the provider to the job. Define what you need tested or managed, which rules apply (PCI DSS, SEC disclosure, NYDFS, HIPAA, FedRAMP, or CMMC), and who will do the work. Then ask for a sample report, named team members and their credentials, references from similar US organizations, and a written scope covering retesting and price.
Even with a strong shortlist, buyers should do their due diligence. Here are some tips to ensure you choose the right provider for your needs:
By keeping these points in mind, you can approach the vendor selection process with a clear head. Use them with the profiles above to start your evaluation.
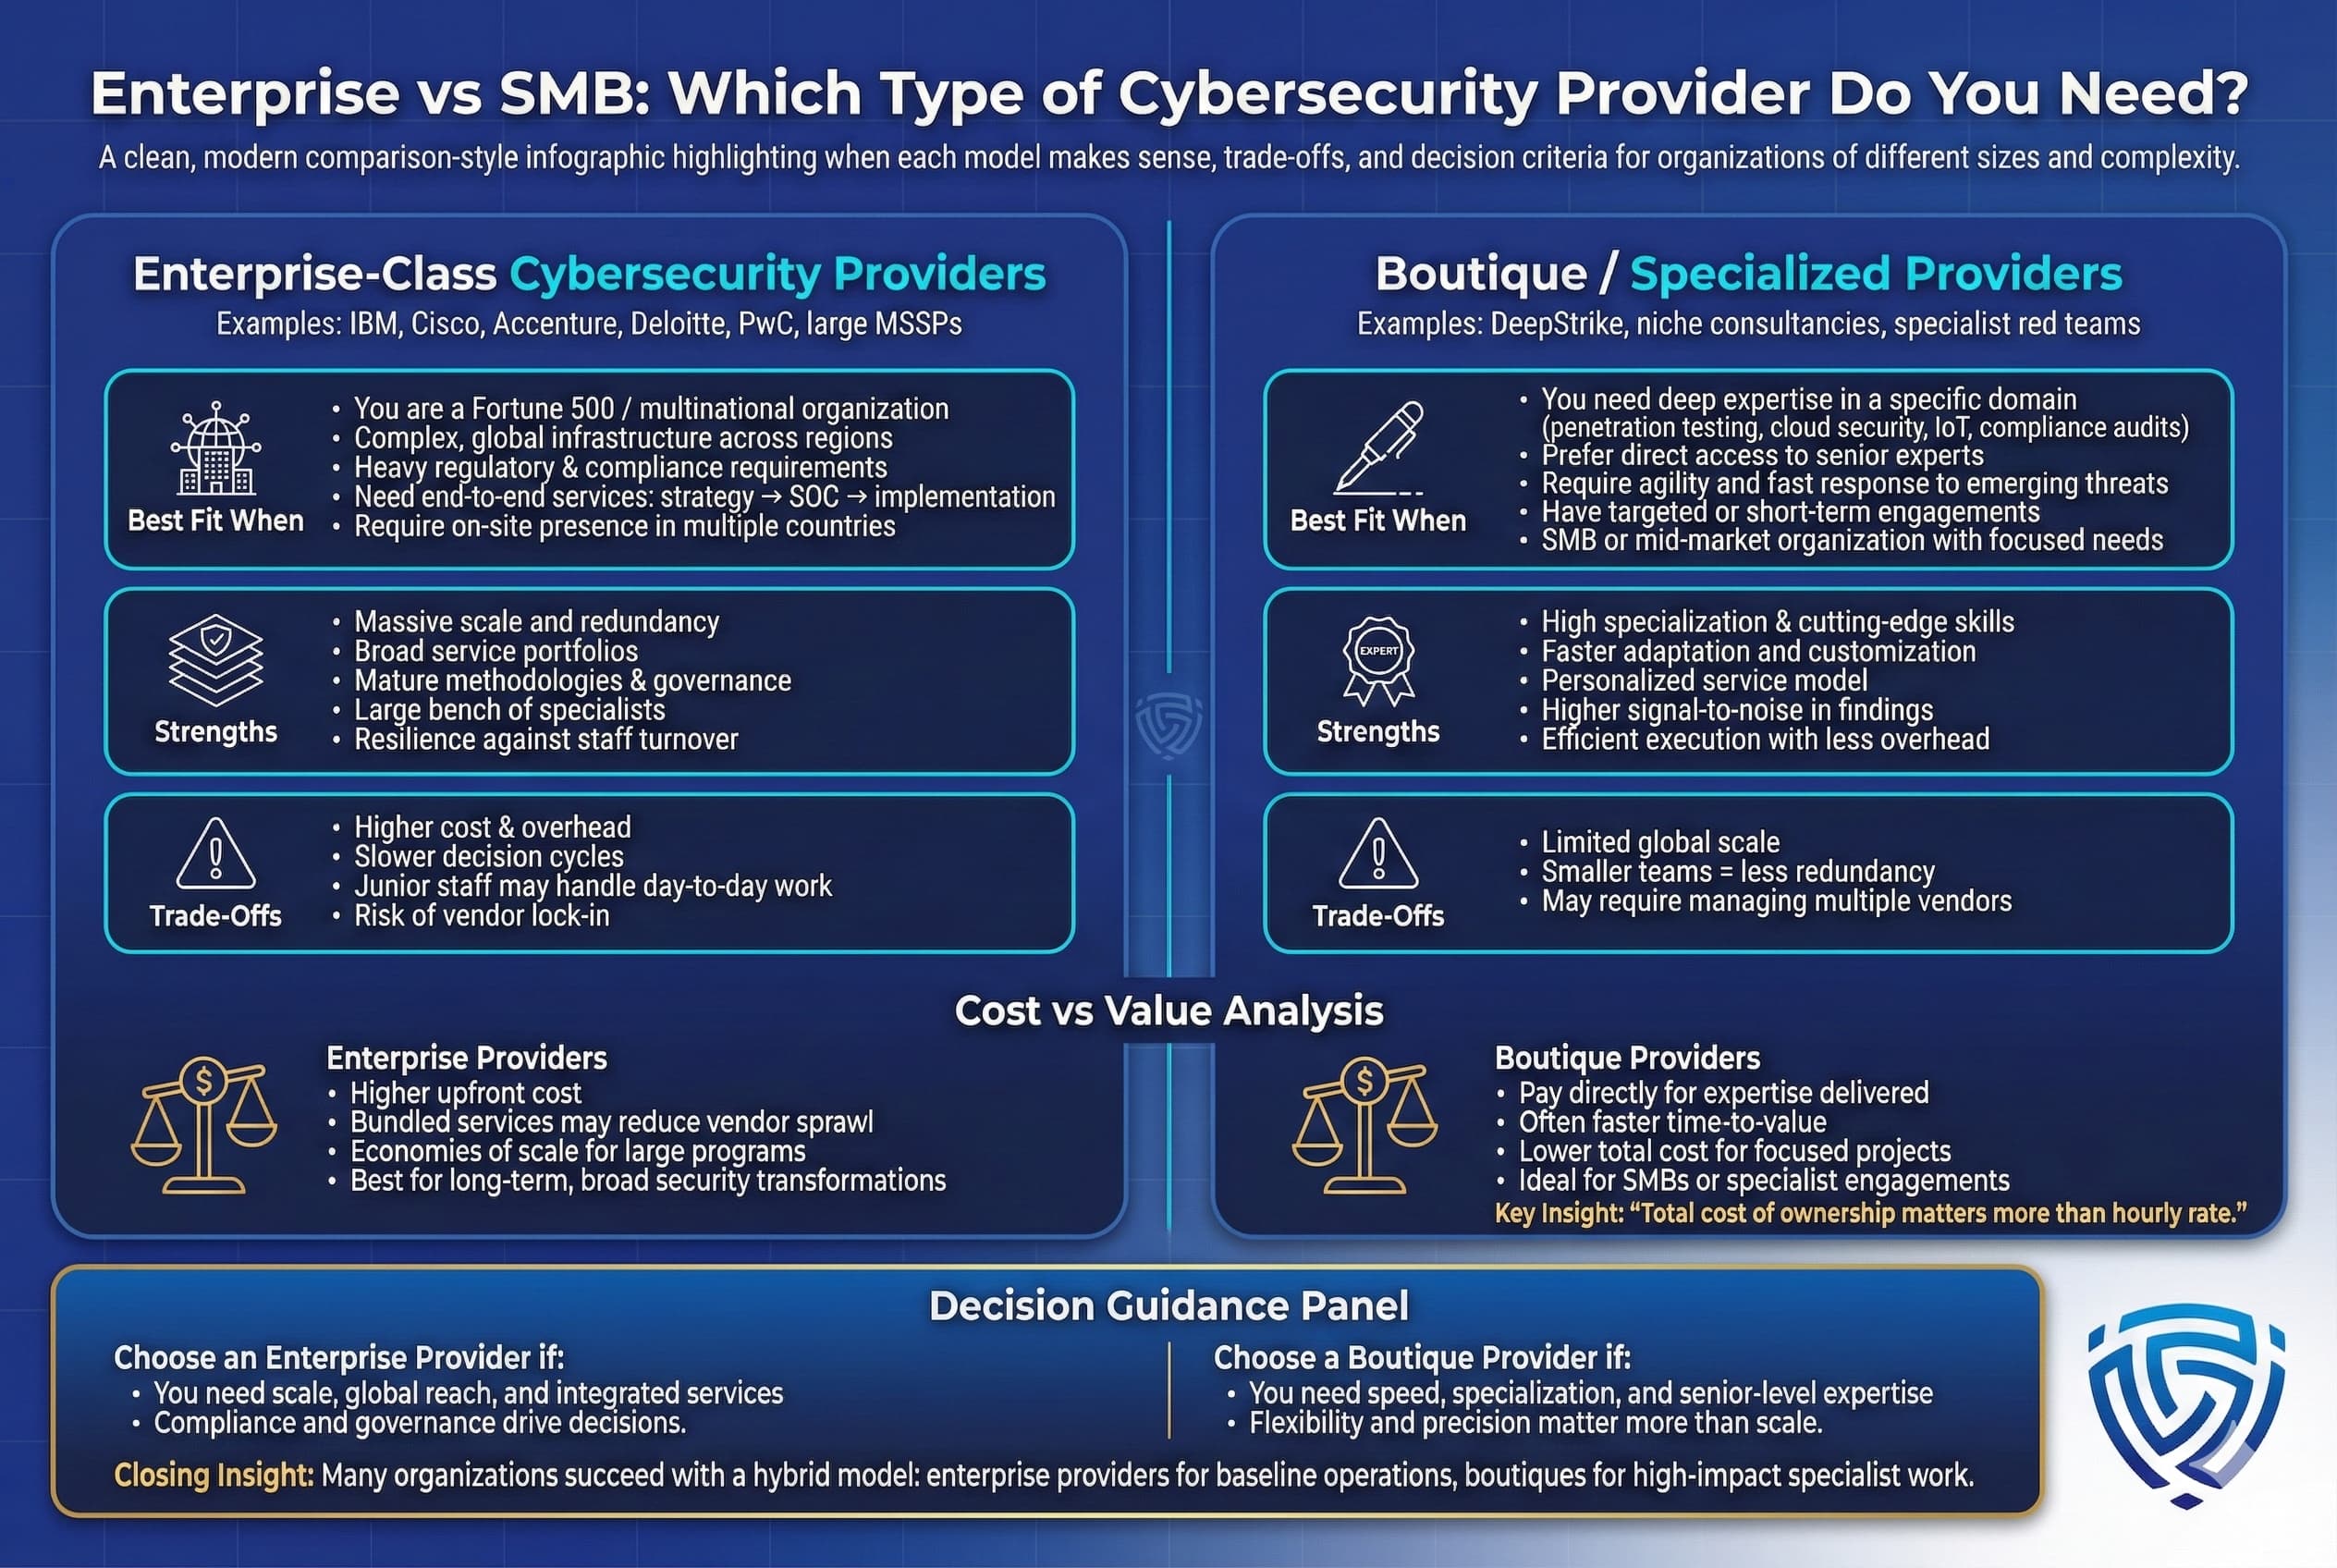
It depends on scope more than company size. Large providers such as IBM or Cisco suit organizations that need many services, multi-jurisdiction compliance support, and around-the-clock coverage from one partner. Boutique specialists suit a defined need such as application or cloud penetration testing, where direct access to senior testers matters more than global scale.
Cybersecurity providers come in all sizes, generally falling into two camps: large enterprise class firms and boutique specialized firms. Both have advantages; the key is determining which suits your organization’s needs.
In summary, large providers are like a one stop department store, convenient and comprehensive whereas boutique firms are like specialty shops with expert craftsmen. Enterprises with broad needs and high assurance requirements may lean towards the former, while those with specific pain points or seeking a tailored approach might opt for the latter. Some organizations even use a mix: a big MSSP to cover the basics and niche experts for specialized testing or projects. The key is to assess your internal team’s strengths, your risk profile, and the complexity of your environment, and choose the provider type or combination that addresses your gaps most effectively and efficiently.
The cost of a professional penetration test can vary widely depending on scope and complexity. On the low end, a small test e.g. a simple web app or small network may cost a few thousand dollars, while complex tests for large enterprises, multiple networks, extensive applications can run into tens of thousands or more. Factors that influence cost include the number of IPs or applications in scope, testing depth gray box with credentials vs black box, and any special methodologies social engineering, hardware testing, etc.. Be wary of unusually low quotes; those often indicate a superficial automated scan rather than a real manual pentest. Keep in mind the value: considering the average US breach cost about $11.5M in IBM’s 2026 report, spending tens of thousands on a quality pentest that prevents a breach is usually worth it. Many providers will work with you to right size the scope to your budget. Also ask about retesting: DeepStrike’s published Basic plan, for example, lists 12 months of remediation retesting, which adds value. Ultimately, budget for at least an annual pentest see below on frequency and treat it as an investment in risk reduction rather than a one time expense.
Expertise is more important, and certifications are one way to gauge that. A skilled team with solid certifications OSCP, CISSP, GIAC, CREST, etc. generally indicates they have proven knowledge and have been vetted against industry standards. Tools are just means to an end. Practically all reputable firms will have access to similar toolsets, vulnerability scanners, SIEM platforms, etc.. What differentiates providers is how they use those tools and their human creativity/insight. For example, an automated scanner might flag common issues, but an OSCP certified pentester could exploit a chain of low risk findings into a major breach. That said, look for a provider that has both: talented people and a robust toolset. Providers with relevant certifications and accreditations like ISO 27001 for the company, or SOC 2 Type II reports also demonstrate they follow security best practices internally. But don’t be blinded by alphabet soup. Ask providers to explain how their team’s experience will solve your specific problems. Also, in some domains, certifications like PCI QSA for compliance assessments or CREST for pentesting in certain regions might be mandatory or add credibility. In summary: use certifications as a quality indicator and a tie breaker, but also consider case studies, testimonials, and your gut feeling of their competence. A great provider will happily discuss methodologies often following standards like OWASP, NIST rather than just touting tools.
Timelines can range from a few days to several weeks. A basic external network pentest might take 1–2 weeks including reporting. A web or mobile app test is often 1–2 weeks per application, complex apps could be longer. Comprehensive internal network pentests for midsize companies usually last 2–4 weeks end to end. For large enterprise environments, testing can extend to 4–6 weeks or more, especially if multiple phases recon, exploitation, pivoting internally are involved. Additionally, time is needed upfront for scoping and getting necessary access IP whitelisting, credentials for gray box tests, etc., and afterwards for report review and remediation discussions. Incident response or compromise assessments typically take a few weeks for data collection and analysis, but can be shorter if the situation is urgent teams will work 24/7 in a crisis. Security audits like ISO 27001 readiness might involve sporadic engagement over a month or two. It’s wise to communicate any deadlines like compliance dates or board meetings to the provider. Many will adjust resources to meet a hard deadline if needed. Keep in mind, rushing a pentest is not advisable; testers need sufficient time to be thorough. Conversely, extremely prolonged tests can lose momentum so a focused window with clear scope is best. Always factor in time for remediation and retest after the initial findings. A good rule of thumb: for an average environment, budget about 3 weeks for the active testing and another week for report/fix validation. Simpler projects can be quicker, and very complex ones proportionally longer.
A high quality report is one of the key outcomes of any security engagement. You should expect:
In essence, the deliverable should be actionable. It’s not just about finding problems, but enabling you to fix them and improve. A red flag is a report that’s just scanner output or lacks context. Top firms put significant effort into custom prose, clear visuals, and specific guidance. For managed services MDR/MSSP, deliverables are more continuous e.g., a portal with dashboards, monthly service reviews, and incident tickets with analysis when threats are detected. Ensure any provider clearly defines what you’ll receive and in what timeframe. Don’t hesitate to ask for a sample report beforehand sanitized of course to judge their reporting quality.
At minimum, annually. Most standards and experts recommend a full scope penetration test at least once per year. Many compliance frameworks such as PCI DSS, for example, require annual testing and after significant changes. However, given the pace of threats and development, more frequent testing is advised for critical systems. A common approach is to do an annual big test and supplemental tests quarterly or bi annually on key areas. For instance, if you have a customer facing web app, you might pentest it before each major release, not just once a year. Continuous Pentesting or PTaaS Pentest as a Service is an emerging model where portions of your environment are tested on a rolling basis throughout the year; this can catch issues closer to their introduction. Additionally, you should do vulnerability scanning much more frequently monthly or weekly for externals, at least quarterly for internals, or continuous with tools. If you’re using an MDR service, you’re essentially having your defenses tested 24/7 by how well they detect probes and attacks. Risk profile matters: if you’re in a high target industry finance, healthcare or handle sensitive data, consider semi annual or quarterly pen tests, and definitely test after any major infrastructure or application changes. Also, mix up the types of assessments: one quarter do a social engineering test, another quarter a cloud security review, etc., to cover different angles. For SMBs, resource constraints might limit you to annual testing if so, focus it on your most critical assets each year. Remember, the threat landscape is dynamic; new vulnerabilities like Log4j, etc. can emerge anytime. Some companies supplement annual pen tests with bug bounty programs or periodic red team exercises to get more frequent coverage. In summary, make security testing a regular, ongoing practice rather than a one off. As a baseline: annual comprehensive pen test, with additional targeted tests in between, is a solid strategy to ensure continuous improvement and no nasty surprises lurking.
Automated tools are necessary but not sufficient. They are a great first line of defense in fact, any good security program will use vulnerability scanners, automated compliance checks, SIEM correlation rules, etc. However, tools have limitations. Scanners might detect known common weaknesses, missing patches, misconfigurations but they can’t think creatively or understand business logic. Many breaches occur due to complex attack chains or logic flaws that automated tools simply don’t catch. For example, a scanner might not realize that by using a sequence of normal low risk actions across different systems, an attacker could transfer funds or steal data that insight comes from human expertise. Hiring a cybersecurity company or having in-house experts brings that human element: people who can interpret results, find unknown vulnerabilities, and reduce false positives. Additionally, professional testers and analysts use tools as part of their arsenal, but they validate and probe deeper. Automated tools also require configuration and tuning. It's easy to get a false sense of security if a tool is misconfigured or not scanning everything. A security firm can ensure tools are used correctly and can augment them with manual techniques. Another aspect is context and advice: a scanner might tell you port 443 is open with TLS 1.0, but a human consultant can tell you what that means in terms of risk to your specific business and how to prioritize fixing it among all issues. That said, for day to day hygiene, automated tools especially for patch management and log analysis are indispensable and many security companies will help you set those up too. Think of it like medical care: you have automated blood pressure cuffs and apps, but you still need a doctor to interpret and treat effectively. In cybersecurity, use tools to cover the basics continuously, and use expert driven assessments to deep dive and audit the efficacy of those tools. The combination yields the best security posture.
In cybersecurity, product vendors develop and sell software or hardware solutions for example, firewall appliances, antivirus software, SIEM platforms, etc. Service providers offer expertise and outcomes as a service like consulting engagements, managed security monitoring, or incident response handling. The difference often comes down to what you are buying: a tool that your team operates on versus a result delivered by the vendor’s team service. However, the line is blurring. Many companies, especially those in this Top Companies list, do both. For instance, CrowdStrike is a product company Falcon platform but also has managed threat hunting services. IBM sells security products (such as IBM Verify for identity and Guardium for data protection) and provides managed security services through its own staff. When evaluating a vendor, it’s important to clarify if you’re looking for technology to empower your team or if you want to offload work to the provider. Pros of product vendors: you maintain control and can customize internally; potentially lower ongoing cost if you have the expertise. Cons: you need skilled staff to use them fully, and the responsibility is on you to react to what the product finds. Pros of service providers: they bring expertise and can often detect/respond faster with their specialized focus; less burden on your team. Cons: you are entrusting an external party so vet them for trust and skill, and costs can accumulate as services are ongoing. Many top companies package product + service together like an MDR service using their own XDR product. This can be efficient, but ensure the combined offering truly fits your needs. Some organizations prefer a best of breed product from one company and services from another or in house. There’s no one size answer, it depends on your internal capabilities and preferences for control vs outsourcing. In summary, know that most leading cybersecurity companies today offer both: platforms to secure you and expertise to manage or enhance those platforms. Evaluate each aspect on its own merits. You might love a vendor’s tool but not need their services, or vice versa. The good news is integrated offerings can simplify things if they align well with your requirements.
Translating security spend into business terms is key. Here are a few angles:
Finally, break down deliverables in business language: e.g., This penetration test will help us protect customer data by identifying weak points before attackers do, or This MDR service means we have experts watching our systems 24/7, so our small IT team doesn’t have to and we can respond to threats in minutes instead of days. Tie it to business uptime, customer trust, and financial protection. Present it as an investment with clear outcomes, not just a cost. Often, including a brief from the provider’s proposal with their results stats or client success stories can bolster your case. In short, speak in terms of risk reduced, value gained, and alignment with business goals. Management is likely to approve spending when they see it supports the company’s continuity and success.
Cyber threats don’t discriminate by company size. In fact, attackers often target smaller firms as easy prey, or as stepping stones to larger partners/clients. While you might not need a multi million dollar security program, you absolutely need effective security measures appropriate to your business. The good news is many top companies have offerings for smaller organizations, or there are high quality smaller vendors that made our list like DeepStrike for specialized testing or Rapid7’s tailored services. Start by identifying your crown jewels, the data or systems that, if compromised, could be fatal to your startup. It could be your intellectual property, customer data, or even just your website and reputation. Then assess what internal capability you have. Many startups have very limited IT/security staff, so bringing in an external expert to do a security assessment or set up some defenses is wise. You might not hire IBM Security to manage your operations if you’re 50 people, but you could use a company like Arctic Wolf MDR for SMB or a boutique consultancy to harden your app. The key is scoping: you can engage top providers for a right sized engagement e.g., a one time cloud config review, or a lightweight managed detection service that fits a small company budget. Also consider that small companies often need to prove security to win clients. Having a respected security firm’s report or service can punch above your weight in giving enterprises confidence to do business with you. Ultimately, no company is too small for hackers but your defenses can be agile and scaled to your size. Perhaps focus on one or two critical security services; for instance, many startups start with a solid cloud security posture review and a recurring pentest, and as they grow, they layer in more maybe a vCISO service or MDR. Leverage the fact that some big name products have tiered pricing for small users or use open source tools initially, but validate with occasional expert audits. In summary, you may not need all the bells and whistles that a Fortune 100 does, but you do need the essentials. Top cybersecurity companies can provide high quality essentials in a package for small firms and that could save your startup from a catastrophe that derails your growth. Security, like insurance, is often more affordable than the cost of a single incident. Even as a lean startup, aim to allocate some budget a few percent of IT spend to security from the get go it will pay off in stability and trust as you scale.
Leading cybersecurity companies invest heavily in threat intelligence and R&D to stay ahead of the curve. They have dedicated research teams like Unit 42 at Palo Alto, Talos at Cisco, X Force at IBM, etc. that continuously monitor hacker forums, malware samples, breach reports, and vulnerabilities. For instance, as of late 2026, many are closely tracking AI driven cyber threats and deepfakes. These research units publish blogs, advisories, and feed updates into their products e.g., new detection signatures or IoCs. Additionally, top firms participate in industry sharing groups like FS ISAC, CERTs so they get early warnings of threats affecting certain sectors. When a new critical vulnerability zero day emerges, companies like Microsoft, CrowdStrike, etc., often already have analysts reverse engineering it and developing patches or detection rules within hours sometimes in collaboration under NDAs before public disclosure. Many providers also use AI and machine learning defensively: for example, training models on the latest attack patterns so their tools can identify novel variants CrowdStrike reducing breach detection time with AI. They also run labs and testing environments, think honeypots, research sandboxes to see how new threats behave. Importantly, firms engaged in incident response learn from every breach they investigate, and that knowledge is folded back into preventative services. The competitive nature of the industry also means if one company finds a new attack technique, others quickly study and account for it. Clients of top providers benefit through regular threat briefing reports, updated controls, and sometimes direct alerts if a threat is relevant to them. So, in short, these companies stay up to date by maintaining expert teams, leveraging global telemetry often millions of endpoints or sensors reporting in, collaborating across the community, and applying automation to digest massive amounts of threat data. Part of why you choose a top vendor is to essentially outsource that continuous research burden to them so you get the latest protections or advice because it’s their job to live on the bleeding edge so you don’t have to. Always feel free to ask a prospective provider how they keep current; the depth of their answer will tell you a lot about their internal excellence. Companies in our Top list will usually have impressive answers, showing that continuous innovation and intel is in their DNA.
There’s no one size fits all timeline, but a general guideline is to continually evaluate and refresh as needed while avoiding knee jerk changes. Many organizations do a formal review of their security stack annually or bi annually. If your current tools or provider are meeting your needs and keeping up through updates, you don’t necessarily need to rip and replace on a schedule. However, signs it’s time to update or change include: your threat landscape changed e.g., moved significantly to cloud you may need new cloud focused tools, your provider is not performing or has frequent misses, or new solutions offer compelling advantages like significant automation or consolidation benefits. Technology evolves fast for instance, five years ago few had a Zero Trust Network Access tool, now many are replacing VPNs with ZTNA like Zscaler or Palo Alto Prisma. If you’ve used the same AV for 7-10 years, it’s definitely worth evaluating next gen EDR solutions now. As a rule of thumb, major security technologies often have a lifecycle of ~5 years before a disruptive improvement may warrant change as long as support and updates continue in that period. Providers: if you outsourced your SOC to an MSSP and after a couple years you’re not happy with responsiveness or outcomes, shop around. Sometimes switching can increase security and even reduce cost if a new provider has a more efficient approach. On the other hand, be cautious of shiny object syndrome jumping to a new vendor or tool just because it’s hyped, without planning the migration and ensuring it truly fits, can cause gaps. A best practice is to keep an eye on independent evaluations of Gartner, MITRE ATT&CK results, etc. yearly, and do proof of concepts with new tech every few years to ensure you have the best for your needs. Also, consult your internal metrics: if certain tools have tons of unaddressed alerts or your team complains about them, it might be time to replace or upgrade. When it comes to managed services, contract lengths are often 1-3 years; it’s wise to align evaluations with those cycles you might bid out the service at renewal to see if you should stay or switch. In summary, evolution not revolution maintains an ongoing improvement mindset, and updates or changes providers when clear benefits in security or efficiency justify it. A static defense in a dynamic threat world can be risky, so regular tune ups and occasional overhauls with justification are healthy.
Developing an Incident Response IR plan is crucial, and leveraging your providers can greatly enhance it. Here’s an approach: First, assess your internal capabilities. What skills and resources do you have in house for IR? Identify gaps in expertise, coverage of hours, forensic tools, etc.. Next, involve a provider early for proactive preparation. Many top companies like IBM, Mandiant now part of Google Cloud, etc. offer incident response planning services where they’ll help you create or refine your IR plan and even run tabletop exercises. Take advantage of that; their real breach experience ensures your plan is practical. Ensure roles and responsibilities are clearly defined between your team and the provider. For instance, if you have a retainership with a firm like CrowdStrike or Cisco, your plan should state when and how to escalate to them. Include provider contact info, SLA expectations, and any legal or NDA prerequisites in the plan. Run mock drills at least annually some do quarterly mini drills have your provider participate if possible, or at least review the results with them. This helps everyone get familiar with the process before a crisis. Additionally, integrate your IR plan with providers’ services: if you use an MDR service, the plan should reflect how they will notify you and what actions they take vs what your team does. Many providers have an IR platform or playbooks ask if you can adapt those into your plan. During plan development, consider including your legal, PR, and execs as well because top providers can also advise on communications and compliance steps post incident. The ideal approach is collaborative: you have an internal plan that’s enhanced by the provider’s expertise, and both sides know how to coordinate. Also, clarify commercial terms before an incident if you might need emergency incident response from a firm, having a retainer contract in place is far better than negotiating terms during a breach. That retainer usually includes some hours for planning and drills too. In summary, engage your security providers not just as emergency contacts but as partners in planning. They’ve seen the worst; use that knowledge to bulletproof your IR plan. Document it, practice it, and keep it updated e.g., if you adopt a new technology, add a playbook for incidents on that. With a solid plan that integrates external experts, you’ll handle incidents calmly and effectively, minimizing damage.
The cyber landscape is always evolving. As of 2026 and beyond, a few emerging or rapidly maturing technologies stand out:
In summary, AI/ML, cloud native security SASE, zero trust, identity centric security, and automation are the themes to watch. When planning investments, consider these trends and ask providers how they’re adapting. Many of the top companies in this list are already incorporating these emerging techs into their roadmaps e.g., many have AI in marketing now, but look at concrete features. It’s wise to pilot new tech on a small scale to see value before full adoption. But don’t chase hype; focus on technologies that solve your current challenges or clear challenges you foresee like securing an increasingly cloud based workforce. The goal is to evolve your security capabilities proactively, so you’re not caught off guard by new threat paradigms or business shifts.
No single company leads every category. On this list, Palo Alto Networks, Fortinet, Cisco and Zscaler are the usual shortlist names for network and zero trust security, CrowdStrike and SentinelOne for endpoint and XDR, and IBM for consulting and managed security at enterprise scale. The right leader for you is the one that fits your environment, compliance needs and team size, so compare two or three in a proof of concept instead of choosing on brand size or market value.
The phrase usually means the Big Four professional services firms, Deloitte, PwC, EY and KPMG, which run cyber consulting, risk and incident response practices alongside their audit businesses. They are not security product vendors. People also use it loosely for the largest security product companies, such as Palo Alto Networks, CrowdStrike, Fortinet, Cisco and Zscaler. If you need a SOC 2 report, it must come from a licensed CPA firm; for products or managed detection, compare the vendors profiled above.
Several companies on this list publish FedRAMP authorizations for specific government offerings, as checked on 3 November 2026: CrowdStrike (Falcon platform for government, High), SentinelOne (EDR, AI SIEM, CNAPP and Wayfinder on AWS GovCloud, High), Zscaler (government versions of ZIA and ZPA, High), IBM (IBM Cloud for Government, High; MaaS360, Moderate), Palo Alto Networks (Government Cloud Services, Moderate), Rapid7 (InsightGovCloud, Moderate) and Cisco (Duo Federal and Webex for Government, Moderate). An authorization covers a defined boundary, not every product, so confirm the exact service on the FedRAMP Marketplace before procurement.
Selecting the right cybersecurity partners is a critical decision that should be guided by objective evaluation and an understanding of your unique needs. In this article, we provided a research driven overview of the top cybersecurity companies in the USA 2026. As the publisher of this guide and one of the listed providers, DeepStrike selected providers using the criteria above, focusing on proven expertise, service quality, and suitability for various use cases. Remember that best is context dependent: the best solution for a global bank might differ from that for a tech startup. Use this guide as a starting point to narrow your options and then engage directly with potential providers to ask the tough questions.
The companies listed cover different parts of the US market, from application penetration testing to FedRAMP-authorized cloud platforms and managed detection. Start from the rules in the regulatory section above (PCI DSS, SEC disclosure, NYDFS, HIPAA, FedRAMP, or CMMC), shortlist the providers whose published services and authorizations match them, and check each claim against the provider's current pages before you buy. DeepStrike publishes this guide and is one of the listed providers, so weigh its entry accordingly. Organizations with cross-border operations can pair this list with the top cybersecurity companies in Canada when building a North American shortlist.
Ultimately, cybersecurity is not a set and forget endeavor. Whichever partners or products you choose, maintain an active relationship. Continuously assess performance, stay updated on emerging threats your providers should help with, and don’t hesitate to adjust course as your company grows or new risks emerge. An effective security strategy in 2026 leverages both cutting edge technology and human expertise. The top companies we covered offer a mix of both and find the mix that earns your trust.
About the Author
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
