August 3, 2026
Updated: October 22, 2026
Scope, methodology, reports, tools, cost drivers, compliance, and buyer guidance

Mohammed Khalil
VAPT stands for vulnerability assessment and penetration testing. It combines broad checks for security weaknesses with focused, human-led testing of selected attack paths. A vulnerability assessment identifies and prioritizes weaknesses; a penetration test examines whether selected weaknesses or control failures can cause meaningful harm.
VAPT testing is useful when you need both coverage and evidence to guide remediation. The work should define which systems, user roles, and scenarios are tested, what actions are authorized, how findings are reported, and how fixes will be retested. The acronym alone does not define the service.
The main difference is breadth versus focused validation. Vulnerability assessment (VA) identifies and evaluates weaknesses across an approved scope. Penetration testing (PT) investigates selected controls and attack paths. Both can use automation and manual analysis.
| Dimension | Vulnerability assessment | Penetration testing |
|---|---|---|
| Primary question | What weaknesses have been detected? | What can an authorized attacker achieve against selected targets or controls? |
| Coverage | Broad across reachable assets and checks | Focused on authorized targets, roles, paths, and objectives |
| Access model | Often credentialed and uncredentialed checks for coverage | White-, gray-, or black-box knowledge chosen for the test objective |
| Automation | Central for scale, supplemented by analysis | Supporting role; human reasoning directs the test |
| Validation | Confirmation and context where useful | Controlled validation where authorized, safe, and necessary |
| Business logic | Limited unless assessed manually | Common focus for applications, APIs, and workflows |
| False positives | Must be triaged and classified | Lower for demonstrated findings, but interpretation and scope limits still matter |
| Production risk | Generally lower, but scans can still disrupt fragile systems | Potentially higher; requires windows, rate limits, monitoring, and stop conditions |
| Prioritization | Severity, exposure, exploit likelihood, asset context, and ownership | Demonstrated path, reachable impact, control failure, and business context |
| Cadence trigger | Recurring visibility, new assets, changes, and new vulnerability intelligence | Critical releases, trust-boundary changes, assurance milestones, incidents, or explicit obligations |
| Output | Assessed weakness inventory with coverage and remediation context | Evidence-backed findings, attack paths, control observations, limitations, and remediation |
| Limitation | Cannot prove that every detected weakness is exploitable | Cannot establish complete coverage or continuing security beyond the tested conditions |
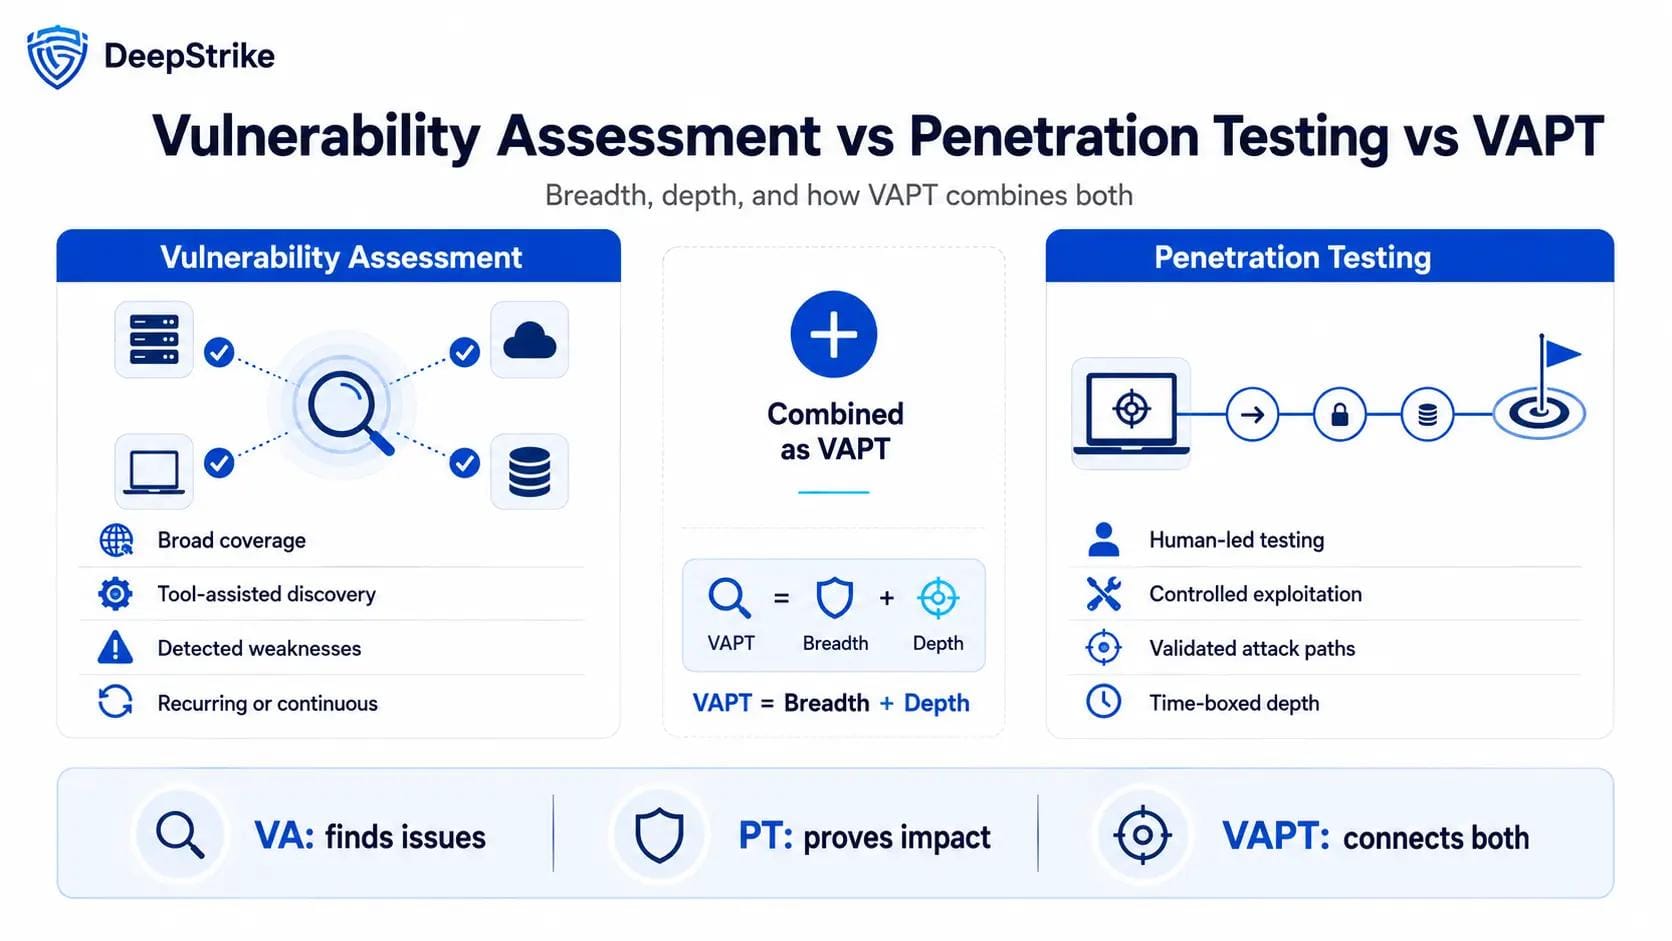
Figure 1. Vulnerability assessment provides breadth, penetration testing provides authorized depth, and VAPT coordinates both.
An assessment can combine asset discovery, credentialed and uncredentialed scanning, configuration review, dependency analysis, and manual confirmation. A useful result identifies affected assets, validation status, exposure, remediation priorities, and coverage gaps. It should explain the findings rather than simply export scanner results.
A penetration test examines authorization, business logic, identity relationships, and other paths that need human judgment. Controlled validation establishes impact where permitted and safe. A blocked path is useful evidence too, but neither result proves that every path was tested. See what penetration testing is and how it works for a deeper explanation.
| Your immediate decision | Start with | Evidence to request |
|---|---|---|
| Find and prioritize weaknesses across a changing estate | Vulnerability assessment | Asset coverage, authentication status, validated findings, and remediation owners |
| Test a critical release, control, or suspected attack path | Penetration testing | Tested roles and workflows, controlled validation, business impact, and limitations |
| Connect broad discovery with focused adversarial validation | Coordinated VAPT | Both sets of evidence, a shared remediation plan, and agreed retesting |
Choose according to the decision you need to make. Every option requires written authorization, defined limits, and an accountable owner for the results.
Common types of VAPT testing cover web applications, APIs, mobile apps, networks, cloud environments, and wireless or connected devices. These categories describe what is tested. Black-box, gray-box, and white-box describe the information and access testers receive.
| Type | Typical focus | Common decision supported |
|---|---|---|
| Web application | Authentication, authorization, session handling, business logic, server and client behavior | Release assurance, customer-facing risk, control validation |
| API | REST, GraphQL, object and function authorization, data exposure, rate controls, integrations | API-first product and partner assurance |
| Mobile | Client storage, platform controls, transport, reverse engineering, API behavior | Mobile release and sensitive-data assurance |
| Network and identity | Services, segmentation, directory and identity paths, privilege boundaries | Internal/external exposure and lateral-path assurance |
| Cloud | Identity and access, configuration, storage, workloads, management plane, authorized attack paths | Migration, architecture change, cloud-control assurance |
| Wireless and connected devices | Wireless controls, device interfaces, firmware, management paths | Site, device, IoT, or technology-specific assurance |
| Social engineering | Separately authorized phishing, pretexting, physical, or human-control scenarios | Human and process control validation |
For technology-specific scope, see web application penetration testing, cloud penetration testing, and the network penetration testing guide. Cloud work must respect provider policy and shared responsibility. Wireless, connected-device, social-engineering, physical, and denial-of-service scenarios each require explicit authorization and suitable safety controls.
These terms describe the information and access supplied to testers. They are separate from whether testing starts inside or outside a network.
| Model | Information and access supplied | Useful when |
|---|---|---|
| Black-box | Little prior system knowledge; credentials are usually not supplied | The question concerns what an external or otherwise uninformed starting position exposes |
| Gray-box | Selected documentation, test accounts, or limited system knowledge | You need to examine authenticated user roles, APIs, or realistic limited-access scenarios |
| White-box | Detailed architecture, relevant source or configuration, and agreed access | You need deeper control coverage or a focused review within a limited testing window |
More information can improve coverage and reduce time spent discovering basic system behavior. It does not authorize additional targets or unsafe actions. Define the exact starting conditions in the rules of engagement instead of relying on the label alone.
Combining assessment and penetration testing connects broad discovery with focused evidence. The benefits are clearer priorities, fewer unvalidated scanner findings, more useful remediation, and a documented record for risk, customer, or audit decisions. Those benefits depend on actual coverage and follow-through.
The work can be organized in three ways:
A report should distinguish observed weaknesses, confirmed impact, blocked paths, and untested conditions. Missing credentials, third-party restrictions, prohibited actions, and time limits all affect what the result can support.
| Scope element | Vulnerability assessment | Penetration testing | Authorization treatment |
|---|---|---|---|
| Asset and service discovery | Included when approved | Included when approved | Exact ranges, domains, accounts, and ownership documented |
| Credentialed checks | Optional for coverage | Optional for role/path testing | Credentials, roles, storage, and permitted use documented |
| Unauthenticated testing | Common for external visibility | Common for selected attacker perspectives | Sources, rate limits, and exclusions documented |
| Manual validation | Used to confirm and contextualize | Core human-led activity | Techniques remain inside the rules of engagement |
| Controlled exploitation | Usually avoided or narrowly limited | Used only where necessary, safe, and permitted | Explicit written permission and stop conditions required |
| Privilege escalation or lateral movement | Normally outside VA | Optional for selected paths | Exact depth, target boundaries, and evidence limits required |
| Social engineering or physical testing | Separate scope | Separate scenario | Separate objectives, populations, pretexts, and approvals required |
| Denial-of-service or destructive actions | Excluded by default | Excluded by default | Separately approved only with strict safety planning |
| Third-party or provider-managed systems | Not implied by reachability | Not implied by reachability | Asset-owner and provider permissions required |
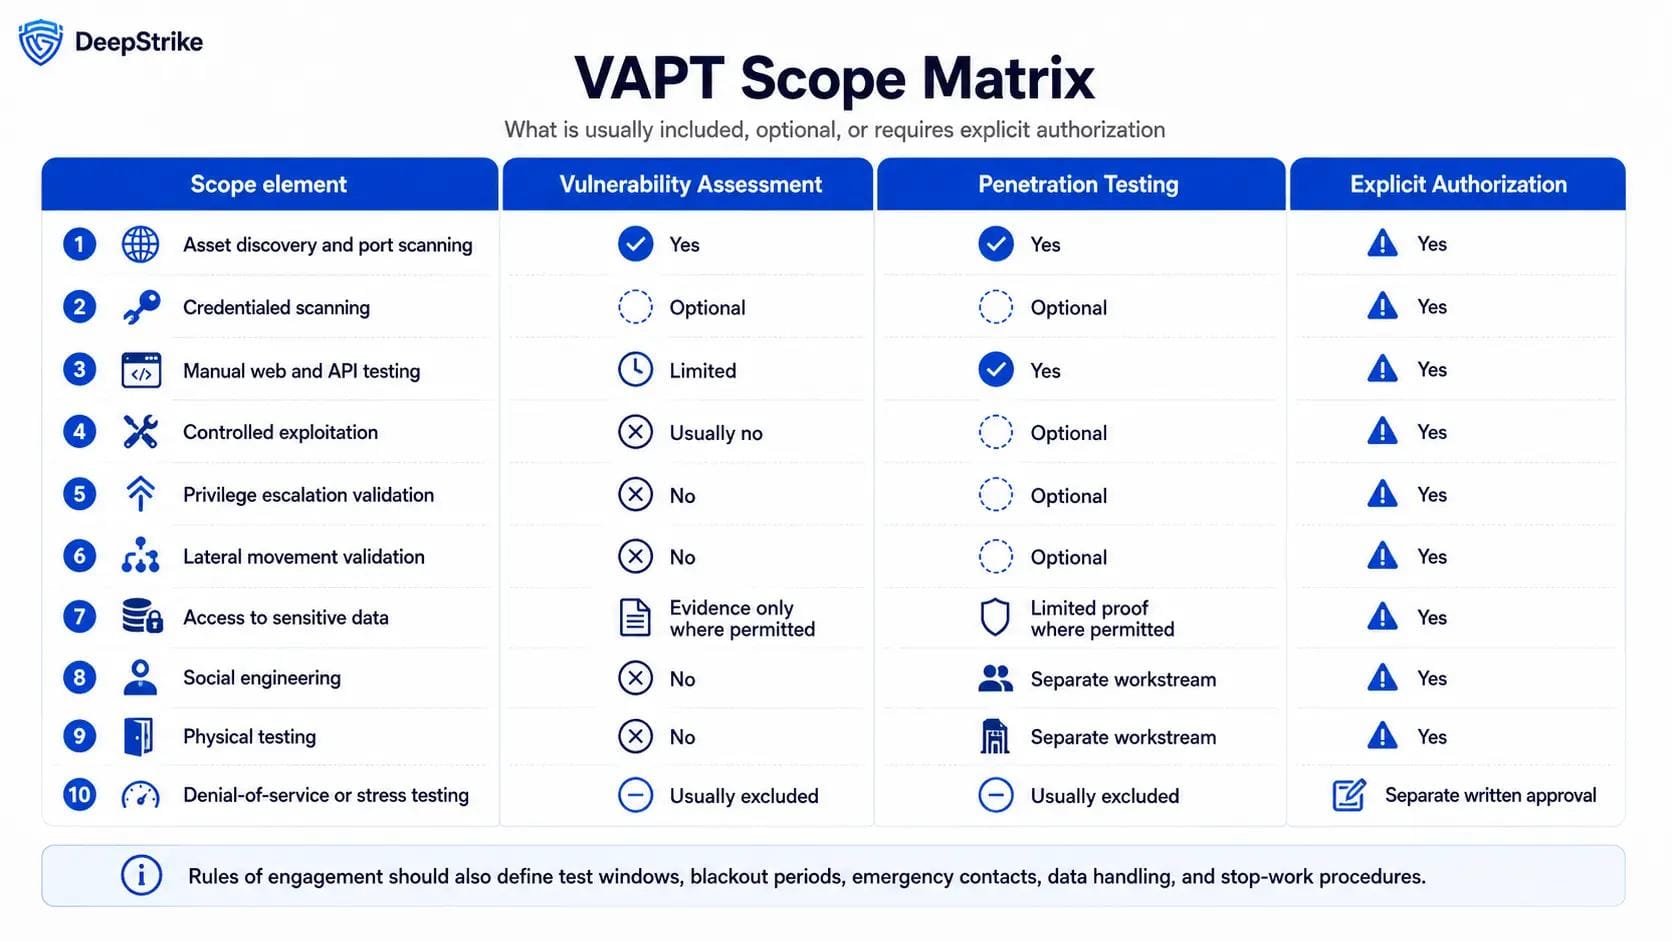
Figure 2. Reachability is not authorization: scope elements require documented permission and safety limits.
Credentialed checks improve visibility into configurations and roles; unauthenticated checks show what the chosen starting position can reach. Record unavailable credentials as a coverage limitation. Internal or external access does not establish ownership: connected SaaS, cloud, and third-party systems still need the relevant permissions.
Fragile, clinical, industrial, or safety-critical systems may require staging, passive review, rate limits, maintenance windows, or exclusions. Choose a safer method when the operational risk exceeds the evidence value.
The following is a practical engagement structure informed by the Penetration Testing Execution Standard, NIST SP 800-115, and OWASP web-testing guidance. It is not a universal mandatory sequence; the objective, system, authorization, and evidence needs determine the final design.
For more depth on the penetration-testing workstream, use the dedicated penetration testing methodology guide.
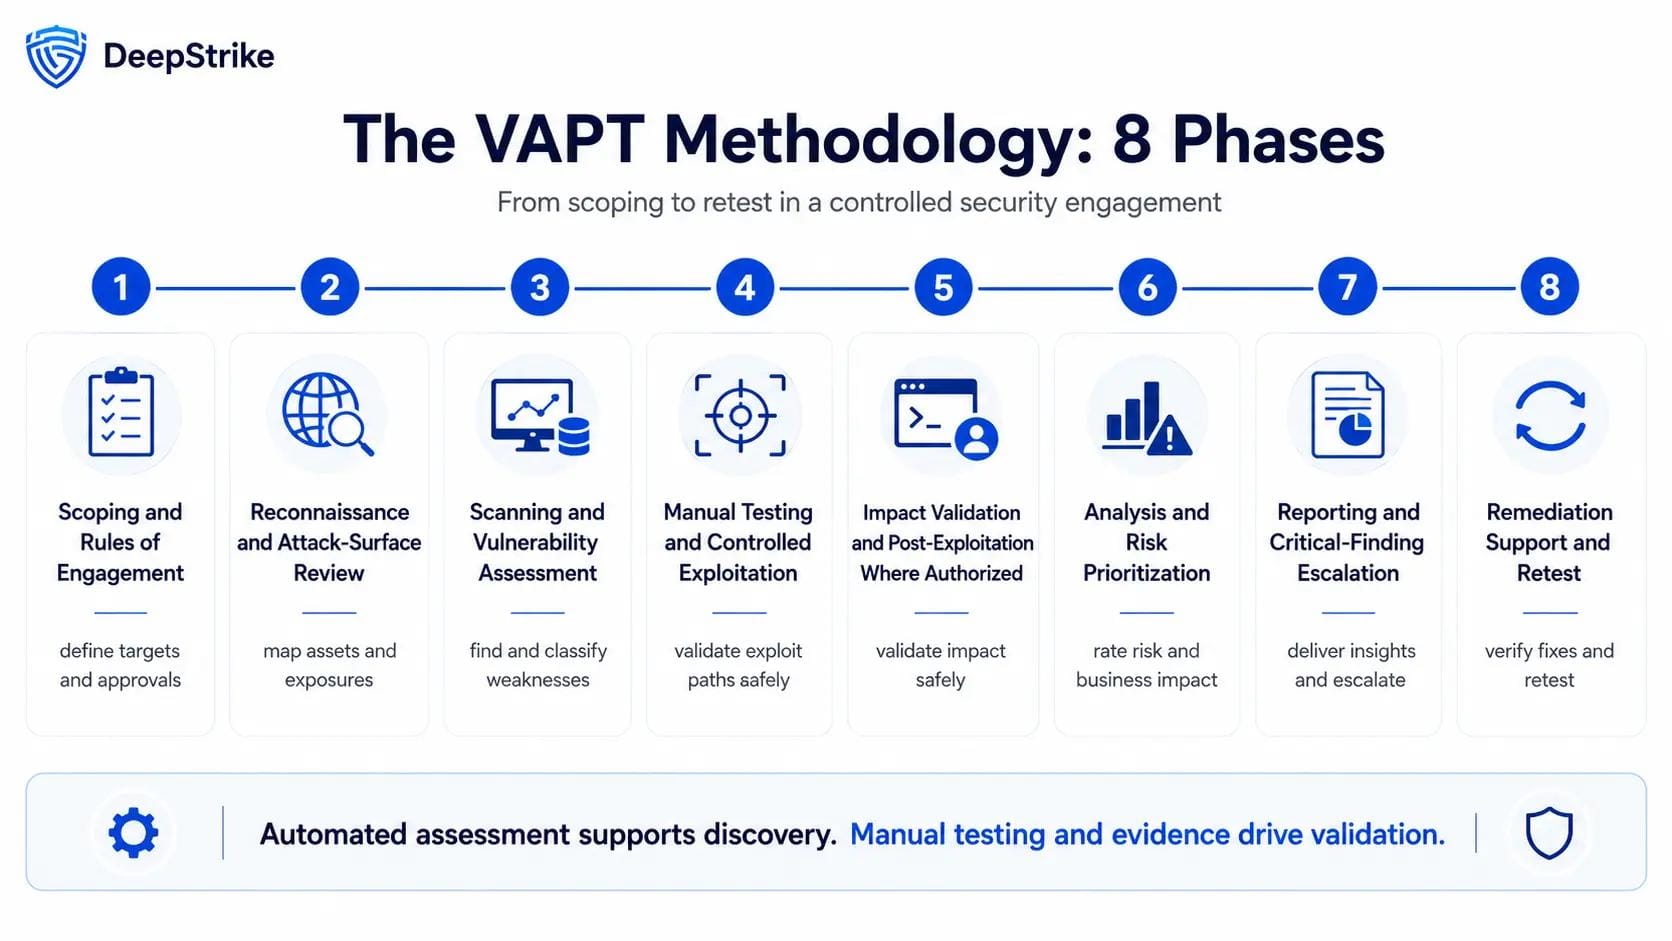
Figure 3. A VAPT engagement moves from authorization and discovery to evidence, remediation support, and scoped retesting.
| Phase | Expected evidence | Primary owner | Safety or quality checkpoint |
|---|---|---|---|
| Scope and rules | Authorization, target list, exclusions, roles, windows, stop plan | Sponsor and asset owners | Do not test until ownership and authority are clear |
| Reconnaissance | Asset/interface map and assumptions | Test lead and system owners | Reconcile discovered assets before expanding activity |
| Discovery and review | Raw signals, coverage, credential status, configuration observations | Test team | Tune rates; track unreachable and unauthenticated coverage |
| Manual analysis | Reproduction notes, validation status, selected paths | Test lead | Require human review; avoid treating tool output as proof |
| Impact analysis | Minimum necessary proof and affected boundary | Test lead and incident contact | Stop at agreed impact; minimize sensitive data and persistence |
| Reporting | Finding records, limitations, priorities, owners, dependencies | Test lead and risk owner | Separate confirmed, suspected, blocked, and untested conditions |
| Remediation support | Clarifications, root-cause decisions, exception record | Engineering and risk owners | Keep status and residual risk visible |
| Retest and closure | Retest scope, method, evidence, outcome, closure decision | Test lead and finding owner | Do not represent a focused retest as a new full assessment |
Use COVER to match the activity to the decision. COVER is a DeepStrike decision aid, not an industry standard and not a guarantee of an outcome.
The answers should determine the activity, authorized scope, access model, trigger or cadence, evidence, remediation ownership, and retest criteria.
| Scenario | Recommended activity | Why | Critical scope question | Trigger or cadence logic | Expected evidence |
|---|---|---|---|---|---|
| Asset visibility is incomplete | Vulnerability assessment beginning with inventory validation | The first need is defensible coverage, not an assumed attack path | Which domains, ranges, accounts, environments, and owners are known? | Repeat after material asset or ownership change and new exposure | Reconciled inventory, coverage gaps, findings, and confidence |
| Large, changing estate needs routine discovery | Vulnerability assessment within vulnerability management | Scale and volatility require repeatable discovery and triage | Which assets can be assessed safely and with authenticated access? | Based on exposure, change rate, threat intelligence, and remediation cycles | Trendable findings, owners, and verification status |
| Critical application is approaching release | Gray- or white-box penetration test supported by targeted assessment | Focused adversarial assurance can test roles and logic before launch | Which roles, APIs, transactions, data, and integrations are critical? | Before a material release and after security-relevant design change | Validated findings, tested flows, limits, and release-decision input |
| Suspected path or high-value control needs validation | Focused penetration test | The objective is to test a hypothesis, not survey the estate | What start condition, target outcome, and impact limit define the scenario? | When threat modeling, an incident, or assessment evidence supports the hypothesis | Path evidence, blocked steps, control behavior, and uncertainty |
| Customer or contract asks for evidence | VA, PT, or both according to the exact clause | “VAPT” may not match the requested scope, independence, or report | What systems, methods, qualifications, dates, and artifacts are required? | According to the obligation and material changes | Evidence mapped to the requirement with limitations |
| Material architecture or identity change | Targeted assessment plus PT where attack paths changed | New trust, privilege, or connectivity can create known and contextual weaknesses | Which boundaries, identities, data flows, and inherited controls changed? | Before or after rollout according to risk and rollback capability | Changed-scope coverage, validated paths, and remediation actions |
| A fix needs verification | Focused retest | The decision is whether remediation blocks the original condition and variants | Which finding, root cause, instances, and variants are in retest scope? | After the fix is deployed in the agreed environment | Fixed, partial, failed, untested, residual-risk, and closure status |
| Mature program combines discovery and assurance | Coordinated VAPT program | Broad visibility and focused evidence serve different decisions | Which assets need continuous ownership and which scenarios merit time-bounded testing? | Risk-based discovery plus event-driven or planned assurance | Coverage trends, paths, control evidence, remediation, and retest history |
Prioritization should combine technical severity with the environment in which a weakness exists. Useful inputs include confirmed path evidence, asset and business criticality, reachability, exposure, privileges and prerequisites, affected data, potential impact, compensating controls, control successes and failures, operational safety, dependency order, and the effort required to remove the root cause.
CVSS v4.0 communicates technical vulnerability severity through Base, Threat, Environmental, and Supplemental metric groups. When a numerical score is used, record the version and vector where appropriate. CVSS is not a complete business-risk score and cannot replace environment-specific judgment.
EPSS estimates the probability that a published CVE will be exploited in the wild in the next 30 days. It is an exploitation-likelihood input for CVEs, not a severity score, a certainty, or a measure for every configuration or business-logic flaw.
The CISA Known Exploited Vulnerabilities Catalog identifies vulnerabilities with evidence of exploitation in the wild. Inclusion should inform prioritization; absence does not make a vulnerability safe. Exposure, affected versions, controls, and business consequence still matter.
Confirmed attack-path evidence deserves weight, but it is not the only signal. A finding can remain important when validation was unsafe, prohibited, unnecessary, or blocked by a temporary condition. Conversely, a successful proof of concept demonstrates the tested condition; it does not establish the maximum possible impact.
Consider this illustrative prioritization example; it is not a reported client finding. A medium-severity issue affects an internet-reachable payment-approval workflow and lets a low-privilege user cross a critical authorization boundary. A separate high-severity library issue exists on an isolated development host behind strong segmentation, with no sensitive data and a compensating control. The workflow issue may need earlier remediation because reachability, business role, and observed path create greater current risk. The isolated issue still needs an owner and an explicit decision.
Prioritize root causes and dependencies as well as tickets. Repairing a central authorization control, identity boundary, or deployment pattern can reduce several findings more reliably than patching symptoms one by one. Keep “open,” “fixed,” “partially fixed,” “mitigated,” “accepted,” and “not retested” as distinct states, with residual risk and decision authority recorded.
Tools support a VAPT engagement; they do not define its quality. Selection depends on the target, authorization, environment sensitivity, rate limits, and tester judgment.
| Purpose | Representative tools | What they support |
|---|---|---|
| Vulnerability discovery | Nessus, Qualys, OpenVAS, InsightVM | Broad detection, configuration checks, credentialed coverage |
| Network mapping | Nmap and protocol-specific clients | Hosts, services, segmentation, and attack-surface context |
| Web and API testing | Burp Suite, ZAP, custom scripts | Request analysis, authorization, input handling, and workflow testing |
| Controlled validation | Metasploit and specialist utilities | Reproducible testing of selected conditions where authorized |
| Internal identity testing | Directory, credential, graph, and protocol tools | Trust relationships, privileges, and lateral-path analysis |
| Cloud assessment | Prowler, ScoutSuite, Pacu, provider-native tools | IAM, configuration, storage, and authorized cloud paths |
For tool-selection criteria and limitations, see our penetration testing tools guide. A tool list alone does not establish the quality or depth of an engagement.
These sources serve different purposes. Awareness lists, verification standards, testing guides, risk frameworks, adversary knowledge bases, and severity models must not be presented as interchangeable or as one complete VAPT methodology.
| Source | Version or status used here | Appropriate role | Boundary |
|---|---|---|---|
| OWASP Top 10 | 2025 edition | Web-application awareness and risk themes | Not a complete test plan |
| OWASP WSTG | v4.2 stable | Detailed web-testing guidance | Must be adapted to the application and scope |
| OWASP ASVS | v5.0.0 | Application security verification requirements | Coverage target, not an automatic engagement method |
| OWASP MASVS and MASTG | MASVS verification requirements and maintained MASTG testing guidance | Mobile verification requirements and testing guidance | Requires platform and application context |
| PTES | Published community standard | Penetration-test engagement structure and technical guidance | Not a law or universal contractual requirement |
| NIST SP 800-115 | Final, 2008 | US technical guide to testing and assessment | Guidance, not a complete modern program by itself |
| OSSTMM | Version 3 | Operational security testing methodology | Use only when its model fits the objective |
| MITRE ATT&CK | Continuously updated knowledge base | Threat-informed adversary behavior and technique mapping | Not a standalone penetration-test method |
| NIST CSF | Version 2.0 | Cybersecurity-risk outcomes and communication | Does not prescribe how every outcome must be achieved |
| CVSS | Version 4.0 | Technical vulnerability severity communication | Not exploit likelihood or business risk |
The OWASP Top 10:2025 is an awareness document and risk-categorization baseline. It should inform communication and coverage conversations, not replace OWASP testing guidance or application-specific business-logic and authorization testing.
The OWASP Web Security Testing Guide v4.2 is the current stable web-testing guide.
OWASP ASVS v5.0.0 can help define application control-verification requirements and rigor.
For mobile work, OWASP MASVS supplies verification requirements, while the MASTG supplies maintained testing guidance.
NIST SP 800-115 provides technical guidance for planning and conducting security testing and assessment, but an engagement still needs current system-specific methods and authorization controls.
OSSTMM 3 is an operational security-testing methodology, not a universal compliance requirement.
MITRE ATT&CK is a knowledge base of adversary tactics and techniques. It can support threat-informed scenarios, but it does not define a complete test scope, authorization model, or evidence standard.
NIST CSF 2.0 provides high-level cybersecurity outcomes and does not prescribe one method for achieving them.
The list helps communicate common risk themes. A professional web VAPT should use a broader, scoped test plan rather than claiming “OWASP Top 10 coverage” as proof of completeness.
The report is the core deliverable. It should serve executives who need risk and business context and engineers who need attributable evidence and actionable remediation. It must not be a scanner export with branding.
| Section | What it should contain |
|---|---|
| Executive summary | Material paths, business consequence, important controls, and decision implications |
| Authorization and scope | Owner, targets, roles, dates, environments, exclusions, and access model |
| Method and coverage | Activities performed, applicable guidance, tools where relevant, unreachable scope, and limitations |
| Findings | Affected assets, status, evidence, technical explanation, and severity model |
| Path and control evidence | Demonstrated steps, blocked steps, control behavior, and bounded negative evidence |
| Business context | Data, systems, users, or processes placed at risk under the tested conditions |
| Remediation | Specific fixes, root cause, affected instances, owners, dependencies, and acceptance criteria |
| Retest | Agreed retest scope, method, outcome, residual risk, and closure status |
| Appendices | Assumptions, relevant references, sanitized tooling detail, and out-of-scope items |
The penetration testing report guide covers detailed deliverable design. A combined VAPT report should still distinguish raw scanner signals, assessed weaknesses, confirmed findings, suspected conditions, validated paths, blocked paths, unverified items, and untested conditions.
Evidence should be sufficient for remediation and review without collecting unnecessary personal, production, or customer data. Define access, encryption, delivery, retention, and deletion before testing. Link each finding to an owner and dependency, and keep accepted or unresolved residual risk visible instead of collapsing every item into “closed.”
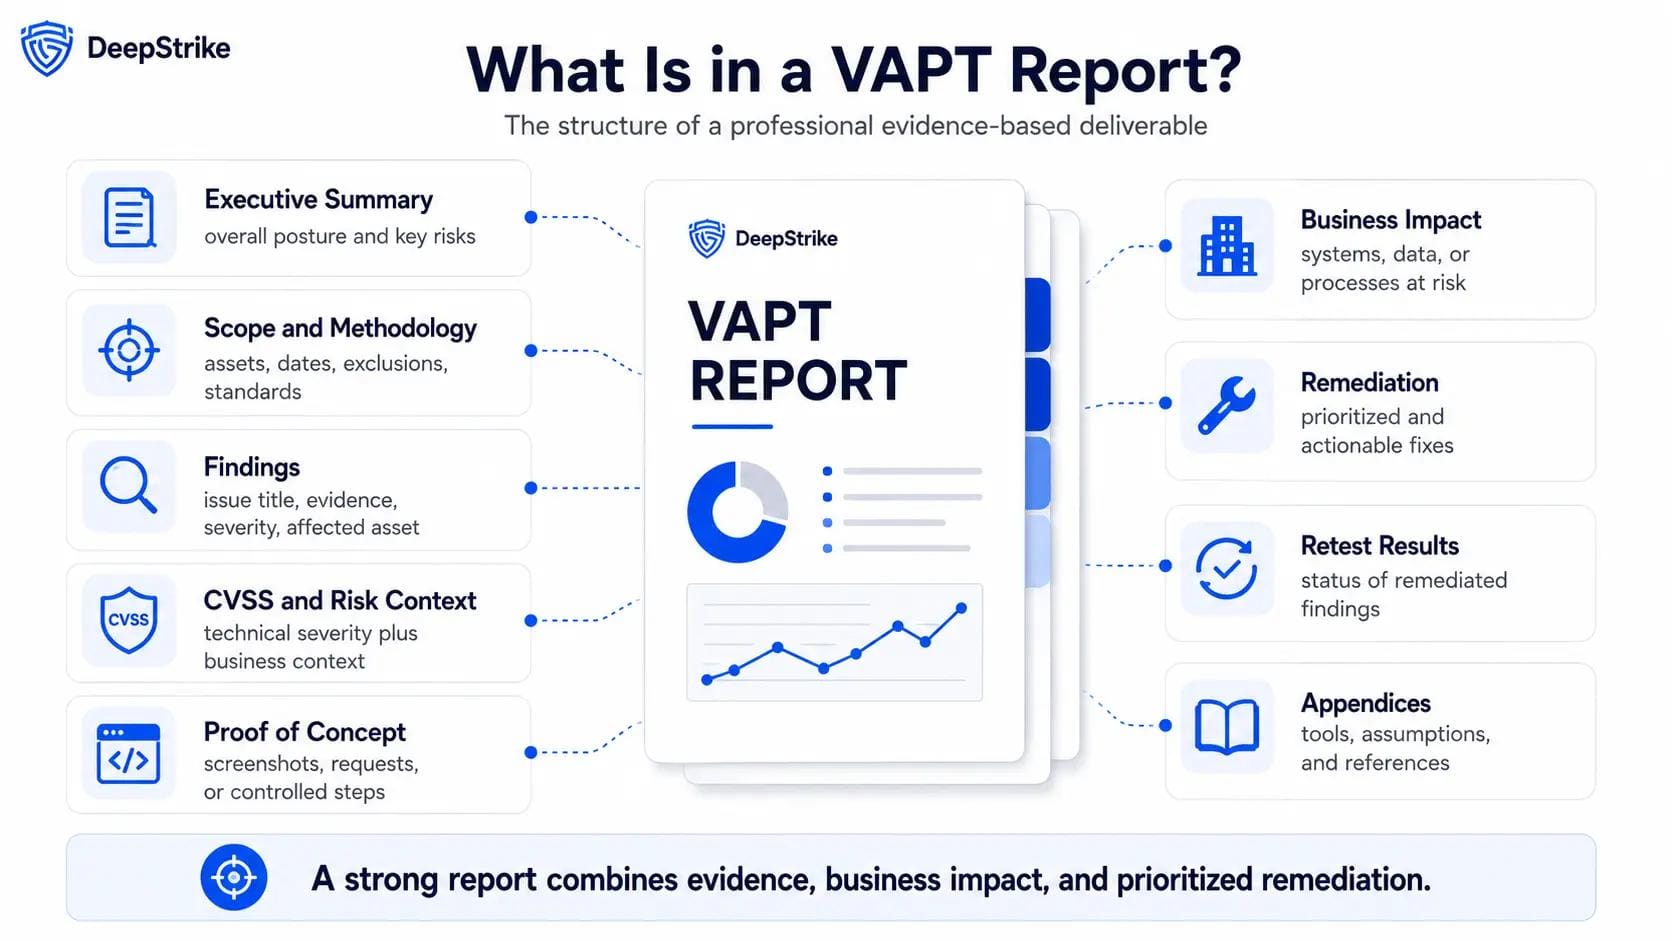
Figure 4. A defensible report connects scope, evidence, impact, remediation, and retest status.
Suppose a SaaS company authorizes testing of two synthetic tenants in a staging environment. Both contain dummy records. The objective is to determine whether ordinary users can cross tenant boundaries. This is an explanatory example, not a DeepStrike client result or a claim that a particular scanner produced these findings.
| Evidence stage | Example record | Decision it supports |
|---|---|---|
| Assessment coverage | The team inventories the application, API routes, dependency signals, and available user roles; it records any inaccessible routes | Whether the planned assets and perspectives were actually assessed |
| Manual test | Using approved test accounts, the tester checks whether one tenant can retrieve a dummy record belonging to the other | Whether the application enforces the intended authorization boundary |
| Controlled result | A permitted check returns the other test tenant's dummy record; the tester stops after the minimum agreed proof | A confirmed cross-tenant access finding within the tested conditions |
| Finding record | Affected route and build, prerequisites, sanitized request/response evidence, impact, scope limits, and severity rationale are recorded | What engineering must reproduce and what the risk owner must evaluate |
| Remediation | The application owner applies server-side tenant authorization consistently and adds regression tests | Whether the root cause is addressed across affected instances |
| Retest | The same scenario and agreed neighboring roles or routes are tested on the fixed build; authorized access is checked as well | Whether the fix blocks the original flaw without breaking legitimate access |
If one route is fixed but another agreed variant still exposes a dummy record, the outcome is partially fixed. If the fixed environment or required account is unavailable, it is not retested. Neither status should be presented as a clean closure.
The important distinction is the evidence trail: an inventory or scan signal becomes an assessed condition, a controlled test establishes a specific impact, and a retest evaluates an agreed correction. The report must also identify what was not examined. Do not turn one successful test into a claim about every tenant, route, build, or production record.
VAPT is not:
A clean result is a bounded observation about an agreed scope, time, access model, and set of actions. Its value depends on tester judgment, authorization, coverage, evidence, remediation, and retesting.
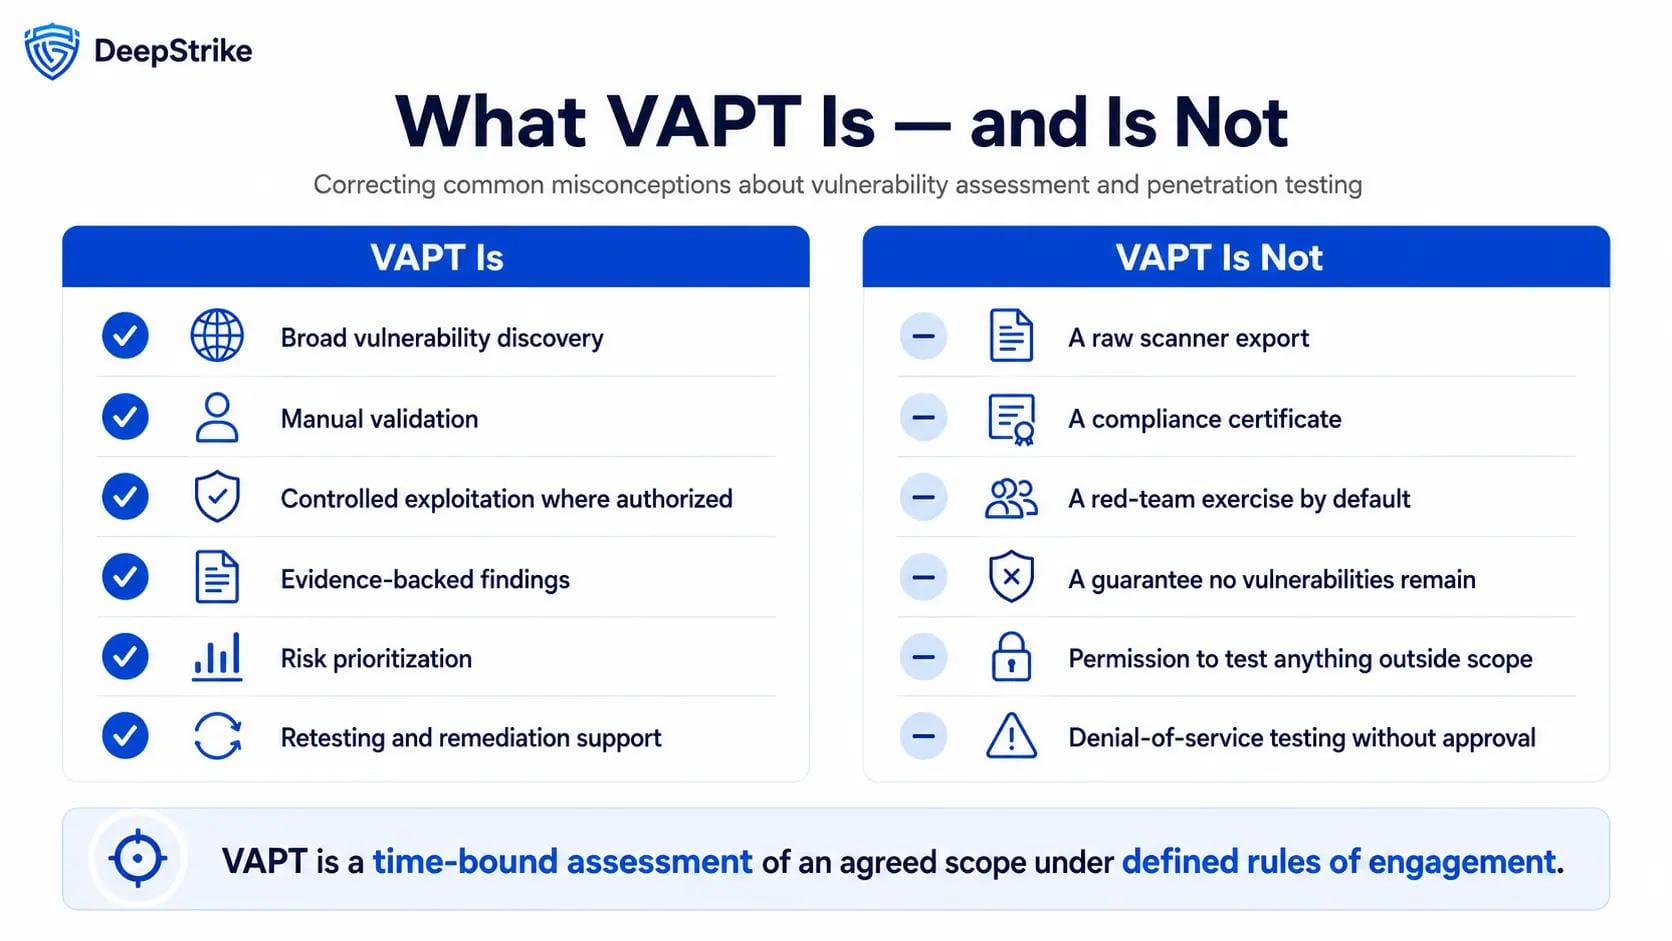
Figure 5. VAPT is bounded security evidence, not unrestricted exploitation, certification, or a guarantee.
Scanning, assessment, penetration testing, and ongoing vulnerability management serve different purposes. Use the distinctions below when a proposal combines several labels.
| Practice | Primary question | Typical approach | Typical output | Important limit |
|---|---|---|---|---|
| Vulnerability scanning | Which known indicators can tools detect? | Automated or tool-assisted checks | Raw or normalized scanner results | Coverage and accuracy depend on reachability, credentials, signatures, and configuration |
| Vulnerability assessment | What weaknesses exist and how should they be understood? | Scanning, configuration review, analysis, and manual validation | Contextual weakness inventory and remediation guidance | Usually does not attempt broad adversarial exploitation |
| Vulnerability management | How will the organization continuously discover, prioritize, remediate, and verify weaknesses? | Recurring governance and operational workflow | Owned backlog, exceptions, metrics, and verification | A program, not a one-time test |
| Penetration testing | Can selected controls or attack paths be defeated? | Human-led adversarial analysis supported by tools | Validated findings, paths, limitations, and evidence | Time-, scenario-, and scope-bounded |
| VAPT | How can breadth and focused validation support one assurance decision? | Objective-specific coordination of VA and PT | Consolidated evidence, priorities, remediation, and retest status | The label alone does not define method or depth |
| Security audit | Do controls, records, and practices meet defined criteria? | Evidence review, interviews, sampling, and testing | Control conclusions, exceptions, and audit evidence | Not automatically an adversarial test |
| Red team | Can an adversary achieve broader objectives while testing detection and response? | Goal-led multi-stage simulation across authorized domains | Objective outcomes, attack narrative, and defensive observations | Requires separate goals, rules, and authorization |
A VAPT program needs owners and repeatable decisions between individual engagements. Its policy and working practices should cover:
The policy should also distinguish VAPT from separately scoped red-team, social-engineering, physical, resilience, code-review, and architecture-review work.
Compliance language must be tied to the exact framework, edition, scope, validation path, and responsible authority. “VAPT” is not a substitute for a requirement that separately specifies scanning, penetration testing, assessor independence, evidence, segmentation validation, remediation, or retesting.
| Source or obligation | Formal position | How VAPT may relate | Boundary |
|---|---|---|---|
| PCI DSS v4.0.1 | Specific scanning and penetration-testing requirements for applicable payment-card scope | VA and PT evidence can address the relevant 11.3 and 11.4 controls | Applicability depends on entity, environment, validation path, and segmentation use |
| FTC Safeguards Rule | Specific testing duties for covered financial institutions, with a continuous-monitoring alternative | Annual PT and six-month system-wide VA apply when the stated alternative conditions are met; material changes also trigger testing | Not a universal rule for every company |
| HIPAA Security Rule | Current risk-analysis and safeguard duties; more specific scanning/PT cadence remains proposed | VA can inform risk analysis; PT can support risk-based control evaluation | The proposed annual PT and six-month scanning language is not final law |
| SOC 2 | Criteria-based attestation over selected controls | VAPT evidence may support risk assessment, monitoring, or selected control operation | No universal penetration-testing checkbox applies to every SOC 2 scope |
| ISO/IEC 27001:2022 | Risk-based ISMS requirements | VAPT can support vulnerability and control evidence within the selected risk treatment | No one pentest cadence applies to every certified or implementing organization |
| GDPR Article 32 | Risk-appropriate technical and organizational measures, including regular testing/evaluation | VAPT may be one way to test selected security measures | GDPR does not prescribe VAPT as a universal method |
| NIST publications | Voluntary guidance or tailorable control catalogs unless adopted by an authority or contract | VA, PT, and VAPT can support selected outcomes and controls | NIST does not create one universal private-sector annual pentest mandate |
In NIST SP 800-53 Rev. 5, including Release 5.2.0, RA-5 and CA-8 distinguish vulnerability monitoring and scanning from penetration testing. Their scope and frequency are organization-defined. The catalog is tailorable and does not automatically bind every private organization.
For applicable payment-card scope, the PCI SSC document library lists PCI DSS v4.0.1 as current. Requirements 11.3.1 and 11.3.2 address periodic internal and approved-scanning-vendor external scans; 11.3.1.3 and 11.3.2.1 address scans after significant changes. Requirement 11.4.1 defines the penetration-testing methodology. Requirements 11.4.2 and 11.4.3 cover internal/external cadence and change-triggered testing; 11.4.4 addresses correction and repeat testing; and 11.4.5–11.4.6 address segmentation testing where applicable.
The FTC Safeguards Rule guidance states that covered financial institutions may use continuous monitoring for information systems; if they do not, they must conduct annual penetration testing and vulnerability assessments including system-wide scans every six months, plus testing after material changes or other material-impact circumstances. Coverage and exemptions must be evaluated against the rule.
The current HIPAA Security Rule requires regulated entities to protect electronic protected health information through appropriate safeguards and risk analysis. It does not currently create a general annual-penetration-testing requirement.
HHS states that the HIPAA Security Rule NPRM would require vulnerability scanning at least every six months and penetration testing at least once every 12 months, while also stating that the current rule remains in effect during rulemaking. Treat those proposed frequencies as proposal status unless HHS finalizes the change.
The AICPA Trust Services Criteria support evaluation of controls relevant to security, availability, processing integrity, confidentiality, and privacy. Whether penetration testing is part of the evidence depends on the organization's controls, commitments, auditor judgment, and scope; SOC 2 does not impose one universal PT checkbox.
ISO/IEC 27001:2022 defines requirements for an information security management system and risk management. VAPT can support selected risk treatment and control evidence, but exact control mapping must use the licensed edition and the organization's Statement of Applicability.
GDPR Article 32 calls, as appropriate to risk, for a process that regularly tests, assesses, and evaluates the effectiveness of security measures. It does not name VAPT as the universal implementation.
Cyber-insurance questionnaires, customer demands, and contractual testing clauses are contract-specific. Verify the exact wording, systems, independence, date, qualifications, artifacts, and retest expectations rather than translating “annual test” into an assumed universal VAPT package.
A report can support an audit, customer review, insurance request, or control-assurance process. It does not by itself establish compliance, certification, legal conformity, audit success, breach prevention, or immunity from enforcement.
For healthcare scope and evidence planning, see the HIPAA penetration testing guide.
The broader penetration testing for compliance guide covers deeper framework and evidence planning.
There is no universal schedule. Cadence should follow change rate, internet exposure, criticality, threat changes, releases and migrations, identity or architecture changes, incidents, control failures, contractual or regulatory obligations, unresolved findings, and remediation cycles.
Vulnerability assessment may run frequently in a changing estate, but frequency alone does not create coverage or quality. Teams must know which assets were reached, whether checks were authenticated, how results were validated, and whether owners remediated and verified them.
Penetration testing should follow a specific assurance decision: a critical release, a material trust-boundary change, a new high-value workflow, a supported attack-path hypothesis, a customer obligation, an incident, or a risk-based program milestone. Repeating the same scope mechanically may provide less value than adapting the test to what changed.
Continuous scanning is not continuous penetration testing. A continuous penetration-testing delivery model may enable faster human-led validation, but the tester involvement, triggers, scope, and retest terms still need definition.
A focused retest checks agreed remediation. It does not replace a future full assessment or penetration test, and a clean test does not promise that the environment will remain secure.
Cost and duration depend on the decision and scope, not on the acronym. Important factors include asset count and type, authenticated roles, user journeys, API and integration depth, business-logic complexity, internal identity and segmentation, cloud accounts and regions, access model, production limits, test windows, evidence requirements, report audiences, workshops, escalation, and retest terms.
For published budget benchmarks and their scope assumptions, see the penetration testing cost guide. Treat benchmarks as orientation; an engagement quote should reflect your actual scope.
The vulnerability assessment pricing guide explains factors specific to broad assessment work.
Ask for a schedule that separates access preparation, active testing, reporting, remediation, and retesting. A quoted test window is not the same as the elapsed time until findings are closed. Delayed credentials, unstable environments, or unavailable owners can change the schedule even when tester effort stays the same.
Compare proposals only after scope, access, exclusions, evidence, tester effort, deliverables, and retesting are aligned. A lower quote may represent a narrower scan, fewer roles, fewer targets, limited manual analysis, or reduced remediation support rather than equivalent work.
VAPT validates rather than replaces the controls used throughout development and operations:
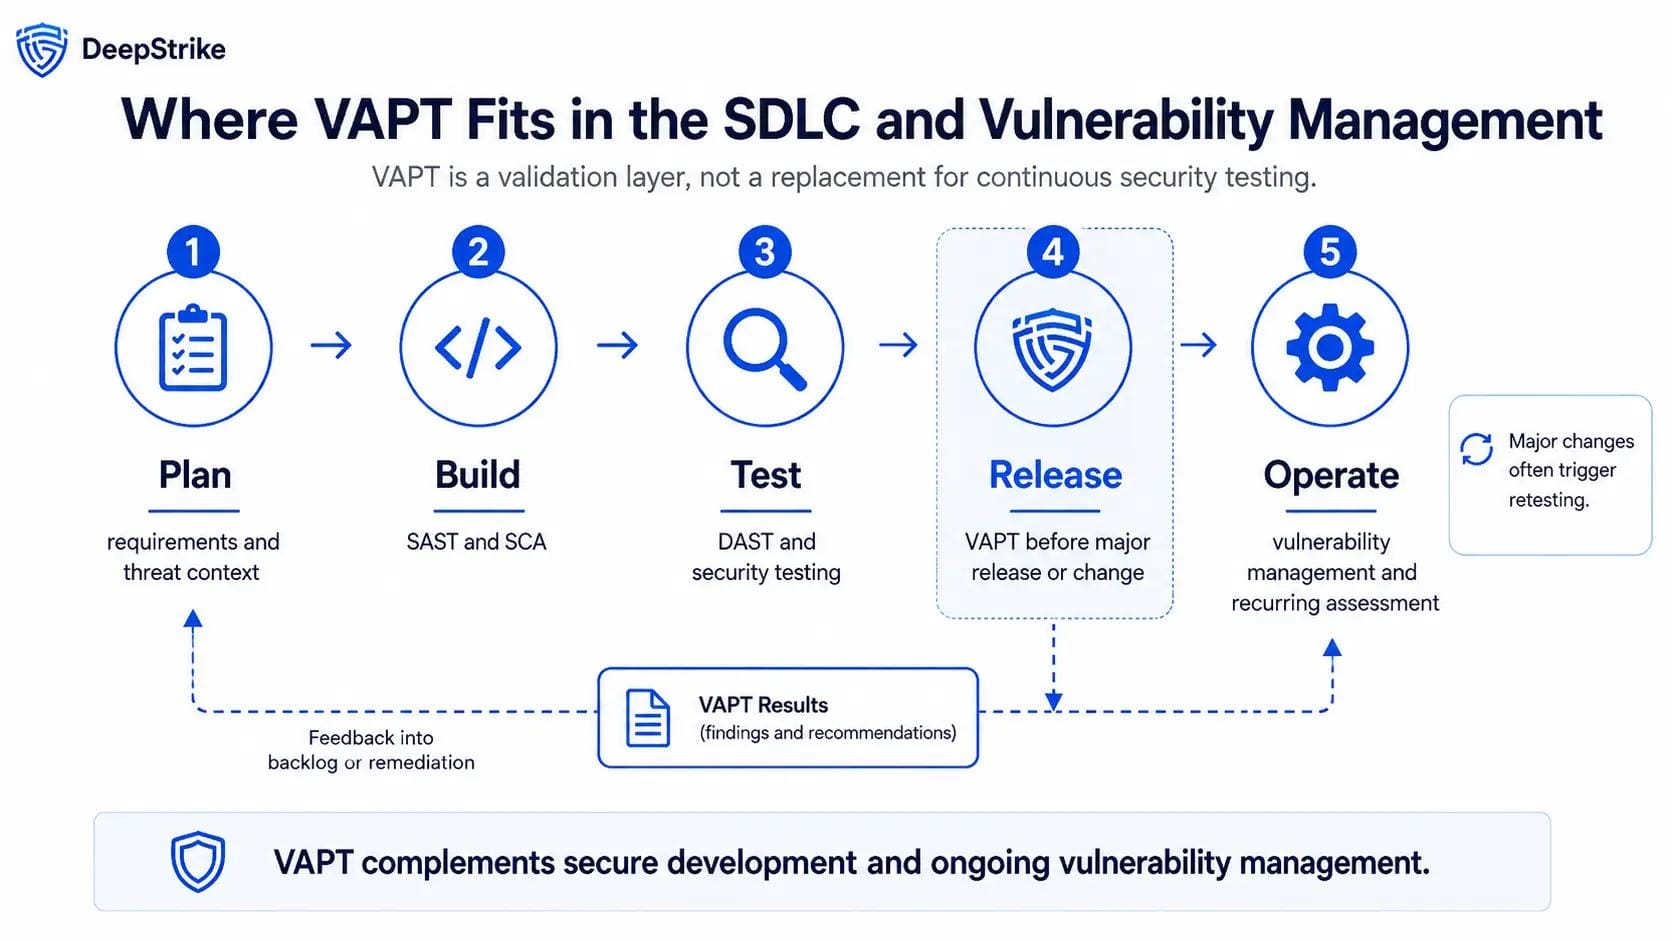
Figure 6. VAPT complements continuous vulnerability management at risk-significant release and change points.
Start with the decision the engagement must support. A useful proposal makes the objective, exact assets and roles, ownership, access model, evidence, safety constraints, reporting, and retesting comparable before price or brand claims are evaluated.
Ask prospective providers six questions:
Do not use one certification, a fixed “manual testing percentage,” or a tool list as a universal quality proxy. Relevant experience, reasoning, authorization discipline, evidence, safety, and communication matter more than an arbitrary marketing ratio.
Use our guide to choosing a penetration testing company to evaluate provider evidence and prepare procurement questions.
The VAPT service provider guide provides a starting point for researching providers. Confirm each provider's current capabilities against your scope.
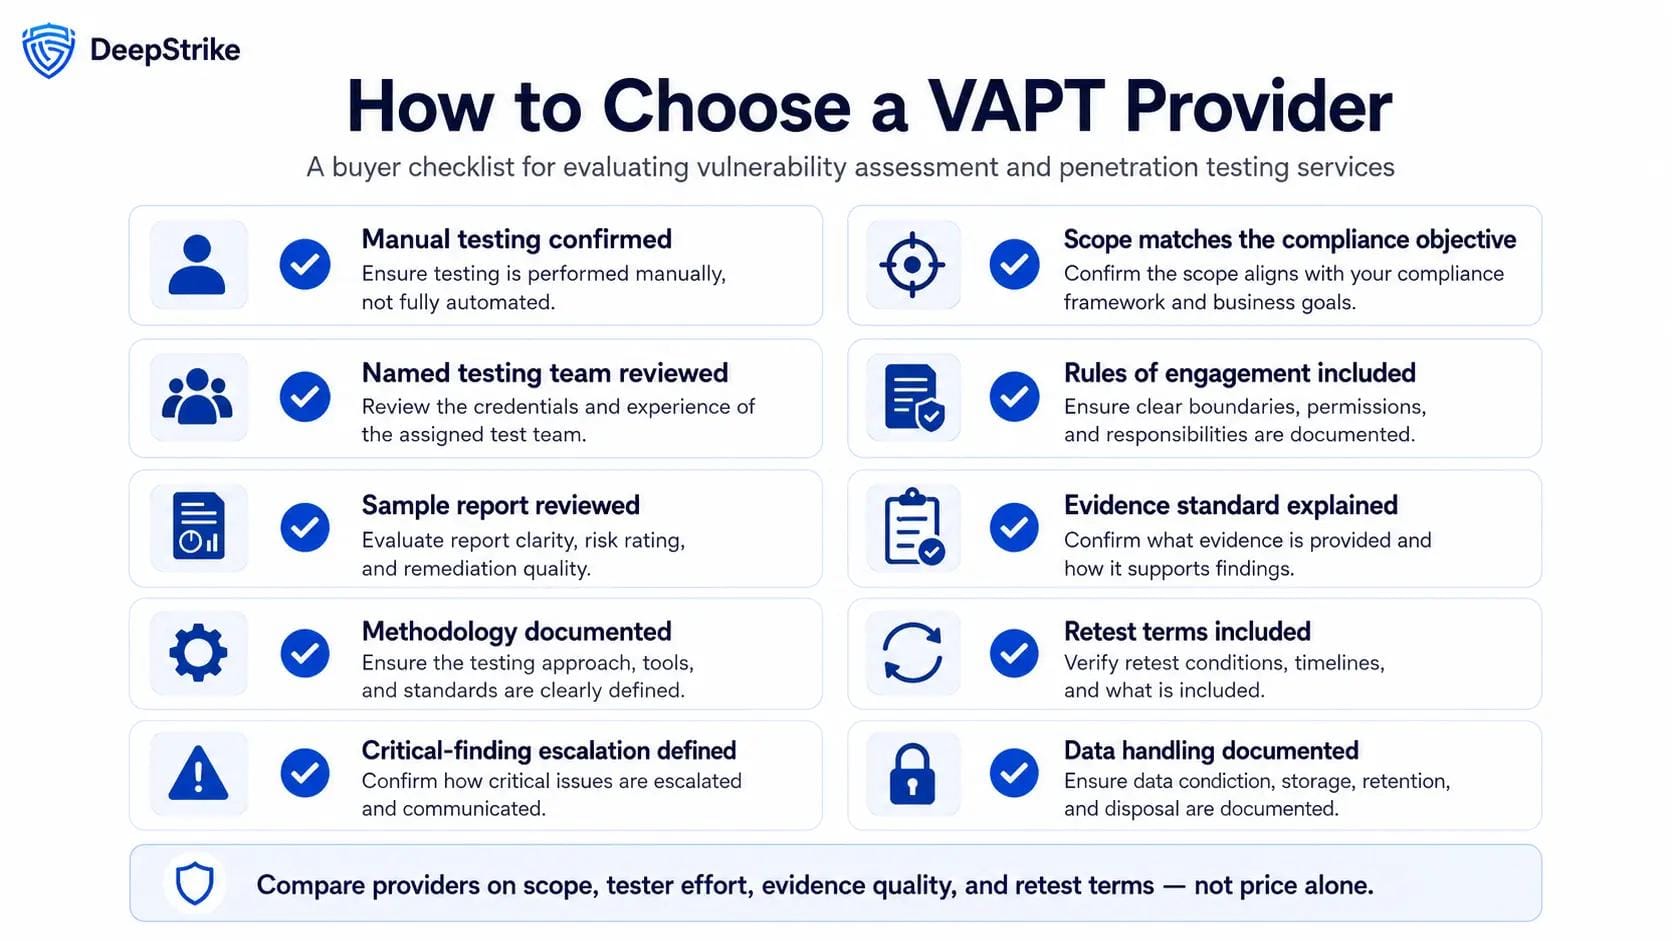
Figure 7. Compare providers on scope, method, evidence, safety, communication, retesting, and data handling.
Before signing, confirm that the proposal or statement of work defines:
Verify any claim about turnaround, price, certifications, tester location, experience, ratings, included retesting, platform features, or compliance support in the current proposal and contract.
It can be controlled, but it is never risk-free. Production testing requires written authorization, verified ownership, a narrow scope, approved windows, rate limits, monitoring, prohibited actions, stop conditions, emergency contacts, data-handling rules, and rollback readiness. Fragile or safety-critical actions may need staging, a safer validation method, or explicit exclusion.
VAPT identifies weaknesses and tests selected attack paths within a defined scope. Red teaming usually pursues broader adversary objectives and evaluates detection and response across people, process, and technology. A security audit evaluates evidence against defined criteria. The activities can inform one another, but their objectives, authorization, methods, and conclusions differ.
Fix obvious critical exposures when delay creates unacceptable risk, but do not assume every finding must be closed first. Leaving selected findings in scope can help test realistic chaining or compensating controls when that evidence supports the objective and the rules permit it. Record what was fixed, deferred, excluded, or left for validation so the result remains interpretable.
There is no defensible universal duration. The schedule depends on assets, roles, integrations, access, environment stability, safety windows, manual depth, evidence, stakeholder availability, remediation support, and retesting. A proposal should show assumptions and workstreams rather than using one generic duration for every scope.
Retain only the approved evidence needed for the stated purpose: authorization, scope, method, dates, access model, limitations, finding and retest status, remediation decisions, and relevant control observations. Define retention, access, encryption, secure delivery, and deletion before testing. A retained report can support review; it does not by itself prove compliance.
Asset and engineering owners should implement fixes, while the security or risk owner governs prioritization, exceptions, and residual-risk decisions. The test provider can clarify evidence and retest agreed changes but should not silently become the business risk acceptor. Each finding needs an accountable owner, dependencies, target state, acceptance criteria, and closure decision.
Automation can perform repeatable checks and some controlled validation. It does not, by itself, establish that a tester assessed your application's authorization rules, business workflows, or unusual trust relationships. Compare the actual tested scenarios and evidence with your objective. If the purchase requires a human-led penetration test, make that expectation explicit in the scope and report acceptance criteria.
A completion letter may confirm that a defined engagement occurred. Its value depends on the underlying scope, dates, methods, findings, and retest status. It does not replace the report or establish compliance with every applicable obligation. Ask the customer or auditor which evidence they require before purchasing a test for that purpose.
Use vulnerability assessment for broad, repeatable visibility and penetration testing for focused, human-led assurance. Use both when the decision needs coverage connected to defensible evidence, contextual prioritization, remediation ownership, and retesting. Keep authorization, untested conditions, and residual risk visible throughout the lifecycle.
To define an authorized scope around the objective and evidence your organization actually needs, request a technical VAPT proposal from DeepStrike.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements for Fortune 500 companies, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
The linked standards and official guidance support the technical and compliance distinctions in this article. Regulatory statements should be rechecked when planning an engagement. The scenario above is illustrative; COVER is DeepStrike's decision aid rather than an industry standard.
Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us