November 6, 2025
Updated: September 2, 2026
The anatomy of a pentest report, section by section, and how to tell a real one from an automated scan with a cover page.

Mohammed Khalil
Updated: September 2026. Reflects current reporting standards, CVSS v3.1 and the newer CVSS v4.0, and the frameworks auditors expect (OWASP WSTG, PTES, MITRE ATT&CK, NIST SP 800-115).
A good report is built in two layers: a business-readable executive summary for leadership and auditors, and a reproducible technical body for the engineers who fix things. It follows a predictable anatomy so every reader can find what they need.
| # | Section | Who it is for | What it must answer |
|---|---|---|---|
| 1 | Executive summary | Leadership, auditors | What is our risk, in business terms, and what do we do next? |
| 2 | Scope and rules of engagement | Everyone | What was tested, when, from where, and what was off-limits? |
| 3 | Methodology | Auditors, engineers | Which standard was followed (OWASP WSTG, PTES, NIST SP 800-115)? |
| 4 | Findings summary | Everyone | How many issues, at what severities, at a glance? |
| 5 | Detailed findings | Engineers | For each issue: what, where, proof, impact, and the fix |
| 6 | Risk rating methodology | Auditors, engineers | How was severity decided, and is it defensible? |
| 7 | Remediation roadmap | Engineering leads | What order do we fix things in, and by when? |
| 8 | Retest results | Auditors, leadership | Did the fixes actually hold? |
| 9 | Appendices | Engineers | Raw output, tool versions, payloads, full logs |
The line to hold onto: a report that cannot be reproduced by your engineers, and cannot be understood by your board, has failed at both jobs.
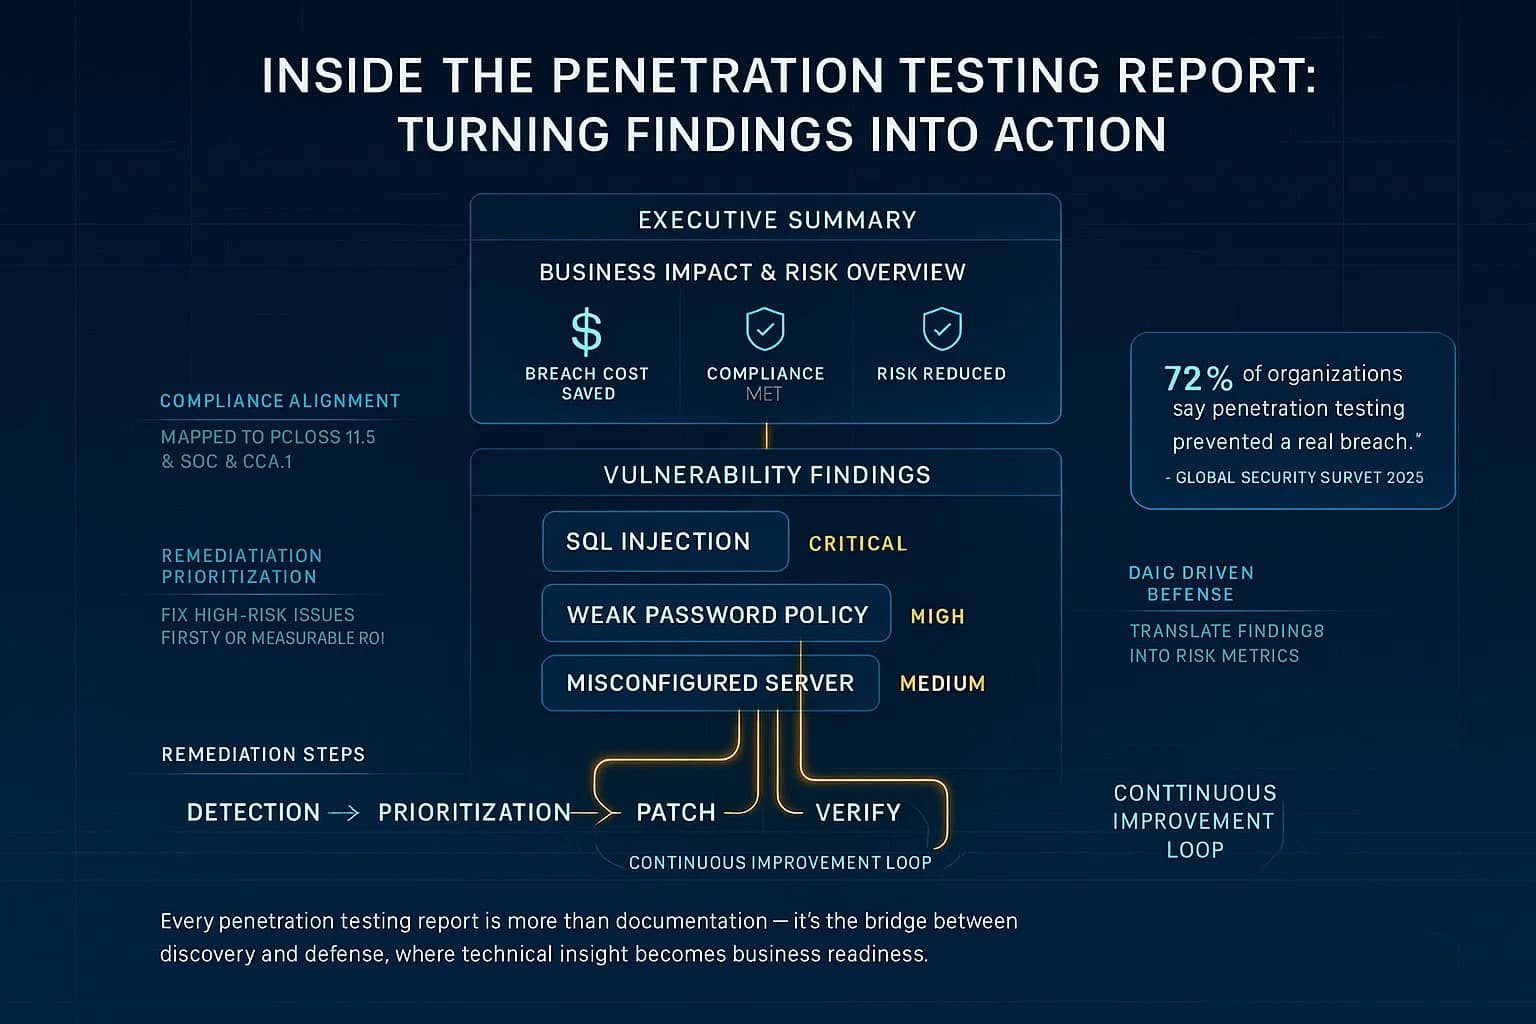
A penetration testing report is the final document produced after a pentest that lays out what was tested and what was found. It contains a detailed analysis of every vulnerability uncovered during the test describing each issue, its risk, and remediation steps. For example, one expert guide describes it as a document that contains a detailed analysis of the vulnerabilities uncovered during the security test. It records the vulnerabilities, the threat they pose, and possible remedial steps. In practice, a report always includes a high-level executive summary for non-technical stakeholders and in-depth technical findings for engineers, while the required reporting depth can also affect the overall penetration testing cost.
This report is the bridge between security testing and security action. Executives use it to understand business impact and make risk decisions, while developers and IT staff use it to fix issues. In short, it’s both the elevator pitch for management and the field manual for remediation. Curious about the penetration test itself? See our article What is Penetration Testing? for background.
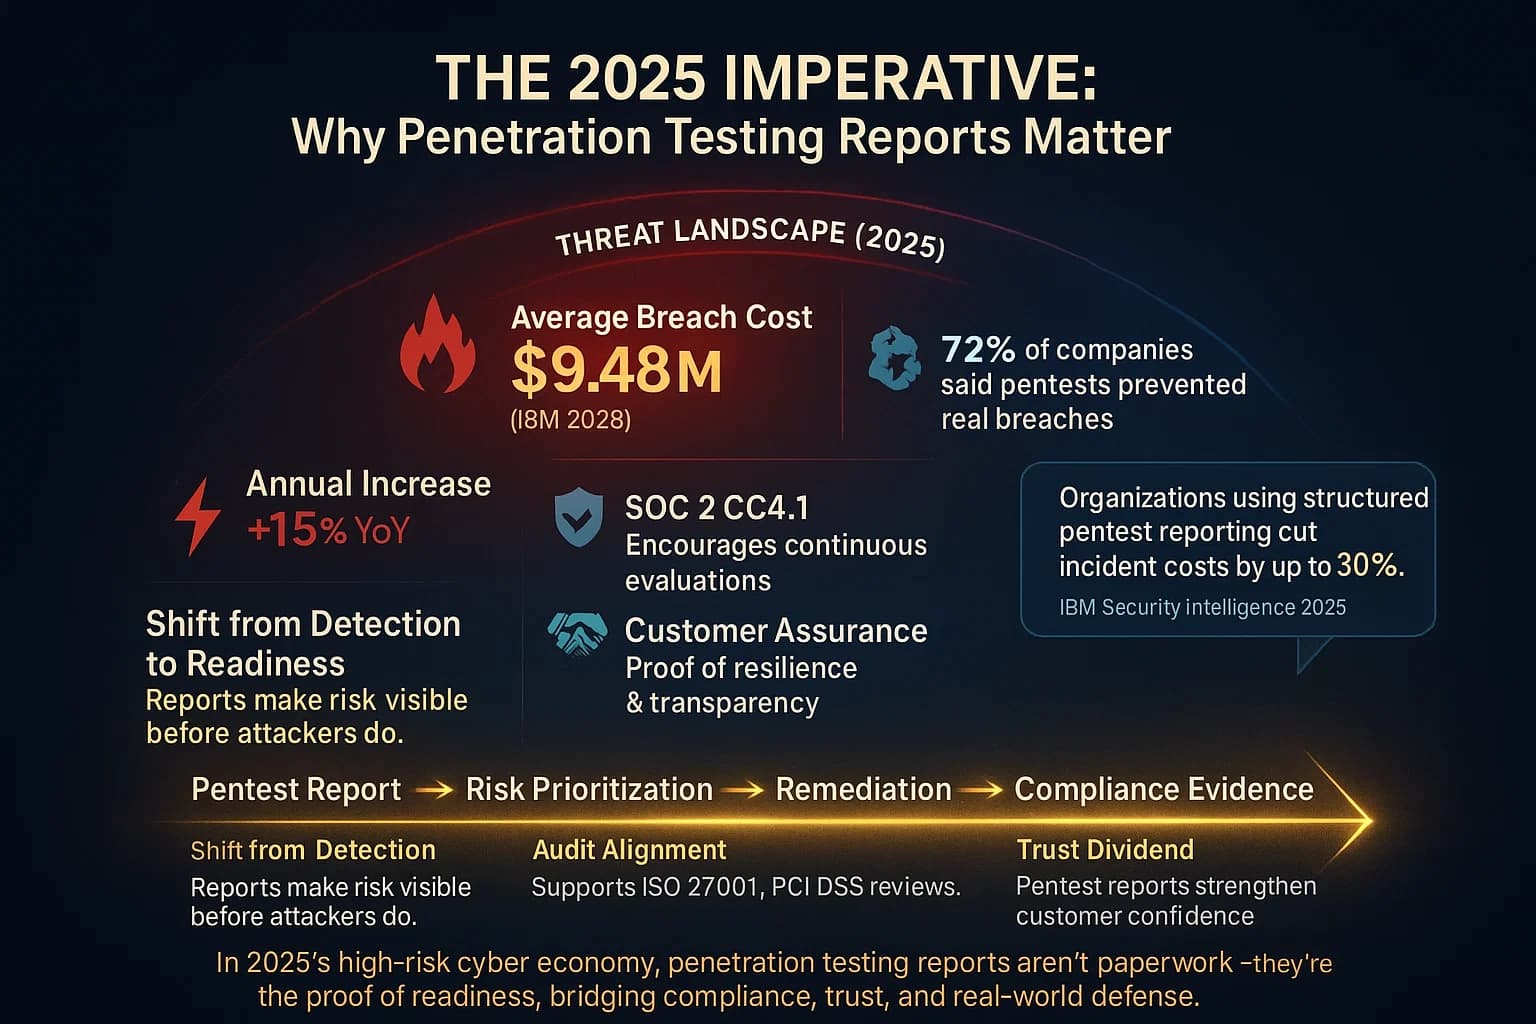
With cyber threats and regulations multiplying, a clear pentest report is more important than ever. Each year, attackers grow bolder and breaches more costly. IBM's Cost of a Data Breach Report 2026 put the global average at a record $4.99 million and the US average at $11.5 million, more than double the global figure. For US organizations, documenting risks through external penetration testing before an attacker finds them saves money and prevents damage. A good report helps teams fix high-risk issues quickly and proves to stakeholders that you are serious about security.
For UK organizations preparing for compliance reviews, compliance is another driving force. Many standards expect evidence of pen testing. PCI DSS Requirement 11.4 (renumbered from 11.3 in the retired v3.2.1) explicitly covers penetration testing: tests must cover both network and application layers, internally and externally, and the methodology and results must be documented and retained. Likewise, SOC 2's Trust Services Criteria CC4.1 encourage diverse security evaluations, specifically mentioning penetration tests as one option. Even though SOC 2 does not strictly mandate pentesting, auditors often expect one and review the report to confirm that critical vulnerabilities were addressed.
Moreover, customers and partners increasingly demand assurance. A polished pentest report or accompanying attestation can demonstrate robust defenses to clients, investors, or regulators. It can even be a marketing point: one firm notes that pentest reports help achieving compliance with industry standards and building trust with customers by showing you’re transparent about security.
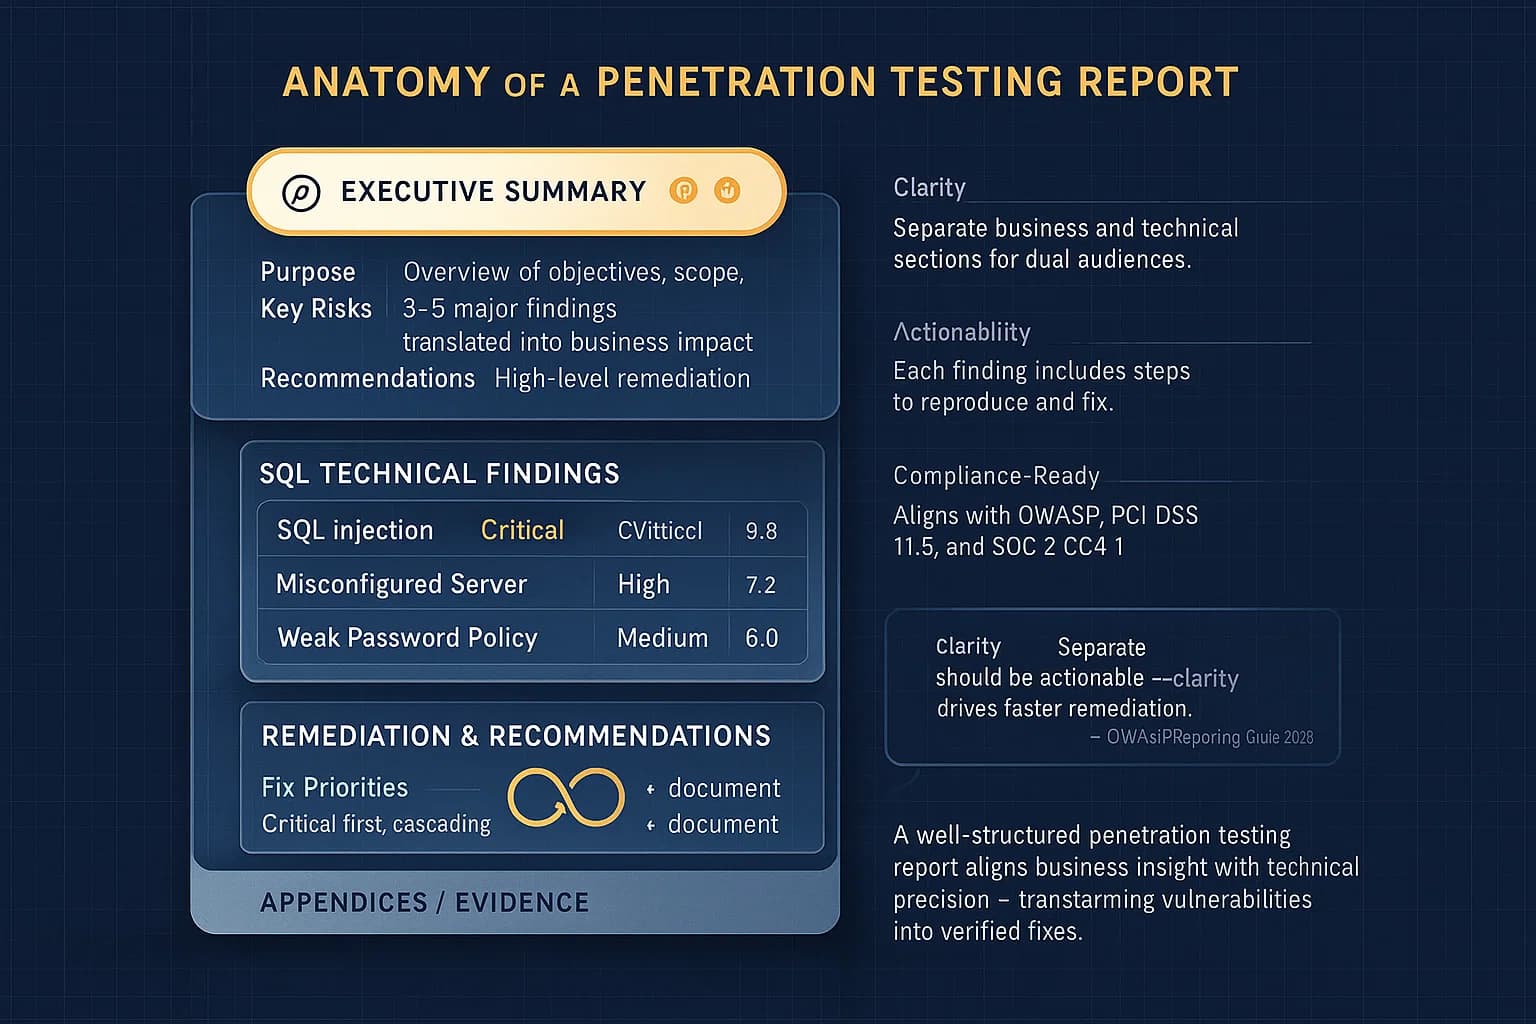
A professional penetration testing provider typically delivers a report with three main parts:
Additional sections often include the scope and methodology what systems were tested, in what mode e.g. black box or gray box and appendices, detailed logs, tool output, evidence. For compliance, also include an attestation letter or summary that certifies the test was done by authorized testers and summarizes the overall result. Many organizations provide an attestation statement alongside the report to share with partners or regulators.
Internal vs External Penetration Testing Quick Comparison
| Aspect | External Test | Internal Test |
|---|---|---|
| Threat Model | Simulates an outside attacker on public networks, websites, email, etc.. Targets firewalls, web apps, VPNs, etc. | Simulates an insider threat or compromised host inside the network. Targets internal servers, AD, Wi Fi, etc. |
| Access | Tester starts from the Internet with no credentials. | Tester has a foothold e.g., employee network access. |
| Common Findings | Open ports, misconfigured servers, outdated internet facing software. | Unpatched internal systems e.g. SMB/RDP exploits, weak credentials, misconfigured user permissions. |
| Goal | Breach perimeter defenses and access data from outside. | Move laterally within network to gain high privilege access. |
| Typical Use Cases | Compliance, assessing perimeter security posture. | Testing internal controls especially after breaches or in large LANs. |
External testing seeks to identify vulnerabilities that attackers may exploit on public networks, while Internal testing identifies vulnerabilities that could be exploited internally by malicious employees.
Another key comparison is between penetration testing vs vulnerability scanning. A vulnerability assessment or scan is typically an automated process that finds and lists potential issues. In contrast, penetration testing is an active attempt to exploit vulnerabilities. As PCI DSS notes, a vulnerability scan simply identifies and reports noted vulnerabilities, whereas a penetration test attempts to exploit the vulnerabilities to determine whether unauthorized access or other malicious activity is possible. In other words, scanning says X and Y are problems; pentesting says we exploited X to get admin, here’s proof, and here’s how to fix it.
Most of a report's value sits in the individual findings, and this is where weak reports give themselves away. Every finding should carry the same fields, in the same order, so an engineer can work through them without hunting.
| Field | What it must contain |
|---|---|
| ID and title | A stable reference (for example PT-2026-014) and a plain description of the issue |
| Severity | A rating with the reasoning behind it, not just a number |
| Affected asset | The exact host, URL, endpoint, or parameter, not "the web app" |
| Description | What the flaw is and why it exists in this specific system |
| Business impact | What an attacker gains: data, access, money, downtime |
| Steps to reproduce | Exact requests, payloads, and preconditions an engineer can follow |
| Evidence | Screenshots, request/response pairs, or output proving exploitation |
| Remediation | A specific fix for this code or configuration, not generic advice |
| References | CWE, OWASP, or vendor advisory the finding maps to |
The single most useful test of a report: pick a finding at random and hand it to an engineer who was not on the engagement. If they can reproduce the issue from the report alone, the reporting is sound. If they have to email the tester, it is not.
Most reports rate findings with the Common Vulnerability Scoring System. CVSS v3.1 remains the most widely used in reports and compliance workflows, while CVSS v4.0 is being adopted gradually and adds finer-grained metrics. Scores run 0.0 to 10.0 and map to None, Low, Medium, High, and Critical bands.
The limitation matters as much as the score. Base CVSS describes a vulnerability in the abstract, not the risk to your business. A CVSS 9.8 on an isolated internal test server can matter less than a CVSS 6.5 on an internet-facing system holding customer data. A good report says so: it uses CVSS for a common language, then adjusts priority using environmental context and exploitability, and explains that reasoning. If every finding in a report carries a bare CVSS number with no business context, the tester has outsourced the thinking to you. Prioritising by real exploitability rather than raw score is the same discipline covered in our vulnerability management guide.
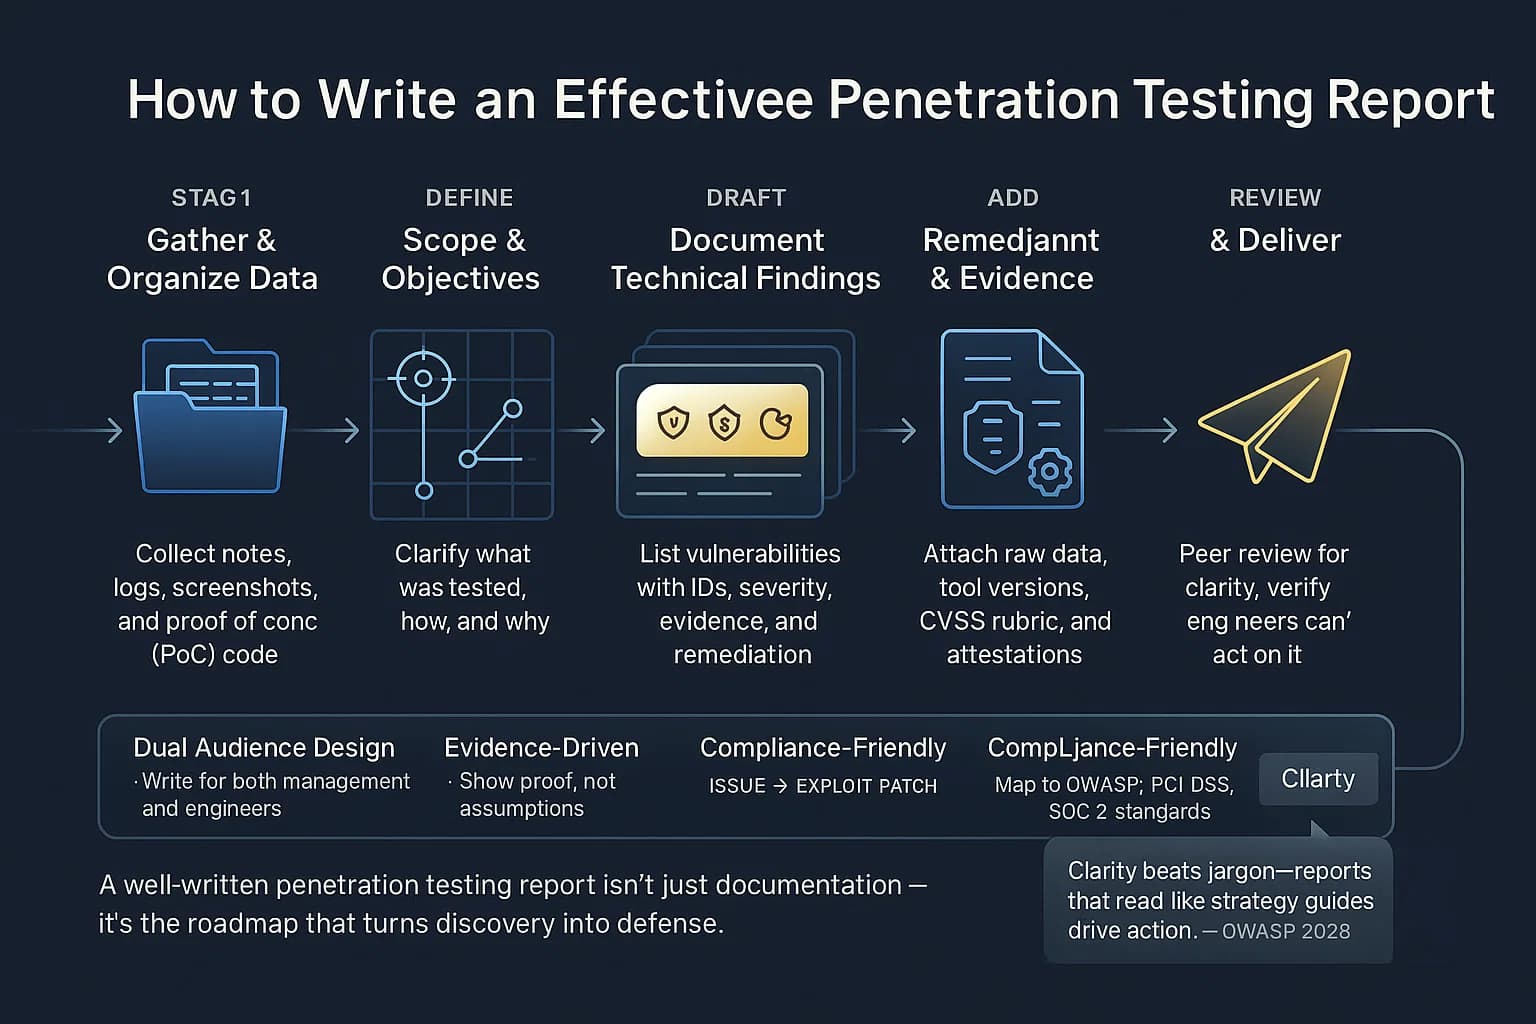
Putting the report together is as important as the test itself. Here are practical steps practitioners recommend:
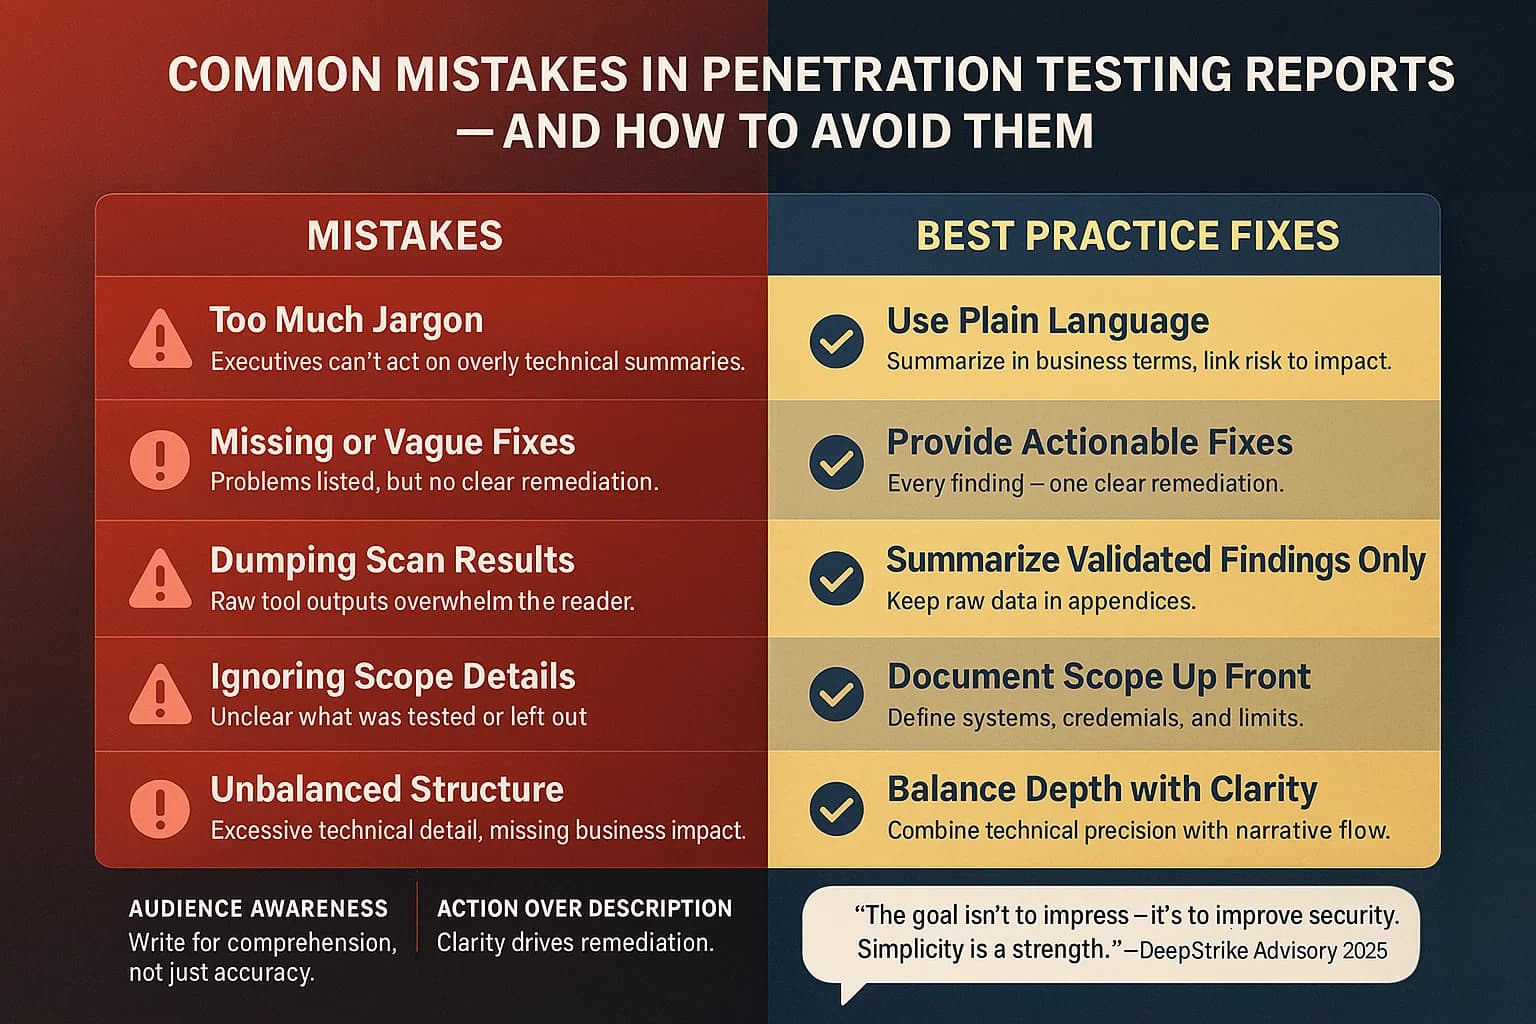
By following a structured format and keeping the audience in mind, you’ll maximize the report’s value. Remember: the goal isn’t just to write a document, but to guide real security improvements.
Most people encounter a pentest report as the recipient, not the author. A practical order of operations:
| Reader | What they need | Where they look |
|---|---|---|
| Board and executives | Risk in business terms and a decision to make | Executive summary only |
| Security lead | Prioritisation and the remediation roadmap | Summary, findings summary, roadmap |
| Engineers and developers | Exact reproduction steps and a specific fix | Detailed findings and appendices |
| Auditors and customers | Scope, methodology, and proof of retest | Scope, methodology, retest results, attestation |
This is why the two-layer structure exists. A report written only for engineers never gets budget approved; a report written only for executives never gets anything fixed.
Penetration testing reports are more than just paperwork they are the blueprint for fixing security gaps. By documenting findings clearly and recommending concrete fixes, a report turns a pen test from a one time audit into continuous security improvement. In today’s landscape with rampant cyber threats and strict audits, a well written report is essential for any organization serious about resilience.
Ready to strengthen your defenses? Today's threats demand more than awareness, they require readiness. If you want to validate your security posture, uncover hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of experienced practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services to see how we can uncover vulnerabilities before attackers do. Drop us a line our experts are always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements for Fortune 500 companies, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
A penetration testing report is the end result of a pentest. It’s a written document that details all vulnerabilities found, how they can be exploited, and how to fix them. Think of it as a roadmap for improving security: it includes a high level executive summary plus detailed technical sections covering each finding.
Typically, a professional report has an Executive Summary goals, overall risk, business impact, Technical Findings each vulnerability with severity, description, evidence, and remediation, and Recommendations prioritized fixes and next steps. Appendices often list test scope/methodology, tool output, and references. OWASP’s guidelines and industry templates recommend this structure to clearly address both management and technical audiences.
Multiple roles: Executives and managers read the summary to understand business risk and compliance status. Security and IT teams use the technical details to implement fixes. Developers examine specific code or config issues. It can even be shared with auditors or clients as proof of diligence. In fact, a pentest report can support certifications like SOC 2 or ISO 27001, demonstrating you’ve tested and fixed vulnerabilities.
Industry best practices suggest at least annually or after any major change. For example, PCI DSS requires yearly tests or after significant upgrades. In dynamic environments like continuous deployment, more frequent or continuous testing via a PTaaS model is recommended. Regular reports keep security posture up to date. At a minimum, updating your report annually and after each re-test ensures new vulnerabilities haven’t crept in.
It depends on the standard. Some explicitly require documented pentests, such as PCI DSS Requirement 11.4 and HIPAA guidance, while others like SOC 2 treat them as a strong recommendation rather than a hard requirement. SOC 2's CC4.1 covers ongoing evaluations including penetration testing, so running one helps demonstrate your controls. In general, even where it is not strictly required, a good report greatly simplifies an audit and provides valuable evidence of security effort.
A vulnerability scan assessment automatically finds known issues and lists them. A pentest goes further by actively exploiting vulnerabilities to show their real impact. In simple terms: a scan says these issues exist, whereas penetration testing proves how they can be used maliciously. Thus, pentest reports usually have more depth, context, and prioritization than simple scan reports.
Most reports use CVSS v3.1, which remains the most widely used version in reporting and compliance workflows, while CVSS v4.0 is being adopted gradually and adds finer-grained metrics. Scores run from 0.0 to 10.0 across None, Low, Medium, High, and Critical bands. A good report treats CVSS as a common language rather than the final answer, and adjusts priority using your environment and real exploitability.
A good report is reproducible and specific: every finding names the exact affected asset, includes the requests and evidence needed to reproduce it, explains business impact, and gives a fix for your code or configuration. A bad one reads like a tool export: generic descriptions, bare CVSS numbers with no context, boilerplate remediation advice, no chained attack paths, and no retest. The quickest test is to hand one finding to an engineer who was not on the engagement and see whether they can reproduce it from the report alone.
There is no standard length, and length is a poor quality signal on its own. What matters is that the executive summary stays short enough for leadership to read in full, each finding carries complete reproduction detail, and bulk output such as full scan results and logs goes into appendices rather than padding the body. A tight twenty-page report with reproducible findings beats an eighty-page one built from scanner output.
Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us