August 31, 2025
Updated: November 5, 2026
Understand what a vulnerability assessment costs in 2026, what drives pricing, and how to budget using verified tool prices and rate data.

Mohammed Khalil
Quick answer: In 2026, vulnerability assessment cost ranges from $0 for free scanners to a few thousand dollars a year for a commercial scanning subscription, and roughly $1,000 to $11,000 for a scoped, expert-led assessment of a small or mid-sized environment. Expert-led work is priced by tester hours, and GSA CALC+ rate data puts the middle half of penetration tester ceiling rates at about $126 to $196 an hour. Scope drives the total more than anything else: the number of IPs, hosts, applications, API endpoints and cloud accounts, plus any compliance reporting.
So, how much does a vulnerability assessment cost? The honest answer is a frustratingly wide range: from free and low-cost automated scanners to manual engagements that are quoted per scope and priced by expert time. But the number on the quote isn't the real story. The real story is about risk, and in 2026, the stakes have never been higher.
The threat landscape is relentless. The Verizon 2026 Data Breach Investigations Report (DBIR) found that exploitation of vulnerabilities is now the most common initial access vector for breaches, rising to 31%, while credential abuse, the previous leader, fell to 13%. Attackers aren't just knocking on the door; they're actively looking for unlocked windows.
This is why understanding vulnerability assessment pricing is so critical. It’s not just a line item in your IT budget; it's a direct investment in your organization's resilience. The cost is fundamentally tied to the level of human expertise and the thoroughness of the methodology you're paying for. When you compare this investment to the potential fallout of a breach, which the IBM 2026 Cost of a Data Breach Report puts at a record $4.99 million globally and $11.5 million for U.S. companies, the value proposition becomes crystal clear.
Pricing at a Glance: Verified Reference Points (checked November 2026)
This guide breaks down every factor that goes into a quote, so you can make an informed decision that protects your business without breaking the bank.
Before we talk numbers, we need to get the terminology right. This is where many businesses make their first, most critical mistake.
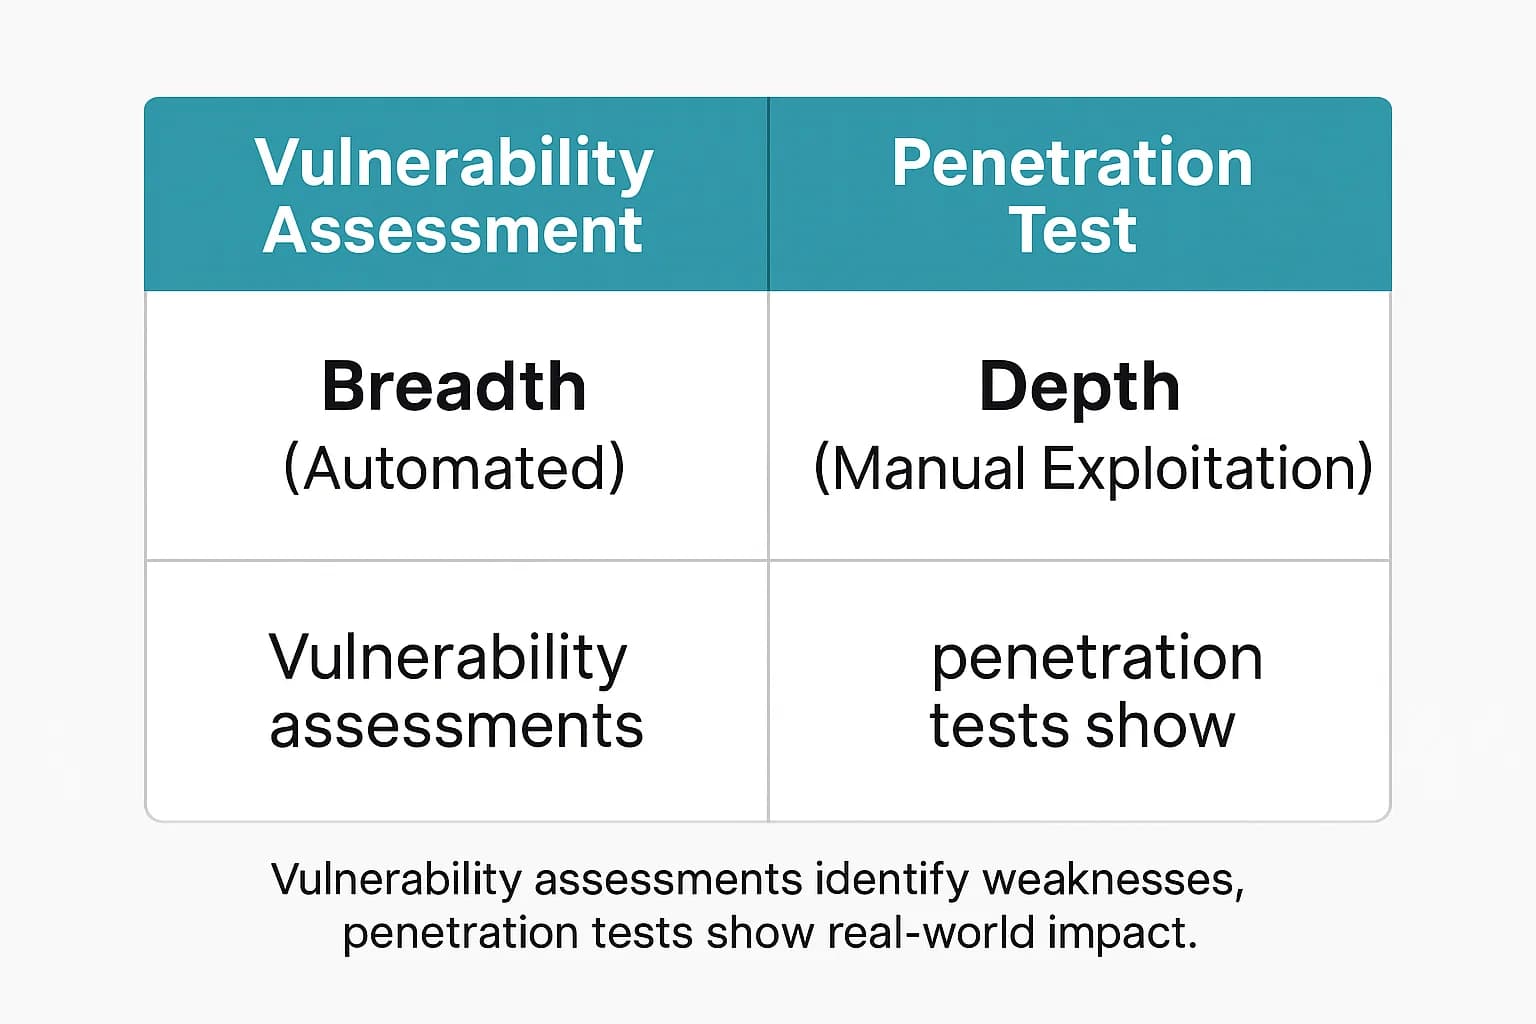
A Vulnerability Assessment (VA) is a systematic process of identifying, quantifying, and prioritizing security weaknesses in a system. Think of it as a comprehensive inventory of potential problems. VAs are often automated and rely on scanning tools like Tenable Nessus, Qualys, or OpenVAS to check your systems against a massive database of known vulnerabilities (CVEs). The primary goal is breadth to find as many known issues as possible across a wide range of assets. It answers the question:
“What are our weaknesses?”
A Penetration Test (Pentest), on the other hand, simulates a real-world attack. A pentester doesn't just find vulnerabilities; they actively try to exploit them to gauge the actual business impact. This process is heavily manual and uncovers issues automated scanners can't see. A pentest answers the question: “What can an attacker actually do with our weaknesses?” For a deeper dive, see our guide on the vulnerability assessment vs penetration testing debate.
Buyer Beware: "Penetration Tests" Priced Like a Scanner License Be extremely wary of any service advertised as a "penetration test" that costs about the same as a year of a commercial scanner license (Nessus Professional lists at $4,790 per year). A true pentest involves days of a certified expert's time and creativity. At the CALC+ median of about $156 per hour, that price buys roughly 30 hours of tester time, which can cover only a small, tightly scoped test. Ask how many tester hours are included and what manual testing they cover; if the answer is mostly automated scanning, you are buying a scan, not a pentest.
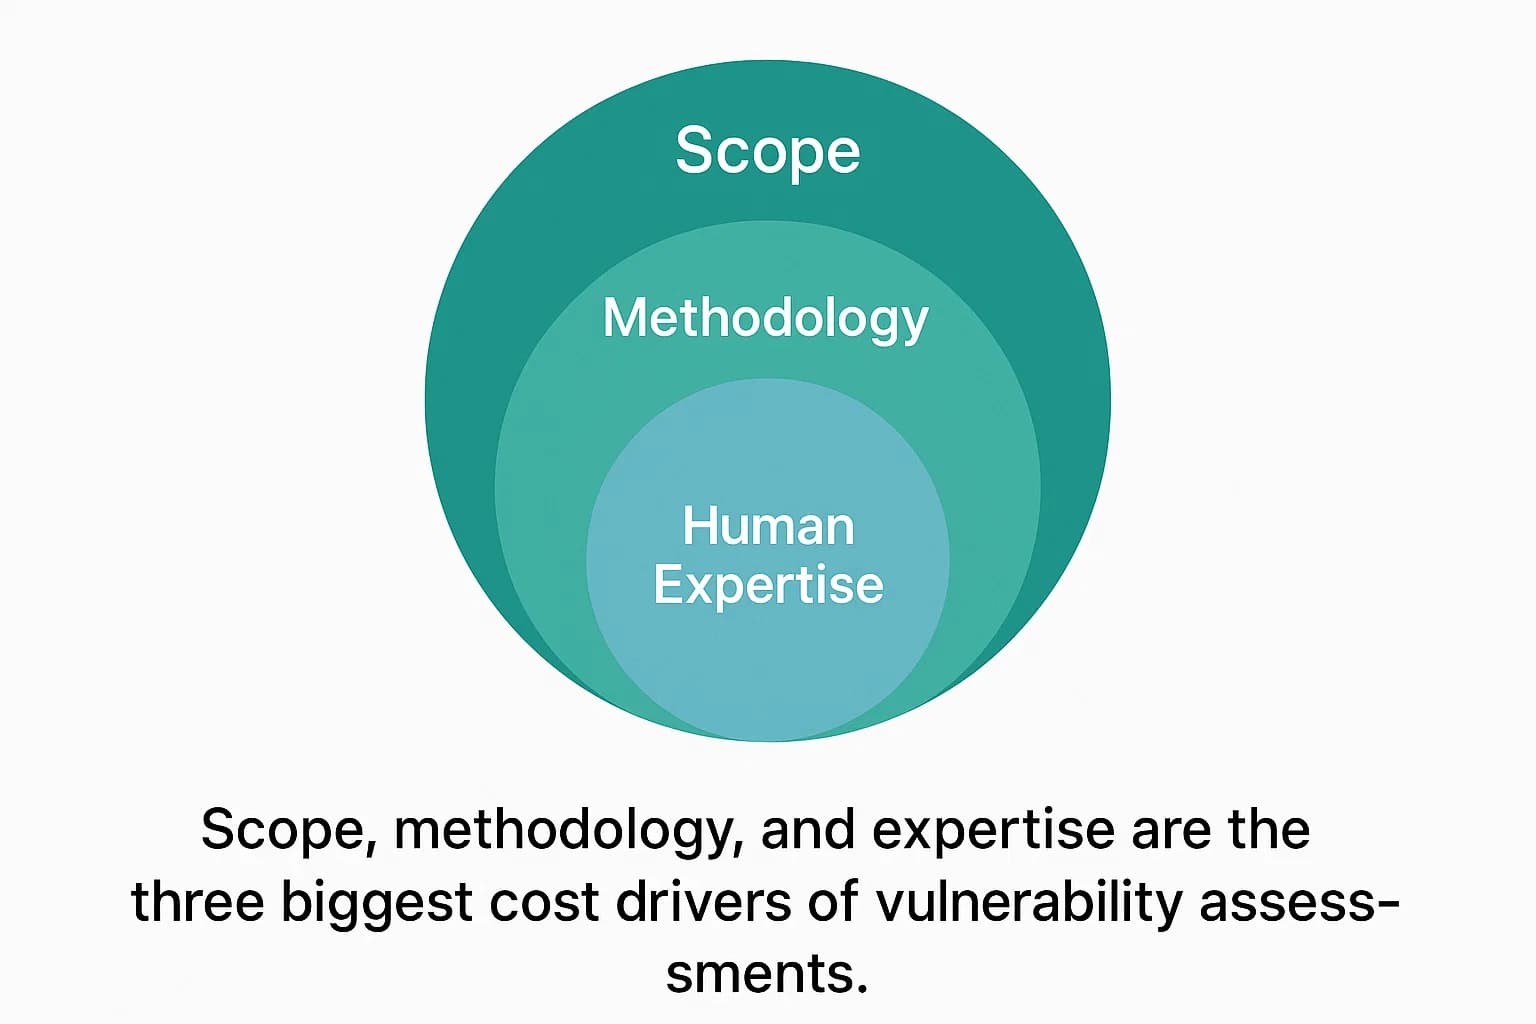
The cost of a vulnerability assessment is primarily driven by the scope and complexity of the assets being tested, the testing methodology (black, white, or grey box), and the experience of the security professionals involved.
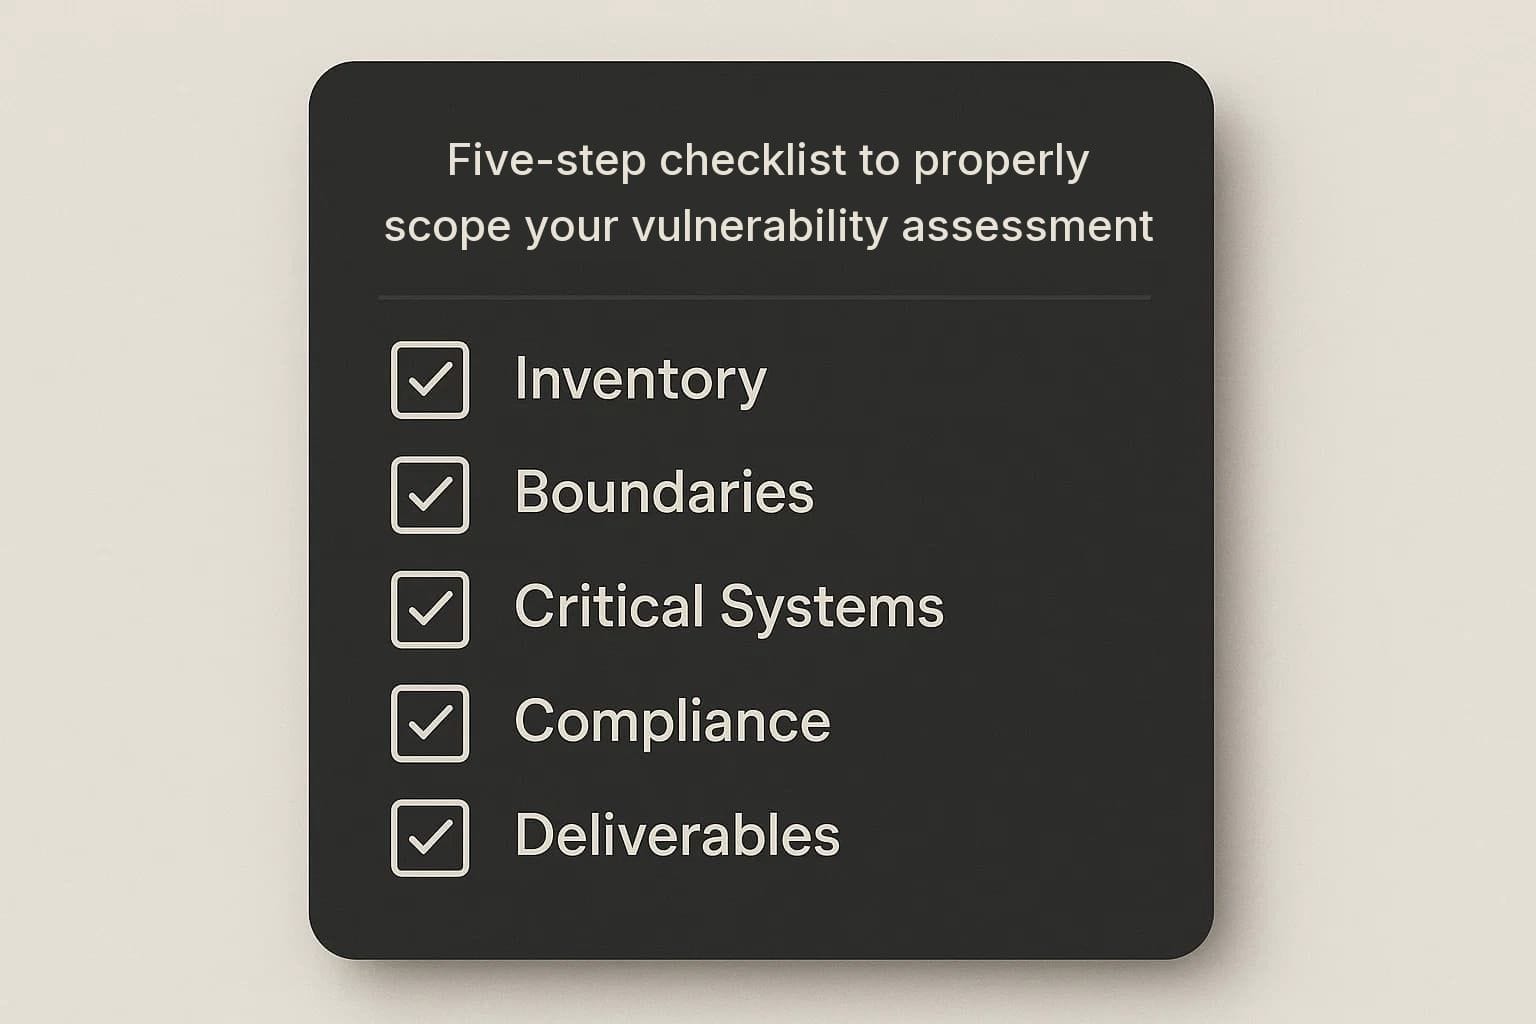
An ambiguous scope is a common cause of failed engagements. Use this checklist to ensure you get an accurate quote for the work you actually need.
Most budgets combine two cost types: a recurring subscription for automated scanning and a scoped, time-based fee for manual testing of networks, web apps and cloud. Here is how each type is typically priced.
To turn rate data into a rough budget, multiply the expert hours your scope needs by a market rate. As an illustration only (not a quote): an engagement needing 40 to 80 hours of tester time at the CALC+ median of about $156 per hour comes to roughly $6,200 to $12,500 before reporting and retesting. Ask every vendor for a scoped quote and compare the hours and deliverables, not just the total. For a full overview of options, explore our vapt services provider.
The table turns tester hours into budget ranges for the requests buyers ask about most. The hours are our planning assumptions for a scan-plus-manual-validation assessment, not quotes, multiplied by the middle half of GSA CALC+ penetration tester ceiling rates (about $126 to $196 an hour). Commercial rates vary by region, firm and urgency, so use it to sanity-check quotes, not to replace them.
| Scope | Typical work included | Assumed tester hours | Estimated cost range |
|---|---|---|---|
| External vulnerability assessment, up to 10 public IPs | Service discovery, vulnerability scan, manual validation of findings, short report | 8 to 16 | About $1,000 to $3,100 |
| Internal vulnerability assessment, office network of about 50 to 250 hosts (servers, switches, firewalls) | Authenticated scans, firewall and switch configuration review, false-positive triage, report | 24 to 40 | About $3,000 to $7,800 |
| Web application plus API, one app with a few user roles and under 50 endpoints | Authenticated web app scan, manual checks of access control and business logic, API endpoint review | 24 to 56 | About $3,000 to $11,000 |
| Cloud configuration review, one AWS, Azure or Google Cloud account | Identity and access policy review, storage and network exposure, benchmark comparison | 16 to 40 | About $2,000 to $7,800 |
| Retest or rescan of fixed findings | Rescan and manual confirmation of fixed high and critical findings, updated report | 4 to 8 | About $500 to $1,600 |
Compliance pushes quotes above these ranges: auditors expect evidence for each requirement, and PCI DSS external scans must be run by an Approved Scanning Vendor (ASV), usually a separate line item. Larger estates add hours in proportion to hosts, roles and endpoints.
If you need a full penetration test rather than an assessment, our penetration testing cost guide covers that budget. For combined VAPT engagements, see what determines VAPT cost and duration, and for API-heavy scopes, our API penetration testing services guide explains how endpoints and roles drive the quote.
If you are budgeting for continuous scanning rather than a one-off assessment, you are buying software. It is priced per asset, per web domain (FQDN), per user or per license. These are the published list prices we checked on November 5, 2026:
| Product | Published price | Pricing basis | Notes |
|---|---|---|---|
| Tenable One Vulnerability Management | $3,700 per year | 100 assets; online purchase up to 250 assets | Larger estates are quoted by Tenable or a partner |
| Tenable Nessus Professional | $4,790 per year | Annual license | Standalone scanner; Tenable lists unlimited vulnerability scanning |
| Tenable Nessus Expert | $6,790 per year | Annual license | Adds web app scanning and external attack surface discovery |
| Tenable One Web App Scanning | $6,790 per year | 5 FQDNs | Dynamic scanning of web apps and APIs |
| Microsoft Defender Vulnerability Management add-on | $2.00 per user per month | Per user | Requires Microsoft Defender for Endpoint Plan 2 or a suite that includes it |
| Qualys VMDR; Rapid7 InsightVM and Exposure Command | Not published | Quote | Ask for pricing by asset count and modules |
| Qualys Community Edition; OpenVAS (Greenbone) | Free | Not applicable | Limited scale and support |
| CISA vulnerability scanning | Free | Eligible organizations only | Critical infrastructure and state, local, tribal and territorial governments, among others |
A worked example for a 500-person company: Microsoft's Defender Vulnerability Management add-on at $2 per user per month comes to $12,000 a year for 500 users, on top of the Defender for Endpoint Plan 2 licenses it requires. Per-asset scanners scale with servers, workstations and cloud instances instead, so count assets, not employees, before comparing. Someone still has to triage findings and drive fixes, which our vulnerability management guide covers step by step.
The assessment invoice is rarely the whole cost. Budget for these items too:
A low quote is not automatically a bad one; an external assessment of a few IPs can legitimately cost a few thousand dollars or less. What matters is whether the price matches the work, so ask:
If the answers describe mostly automated output, you are buying a scan, which is fine for routine coverage if it is priced and labeled as one. Our guide to automated penetration testing explains what automation can and cannot find.
If you need an assessment to satisfy a compliance requirement, expect the cost to be higher. Regulations transform a technical exercise into a formal, audit-readiness engagement where the reporting and documentation standards are just as important as the testing itself. For a broader comparison of assessment types, scope, and cost, see our guide to security assessment services.
It's easy to see a penetration test as an expense. It's more accurate to see it as an investment with a massive potential return. The math is simple: a scoped assessment fee versus a $4.99 million average breach cost globally, or $11.5 million in the U.S., per IBM's 2026 report.
As a simple illustration (hypothetical numbers, not a study finding): if a $20,000 assessment reduced the expected loss from a $1 million breach scenario by 40%, the expected loss reduction would be $400,000, or 20 times the cost of the assessment.
Beyond preventing a catastrophic breach, a strong testing program delivers other tangible benefits. It's often a prerequisite for obtaining favorable terms for cyber insurance, directly impacting another business cost center. Furthermore, the Verizon 2025 DBIR found that the median time to mass exploitation for its edge-device vulnerability subset was zero days, and the 2026 DBIR found only 26% of CISA KEV vulnerabilities were fully remediated in 2025, with a median of 43 days to full resolution. A proactive assessment program helps you find and fix flaws before they become a five-alarm fire drill. This is why continuous penetration testing matters.
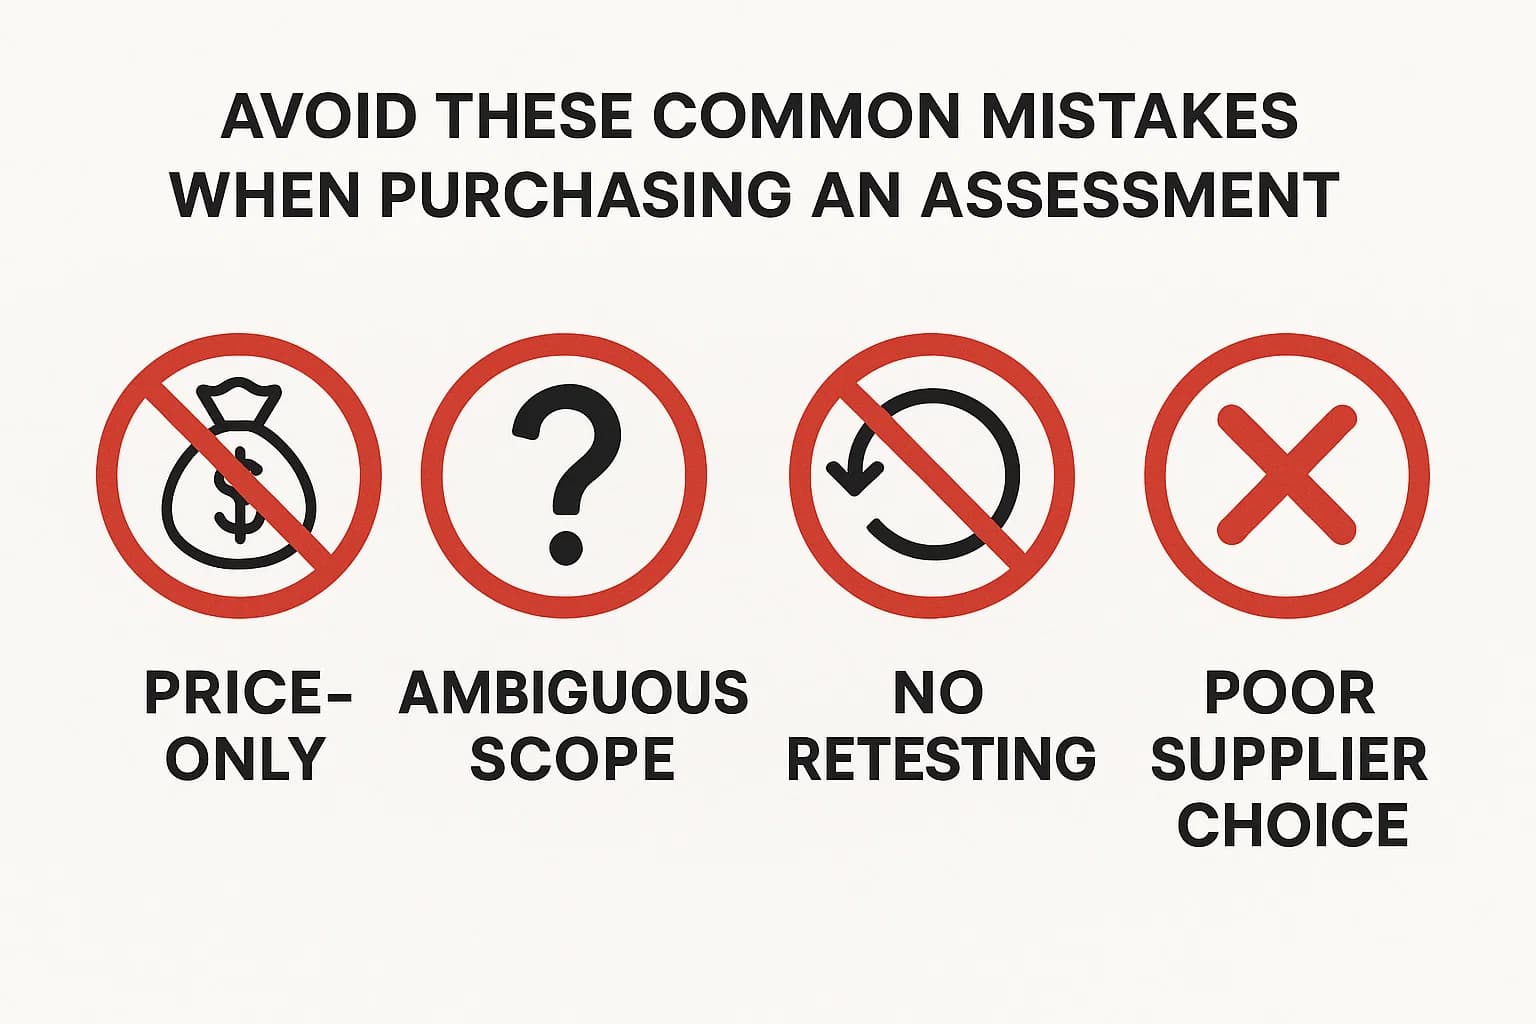
Getting the most value from your security budget means avoiding common procurement pitfalls.
1. How much does a vulnerability assessment cost for SMBs?
Free and low-cost options exist: Qualys Community Edition is free, OpenVAS is open source, and CISA offers free scanning to eligible organizations. Commercial scanner subscriptions start in the low thousands per year (as of November 2026, Tenable lists Tenable One Vulnerability Management at $3,700 per year for 100 assets and Nessus Professional at $4,790 per year). Manual assessments and penetration tests are quoted per scope because they are priced by expert time; GSA ceiling rates for penetration testers have a median of about $156 per hour.
2. What are the main factors that drive the price of an assessment?
The primary cost drivers are the scope (number of assets like IPs or web pages), the complexity of the systems, the testing methodology (black, white, or grey box), and any specific compliance requirements like PCI DSS or HIPAA that demand more rigorous documentation.
3. How long does a vulnerability assessment take in 2026?
An automated vulnerability scan can be completed in hours. However, a comprehensive manual assessment or penetration test is a more involved process, often taking one to several weeks, depending on the scope and complexity of the environment.
4. Are remediation and retesting included in the cost?
It varies by vendor. Many quotes for manual penetration tests include a retest of critical findings within a set window after the report. However, extensive remediation support or multiple retests often come at an additional cost, so it's crucial to clarify this upfront.
5. How often should we perform a vulnerability assessment?
Run automated scanning continuously or on a fixed schedule, and test critical systems manually at least annually. PCI DSS v4.0.1 requires vulnerability scans at least every three months and internal and external penetration tests at least every 12 months and after significant changes, and FedRAMP requires a 3PAO penetration test at least every 12 months. High-risk environments often test more frequently.
6. Is a rescan after fixes standard, and what does it cost?
Many vendors include one retest of fixed findings within a set window after the report, but it is not universal, so confirm it before you sign. If it is billed separately, retesting a handful of fixed high and critical findings is usually 4 to 8 tester hours, about $500 to $1,600 at the middle half of GSA CALC+ penetration tester rates.
7. What is a reasonable quote for an external vulnerability assessment of 10 public IPs?
For scanning plus manual validation and a short report, 8 to 16 tester hours is a reasonable planning range, which comes to about $1,000 to $3,100 at the middle half of GSA CALC+ penetration tester rates. Quotes well above that should include more manual testing, such as a full external penetration test. Quotes well below it are usually automated scans.
8. How much does vulnerability management software cost?
Published list prices start at $3,700 a year for Tenable One Vulnerability Management (100 assets) and $4,790 a year for Nessus Professional, and Microsoft lists its Defender Vulnerability Management add-on at $2 per user per month. Qualys and Rapid7 quote their platforms by asset count. Free options include Qualys Community Edition, OpenVAS and, for eligible organizations, CISA vulnerability scanning.
For more answers, check out our comprehensive Pen Testing FAQs.
Understanding vulnerability assessment pricing isn't about finding the cheapest option, it's about making the smartest investment in your security. The cost is a direct function of scope, complexity, and the level of human expertise you bring in. While a low-cost automated scan can provide a baseline, a manual, expert-led penetration test is what uncovers the critical risks that lead to devastating breaches. By viewing this as a high-ROI investment against the catastrophic cost of a data breach, you can build a defensible business case for a security program that truly protects your organization.
Ready to Strengthen Your Defenses?
The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Every engagement is quoted per scope, so drop us a line for a scoped quote based on your environment.
About the Author
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
