June 29, 2025
Updated: November 5, 2026
In 2026, cyber insurance claims data reveal a harsh reality: BEC and FTF drive 58% of claims, ransomware losses average $269K, and breach costs hit a record $4.99M. This guide breaks down the stats behind denials, coverage gaps, and how to secure your policy payout.

Mohammed Khalil
The cyber insurance landscape in 2026 presents a dangerous paradox for business leaders. After years of relentless price hikes, cyber insurance rates have been falling, and a fiercely competitive market has created what looks like a golden opportunity for buyers. But here’s the catch: while the price of coverage is going down, the financial impact of a successful cyberattack has never been higher.
This is the great disconnect of 2026. The global average cost of a data breach has climbed to a record $4.99 million, according to IBM's 2026 Cost of a Data Breach Report. This creates a "buyer's trap," where a lower premium can lull an organization into a false sense of security. The reality is that insurers are competing on price by demanding higher standards of security from their clients. The burden of proof and the consequences of failure are shifting squarely onto the policyholder.
This article is an essential guide for leaders navigating this complex new reality. We’ll dive deep into the latest cyber insurance claims statistics, breaking down what’s driving losses, who is being targeted, and why claims get denied. By understanding the hard data, you can make smarter decisions to justify security investments, choose the right coverage, and ensure that when you need it most, your policy actually pays. Understanding your risk profile starts with a clear view of your vulnerabilities, and the latest cybersecurity vulnerability statistics paint a sobering picture.
On the surface, the cyber insurance market looks favorable for buyers. Reinsurer Munich Re estimates the global market at nearly $15 billion in premiums in 2025, and expects it to reach around $28 billion by 2030. In the U.S., the National Association of Insurance Commissioners (NAIC) recorded the first-ever decline in cyber direct written premium in 2024, followed by a modest rebound: domestic premium reached $7.46 billion in 2025 ($9.46 billion including alien surplus lines insurers, up 3.5%), while reported claims rose 20% to 56,323.
So, what’s going on? This isn't a sign of reduced risk. It’s a market correction. During the recent hard market, insurers raised rates dramatically and became highly profitable. That profitability attracted intense competition, forcing carriers to lower prices to win business. Margins are now tightening: according to the NAIC's 2026 Report on the Cybersecurity Insurance Market, the U.S. cyber loss ratio rose to 53% in 2025 from 48.7% in 2024, while claims and policy counts kept climbing.
However, this price war comes with a critical string attached: insurers are tightening their underwriting requirements and scrutinizing claims more than ever before. They can only afford to offer lower premiums if they are confident their insureds are low risk. They achieve this by being highly selective and enforcing strict security controls as a prerequisite for coverage. This means the “deal” of a lower premium is contingent on the business already having a mature, defensible security program supported by professional penetration testing. For organizations that are prepared, it's a buyer's market. For those with weak security hygiene, it's a minefield.
To navigate the market, you have to understand what’s actually driving claims. The data reveals a clear split between the most frequent types of claims and the most financially severe.
For a claims-wide baseline, Verizon's inaugural 2026 Breach Impact Study, built with CyberAcuView on 69,683 U.S. cyber insurance claims (38,181 with paid losses) from January 2019 to October 2025, found a median financial impact of about $83,000 per paid claim: roughly $38,000 for small and medium-sized businesses and about $283,000 for large enterprises.
By a huge margin, the most common incidents are simple, low tech, and devastatingly effective. According to Coalition's 2026 Cyber Claims Report (covering 2025 claims), Business Email Compromise (BEC) and Funds Transfer Fraud (FTF) together accounted for 58% of all cyber insurance claims.
A standalone BEC incident, where an attacker gains access to an email account to spy or steal data, has a relatively low average loss of $27,000, down 28% year over year even as BEC frequency rose 15%. The real damage occurs when BEC is used as a launchpad for FTF: 52% of FTF claims originated as a BEC. FTF was the second most common claim type at 27% of claims, with an average loss of $141,000, and Coalition found that 71% of FTF claims were a direct result of social engineering.
There is a silver lining here, but it requires swift action. Insurers and law enforcement have become adept at clawing back stolen funds if notified immediately. In 2025, Coalition recovered $21.8 million in stolen funds for policyholders, an average of $202,000 per recovery. This proves that the first call you make after discovering a fraudulent transfer should be to your insurer’s claims hotline. These attacks are fundamentally a form of social engineering, a threat illuminated by the latest phishing statistics.
While BEC is the most frequent claim, ransomware remains the undisputed king of cost. Coalition's 2026 report found ransomware was the costliest claim type in 2025, with an average loss of $269,000. Dual extortion (encryption plus data theft) made up 70% of ransomware events and roughly doubled the cost of an incident.
The dynamics of ransomware are changing rapidly. Here’s what the data shows:
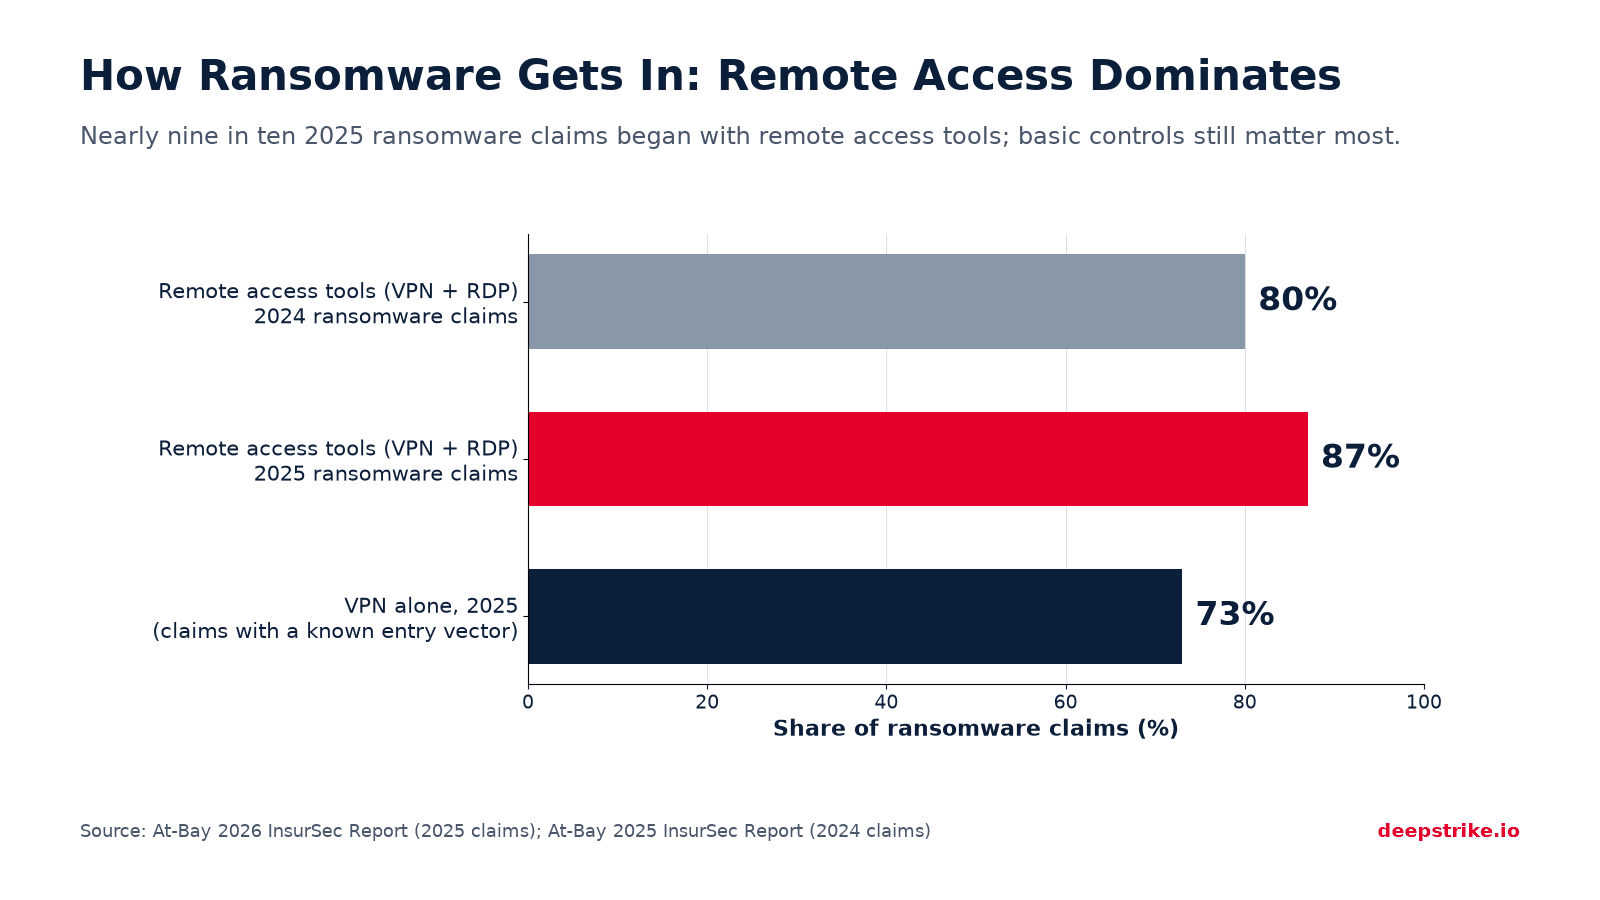
However, the most critical insight is not about the ransomware itself, but how the attackers get in. At-Bay's 2026 InsurSec Report found that remote access tools such as VPNs and RDP were the entry point for 87% of ransomware claims in 2025, up from 80% in 2024 per At-Bay's 2025 report. VPNs alone accounted for 73%, and SonicWall devices were linked to 27% of ransomware claims.
Breach data points the same way. IBM's 2025 Cost of a Data Breach Report (prior edition) named phishing the top initial attack vector (16% of breaches), and the Verizon 2026 DBIR found vulnerability exploitation behind 31% of initial access, with credential abuse at 13% initially and present at some stage in 39% of breaches.
This tells us that preventing the most expensive claims starts with mastering the basics: securing remote access, enforcing multi factor authentication, and patching compromised network vulnerabilities. Digging into the ransomware statistics shows just how prevalent these malware attacks have become.
The final piece of the claims puzzle is the data breach itself, and its costs keep climbing. IBM's 2026 Cost of a Data Breach Report puts the global average cost at a record $4.99 million, and the U.S. average at $11.5 million. For heavily regulated sectors, the figures are even higher: healthcare breaches average $6.64 million, and financial sector breaches about $6.3 million.
What’s driving this cost? It's not just IT recovery and downtime anymore. Regulatory action and class action lawsuits are major drivers. Allianz Commercial reports that non-attack incidents, such as wrongful data collection and processing or technical failures, made up a record 28% of large claims by value in 2024. Coalition's 2026 report adds that 72% of privacy rights claims cited the California Invasion of Privacy Act to target web tracking technologies.
This signals a fundamental shift. The definition of a "cyber incident" is expanding beyond traditional security breaches to include failures in data governance and privacy compliance. A company can now face a multi million dollar claim without a single malicious actor ever touching its network. The mounting financial and reputational damage is reflected in the latest data breach statistics.
Claims data shows that smaller and mid-sized organizations file most cyber claims, while large companies drive most of the cost: in NetDiligence's 2026 Cyber Claims Study, organizations under $2 billion in revenue filed 97% of claims, yet large companies accounted for 56% of total incident costs. Exposure also varies by sector, with governments, manufacturing, and technology among the most exposed.
Understanding who is being targeted is just as important as knowing how. The claims data reveals clear patterns based on company size and industry sector, allowing leaders to benchmark their own risk.
Size cuts both ways: in NetDiligence's 2026 Cyber Claims Study (10,309 claims from 2021 to 2025), organizations under $2 billion in revenue filed 97% of claims, while large companies, just 3% of claims, accounted for 56% of total incident costs.
Ransomware pressure shifts between company sizes from year to year. At-Bay's 2025 InsurSec Report found that businesses with $25 million to $100 million in revenue saw a 46% increase in ransomware claim frequency and a 47% increase in severity in 2024. In 2025 the pressure spread: At-Bay's 2026 report shows businesses under $25 million in revenue saw ransomware frequency rise 21% and severity climb 40% to $422,000, while Coalition found that businesses with more than $100 million in revenue had claims frequency five times higher than smaller organizations, with an average loss of $268,000.
The logic behind the 2024 spike was simple: mid sized companies combine significant revenue, valuable data and critical operational dependencies, but often lack the mature, enterprise grade security posture of their larger peers. The 2025 figures show that no size band is safe, though: smaller firms saw the fastest ransomware growth, while firms above $100 million in revenue had the most frequent claims. Benchmark against the band that matches your revenue and controls rather than assuming your size keeps you under the radar.
The risk profile also changes dramatically by industry. The data shows a clear difference between which sectors experience the most frequent attacks versus which suffer the most expensive ones.
This data provides a powerful lens for risk management. A leader at a manufacturing firm should be acutely aware of their ransomware exposure and prioritize operational resilience. A real estate company, which handles large wire transfers, should focus intensely on preventing FTF. For organizations in healthcare and finance, navigating HIPAA compliance challenges and meeting PCI DSS Penetration Testing Guide is not just a matter of compliance, but a core defense against crippling claims.
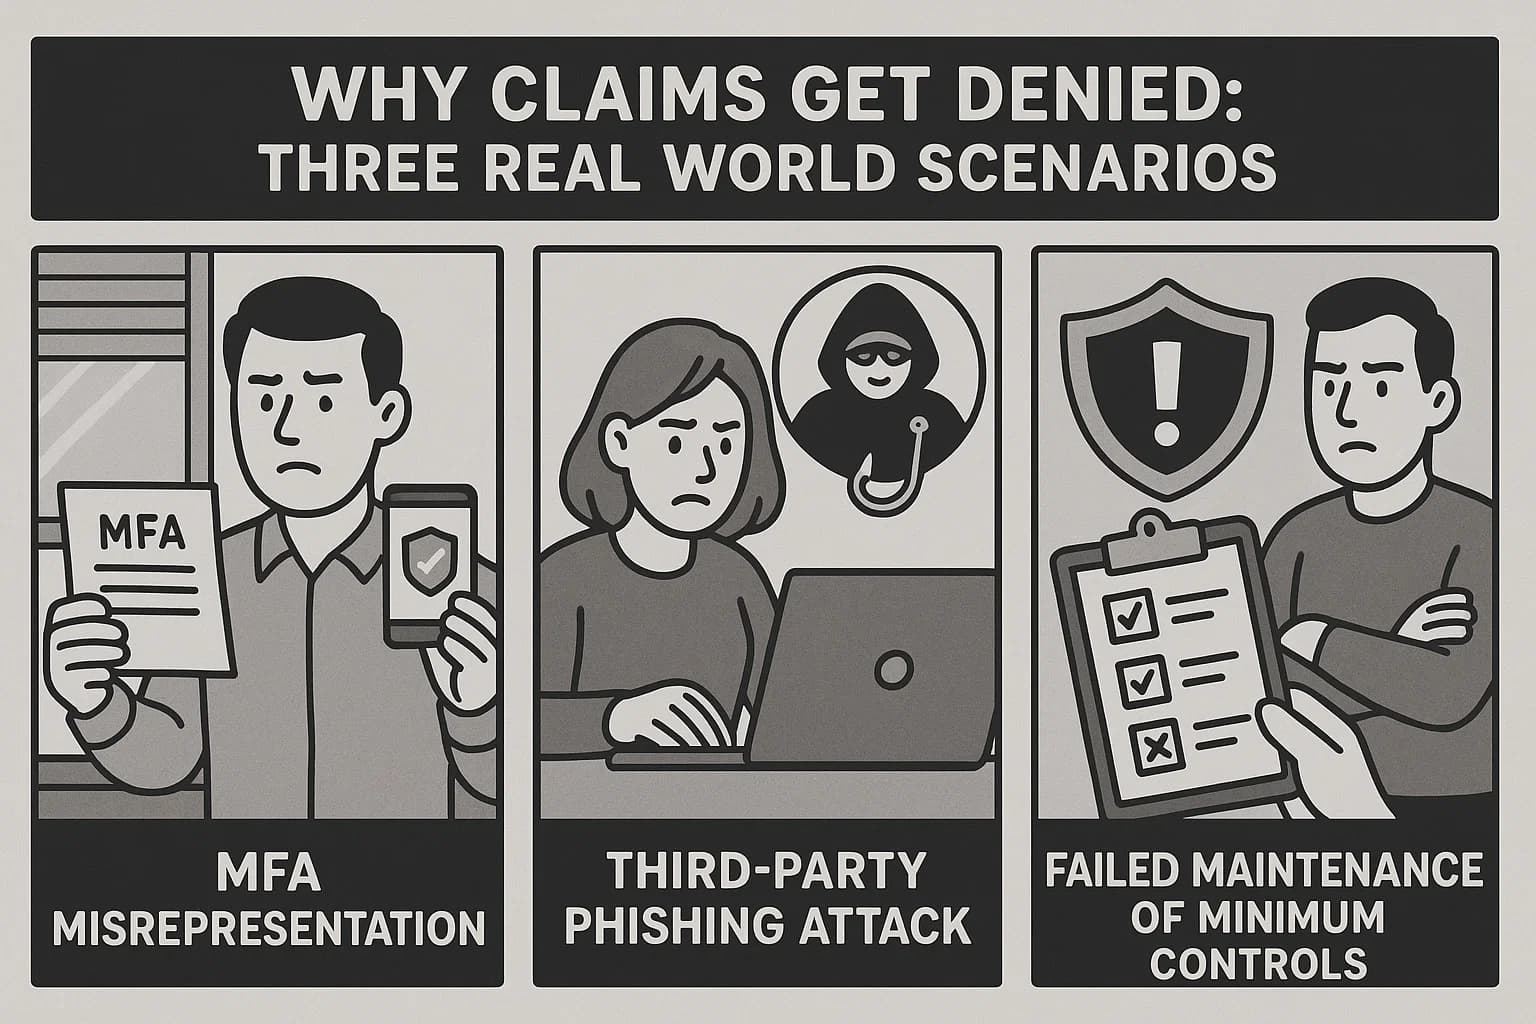
One of the most persistent myths in the industry is that "insurers never pay claims". The reality is that claim denials are rare, but many disputed claims turn on contractual issues such as application accuracy, exclusions and notice. A cyber insurance policy is a legal contract with strict obligations. The following real world cases are powerful cautionary tales that every business leader should understand.
To avoid the pitfalls highlighted in the case studies, leaders must understand the fundamental structure of their cyber insurance policies. These are not standardized products, and the details matter immensely.
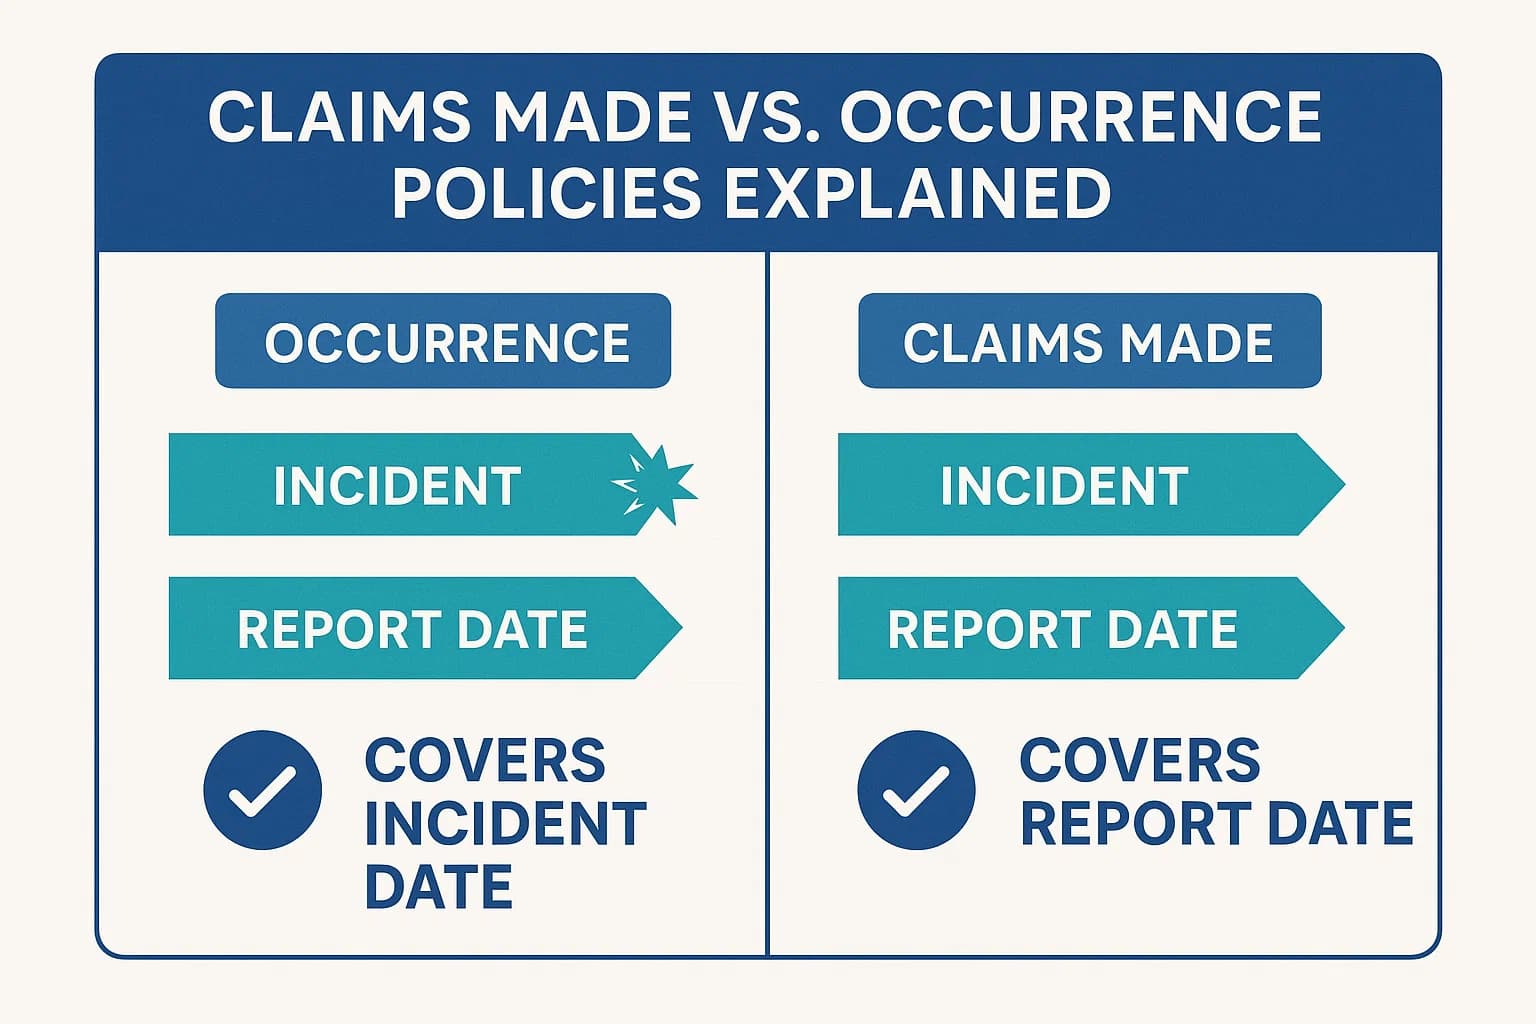
Liability policies come in two main flavors, and for cyber insurance, this distinction is everything.
This structure introduces two critical concepts:
The key takeaway is that the claims made nature of cyber insurance makes continuous, uninterrupted coverage essential. Any gap in coverage can leave your organization completely exposed for past actions.
Every policy has exclusions, but in the evolving world of cyber, some are more critical than others. Based on analysis from legal experts at firms like Reed Smith, here are the key exclusions to scrutinize :
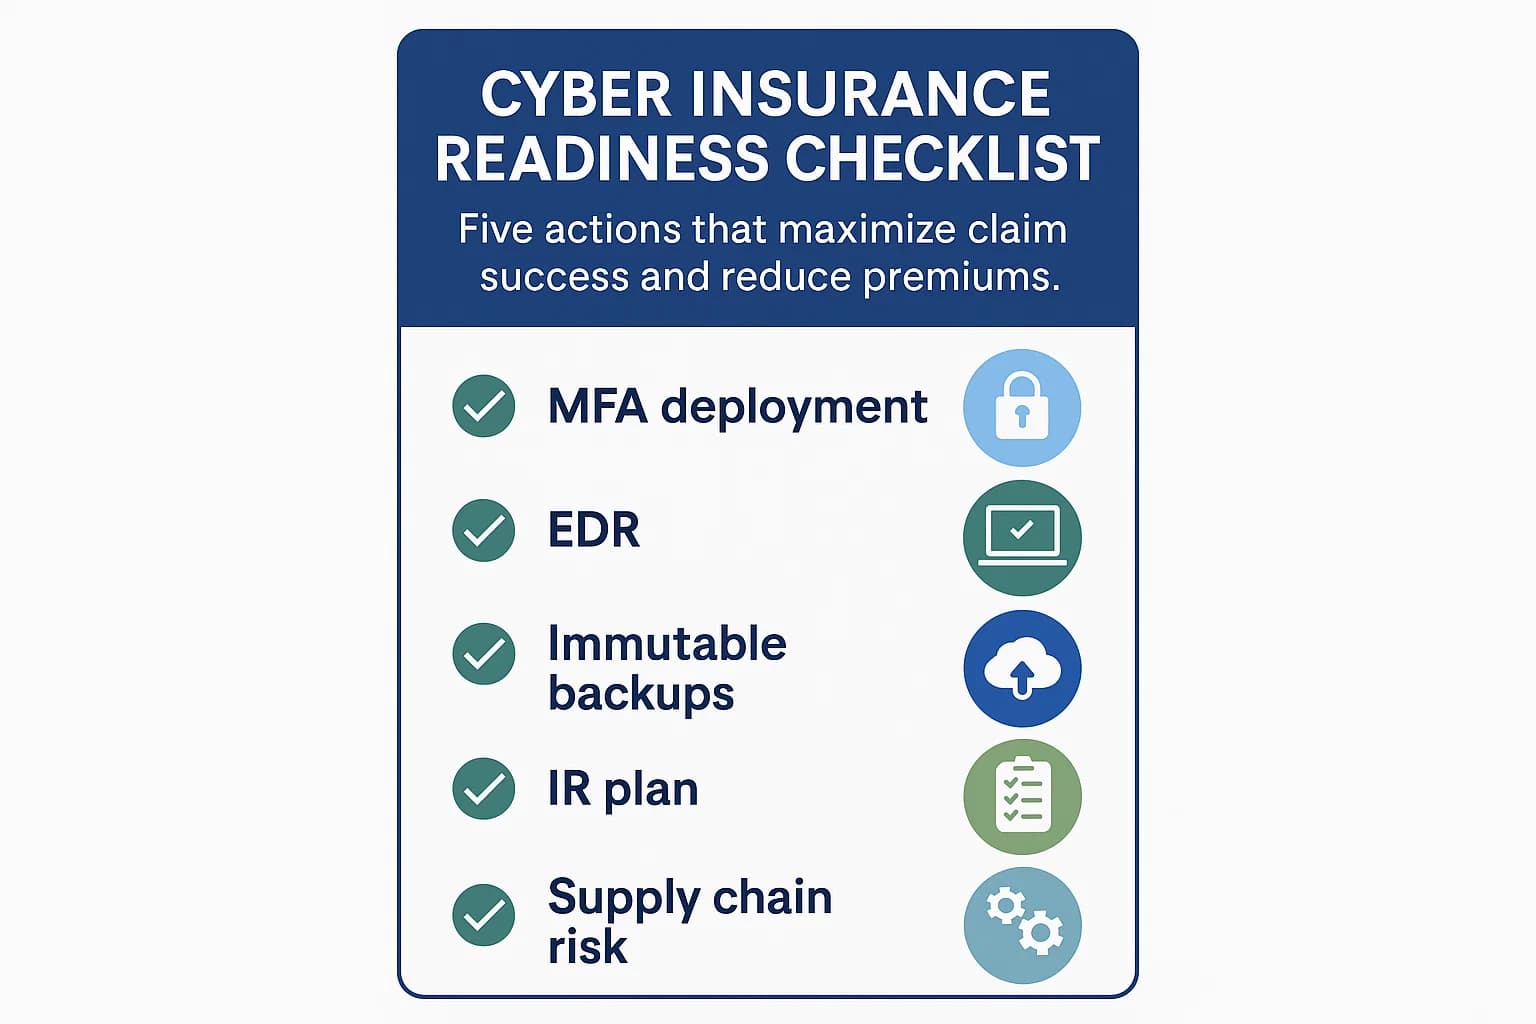
Translating this analysis into action is the final step. The following checklist provides a practical guide for business leaders to improve their insurability and maximize the chances of a successful claim recovery.
It varies dramatically by incident type. Coalition's 2026 Cyber Claims Report puts the average claim in 2025 at $116,000. Ransomware was the costliest type at $269,000, FTF averaged $141,000 and BEC $27,000. The total cost of a major data breach, including regulatory fines and legal fees, averages a record $4.99 million globally according to IBM's 2026 report.
Business Email Compromise (BEC) and the resulting Funds Transfer Fraud (FTF) are by far the most common, collectively making up 58% of all claims in Coalition's 2025 claims data. 52% of FTF claims started as a BEC, and 71% of FTF claims were a direct result of social engineering, so these attacks often succeed through human error.
Yes, most cyber policies provide coverage for ransom payments where it is legally permissible to pay. However, insurers often require that you use their approved panel of negotiators. Coalition reports that its incident response team negotiated ransom payments down by an average of 65%. It's important to note that fewer companies are choosing to pay (86% of Coalition's ransomware victims refused in 2025), and some governments are moving to ban payments by public sector entities, which could change the landscape.
In the current competitive market, the single best way to lower your premiums is by demonstrating a strong, mature, and evidence backed security posture. Implementing and being able to prove the effectiveness of mandatory controls like comprehensive MFA, EDR, regular vulnerability scanning, employee security training, and having a tested incident response plan will make you a more attractive risk to insurers and can lead to significant premium reductions.
Generally, yes. Policies are designed to respond to incidents that arise from employee mistakes, such as clicking on a phishing link, misconfiguring a cloud server, or falling for a social engineering scam. However, policies typically exclude intentional malicious acts by insiders. If your own employee intentionally steals data or sabotages systems, that would likely need to be covered by a separate Crime or Fidelity insurance policy.
The most common reasons are contractual failures by the policyholder. These include:
1) Misrepresenting the state of your security controls on the insurance application (e.g., saying you have MFA everywhere when you don't);
2) The specific incident falls under a clear policy exclusion (like an act of war or a failure of public infrastructure);
3) Failure to report the incident to the insurer within the strict timeframe required by the policy.
The cyber insurance claims statistics for 2026 paint a clear picture of a market at a crossroads. The era of buying a policy as a simple financial backstop for poor security is over. Today, lower prices are directly tied to higher expectations, and proactive, evidence based cybersecurity is no longer optional; it's a prerequisite for insurability.
The data shows that attackers are targeting the path of least resistance, whether through a simple phishing email leading to a massive wire transfer or an unpatched VPN leading to a crippling ransomware event. The most powerful takeaway from this analysis is that your insurance policy is a contract, and your application is a legally binding promise. Understanding the language of that contract and fulfilling your security obligations is the final, critical line of defense.
Ultimately, business leaders should reframe their view of cyber insurance. It is no longer just a tool for risk transfer; it is a strategic partnership. The requirements set forth by insurers are not arbitrary hurdles; they are a data backed blueprint for building a more resilient, defensible, and successful organization in the face of ever present digital risk.
Security questions don’t wait. Neither should you. Whether you're evaluating PTaaS, need help with a red team assessment, or just want to see what DeepStrike can uncover Reach out. We’re always happy to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
