February 6, 2025
Updated: November 5, 2026
From MFA enforcement to token handling and misconfiguration checks, this guide walks you through how to secure your Auth0 apps against real-world attacks.

Hossam Ahmed
Auth0 is a widely used authentication and authorization platform that simplifies identity management for web and mobile applications. It allows developers to integrate secure login, multi-factor authentication (MFA), and single sign-on (SSO) without having to build complex authentication systems from scratch.
For U.S. teams securing Auth0-backed applications, improper configurations or weak security measures can expose authentication systems to credential theft, account takeover, and token-handling risks. Attackers often target authentication systems to steal user credentials, take over accounts, or exploit vulnerabilities in token handling. To prevent these risks, it is essential to follow best practices and implement strong security controls when using Auth0.
This guide will walk you through key strategies to secure your Auth0 applications. From enforcing strong authentication methods and protecting API access to mitigating common security threats, you will learn how to build a robust security framework. By applying these measures, you can safeguard user data, prevent unauthorized access, and enhance the overall security of your applications.
Configuration reviews catch a lot; web application penetration testing checks how the login flow stands up to realistic attacks within an agreed scope.
MFA protects the Dashboard login, but the role decides how much a compromised or careless account can change. Auth0 offers scoped tenant member roles besides Admin. Viewer - Config Settings gives read-only access to configuration without secrets, billing, users or logs. Editor - Specific Apps can change only the applications assigned to it and can't create new ones. Editor - Users and Viewer - Users suit support staff who manage accounts but never touch connections or keys.
iss) and audience (aud) before accepting authentication..exp) before accepting authentication.Auth0 Attack Protection has four features, and their defaults are a starting point, not a finished configuration. Check each one under Security > Attack Protection, then make sure the events they raise reach someone who will act on them.
| Feature | What it stops | Default behavior | Log events to alert on |
|---|---|---|---|
| Brute-force Protection | Repeated failed logins against one account from one IP address | Threshold of 10 failed attempts per user and IP; blocks that IP for that user; account lockout is off by default | limit_wc |
| Suspicious IP Throttling | One IP address trying many accounts (credential stuffing) or mass signups | On by default in new tenants; throttles the IP after high login or signup velocity | limit_mu |
| Breached Password Detection | Logins and signups with passwords that appear in breach lists | Blocks or flags breached credentials, depending on the response you configure | pwd_leak |
| Bot Detection | Scripted logins from IP addresses with a bad reputation | Shows a CAPTCHA when a login attempt looks automated | Spikes in f, fp and fu (failed logins) |
Sources: Auth0's Attack Protection overview and Brute-force Protection pages, checked November 2026. The codes come from Auth0's log event filter reference: limit_wc marks an IP blocked after more than 10 failed attempts against one account, limit_mu an IP blocked after more than 100 failed logins or more than 50 signup attempts, and pwd_leak a login attempt with a leaked password. If you use rotating refresh tokens, also alert on ferrt. Auth0 logs that failed exchange when a used refresh token is replayed, and it revokes the whole token family when it detects reuse, which often points to a stolen token.
Retention is short, so export your logs. Auth0 keeps tenant logs for 1 day on Starter plans, 5 days on Essentials, 10 days on Professional and 30 days on Enterprise. A log stream sends them to Datadog, Splunk, Sumo Logic, a Marketplace integration or your own webhook, so investigations aren't limited to that window. The webhook hardening steps in the General section below apply to custom log streams.
A well-configured tenant doesn't help if the library that handles sessions or verifies tokens has a flaw. Auth0's SDKs get security fixes regularly, published as GitHub security advisories. Recent examples:
Note on Rules: Auth0 Rules have been read-only since November 18, 2024 (and unavailable in tenants created after October 16, 2023); they stop running and are removed after January 31, 2028. Implement the checks below in post-login Actions.
const myApiKey = event.secrets.MY_API_KEY;
exports.onExecutePostLogin = async (event, api) => {
  if (!event.user.email || !event.user.email_verified) {
    api.access.deny('Access denied.');
  }
};
const emailSplit = event.user.email.split('@');
const userEmailDomain = emailSplit[emailSplit.length - 1].toLowerCase();
if (userEmailDomain === 'example.com') {
  // Grant access
}
allowRememberBrowser to reduce MFA prompts safely.event.authentication to track MFA session history securely.if (event.request.query.prompt === 'none') {
// ❌ BAD: Can be abused
}
if (event.user.app_metadata.lastLoginDeviceFingerPrint === deviceFingerPrint) {
  // ❌ BAD: Can be spoofed
}
Require Email Verification for Email-Based Logins
Check for Existing Users During OAuth Registration
GET /api/v2/connections/{connection_id}
Authorization: Bearer {your_management_api_token}

PATCH /api/v2/connections/{connection_id}
Content-Type: application/json
Authorization: Bearer {your_management_api_token}

{
  "options": {
    ...every existing option from the GET response...,
    "disable_signup": true
  }
}
disable_signup is set to true for all relevant connections.Both issues below come from DeepStrike penetration tests of applications built on Auth0 (client details withheld). Neither was an Auth0 vulnerability. Both came from settings or application logic, which is why reviews and testing have to cover the application as well as the tenant.
What we found: The application was meant to be invite-only and hid its signup button. But Disable Sign Ups was off on the default database connection (Username-Password-Authentication). Hiding a button doesn't close the endpoint. Auth0's Authentication API accepts signups at POST /dbconnections/signup with a client ID, email, password and connection name, and a normal login page exposes all of those except the password.
Impact: Anyone could create an account. That let outsiders reach features meant for invited users and create fake accounts in bulk.
Fix: Turn on Disable Sign Ups for every database connection that shouldn't accept self-registration (the steps are in the checklist above), create users through the Management API or an invitation flow, and alert on unexpected ss (successful signup) events.
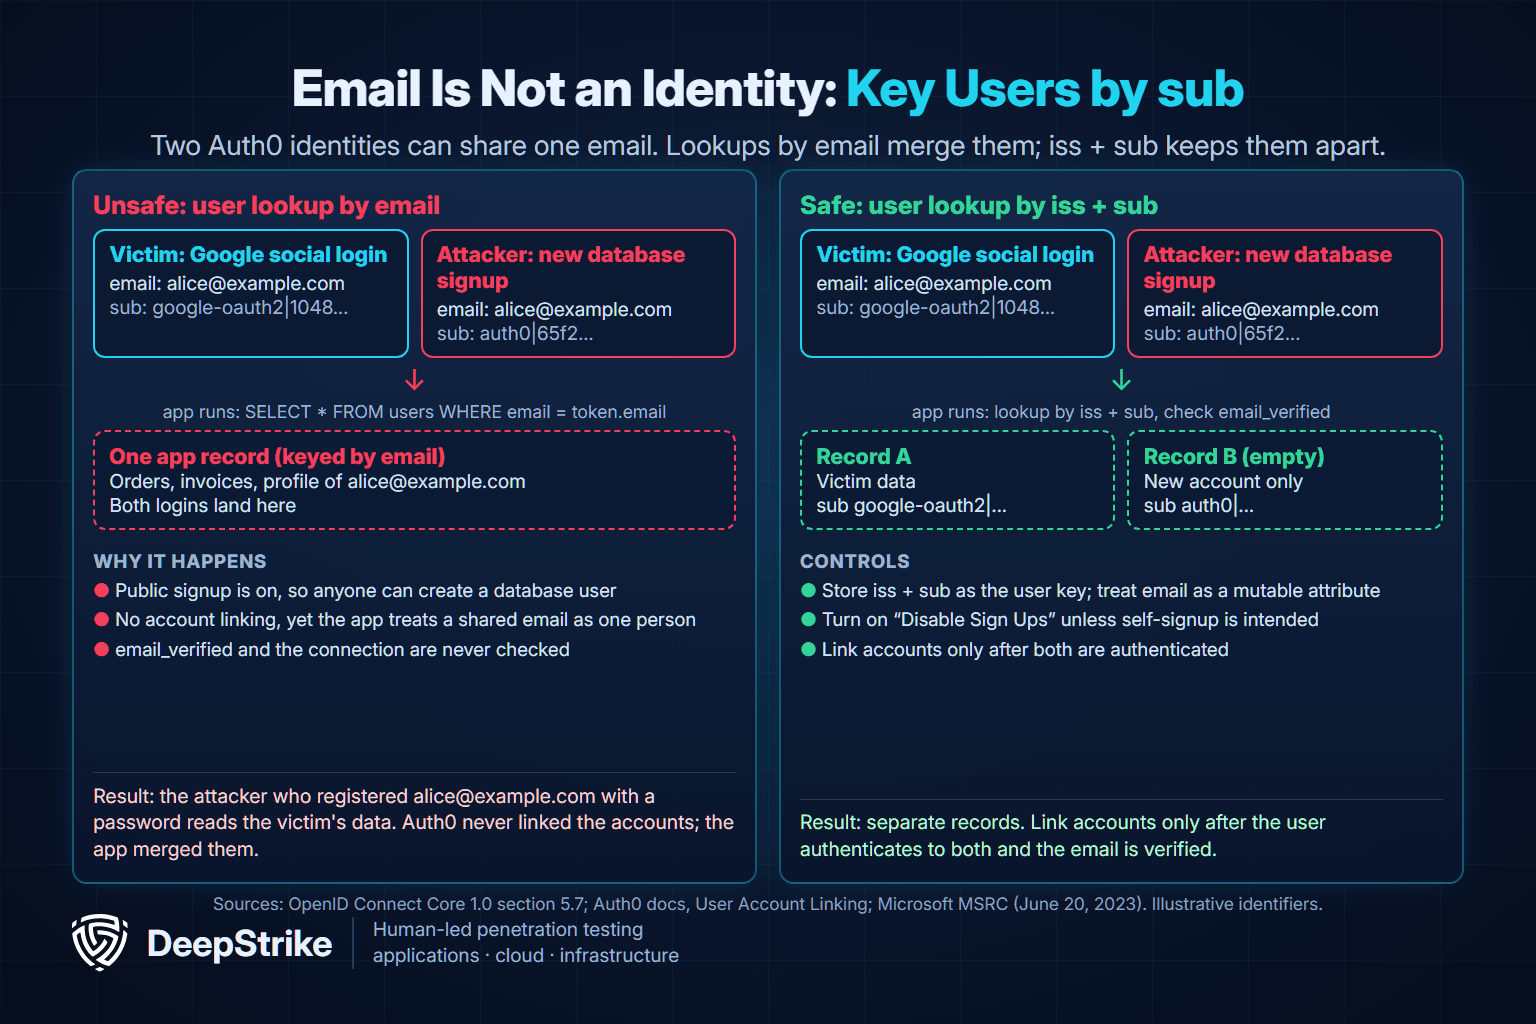
What we found: The application loaded user records by the email claim in the ID token. A user who signed up with Google and someone who later registered the same email through the database connection got two separate Auth0 identities with different sub values, because account linking wasn't configured. The application treated them as one person anyway.
Impact: An attacker who registered a victim's email address with a password could read the victim's data. Auth0 never linked the accounts; the application merged them. It's the same anti-pattern Microsoft warned about in June 2023, when it told developers never to use the email claim for authorization or primary user identification.
Fix:
Flaws like these show up when someone tests signup, login and account recovery with the same rigor as the rest of the app. Our web application penetration testing services cover those flows. For related patterns, see how OAuth flows go wrong, a cross-subdomain JWT account takeover and why lookups by user-controlled identifiers turn into IDOR.
Securing authentication and authorization is critical for protecting user data and maintaining trust in your application. Auth0 provides a powerful and flexible identity management solution, but improper configurations can expose your system to security vulnerabilities, data breaches, and compliance risks.
By following the best practices outlined in this guide, you can minimize security threats and ensure that your Auth0 implementation is robust and resilient.
If you need a security review of your Auth0 app to identify potential misconfigurations, feel free to contact us at DeepStrike!
Auth0 provides strong building blocks, including MFA, Attack Protection and signed tokens, but several protective settings are yours to turn on. Database connections accept public signups until you enable Disable Sign Ups, account lockout is off by default in Brute-force Protection, and API access tokens last 24 hours unless you shorten them. Review those settings and your application's own identity logic.
One email address can belong to several Auth0 identities, such as a Google login and a database signup, and email addresses can change. OpenID Connect treats only the iss and sub claims together as a stable identifier. Key user records by sub and check email_verified before trusting an email.
Auth0's documentation lists 1 day on Starter plans, 5 days on Essentials, 10 days on Professional and 30 days on Enterprise. Use a log stream to send logs to your SIEM if you need longer retention or alerting.
By default it blocks an IP address from logging in to a specific account after 10 failed attempts and returns a too_many_attempts error. The block ends after 30 days, when an admin removes it, when the user follows the unblock link in the notification email, or when the user changes their password. Lockout across all IP addresses stays off unless you enable it.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
