July 5, 2026
Updated: November 12, 2026
A source-backed 2026 guide to energy and utilities cybersecurity statistics covering power grid risk, OT/ICS, ransomware, DDoS, cloud, APIs, oil and gas, water utilities, and critical infrastructure threats.

Mohammed Khalil
Energy and utilities cybersecurity statistics in 2026 show a sector defined less by single headline incidents and more by persistent exposure across utilities IT, OT, cloud, remote access, customer-facing services, and supplier-connected environments. The strongest datasets point to five recurring realities: utilities remain breach-prone, ransomware pressure on industrial organizations remains high, DDoS volume is rising sharply, internet-facing OT exposure still persists, and third-party access remains one of the least mature control areas.
Use this table before turning any statistic into a board slide, budget request, or comparison point. The source scope determines how safely the number can be applied to energy and utility decisions.
| Source Scope | What It Means | How to Use It |
|---|---|---|
| Energy-specific | Data that directly measures energy companies, electric power, oil and gas, pipelines, renewables, or energy-sector incidents. | Use as the strongest evidence for energy-sector risk, budget prioritization, and executive reporting. |
| Utilities-specific | Data that specifically covers utilities such as electricity, water, wastewater, gas distribution, or utility-sector breach patterns. | Use for utility boards, municipal operators, customer-service risk, outage planning, and sector-specific benchmarking. |
| OT/ICS-wide | Industrial-control-system or cyber-physical-system telemetry across multiple industries, often including energy, water, manufacturing, transportation, and natural resources. | Use for OT exposure, segmentation, remote access, KEV, SCADA, and industrial-control risk, but do not present it as energy-only. |
| Critical-infrastructure-wide | Government, regulator, or sector-body data across multiple essential sectors such as energy, water, transportation, healthcare, communications, and government. | Use for policy, compliance, resilience, and national-risk framing while keeping the broader scope clear. |
| Cross-industry | Broad cybersecurity research across many industries, often covering ransomware, breach cost, API abuse, DDoS, cloud, identity, or third-party trends. | Use as context for shared risks, not as proof that the same rate applies to utilities or energy organizations. |
| Category | Statistic | Source | Year | Scope | Why It Matters |
|---|---|---|---|---|---|
| Utilities breaches | 638 incidents, 597 with confirmed data disclosure | Verizon DBIR executive summary | 2026 | Utilities sector | Confirms utilities remain a live breach category, not an edge case |
| Utilities breach patterns | System intrusion, basic web application attacks, and social engineering represent 94% of utility breaches | Verizon DBIR executive summary | 2026 | Utilities sector | Shows why utilities need both perimeter hardening and human-layer controls |
| Energy critical infrastructure complaints | 54 ransomware complaints and 31 data-breach complaints | FBI IC3 annual report | 2025 | U.S. energy critical infrastructure | Gives a government-sourced baseline for energy-sector reporting |
| Water critical infrastructure complaints | 25 ransomware complaints and 11 data-breach complaints | FBI IC3 annual report | 2025 | U.S. water/wastewater critical infrastructure | Supports treating water utility cyber risk separately from energy |
| Industrial and energy breach cost | Average breach cost was USD 5.50 million for the industrial sector and USD 5.24 million for the energy sector (USD 5.00 million and USD 4.83 million in 2025; industrial was USD 5.56 million in the 2024 edition) | IBM Cost of a Data Breach Report 2026 | 2026 | Industrial and energy sectors in a cross-industry study | Useful budget benchmark for industrial and utility leadership teams |
| OT exposure | 40% of organizations analyzed had OT assets insecurely connected to the internet | Claroty State of CPS Security OT Exposures | 2025 | OT across industrial, logistics, transportation, natural resources | Internet exposure still remains one of the clearest OT risk multipliers |
| OT exploitable weaknesses | 12% of analyzed OT devices contained KEVs; 7% of devices were exposed with KEVs linked to ransomware | Claroty State of CPS Security OT Exposures | 2025 | OT-wide | Prioritization should focus on exploitable, exposed, ransomware-relevant assets |
| IT/OT convergence impact | 24% of respondents said intrusions affected both IT and OT systems, down from 60% in 2025 | Fortinet State of OT and Cybersecurity 2026 | 2026 | Global OT survey | IT incidents can still create OT disruption even without direct controller compromise, though less often than a year earlier |
| Industrial ransomware targeting | Q4 2025: 49 oil and natural gas incidents, 31 electric incidents, 9 renewables incidents, 3 water incidents | Dragos industrial ransomware analysis | 2025 | Industrial victim tracking | Energy subsectors are persistent ransomware targets, even if volume is lower than manufacturing |
| DDoS scale | 2025 DDoS attacks more than doubled to 47.1 million | Cloudflare DDoS threat report | 2026 reporting on 2025 | Internet-wide | Utilities should assume public-facing service disruption risk is rising |
| API attack volume | 150 billion API attacks were documented from January 2023 to December 2024 | Akamai State of Apps and API Security | 2025 | Internet-wide | Relevant for utility portals, mobile apps, billing APIs, and partner integrations |
| Third-party exposure | Third-party involvement rose 60% year over year and reached 48% of all breaches | Verizon DBIR 2026 | 2026 | Cross-industry | Critical for vendor access, MSSPs, contractors, and supplier-connected operations |
| Energy attack ranking | Energy was the 4th most attacked industry, with 8% of incidents; 50% of energy cases began with exploitation of public-facing applications | IBM X-Force Threat Intelligence Index | 2026 | X-Force incident-response caseload | Places energy among the most targeted sectors and points to internet-facing exposure |
| Industrial ransomware groups | 119 ransomware groups targeted industrial organizations in 2025, up from 80 in 2024; OT ransomware dwell time averaged 42 days | Dragos OT/ICS Year in Review | 2026 reporting on 2025 | Industrial organizations, multiple sectors | More groups and long dwell times make OT visibility and containment a budget priority |
The concentration is clear. Utility breach data points to system intrusion, web attack paths, and social engineering. OT data points to exposed assets and exploitable weaknesses. Industrial ransomware tracking shows sustained pressure on electric and oil-and-gas organizations. Internet telemetry shows DDoS and API abuse continue to rise at a pace that matters to any utility running customer-facing digital services.
Energy and utilities cyber risk is shaped by the combination of critical-infrastructure dependence, IT/OT convergence, and availability-sensitive operations. The strongest statistics show that utilities still face real breach volume, ransomware remains persistent across industrial organizations, DDoS volume is climbing, internet-facing OT exposure has not disappeared, and third-party remote access remains a major weak point. Cloud services, APIs, smart-grid workflows, IoT, and customer portals widen the attack surface further. Regulatory pressure is increasing, but the data does not support a compliance-only response. For energy and utility leaders, the implication is straightforward: budgets should move toward visibility, exposure reduction, segmentation, recovery readiness, and repeated security validation.
Energy and utility organizations operate attack surfaces that look materially different from standard enterprise environments. The sector spans electric generation, transmission, and distribution; oil and gas production, transportation, and refining; and water and wastewater treatment and distribution. In the United States alone, CISA describes the electricity segment as containing more than 6,413 power plants, while GAO notes that the country also relies on nearly 170,000 water and wastewater systems.
That operating model creates layered cyber risk. Utilities often combine customer and billing systems, public web services, outage and dispatch processes, remote maintenance workflows, and OT environments built around PLCs, HMIs, SCADA, historians, engineering workstations, and field communications. NIST SP 800-82 emphasizes that OT security has to account for performance, reliability, and safety requirements that differ from conventional IT security design.
The result is that impact cannot be read only through breach counts. In these sectors, a successful intrusion can affect service availability, dispatch decision-making, plant support systems, regulatory reporting, environmental controls, customer confidence, or physical process continuity. That is why the most useful energy sector cybersecurity statistics are those that help leaders judge exposure, recovery capability, and attack-path realism rather than simply count malware families or generic cyber incidents.
This article prioritized official and primary-source material first, then sector bodies, then OT/ICS telemetry and credible cross-industry cyber reports. Government and regulatory sources were used for infrastructure scope, critical-infrastructure complaint data, water-sector findings, and regulatory context. OT/ICS vendor reporting was used for exposure, ransomware, and industrial telemetry where the dataset and scope were explicit. Broader cybersecurity statistics and cross-industry reports were included only when they added decision value for cloud, API, breach cost, ransomware, or supply-chain benchmarking.
| Criterion | Requirement | Why It Matters |
|---|---|---|
| Source credibility | Prefer government, regulators, sector bodies, primary reports, and established threat research | Weak roundup pages distort executive decisions |
| Publication year | Prefer 2024–2026; use older data only for historical context | Threat patterns and regulations change quickly |
| Energy and utilities specificity | Label energy, utilities, water, industrial, OT, and critical-infrastructure-wide data separately | Prevents false sector claims |
| OT/ICS specificity | Distinguish IT breach data from OT exposure or ICS telemetry | IT and OT statistics answer different budget questions |
| Scope clarity | State whether the number is utility-specific, industrial-wide, CPS-wide, or internet-wide | Scope is often the difference between useful and misleading |
| Measurement definition | Note whether a number measures incidents, complaints, victims, exposures, losses, or survey responses | Not all “cyber stats” measure the same thing |
| Regional relevance | Call out whether the source is U.S.-specific, EU-specific, or global | Regulatory and reporting contexts vary by region |
| Cross-industry caveat | Keep cloud, DDoS, API, and breach-cost benchmarks clearly labeled | These can inform utilities without pretending to be utility-only data |
| Reproducibility | Favor sources that publish methodology or dataset framing | Verification matters in procurement and board reporting |
| Avoidance of unsupported roundups | Exclude unattributed statistic lists and blog aggregations | Prevents fabrication and circular sourcing |
| Practical security relevance | Prefer numbers that influence exposure management, recovery, segmentation, and testing | Decision value matters more than numeric novelty |
| Operational safety relevance | Exclude claims that ignore the uptime and safety constraints of OT | Security guidance that ignores process safety is not useful |
Several statistics were intentionally excluded. Where no defensible energy-specific number was available, this guide either used a clearly labeled cross-industry benchmark or stated the limitation directly. That is particularly important for insider risk, cloud compromise, and modern API abuse, where many published numbers are real but not sector-specific enough to be presented as utility statistics.
The 2026 landscape is defined by the compression of once-separate attack surfaces. Verizon’s 2026 DBIR found that vulnerability exploitation became the leading initial access vector at 31% of breaches with a known vector (credential abuse fell to 13%), third-party involvement reached 48% of breaches after a 60% year-over-year increase, and ransomware rose to 48% of all breaches. That combination matters to utilities because it maps directly to vendor-supported systems, internet-facing portals, remote access platforms, and multi-operator environments.
Incident-response data puts energy near the top of the target list. IBM’s 2026 X-Force Threat Intelligence Index ranked energy as the fourth most attacked industry, with 8% of the incidents X-Force responded to in 2025. Exploitation of public-facing applications was the initial access vector in 50% of those energy cases, and Asia-Pacific (27%) and Europe (22%) accounted for the largest regional shares. That is incident-response caseload rather than a census of all attacks, but it points to the same internet-facing exposure the Verizon data shows.
For OT and ICS defenders, the warning signs are equally clear. Claroty found KEVs on 12% of nearly one million OT devices analyzed, while 40% of organizations in the dataset had those assets insecurely connected to the internet. CISA and the FBI also warned in 2026 that adversary activity against internet-facing PLCs caused disruptions across several U.S. critical-infrastructure sectors, while CISA’s February 2026 alert on the Poland energy incident highlighted vulnerable edge devices and OT/ICS security gaps.
This is why the modern utility cyber-threat model is not just ransomware or phishing. It is a stack: exposed services, weak remote access, supplier pathways, identity abuse, customer-facing applications, OT visibility gaps, and incident-response designs that still assume IT and OT can be managed separately. The statistics support a view of energy cyber risk as a continuity and safety problem, not only a confidentiality problem.
| Threat Area | Key Statistic | Source | Energy / Utilities Relevance | Security Takeaway |
|---|---|---|---|---|
| Ransomware | 54 energy-sector ransomware complaints; 25 water/wastewater ransomware complaints | FBI IC3 2025 | U.S. critical infrastructure | Government complaint data confirms real sector pressure |
| Data breaches | Utilities: 638 incidents, 597 with confirmed data disclosure | Verizon DBIR 2026 | Utilities sector | Breach activity is material enough to justify sector-specific benchmarking |
| Social engineering | Social engineering is one of the three patterns that make up 94% of utility breaches | Verizon DBIR 2026 | Utilities sector | Awareness and identity controls still matter in utility environments |
| Credential and software exploitation | Vulnerability exploitation was the initial access vector in 31% of breaches with a known vector; credential abuse was 13% | Verizon DBIR 2026 | Cross-industry benchmark relevant to vendor-heavy utility estates | Patch prioritization and exposure reduction matter more than vulnerability counts alone |
| Remote access compromise | 46% of CPS organizations said they were breached in the last 12 months because of third-party access | Claroty 2025 survey | Global CPS survey (1,100 respondents, multiple sectors) | Vendor access should be treated as a primary attack path |
| Exposed services | 40% of organizations analyzed had OT assets insecurely connected to the internet | Claroty OT Exposures 2025 | OT-wide | External attack surface reduction is a high-value control |
| OT / ICS exploitation | 12% of OT devices contained KEVs; 7% had KEVs linked to ransomware | Claroty OT Exposures 2025 | OT-wide | Risk ranking should prioritize exploitable and ransomware-relevant assets |
| IT/OT convergence | 24% of respondents said intrusions affected both IT and OT systems (60% in 2025) | Fortinet 2026 OT report | OT-wide survey with energy-related respondents | IT compromise can still create OT disruption even without controller malware |
| DDoS | 2025 saw 47.1 million DDoS attacks; Nozomi says DoS techniques accounted for over a third of techniques detected in customer OT/IoT environments | Cloudflare; Nozomi | Internet-wide plus OT/IoT telemetry | Utilities should treat availability as a core cyber objective |
| Cloud and multi-environment risk | 40% of all breaches involved data distributed across multiple environments | IBM 2024 (newer edition available) | Cross-industry benchmark | Hybrid estates increase investigation and recovery complexity |
| API abuse | Akamai documented 150 billion API attacks in 2023–2024 | Akamai 2025 | Internet-wide benchmark | Utilities with portals, apps, AMI integrations, and partner APIs need dedicated API controls |
| Supply chain | Third-party involvement rose 60% and reached 48% of breaches | Verizon DBIR 2026 | Cross-industry benchmark | Supplier security review needs to go beyond questionnaires |
The most important pattern across these threat areas is overlap. The same organization can face exposed internet services, supplier-connected remote access, cloud configuration drift, utility web-app risk, and OT segmentation weaknesses at the same time. That is why isolated control purchases often fail to change the risk picture.
Utilities-specific breach data is stronger than many buyers assume. Verizon’s 2026 DBIR utilities snapshot shows 638 incidents and 597 confirmed disclosures, with 94% of utility breaches concentrated in system intrusion, basic web application attacks, and social engineering. External actors accounted for 97% of utility breaches, and espionage appeared in 71% of utility breach motives, which is unusually high compared with many commercial sectors.
That matters because the electric power environment combines public-facing services, market and dispatch platforms, substations, remote support workflows, and increasingly distributed digital infrastructure. CISA describes the U.S. electricity segment as containing more than 6,413 power plants, and NERC continues to frame CIP standards as the backbone of mandatory security controls for the North American bulk power system.
Ransomware tracking also supports treating the power sector as a continuing target rather than a Colonial-Pipeline-only lesson. Dragos counted 31 electric-sector industrial ransomware incidents in Q4 2025 after 15 electric incidents in Q1 2025, while CISA’s alert on the December 2025 Poland energy-sector incident pointed directly to edge-device and OT/ICS weaknesses. Grid operators and utilities therefore need to think about cyber resilience as a blend of breach prevention, outage resilience, and grid-continuity preparation.
Statistics show volume; incidents show consequence. The public record since 2015 shows attackers moving from IT intrusion toward deliberate operational impact on grid equipment, and from opportunistic access toward long-term pre-positioning. The table below lists the energy incidents with primary public reporting that security leaders cite most often.
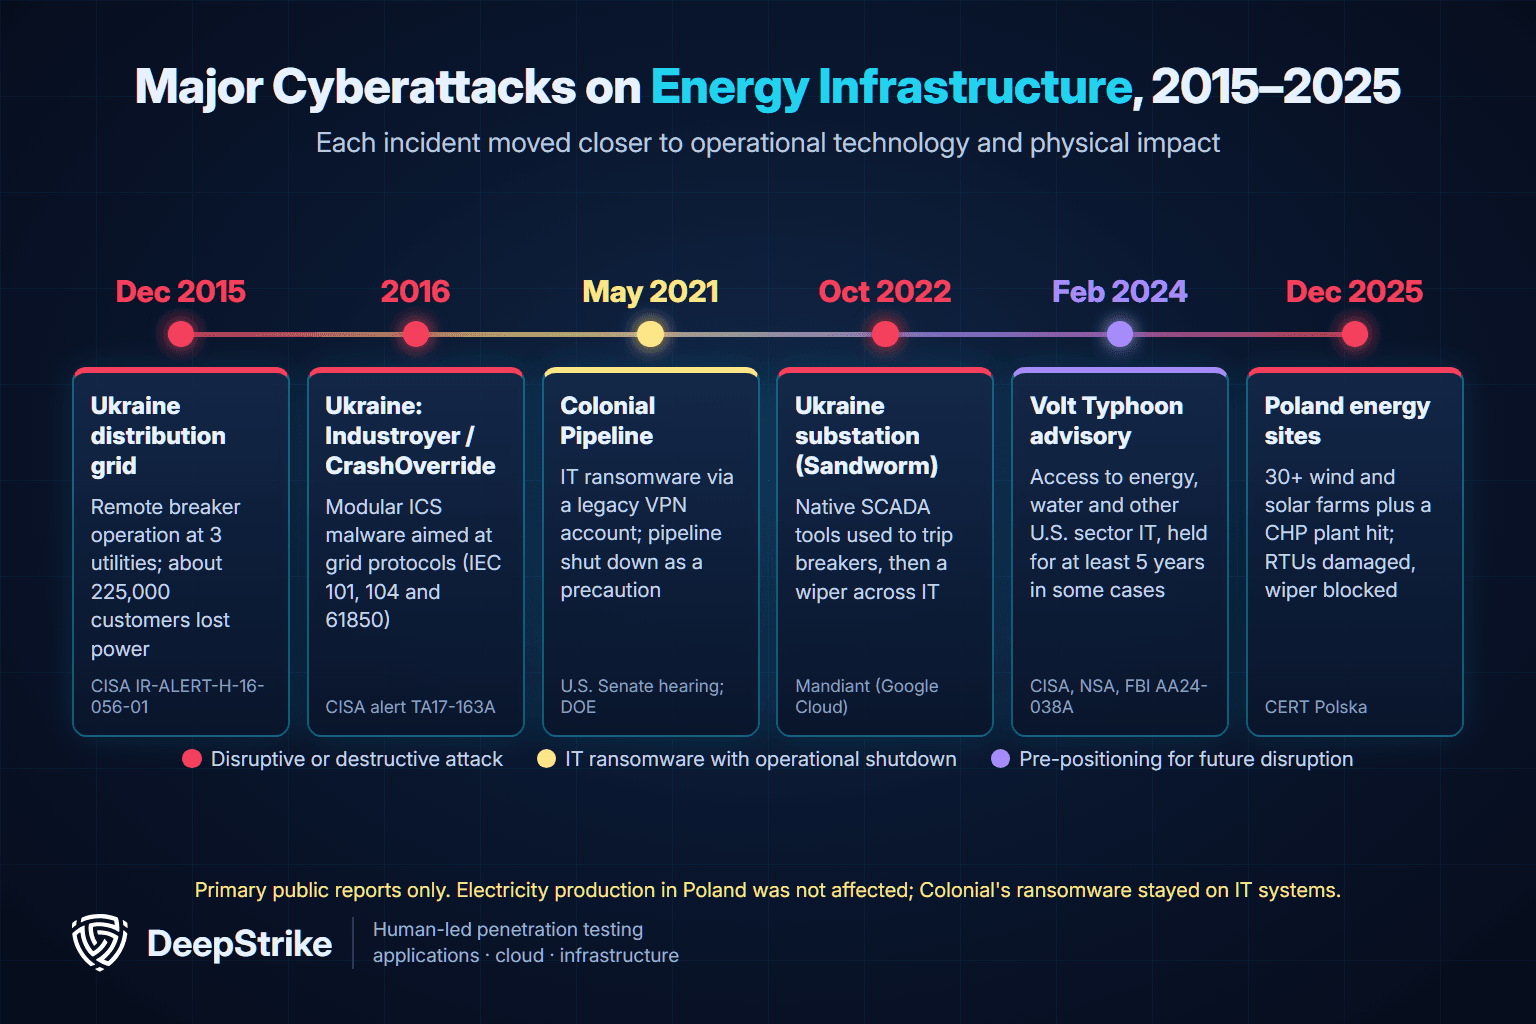
| Date | Incident | What happened | Primary source | Lesson for utilities |
|---|---|---|---|---|
| December 2015 | Ukraine distribution grid attack | Remote intruders operated breakers at three regional distribution companies, cutting power to about 225,000 customers, then wiped systems with KillDisk and corrupted substation serial-to-Ethernet firmware | CISA ICS alert IR-ALERT-H-16-056-01 | Stolen credentials plus legitimate remote tools were enough to reach control systems |
| 2016 | Ukraine: Industroyer / CrashOverride | Russian state actors deployed modular ICS malware built around grid protocols IEC 101, IEC 104 and IEC 61850 | CISA alert TA17-163A | Grid-protocol-aware malware turned outage capability into reusable code |
| May 2021 | Colonial Pipeline ransomware | DarkSide encrypted IT systems after entering through a legacy VPN profile; the company proactively shut down the pipeline | U.S. Senate hearing (June 2021); DOE | IT-only ransomware can still force an operational shutdown |
| October 2022 | Ukraine substation attack (Sandworm) | Attackers used native MicroSCADA tooling to issue commands likely meant to open breakers, then deployed a CaddyWiper variant across IT two days later | Mandiant (Google Cloud), November 2023 | Living-off-the-land OT attacks leave little malware to detect |
| February 2024 | Volt Typhoon advisory | CISA, NSA and FBI confirmed PRC state actors in IT environments of communications, energy, transportation and water organizations, with access kept for at least five years in some cases | CISA advisory AA24-038A | Pre-positioning for future disruption is a current, not hypothetical, threat |
| 29 December 2025 | Poland energy-sector attack | Attackers hit more than 30 wind and solar farms and a large CHP plant, damaging RTUs and protection devices at grid connection points; the CHP plant’s EDR blocked the wiper and electricity production was not affected | CERT Polska incident report (January 2026) | Distributed renewables and edge devices are now direct targets |
Sources: CISA’s 2015 Ukraine alert, CISA’s CrashOverride alert, Colonial Pipeline testimony to the U.S. Senate, Mandiant’s Sandworm analysis, CISA advisory AA24-038A and CERT Polska’s incident report.
Two patterns repeat across these cases. First, attackers relied on legitimate access: harvested credentials and VPN connections in 2015, a legacy VPN profile at Colonial, native SCADA software in 2022 and living-off-the-land techniques in the Volt Typhoon campaign. Second, several attacks deliberately damaged recovery, through KillDisk, wipers, corrupted device firmware and, in Ukraine in 2015, scheduled disconnection of server UPS units. For utilities, that makes identity and remote-access control, east-west monitoring and tested restoration the controls the incident record supports most. For background on the actors involved, see our analysis of state-sponsored APT threats.
Oil and gas should not be treated as an abstract critical-infrastructure category. It is an operationally distributed environment with compressor stations, pipeline control systems, terminals, refineries, contractor access, and remote assets that often rely on external communications and supplier support. CISA’s energy-sector framing explicitly includes electricity, oil, and natural gas segments, while TSA continues to maintain mandatory pipeline cybersecurity directives.
Dragos’s industrial ransomware tracking shows why that matters in practice. In Q4 2025, Dragos recorded 49 oil-and-natural-gas incidents, alongside 31 electric incidents, and it described energy-related sectors as consistently targeted throughout the quarter. Earlier 2025 tracking also showed oil and natural gas incidents in Q1 and Q2, confirming sustained attention rather than a single-quarter spike.
The Colonial Pipeline case remains relevant because it showed how an IT-side ransomware event can force operational shutdown decisions in pipeline environments. DOE states that Colonial proactively shut down its pipeline system in response to the May 2021 ransomware attack. The lesson for refinery, terminal, and midstream leaders is not that every ransomware event will hit OT directly. It is that OT-adjacent business systems can still become operational choke points.
Water statistics deserve their own treatment because the sector has different economics, staffing realities, and regulatory dynamics than the power and oil-and-gas segments. GAO notes that the United States has nearly 170,000 water and wastewater systems, many of them small and resource-constrained. EPA’s 2024 enforcement alert then added a sharper warning: over 70% of inspected drinking-water systems since September 2023 were out of compliance with basic statutory requirements, and inspectors found issues such as default passwords, shared logins, and former-employee access that had not been curtailed.
Recent oversight data shows that federal attention on water cybersecurity is not theoretical. EPA’s FY 2027 congressional justification states that in FY 2025 the agency either led or accompanied inspections at over 210 community water systems, with more than 170 including an evaluation of cybersecurity risks, and conducted off-site compliance monitoring at about 340 systems. In a 30 July 2026 public service announcement, the FBI and EPA reported that water and wastewater utilities in at least seven states had reported attacks since 27 July 2026 on internet-facing Rockwell Automation/Allen-Bradley MicroLogix PLCs, some of which degraded water operations.
Complaint and ransomware telemetry reinforces the point. FBI IC3 logged 25 ransomware complaints and 11 data-breach complaints for water and wastewater systems in 2025, while Dragos recorded water-sector incidents in every quarter of 2025 (2, 6, 4 and 3 from Q1 to Q4). The right conclusion is not that water is safe because its volume is lower than manufacturing. It is that a sector with smaller teams and older estates is still facing persistent essential-service cyber pressure.
Utilities do not need a generic explanation of OT. They need a reminder that OT security is governed by constraints that standard IT programs often underweight: safety, uptime, fragile assets, engineering ownership, specialized protocols, and consequences that extend beyond data loss. NIST SP 800-82 states directly that OT security must address unique performance, reliability, and safety requirements.
The numbers on exposure are difficult to ignore. Claroty’s 2025 OT exposures research found KEVs on 12% of analyzed OT devices, ransomware-linked KEVs on 7% of devices, insecure internet connectivity in 40% of organizations, and OT assets communicating with malicious domains in more than 12% of industrial organizations. Fortinet’s 2026 survey found that 24% of respondents reported intrusions affecting both IT and OT systems, down from 60% in its 2025 edition.
MITRE ATT&CK for ICS also helps explain why utility cyber risk cannot be reduced to “patch faster.” The current ICS matrix spans 12 tactics, including Inhibit Response Function, Impair Process Control, and Impact, which are directly tied to operational disruption rather than only data theft. Smart-grid and distributed-energy environments make this more pressing because more digital connectivity means more pathways into operational workflows, as seen in CISA’s Poland alert and DOE’s DER cybersecurity guidance.
Our SCADA penetration testing guide explains how to test utility control networks without risking operations.
Ransomware remains the most visible cyber risk in energy and utilities because it sits at the point where IT disruption, operational dependency, supplier access, and executive pressure meet. FBI IC3 received more than 3,600 ransomware complaints in 2025 with reported losses exceeding $32 million, while noting that ransomware remains among the highest reported cyber threats targeting critical infrastructure organizations. Those reported losses understate true impact because business interruption and remediation costs are often not fully captured in IC3 reporting.
Cross-industry data points the same way. Verizon’s 2026 DBIR says ransomware grew to 48% of all breaches, and the 2026 report also highlights the continued growth of third-party breaches. For energy and utility leaders, that pairing matters more than the ransomware headline alone because it shows how supplier-connected or service-provider-connected environments can become the delivery path for extortion events.
Industrial telemetry keeps the energy picture honest. Dragos documented 742 ransomware incidents affecting industrial entities in Q3 2025 and substantially higher Q4 activity, including 49 oil-and-natural-gas incidents, 31 electric incidents, 9 renewables incidents, and 3 water incidents. Those counts come from industrial victim tracking and should not be read as confirmed OT encryption cases in every instance. But they do show sustained targeting of operationally sensitive sectors. The pace held into 2026: Dragos’s Q2 2026 analysis counted 1,140 ransomware incidents affecting industrial organizations, up 12% from 1,020 in Q1 2026, and found no case in which operators directly manipulated a control system.
The annual view points the same way. Dragos’s 2026 OT/ICS Year in Review (February 2026) counted 119 ransomware groups targeting industrial organizations in 2025, up 49% from 80 in 2024, and about 3,300 industrial organizations affected worldwide. It put the average ransomware dwell time in OT environments at 42 days, compared with about 5 days for organizations with comprehensive OT visibility, and reported that the ELECTRUM group targeted combined heat and power facilities and renewable energy management systems in Poland in December 2025. Utilities can compare these figures with ransomware statistics across all sectors.
For buyers, the implication is operational. Recovery readiness has to cover identity systems, jump hosts, VPNs, virtualization, backup orchestration, historians, dispatch-adjacent applications, billing, and customer communications. Segmentation validation and restoration testing matter because ransomware in these environments is often dangerous precisely when it remains “only” in IT.
Availability has become a first-order cyber metric for utilities. Cloudflare reported that DDoS attacks more than doubled in 2025 to 47.1 million, with an average of 5,376 DDoS attacks every hour. In Q2 2025 alone, Cloudflare blocked more than 6,500 hyper-volumetric DDoS attacks, averaging 71 per day, and reported a peak attack size of 7.3 Tbps; the largest attack Cloudflare reported for all of 2025 reached 31.4 Tbps. That is internet-wide data, but it directly matters to utility customer portals, payment systems, DNS, outage reporting, and public communications channels.
Nozomi’s OT/IoT telemetry shows why DDoS cannot be dismissed as a “web-only” issue. In its July 2025 Trends & Insights release, Nozomi ranked Energy, Utilities & Waste among its top five targeted sectors and said network denial of service and denial of service together accounted for over a third of techniques associated with raised alerts in customer environments.
Cloud and API exposure broaden the picture further. Akamai documented 150 billion API attacks from January 2023 through December 2024 and reported a 33% year-over-year rise in global web attacks. IBM’s 2024 breach research found that 40% of all breaches involved data distributed across multiple environments and that public-cloud breaches carried the highest average cost at USD 5.17 million. For utilities, the relevance is immediate: customer apps, AMI integrations, DER management interfaces, vendor APIs, and cloud-hosted support systems all add internet-facing control and data paths.
Few categories have moved from secondary concern to board-level issue as quickly as supplier and remote-access risk. Verizon’s 2026 DBIR says third-party involvement rose 60% year over year and reached 48% of total breaches. That is a cross-industry figure, but it is especially relevant to utilities because they depend heavily on external maintenance, engineering support, telecoms, OEMs, cloud platforms, and managed service providers.
Claroty’s 2025 CPS survey strengthens that conclusion in operational environments. The survey found that 67% of respondents are reconsidering supply-chain geography, 73% are re-evaluating third-party remote access to CPS operations, and 46% said their organization experienced a breach in the last 12 months caused by third-party vendor access. It also found that 54% discovered security gaps or weaknesses in vendor contracts after incidents. As survey data, these figures are not utility-specific complaint counts, but they are highly relevant to energy and utility procurement teams.
Utilities should read these numbers as a procurement and architecture problem, not only a vendor-risk-management paperwork problem. The real controls sit in enforced MFA, brokered access, privilege boundaries, logging, session recording, asset-level access rules, contract language, and the removal of persistent vendor pathways that no longer serve a business need. The same logic applies inside the plant: strict access controls on control-room workstations, engineering laptops, and removable media limit what a careless or malicious insider can reach.
The regulatory picture is increasingly regional, but the direction of travel is consistent. In the United States, NERC’s CIP standards remain the mandatory control spine for the bulk electric system, TSA continues to issue pipeline cybersecurity directives, and EPA has increased direct water-system cyber oversight. CISA’s Cross-Sector Cybersecurity Performance Goals are now part of the common language of critical-infrastructure risk reduction, and CISA’s 2025 adoption report said the strongest impact was visible in sectors including Water and Wastewater Systems.
In the European Union, NIS2 tightened cybersecurity obligations across critical sectors and explicitly covers energy, drinking water, and wastewater. The European Commission and EUR-Lex materials also make clear that supply-chain risk management is now part of the expected control set, not an optional add-on. ENISA’s newer analyses continue to emphasize sector-specific implementation challenges tied to OT constraints, legacy systems, and cross-jurisdictional complexity.
The largest regulatory change for North American grid operators since 2024 is internal monitoring. NERC’s CIP standards (CIP-002 through CIP-014) already cover asset categorization, electronic and physical security perimeters, access control, incident response, recovery and supply-chain risk for the bulk electric system. On 26 June 2025, FERC Order No. 907 approved CIP-015-1, which requires internal network security monitoring (INSM) for network traffic inside the electronic security perimeter of high-impact and medium-impact BES Cyber Systems. FERC also directed NERC to extend INSM to electronic access control or monitoring systems and physical access control systems outside that perimeter. In practice, regulators now expect utilities to detect an attacker who is already inside, not only to keep one out.
| Framework | Applies to | Mandatory? | Core focus | Recent milestone |
|---|---|---|---|---|
| NERC CIP (CIP-002 to CIP-014) | North American bulk electric system | Yes, enforced by NERC and FERC in the U.S. and by Canadian regulators | Asset categorization, perimeters, access, incident response, recovery, supply chain | Standards revised on a rolling basis |
| NERC CIP-015-1 | High- and medium-impact BES Cyber Systems | Yes, once effective | Internal network security monitoring inside the electronic security perimeter | FERC Order No. 907, 26 June 2025 |
| TSA pipeline security directives | TSA-designated critical pipelines in the U.S. | Yes | Segmentation, access control, monitoring, incident reporting and response plans | Directives reissued periodically |
| NIST Cybersecurity Framework 2.0 | Any organization | Voluntary | Govern, Identify, Protect, Detect, Respond, Recover | Version 2.0 released February 2024 |
| NIST SP 800-82 Rev. 3 | OT and ICS environments | Voluntary guidance | OT risk management, architecture and safety-aware controls | Rev. 3 published September 2023 |
| ISA/IEC 62443 series | Asset owners, integrators and product suppliers in OT | Voluntary unless required by contract or regulation | Zones and conduits, security levels, secure product development | Widely referenced in procurement |
| IEC 62351 series | Power-system communication protocols | Voluntary | Authentication and encryption for protocols such as IEC 61850 and IEC 60870-5-104 | Used in substation and DER designs |
| EU NIS2 Directive | Essential and important entities, including energy, drinking water and wastewater | Yes, through national law | Risk management, supply-chain security, incident reporting, management accountability | National transposition deadline 17 October 2024 |
| EU Cyber Resilience Act | Manufacturers of products with digital elements sold in the EU, including OT and grid devices | Yes | Secure-by-design products and vulnerability handling | Reporting duties from 11 September 2026; main obligations from 11 December 2027 |
Sources: NIST Cybersecurity Framework, NIST SP 800-82 Rev. 3, IEC overview of IEC 62443, the NIS2 Directive on EUR-Lex and the European Commission’s CRA reporting page. For the EU obligations in more depth, see our guides to NIS2 penetration testing and compliance and the Cyber Resilience Act.
Most utilities map one control set to several of these frameworks rather than running separate programs. The statistics above suggest where that mapping needs evidence instead of paperwork: internet-facing exposure, third-party remote access, IT/OT segmentation and the new internal-monitoring expectation are all areas where a control can exist on paper and still fail under test.
For multinational operators, the practical implication is that “compliance maturity” should not be confused with “cyber resilience maturity.” Regulations are increasingly forcing energy and utility organizations to formalize controls around asset visibility, incident reporting, supply chain relationships, and security governance. The statistics in this article suggest that the organizations that benefit most will be those that use regulation to accelerate validation, not just documentation.
The statistics support a disciplined priority stack.
First, visibility still matters because it remains the prerequisite for every other control. If 40% of organizations in Claroty’s OT exposure study still had internet-connected OT assets, many defenses are failing before detection or response even begins. Asset inventory, service discovery, exposure review, and external attack-surface validation should therefore be treated as foundational work.
Second, utilities should assume that third parties and remote access are part of the core attack surface. The combination of Verizon’s 48% third-party breach involvement and Claroty’s 46% breach-via-third-party-access survey result is strong enough to justify tighter procurement controls, access brokering, session governance, contract reviews, and recurring access recertification.
Third, cloud, applications, and APIs are no longer secondary to critical infrastructure security. Utility portals, billing systems, mobile apps, and partner APIs often hold the keys to identity, payments, and customer operations. That makes API security testing, web application penetration testing, cloud penetration testing, and identity hardening practical control areas, not side projects.
Fourth, ransomware readiness needs to be tested rather than assumed. The available data supports investment in network segmentation, immutable and restoration-tested backups, detection engineering, tabletop exercises, and controlled red-team or penetration-testing programs focused on real attack paths. In OT-adjacent environments, testing should be carefully scoped, coordinated with operations, and designed to avoid production disruption.
Energy and utility organizations can use these findings to prioritize validation across internet-facing assets, cloud environments, APIs, customer portals, identity systems, network infrastructure, and safely scoped OT-adjacent environments. DeepStrike’s relevance in this context is practical rather than promotional: penetration testing, API penetration testing, cloud penetration testing, network testing, red team assessments, remediation tracking, and retesting support all fit naturally into a security-validation program based on exposure rather than assumptions.
| Security Area | What the Statistics Suggest | What Energy and Utility Teams Should Check |
|---|---|---|
| External attack surface | Internet-facing OT and utility services remain a recurring problem | Public IP inventory, orphaned services, edge-device lifecycle, KEV exposure |
| OT asset visibility | Blind spots remain common even in mature programs | Passive OT discovery, asset criticality, ownership mapping |
| IT/OT segmentation | IT intrusions still reach OT operations in a meaningful share of organizations | Firewall rules, jump hosts, one-way flows where justified, segmentation validation |
| DDoS resilience | Availability attacks are rising sharply | CDN/WAF/DDoS posture, DNS resilience, outage-portal failover |
| Ransomware readiness | Energy and industrial organizations remain persistently targeted | Offline backups, restoration testing, identity containment, admin isolation |
| Backup resilience | Recovery time is a business issue, not just an IT issue | Recovery priorities for dispatch, billing, portals, and OT-adjacent systems |
| API security | Utility digital services increasingly depend on APIs | API inventory, auth review, rate limiting, API pentesting |
| Cloud security | Hybrid environments increase breach complexity | IAM, logging, CSPM, secret management, internet exposure review |
| Customer portal security | Web app paths remain central in utility breaches | Auth flows, session management, account takeover controls |
| Mobile app security | Apps increasingly connect customers to utility workflows | Mobile app testing, API abuse scenarios, token handling |
| Identity and MFA | Credentials and social engineering remain frequent pathways | MFA coverage, phishing-resistant auth for admins, conditional access |
| Privileged access | OT and utility support roles are high-impact accounts | PAM, session recording, break-glass governance |
| Remote vendor access | Supplier-connected access is one of the clearest risks | Brokered access, time-bound access, contract requirements |
| Logging and monitoring | Operational disruption often begins before it is classified as OT compromise | Cross-domain telemetry, identity logs, VPN logs, EDR, OT anomaly detection |
| Incident response | Utility recovery requires more than SOC playbooks | OT-aware IR plans, executive decision points, customer comms plans |
| Third-party risk | Contract and supplier gaps are regularly discovered after incidents | Security clauses, access reviews, evidence requirements, termination pathways |
| Vulnerability management | Vulnerability counts alone do not indicate utility risk | KEV-based prioritization, exposure-based remediation, compensating controls |
| Penetration testing cadence | Static annual testing is often too slow for changing estates | Risk-based cadence for web, API, cloud, and external infrastructure |
| Red team validation | Attack-path realism matters in high-impact environments | Objective-based assessments, detection validation, safe OT-adjacent scoping |
| Internal network monitoring | NERC CIP-015-1 now expects monitoring inside the electronic security perimeter | East-west sensor coverage, traffic baselines, alert triage for control-network anomalies |
| Executive reporting | Board discussions should connect cyber metrics to continuity | Report exposure reduction, restoration readiness, supplier risk, and service availability |
The first mistake is scope inflation. Utilities-specific breach data, OT-wide telemetry, industrial ransomware leak-site counts, and internet-wide DDoS metrics cannot be treated as if they were measuring the same thing. They answer different questions and should stay separated in board papers and procurement memos.
The second mistake is category mixing. Energy, utilities, industrial, and critical infrastructure overlap, but they are not interchangeable labels. Water cybersecurity statistics should not be repackaged as energy-sector numbers, and industrial OT findings should not be presented as utility-only evidence without a clear caveat.
The third mistake is control-free storytelling. A long list of cyber numbers becomes marketing filler unless it leads to decisions about exposure management, segmentation, vendor access, application testing, cloud review, restoration testing, and executive reporting. Statistics are useful when they change priority, budget, or validation scope. They are not useful when they are used as dramatic decoration.
What are the most important energy and utilities cybersecurity statistics?
The most decision-useful figures are the ones that connect to real control priorities: Verizon’s utility-specific breach snapshot, FBI IC3’s critical-infrastructure complaint counts for energy and water, OT exposure data on internet-connected assets and KEVs, industrial ransomware counts for electric and oil-and-gas organizations, and current DDoS, API, and cloud-breach benchmarks. Together, those numbers speak to exposure, continuity, and recovery rather than just cyber volume.
Why are energy and utilities high-risk cybersecurity sectors?
Because they combine essential-service dependency, IT/OT convergence, public-facing digital services, supplier-connected operations, and systems that often cannot be patched or restarted on ordinary enterprise timelines. NIST’s OT guidance highlights the sector’s performance, reliability, and safety constraints, while current utility breach, ransomware, and OT-exposure statistics show that these are active attack surfaces, not just theoretical weaknesses.
What is the biggest cyber risk for electric utilities?
There is no single dominant risk, but the strongest data suggests utilities should focus on the combined effect of system intrusion, web-application exposure, social engineering, third-party access, and OT-adjacent continuity dependencies. Verizon’s utilities snapshot is especially useful here because it shows 94% of utility breaches clustering around a small set of recurring patterns.
How serious is ransomware for the energy sector?
Serious enough to treat as a continuity issue rather than only a malware issue. FBI IC3 continues to classify ransomware as one of the highest reported cyber threats to critical infrastructure, and Dragos documented sustained ransomware targeting across electric utilities, oil and natural gas, renewables, and water in 2025. The most important nuance is that operational disruption can happen even when the initial compromise stays on the IT side.
Why is OT cybersecurity important for utilities?
Because utility operations depend on OT for monitoring, control, and safe process execution. NIST SP 800-82 emphasizes the unique performance and safety requirements of OT, and current exposure research shows that exploitable weaknesses and internet-connected OT assets still exist at meaningful levels. That means utilities need controls and testing approaches that fit operational realities rather than simply copying IT playbooks.
What is the difference between IT and OT cybersecurity in utilities?
IT cybersecurity focuses heavily on confidentiality, user productivity, and enterprise data protection. OT cybersecurity has to account for process continuity, engineering workflows, safety, and the physical consequences of disruption. Fortinet’s survey is useful here: 24% of respondents in its 2026 edition said intrusions affected both IT and OT (60% in 2025), showing that the boundary still matters even as the environments converge.
How do cloud, APIs, and IoT affect energy cybersecurity?
They expand the number of externally reachable workflows attached to utility operations. Customer portals, billing systems, AMI integrations, DER management tools, outage applications, and supplier workflows increasingly rely on cloud and API infrastructure. Akamai’s API attack volume and IBM’s multi-environment breach findings show why these technologies now belong inside energy-cybersecurity planning rather than beside it.
What cybersecurity frameworks apply to energy and utilities?
In the United States, NERC CIP applies to parts of the bulk electric system, TSA directives apply to covered pipelines, and EPA oversight has become more active in water. NIST SP 800-82 is a key reference for OT security, while CISA’s Cross-Sector Cybersecurity Performance Goals provide a practical baseline across critical infrastructure. In the EU, NIS2 extends cybersecurity obligations across sectors including energy, drinking water, and wastewater.
How should CISOs use energy cybersecurity statistics?
Use them to shape prioritization, not to replace diagnosis. Good statistics help justify asset visibility work, supplier-access reform, DDoS resilience, segmentation validation, application and API testing, cloud review, restoration testing, and executive reporting. They are most useful when tied to a clear scope statement and a change in control coverage or testing cadence.
How often should energy and utility organizations test security controls?
There is no universal annual number that safely fits every utility. Testing cadence should follow change rate and exposure: internet-facing portals and APIs need more frequent validation than static back-office systems, and OT-adjacent testing must be carefully scoped with operations. High-risk environments benefit from a layered cadence of vulnerability review, external testing, cloud and API testing, tabletop exercises, and periodic objective-based red-team work.
What is NERC CIP?
NERC CIP (Critical Infrastructure Protection) is the set of mandatory cybersecurity Reliability Standards for the North American bulk electric system, enforced by NERC and FERC in the United States. Standards CIP-002 through CIP-014 cover asset categorization, security perimeters, access control, incident response, recovery and supply-chain risk. In June 2025 FERC Order No. 907 approved CIP-015-1, which adds internal network security monitoring for high- and medium-impact BES Cyber Systems.
What are the biggest cyberattacks on the power grid?
The most cited cases are the December 2015 Ukraine attack, which cut power to about 225,000 customers; the 2016 Industroyer (CrashOverride) attack in Ukraine; the May 2021 Colonial Pipeline ransomware incident; Sandworm’s October 2022 substation attack in Ukraine; the Volt Typhoon pre-positioning disclosed by CISA in February 2024; and the December 2025 attack on more than 30 wind and solar farms and a CHP plant in Poland.
Where does energy rank among the most attacked industries?
IBM’s 2026 X-Force Threat Intelligence Index ranked energy as the fourth most attacked industry, accounting for 8% of the incidents X-Force responded to in 2025. Exploitation of public-facing applications was the initial access vector in half of those energy cases.
The strongest energy and utilities cybersecurity statistics point to a practical conclusion. Utility cyber risk is not concentrated in one threat class. It sits across ransomware, DDoS, OT/ICS and SCADA exposure, power-grid and service-availability risk, cloud and API dependencies, IoT and smart-grid expansion, and third-party access to critical environments. The best current data also shows that utilities-specific breach activity, industrial ransomware pressure, supplier-driven exposure, and internet-facing attack volume all remain material in 2026.
That is why energy and utilities cybersecurity statistics should guide security validation, not replace it. Organizations can use these findings to prioritize validation across internet-facing assets, cloud environments, APIs, customer portals, identity systems, network infrastructure, and safely scoped OT-adjacent environments. DeepStrike helps teams validate real-world exposure through penetration testing, API penetration testing, cloud penetration testing, network testing, red team assessments, remediation tracking, and retesting support.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
