August 8, 2025
Updated: November 5, 2026
The latest cybersecurity skills gap statistics from ISC2, IBM, WEF and ISACA: skills shortages, unfilled roles, breach costs, and the real reasons behind the shortage.

Mohammed Khalil
We're facing a strange paradox in cybersecurity. ISC2's 2024 study put the global workforce at 5.5 million professionals, up just 0.1% on 2023, while the gap, the shortfall between the defenders available and those needed, reached 4.8 million unfilled roles. That was the last gap estimate ISC2 published: its 2025 study stopped counting the headcount gap and measured skills instead, finding that 59% of organizations now have critical or significant skills needs.
So, what gives?
The cybersecurity talent shortage is no longer a simple pipeline issue. It has morphed into a complex, multifaceted crisis driven by a perfect storm of factors. It's a raw headcount deficit, a critical mismatch of modern skills, and a resource crisis fueled by economic headwinds that are forcing budget cuts and hiring freezes even as threats escalate.
Broader cybersecurity statistics reinforce the stakes. In ISC2's 2024 study, 74% of security professionals called the threat landscape the most challenging in five years, and IBM's 2026 report puts the average cost of a data breach at a record $4.99 million. This cyber workforce gap is a direct threat to business survival. This isn't just an HR problem to solve; it's a strategic risk that demands an immediate and intelligent response.
Yes, cybersecurity is in demand, though unevenly. The U.S. Bureau of Labor Statistics projects 21% job growth for information security analysts from 2025 to 2035, and CyberSeek counted 514,359 U.S. cybersecurity job listings in its latest year. Experienced cloud, AI and engineering talent is hardest to hire; entry-level roles are more competitive.
That answer can look odd next to the budget cuts and hiring freezes described later in this article. Both things are true at once: long-term demand for security work keeps rising, while short-term hiring depends on budgets. Three sources measure different parts of the picture, and each is worth reading on its own terms.
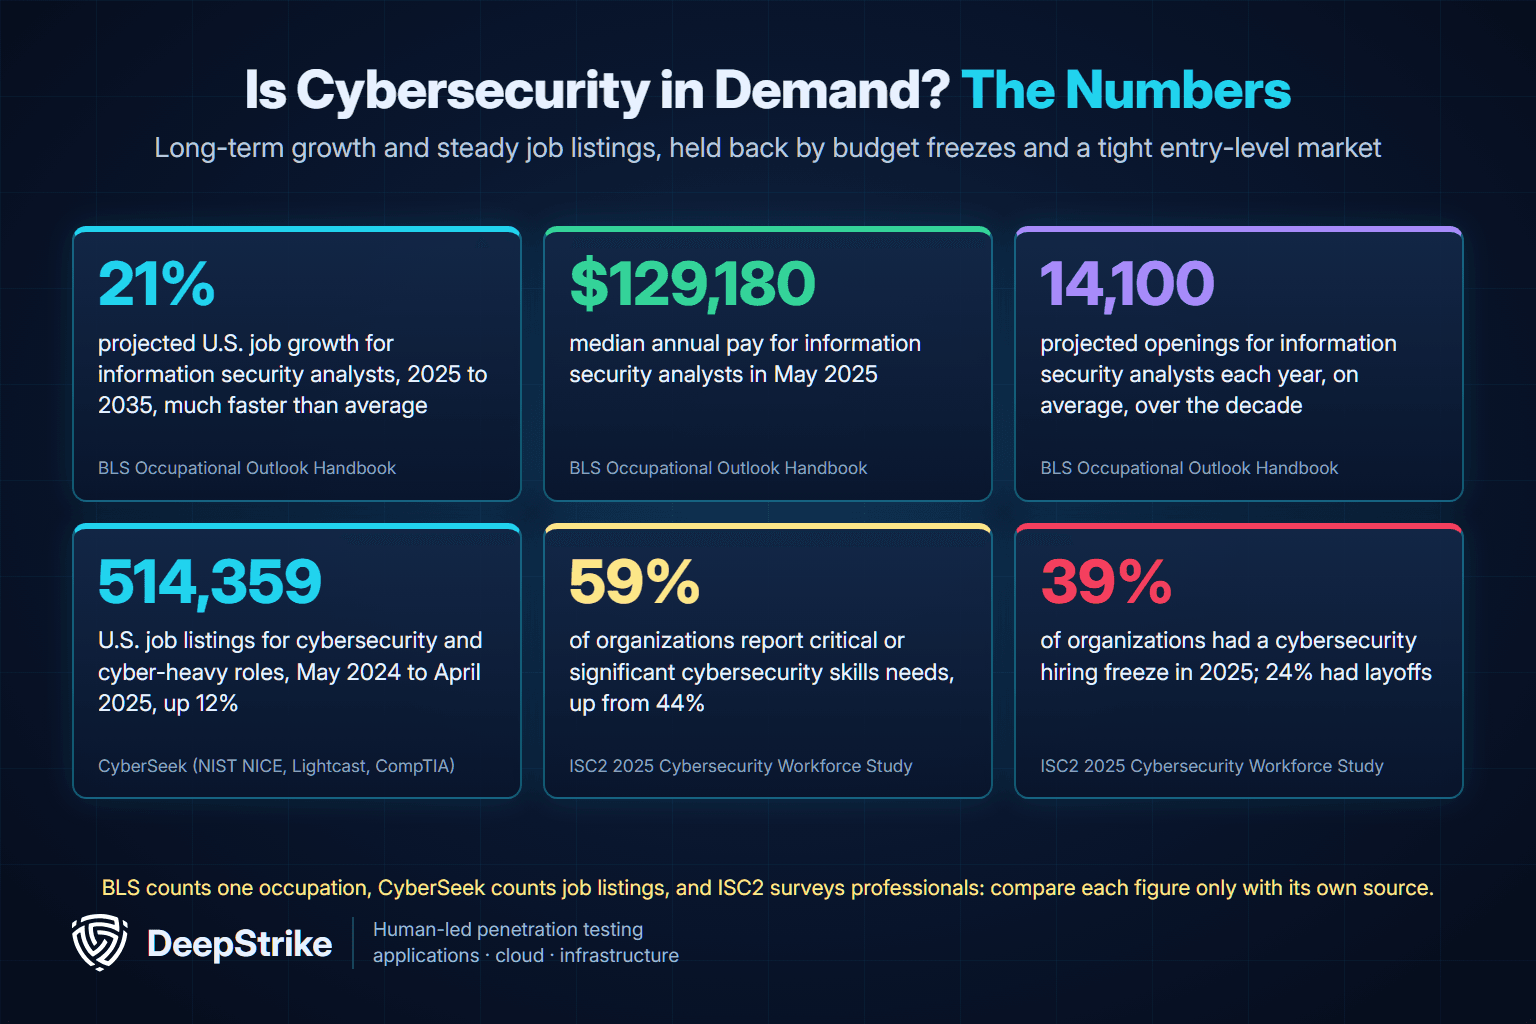
The BLS Occupational Outlook Handbook is the standard U.S. government source for the question, and it covers one occupation: information security analysts. In its current edition, analysts held about 192,900 jobs in 2025. BLS projects employment to grow 21% from 2025 to 2035, "much faster than the average for all occupations", adding about 40,600 jobs. It also expects about 14,100 openings a year on average, many of them created when workers retire or move to other occupations.
Pay reflects that demand. The median annual wage for information security analysts was $129,180 in May 2025. The lowest 10% earned less than $75,090 and the highest 10% more than $199,850. Median pay also varies by industry:
| Industry | Median annual wage, May 2025 |
|---|---|
| Information | $138,650 |
| Computer systems design and related services | $132,410 |
| Finance and insurance | $130,630 |
| Management of companies and enterprises | $128,950 |
| Management, scientific, and technical consulting services | $125,420 |
Source for the table: BLS Occupational Outlook Handbook, information security analysts. Higher growth rates that still circulate online, such as 29% for 2024 to 2034 or 32% for 2022 to 2032, come from earlier BLS projection cycles. The current 21% rate is lower, but BLS still classes it as much faster than average. BLS also notes that the role typically needs a bachelor's degree plus related work experience, which is one reason demand does not translate directly into entry-level vacancies.
CyberSeek, a joint project of NIST's NICE program, Lightcast and CompTIA, counts online job listings rather than one occupation. Its June 2025 update found employers posted 514,359 listings for dedicated cybersecurity jobs and technical roles with heavy cybersecurity requirements between May 2024 and April 2025. That was an increase of nearly 57,000 listings, or 12%, over the slower hiring period before it.
The same release adds detail that the headline number hides:
Treat listings as a measure of recruiting activity, not a count of unique or filled vacancies. Some listings are also for IT jobs where security is only part of the work.
The ISC2 2025 Cybersecurity Workforce Study, published in December 2025 from a survey of 16,029 professionals, looks at demand from inside security teams. ISC2 did not publish a workforce gap estimate this year. It measured skills needs instead: 95% of organizations have at least one, and 59% describe theirs as critical or significant.
The study shows what hiring managers are actually looking for. Their top technical priorities are cloud security (29%), AI (27%), security engineering (24%), security analysis (23%) and risk assessment (23%). Professionals themselves see AI (44%) and cloud security (40%) as the most in-demand skills. On the nontechnical side, managers prioritize problem-solving (29%), collaboration (24%) and communication (22%).
The same survey explains why demand does not always mean easy hiring. Thirty-nine percent of organizations had a hiring freeze and 24% had layoffs in 2025, and 26% expect more layoffs in the next 12 months. Even so, 87% of respondents believe there will always be a need for cybersecurity professionals, and 66% would recommend the field to young people.
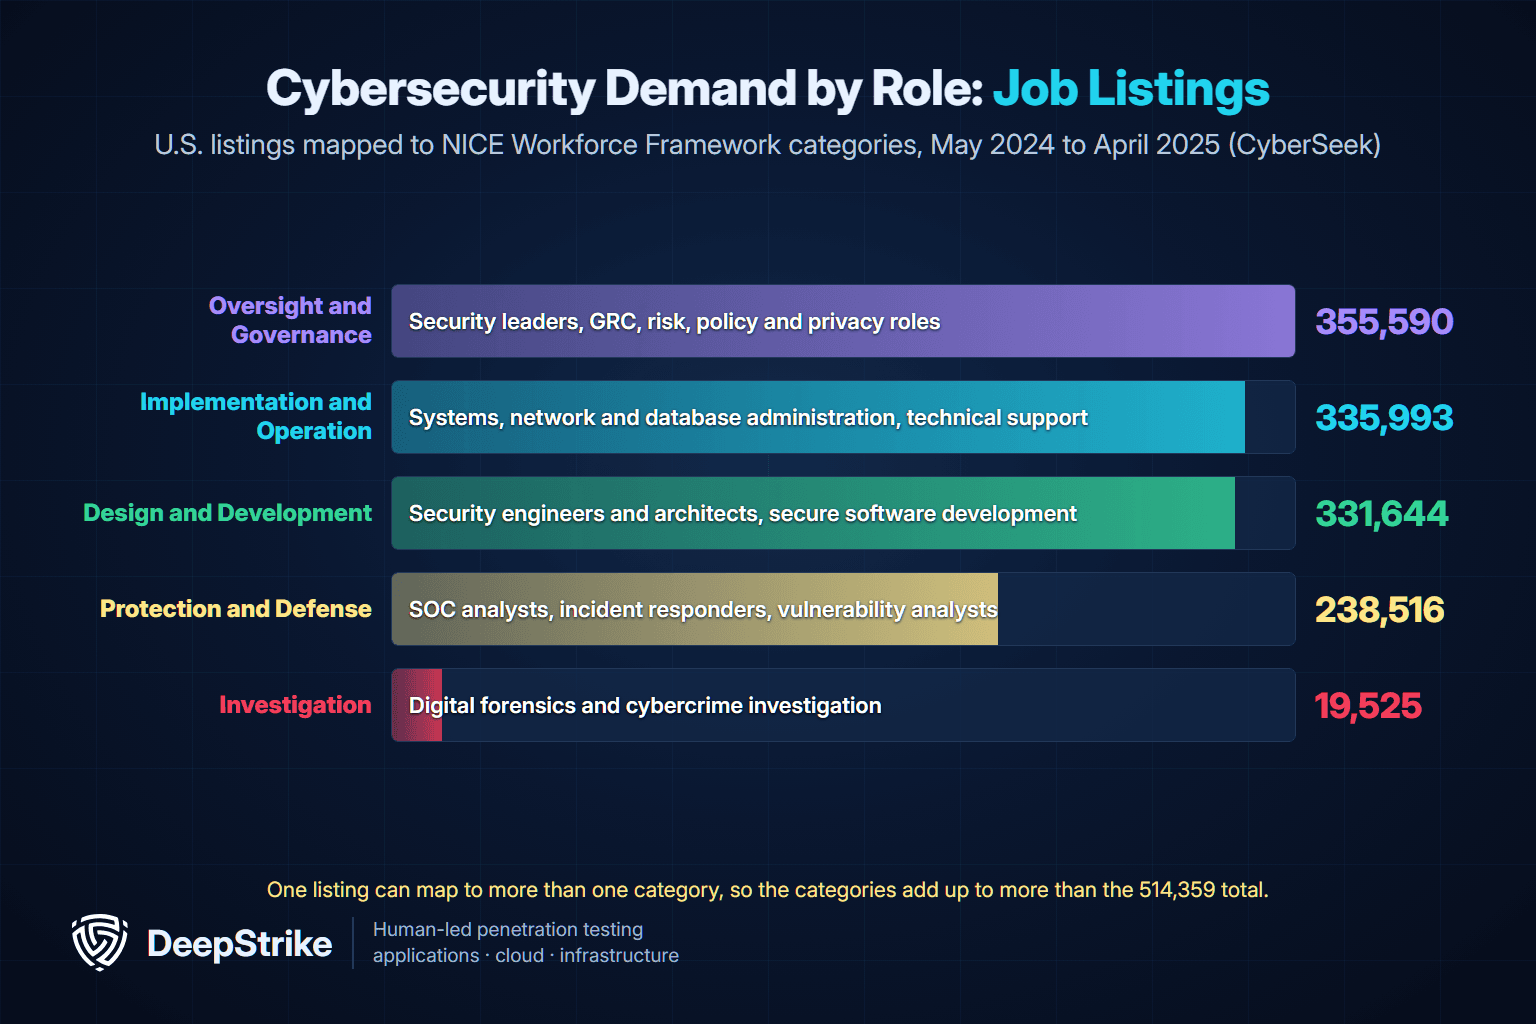
CyberSeek maps each listing to the categories of the NICE Workforce Framework for Cybersecurity, which gives the clearest public view of demand by role. A listing can fall into more than one category, so the rows add up to more than the 514,359 total.
| NICE Framework category | U.S. job listings, May 2024 to April 2025 | Example roles |
|---|---|---|
| Oversight and Governance | 355,590 | Security managers and CISOs, GRC and risk analysts, policy and privacy roles |
| Implementation and Operation | 335,993 | Systems, network and database administrators, technical support specialists |
| Design and Development | 331,644 | Security engineers and architects, secure software developers |
| Protection and Defense | 238,516 | SOC analysts, incident responders, threat analysts, vulnerability analysts |
| Investigation | 19,525 | Digital forensics analysts, cybercrime investigators |
Source for the table: CyberSeek data as published by NIST NICE, June 2025. Example roles follow the NICE Framework work roles in each category.
Read together with the ISC2 findings, the data points to four areas of particularly strong demand:
For job seekers, the takeaway is that demand rewards demonstrable skills more than titles. ISC2 found that IT experience is the most common route into the field (56% of respondents), and the cybersecurity certifications employers request most often are a practical way to show readiness. For employers, the same numbers explain why the skills gap persists: the roles that are hardest to fill are the ones that take years to grow internally.
For years, we've talked about the skills gap as a pipeline issue. That's still true, but it misses the bigger picture of what's happening now. The very nature of the gap has changed. It’s deeper, more nuanced, and driven by forces both inside and outside our organizations.
Let’s start with the hard numbers. The ISC2 2024 Cybersecurity Workforce Study, the last edition to publish a gap estimate, put global demand for cybersecurity professionals at 10.2 million. With a workforce of 5.5 million, that left a gap of 4.76 million, up 19%. The ISC2 2025 study (December 2025) dropped the headcount estimate and found that 95% of organizations have at least one skills need and 59% have critical or significant needs. The problem is that demand is accelerating far faster than our ability to train and absorb new talent.
Economic pressure slammed the brakes on hiring. In 2024, some regions like the Middle East, Africa, and Asia Pacific saw modest workforce growth, while North America and Europe saw reductions. This slowdown, combined with ever increasing need, widened the gap.
Even if you could magically fill every open role tomorrow, you’d still have a problem. A huge part of the skills gap is qualitative, not just quantitative. Many security teams are functionally unprepared for modern threats because they lack the right expertise.
A fully staffed team can still miss critical cloud misconfigurations if no one has cloud security expertise.
ISC2's 2025 study found that AI is now the most pressing skills need (41%), followed by cloud security (36%). Its 2024 first-look findings listed the top skills gaps as:
Interestingly, while these technical skills are desperately needed, hiring managers are also increasingly prioritizing nontechnical skills like problem-solving, critical thinking, and communication. This suggests a growing recognition that while technology like AI will automate some tasks, human ingenuity is irreplaceable for managing the tools and guiding the overall strategy.
The biggest shift came in ISC2's 2024 study: for the first time, the leading cause of staff shortages was not an inability to find qualified people. It was a lack of money.
The 2024 study found that lack of budget was the top reason for both staff shortages (39%) and skills gaps (33%). In 2024, organizations reported significant resource reductions:
Those pressures barely eased in 2025: 36% of organizations faced budget cuts, 24% layoffs and 39% hiring freezes, and 88% had experienced at least one significant cybersecurity consequence linked to skills shortages (ISC2 2025).
This has created a dangerous situation where the need for defenders has never been greater, yet companies are actively cutting back on the resources required to hire and train them. The skills gap has evolved from a talent pipeline problem into a direct reflection of an organization's financial health and risk tolerance.
This isn't an abstract problem for boardrooms to debate. The skills gap has tangible, painful consequences that show up in breach reports, operational downtime, and on the bottom line.
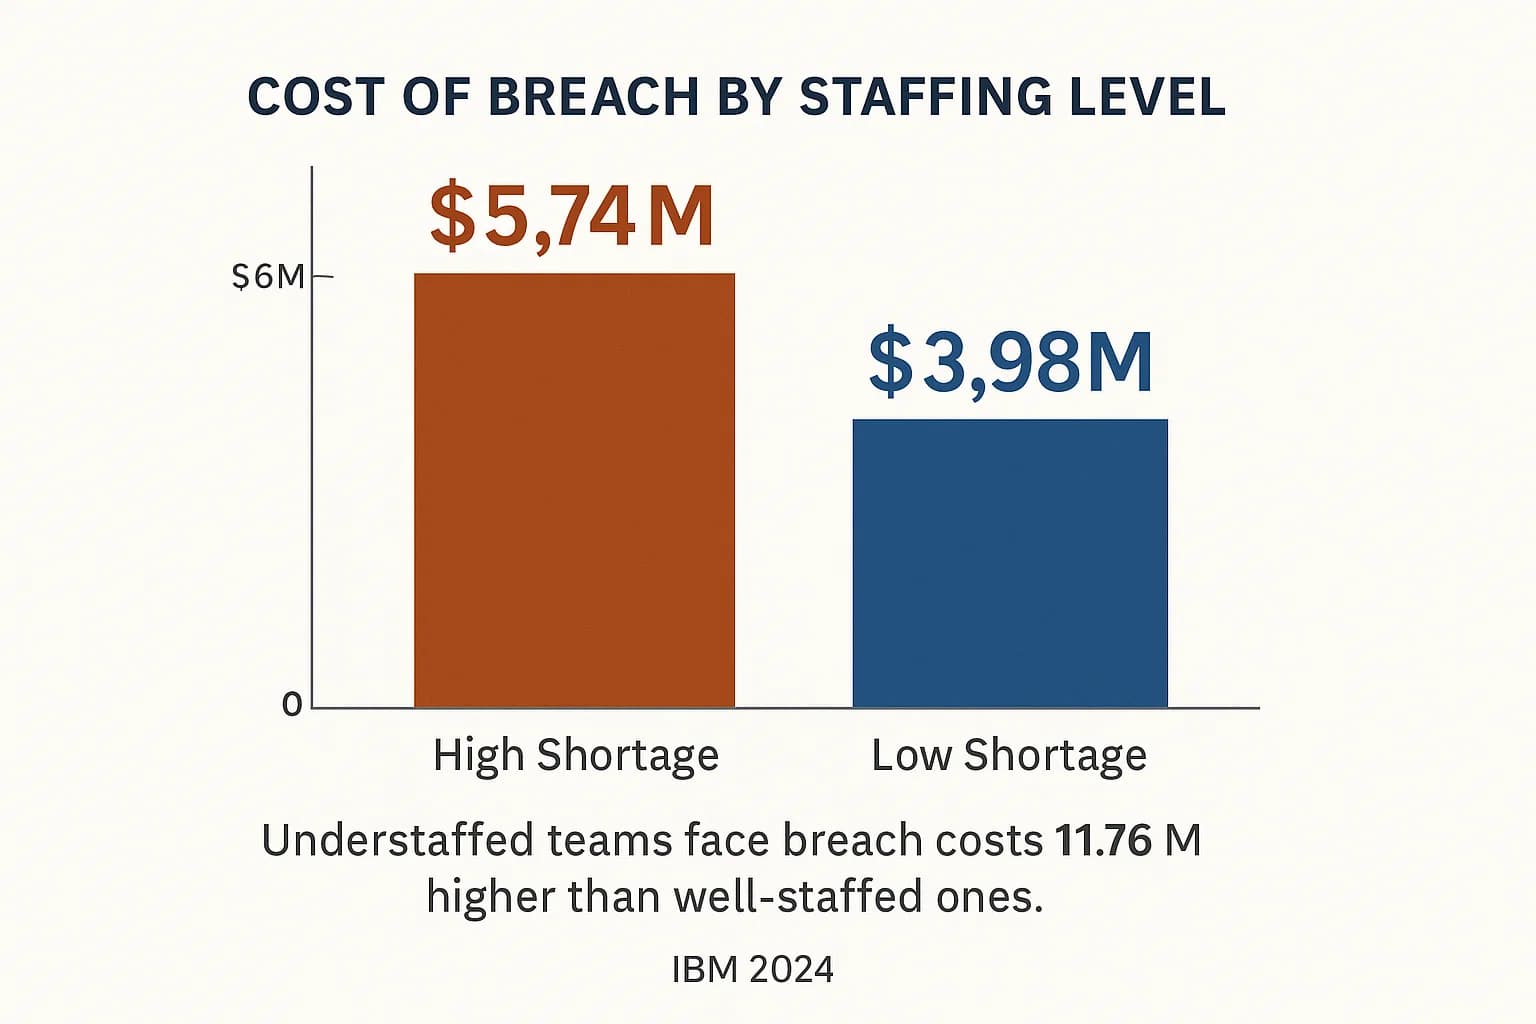
The numbers don't lie. IBM's 2024 Cost of a Data Breach Report put the global average cost of a breach at $4.88 million, a 10% jump in one year, and its 2026 report puts it at a record $4.99 million.
Here is the most critical connection: in IBM's 2024 report, organizations with a high-level security skills shortage saw average breach costs of $5.74 million, against $3.98 million for those with a low-level shortage or none, a $1.76 million difference. In its 2026 data, IBM puts the average for organizations with a high-level shortage at $5.17 million.
Why? Because understaffed teams are overwhelmed. They can't monitor alerts effectively, patch systems quickly, or respond to incidents fast enough. This gives attackers more time inside a network, known as "dwell time", to find valuable data and do more damage. In IBM's 2024 study, breaches involving stolen credentials took the longest to identify and contain, at 292 days on average.
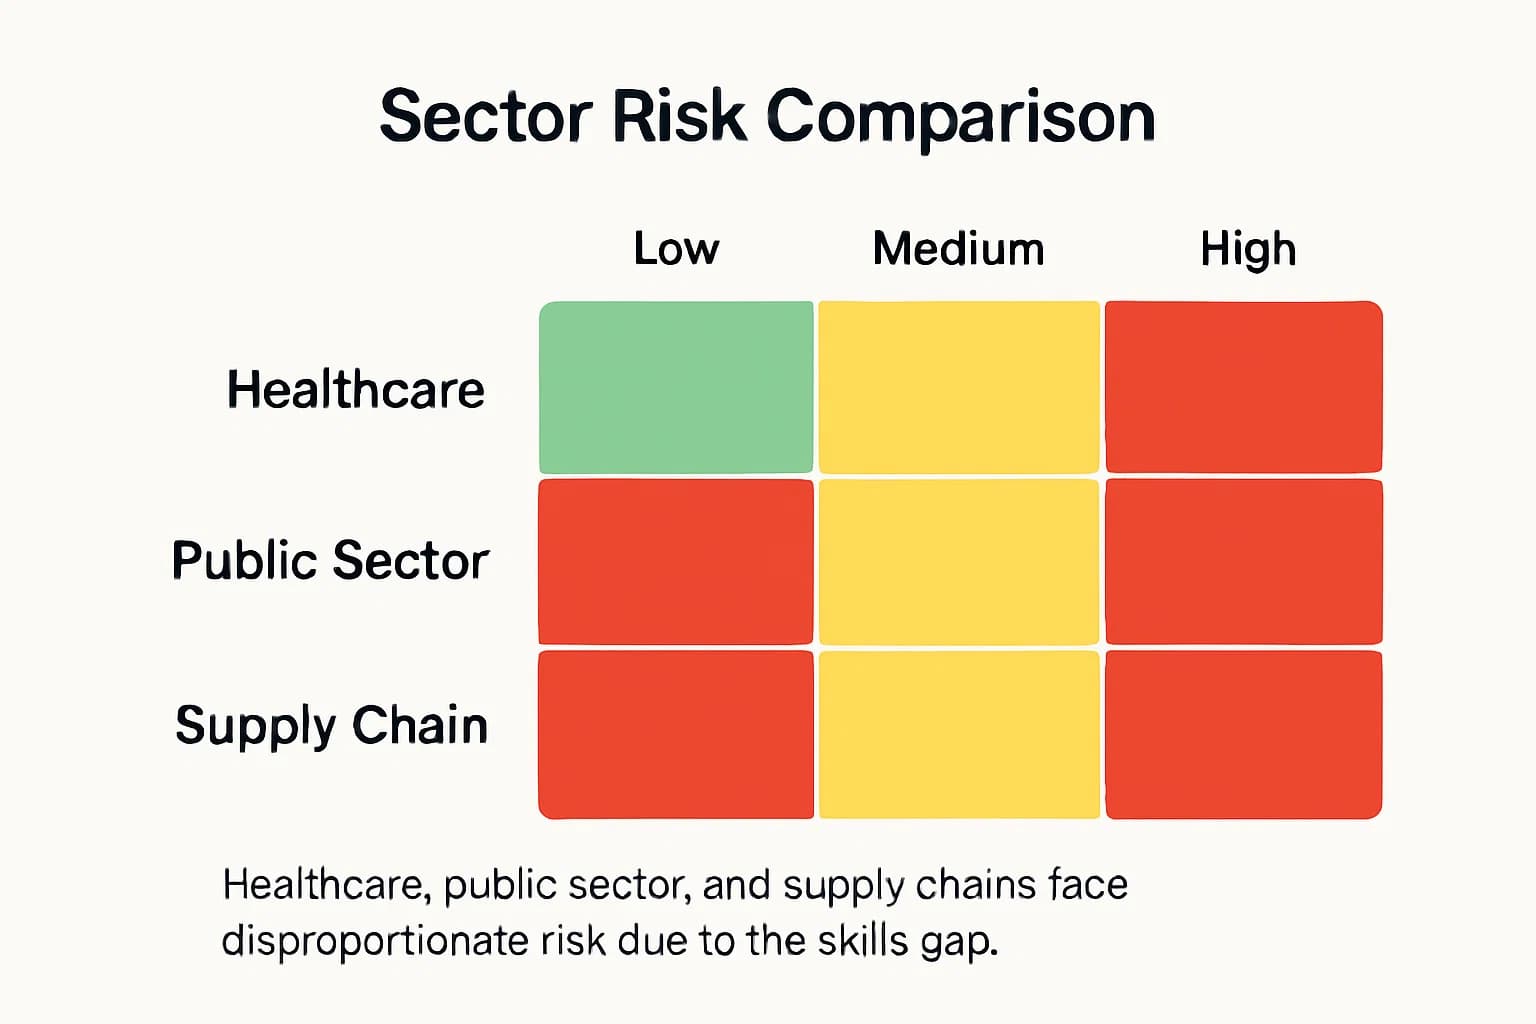
While every industry feels the pain, the skills gap is a potential catastrophe for the sectors we rely on most.
Case Insight: Healthcare on High Alert
The healthcare sector is a perfect storm of high value data, interconnected legacy systems, and chronically underfunded IT departments. Here, the skills gap doesn't just lead to financial loss; it can disrupt patient care and put lives at risk. The industry has the highest data breach costs of any sector: $9.77 million per incident in IBM's 2024 report and $6.64 million in 2026, still the highest for the 15th consecutive year.
The massive events of 2024 and 2025, such as the Change Healthcare attack affecting over 192 million people, serve as a terrifying illustration. While reports don't explicitly name the skills gap as the cause, these are textbook examples of what happens when a highly targeted industry is overwhelmed. A lack of skilled personnel to manage complex systems and respond to sophisticated threats undoubtedly makes such catastrophic breaches more likely.
The Public Sector and Supply Chain Under Strain
The public sector is another area of major concern. The World Economic Forum's 2025 Global Cybersecurity Outlook reported that 49% of public sector organizations lacked the necessary talent to meet their security goals, a 33% increase from 2024. In the 2026 edition, lack of expertise was the second-biggest challenge for the public sector (57%), and 46% of small organizations reported a lack of cybersecurity skills, against 29% of large ones.
This risk is amplified by our reliance on complex digital supply chains. In its 2025 Global Cybersecurity Outlook, the WEF reported that 54% of large organizations saw supply chain challenges as the biggest barrier to cyber resilience. Your internal team can be world class, but if you lack the skilled personnel to properly vet your third party vendors, you inherit all of their vulnerabilities.
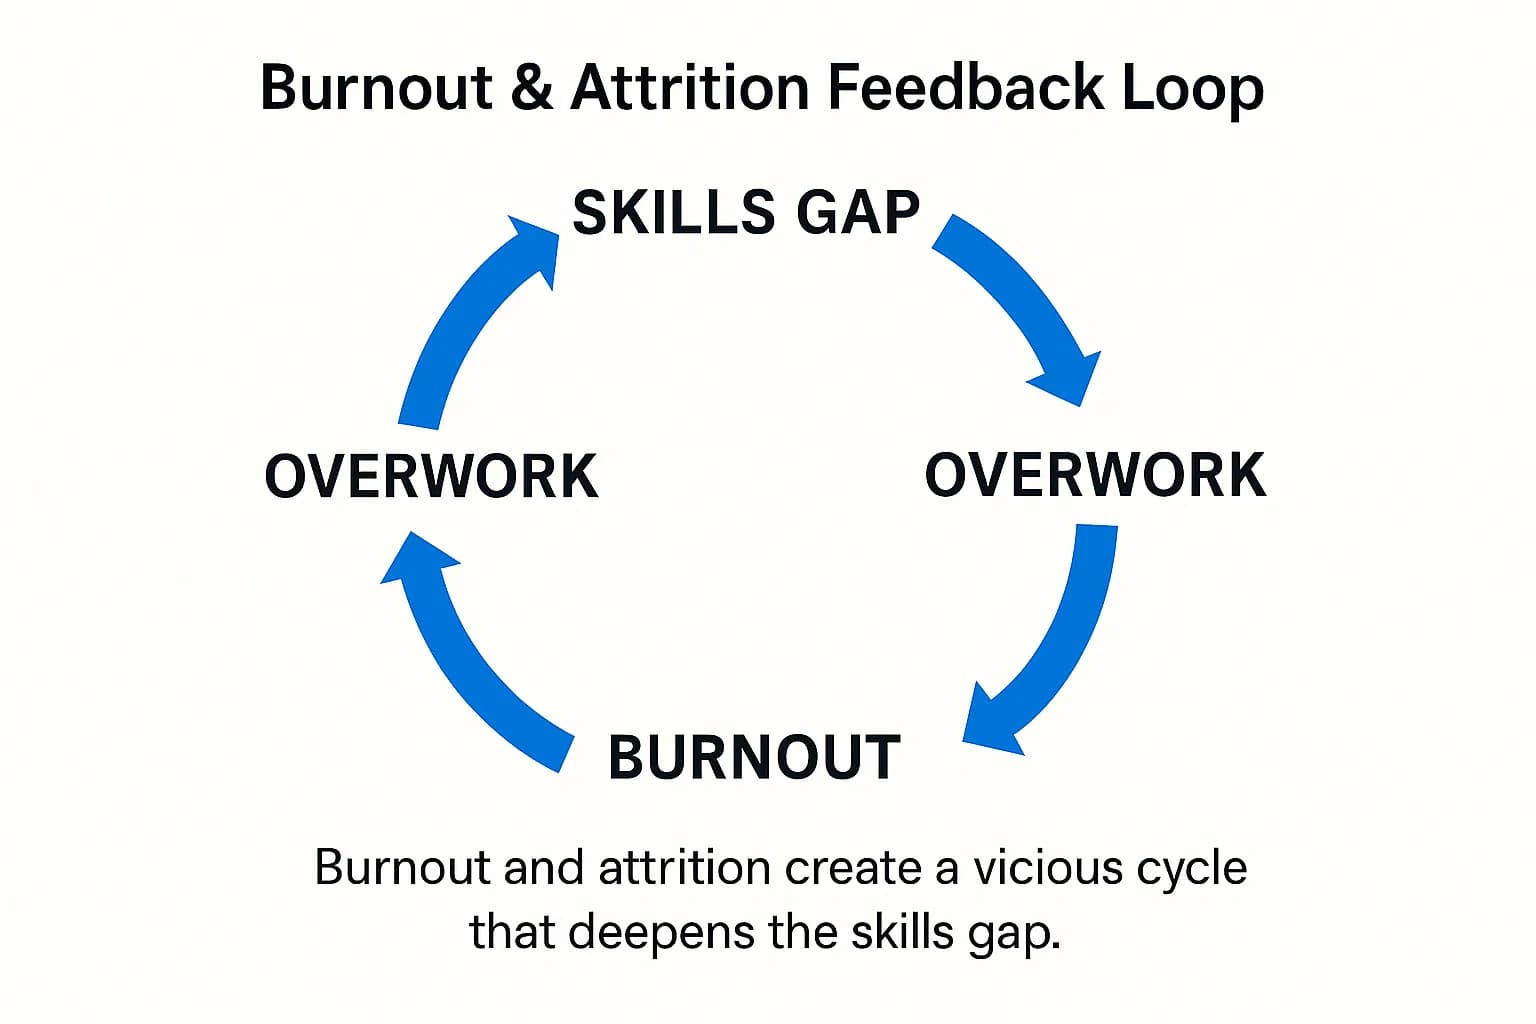
The skills gap isn't just about a failure to hire new people. It's also about a systemic failure to keep the talented professionals we already have.
The cybersecurity profession is in the middle of a burnout epidemic. Gartner predicted in 2023 that nearly half of all cybersecurity leaders would change jobs by 2025, a quarter of them for different roles entirely, due to work-related stress. ISACA's 2025 research backs this up: 66% of professionals say their role is more stressful now than five years ago, and high stress was the top reason for leaving (47%). ISACA's State of Cybersecurity 2026 (September 2026) shows the pressure rising: 68% say their role has become more stressful over the past five years, and high work stress is now the leading reason people leave (52%), followed by limited promotion and development opportunities (47%).
In ISACA’s 2024 report, the top reasons people left their jobs were:
This creates a vicious cycle: the skills gap increases the workload, which causes burnout, which leads to high turnover, which widens the skills gap even further.
Organizations often shoot themselves in the foot with flawed hiring practices. There's a major disconnect between the skills employers say they want and what their job descriptions demand. Many job postings for entry-level roles still demand multiple advanced certifications and unrealistic years of experience.
Candidates may use writing tools such as UndetectedGPT to revise application drafts, but polished wording should not substitute for evidence of ability. Employers should assess practical cybersecurity skills through relevant work samples and structured interviews.
This gatekeeping chokes the talent pipeline. ISC2's 2024 study found that nearly one third (31%) of security teams have zero entry-level professionals. This is a systemic failure to invest in growing talent. The talent pool also remains under diversified: ISC2 research found women make up 22% of security teams on average, indicating we’re not tapping all potential talent.
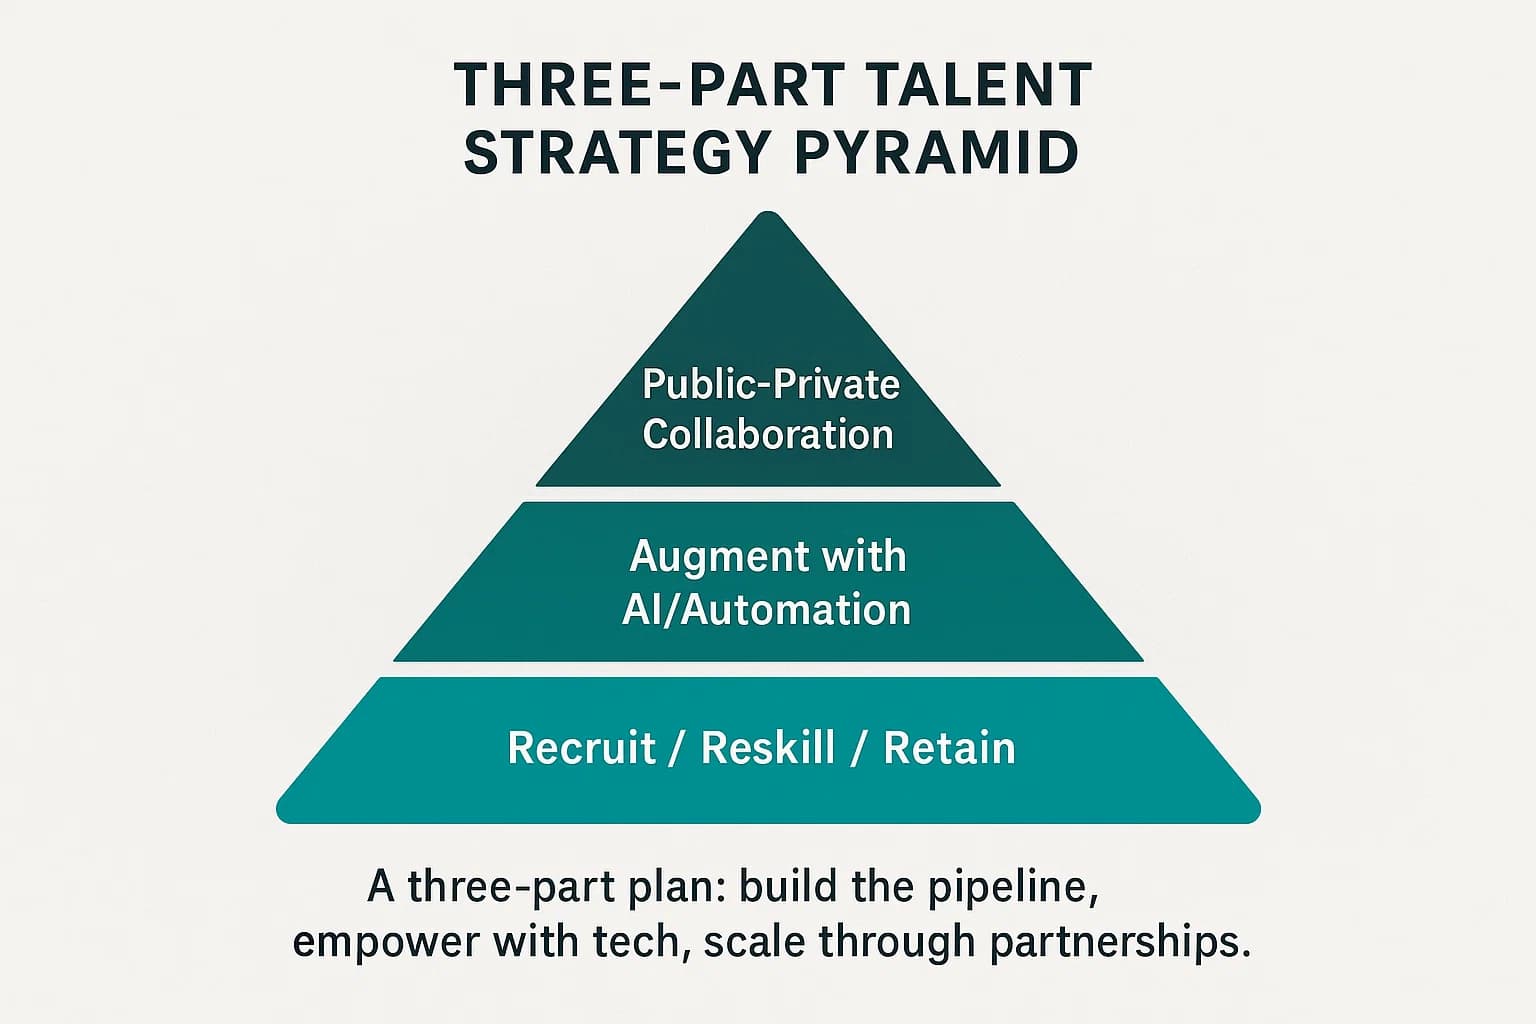
Solving this crisis requires a fundamental shift in strategy. We need to move beyond just trying to "hire more people" and adopt a holistic approach that builds resilience from the inside out.
It all starts with people. If you can't find them, build them. If you have them, keep them.
Organizations considering offshore staffing solutions should assess candidates’ role-specific skills and establish clear supervision and data-access controls before assigning security-sensitive work.
Embrace Apprenticeships and "New Collar" Talent
The traditional four year degree is no longer the only path into cybersecurity. Forward thinking organizations are embracing "new collar" talent and apprenticeship models. In the UK, programs from the Civil Service and Santander provide excellent apprenticeships. In the U.S., companies like IBM, Boeing, and Accenture are leading the way with their own programs that focus on hands-on skills.
Invest in Upskilling and Certifications
Investing in your team's professional development is one of the most powerful retention tools you have. It directly addresses a key reason people leave: a lack of growth opportunities. A cyber security course can also provide a structured way for professionals to strengthen relevant security skills. The good news is that ISC2's 2025 hiring research found that 89% of hiring managers would consider candidates with only entry-level cybersecurity certifications, so certifications are a credible on-ramp. Funding them is a smart investment, especially for roles where internal context is invaluable. Purple teaming exercises, where offensive and defensive staff work through the same attack scenarios together, also build practical skills on both sides.
Build a Culture That Keeps People
You can’t solve a burnout problem with pizza parties. You need to address the root causes of stress. The most resilient organizations treat their security team's well-being as a core component of their defense strategy: realistic on-call rotations, automation of repetitive alert triage, and clear paths for growth. This reframes employee well-being from a "soft" perk into a hard-nosed business continuity strategy.
With teams stretched thin, technology must become a force multiplier.
Using AI as a Force Multiplier, Not a Replacement
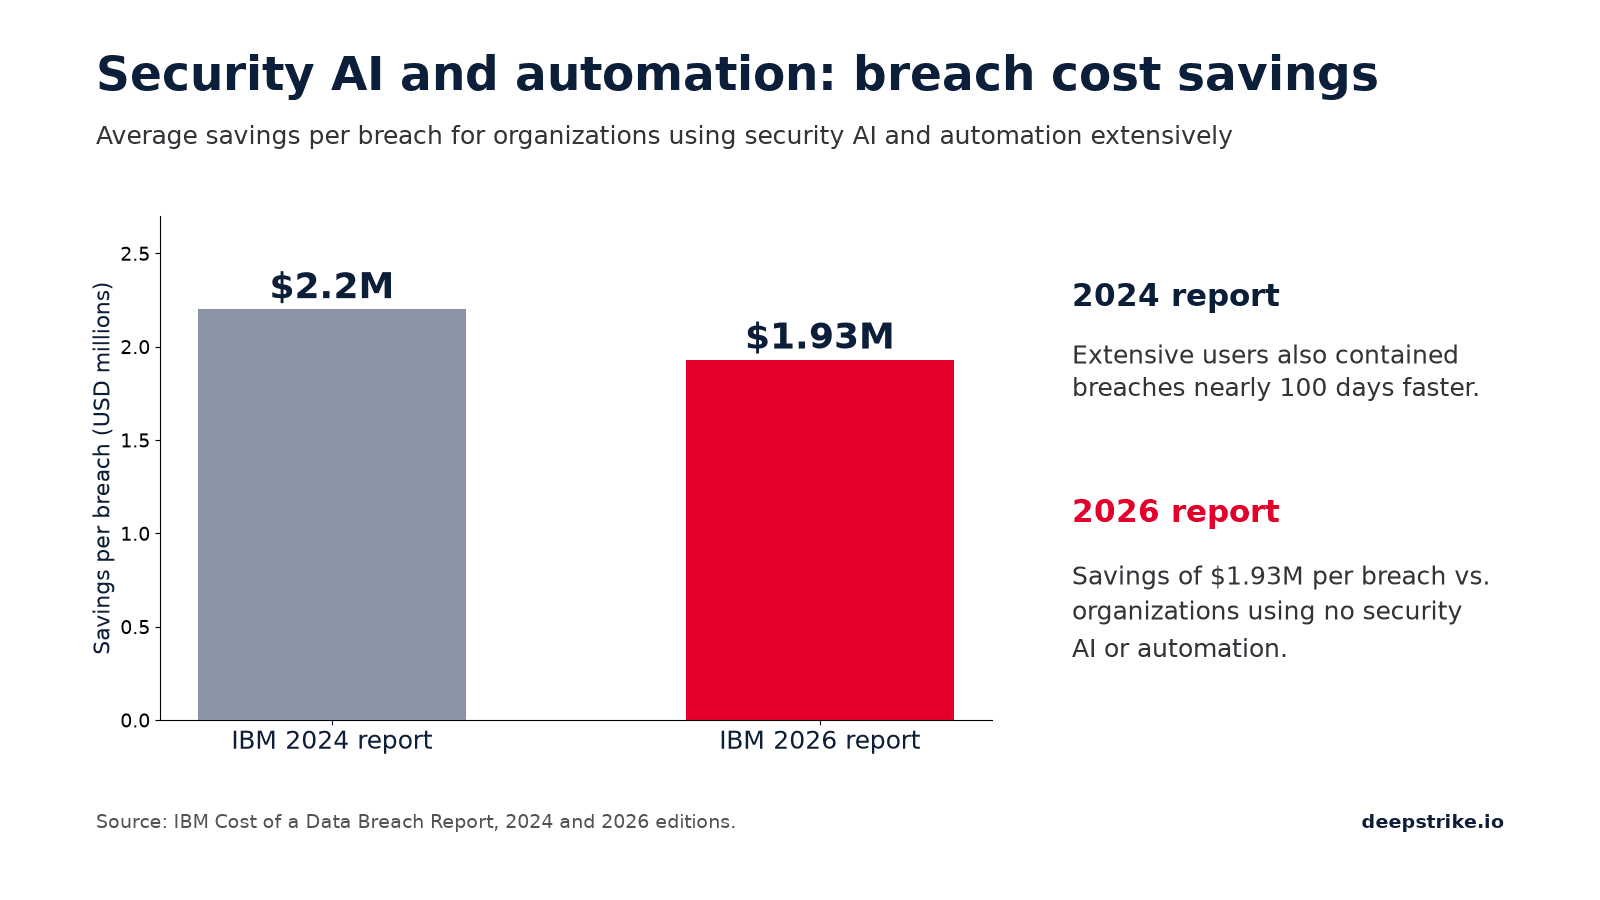
IBM's 2026 report found that organizations making extensive use of security AI and automation saved an average of $1.93 million per breach (the figure was $2.2 million in 2024, when IBM also found they contained breaches nearly 100 days faster). The key is to use AI tactically to handle high-volume tasks, freeing up your human analysts for high-value work like threat hunting and analyzing sophisticated intrusions.
Consolidate and Optimize Your Toolset
Tool sprawl is a silent killer of productivity. Many enterprises run dozens of separate security tools, each with its own alerts and consoles. The solution isn't just to cut vendors but to shift toward tool optimization. A platform approach, like using a unified security platform, can provide more value than a dozen disconnected point solutions.
Finally, we need to scale these solutions by adopting standardized approaches and working together.
A Blueprint for Your Workforce: Implementing the NICE Framework
You don't have to reinvent the wheel. The Workforce Framework for Cybersecurity (NICE Framework), published as NIST SP 800-181 Rev. 1, provides a free, comprehensive blueprint for workforce planning. It establishes a common language for defining job roles, conducting skills assessments, and designing targeted training programs.
The Power of Collaboration
No single company can solve a 4.8 million person problem. Progress requires collective action. This includes supporting national-level efforts like CISA's 2024–2026 Cybersecurity Strategic Plan, which focuses on workforce development and proactive defense.
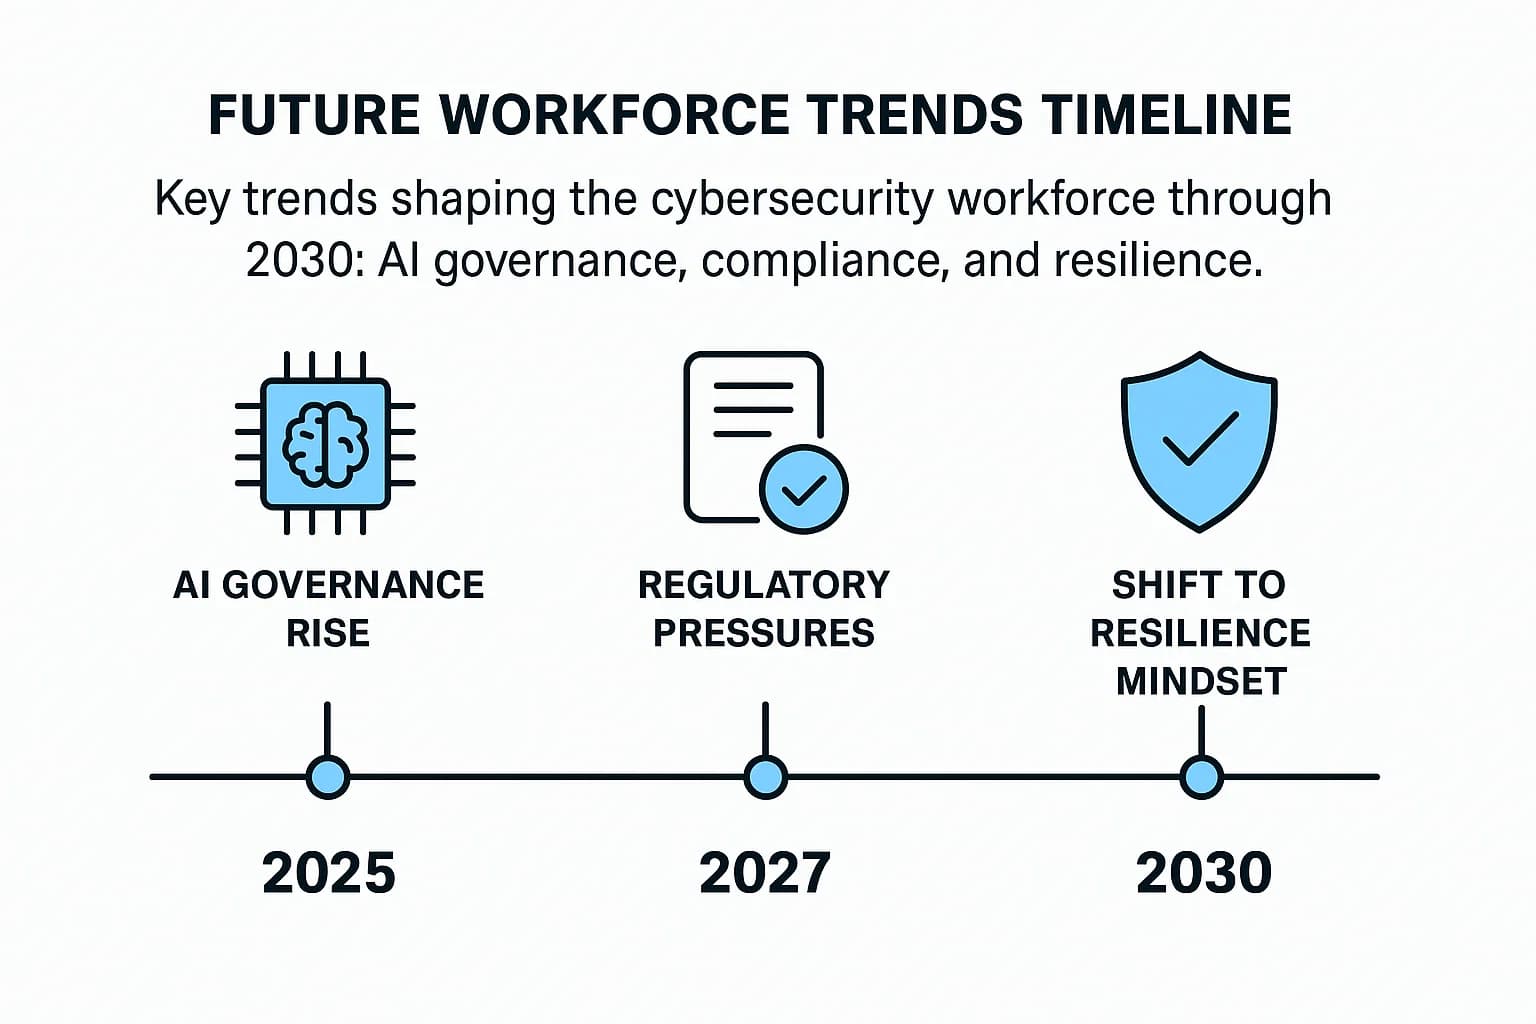
Looking ahead, the road is challenging but not without hope. The strategies being implemented today will shape the security landscape for the next decade.
In the near term, the gap will likely remain stubbornly wide. However, the massive global investment in education, apprenticeships, and reskilling programs is a long term play that should start to bend the curve by the late 2020s. The goal may not be to close the gap to zero but to manage it down to a sustainable level.
As this happens, the role of the cybersecurity professional will also evolve. With AI handling more routine tasks, the human expert will become more of a strategic risk advisor, a complex threat investigator, and an AI systems manager.
Three major trends will define the future of the cyber workforce:
What is the main cause of the cybersecurity skills gap today?
Money and skills, more than headcount. ISC2's 2024 study found lack of budget was the top cause of staff shortages (39%). In 2025, 36% of organizations still faced budget cuts and 39% hiring freezes, while 59% reported critical or significant skills needs, led by AI (41%) and cloud security (36%).
How does the skills gap affect a company's security?
It directly increases risk. ISC2's 2024 study found organizations with critical or significant skills gaps are almost twice as likely to suffer a material breach. IBM's 2024 report found breaches cost $1.76 million more at organizations with high-level skills shortages, and its 2026 data puts their average breach at $5.17 million.
What are the most in demand cybersecurity skills right now?
ISC2's 2025 study ranks AI (41%) and cloud security (36%) as the most pressing skills needs. Its 2024 first-look findings also highlighted zero trust implementation (27%), digital forensics and incident response (25%), and application security and penetration testing (24% each). Employers are also heavily prioritizing non technical skills like communication, critical thinking, and problem solving.
Is AI making the cybersecurity skills gap better or worse?
It's doing both. AI is now the biggest skills need itself (41% in ISC2's 2025 study), creating new demand for specialized talent. However, it's also a key solution: IBM's 2026 report found extensive use of security AI and automation cut breach costs by $1.93 million on average.
How can someone with no experience get into cybersecurity?
Focus on foundational knowledge and alternative pathways. Pursue entry-level certifications like (ISC)²'s Certified in Cybersecurity (CC) or CompTIA Security+. Look for apprenticeships and "new collar" jobs that value aptitude over a four-year degree. Build practical skills on platforms like TryHackMe or HackTheBox.
What are companies doing to solve the talent shortage?
Leading companies are investing in upskilling their current staff, funding certifications, creating apprenticeship programs, adopting AI and automation to augment their teams, and revising hiring practices to focus more on demonstrable skills.
Is the cybersecurity skills gap a myth?
No, it is not a myth. The last published estimate put the global workforce gap at 4.8 million (ISC2 2024), 58% of organizations said skills gaps put them at significant risk, 59% reported critical or significant skills needs in 2025, and IBM links high-level skills shortages to higher breach costs. The skills gap is a well-documented and critical business challenge.
Is cybersecurity a good career in 2026?
For most people with relevant skills, yes. BLS projects 21% growth for information security analysts from 2025 to 2035, with a $129,180 median wage in May 2025. ISC2's 2025 study found 68% job satisfaction and 66% of professionals would recommend the field. The trade-offs are real: 48% feel exhausted keeping up with threats, and entry-level hiring is competitive.
Which cybersecurity jobs are in highest demand?
By U.S. job listings, governance and risk roles lead (355,590 listings from May 2024 to April 2025), followed by implementation and operation (335,993) and security design and engineering (331,644), according to CyberSeek. ISC2's 2025 study shows hiring managers prioritize cloud security (29%), AI (27%) and security engineering (24%).
Today's cybersecurity skills gap is not a single problem but a perfect storm: a massive talent deficit, a critical capabilities mismatch, and a resource crisis fueled by economic pressures. The consequences are clear: higher risks, more expensive breaches, and a burnt out workforce.
Simply trying to "hire more people" is a failing strategy. The path forward requires a multi pronged, resilient approach. We must fix the broken talent pipeline with apprenticeships and skills based hiring, invest in the people we already have through continuous training and wellness programs, and strategically leverage technology like AI to make our human teams stronger, more efficient, and more effective.
Ready to Strengthen Your Defenses?
Today's threats demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services for businesses to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
About the Author
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
