June 26, 2025
Updated: November 5, 2026
How the U.S., China, UK, Germany, Japan and Australia invest in cyber defense, and how much companies spend by IT budget share, employee and industry.

Mohammed Khalil
Quick answer: Cybersecurity spending by country is led by the United States, which IDC expects to spend about $150 billion of a $308 billion global total in 2026, far ahead of any other nation. Gartner forecasts worldwide end-user spending on information security of about $240 billion in 2026, up 12.5%. At company level, security took 9.9% of IT budgets in the 2026 IANS and Artico Search benchmark, and small firms spend a far larger share. How well that money is spent matters more than the total.
Cybercrime has become a direct and escalating tax on global business. Cybersecurity Ventures projected that cybercrime costs would reach $10.5 trillion a year by 2025, comparing the total to the world's third largest economy after the U.S. and China; that is a modelled estimate, not a measured figure. The measured numbers are alarming enough: the FBI's Internet Crime Complaint Center received 1,008,597 complaints with $20.9 billion in reported losses in 2025, up from $16.6 billion in 2024. The sheer scale of this problem is detailed in our latest cyber crime statistics report.
In response, global cybersecurity spending by country and by enterprise keeps climbing. Gartner's latest public forecast (July 2025) puts worldwide end user spending on information security at $213 billion in 2025, up from $193 billion in 2024, and projects a 12.5% rise to $240 billion in 2026. A February 2026 Gartner update raised the 2026 estimate to about $244 billion (11.6% growth in constant currency). This surge is not optional; it's a fundamental reaction to a hyper evolving threat landscape.
Understanding these global spending dynamics is no longer a niche IT concern. It is a critical strategic imperative for CISOs, CFOs, and boards. This report moves beyond the headlines to dissect who is spending, why they are spending, and how they are allocating their budgets. We will analyze national priorities, uncover the key drivers forcing investment, and provide a framework for calculating the real return on your security spend. This is your guide to navigating the financial realities of cyber defense in 2026.
Viewed alongside broader cybersecurity statistics, the macroeconomic picture of cybersecurity spending reveals a market compelled into rapid, sustained growth. Faced with threats that are more automated, sophisticated, and widespread than ever before, nations and corporations are escalating their defensive investments. This section breaks down the top-line forecasts and spending patterns of the world's key economic powers.
Multiple top tier analyst firms project strong, double digit growth for the cybersecurity market, signaling a powerful and non negotiable investment cycle. While specific figures vary based on methodology such as tracking end user spending versus total market value the consensus points to a market that is not just growing, but accelerating.
Gartner and IDC measure different things, so their totals should not be added together or compared directly. Gartner tracks end user spending on security software, security services and network security: $213 billion in 2025 and a forecast $240 billion in 2026 (July 2025). IDC's Worldwide Security Spending Guide, which also counts security hardware, projects $308 billion in 2026 (+11.8%) and $430 billion by 2029 (March 2026); a later V2 release of the 2026 guide puts this year at $310.42 billion, up 13.2% from 2025. For reference, IDC's March 2025 forecast had called for 12.2% growth in 2025 and $377 billion by 2028.
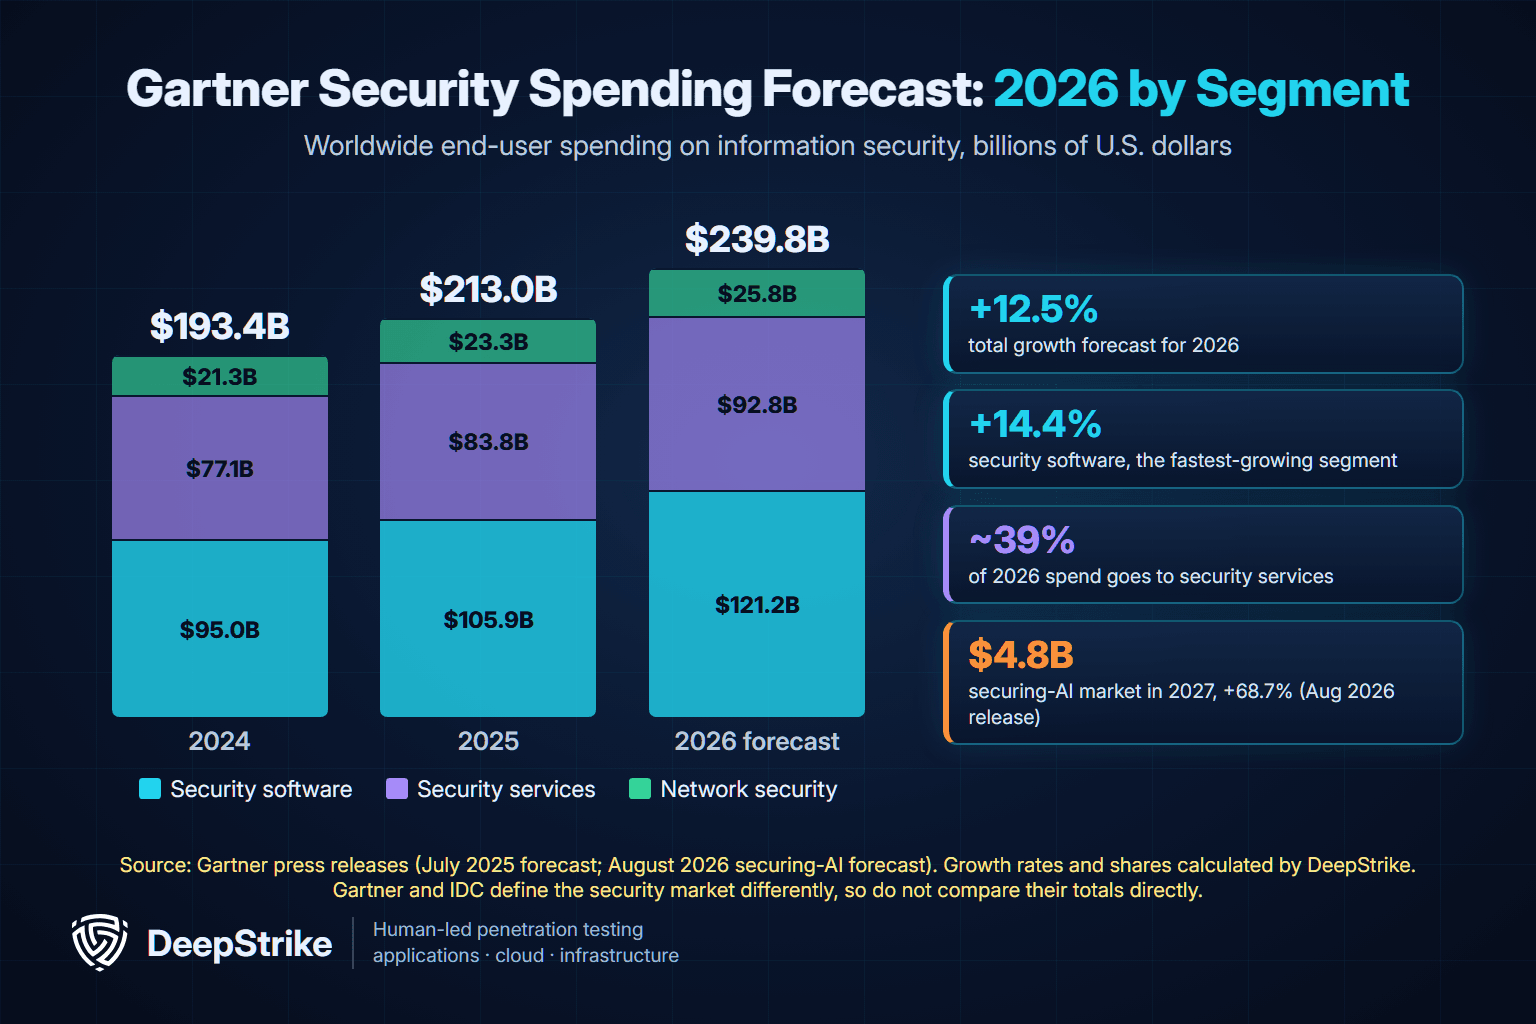
This spending is not uniform across all categories. In Gartner's forecast, security software remains the largest and fastest growing segment, rising from about $105.9 billion in 2025 to $121.2 billion in 2026 (+14.4%), while security services grow from $83.8 billion to $92.8 billion (+10.7%). This dual focus highlights a clear market strategy: organizations are acquiring advanced tools while outsourcing specialist capabilities such as penetration testing services to validate whether those investments reduce exploitable risk.
A significant portion of this growth is tied to AI. Gartner names the expanding use of AI and generative AI, by both internal users and attackers, as a key growth driver across its forecast period, and IDC expects cloud native application protection platforms (CNAPP), identity and access management and data security software to be the fastest growing software categories in 2026 as organizations secure AI workloads and non human identities.
While global spending is on the rise, the distribution and strategic priorities vary significantly from one nation to another. The country figures below come from different sources and measures (analyst market forecasts, government budgets and damage estimates), each labelled with its year, so read them as signals of scale and priority rather than a strict league table.
The spending data reveals a fascinating paradox. The United States leads in absolute spending by a massive margin, yet on readiness measures such as the National Cyber Security Index (NCSI) it ranks 29th, behind smaller nations such as Lithuania (6th) and Estonia (7th), while the UK sits 41st. This suggests that the way money is spent is more critical than the sheer amount. A smaller nation with a highly coordinated national strategy, strong public private partnerships, and an unwavering focus on foundational cyber hygiene can achieve greater resilience than a larger nation with a fragmented, tool heavy approach. This is a crucial lesson for CISOs: a bigger budget is not a silver bullet. Strategic allocation, process maturity, and investment in human factors are the real differentiators.
Most mid-sized and large companies spend roughly 8% to 12% of their IT budget on cybersecurity, and small companies often spend two to three times that share. The most recent benchmark, the 2026 IANS and Artico Search Security Budget Benchmark of more than 500 CISOs, puts security at 9.9% of IT spending, the same level as 2021. Measured against revenue, the 2025 edition of the same study found security averaged 0.69% of company revenue. Per employee, small and midmarket firms averaged about $3,800 in IANS data, while the widely quoted $2,700 figure comes from a 2020 survey of financial institutions.
Those three ratios measure different things, so use them together rather than picking one. Share of IT budget shows how security competes with other technology priorities. Share of revenue shows how it compares with the size of the business. Spend per employee scales with the number of people, identities and devices you have to protect. Every figure below carries its source, survey year and respondent group, because many statistics roundups mix them.
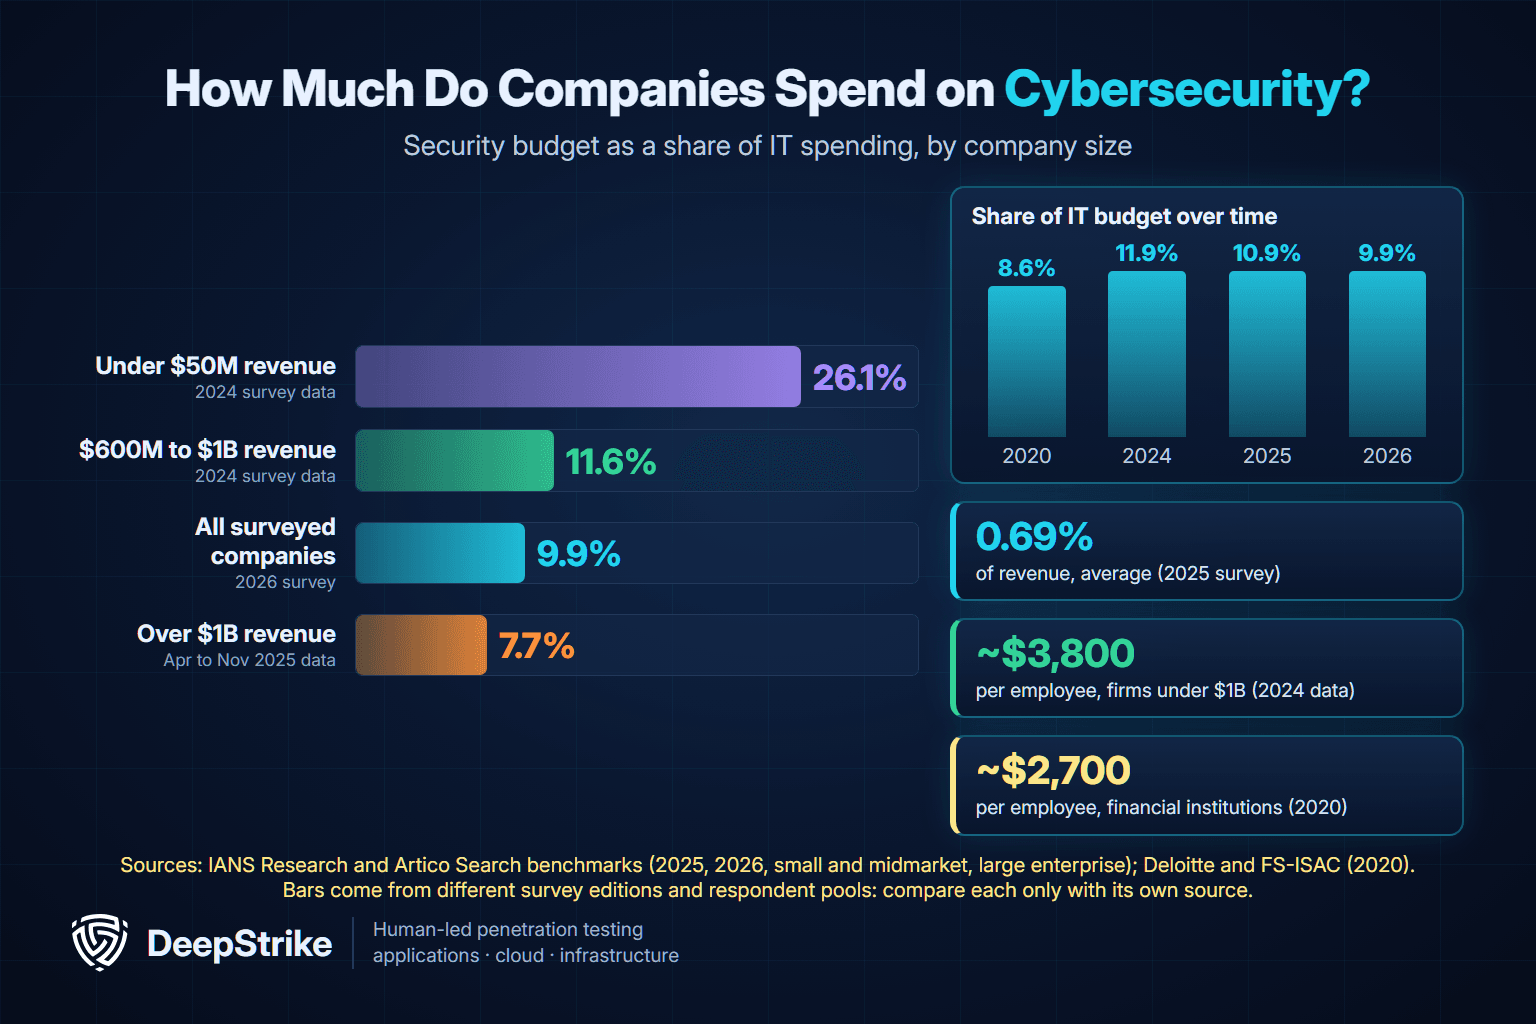
IANS has tracked the same ratio since 2020. Security's share of IT spending rose from 8.6% in 2020 to 11.9% in 2024, then fell to 10.9% in 2025 and 9.9% in 2026. The 2026 drop is mostly a denominator effect: average security budgets still grew 5% in 2026, although the median was 0% and 55% of CISOs reported flat or shrinking budgets. IT budgets simply grew faster. Gartner forecasts that worldwide IT spending will rise 14.2% in 2026 to $6.37 trillion, led by AI data center and cloud spending, while its end-user security forecast called for 12.5% growth.
| Company segment | Security share of IT budget | Survey data and source |
|---|---|---|
| All surveyed companies | 9.9% | 2026 survey, IANS and Artico Search (500+ CISOs) |
| All surveyed companies | 10.9% (11.9% in 2024) | 2025 survey, IANS and Artico Search (587 CISOs) |
| Under $50 million revenue | 26.1% | 2024 survey data, IANS small and midmarket report (published June 2025) |
| $600 million to $1 billion revenue | 11.6% | 2024 survey data, IANS small and midmarket report (published June 2025) |
| Over $1 billion revenue | 7.7% (down from 8.9%) | Data gathered April to November 2025, IANS large-enterprise report (published April 2026) |
| Financial institutions | 10.9% | 2020 survey, Deloitte and FS-ISAC (53 firms) |
Sources: IANS 2026 benchmark, IANS 2025 benchmark, IANS small and midmarket data, IANS large-enterprise report and Deloitte and FS-ISAC. Read the size bands as separate surveys rather than one curve, because they come from different editions and respondent pools.
Smaller firms spend a bigger share because many security costs are fixed. A company with a modest IT budget still needs email security, endpoint protection, multifactor authentication, backups and someone accountable for incidents. IANS found that firms under $50 million in revenue spent more than 2% of revenue on security, against about 0.6% for firms between $600 million and $1 billion. For small-business breach and attack data, see our small business cybersecurity statistics.
Two public benchmarks exist, and neither is a current cross-industry average. IANS and Artico Search data for companies under $1 billion in revenue (2024 survey, 363 CISOs) shows an average of about $3,800 in security spend per employee, higher at the smallest firms and falling with size. Those firms ran about 1.5 security staff per 100 employees under $50 million in revenue and 0.9 per 100 at $600 million to $1 billion. The figure most often quoted, about $2,700 per employee, comes from Deloitte and FS-ISAC's 2020 survey of 53 financial institutions, up from about $2,300 a year earlier.
The two surveys differ in year, sector and company size, so they are not a trend line. Treat the $2,700 figure as a dated, financial-services reference point, not a 2026 average for all companies. No major analyst firm publishes a free, current, cross-industry per-employee figure. A more useful step is to calculate your own number and compare it with your own history and with peers of the same size and sector.
Here is an illustrative calculation, not a benchmark. A company with $150 million in revenue and 600 employees spends $9 million a year on IT. If security receives 12% of that, the security budget is $1.08 million: $1,800 per employee and 0.72% of revenue. The share of IT spend and the share of revenue both fall between the IANS figures for smaller and larger firms, but spend per employee is well below the $3,800 small and midmarket average. When ratios disagree like this, check whether identity, endpoint and testing coverage has kept pace with headcount.
Industry changes both how much is spent and what it is spent on. In IDC's March 2026 Worldwide Security Spending Guide, banking, federal and central government, capital markets, telecommunications and healthcare providers are the five largest spenders in 2026, together accounting for more than a third of global security spending. Capital markets, media and entertainment, and software and information services are the fastest-growing industries. In the U.S., IDC names financial services, healthcare and government as the main drivers. China's 2024 industry split, led by government, financial services and telecommunications, is covered in the country breakdown above.
Three patterns hold across sectors:
Gartner also publishes an information security forecast by vertical industry, but its figures are available only to Gartner clients, so we do not quote them here. Be cautious with industry tables in free reports that cite no primary survey or forecast.
Gartner's most recent public worldwide security forecast, in its July 2025 press release, expects end-user spending on information security to reach $239.8 billion in 2026, up 12.5% from $213.0 billion in 2025. These are forecasts of what organizations will spend on security products and services, not measured spending, and Gartner has since updated the 2026 figure for its clients (about $244 billion in February 2026, as noted above).
| Segment | 2024 | 2025 | 2026 forecast | 2026 growth |
|---|---|---|---|---|
| Security software | $95.0B | $105.9B | $121.2B | 14.4% |
| Security services | $77.1B | $83.8B | $92.8B | 10.7% |
| Network security | $21.3B | $23.3B | $25.8B | 11.0% |
| Total | $193.4B | $213.0B | $239.8B | 12.5% |
Source: Gartner (July 2025); growth rates calculated by DeepStrike from Gartner's published figures. Later Gartner press releases add regional and emerging-market detail: end-user security spending in the Middle East and North Africa is forecast to reach $4.07 billion in 2026 (+10.1%), and the market for securing AI is forecast to grow from $2.8 billion in 2026 to $4.8 billion in 2027 (+68.7%).
Two things stand out. Software is growing fastest and passes $120 billion in 2026, while services still take close to 39% of the total, which reflects how many organizations buy outside expertise rather than hire it. And securing AI is still small, roughly 1% of total security spending if the two forecasts are set side by side, but it is growing several times faster than the market as a whole.
Use the numbers above as guardrails, not targets. A practical benchmark takes four steps:
The surge in global cybersecurity spending is not happening in a vacuum. It is a direct reaction to a handful of powerful, interconnected forces that are fundamentally reshaping the digital risk landscape. Understanding these catalysts is essential for any leader tasked with building a defensible budget.
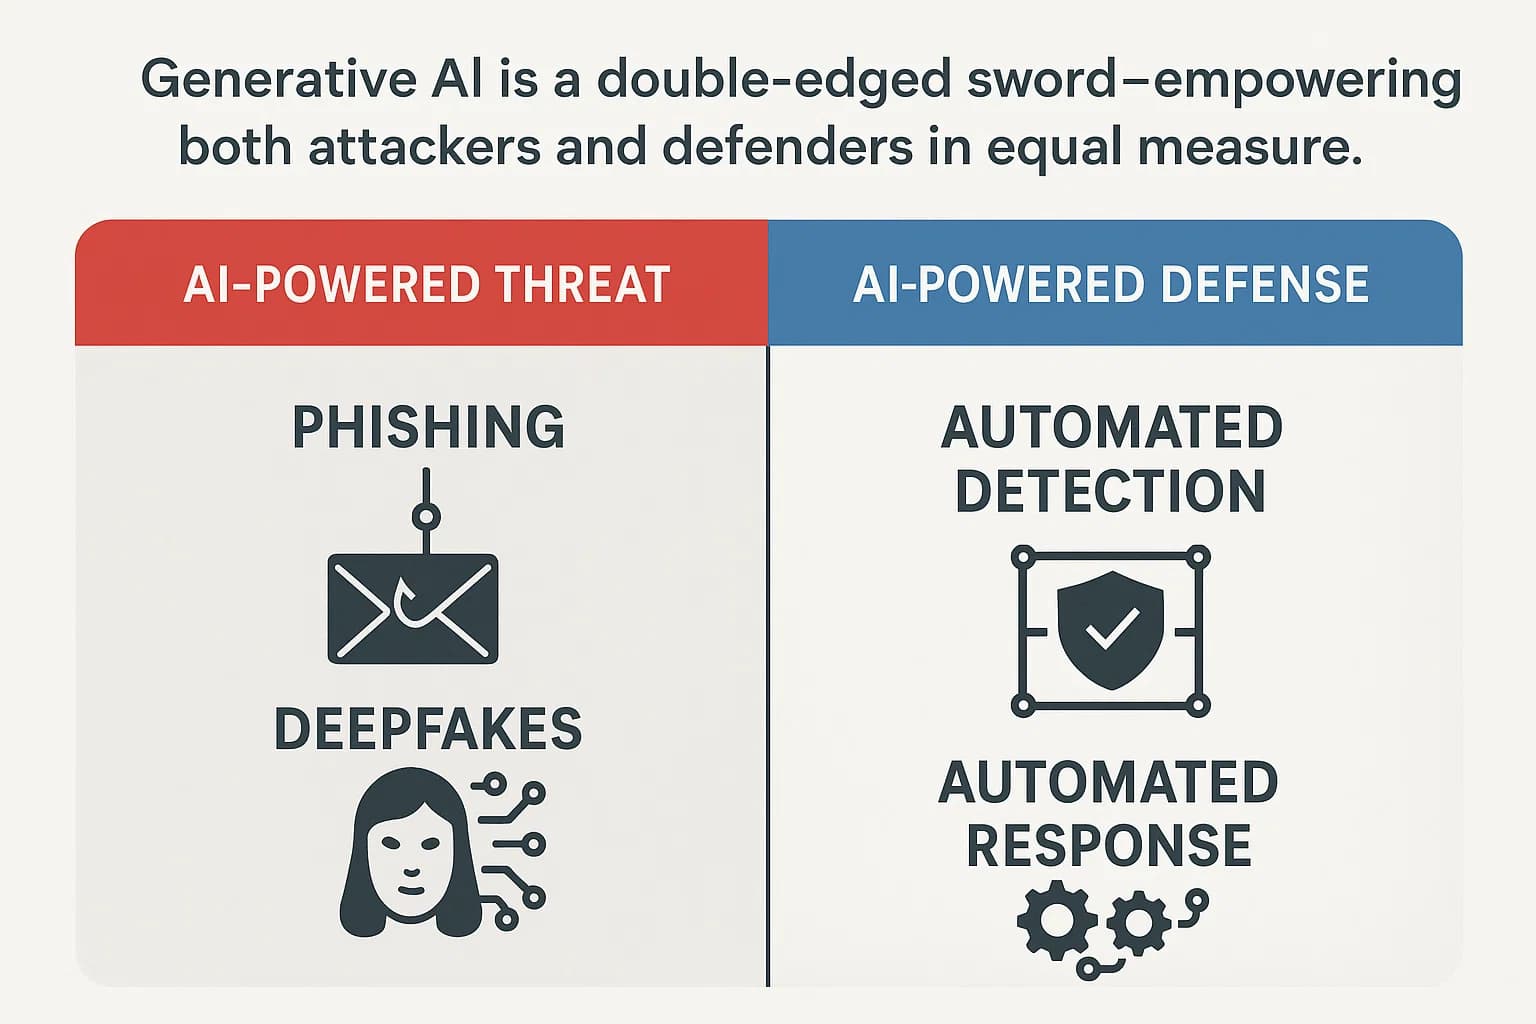
Artificial Intelligence is the single most disruptive force in cybersecurity today, acting as both a powerful weapon and an indispensable shield. On the one hand, attackers are weaponizing generative AI to create hyper realistic phishing emails, deepfake social engineering campaigns, and adaptive malware that can bypass traditional defenses. The barrier to entry for launching sophisticated attacks has been dramatically lowered. Gartner predicts that by 2027, 17% of total cyberattacks and data leaks will involve generative AI, and IBM's 2026 research found that about one in four malicious breaches were already AI enabled.
On the other hand, organizations are compelled to invest heavily in their own AI powered security tools for advanced threat detection, automated incident response, and behavioral anomaly analysis. The business case is compelling: in IBM's 2026 Cost of a Data Breach report, organizations that use security AI and automation extensively save an average of $1.93 million in breach costs compared to those that do not. This dual nature of AI is a primary spending driver, with Gartner naming the use of AI and GenAI by both defenders and attackers as a key growth driver for security spending. The rapid evolution of these threats is a central theme in our Malware Attacks and Infections analysis.
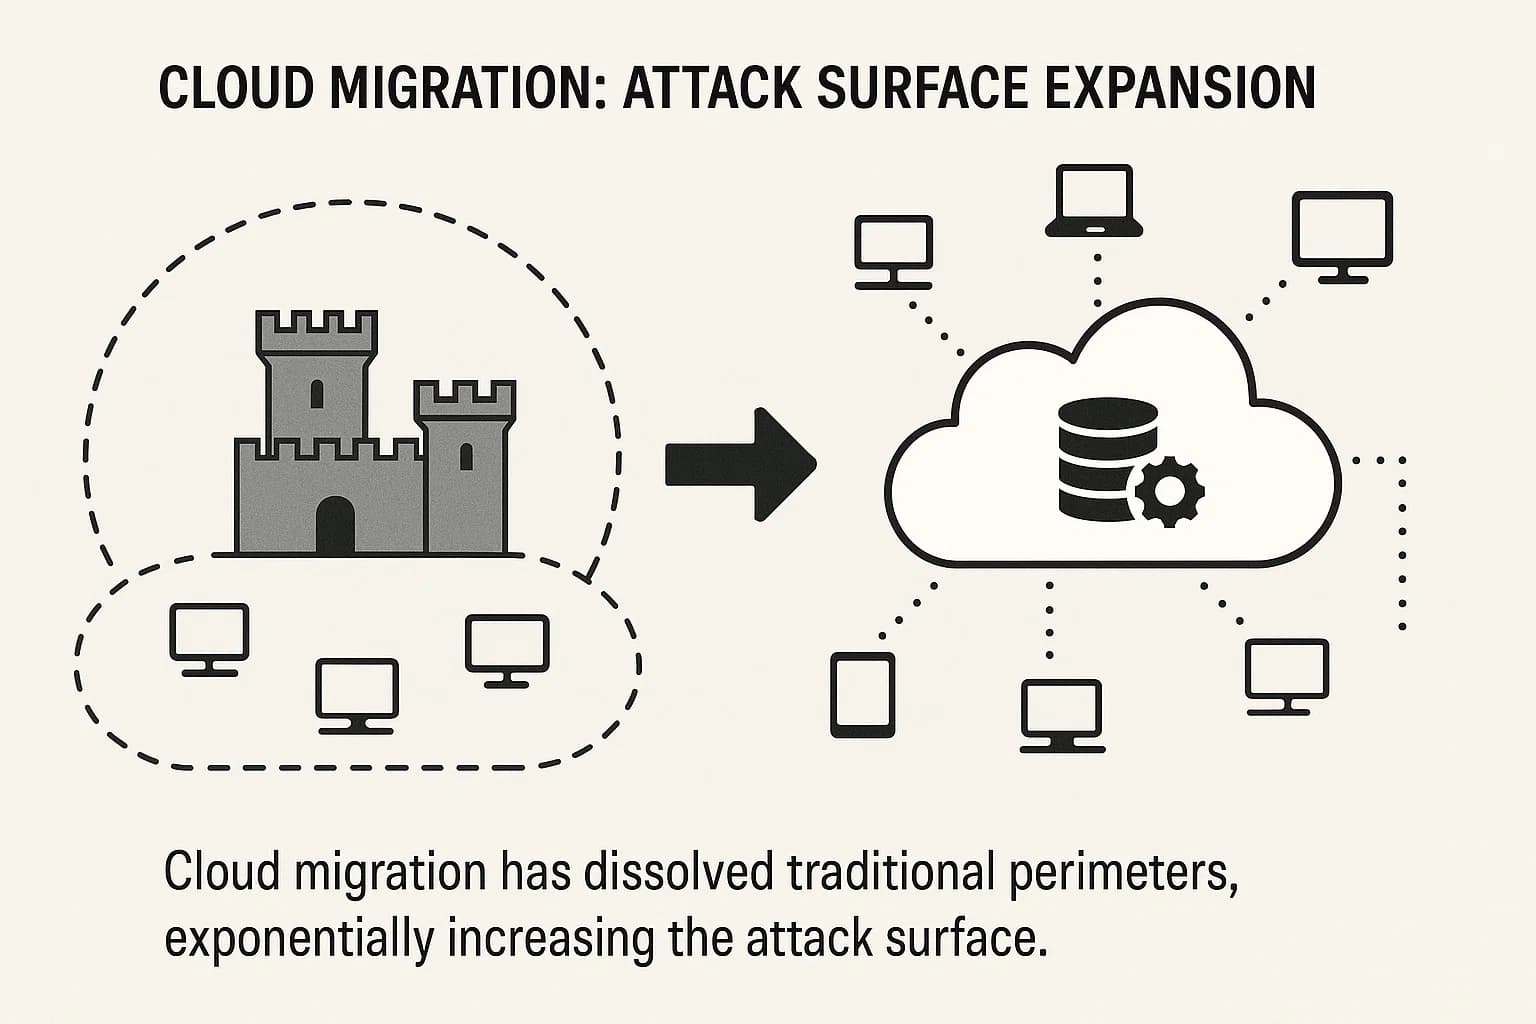
In 2026, digital transformation is synonymous with cloud adoption. However, this strategic shift from on premise data centers to sprawling, multi cloud environments has effectively dissolved the traditional network perimeter, dramatically expanding the attack surface. Security is no longer about building a strong wall around a castle; it's about protecting countless assets scattered across a borderless digital landscape.
Cloud specific risks now dominate the threat landscape. Misconfigurations, insecure APIs, and identity based attacks have become common entry points for adversaries. Gartner attributes security software's position as the fastest growing segment to the continued move from on premises to cloud based systems, with cloud security posture management and cloud access security brokers the main drivers. Consequently, organizations are prioritizing investments in Cloud Security Posture Management (CSPM) and Identity and Access Management (IAM) to regain visibility and control. Securing these new architectures requires a deep understanding of cloud native weaknesses, including GraphQL API vulnerabilities.
A critical, and often underestimated, driver of spending is the global shortage of skilled cybersecurity professionals. ISC2's 2024 Cybersecurity Workforce Study estimated a workforce gap of 4.8 million people worldwide, up 19% year over year. This isn't just an HR problem; it's a direct financial risk. In IBM's 2024 study, organizations reporting a high level skills shortage faced average breach costs of $5.74 million, significantly higher than the $3.98 million faced by those with low or no shortage.
Unable to hire and retain the necessary in house talent, companies are increasingly turning to the security services market. This has fueled strong growth in security consulting, managed security services, and flexible delivery models like penetration testing as a service ptaas. IDC expects managed security services to be the fastest growing security services category in 2026, as businesses choose to "rent" the expertise they cannot "buy".
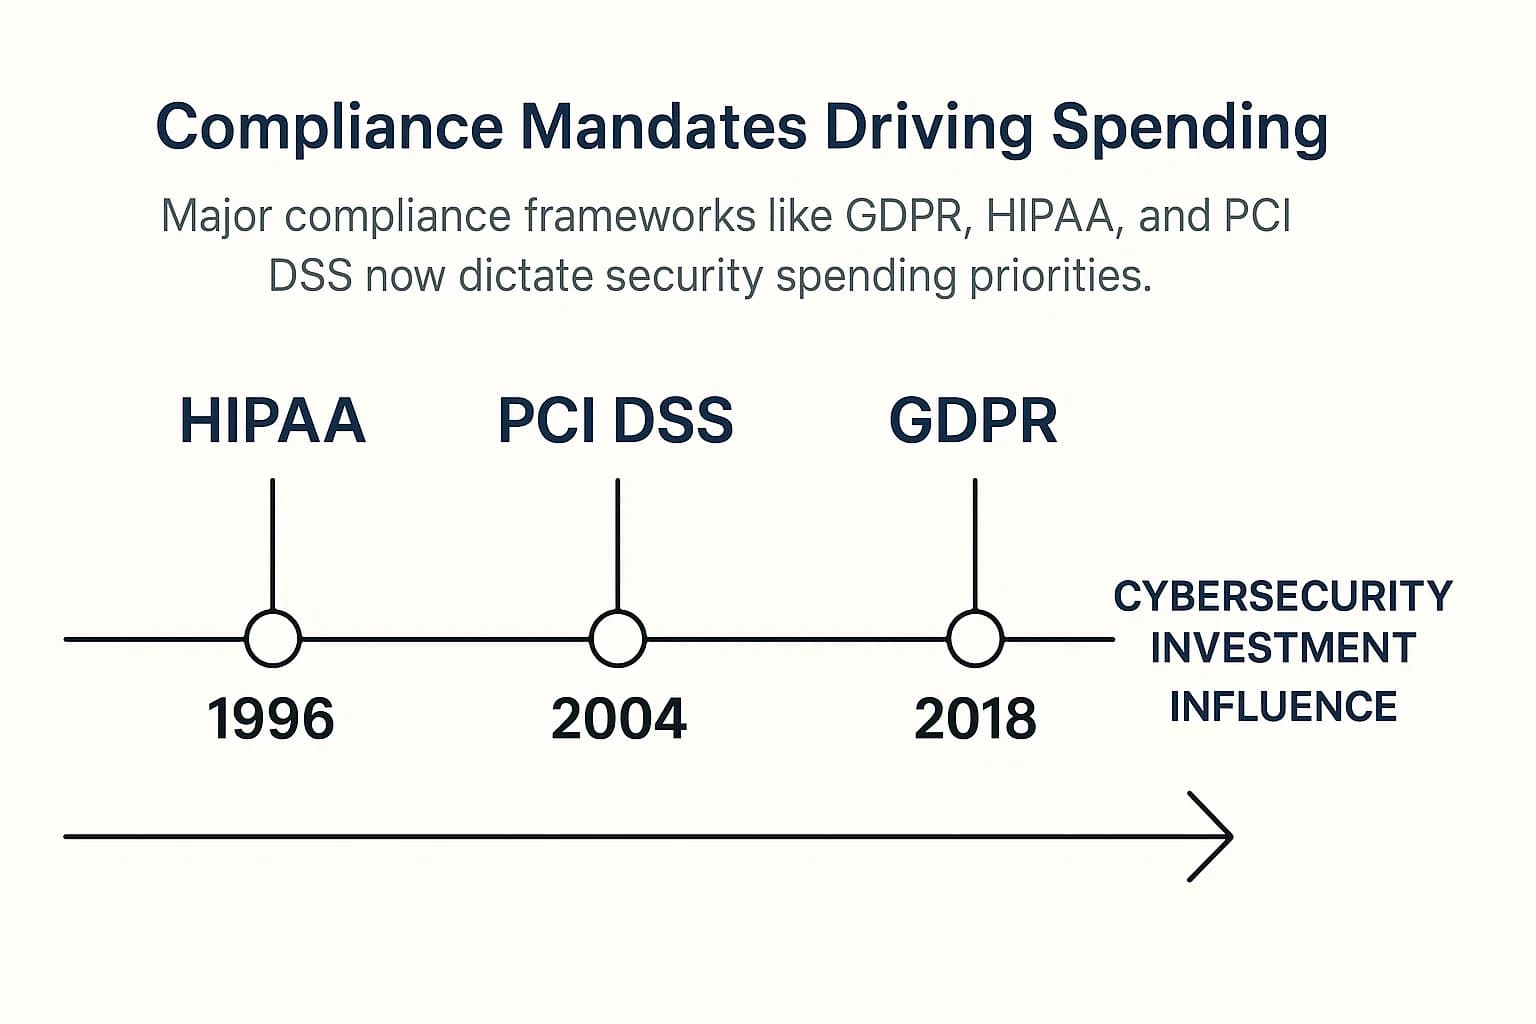
A complex and ever expanding web of regulations is acting as a powerful forcing function for cybersecurity investment. Mandates like the General Data Protection Regulation (GDPR) in Europe, the Health Insurance Portability and Accountability Act (HIPAA) in the U.S., and the Payment Card Industry Data Security Standard (PCI DSS) globally are no longer mere suggestions. GDPR and HIPAA are legal requirements backed by regulatory penalties, and PCI DSS is an industry standard that card brands and acquiring banks enforce through contracts, with fines and higher fees for non-compliance.
These regulations often dictate specific security controls and validation activities, directly shaping budget allocations. For example, PCI DSS 4.0 explicitly requires both annual penetration tests and quarterly vulnerability scans by an Approved Scanning Vendor (ASV), leaving no room for interpretation. This regulatory pressure is a major factor in purchasing decisions, and IDC points to NIS2, DORA and the EU AI Act as forces pushing Western European security spending to about $69 billion in 2026. As a result, compliance has become a major driver of security investment, with budgets needing to account for audits, specialized tooling, and validation services to meet these legal obligations. For healthcare organizations, our HIPAA penetration testing guide breaks down these specific requirements in detail.
These four drivers do not operate in isolation. They form a powerful, interconnected feedback loop. Consider a company undergoing a cloud migration that adopts new AI powered tools. This expands the attack surface, but the internal team lacks the skills to secure it due to the skills gap. This situation creates a high risk of non compliance with regulations like GDPR. The CISO is therefore compelled to allocate budget to a managed cloud security provider and a specialized PTaaS platform, a single strategic investment that addresses all four drivers simultaneously. Understanding this interconnectedness is the key to building a truly holistic and defensible budget.
In an environment of intense scrutiny, CISOs must evolve from technical managers into strategic business partners. This means building a cybersecurity budget that is not just a list of expenses, but a compelling business case rooted in risk reduction and value creation.
The most pervasive myth in cybersecurity budgeting is that a bigger budget automatically equates to better security. The available readiness data does not support this.
The 2025 CYE Cybersecurity Maturity Report concludes that more security spending is not, by itself, making businesses safer. In CYE's data, heavy spenders such as the US and Germany did not top the maturity rankings, while higher-ranking countries such as Norway and Japan combined focused investment, a cohesive strategy and strong execution. This demonstrates that a well coordinated strategy and a focus on fundamentals can outperform raw spending.
The real issue is often not the size of the budget but its allocation. Many organizations fall into the trap of spending on "shiny new tools" while neglecting foundational cyber hygiene, such as patch management and user training. A lack of clear visibility into the true attack surface means that money is often spent protecting the wrong assets or defending against the wrong threats. The first step in smart spending is to understand your real world weaknesses, which is why differentiating between a vulnerability assessment vs penetration testing is so critical to an effective strategy.
For decades, CISOs have struggled to justify security spending in terms that resonate with the C suite. The perception of cybersecurity as a cost center persists, and in many organizations security still sits inside the IT budget, forced to compete with other operational priorities. A helpful way to reframe the conversation is to think of your cybersecurity budget like home insurance. You don’t buy it hoping to use it, but you’d never skip it. It's a strategic investment in protecting your most valuable assets.
The solution is to shift the conversation from cost to value by calculating the Return on Security Investment (ROSI). This financial framework reframes security as a mechanism for loss prevention and business enablement.
The formula is straightforward: ROSI = ((ALE x Mitigation Ratio) - Cost of Solution) / Cost of Solution
Here’s a practical example:
This calculation transforms the budget request. The conversation is no longer, "Can we afford this $150,000 tool?" Instead, it becomes, "Can we afford not to invest $150,000 to prevent a potential loss of $998,000?" To calculate your potential losses accurately, you need up to date figures from our data breach statistics report.
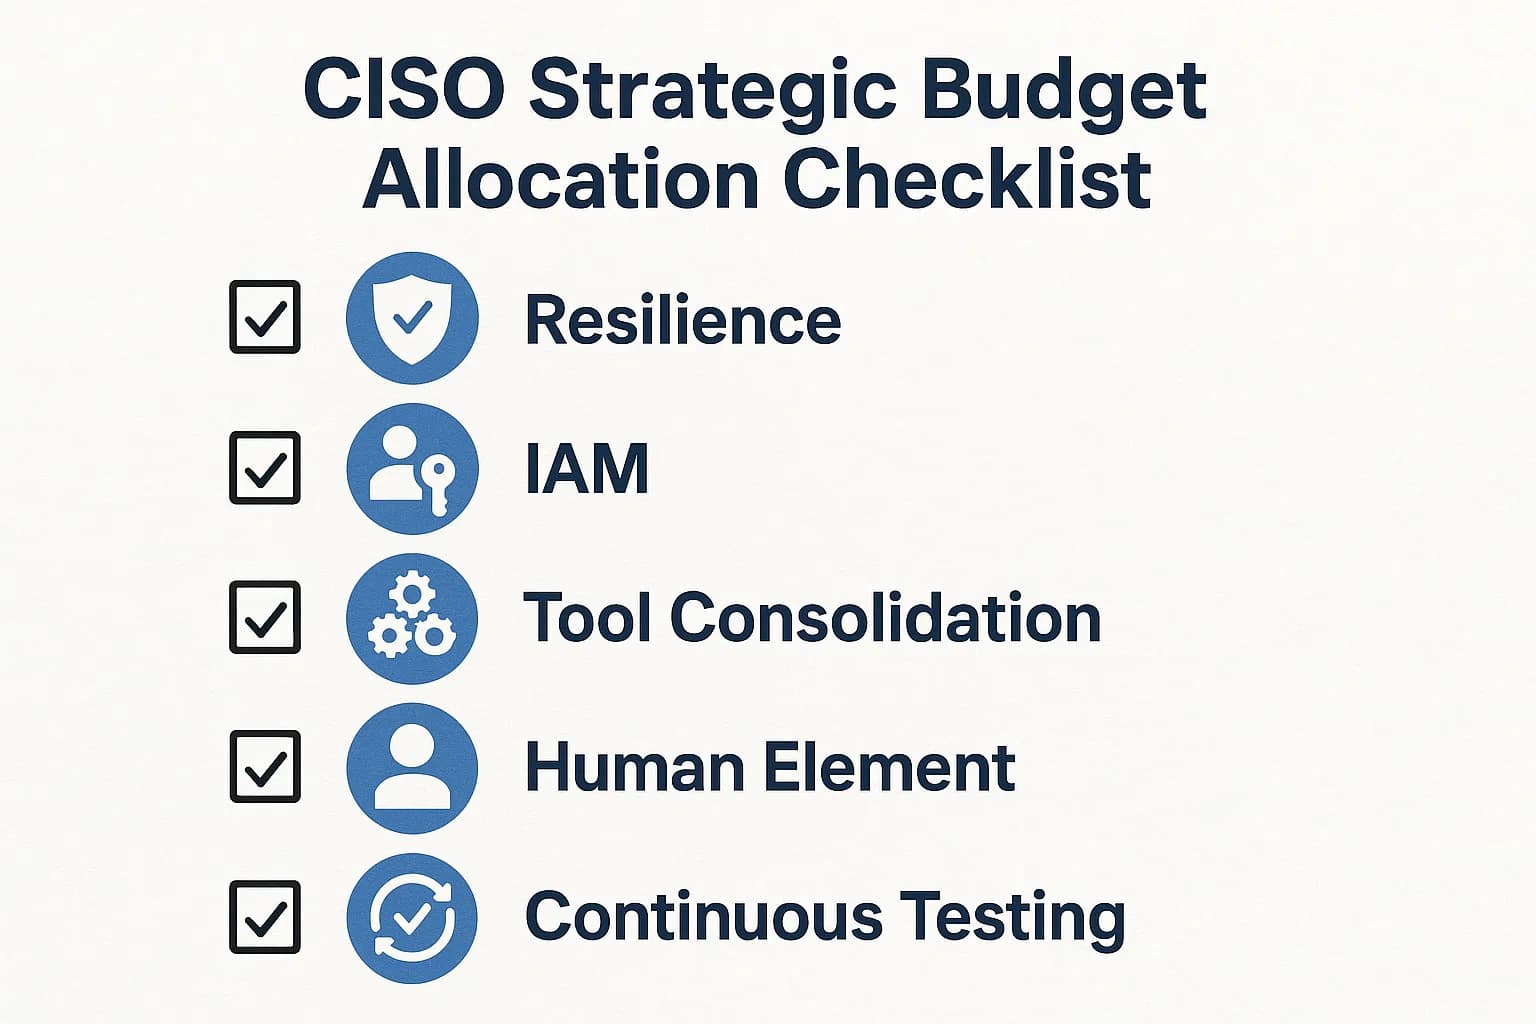
Building a modern, defensible budget requires a focus on strategic priorities that deliver the greatest risk reduction.
To illustrate these principles in action, consider the case of "FinSecure," a composite mid sized global bank based on real world scenarios.
FinSecure faced a familiar predicament: rising cyber insurance premiums, mounting pressure from regulators, and a security budget that was growing but failing to improve their actual risk posture. Their traditional approach consisted of annual, compliance driven spending that left them perpetually behind the threat curve. The breaking point came after a minor but costly data breach originating from a third party vendor, which exposed critical weaknesses in their supply chain security and incident response capabilities.
The new CISO initiated a fundamental strategic shift, moving the budget away from a reactive, tool based model to a proactive, risk based one.
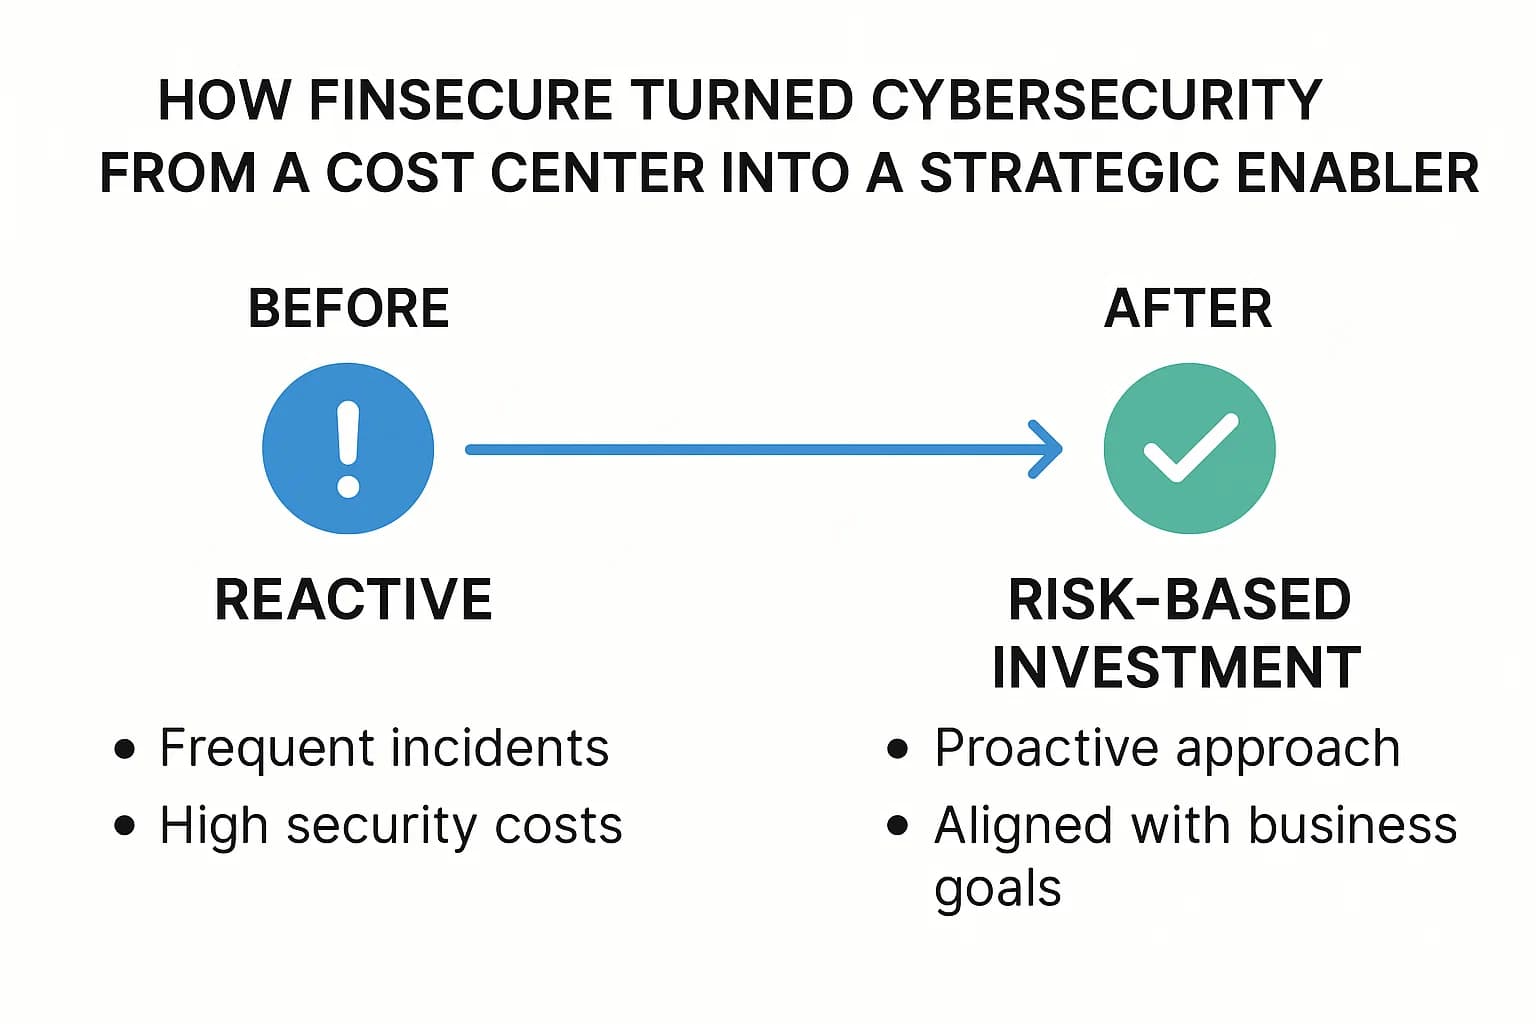
In this illustrative scenario, within 18 months, FinSecure reduced its mean time to detect (MTTD) threats by over 60%, lowered its projected Annualized Loss Expectancy (ALE) by 45%, and successfully negotiated a 15% reduction in its cyber insurance premium. Their security budget was no longer a contentious cost center but a defensible, value driving investment. Their success was driven by a deeper understanding of their true attack surface, a core benefit of evolving from simple vulnerability scanning to a full red team vs blue team exercise model.
The United States is the largest spender in absolute terms. IDC forecasts U.S. security spending of $150 billion in 2026, roughly half of its $308 billion global total and far ahead of any other country.
This varies dramatically by company size and industry. In the IANS and Artico Search benchmark, security's share of IT spending fell to 9.9% in 2026 (from 10.9% in 2025 and 11.9% in 2024) as AI-driven IT budgets grew faster, even though security budgets grew 5% on average in 2026 (median growth 0%). Smaller firms spend a larger share: among small and midmarket organizations, security averaged 26.1% of IT spend at companies under $50 million in revenue, falling to 11.6% at those with $600 million to $1 billion in revenue.
There is no single magic number. IANS data shows the average share of the IT budget going to security rose from 8.6% in 2020 to 11.9% in 2024, then fell to 10.9% in 2025 and 9.9% in 2026, so roughly 8% to 12% is a common reference range for mid-sized and large organizations; companies above $1 billion in revenue averaged 7.7%. Smaller companies and high risk, regulated industries such as finance and healthcare often allocate a larger share.
There is no current cross-industry public benchmark. In IANS and Artico Search data from 2024, companies under $1 billion in revenue averaged about $3,800 per employee, with the smallest firms spending the most per head. The widely quoted figure of about $2,700 per employee comes from Deloitte and FS-ISAC's 2020 survey of 53 financial institutions. Because both figures are dated and limited to specific groups, calculate your own figure and compare it with peers of the same size and sector.
In the 2025 IANS and Artico Search benchmark of 587 CISOs, security budgets averaged 0.69% of company revenue, flat year over year. Smaller companies spend a higher share: IANS found firms under $50 million in revenue spent more than 2%, against about 0.6% for firms between $600 million and $1 billion. Financial institutions in the 2020 Deloitte and FS-ISAC survey spent about 0.48% of revenue.
Gartner forecasts worldwide end-user spending on information security of about $240 billion in 2026, up 12.5% from $213 billion in 2025, in its July 2025 press release. IDC, which defines the market more broadly, forecasts $308 billion. The two firms measure different things, so do not add or directly compare their totals.
The top drivers are the dual threats and opportunities presented by Artificial Intelligence, the security complexities of mass migration to the cloud, the persistent global cybersecurity skills shortage forcing reliance on services, and increasing pressure from government and industry regulations.
Yes. IDC forecasts global security spending will grow from $308 billion in 2026 to $430 billion by 2029, and Gartner projected in July 2025 that worldwide end user information security spending would rise 12.5% to $240 billion in 2026 (a February 2026 Gartner update put 2026 at about $244 billion). The growth is driven by the escalating cost and sophistication of cybercrime and the need to secure AI.
The most common method is calculating the Return on Security Investment (ROSI). This is done by comparing the cost of a security solution to the amount of financial loss it prevents. The formula involves multiplying the Annualized Loss Expectancy (ALE) by the solution's mitigation rate, subtracting the solution's cost, and then dividing by the solution's cost.
While high profile threats like ransomware command attention, the most pervasive threat vector remains the human element. Verizon's 2026 DBIR found a human element in 62% of breaches, and credential abuse appeared at some stage in 39%. This reality drives consistent, heavy spending on Identity and Access Management (IAM), Multi Factor Authentication (MFA), and continuous security awareness training, a fact underscored by our latest password statistics.
The era of cybersecurity as a simple IT line item is definitively over. In 2026, global spending will continue its relentless climb, but the narrative has fundamentally shifted from quantity to quality. The data is clear: throwing money at the problem is a failing strategy. The world's most cyber resilient nations and organizations are pivoting from reactive, compliance driven spending to proactive, risk based investment.
The key takeaways are unmistakable:
Your cybersecurity budget is more than a defense mechanism; it's a strategic enabler for digital transformation, a protector of customer trust, and a core pillar of business continuity. Navigating this complex landscape requires more than just data; it requires expert guidance.
Need expert guidance? We’re here to help. Whether you’re planning a security strategy, facing compliance challenges, or just want an expert opinion, Reach out. At DeepStrike, we don’t sell fluff, just clear, actionable advice from real world practitioners.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
