November 18, 2025
Updated: November 5, 2026
A data-driven look at daily dark web activity users, markets, stolen data, cybercrime services, and the law-enforcement operations monitoring this hidden ecosystem.

Mohammed Khalil
Ever wonder what really goes on in the dark web each day? In simple terms, it hums with activity. Millions of people use anonymity networks such as Tor every day, and a minority of them visit hidden sites (on Tor, I2P and similar networks) where illicit goods are bought and sold, from narcotics and weapons to stolen credit cards and hacking tools. Media sometimes focus on sensational stories, but the reality is a highly organized underground economy.
On a daily basis, this hidden network of sites, a tiny fraction of the Internet, is dominated by illegal commerce and information exchange. For example, darknet markets received about $1.7 billion in crypto in 2025 (TRM Labs), and SpyCloud's 2026 report counts 65.7 billion stolen identity records recaptured from criminal sources. Understanding these daily activities is crucial in 2026 because the dark web directly fuels modern cyberthreats: every leaked password or malware kit there can lead to real world attacks. In short, staying on top of what's happening in the dark web helps organizations protect themselves from breaches, extortion, and fraud.
The dark web refers to websites hosted on encrypted networks like Tor or I2P that are not indexed by regular search engines. It’s essentially a hidden subsection of the broader deep web. While surface web (the normal Internet) contains public sites you can find via Google, and deep web includes private or password-protected content (e.g., online banking), the dark web is specifically hidden by design for anonymity. In practice, this means you need a special browser like the Tor Browser to visit .onion addresses and other concealed sites. Check out our Deep Web vs Dark Web guide.
| Layer / Category | Accessibility | Typical Content | Relative Size |
|---|---|---|---|
| Surface Web | Standard browsers Chrome, etc. | Public websites news, shopping, social media | Small share of total online content |
| Deep Web | Login/password protected | Private data bank accounts, emails, academic journals | Most online content (exact share cannot be measured) |
| Dark Web | Tor/I2P browsers | Anonymized sites illicit marketplaces, secret forums, whistleblower platforms | Tiny: about 0.5 to 0.7 million v3 .onion addresses seen per day (Tor Metrics, Sep to Oct 2026) |
This table shows that the dark web is tiny compared to the rest of the Internet. Yet, as with an iceberg, it hides a vast underground economy below the surface. Practically all content there aims for privacy or secrecy. A King's College London study (Moore and Rid, 2016) found that about 57% of the dark web sites it could classify hosted illicit material such as drugs, illicit finance, and hacking tools. The remainder includes legitimate uses, such as secure communication for journalists or activists.
Unlike the open web, the dark web has its own ecosystem: search engines e.g. Ahmia and directories let users find hidden sites, and forums serve as community hubs. Many attackers and researchers even develop specialized search tools for .onion domains. In short, the dark web is a small piece of the Internet where privacy and anonymity reign which is why it attracts criminals, but also some privacy conscious users.
On any given day in 2026, roughly 3 million people connect to the Tor network directly, according to Tor Metrics, plus roughly 200,000 to 270,000 more through bridges. That may seem small compared to billions on the open web, but it's substantial for an anonymous network. The estimates also swing: Tor Metrics showed about 2.1 to 2.3 million daily users in early 2025, then short-lived spikes far above normal levels that likely reflect automated traffic, before settling at roughly 3.0 to 3.3 million a day in September and October 2026. Users are concentrated in a few countries: the U.S. and Germany together account for close to 30% of directly connecting users, followed by the UK, Finland, Brazil, France, India, and the Netherlands.
In practice, only a minority of Tor users visit hidden sites daily. Many use Tor just for extra privacy on the surface web. A 2020 PNAS study estimated that on an average day only about 6.7% of Tor users connect to onion services. Applied to today's user numbers, that still means on the order of 200,000 people browsing dark web markets and forums every day.
Daily behavior varies by user:
Behind the scenes, technical activity runs 24/7: cryptocurrency transactions (mostly in Bitcoin, Monero, etc.) flow through the network to pay for goods, and encrypted chats and forums buzz with new posts. Automated bots index .onion sites and monitor chatter. In short, the dark web never sleeps: every hour sees new illicit deals, data trades, and criminal coordination.
The core of daily dark web activity is marketplaces and forums. These hidden sites act like underground eBay or Amazon, but for illegal products. Typical examples include Brian's Club for stolen credit cards, Russian Market for infostealer logs, and large Russian-language drug markets. These sites list tens of thousands of items and services. Western markets are less stable: Abacus Market, then the largest Western market, went offline in July 2025 in what TRM Labs assessed as a likely exit scam. More recent entrants like TorZon Market have since joined that top tier.
Top categories of illicit trade by volume are:
For example, popular markets have reputation systems and escrow, and some even require vendor licenses. It's a surprisingly professionalized ecosystem, with escrow and dispute resolution that mimic legal e-commerce trust models. Full details on specific markets can be found in our Top 7 Dark Web Marketplaces roundup.
The payment currency is almost always crypto. Buyers and sellers trade in Bitcoin, Monero, etc., to stay anonymous. Darknet markets are only a small slice of crypto crime: Chainalysis found that illicit crypto addresses received at least $154 billion in 2025, driven mostly by sanctioned entities, while darknet markets took in about $1.7 billion according to TRM Labs (more in our dark web statistics).
Prices fluctuate daily with demand. For instance, law enforcement crackdowns or new vulnerabilities can spike interest and price in certain data. Monitoring these prices via a Dark Web Price Index gives insight into what attackers value. In short, the dark web’s economy is highly active every day people are constantly listing, bidding, and closing deals in this black market.
Every day the dark web fuels cyberthreats around the world. Some key trends to watch:
Overall, virtually any cyberattack element is available on the dark web. From a day to day perspective, new goods hacked databases, botnet services, stolen cookies and services hacking gigs, VPN exits continuously appear. This avalanche of resources accelerates attacks in the real world.
Although hidden, the dark web is far from lawless. Agencies worldwide actively track and infiltrate it every day. Undercover agents pose as buyers or sellers on forums; automated crawlers index secret sites. Cryptoforensics teams trace Bitcoin flows to link addresses. When criminals slip up reusing an email, accessing outside Tor, etc., they can be unmasked.
Several high profile takedowns occurred in recent years, showing how global police follow dark web activity closely:
These actions demonstrate daily vigilance. Whenever major players or transactions emerge, law enforcement works undercover to intercept them. For more on these methods, see our article How Law Enforcement Tracks Criminals On The Dark Web. That said, a successful takedown only temporarily disrupts trade the dark web economy is resilient, with new markets springing up quickly after any closure.
In parallel, corporate defenders also monitor the dark web daily. Organizations use specialized Dark Web Monitoring Tools to scan paste sites, forums, and marketplaces for leaked company data. Threat intelligence analysts parse dark chats and listings to spot targeted attack plans. Continuous monitoring turned on 24/7 means defenders can get early warning if, for example, employee credentials or proprietary data appear online. Similarly, in boards and security operations centers, analysts check dark web indicators alongside open source chatter. All of this means that what happens on the dark web daily doesn’t stay secret someone is listening and documenting it.
Because the dark web is mysterious, there are lots of myths about it. Here are some truths drawn from daily observations:
For more common misconceptions, check out our Dark Web Myths vs Reality guide, which digs deeper into these misunderstandings.
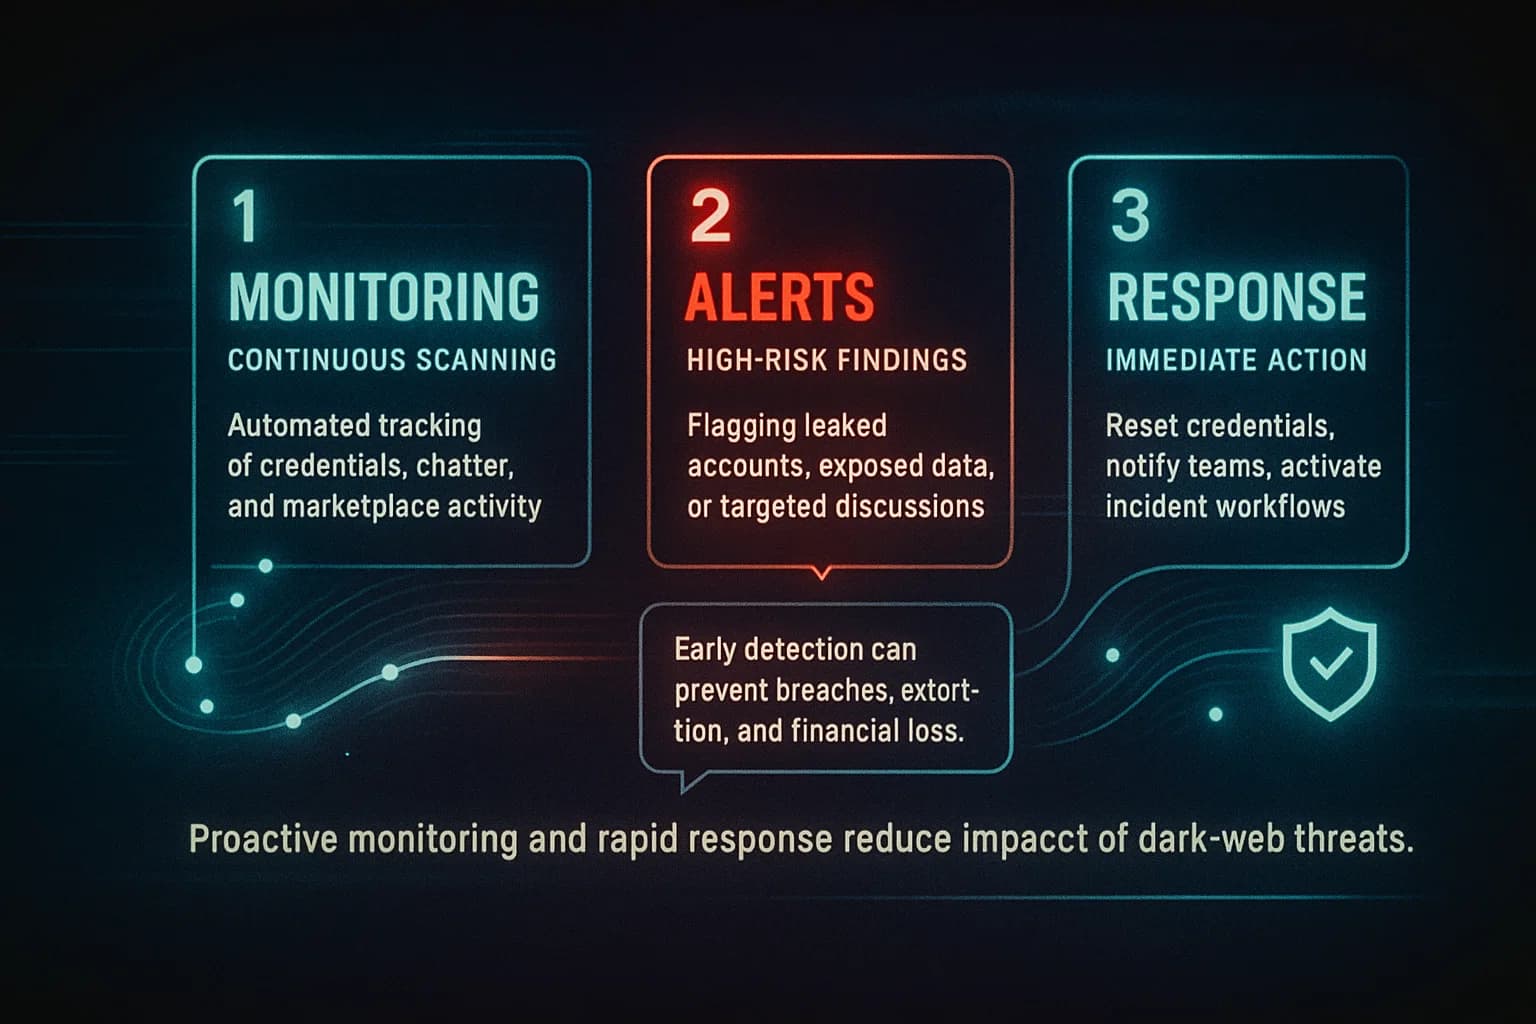
Given all these daily dark web activities, UK organizations tracking dark web activity need a playbook. Here’s a step by step approach:
By following these steps continuously, organizations flip the script: instead of being surprised by attacks, they proactively watch what happens on the dark web each day and adjust defenses. Frameworks such as NIST CSF and ISO 27001 expect organizations to gather threat intelligence, and dark web monitoring is one way to do that.
Daily life on the dark web is a hidden one, but its effects spill into the open world. Every day, roughly 3 million people use Tor, and a much smaller group, on the order of 200,000, visit onion services, where illicit trade in drugs, data and hacking help is concentrated. These activities power an underground economy worth billions annually. While law enforcement and security teams work tirelessly to watch this space, defenders must be just as vigilant. A professional red-team engagement can test whether leaked credentials, malware, or access sold through underground markets can be chained into a realistic intrusion against the organization.
In 2026, the key takeaways are clear: Know your enemy's marketplace. Monitor the dark web for your data, keep an eye on illicit price trends, and simulate attacks with penetration testing. By treating the dark web as part of your threat landscape, you turn a blind spot into early warning. If you want to strengthen your defenses, our team can help.
Ready to Strengthen Your Defenses? The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. DeepStrike's Premium plan also includes Dark Web Monitoring, weekly automated vulnerability scanning and attack surface management alongside continuous penetration testing.
Our team of practitioners provides clear, actionable guidance to protect your business. Explore our Penetration Testing Services to see how we can uncover vulnerabilities before attackers do. Drop us a line we’re always ready to dive in.
About the AuthorMohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
The dark web is the hidden portion of the internet accessible only via special anonymizing browsers Tor, I2P. It is a subset of the deep web sites not indexed by Google. Unlike the deep web which includes private accounts and paywalled content, the dark web is specifically hidden to provide anonymity.
Tor Metrics estimates about 3 million people connect to Tor directly each day (September to October 2026), plus roughly 200,000 to 270,000 through bridges. Only a minority visit .onion sites: a 2020 PNAS study put it at about 6.7% of users on an average day. The largest user bases are in the U.S., Germany, the UK, Finland, Brazil, France, India, and the Netherlands.
Simply using Tor isn't illegal, but much of the dark web is used for illegal trade. A 2016 King's College London study found that about 57% of the dark web sites it could classify hosted illicit content (drugs, illicit finance, hacking, etc.). Many legitimate activities also happen, such as privacy tools and activism, but most dark web sites facilitate crime.
Virtually everything illegal under the sun. Daily commerce includes: controlled substances cocaine, fentanyl, etc., stolen personal data SSNs, credit cards, social media accounts, malware and hacking tools, counterfeit documents IDs, diplomas, ransomware kits, and more. Cybercriminals can even hire services like money laundering or DDoS for hire. The dark web essentially has a black market for any illicit need.
Yes, agencies around the world actively monitor and infiltrate it. They use undercover agents and analysis like tracing cryptocurrency flows to identify criminals. Famous examples Silk Road, AlphaBay, Hydra were shut down by law enforcement. While anonymity tools make it hard, skilled investigators take advantage of mistakes and covert operations to break cases.
Organizations and individuals use dark web monitoring services. These services scan hidden sites and alert you if your email or company domain appears in any leaks. You can also check free breach notification tools like Have I Been Pwned to see if your accounts have been exposed. Proactively changing passwords and using MFA are best defenses.
Yes. Every day there is churn: new sites pop up, old ones go offline, administrators get arrested and replaced. Whenever a market is taken down, another rises quickly. Additionally, new cybercrime trends emerge AI generated phishing kits, new exploit marketplaces. Staying current requires continuous monitoring of the dark web ecosystem.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
