June 16, 2026
Updated: November 5, 2026
Vendor security, SaaS exposure, API risk, and software supply chain data for 2026.

Mohammed Khalil
Third-party risk statistics for 2026 show that vendor risk is no longer a procurement-only problem or a questionnaire-only problem. The current exposure model is broader: SaaS vendors, managed service providers, cloud integrations, APIs, software dependencies, outsourced IT, customer support systems, identity providers, payment processors, and privileged vendor access all create real attack paths. Recent research shows a meaningful share of breaches now involve third parties, large supply-chain compromises continue to rise, SaaS oversharing and overprivileged API access remain common, and software supply chain abuse is scaling through open-source ecosystems.
That matters because third-party risk creates business exposure far beyond technical inconvenience. It can trigger data breaches, customer notification obligations, regulatory and contractual review, downtime, trust damage, delayed sales cycles, insurance scrutiny, and board-level reporting pressure. Public-company disclosure rules, healthcare breach obligations, payment-card service-provider evidence requirements, and customer security reviews all push organizations toward better evidence, better access control, and better testing. This article uses publicly available 2024–2026 data and labels each statistic by data type so third-party-specific evidence is not mixed carelessly with broader breach, cloud, SaaS, API, or supply chain benchmarks.
This 2026 guide combines third-party-risk research, breach benchmarks, vendor-risk survey data, software supply chain research, cloud and SaaS security data, regulatory and framework guidance, and public incident case studies. Each statistic is labeled by data type so general breach, cloud, SaaS, or supply chain benchmarks are not treated as third-party-risk-only evidence. Where a statistic is not third-party-specific, it is used only as context for vendor security and supply chain risk decisions. Source links should point to official report pages or source hubs where available.
| Statistic | Data type | What it shows | Third-party risk implication | Source |
|---|---|---|---|---|
| 48% of breaches in Verizon’s 2026 DBIR involved a third party, up from 30% in the 2025 edition (15% in 2024). | Third-party-risk benchmark | Third-party involvement is no longer marginal in real-world breach analysis. | Vendor connections, suppliers, MSPs, and shared-service providers now deserve the same scrutiny as internet-facing assets. | Verizon DBIR 2026 |
| 35.5% of 1,000 breaches analyzed for 2024 were linked to third-party access. | Third-party breach benchmark | A second, independent dataset puts vendor-linked breaches at more than one in three. | Treat vendor access as a recurring breach path in threat models and board reporting, not an edge case. | SecurityScorecard 2025 Global Third-Party Breach Report (2024 data) |
| 41.4% of ransomware attacks in the same dataset involved third-party access. | Ransomware benchmark | Ransomware crews reuse vendor credentials, remote tools, and supplier software. | Segment vendor access and rehearse a vendor-compromise scenario in ransomware tabletop exercises. | SecurityScorecard 2025 Global Third-Party Breach Report (2024 data) |
| Only 23% of third-party organizations fully remediated missing or improperly secured MFA on their cloud accounts. | Third-party-risk benchmark | Vendor cloud exposures are fixed slowly and often incompletely. | Ask vendors for MFA and least-privilege evidence for the services you use, and retest it. | Verizon DBIR 2026 |
| The global average cost of a data breach was $4.99 million in IBM’s 2026 report, up from $4.44 million in 2025. | Breach benchmark | Even non-third-party-specific breach costs remain financially material. | When a high-risk vendor is involved, TPRM decisions become cost-containment decisions, not just compliance decisions. | IBM Cost of a Data Breach 2026 |
| Large supply-chain and third-party compromises nearly quadrupled since 2020. | Supply-chain benchmark | Attackers increasingly target trusted ecosystems instead of a single perimeter. | Supplier trust paths, SaaS integrations, CI/CD systems, and vendor identities are strategic targets. | IBM X-Force / IBM Think 2026 |
| IBM observed a 44% year-over-year increase in exploitation of public-facing applications. | Breach benchmark | Internet-facing applications remain a fast route into interconnected environments. | Vendor portals, support consoles, partner apps, and exposed admin surfaces need ongoing validation. | IBM X-Force / IBM Think 2026 |
| 63% of organizations reported external data oversharing in SaaS environments. | SaaS benchmark | Data exposure often happens through configuration and sharing, not only “hacks.” | SaaS risk review must include tenant configuration, sharing controls, and data handling paths. | CSA State of SaaS Security 2025 |
| 56% said employees upload sensitive data to unauthorized SaaS apps. | SaaS benchmark | Shadow SaaS continues to move sensitive data outside approved oversight. | Vendor inventory and data-flow mapping must include unsanctioned apps and AI-enabled services. | CSA State of SaaS Security 2025 |
| 56% reported concerns about overprivileged API access in SaaS-to-SaaS integrations. | API benchmark | API risk is often really permission-risk. | Vendor due diligence should validate scopes, tokens, service accounts, and least privilege. | CSA State of SaaS Security 2025 |
| 58% struggle to enforce privileges, and 54% lack lifecycle automation for SaaS identities. | SaaS benchmark | Third-party risk often becomes identity governance risk. | Recurring access review, offboarding, and NHI governance are critical TPRM controls. | CSA State of SaaS Security 2025 |
| 57% of organizations were hit by an API-related data breach in the last two years. | API survey benchmark | APIs are now a direct breach path, not only an integration convenience. | High-risk partner APIs need testing, authorization review, and logging validation. | Traceable / Ponemon 2025 State of API Security |
| Only 21% reported a high ability to detect API attacks, and only 13% could prevent more than half of them. | API survey benchmark | Defensive maturity at the API layer remains weak. | Technical validation should focus on API discovery, auth logic, abuse paths, and response telemetry. | Traceable / Ponemon 2025 State of API Security |
| Cloudflare says APIs account for 57% of the dynamic internet traffic it processes. | Cloud benchmark | APIs are not edge cases; they are core operational infrastructure. | Third-party API risk now sits near the center of customer data exchange and workflow automation. | Cloudflare 2024 API Security and Management Report |
| 87% of organizations reported at least one API-related security incident in the past 12 months. | API survey benchmark | API incidents are now routine for large enterprises (1,840 respondents in 10 countries). | Partner and vendor APIs need inventory, authorization testing, token review, and monitoring. | Akamai 2026 API Security Impact Study (2025 data) |
| Only 23% of enterprises with full API inventories know which of their APIs return sensitive data. | API visibility benchmark | Having an API inventory is not the same as knowing where sensitive data flows. | Map sensitive data flows through partner and SaaS APIs before scoping vendor API tests. | Akamai 2026 API Security Impact Study (2025 data) |
| Sonatype identified more than 454,600 new malicious packages in 2025, bringing the cumulative total to more than 1.233 million. | Software supply chain benchmark | Package ecosystems are now an industrialized malware delivery channel. | SBOM, dependency governance, and CI/CD validation are now third-party risk controls, not just AppSec hygiene. | Sonatype 2026 State of the Software Supply Chain |
| GitHub reported 7,197 malware advisories in 2025. | Software supply chain benchmark | Open-source malware and advisory volume continue to scale. | Dependency review must prioritize exploitability, package trust, and update governance. | GitHub Advisory Database trends 2026 |
| Mandiant and Snowflake notified approximately 165 potentially exposed organizations in the 2024 campaign, and at least 79.7% of the accounts used by the threat actor had prior credential exposure. | Case-study evidence | Third-party cloud incidents often depend on identity hygiene more than platform “breach” narratives. | Vendor risk assessment should include MFA, credential rotation, contractor access, and network allow-list review. | Mandiant Snowflake campaign analysis |
| HHS says Change Healthcare later notified OCR that approximately 192.7 million individuals were impacted. | Case-study evidence | A third-party concentration event can become a sector-wide operational and privacy crisis. | Critical vendor dependency, healthcare business-associate obligations, and incident communication plans must be treated as resilience controls. | HHS OCR Change Healthcare FAQ |
Sources for the newer rows: the SecurityScorecard Global Third-Party Breach Report (1,000 breaches from 2024), the Akamai 2026 API Security Impact Study (1,840 security professionals, 2025 data) and the Verizon 2026 DBIR. SecurityScorecard and Akamai are vendor-published research, so treat them as context next to Verizon. The SecurityScorecard and Verizon third-party percentages come from different samples and definitions, so they should not be read as a trend. For what to test in vendor APIs, the OWASP API Security Top 10 (2023) lists broken object level authorization first.
Third-party risk is not measured simply by how many vendors you have. A 20-vendor environment with deep admin access, broad SaaS permissions, unmanaged APIs, and outsourced support access can be riskier than a 200-vendor environment with strong segmentation and narrow scopes. The real drivers are data sensitivity, access depth, integration type, identity privilege, token lifetime, hosting model, incident visibility, and who actually controls remediation. That framing is consistent with NIST’s supply-chain guidance and the CSF 2.0 focus on supplier criticality, due diligence, contract requirements, and monitoring throughout the relationship.
Broad breach or supply-chain statistics still matter, but they should be treated as context unless the source explicitly segments third-party exposure. That is why the table above separates third-party-risk benchmarks from SaaS, API, software supply chain, and general breach benchmarks. Blending those categories without labeling them produces weak decisions and weak executive reporting.
The most actionable third-party statistics are the ones that map to fixable gaps: incomplete vendor inventory, weak data mapping, stale access, permissive OAuth grants, excessive API scopes, unmanaged dependencies, poor cloud role design, delayed incident notification, weak technical validation, and missing retest evidence. In other words, the useful question is not “how many vendors do we have?” but “which vendors can materially affect our data, identity, uptime, customer commitments, or release chain?”
Third-party risk is the security, privacy, operational, financial, regulatory, and reputational exposure created when an organization depends on external vendors, suppliers, SaaS platforms, service providers, cloud providers, software components, contractors, business partners, or outsourced processes. NIST frames this broadly: risks arise when products and services may contain malicious functionality, counterfeit content, or vulnerabilities caused by weak development or manufacturing practices, and those risks become harder to manage when organizations lack visibility into how technology is developed, integrated, and deployed. ISO’s supplier-relationship guidance takes a similar view by centering information security risk within supplier relationships rather than treating procurement as a narrow buying exercise.
In practical terms, that definition includes SaaS vendor risk, cloud provider risk, managed service provider risk, outsourced IT risk, supplier risk, contractor access risk, vendor API risk, third-party data processing risk, third-party data breach exposure, fourth-party risk, open source dependency risk, software supply chain risk, CI/CD supply chain risk, identity-provider dependency, payment processor dependency, customer support platform risk, vendor remote access, privileged vendor access, vendor incident notification obligations, supplier business continuity, and third-party compliance evidence. The shared theme is simple: if an external party can affect your confidentiality, integrity, availability, customer commitments, or disclosure obligations, it belongs in scope.
A useful taxonomy helps avoid confusion:
Third-party risk is the umbrella category. Vendor risk management is the operating discipline for assessing and managing the risk posed by external providers. Supply chain risk management is broader and includes upstream and downstream technology, services, and dependencies. Software supply chain security is the narrower discipline focused on packages, dependencies, build systems, release integrity, and provenance. Third-party cyber risk emphasizes security-specific exposure. Fourth-party risk covers your vendors’ dependencies. Data processor risk is the privacy and regulatory side of the same problem. Outsourcing risk covers operational transfer and loss of direct control. Procurement risk is the acquisition and contract lens. Compliance risk is what happens when a third party jeopardizes your ability to meet legal, regulatory, or customer obligations. Operational resilience risk is the continuity lens. Vendor security assessment is the evidence-gathering and validation process. Vendor penetration testing is the technical proof layer applied where exposure justifies direct testing.
That distinction matters because many organizations still collapse everything into a vendor questionnaire. NIST’s CSF 2.0 explicitly pushes organizations further: suppliers should be known and prioritized by criticality, due diligence should happen before the relationship begins, supply-chain requirements should appear in contracts, suppliers should be included in incident planning and recovery, and the risk should be monitored through the relationship and after it ends. That is a governance model, not a form-distribution model.
Third-party risk management in 2026 is no longer a once-a-year procurement workflow. Mature TPRM connects vendor inventory, data mapping, access review, contractual controls, technical validation, continuous monitoring, incident response, and remediation tracking. That direction is consistent with NIST CSF 2.0, NIST SP 800-161, PCI guidance on third-party evidence, and the current reality that a meaningful share of breaches now involve third parties.
Questionnaires still matter. Security ratings still matter. SOC 2 reports, ISO 27001 certifications, PCI validations, and trust-center materials still matter. But they answer a narrower question than many teams assume. They help you understand a vendor’s declared control environment and independently assessed scope. They do not prove that your specific OAuth grant is safe, your support integration is minimally privileged, your cloud trust relationship is narrow, your vendor’s API authorization model is correct, or your remediation actually worked after a serious finding. PCI’s own third-party guidance stresses responsibility mapping, validation evidence, and continuous review rather than blind reliance on attestation.
That is why TPRM should be tiered. A marketing SaaS tool with low-sensitivity data and no admin path does not need the same evidence depth as a payroll processor, claims clearinghouse, customer-support platform, identity provider, or managed service provider with production access. A practical tiering model uses four variables first: data sensitivity, access depth, business criticality, and technical connectivity. Everything else comes after that.
| TPRM area | What it covers | Common failure | Validation method |
|---|---|---|---|
| Vendor inventory | List of vendors and services | Unknown vendors and shadow SaaS | SaaS and procurement review |
| Data mapping | What data vendors access | Sensitive data not tracked | Data flow review |
| Access review | Users, tokens, keys, vendor accounts | Stale or overprivileged access | IAM and SaaS review |
| Security questionnaire | Vendor control claims | Self-reported evidence only | Evidence review |
| Technical integration | APIs, SSO, webhooks, cloud links | Unvalidated trust path | API/cloud testing |
| Incident visibility | Vendor notification and logs | Late or unclear breach scope | IR and contract review |
| Remediation tracking | Vendor fixes | No proof fixes worked | Retest evidence |
A mature program treats remediation and retesting as core TPRM activities, not as side notes. Verizon’s 2026 finding that 48% of breaches involved a third party, its 2025 data on slow secret remediation, plus Mandiant’s Snowflake analysis of stale credentials and missing MFA, show why point-in-time review is not enough for high-risk vendors.
A strong vendor security assessment should establish what the vendor does, what data it touches, what identities or systems it can access, what it depends on, and what evidence proves its controls are functioning for the services you actually use. That means going beyond “Do you have SOC 2?” into scope, integration design, access boundaries, logging depth, test coverage, and remediation proof. PCI guidance is especially clear here: the customer must understand which requirements are met by the third party, monitor compliance status, and request evidence relevant to the services actually provided.
At minimum, a vendor risk assessment should capture vendor inventory, business owner, data classification, access level, authentication method, SSO and MFA status, admin permissions, API access, cloud integration, webhook exposure, encryption evidence, audit logging, incident notification terms, relevant assurance documents, vulnerability-management evidence, data deletion and retention obligations, fourth-party dependencies, resilience and continuity plans, and remediation tracking. For software suppliers, NIST’s SSDF gives useful structure because it lets software purchasers use a common vocabulary with suppliers during acquisition and management activities.
| Vendor assessment area | Key question | Evidence to request |
|---|---|---|
| Data access | What data can the vendor view, process, or store? | Data flow and data processing evidence |
| Identity | How are vendor accounts authenticated? | SSO/MFA configuration evidence |
| Privileged access | Can vendor users administer systems? | Role and access review |
| APIs | Does the vendor integrate with internal systems? | API documentation and security evidence |
| Cloud integration | Does the vendor connect to cloud resources? | IAM policy and logging evidence |
| Security testing | Has the vendor tested relevant systems? | Pentest summary and remediation status |
| Compliance | Which controls are independently assessed? | SOC 2, ISO 27001, PCI, HIPAA evidence |
| Incident response | How and when will the vendor notify? | IR policy and contract clause |
| Fourth parties | Who does the vendor depend on? | Subprocessor list |
| Remediation | Are findings tracked and verified? | Remediation tracker and retest letter |
A defensible vendor assessment package usually contains three layers of evidence. The first is assurance material: audit reports, certificates, policies, and architecture summaries. The second is integration evidence: scopes, roles, API docs, configuration screenshots, and data flow diagrams. The third is validation evidence: test summaries, issue trackers, tabletop outputs, and retest letters. The first layer tells you a vendor has a program. The second tells you how your environment is actually connected. The third tells you whether the connection has been challenged and fixed.
A high-quality vendor risk assessment should let an executive answer seven questions quickly: What data does this vendor touch? What access does it have? How is that access authenticated? Which integrations create trust paths? Which third parties sit behind it? What evidence proves controls were assessed? And what process verifies remediation when issues are found? If those answers are incomplete, the vendor is not fully assessed yet.
Organizations often assume that if internal controls are strong, customer data is reasonably safe. Third-party incidents keep disproving that assumption. SaaS oversharing, unauthorized app use, permissive API scopes, support-system compromise, identity weaknesses, and vendor-held secrets can all expose data even when the organization’s own endpoint and network controls are well managed. CSA’s 2025 SaaS benchmark is especially revealing: 63% reported external data oversharing, 56% said employees upload sensitive data to unauthorized SaaS apps, 56% expressed concern about overprivileged API access, and 58% struggled to enforce privileges.
Third-party breaches are also harder to scope than internal incidents. Logs may sit with the service provider. Detection timelines may depend on a vendor’s own investigation quality. Notification timing may be contract-dependent. In healthcare, HHS reminds covered entities and business associates that breach notification duties still apply when the breach occurs at or by the business associate, and in public-company contexts the SEC’s materiality and disclosure clock can quickly turn a vendor incident into a securities disclosure issue.
| Third-party exposure path | How it happens | Business impact | Validation method |
|---|---|---|---|
| SaaS vendor breach | Vendor platform exposes customer records | Notification and trust damage | Vendor evidence review |
| API integration flaw | Partner API exposes excessive data | Data leakage | API penetration testing |
| Cloud integration gap | Vendor role has broad cloud access | Infrastructure exposure | Cloud IAM review |
| Support platform compromise | Customer support data accessed | Privacy and customer trust risk | SaaS access review |
| Data export misuse | Vendor exports sensitive data | Data loss and retention risk | Data handling review |
| MSP compromise | Managed service account abused | Broad environment compromise | Vendor access review |
| Software dependency flaw | Component introduces vulnerability | Product exposure | SCA/SBOM review |
Recent case studies make those paths concrete. Okta disclosed that a threat actor accessed files associated with 134 customers inside its support system and used session tokens to hijack the sessions of five customers. Mandiant’s Snowflake analysis found approximately 165 potentially exposed organizations, with prior credential exposure in at least 79.7% of the accounts used by the attacker. Change Healthcare later became a reminder that a critical third-party provider can turn into a national-scale operational and privacy event.
For many organizations, third-party risk is now identity risk wearing a vendor badge. Contractors, partners, MSPs, SaaS integrations, API keys, OAuth grants, service accounts, support portals, and remote-access tools create persistent access paths that outlive onboarding packets. CSA’s 2025 data on privilege enforcement, lifecycle automation, non-human identity monitoring, and overprivileged API access points to the same conclusion: identity governance is now a TPRM control.
| Access risk | How it appears | Impact | Validation method |
|---|---|---|---|
| Stale vendor account | Vendor user remains active after work ends | Unauthorized access | Access review |
| Overprivileged role | Vendor gets admin access by default | Excessive blast radius | Least-privilege review |
| API key sprawl | Long-lived integration keys | Data exposure | Secrets review |
| OAuth grant risk | App has broad scopes | Persistent SaaS access | OAuth review |
| Shared vendor account | No individual accountability | Weak audit trail | Identity review |
| Weak MFA | Vendor users lack strong auth | Account compromise | MFA evidence review |
| Poor logging | Vendor actions not traceable | Weak investigation | Logging validation |
The Snowflake campaign adds an important nuance: contractor systems mattered. Mandiant observed several investigations in which infostealer infections happened on contractor systems used for personal activity, creating a bridge into customer environments. That is precisely why third-party access review should cover device trust assumptions, not only account status.
| Business type | Common third-party exposure | Main risk | Validation priority |
|---|---|---|---|
| SaaS | Cloud vendors, support tools, APIs, identity apps | Customer data exposure | SaaS/API/cloud review |
| Healthcare | EHR vendors, billing processors, third-party portals | PHI exposure | Vendor access and portal/API testing |
| Fintech | Payment processors, KYC vendors, banking APIs | Fraud and regulated data exposure | API and transaction workflow testing |
| Ecommerce | Payment, logistics, marketing SaaS | Customer/payment data exposure | Web/API/vendor review |
| Enterprise vendor | Customer security reviews | Trust and contract risk | Evidence package and pentest |
| Critical infrastructure | OT vendors, remote access, MSPs | Operational disruption | Access and segmentation testing |
| Cloud provider / MSP | Privileged customer environment access | Multi-tenant impact | Cloud/IAM/segmentation review |
| Manufacturing | ERP, suppliers, logistics, remote maintenance | Operational downtime and ransomware | Segmentation and remote access testing |
| Education | LMS, cloud storage, identity platforms | Student data exposure | SaaS access and cloud review |
| Legal and professional services | Document platforms, email, e-signature vendors | Confidential client data exposure | Identity and vendor access review |
| Government contractors | Subcontractors, cloud, software suppliers | Sensitive data and compliance exposure | Supply chain review and access control |
The sector angle matters because “third-party risk” does not behave the same way in every environment. Healthcare risk is often dominated by data processors and care-operation dependencies. Fintech risk leans heavily on APIs, transaction workflows, and outsourced verification. SaaS and cloud-native businesses tend to accumulate integration risk through OAuth, support tooling, secrets, and software supply chain dependencies.
Verizon’s 2026 DBIR shows how much the third-party share of breaches varies by sector. In its industry snapshots, third-party involvement ranges from about a third of breaches in healthcare and finance to more than two-thirds in retail.
| Industry (DBIR 2026) | Third-party share of breaches | Typical third-party exposure |
|---|---|---|
| Retail (NAICS 44–45) | 68% | Payment gateways, ecommerce platforms, fulfillment, marketing scripts |
| Manufacturing (NAICS 31–33) | 61% | Suppliers, ERP, logistics, remote maintenance |
| Small and medium-sized businesses | 55% | MSPs, SaaS, outsourced IT |
| Educational services (NAICS 61) | 40% | LMS, cloud storage, identity platforms |
| Public administration (NAICS 92) | 36% | Contractors, cloud providers, software suppliers |
| Financial and insurance (NAICS 52) | 34% | Fintechs, payment processors, KYC vendors, APIs |
| Healthcare (NAICS 62) | 32% | EHR, billing, claims, and lab vendors |
| All industries | 48% | Up from 30% in the 2025 DBIR |
These are shares of each sector’s confirmed breaches in Verizon’s dataset, not industry-wide breach rates, and sector sample sizes differ. For a professional-services view, see our law firm data breach statistics.
Two widely cited datasets put the third-party share of breaches between roughly one-third and one-half. Verizon’s 2026 DBIR found third-party involvement in 48% of breaches, a 60% increase on the 30% reported a year earlier. SecurityScorecard’s 2025 Global Third-Party Breach Report linked 35.5% of 1,000 breaches from 2024 to third-party access. The gap reflects method: Verizon counts several kinds of vendor involvement across its incident dataset, while SecurityScorecard analyzed its own breach sample. Either way, a vendor is now a routine breach path, not an exception.
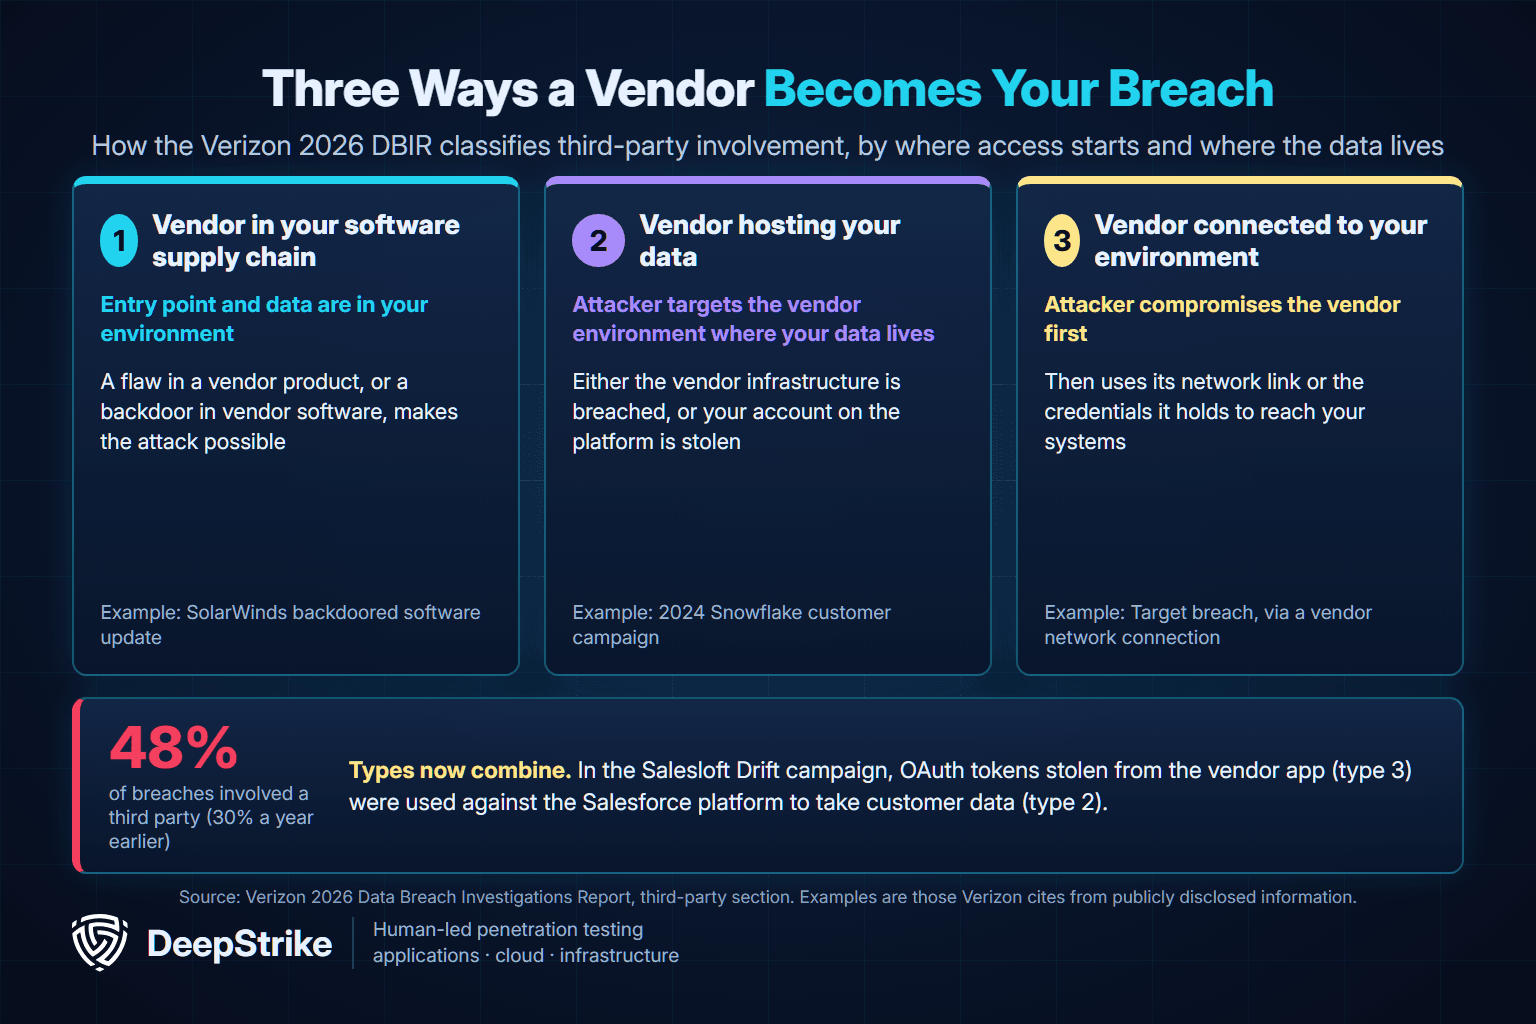
Verizon’s third-party metric combines three relationship types, defined by where initial access happened and where the breached data was stored:
Verizon notes that recent breaches increasingly combine two or all three. In the Salesloft Drift campaign it describes, OAuth tokens stolen from the vendor’s application were then used against the Salesforce platform to take customer data. Two related terms help with scoping: a fourth-party breach starts at your vendor’s own supplier, and supplier fraud, such as invoice redirection through an impersonated vendor, can cause losses without exposing any data. Each one needs different controls and evidence, which is why third-party risk management programs map vendors by access path, not only by contract.
In SecurityScorecard’s 2024 data, 41.4% of ransomware attacks involved third-party access. MSP remote-management tools, vendor VPN accounts, file-transfer products, and support credentials give ransomware crews trusted paths into many environments at once. Our MSP cybersecurity statistics cover incident counts and RMM abuse in more detail, and the wider trend is tracked in our ransomware statistics.
The practical defenses are segmentation that keeps vendor access away from critical systems, monitoring of vendor sessions, and a cybersecurity tabletop exercise that rehearses a compromised supplier. Mature programs can add a red team assessment that starts from a simulated vendor foothold and tests whether detection and containment work.
The 2026 DBIR includes resolution data collected from inside third-party cloud environments. Only 23% of third-party organizations fully remediated missing or improperly secured MFA on their cloud accounts, although half of those findings were resolved within about a month. Weak passwords and excessive permissions were slower: half took almost eight months to resolve, and only 31% of organizations fully remediated them. In a separate point-in-time dataset, 37% of organizations had an IaaS admin account with MFA disabled, compared with 14% on Snowflake.
For vendor risk teams, the lesson is to request authentication and privilege evidence for the specific services you use, then verify fixes with a retest instead of accepting a closed ticket. Our vendor risk statistics cover assessment and monitoring benchmarks in more depth.
On October 2, 2025, Red Hat confirmed that an unauthorized third party had accessed and copied data from a GitLab instance used for internal Red Hat Consulting collaboration in select engagements. Red Hat said the instance held consulting engagement reports that may include project specifications, example code snippets, and internal communications, and that it was notifying affected customers. The Crimson Collective group claimed far more, including about 800 customer engagement reports that could contain infrastructure details and authentication tokens; Red Hat did not confirm those claims, as BleepingComputer reported. Our write-up of the Red Hat Consulting GitLab breach covers the timeline.
The lesson goes beyond one vendor. Consultants, auditors, and testing providers hold documents that describe your environment. Treat those reports as sensitive data, limit the secrets you share during an engagement, and rotate any credentials a service provider held once its work ends or after it reports an incident.
Third-party breaches are often harder to contain because logs, evidence, and fixes sit with the vendor. IBM’s 2026 report puts the global average breach at $4.99 million, and vendor incidents add coordination costs that a first-party breach may not have:
| Cost category | Third-party breach example | Why it matters |
|---|---|---|
| Incident response | Investigation is needed in both the vendor and customer environments | Scope may be unclear and evidence incomplete |
| Legal and regulatory review | Customer data exposed by a processor or SaaS vendor | Notification duties can still fall on the customer |
| Vendor investigation delay | Vendor shares limited logs or slow updates | Slows containment, disclosure, and recovery |
| Operational downtime | A SaaS, MSP, or cloud vendor outage stops work | Revenue suffers even without an internal compromise |
| Ransomware recovery | Vendor credentials enable ransomware entry | Recovery spans several systems and trust relationships |
| Customer notification | Data stored by a vendor is exposed | Customers blame the brand that collected the data |
| Contract remediation | Security clauses, indemnity, and notice terms need review | Adds legal and procurement work |
| Replacement vendor cost | A high-risk vendor has to be replaced | Migration and integration add cost and disruption |
| Cyber insurance impact | A claim is tied to a vendor-related breach | Underwriting, coverage, and premiums can change |
A simple way to rank vendors is expected loss = likelihood of a vendor-path compromise × business impact. Likelihood rises with data sensitivity, access depth, the number of vendor accounts, API scopes, SaaS admin rights, cloud privileges, and weak segmentation or logging. Impact rises with regulatory exposure, customer trust, recovery dependency, vendor concentration, slow notification, and fourth-party dependencies. Treat the formula as a prioritization aid, not an actuarial model.
Supply chain cybersecurity includes vendors, software suppliers, package ecosystems, build systems, CI/CD services, cloud platforms, identity providers, and managed services. NIST’s supply-chain guidance explicitly treats products and services as risk carriers across development, integration, and deployment, not just across procurement. That broader definition is important because many of the most damaging modern incidents did not begin with a classic “vendor questionnaire failure”; they began with trust abuse in software, identity, or service relationships.
Software supply chain attacks differ from normal vendor risk in one important way: the compromise is often shipped downstream into customer environments through code, packages, update channels, or build tooling. That is why SBOM visibility matters, but visibility alone is not enough. An SBOM tells you what is present. It does not, by itself, tell you whether a component is exploitable in your environment, whether the package was tampered with upstream, whether CI/CD tokens were exposed, or whether a release process can be trusted. NIST’s SSDF supports supplier communication and secure development practices, while real-world advisory and malware data from GitHub and Sonatype show why software evidence must extend beyond an inventory file.
| Supply chain weakness | Example risk | Why it matters | Validation method |
|---|---|---|---|
| Vulnerable dependency | Third-party package flaw | Product compromise | SCA and SBOM review |
| Malicious package | Package ecosystem abuse | Build or runtime compromise | Dependency integrity review |
| CI/CD access weakness | Build pipeline token exposed | Production tampering | CI/CD security review |
| Vendor remote access | Supplier has persistent access | Privilege abuse | Access review |
| Managed service compromise | MSP account abused | Multi-customer impact | Vendor access validation |
| File transfer vendor flaw | Transfer platform exploited | Data theft | Exposure and patch review |
| SaaS identity integration | SSO/OAuth trust abused | Account compromise | OAuth and SSO review |
The current software supply chain picture is difficult to ignore. Sonatype identified more than 454,600 new malicious packages in 2025 alone, bringing the cumulative total to more than 1.233 million, and said more than 99% of the malware it tracked that year occurred on npm. GitHub reported 7,197 malware advisories in 2025. These are not edge statistics; they are signals that open-source ecosystems are being treated as scalable attack infrastructure.
An SBOM is useful because it makes dependency exposure discussable. It helps security, procurement, and engineering teams speak the same language. It also improves response speed when a major library, transitive dependency, or supplier component becomes high risk. But a mature program pairs SBOM review with SCA tuning, package integrity checks, secrets management, build provenance, code-signing controls, dependency pinning, and release-process review. That pairing aligns better with the SSDF and the actual threat data than “publish an SBOM and move on.”
The recent incident record reinforces the point. MOVEit showed how a single file-transfer product can cascade through supply chains. Okta’s support-system incident showed how an identity provider’s support environment can create downstream account risk. Snowflake showed the role of weak customer-side identity controls and contractor systems in a cloud-centered campaign. Change Healthcare showed how concentration risk at a critical service provider can become sector-wide operational disruption. These are not one category of failure. They are different forms of trust-path collapse.
If the lesson from 2024–2026 data is that trust paths are the problem, then the obvious response is validation. TPRM cannot rely on questionnaires, certificates, and security ratings alone when vendors touch production systems, sensitive data, APIs, cloud roles, software pipelines, or identity systems. NIST SP 800-115 exists for a reason: organizations need structured technical testing and assessment to determine whether controls actually work. NIST CSF 2.0 and PCI third-party guidance point in the same direction by emphasizing due diligence, evidence, monitoring, and role clarity throughout the relationship.
| Evidence type | What it proves | What it does not prove |
|---|---|---|
| Security questionnaire | Vendor claims and control descriptions | Real exploitability |
| SOC 2 report | Assessed controls over a period | Your specific integration is safe |
| ISO 27001 certificate | ISMS scope and certification | Technical exposure is absent |
| Security rating | External posture signals | Internal control quality |
| Pentest summary | Tested scope and findings | All vendor systems are safe |
| Retest letter | Specific fixes verified | Future releases remain safe |
| SBOM | Component visibility | Exploitability or secure configuration |
| API test | Integration-level weaknesses | Vendor-wide risk |
That is not an argument against questionnaires or assurance reports. It is an argument for using them correctly. They are triage tools and evidence inputs. They narrow where you need deeper testing. They do not replace access review, cloud trust review, API authorization testing, portal testing, or remediation verification. Verizon’s third-party findings, Mandiant’s credential-based Snowflake case work, and CSA’s SaaS privilege data all support that conclusion.
| Testing type | Best for | What it validates |
|---|---|---|
| Vendor security assessment | High-risk suppliers | Evidence quality and control gaps |
| Web app pentest | Vendor portals and customer-facing apps | Auth, session, business logic, data exposure |
| API pentest | Partner APIs and integrations | BOLA, auth, rate limits, excessive data exposure |
| Cloud review | Vendor/cloud trust relationships | IAM, storage, logging, network exposure |
| SaaS/OAuth review | SaaS apps and connected apps | Scopes, grants, SSO, admin access |
| Third-party access review | Contractors, MSPs, support accounts | Least privilege and offboarding |
| SCA/SBOM review | Software supply chain | Dependency visibility and known flaws |
| CI/CD review | Build and deployment chain | Secrets, tokens, release integrity |
| Segmentation testing | Vendor VPN, MSP, and remote access paths | Whether vendor access can pivot to sensitive systems |
| Red team assessment | Mature programs | End-to-end vendor-compromise attack chains |
| Retesting | Remediated findings | Verified closure |
The testing priority should follow exposure, not fashion. If a vendor has an OAuth integration into collaboration suites and CRMs, review scopes, service principals, and app consent flows. If a supplier maintains production systems, review privileged access, segmentation, and logging. If a partner API exchanges customer or payment data, test authorization, object-level access control, rate limiting, and data minimization. If a software supplier contributes code or packages, review dependencies, provenance, secrets, and release policies.
First 30 days. Build or refresh the vendor inventory. Identify vendors with sensitive data, privileged access, production access, payment access, or critical business dependency. Map data flows and system integrations. Enumerate SaaS apps, OAuth apps, SSO integrations, API keys, cloud roles, webhooks, support platforms, and MSP paths. Collect current evidence packages and flag vendors without incident-notification terms. Shadow SaaS and unmanaged integrations should be treated as inventory failures, not minor hygiene issues.
First 90 days. Tier vendors by sensitivity, access depth, business criticality, and integration complexity. Run vendor security assessments on high-risk providers. Review third-party access and privileges. Test partner APIs, vendor-facing applications, and cloud trust relationships. Where software suppliers matter, review dependencies, SBOMs, and CI/CD exposure. Create a remediation tracker and run at least one vendor-breach tabletop.
First 12 months. Move from annual questionnaires to risk-based continuous monitoring. Review high-risk vendor access quarterly. Reassess after major data-flow, contract, integration, or product changes. Add third-party metrics to executive reporting. Test incident notification and escalation workflows. Retest remediated issues and treat closure as unverified until evidence exists.
| Priority | Control | Third-party risk reduced | Validation method |
|---|---|---|---|
| Critical | Vendor inventory | Unknown exposure | Inventory review |
| Critical | Data flow mapping | Untracked sensitive data | Data mapping review |
| Critical | Third-party access review | Stale or excessive access | IAM/SaaS review |
| High | Vendor security assessment | Weak vendor evidence | Evidence review |
| High | API integration testing | Data leakage | API penetration testing |
| High | Cloud integration review | Overprivileged trust | Cloud IAM review |
| High | SBOM and SCA review | Software dependency risk | Supply chain review |
| High | Vendor incident tabletop | Slow response | IR exercise |
| Medium | Remediation retesting | False closure | Retest evidence |
| Metric | What it measures | Why it matters |
|---|---|---|
| High-risk vendor count | Critical supplier exposure | Prioritizes review effort |
| Sensitive-data vendor count | Vendors touching regulated data | Measures data exposure |
| Vendors with privileged access | Vendors with admin or production access | Measures blast radius |
| Vendor MFA/SSO coverage | Identity protection | Reduces account compromise |
| Stale vendor accounts | Offboarding gaps | Reduces unauthorized access |
| API integrations tested | Partner API coverage | Reduces data leakage |
| Critical vendor findings age | Time issues remain open | Measures remediation speed |
| Retest pass rate | Fixes verified | Prevents false closure |
| Vendors with current evidence | SOC 2, ISO, pentest, security docs | Improves audit and buyer readiness |
| Incident notification SLA coverage | Contracted response terms | Improves breach response |
The value of these metrics is that they speak to both operators and executives. They let security teams prioritize effort by exposure, while giving boards and risk committees evidence that third-party cyber risk is being reduced in measurable ways. They also map directly to current regulatory and customer expectations around readiness, disclosure discipline, and supplier oversight.
The most useful 2026 statistics are the ones that connect exposure to action: Verizon’s 48% (2026 DBIR) third-party breach involvement, IBM’s rise in large supply-chain and third-party compromises, CSA’s SaaS oversharing and privilege findings, Traceable’s API-breach data, and software supply chain malware data from Sonatype and GitHub. Together, they show that third-party risk is now driven by access depth, connected systems, and dependency trust, not vendor count alone.
Third-party risk is the exposure created when an organization relies on external vendors, partners, suppliers, contractors, cloud services, SaaS tools, processors, or software components. It includes security, privacy, resilience, contractual, regulatory, and reputational risk. NIST and ISO both frame supplier relationships as sources of risk that must be managed across acquisition, integration, operation, and offboarding, not just at contract signature.
Third-party risk management is the process of identifying, assessing, prioritizing, monitoring, and reducing risk from vendors and dependencies over the full relationship lifecycle. In 2026, mature TPRM includes inventory, criticality tiering, data mapping, access review, contractual requirements, security evidence review, incident coordination, remediation tracking, and technical validation for high-risk integrations. That approach aligns closely with NIST CSF 2.0 and NIST SP 800-161.
Vendor risk management matters because modern organizations do business through external systems. Vendors can access regulated data, administer critical systems, process payments, support customers, and connect through APIs, OAuth, SSO, or cloud roles. When those trust paths fail, the impact can extend to breaches, downtime, customer notifications, regulatory review, and lost trust. Real incidents involving Okta, Snowflake, and Change Healthcare show that downstream impact can be severe.
A third-party data breach is a security incident in which a vendor, service provider, cloud platform, processor, or other external dependency becomes the path through which your data is exposed, accessed, exfiltrated, or misused. Sometimes the vendor itself is breached. Sometimes the problem is your integration design, weak identity controls, or supplier-held credentials. Snowflake and Okta are good examples of how different those paths can look in practice.
Verizon’s 2026 DBIR found third-party involvement in 48% of breaches, up from 30% in the 2025 edition. SecurityScorecard’s 2025 report linked 35.5% of 1,000 breaches from 2024 to third-party access, and 41.4% of ransomware attacks in that sample involved third-party access. The figures differ because the datasets and definitions differ, but both show that roughly one-third to one-half of breaches now involve a vendor or partner.
A vendor security assessment is the structured review of a third party’s security posture, access model, integration design, compliance evidence, incident responsibilities, and remediation maturity. A strong assessment asks what data the vendor touches, what privileges it has, how identities are managed, what other processors it relies on, and what evidence proves relevant controls were assessed. For higher-risk vendors, that should include technical validation and retesting.
Vendor risk usually refers to the risk posed by a specific third party that provides a service to your organization. Supply chain risk is broader. It includes vendors, software suppliers, build and release tools, cloud dependencies, identity providers, and downstream or upstream dependencies. Software supply chain risk is narrower still and focuses on packages, components, CI/CD, provenance, and release trust. NIST SP 800-161 and SSDF help separate those layers.
SaaS vendors create third-party cyber risk through data access, misconfiguration, oversharing, admin roles, tokens, OAuth grants, APIs, support tooling, and non-human identities. CSA’s 2025 survey found frequent data oversharing, unmanaged uploads to unauthorized SaaS apps, and widespread concern about overprivileged API access. In practice, SaaS risk is often less about the existence of the app and more about the permissions, data paths, and governance around it.
Software supply chain attacks can place malicious or vulnerable code inside trusted delivery paths such as packages, dependencies, update channels, build systems, and CI/CD pipelines. That can expose production systems even when the organization did not directly “choose” the malicious artifact. Sonatype’s malicious-package data and GitHub’s malware-advisory trend show that this is not theoretical. The business effects include product compromise, customer impact, emergency patching, and trust erosion.
Organizations reduce third-party risk by maintaining a current vendor inventory, mapping data flows, controlling and reviewing vendor access, tiering vendors by exposure, validating high-risk APIs and cloud integrations, requiring better incident notification terms, reviewing software dependencies, and retesting remediated issues. Frameworks help, but the most effective controls are the ones tied to real access paths and evidence that controls were tested, not only documented.
The most effective testing depends on exposure. High-value options include vendor security assessments, web application penetration testing, API penetration testing, cloud security review, SaaS and OAuth review, third-party access review, SCA and SBOM review, CI/CD review, segmentation testing, incident-response tabletop exercises, continuous penetration testing, and remediation retesting. NIST SP 800-115 supports this validation-first model by treating technical testing and assessment as core security activities.
The highest-risk vendors combine sensitive data with deep access: MSPs and IT providers with admin tools, cloud and identity providers, payment processors, HR and payroll vendors, CRM and help-desk platforms, software suppliers in your build chain, and contractors with network access. Rank them by data sensitivity, access depth, business criticality, and how they connect to your environment.
No. Questionnaires are useful for screening and tiering, but they are self-attested and point-in-time. They do not prove that vendor accounts are least-privileged, that partner APIs enforce authorization, that shared cloud storage is private, or that segmentation works. High-risk vendors need access reviews, technical testing, and retest evidence.
Review high-risk vendor access at least quarterly and test critical vendor-connected systems at least annually, plus after major changes to authentication, network access, APIs, cloud permissions, or data flows. New integrations should get an access review and security validation before they reach production.
Third-party risk in 2026 is about validating the full vendor exposure chain: vendor inventory, data flows, SaaS access, API integrations, cloud roles, software dependencies, privileged access, incident visibility, remediation quality, and retest evidence. The organizations that perform best here do not confuse certificates with safety or questionnaires with closure. They use those inputs to decide where to verify, where to test, and where to keep monitoring. DeepStrike helps organizations validate third-party risk through web application, API, and cloud penetration testing, red team assessments, continuous penetration testing, dark web monitoring, weekly vulnerability scanning, attack surface management, and remediation retesting.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
This article prioritizes official reports, standards bodies, primary incident disclosures, and well-established industry research. Statistics are labeled by data type to distinguish between third-party benchmarks, general breach benchmarks, SaaS benchmarks, API survey data, software supply chain benchmarks, and case-study evidence. Where a source is not third-party-specific, it is used as context rather than as a direct proxy for vendor risk.
• Verizon, 2025 Data Breach Investigations Report.
• Verizon, 2026 DBIR landing page and top takeaways.
• IBM, Cost of a Data Breach Report 2025.
• IBM, Cyberthreats in 2026: X-Force and industry experts weigh in.
• IBM, X-Force Threat Intelligence Index 2026 newsroom summary.
• Cloud Security Alliance, State of SaaS Security Report 2025.
• Traceable with Ponemon Institute, 2025 State of API Security.
• Cloudflare, 2024 API Security and Management Report.
• Sonatype, 2026 State of the Software Supply Chain.
• GitHub, A year of open source vulnerability trends.
• Google Cloud / Mandiant, UNC5537 Targets Snowflake Customer Instances for Data Theft and Extortion.
• Okta Security, Unauthorized Access to Okta’s Support Case Management System.
• HHS OCR, Change Healthcare Cybersecurity Incident FAQ.
• NIST, Cybersecurity Framework 2.0 and supply-chain quick-start material.
• NIST, SP 800-115 Technical Guide to Information Security Testing and Assessment.
• SEC, cybersecurity incident disclosure guidance.
• PCI SSC, Third-Party Security Assurance and Connected-to Service Providers guidance.
• ISO, ISO/IEC 27036 supplier relationship guidance summary.
• SecurityScorecard, Global Third-Party Breach Report (2025 edition, 2024 data).
• Akamai, 2026 API Security Impact Study.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
