June 23, 2026
Updated: November 6, 2026
Federal, state and local government cyber attack and data breach statistics for 2026, the biggest government data breaches since 2024, ransomware trends, and the controls that would have stopped them.

Mohammed Khalil
Short answer: In the latest government cyber breach statistics, U.S. federal agencies reported 32,211 cybersecurity incidents in FY2023, 11 of them major (OMB's FISMA report). Ransomware keeps climbing: Comparitech counted 374 attacks on government bodies worldwide in 2025, up 27%, and 187 in the first half of 2026, 58 of them in the United States. The largest recent government data breaches include the Defense Manpower Data Center (about 3.05 million people), government contractor Conduent (about 62 million people in the HHS breach portal) and the City of Columbus, Ohio (about 500,000 residents).
Government cybersecurity breach statistics for 2026 show that cyber risk in federal, state, and local agencies is driven by ransomware, data breaches, phishing, credential theft, legacy systems, public-facing portals, cloud/SaaS exposures, third-party vendors, contractors, remote access, public APIs, and generally limited evidence of control testing. Recent data indicate that federal agencies report tens of thousands of security incidents annually (32,211 in FY2023) and that ransomware against government keeps rising: Comparitech counted 374 ransomware attacks on government bodies worldwide in 2025, up 27%, and 187 more in the first half of 2026. Government breaches are not just IT failures – they can expose citizen records (names, SSNs, health and benefits data, tax files, law enforcement and court records, voter or permit data) and disrupt core public services (emergency communications, courts, payroll, benefits, utilities, health systems and more).
This article compiles publicly available 2024–2026 data and research. Each statistic is labeled by data type so that government-specific evidence is not conflated with broader breach, ransomware, cloud, identity, or general public-sector benchmarks. We distinguish between federal, state/local, public-sector-wide, and specialized statistics. Practical analysis follows each section to highlight how these figures translate into security and compliance gaps. Wherever possible, we cite authoritative sources like CISA, DHS, GAO, FBI IC3, Verizon, Microsoft, CrowdStrike, Sophos, etc., and we rely on real incidents and industry reports.
This 2026 guide combines government cybersecurity research, public sector breach data, ransomware reports, federal and state/local guidance, compliance resources, breach-cost benchmarks, threat intelligence, and public incident case studies. Each statistic is labeled by data type so broader cybersecurity statistics, including general breach, ransomware, cloud, and identity benchmarks, are not treated as government-only evidence. Where a statistic is not government-specific, it is used only as context for public sector cybersecurity and control-validation decisions. Source links point to official report pages or source hubs where available.
| Statistic | Data type | What it shows | Government cybersecurity implication | Source |
|---|---|---|---|---|
| 32,211 incidents reported by federal agencies (FY2023), up 9.9% | Federal benchmark (OMB FISMA report) | High volume of reported incidents; OMB rated 99% as unsubstantiated or inconsequential | Detection volume is high; the few serious incidents are what testing must prevent | OMB FISMA FY2023 report |
| 11 major federal incidents (FY2023) | Federal benchmark (OMB FISMA report) | Eleven incidents met the 'major incident' threshold | Even well-resourced federal agencies suffer significant breaches | OMB FISMA FY2023 report |
| Email/phishing: 19.2% of federal incidents (FY2023), #2 vector | Federal benchmark (OMB FISMA report) | 6,198 phishing incidents, behind improper usage (38%) | Email and credential attacks are major entry points; agencies need MFA and detection | OMB FISMA FY2023 report |
| 2.8M people in an HHS/CMS contractor ransomware incident; 1.88M in a zero-day exploited at two HHS contractors (FY2023) | Case study (FISMA major incidents) | Large citizen data exposures through contractors | Vendor and contractor security directly determines citizen data exposure | OMB FISMA FY2023 report |
| 374 ransomware attacks on government bodies in 2025 (196 confirmed), up 27% | Public-sector ransomware count (worldwide) | Ransomware against government rose again in 2025 | Agencies need proactive defenses and tested recovery | Comparitech 2025 |
| 187 ransomware attacks on government in H1 2026 (89 confirmed); 31% in the US | Public-sector ransomware count (worldwide) | Roughly one attack a day in early 2026 | Ransomware remains a constant public-sector threat | Comparitech H1 2026 |
| Public Administration: 2,410 confirmed breaches, 69% financially motivated, 33% espionage (DBIR 2026) | Government-specific breach benchmark | Exploitation was the top initial access vector (40%) in public-sector breaches | Patch management and testing of internet-facing systems are top priorities | Verizon DBIR 2026 |
| 48% of breaches involve ransomware (DBIR 2026) | Breach benchmark (all sectors) | Ransomware appears in nearly half of all data breaches, up from 44% | Governments need both prevention and tested incident response/backups | Verizon DBIR 2026 |
| Third-party involvement in 48% of breaches, up 60% (DBIR 2026) | Supply-chain breach trend (all sectors) | Breaches involving vendors or contractors are rising sharply | Vendor/contractor security must be validated | Verizon DBIR 2026 |
| Only 26% of CISA KEV-listed vulnerabilities fully remediated in 2025, down from 38% | Vulnerability benchmark (all sectors) | Median time to full fix rose to 43 days | Known exploited flaws stay open too long; agencies need tracked remediation and retesting | Verizon DBIR 2026 |
| Government share of observed threat activity: 27% (2026), up from 17% (2025) | Threat intelligence (Microsoft) | Government is now the most impacted sector in Microsoft's data | Public sector holds sensitive data and critical functions, making it a prime target | Microsoft Digital Defense Report 2026 |
| Government Facilities: 233 ransomware complaints in 2025 (220 in 2024) | Critical infrastructure benchmark (FBI IC3) | Government ranked 4th among critical infrastructure sectors in 2025 (3rd in 2023 and 2024) | State and local agencies need greater ransomware resilience | FBI IC3 2025 |
| $2.5M median ransom paid by state and local government (2025) | Ransomware survey (Sophos) | Highest median payment of any sector in Sophos' 2025 study; in the 2026 edition, 72% of state and local government organizations paid, the highest rate of any sector | Payment pressure is high; tested recovery reduces it | Sophos State of Ransomware 2025 and 2026 |
| 567 GAO cybersecurity recommendations not yet implemented (of 1,610 since 2010) | Federal oversight (GAO) | Persistent gaps in federal cybersecurity controls | Agencies need evidence that fixes were made and verified | GAO-24-107231 |
| Illinois DHS (705,017 people, privacy-setting error) and Minnesota DHS (~304,000 people, excessive user access) breaches, disclosed Jan 2026 | Case-study evidence | Misconfiguration and over-broad access exposed benefits data | Real examples of how configuration and access-control gaps expose public benefits data | BleepingComputer; GovTech |
| Nevada statewide ransomware attack (Aug 2025): 28-day recovery, no ransom paid | Case-study evidence | Intrusion began months earlier via a fake admin tool; backups were deleted | Shows why backup protection and early detection matter | State of Nevada after-action report |
After viewing the table above, it’s clear that government cyber risk cannot be measured only by incident counts. Agencies and jurisdictions vary widely in how much sensitive citizen data they hold, how critical their services are, and how well-tested their controls are. For example, a single breach of a state benefits portal that exposes personal health or tax records may be far more damaging to citizens than multiple minor incidents elsewhere. Key risk factors include the type and volume of citizen data (IDs, health, tax, criminal records), reliance on legacy systems, exposure of public portals and APIs, cloud/SaaS sharing, third-party access, staffing levels, backup maturity, and incident response readiness.
Broad industry statistics (like "X% of all breaches") are useful context but should be treated carefully. Only when sources explicitly separate “government” or “public sector” data should we assume applicability to agencies. For instance, the 48% ransomware rate from the Verizon DBIR is global across all sectors. However, combined with reports like FBI/FISMA, we know ransomware is also rampant in government (Government Facilities ranked among the top critical infrastructure sectors for ransomware complaints to the FBI, and Comparitech counted 374 attacks on government bodies worldwide in 2025). The most actionable statistics tie directly to fixable gaps. For example, the fact that vulnerability exploits are now the leading breach vector aligns with patching and penetration testing priorities. The surge in third-party incidents highlights the need for vendor security reviews and third-party access audits. And despite high MFA adoption in some sectors, any gaps in identity controls can let credential theft slip in (as phishing was the #2 vector in federal incidents).
In summary, government cybersecurity risk is shaped by the sensitivity of exposed data and the effectiveness of defenses. Ensuring MFA on all privileged accounts, continuously scanning and patching internet-facing systems, testing public web portals and APIs, auditing cloud permissions, validating backups, and conducting ransomware tabletop exercises are among the most direct actions to reduce the vulnerabilities highlighted by these statistics.
The statistics above are counts. This list shows what the biggest recent government data breaches actually looked like, ordered by people affected where a public count exists. It includes one government contractor, because a vendor breach exposes citizen records just as surely as an agency breach. For cross-industry figures, see our data breach statistics.
| Breach | When | Level | People affected | Attack path (as publicly reported) | Control it tests |
|---|---|---|---|---|---|
| Conduent (contractor running services for state programs) | Attack January 2025; counts grew through February 2026 | State programs via vendor | About 62M in the HHS breach portal (10.5M in the Oregon filing alone) | Intrusion into the contractor; names, SSNs, health insurance and medical data exposed | Vendor security evidence and breach-notice terms |
| Defense Manpower Data Center (DoD) | Found July 16, 2026; letters from September 2026 | Federal | About 3.05M (2.76M living, 294,000 deceased) | Vulnerability in a file-sharing system; unencrypted PII accessed from October 2025 | Patching and testing of file-transfer servers; encryption at rest |
| Illinois Department of Human Services | Disclosed January 2026 | State | 705,017 | Privacy-setting error exposed benefits data | Configuration review of shared data |
| City of Columbus, Ohio | Attack July 18, 2024; notices November 2024 | Local | About 500,000 | Rhysida ransomware with data theft (6.5 TB claimed) | Backup protection and egress monitoring |
| Minnesota Department of Human Services | Disclosed January 2026 | State | About 304,000 | Excessive user access to benefits data | Access reviews and least privilege |
| City of Suffolk, Virginia | February 2026 | Local | 157,725 | Ransomware; Cloak claimed 2.5 TB stolen | Ransomware readiness and data minimization |
| City of Middletown, Ohio | Incident July 2025 | Local | 123,791 notified | Cyber incident with data theft | Detection and incident response |
| U.S. Department of the Treasury | December 2024 | Federal | Not disclosed (workstations and unclassified documents) | Stolen key for vendor BeyondTrust's remote-support service; China state-sponsored actor | Third-party remote access |
| State of Nevada | August 2025 | State | No mass-notification count; 28-day recovery, no ransom paid | Fake admin tool months earlier; backups deleted | Early detection and backup isolation |
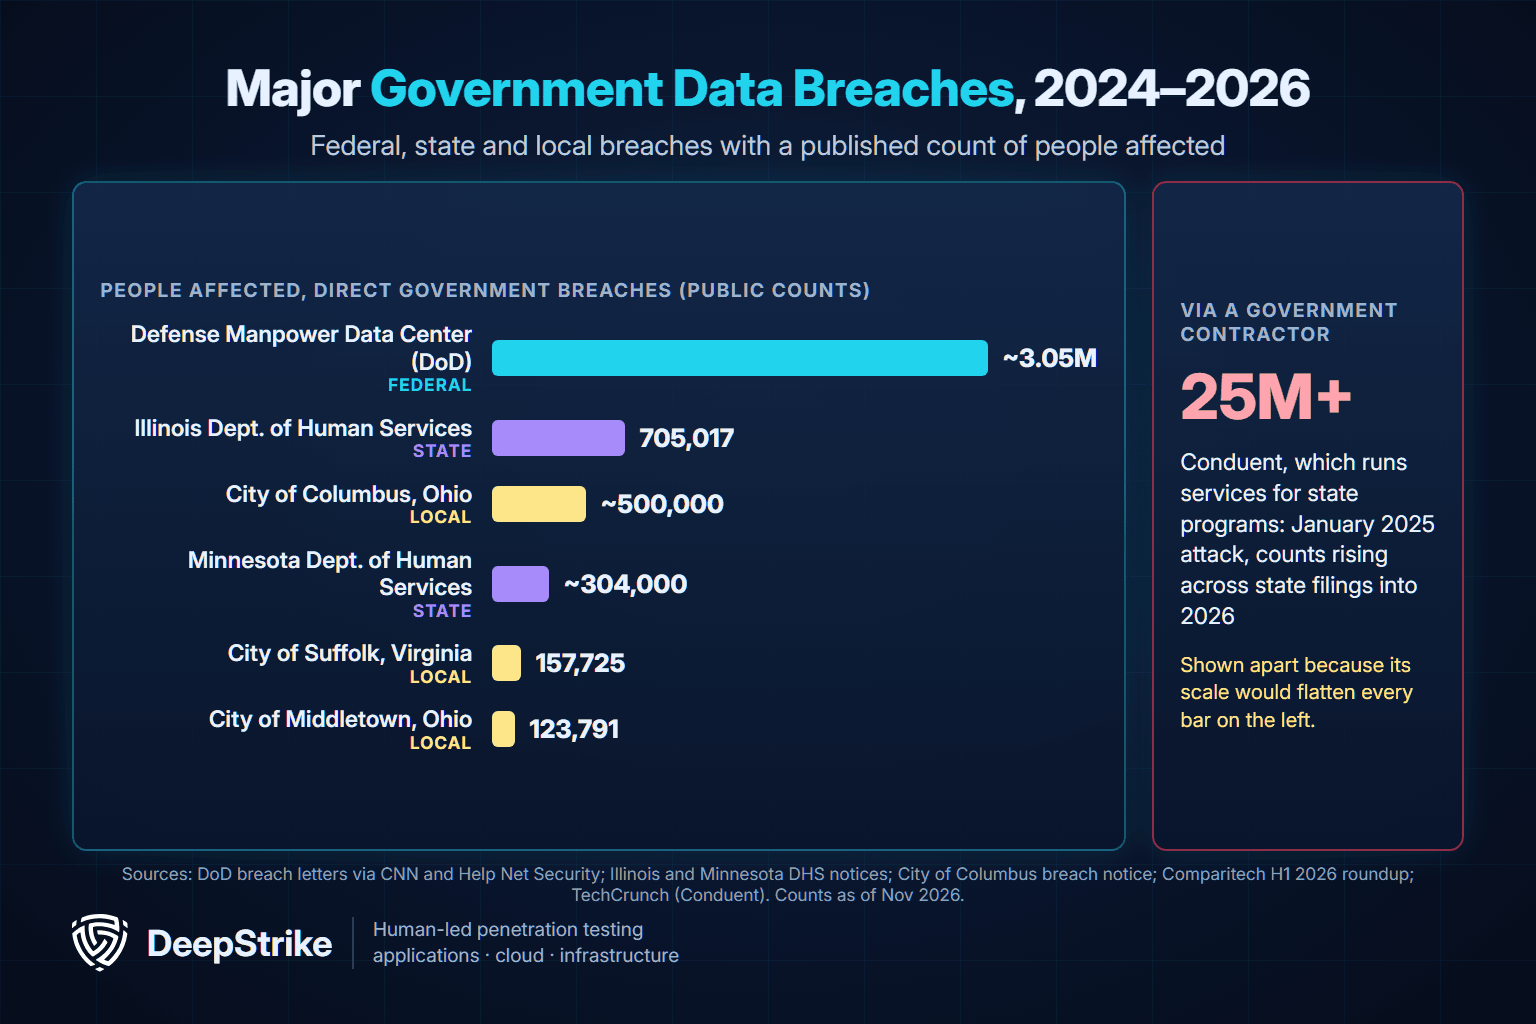
Sources: DMDC figures from Help Net Security (citing CNN and the breach letters); Conduent total from the HHS breach portal, with earlier state-filing counts from TechCrunch; Columbus from Comparitech's report on the city's breach notice; Suffolk and Middletown from the Comparitech H1 2026 government roundup; Treasury from TechCrunch on the department's letter to Congress; Nevada from the governor's after-action release. Illinois and Minnesota figures match the case-study row in the statistics table above.
Three patterns repeat. First, vendors: Conduent and the Treasury intrusion both came through a third party, which fits the rise in third-party breaches. Second, configuration and access: the Illinois, Minnesota and DMDC exposures came from a setting, an access grant or an unpatched file-sharing system, not from novel malware. Third, ransomware with data theft keeps hitting cities and states (Columbus, Suffolk, Saint Paul, Nevada), where the damage is both a breach notice and days or weeks of lost services. Each of these is a control that can be tested before an attacker tests it.
Cities and counties carry most of the U.S. count. Comparitech's first-half 2026 roundup recorded 58 ransomware attacks on U.S. government entities (31% of 187 worldwide), 33 of them confirmed by the victim, down 23% from 75 in the second half of 2025. The median ransom demand fell to $100,000 from $500,000. Named victims were mostly local: Suffolk, Virginia; Winona County, Minnesota (twice); Passaic County, New Jersey; Rusk County, Wisconsin; and Seal Beach, California, among others. Many small-town incidents never produce a public breach count, which is why trackers disagree. For ransomware across all sectors, see our ransomware statistics.
There is no single total, because each source counts something different. Federal agencies reported 32,211 incidents in FY2023, up 9.9% from the 29,319 that the same report gives for FY2022, and 11 met the "major incident" threshold. That is OMB's latest government-wide FISMA count we could find as of November 2026. The FBI IC3 logged 233 ransomware complaints from the Government Facilities sector in 2025. Comparitech tracked 58 ransomware attacks on U.S. government bodies in the first half of 2026, roughly two a week. Read these as incidents, complaints and attacks respectively; they should not be added together.
Public sector cyber attacks include ransomware, exploitation of internet-facing systems, phishing and credential theft, business email compromise, public portal abuse, API authorization flaws, cloud misconfiguration, contractor compromise, and third-party service disruption. These attacks can expose citizen records and interrupt services even when the initial entry point is a vendor account, cloud setting, public-facing form, or legacy remote access path.
For public-sector leaders, the practical question is not only how many attacks happen. It is which systems are exposed, what citizen data is reachable, whether public services can continue during an incident, and whether control evidence proves that remediation worked. This is why the article separates federal, state/local, ransomware, breach, compliance, and case-study evidence instead of treating all cybersecurity statistics as the same.
Government data exposure is the business impact: sensitive public records, public portals, cloud files, vendor systems, and agency databases become reachable to unauthorized users. The most useful public sector breach statistics are the ones that connect the attack path to a control that can be tested: MFA for identity attacks, web/API testing for portals, cloud review for oversharing, vendor access review for contractor risk, and retesting for remediation quality.
A government cybersecurity breach is any security incident affecting a federal, state, local, tribal, or public-sector entity (including public health, safety, utilities, courts, education-run agencies, election offices, or their service providers). It includes unauthorized access, ransomware, data theft, account compromise, phishing, data leakage, cloud misconfiguration, public portal compromise, third-party breach, contractor/managed-service compromise, or operational disruption. Key examples:
Distinctions: “Government cybersecurity” broadly covers the IT and OT security of government operations. “Public sector cybersecurity” includes all government levels (federal, state, local, tribal, educational institutions receiving public funds) and government-run services. “Federal cybersecurity” refers specifically to U.S. federal agencies (often under FISMA/OMB/CISA mandates). “State and local cybersecurity” covers state governments, cities, counties, municipal utilities, etc. “Government ransomware” and “public sector ransomware” often refer to attacks on these entities. “Citizen data exposure” emphasizes personal data risk. “Public service disruption” is the operational impact (e.g. courts, emergency services). “Government compliance risk” relates to meeting FISMA, FedRAMP, CMMC, CJIS, HIPAA, state privacy laws, etc. “Contractor/vendor breach” is specifically when a partner’s breach affects government data or systems. Finally, “cybersecurity awareness” is only one piece; control validation (testing) is needed to prove security.
Public sector cybersecurity spans federal agencies, state departments, local governments, counties, tribal nations, public schools and colleges, law enforcement, courts, public health and safety departments, utilities, election offices, and public-sector vendors. It must protect not only networks and data centers, but also public services and citizen trust. Common risk drivers include:
Public sector defense must balance security and service continuity. For example, agencies operate 24/7 services (911, emergency response) and citizen-facing portals where downtime can have immediate public impact. Attackers target public sector because it holds valuable data and critical infrastructure and may be perceived as having slower patch cycles or higher pressure to pay ransom. In FBI IC3 data, Government Facilities was the third most-targeted critical infrastructure sector by ransomware complaints in 2023 and 2024, and fourth in 2025 with 233 complaints.
| Public sector environment | Main exposure | Common weakness | Validation method |
|---|---|---|---|
| Federal agency | Citizen records, mission-critical systems, contractor/vendor accounts | Complex compliance demands; many legacy or interlinked systems | FISMA/NIST control validation; 3PAO assessments; penetration testing of cloud and key apps |
| State agency | Benefits/tax programs, health data, DMV records, identity databases | Public portals; large centralized databases; dated tech | Web/API pentesting; cloud security assessments; access reviews |
| Local government (city/county) | Municipal services, payroll, utility billing, local police data | Limited IT staff; many legacy on-prem systems | External attack surface scans; application pentests; network segmentation reviews |
| Public health agency | Electronic health/benefits data, vaccine records, hospital systems | Sensitive PHI with vendors; hybrid IT/OT | PHI compliance audits; cloud/app security reviews; EHR vulnerability assessments |
| Court system | Case records and filings; court management systems | Public document access; inconsistent access controls | Public portal testing; application authorization review; encryption checks |
| Public utility (water, power) | Operational controls (SCADA), customer data (billing) | Remote access points; weak OT/IT separation | Network segmentation audit; OT/IT penetration testing; backup restoration tests |
| Election office | Voter registration systems, voting technology (non-voting computers) | Third-party vendors (ballots, apps); remote patches | Vendor/software security review; audit trail testing; compliance pen-testing |
| Public-sector vendor (software provider) | Government data hosted offsite; integration APIs | API vulnerabilities; multi-tenant cloud config | Contractual security evidence; independent security assessment of services |
Interpretation: This matrix highlights how exposures vary by environment. Federal systems may have better budgets but more regulations (NIST/FISMA) and legacy interconnections. State/local entities often run vital but older systems (tax, utilities) with fewer resources. Regardless of level, validation methods (penetration tests, cloud reviews, access audits, etc.) are needed to ensure each environment’s specific weaknesses are found and fixed.
Government data breaches can leak citizen records that are hard to reverse or mitigate. Types of citizen and agency data at risk include:
Not all data has equal impact. For example, a leaked Social Security number or medical record can haunt a citizen for decades. Agencies must classify and minimize data, enforce encryption, and regularly review who has access. Below is a risk matrix:
| Government data type | Why it is sensitive | Breach impact | Control to validate |
|---|---|---|---|
| Citizen identity data (names, DOB, SSNs, license IDs) | Permanent identifiers for identity and fraud | Identity theft, long-term fraud, privacy violation | Encryption-at-rest, MFA on identity systems, IAM audits |
| Tax and benefits data | Financial and eligibility information (income, claims) | Fraud, benefits theft, financial harm | Web/API security testing on tax/benefits apps; input validation and rate limiting |
| Public health data | Medical records, health demographics | Privacy/legal compliance (HIPAA-like); identity risk | Data encryption, strict access controls, regular privacy/security audits |
| Law enforcement records | Sensitive investigations, warrants, tips | Compromises cases, endangers witnesses, undermines trust | Segmentation of network; audit logs review; CJIS encryption and logging |
| Court records | Case documents, filings | Damage to confidentiality, mistrust in justice | Public portal access testing; data redaction checks; audit of public query interfaces |
| Employee records | Payroll, performance, background checks | Insider threat, credential theft, HR data leaks | IAM controls for HR systems; regular user access reviews; secure account management |
| Utility/customer data | Billing, service account info | Fraud (bill payments); service disruption if manipulated | Cloud/app configuration review; network segmentation; backup restore tests |
| Payment/financial data (payments, vendor invoices) | Bank or card data linked to fees/taxes | Financial fraud, unauthorized charges | PCI DSS scope validation; secure payment portal testing; vendor screening |
| Login credentials (staff or citizen portal) | Keys to other systems; potential for takeover | Account takeover; lateral movement | MFA enforcement; session management review; phishing-resistance training |
Interpretation: This table shows the breadth of citizen data at stake. For each data type, agencies should identify who has access, how it’s protected, and how they can validate those protections. For example, if tax records are processed through a web portal, that portal should undergo rigorous security testing. Employee and contractor accounts should be regularly audited for least privilege and protected with phishing-resistant MFA. Encryption and logging of sensitive datasets help in detecting breaches. Importantly, while awareness and policy are necessary, only evidence-backed controls (like regular pentesting and access reviews) ensure this data stays safe.
Ransomware in government is especially perilous because it often targets public services, not just data. A government agency encrypting citizen systems can delay critical operations. Ransomware impacts include:
| Ransomware impact | Government example | Why it matters | Validation method |
|---|---|---|---|
| System encryption | City/county resident portal or internal networks unavailable | Halts public services (payments, records lookup); citizen disruption | Regular backup restore testing; offline backups verification |
| Data theft/exfiltration | Sensitive PII/employee data stolen (e.g., utility customer lists) | Notification costs; privacy damage; identity fraud risk | Endpoint Detection and Response (EDR) and log auditing; data loss prevention (DLP) testing |
| Email outage | Agency-wide email system down | Coordination breakdown; delayed emergency alerts | Email continuity solutions; pen-test of messaging systems; simulate failover |
| Benefits/tax system locked | Eligibility/payment systems (Medicaid, unemployment) encrypted | Residents left without services; backlogs; political fallout | Business continuity plan (BCP) review; redundancies for critical systems |
| Court/justice disruption | Case management/CJIS systems offline | Delays in hearings, evidence processing; legal backlogs | Incident response (IR) tabletop exercises; segregated backups for critical law records |
| Utility operations disruption | Water treatment or power grid SCADA encrypted | Service outages; safety risks; public health impact | Network segmentation testing; OT/IT gap analysis; backup generator and failover drills |
| Extortion/pressure | Threat to publish stolen public data or hold services hostage | Public trust loss; pressure to pay; ransom negotiation | Ransomware tabletop exercise; clear IR plan; public communication strategy |
Interpretation: The matrix illustrates that ransomware in the public sector can impair critical community functions. Even “non-data” impacts like email or system outages erode public safety and trust. Double extortion (leak of citizen data combined with downtime) inflicts both privacy and operational damage. Mitigations must therefore span beyond patching or backups. For instance, having reliable, tested backups (and evidence of restore) is crucial: 69% of ransomware victims in Verizon's 2026 DBIR dataset did not pay, and tested backups are one factor that makes refusing payment possible. Similarly, conducting ransomware tabletop drills can improve decision-making during a siege. If courts or health systems depend on certain portals, those should be tested for resilience and isolated from main networks. In short, practical readiness (backups, segmentation, IR planning) is validated through testing, which is central to reducing the real-world harm of ransomware in government.
Federal agency cybersecurity is framed by standards like NIST SP 800-53, FISMA, OMB guidance, CISA directives, FedRAMP for cloud, CIRCIA incident reporting, Zero Trust mandates, and more. Compliance risk often boils down to evidence and testing. Common gaps include:
| Federal cybersecurity area | Why it matters | Common gap | Evidence to prepare |
|---|---|---|---|
| FISMA/NIST controls | Federal baseline for confidentiality, integrity, availability | Controls documented but not tested annually (weak assurance) | Security Assessment Reports (SARs), POA&M updates, 3PAO reports |
| FedRAMP cloud systems | Cloud authorization ensures baseline security for agency data | Scope creep or outdated monitoring (e.g. missing continuous monitoring results) | Up-to-date FedRAMP package, recent penetration test report, continuous monitoring data |
| Zero Trust | Mandated identity and access modernization (per EO 14028 et al.) | Legacy accounts, shared credentials, weak segmentation | MFA logs, identity access reviews, micro-segmentation evidence |
| CISA directives (e.g. KEVs) | Binding operational requirements for all agencies (known exploited vulnerabilities) | Slow remediation of known risks; lack of timeliness in patching | Vulnerability scan reports, patch compliance metrics, POA&Ms |
| Incident response / reporting | Where applicable, CIRCIA readiness may involve 72-hour covered cyber incident reporting and 24-hour ransom payment reporting, plus coordination with CISA. | IR playbooks exist but infrequently practiced; unclear roles | Tabletop exercise reports, incident logs, response plan documentation |
| Contractor access | Third-parties perform key functions; pose a big risk if compromised | Lack of least privilege or timely offboarding; Shadow IT contracts | Contractor access inventory, background check evidence, account review records |
| Vulnerability management | Critical to address known exploits swiftly | Slow remediation of known exploited vulnerabilities (across all sectors, the DBIR 2026 median time to full fix was 43 days) | Scans showing timely fixes, patches applied, vulnerability risk assessments |
Interpretation: Federal compliance frameworks exist to keep agencies accountable, but the evidence of security is what matters to auditors and regulators. For example, NIST 800-53 covers more than 1,000 controls and control enhancements, but GAO and OMB repeatedly find agencies that have written policies without corresponding test results or verification. FedRAMP-compliant agencies must have current assessments and pentest results for every cloud service; missing these can jeopardize an ATO. A common thread is that controls are often “checkboxed” without dynamic testing. Demonstrating actual security (via penetration testing, IR exercises, vulnerability scans) bridges that gap. Executive summaries of FISMA reports often highlight that detection has improved, but GAO warns continuous monitoring and patching need work. In practice, showing auditors a recent pentest report, proof of IR tabletop completion, or fresh vulnerability scan with patches applied is far more persuasive than a memo stating "MFA is enabled."
State and local governments often operate high-value services (tax collection, courts, utilities, social services, public safety) with far fewer cybersecurity resources than federal agencies. Common exposures include:
Security validation for state/local should therefore focus on practical, high-risk areas:
| State/local risk area | Example exposure | Public impact | Validation method |
|---|---|---|---|
| Resident portal | Online forms for permits, payments, property data | Data leaks (e.g. personal info), service interruptions | Web application/API penetration testing |
| Tax/benefits system | State/county tax filing systems, unemployment portals | Financial fraud, tax evasion, system downtime | Application/API penetration tests; input validation checks |
| Legacy systems | Outdated OS/ERP systems (e.g. old financial systems) | Known exploits, unpatched vulnerabilities | External/internal vulnerability scans; 3rd-party assessment of legacy apps |
| MSP/contractor access | Managed government networks by vendors, remote support tools | Broad compromise risk (one MSP breach hits many) | Review of vendor network access; offboarding process verification |
| Municipal utility | City water control systems, electric grid segments, smart meters | Service outage, billing fraud, safety hazards | Network segmentation review; OT/IT gap analysis; backup/restore drills |
| Public safety IT | Police records systems, dispatch/911 networks | Operational disruption, public safety slowdown | IR tabletop (simulate outage); penetration testing of CAD and record systems |
| Cloud collaboration | City email, file shares, teams (e.g. Office 365, Google Workspace) | Data leakage via over-sharing or phishing; OAuth compromises | Cloud configuration review (e.g. M365/Google security audit); phishing simulation |
| Small agencies (schools, libraries) | Like local government, but often with even smaller budgets | Often targeted as easy victim with data (student info, fines) | Regular vulnerability scans; community training; in-house pen tests |
Interpretation: State/local entities often resemble small and midsize businesses to attackers, as noted by security firms, yet hold very sensitive data (student, voter, health, tax). Because they may lack dedicated security staff, technical validation (penetration testing, AWS/Azure reviews for cloud, etc.) is a force-multiplier. For example, a city water utility may not realize a remote maintenance VPN is insecure until an external test reveals it. Similarly, resident portals should be tested for authorization flaws (for example, a portal test could reveal residents seeing others’ records). Shared services can amplify risk – one compromised managed service provider can affect several municipalities at once – so validating vendor controls is key. In short, prioritizing tests on systems that directly affect citizens (portals, tax systems, utilities, public safety networks) yields the highest impact for limited resources.
Modern government agencies increasingly rely on cloud platforms and public-facing applications, which introduce new risks. Common high-impact systems include:
| System | Common exposure | Breach path | Validation method |
|---|---|---|---|
| Microsoft 365 / Google Workspace | Overly permissive sharing (files, groups, sites); unchecked OAuth or add-ins | Phishing or stolen credentials to access email/files; OAuth token abuse; data exfiltration via cloud | Cloud security review (check sharing policies, apps, device access); identity access audit |
| Resident portal / public websites | Insecure authorization (BOLA), injection flaws, outdated frameworks | Attacker exploits web vulnerabilities to access records or inject malware | Web application penetration testing (auth, injection, session management) |
| Open data / GIS portals | Exposure of sensitive columns; unintentionally published internal data | Discovery of sensitive fields via misconfiguration or scraping | Data audit; content filtering review; penetration test with data exfil check |
| Benefits/permits platforms | Business logic flaws, API vulnerabilities | Exploit API endpoints or sequence logic to alter or steal application data | Application/API pentesting (including BOLA, unprotected APIs) |
| Court/justice portals | Authorization bypass (e.g. judge vs public views), missing encryption | Abuse of session handling to view others’ cases; attack on unencrypted fields | Portal penetration testing; encryption of data in transit at forms, logs |
| Cloud IAM/configurations | Unprotected admin accounts; broad permissions on cloud resources | Any admin credential lead to full cloud takeover or data access | Cloud configuration review (IAM roles, MFA enforcement, log audit) |
| Public APIs | Broken object level auth, excessive data in responses | Throttling or auth bypass returns entire database or PII | API penetration testing; fuzzing for data leaks and auth bypass |
| Remote access (VPN/RDP) | Exposed to internet; weak auth | Brute force, credential stuffing, or VPN exploit gains network entry | External network scan; testing MFA on VPN; patch verification of remote services |
Interpretation: Agencies must treat cloud apps and portals as high-risk attack surfaces. For example, a misconfigured Microsoft 365 group could leak sensitive citizen records via a shared file. Our stat table showed how frequently phishing and credential misuse occur, so ensuring that multi-factor authentication and conditional access policies cover cloud logins is critical. Similarly, public-facing APIs or portals – like a state unemployment API – should be pentested like any web app, because attackers can use automated tools to harvest data. Regular cloud security reviews (e.g. of AWS/Azure accounts), including checking for open storage buckets or excessive privileges, are part of the validation mix. Finally, because government data often flows between agencies via APIs or third-party systems, testing those integrations (via API pentests or vendor assessments) ensures there are no blind spots in data exchange.
Government agencies outsource many functions to third parties: SaaS vendors, cloud providers, systems integrators, managed service providers (MSPs), contractors, and public-sector software vendors. Any of these can become a breach point. Key points:
| Government third-party exposure | How it appears | Public sector impact | Validation method |
|---|---|---|---|
| SaaS vendor (cloud-based govt app) | Agency data hosted on vendor servers | Large-scale data exposure if vendor breached or misconfigured | Vendor security assessment; require FedRAMP/SOC 2; test sample app instance via pentest |
| Contractor access (IT support, consultants) | Admin tools, remote desktops for maintenance | Account takeover => lateral movement into sensitive data/systems | Review contractor accounts/permissions; enforce MFA; simulate contractor roles in pen-tests |
| MSP compromise (manages multiple agencies) | Elevated cloud or network access to agency estates | Broad exposure across multiple agencies if MSP hacked | Vendor/third-party audit; network segmentation; check for shared credentials |
| Cloud provider / configuration | Agency VMs, storage in Azure/AWS/GCP | Misconfigured buckets or security groups expose data or enable break-ins | Cloud configuration audit (IAM roles, security groups); periodic cloud pentest |
| Public-sector software vendor | Custom portals (e.g. permitting system), grant management platforms | Exploitable app vulnerabilities (SQLi, XSS) in critical apps | Contractual security testing; independent web/API pentesting on vendor software |
| Payment processor / e-pay | Online portals for taxes/fees | Financial account compromise or stolen payments | PCI DSS compliance check; vendor penetration test; transaction monitoring |
| API integrations (agency–vendor data feeds) | Data exchange APIs (e.g. HR, GIS, grants) | Excessive data flow or auth bypass | API penetration testing (check for data over-return, BOLA) |
Interpretation: Even if an agency locks down its own network perfectly, vendors and contractors are often the weakest link. Recent federal incidents (like the FY2023 zero-day exploited at two HHS contractors that exposed data on 1.88M people) underscore this point. Agencies should inventory all data flows and access points to third parties. For each vendor, they should insist on security documentation and ideally an independent pentest. For example, a city buying a new cloud permitting system should require the vendor to allow security testing of the deployed app or to supply up-to-date third-party audit reports. Regularly reviewing vendor “subprocessors” lists (e.g. cloud hosting, analytics tools) and tightening what data vendors can see will reduce surprises. In practice, technical validation means either assessing the vendor environment (with their permission) or requiring proof from them (reports, certifications). Given the surge in supply-chain attacks, treating vendor risk as a core part of security posture is essential.
Government agencies must often comply with multiple frameworks (NIST CSF/SP 800-53, FISMA, FedRAMP, CMMC for DoD partners, CJIS for law enforcement, HIPAA for health data, PCI DSS for payments, state privacy laws, grant and insurance requirements, etc.). However, compliance alone doesn’t guarantee security — it’s about having proof that controls work. Common evidence gaps include:
| Compliance/evidence area | Why it matters | Common gap | Evidence to prepare |
|---|---|---|---|
| NIST CSF / SP 800-53 | Security framework for controls and assurance | Controls documented, but no test results to verify effectiveness | Security Assessment Reports; system test outcomes; automated control validation tools |
| FISMA (federal) | OMB requires agencies to manage cyber risk (CIO metrics) | Continuous Monitoring (e.g. CSPM/alerts) lacking; incomplete metrics | Updated POA&Ms; evidence of continuous monitoring (scans, playbook updates) |
| FedRAMP (cloud) | Authorization of cloud services for federal data | Outdated package; missing pentest on cloud services used | Current FedRAMP ATO/ATOC documentation; CSP 3PAO pen test report |
| CJIS (law enforcement) | Protects criminal justice info (FBI policy) | Weak user background checks or access controls on LE systems | CJIS audit artifacts; audit log reviews; access justification records |
| HIPAA-adjacent (public health) | State health agencies handling PHI-like data | Gaps in encryption or breach notification planning | HHS/HIPAA audit trails; risk assessments; data classification docs |
| PCI DSS (payments) | Protects payment card processing, fees | Ambiguous scope (are payments handled by vendor or in-house?) | PCI reports or attestation from vendor; network segmentation proof |
| Cyber insurance / grants | Underwriters require controls claims | Insured agencies may overstate MFA or backup in applications | Documentary proof (MFA logs, EDR deployment evidence, backup test logs) |
| Vendor contract terms | Legal requirement to protect data via contracts | Lack of explicit security requirements (breach notification, audits) | Signed contracts with security addenda; proof of compliance with SLAs |
Interpretation: Audit findings often remark that agencies “claim” to do X, but without demonstrable records. For instance, saying “we have MFA” means nothing if an audit finds many non-administrative accounts with only passwords. FISMA auditors look for artifacts: runbooks, test results, screenshots of scanning tools, etc. Therefore, evidence collection is central: logs, test reports, spreadsheets of user permissions, annotated risk assessments. For FedRAMP, agencies using a cloud service must ensure the provider’s documentation is current and that any updates (e.g. new functionalities) undergo reauthorization. CJIS-required encryption (e.g. in-transit for law enforcement databases) must be verified via testing. In short, aligning with compliance frameworks is not just paperwork; it’s about embedding testing and documentation into the security program so that every claim is backed by proof.
A thorough government cybersecurity assessment must cover people, processes, and technology. Below is a practical checklist of high-impact areas. For each, key questions and evidence are suggested:
| Area | Assessment question | Evidence to collect |
|---|---|---|
| Governance & ownership | Who is accountable for cybersecurity risk and budget? | Org chart, roles/responsibilities, reporting cadence documentation |
| Data inventory | What citizen and agency data is stored where? | Data inventory, data flow maps, data classification policies |
| Citizen data classification | Are systems/data classified by sensitivity (PII, PHI, etc.)? | Classification policies, encryption usage, access control lists |
| Identity and access | Are all staff/admin/contractor accounts protected with MFA? | Logs showing MFA enabled for all privileged and remote access accounts |
| Cloud/SaaS | Are cloud files/groups/apps reviewed regularly? | Cloud security audit reports, configuration review logs (M365, AWS, etc.) |
| Public portals & apps | Can only authorized users access portal data? | Web/API pentest reports; pen test remediation plans |
| APIs & integrations | Are agency/vendor APIs enforcing proper auth and scopes? | API pentest reports; API schema/review documents |
| Vendors/contractors | Who has access to agency data/systems externally? | Inventory of vendors and subcontractors; completed vendor security assessments |
| Remote access | Are VPN/RDP/SSH and admin tools securely configured? | External vulnerability scan of perimeter; configuration review of remote services |
| Network & segmentation | Are critical systems segmented from internet/less secure zones? | Network diagrams; segmentation test results; firewall rule audit |
| Endpoint & device security | Are workstations/servers patched and monitored? | Asset inventory; EDR/XDR deployment status; patch scan reports |
| Backup & recovery | Can all critical systems and data be restored? | Backup logs, restoration test results, backup storage verification |
| Ransomware readiness | Are backups encrypted/offsite and is IR team prepared? | Incident response plan, tabletop exercise reports, backup protection audits |
| Incident response | Has a public-sector breach tabletop been performed? | Tabletop exercise report; post-exercise improvement plan |
| Compliance evidence | Are required controls documented and tested? | Audit reports, compliance checklists, POA&M close-out documentation |
| Security testing & remediation | Are portals, APIs, cloud, and external surface tested regularly? | Latest pentest reports and evidence of remediated findings (with retest results) |
Interpretation: This checklist makes the assessment actionable. For example, verifying "MFA on all accounts" often requires checking the IAM solution or Azure AD reports, not just assuming. Web application pentest reports should specifically cover citizen-data paths on public portals. Even for something like backup readiness, evidence might be a test record showing a key database was fully restored by IT from backup media. By collecting real artifacts (logs, reports, tests), agencies create a portfolio of evidence that satisfies compliance auditors, cyber insurance, and leadership alike. The gap in many agencies is not knowing what they need to prove; this checklist aligns questions with concrete evidence to gather.
First 30 days:
First 90 days:
First 12 months:
| Priority | Control | Government risk reduced | Validation method |
|---|---|---|---|
| Critical | MFA for all admins, staff, contractors | Prevents majority of account takeover attacks | Identity access review (covering 100% critical users) |
| Critical | Inventory & classify citizen data | Identifies unknown sensitive exposures | Data mapping documentation (with CIO approval) |
| High | Pen-test public portals and forms | Prevents unauthorized data access | External web/API penetration testing |
| High | Cloud sharing & OAuth review | Stops unintended data leaks | Cloud configuration audit; remove risky apps |
| High | Contractor/vendor access review | Mitigates third-party compromise | Access review and pruning; no shared secrets |
| High | Backup restore testing | Ensures recovery from ransomware | Documented restore test results |
| High | Incident response tabletop | Improves breach response | Tabletop exercise report; identified improvements |
| High | Compliance evidence inventory | Prevents audit blind spots | Gathered audit artifacts (training, scans, pentests) |
| Medium | Retest remediated issues | Confirms fixes are effective | Re-run scans/tests on previously failed controls |
Penetration testing in government is not a substitute for governance, policy, or legal work — it complements them by verifying technical controls. Systematic testing helps answer: “Can attackers actually exploit this system or is our control effective?” For public-sector agencies, the test focus should match exposures:
| Testing type | Best for | What it validates |
|---|---|---|
| Web application pentest | Citizen portals, public websites, payment or license systems | Authentication flaws, session handling, input validation, access control on data |
| API penetration testing | Agency-to-agency or vendor integrations, internal APIs | Broken object-level auth (BOLA), excessive data exposure, rate-limit bypass |
| Cloud security review | Microsoft 365, Google Workspace, Azure/AWS/GCP configs | IAM roles, sharing settings, logging, privilege escalation paths |
| Public portal testing | E-filing, permit, benefits, court systems | Cross-account or cross-privilege data access, DLP, correct encryption |
| Remote access testing | VPN gateways, RDP hosts, Citrix services | Exposed open ports; verify strong authentication; brute-force resistance |
| External attack surface review | Internet-facing infrastructure (DNS, firewalls, IoT) | Discovery of unexpected open services or outdated systems |
| Vendor access review | Contractor or MSP accounts and networks | Checks if vendor's compromise can reach sensitive assets (pivot testing) |
| Ransomware tabletop | Incident response process and communication | Decision-making effectiveness; gaps in roles, communications, or policies |
| Backup restore test | Recovery capability for critical systems | Ability to restore operations in a timely manner; validates actual backup data integrity |
| Remediation retesting | Any previously identified vulnerabilities | Confirms that fixes were correctly implemented and no longer exploitable |
Interpretation: Regular testing illuminates hidden risks. For instance, a pentest may uncover that a public health portal inadvertently allowed one patient to see another’s lab results (authorization flaw), prompting a patch. A cloud review might reveal legacy credentials that weren’t disabled, leading to a clean-up. Retesting is essential because agencies often “mark as fixed” without confirming – re-running the exploit ensures closure. In government, given the public impact, test findings should reach top leadership with clear remediation deadlines. Testing also builds a risk-based focus: continuous pentesting keeps assessment ongoing rather than annual.
Measuring progress requires the right metrics. The following are key indicators that reflect the security posture of a government organization:
| Metric | What it measures | Why it matters |
|---|---|---|
| MFA coverage (% of staff/admins/contractors) | Percentage of accounts with phishing-resistant multi-factor authentication | Shows resilience against credential theft and BEC; critical first line defense |
| Privileged account count | Number of highly privileged or shared admin accounts | Indicates potential blast radius if account compromised; fewer is better |
| Citizen data system inventory completeness | Extent of documented systems that store sensitive citizen data | Ensures no “unknown” database; reduces shadow-IT/data blindness risk |
| Critical vulnerability age | Time since critical CVEs were first detected on agency systems | Measures patch lag; shorter is better to reduce exploit window |
| Cloud oversharing findings | Number of issues like public buckets or over-shared docs found | Quantifies cloud configuration risks (data leaks) to be fixed |
| Public portal/API critical findings | Count of high-severity weaknesses in citizen-facing systems | Tracks web/application risk exposure affecting citizens’ data |
| Vendor/contractor access review coverage | Percentage of third-party accounts reviewed with least-privilege assurance | Reflects control over supply-chain risk; shows how much third-party exposure is vetted |
| Backup restore success rate | Percentage of key systems successfully restored during tests | Measures actual ransomware recovery capability; a low rate warns of untested backups |
| Mean time to remediate (critical flaws) | Average days to fix high-risk vulnerabilities after discovery | Shorter times reduce attack window; long times indicate resource gaps |
| Retest pass rate | Percentage of remediated vulnerabilities that pass re-testing | Ensures fixes are effective; prevents false “remediation” |
| IR tabletop completion rate | Frequency of conducting and updating incident response exercises | Regular drills correlate with faster, smoother real incident response |
| Compliance evidence completeness | Fraction of required audit artifacts (e.g. control tests, logs) available | Gauges readiness for audits/certifications; low score means likely audit findings |
Interpretation: These metrics help leadership see security posture quantitatively. For example, telling a mayor “95% of staff have MFA” is more concrete than “we encourage MFA usage.” Tracking privileged accounts shows where to apply zero-trust. Likewise, measuring backup restore success – say 90% of systems – gives a numeric goal for disaster recovery. Public agencies should track these in dashboards or scorecards. Over time, trends (e.g. declining vulnerability age or rising MFA coverage) demonstrate improvement. Crucially, combining metrics with context (e.g. “red=some servers fell during last restore test”) informs decisions. Tracking patch latency and MFA coverage is a better risk indicator than counting security tools.
These findings mean that for 2026, government agencies and their contractors must shift from reactive checklists to proactive validation: continuously scanning, testing, and exercising the systems that undergird citizen services.
Government breach statistics highlight rising ransomware and high incident volumes. In FY2023 U.S. federal agencies reported 32,211 security incidents, 11 of them major. Comparitech counted 374 ransomware attacks on government bodies worldwide in 2025 (up 27%) and 187 in the first half of 2026. In Verizon's 2026 DBIR, the public administration sector had 2,410 confirmed breaches, ransomware was present in 48% of all breaches, and third-party involvement rose 60%. These stats show that public-sector attacks are frequent and often involve citizen data or service disruptions.
Public sector cybersecurity refers to protecting government and publicly-funded organization IT systems and data. It includes federal agencies, state and local governments, municipal utilities, public health and safety departments, schools and universities, election offices, and government contractors. It focuses on defending critical citizen-facing services (e.g. 911, courts, tax systems) and sensitive public data (citizen records, financial programs) from cyber threats, balancing security with public-service obligations.
Governments hold valuable data (social security numbers, health records, tax info), operate critical infrastructure, and face pressure to resume services quickly. Attackers see them as lucrative: state/local agencies often have weaker budgets and aging systems, making them easier targets. Critical services mean ransom demands tend to be high. Also, governments often integrate many systems (portals, APIs, vendors), creating many potential entry points.
Security incidents in government are very common. For example, federal agencies saw 32,211 incidents in FY2023 (up 9.9% from FY2022), and 11 of them were “major incidents”. Ransomware against government is also frequent: Comparitech logged 374 attacks on government bodies worldwide (all levels of government, not only US state and local) in 2025, 196 of them confirmed by the victims; 31% of the 187 attacks it counted in H1 2026 were in the US. Many breaches go unreported publicly, so actual numbers may be higher.
Ransomware can cripple public services. It encrypts systems (e.g. payroll, utilities, court records) causing outages, and may steal sensitive data for double extortion. Even if the data isn’t leaked, service disruptions delay emergency response, tax processing, public benefits, etc. For instance, a July 2025 Interlock ransomware attack on St. Paul, Minnesota led the governor to activate the National Guard, and Nevada's statewide attack in August 2025 took 28 days to recover from. Good backups and tested incident response are essential defenses.
Data that persists and can’t be easily changed is highest risk: identities (names, birthdates, SSNs), financial records (tax/benefits history), health info, law enforcement or court records. Government also handles credentials for accessing private accounts. Leaks of this data can lead to long-term fraud or privacy loss for citizens. Hence, data encryption, strict access controls, and minimization of stored data are critical.
Common gaps include legacy unpatched systems, insufficient multi-factor authentication, untested backup/restore processes, and over-exposed public portals or APIs. Third-party and contractor accounts often have excessive access. Many agencies have policies (e.g. for patching or IR) but lack evidence (logs, test reports) showing they work. A GAO report noted hundreds of open recommendations, indicating persistent control gaps.
Contractors, MSPs, and SaaS vendors frequently have privileged access to government networks or data. A breach at a contractor (as happened with HHS/CMS contractors in 2023) can expose millions of records. Since many agencies outsource IT and apps, vendors must be vetted and monitored. Weak vendor security or delayed breach notifications amplify government risk.
Key issues include not just having policies, but proving they work. Agencies must align with frameworks like FISMA/NIST, FedRAMP, CJIS, etc. The critical gaps are often missing evidence: e.g. no current asset inventory, no recent penetration test, no documented access reviews, or untested IR plans. Demonstrating compliance requires collecting test results, audit reports, and tabletop exercise records, not just checkboxes.
Yes. Penetration testing uncovers real-world weaknesses in government apps, networks, and configurations. Testing public portals, APIs, cloud setups, remote access points, and vendor interfaces reveals where attackers can get in or data can leak. For example, pentesting a citizen portal might find that users could see others’ records (authorization flaw). By fixing these flaws and retesting them, agencies turn known vulnerabilities into proven security.
Critical systems should be tested annually or whenever significant changes occur. However, continuous or quarterly testing is ideal for high-exposure areas (public portals, cloud configs, external assets). Regular phishing exercises (at least quarterly) and annual incident response drills are recommended. Continuous vulnerability scanning should be enabled, and every vulnerability closure should be verified by retesting. The key is an ongoing cycle: test, fix, retest.
By people affected, the largest include the Defense Manpower Data Center breach (about 3.05 million people, found in July 2026), the Illinois Department of Human Services exposure (705,017 people, disclosed January 2026) and the Minnesota Department of Human Services breach (about 304,000). Government contractor Conduent, which serves state programs, is listed at about 62 million people in the HHS breach portal after a January 2025 attack. At city level, Suffolk, Virginia notified 157,725 people in 2026.
Federal agencies reported 32,211 cybersecurity incidents in FY2023, up 9.9% from FY2022, according to OMB's FISMA report to Congress; 11 of them were major incidents. For state and local bodies there is no official total: the FBI IC3 received 233 ransomware complaints from the Government Facilities sector in 2025, and Comparitech counted 58 ransomware attacks on U.S. government entities in the first half of 2026.
Comparitech counted 58 ransomware attacks on U.S. government entities in the first half of 2026, 33 of them confirmed, and most named victims were cities and counties. The median ransom demand was $100,000. This is a tracker count built from public reports and gang claims, so the true number is likely higher.
Government cybersecurity in 2026 is fundamentally about validating the entire chain of citizen data and public service continuity. It’s not enough to have policies or awareness; agencies must prove that identity controls (especially phishing-resistant MFA), cloud configurations, public-facing applications, APIs, vendor/contractor access controls, remote access defenses, backup and recovery plans, incident response processes, and compliance controls actually work. This requires a regime of continuous assessment: web and API penetration tests for portals and citizen services, cloud security reviews for SaaS and infrastructure, identity security assessments, backup restore tests, ransomware readiness exercises, and retesting of remediations. Security metrics should tie directly to these activities (e.g. MFA coverage, open critical findings, restore success rates).
DeepStrike helps government agencies and their vendors operationalize this validation. Our services include penetration testing for public portals, APIs and cloud environments, red teaming, and continuous penetration testing with remediation retesting; the Premium continuous plan also includes Dark Web Monitoring, weekly automated vulnerability scanning and Attack Surface Management. By coupling threat insights with hands-on technical testing, agencies can turn statistics into solid security improvements, ensuring public services and citizen data remain protected in 2026 and beyond.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
This article prioritizes official government sources, public-sector cybersecurity reports, breach and ransomware research, federal cybersecurity guidance, compliance frameworks, and public incident evidence. Each statistic is labeled by data type to distinguish government, public-sector, federal, state/local, municipal, ransomware, breach, identity, cloud, compliance, survey, and case-study evidence. Claims based on broad breach or ransomware benchmarks are treated as context unless the source specifically segments government or public-sector data.
• GAO Cybersecurity and Federal Systems Reports
• OMB FISMA and Federal Cybersecurity Guidance
• CISA Cybersecurity Best Practices
• FBI Internet Crime Complaint Center (IC3)
• Verizon Data Breach Investigations Report
• Microsoft Digital Defense Report
• CrowdStrike Global Threat Report
• Sophos State of Ransomware Reports
• Comparitech Government Ransomware and Breach Research
• Emsisoft Ransomware Research
• Comparitech 2025 ransomware roundup
• Comparitech government ransomware roundup H1 2026
• OMB FISMA FY2023 report coverage (The Register)
• GAO-24-107231 cybersecurity recommendations
• FBI IC3 2025 Internet Crime Report
• Microsoft Digital Defense Report 2026: government
• Sophos State of Ransomware 2025 (state and local government median ransom payment)
• Nevada statewide cyber incident after-action release
• Help Net Security: Pentagon DMDC breach, 3 million people
• TechCrunch: Conduent data breach grows to 25M+
• Comparitech: Columbus, Ohio notifies 500,000 residents
• TechCrunch: U.S. Treasury "major incident" via BeyondTrust
• NIST Cybersecurity Framework 2.0
• FedRAMP Documents and Templates
• CISA Known Exploited Vulnerabilities Catalog

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
