October 31, 2025
Updated: November 5, 2026
Learn when FISMA systems need NIST SP 800-53 CA-8 penetration testing and how agencies set test frequency. See how to scope, execute, and document compliant pentests that secure federal systems and meet audit expectations.

Mohammed Khalil
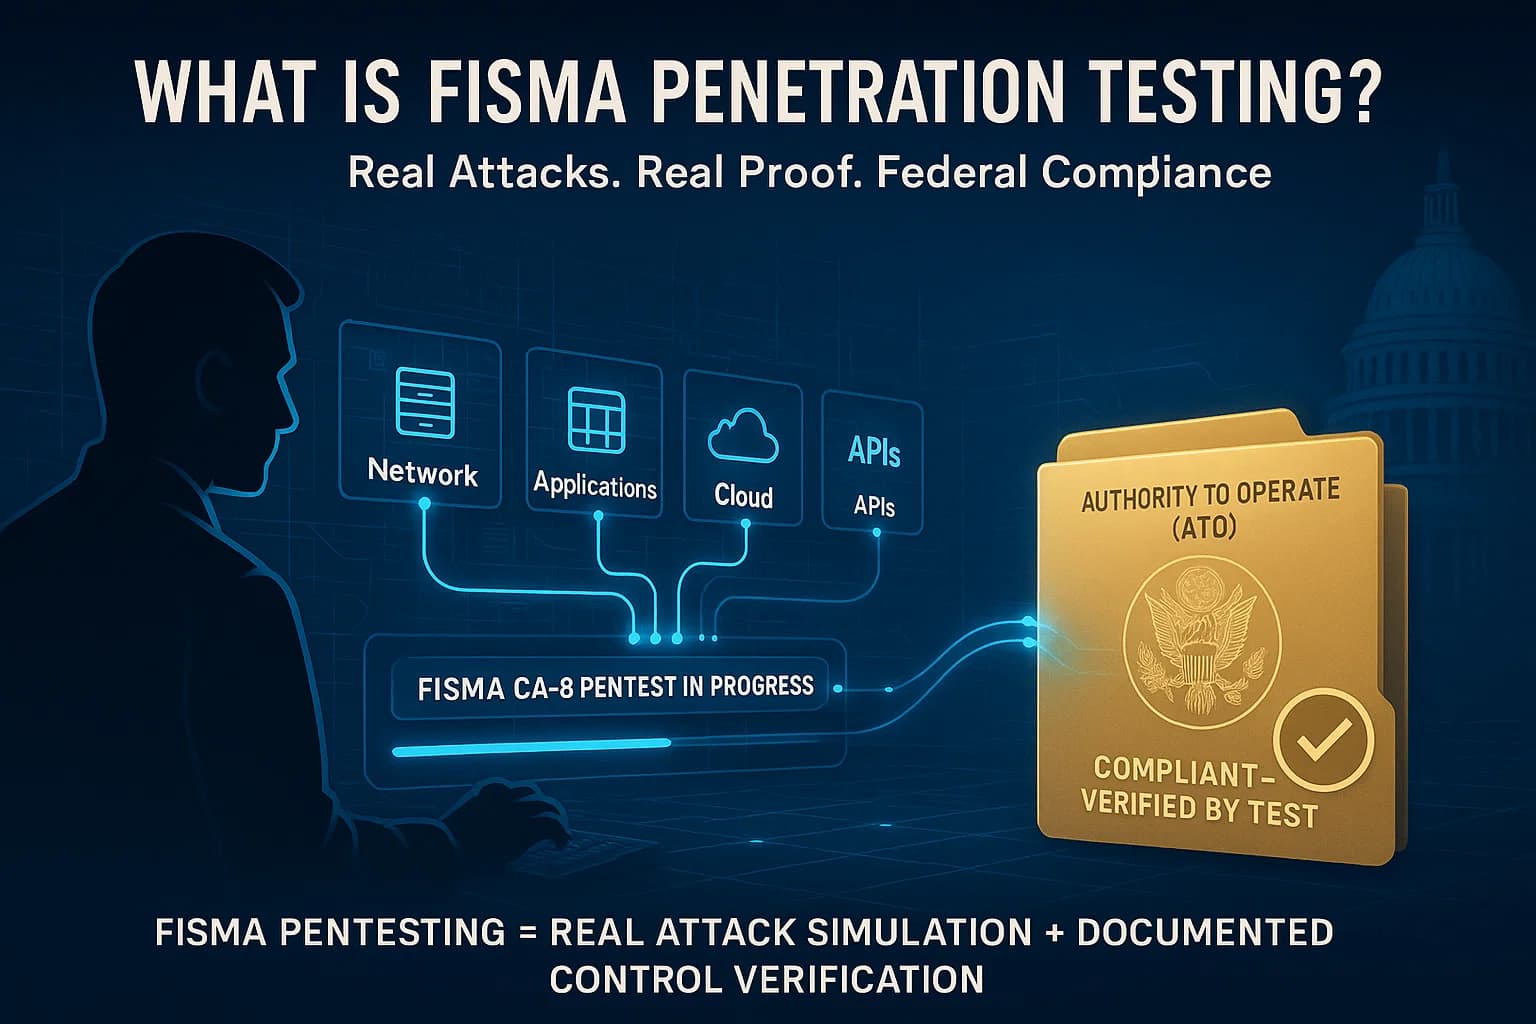
FISMA penetration testing is security testing of U.S. federal systems performed to meet the Federal Information Security Modernization Act (FISMA) and the NIST SP 800-53 CA-8 control where it applies. In practice, it means hiring skilled pentesters to simulate real attacks on in-scope assets (networks, applications, cloud services, etc.). This goes beyond automated scanning, aiming to exploit vulnerabilities in depth. The results feed directly into compliance: each finding is documented against NIST controls in the system’s Authority to Operate package. Need a pentesting refresher? See our What is Penetration Testing? overview.
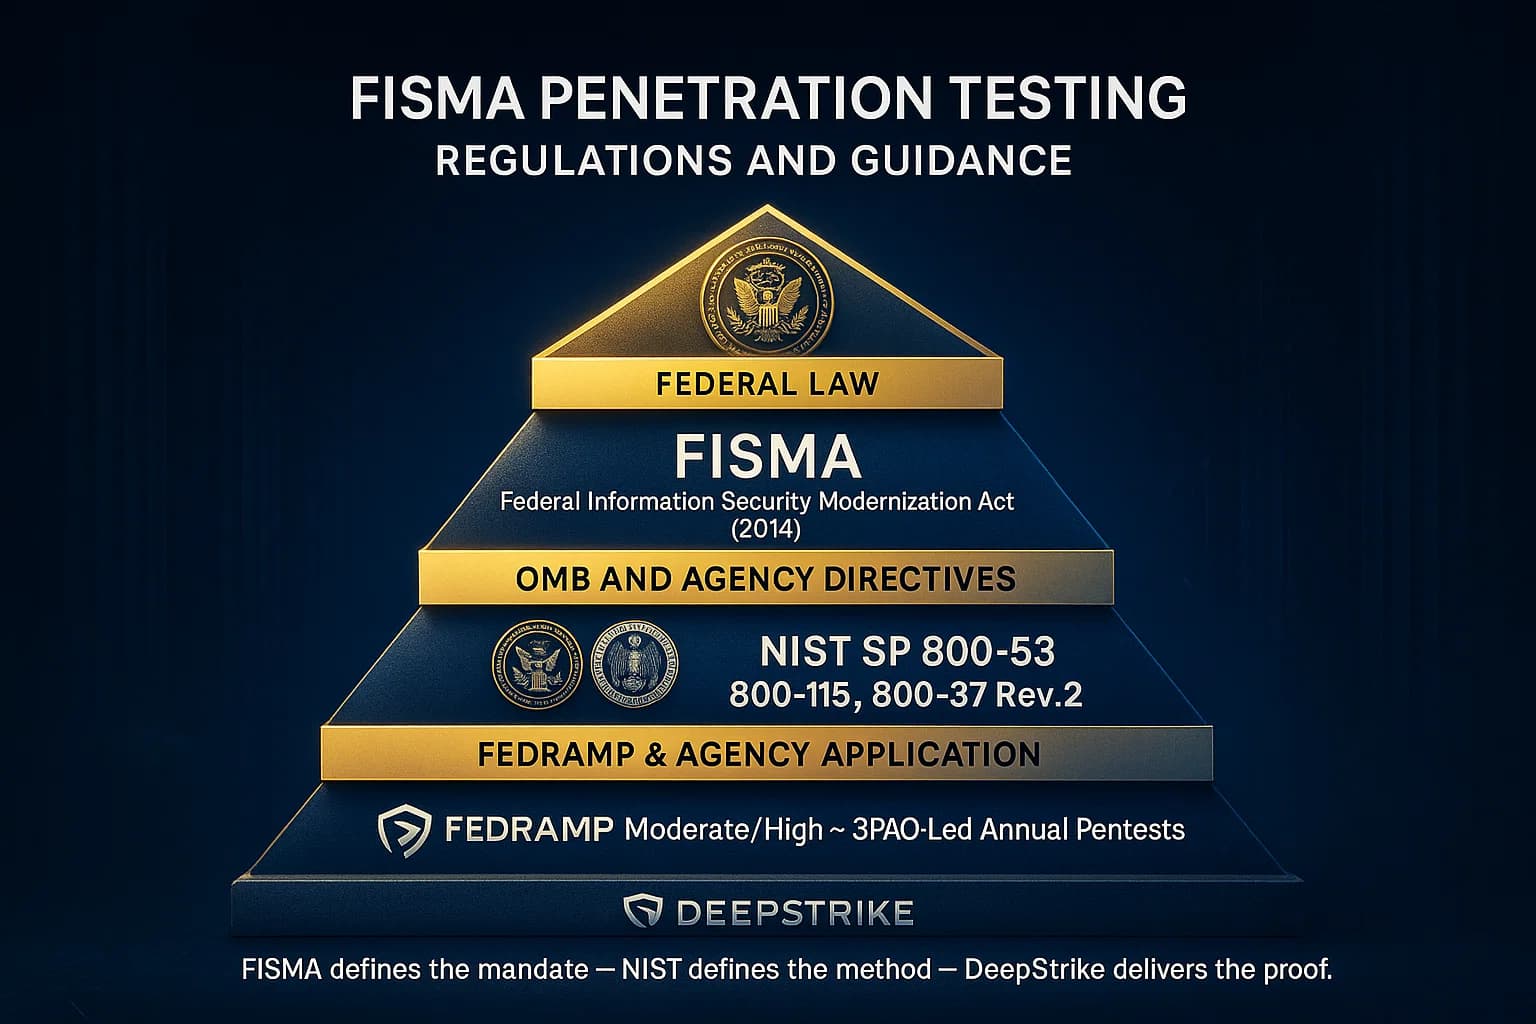
This matters now because federal cyber threats are on the rise. In FY2023, agencies reported 11 major incidents, according to OMB’s FY2023 FISMA report to Congress. Penetration testing helps catch gaps before attackers exploit them. Scans alone can’t prove exploitability, whereas pentests demonstrate real attack paths. For example, a scan might flag an open port or missing patch, but only a pentest will attempt to exploit it and show if it truly leads to a compromise. Agencies set CA-8 frequency in their own policies. GSA’s penetration-testing procedural guide, for example, includes annual testing for its FISMA High Value Assets, and FedRAMP requires 3PAO penetration testing for authorized cloud services. In short, regulatory compliance and good security hygiene demand thorough pentesting now. In summary, FISMA penetration testing is essential to verify your security posture beyond basic scanning.
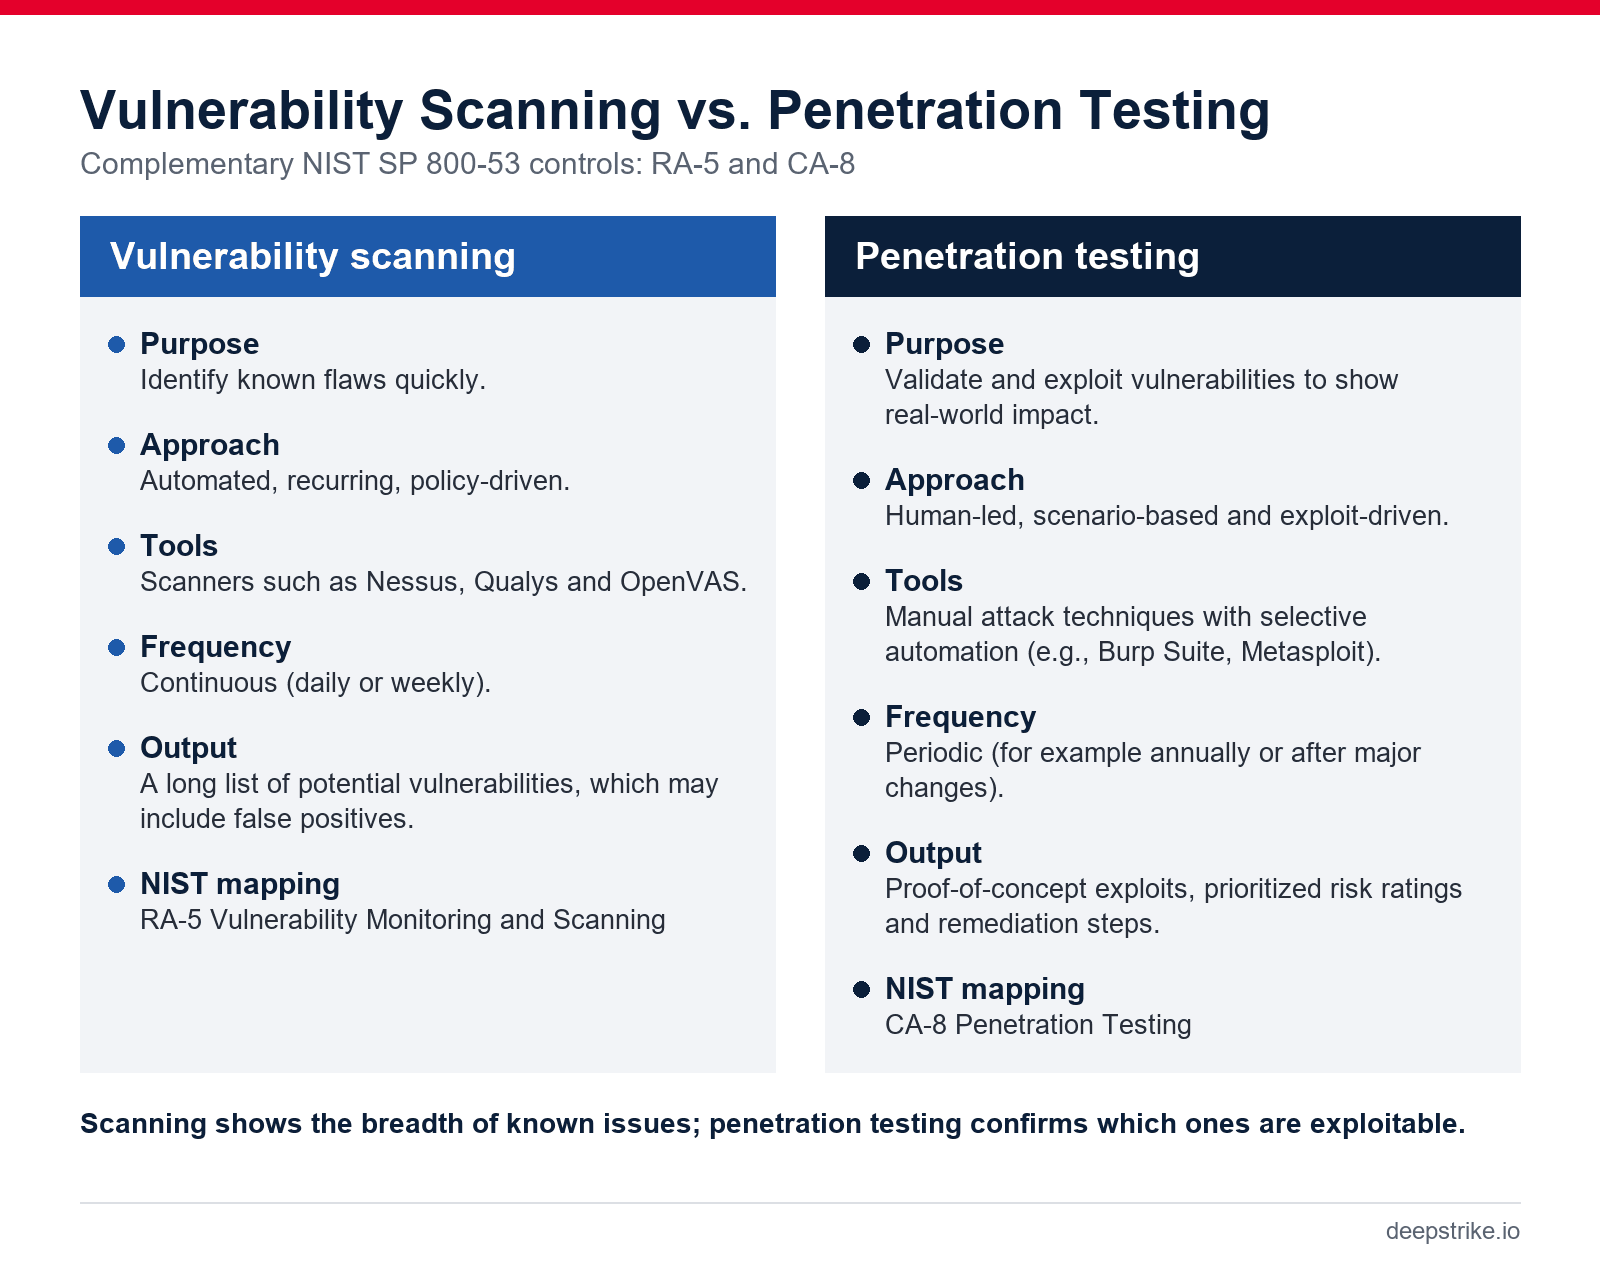
Penetration testing for compliance and vulnerability scanning complement each other under FISMA. Scans under NIST control RA-5 find known flaws quickly, whereas pentests under NIST CA-8 validate which flaws can actually be chained into a breach. Consider this: a scan may list dozens of missing patches or open ports, but a pentester will try exploiting them to see if they truly give an attacker a foothold. The table below highlights key differences:
| Aspect | Vulnerability Scan (Automated) | Penetration Test (Manual) |
|---|---|---|
| Purpose | Identify known flaws across systems (meets NIST RA-5) | Exploit vulnerabilities to prove actual risk (NIST CA-8) |
| Method | Automated tools (scans, scripts) | Manual techniques simulating real attackers |
| Coverage | Broad but shallow (all hosts/services) | Focused depth (critical systems/apps with full exploit attempts) |
| Frequency | Continuous (e.g., weekly/daily monitoring) | Periodic (e.g., annual for HVAs under agency policy) |
| Outcome | Reports of potential issues (many false positives) | Proof-of-concept exploits and prioritized findings with remediation guidance |
Only pentesting confirms which issues an attacker can actually exploit. Scans may list potential vulnerabilities, but pentesters prove which ones pose real risk by chaining them.
Continuous Testing (PTaaS): Some modern platforms offer Penetration Testing as a Service (PTaaS) for ongoing testing, often combining automation and human testers. These can catch issues in real time, but remember FISMA compliance still requires formal, scheduled pentests with full reports.
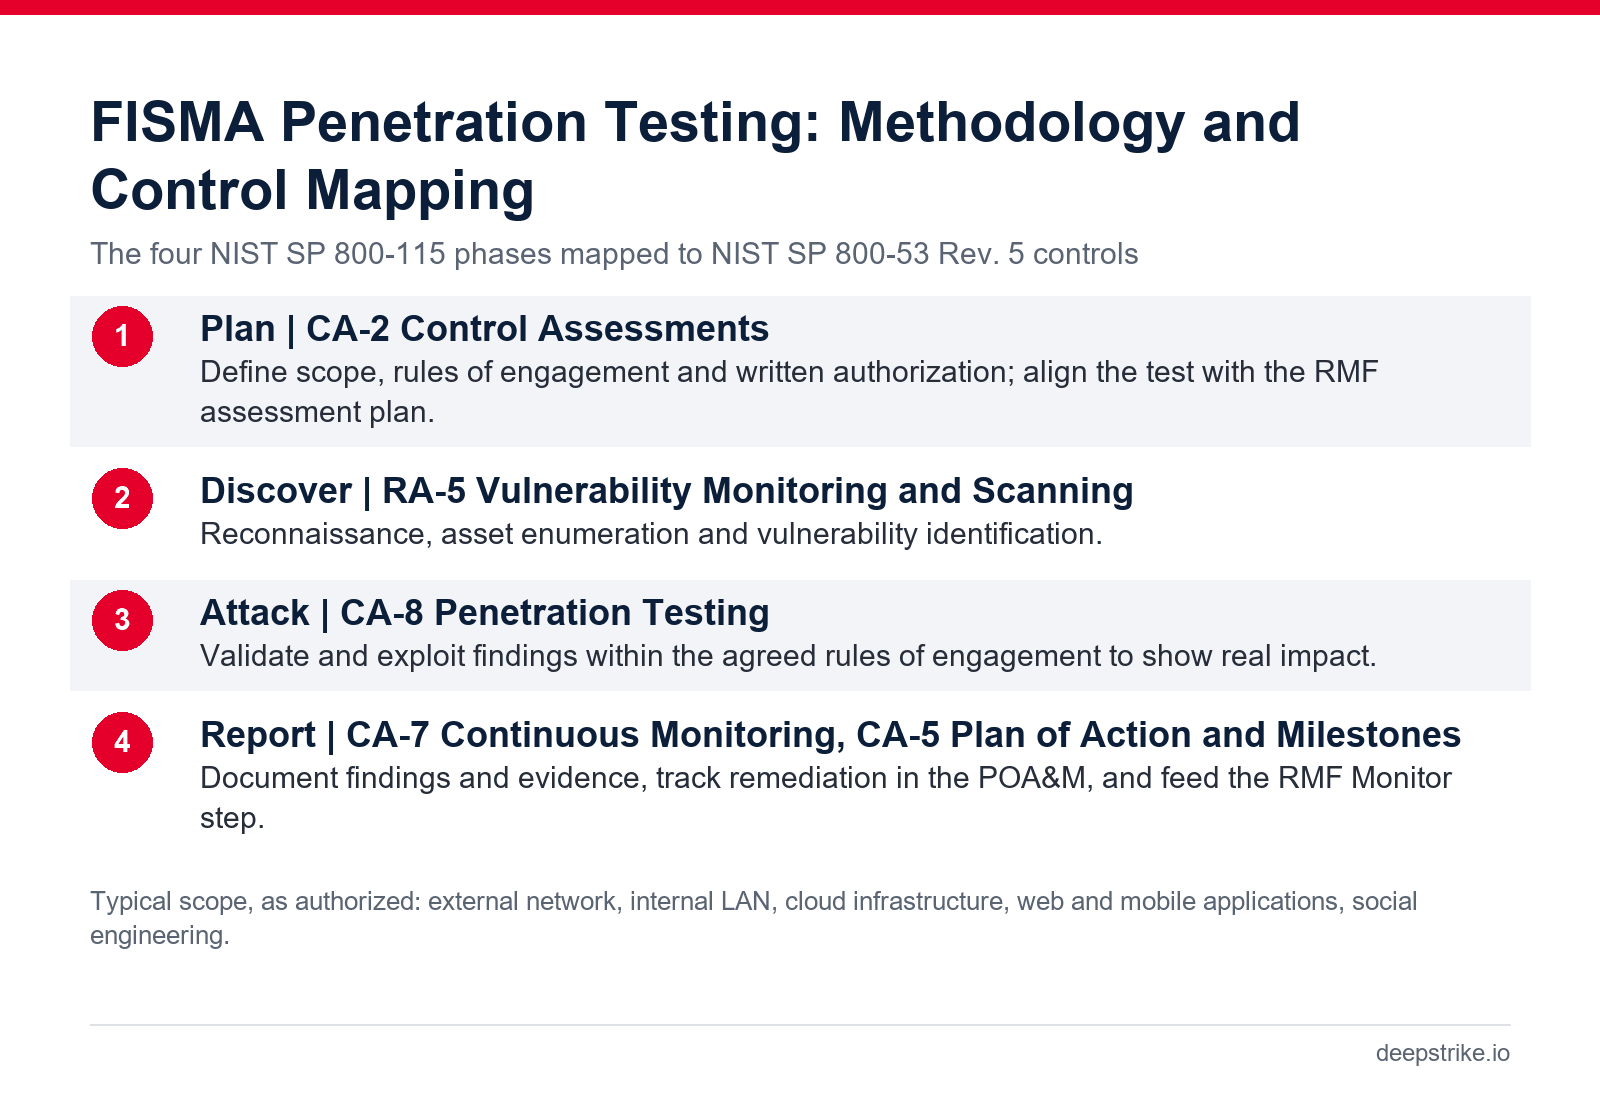
Scoping a FISMA pentest means testing both external and internal assets: internet-facing systems, on-premises networks, cloud environments, web/mobile applications, authentication systems, and even social engineering or physical attempts if allowed (see the difference between internal and external penetration tests). You can choose a black box approach (no insider information) or white box (full documentation); testers often use a gray-box mix. Some pentests become full red team exercises, sustained adversary simulations that rigorously test an organization’s defenses.
Pentests generally follow NIST SP 800-115’s four-phase process:
This structured approach ensures thorough coverage. For example, if a tester gains low-level access, they loop back into Discovery with those new credentials to find further vulnerabilities.
Not just any test will do. NIST CA-8(1) calls for an independent testing agent or team in the High baseline, and many agencies require independent, qualified testers. Key criteria:
Professional penetration testing services require skilled labor, so budget accordingly. Think of the engagement as cyber insurance: the cost of expert testing is small compared with the impact of a major breach.
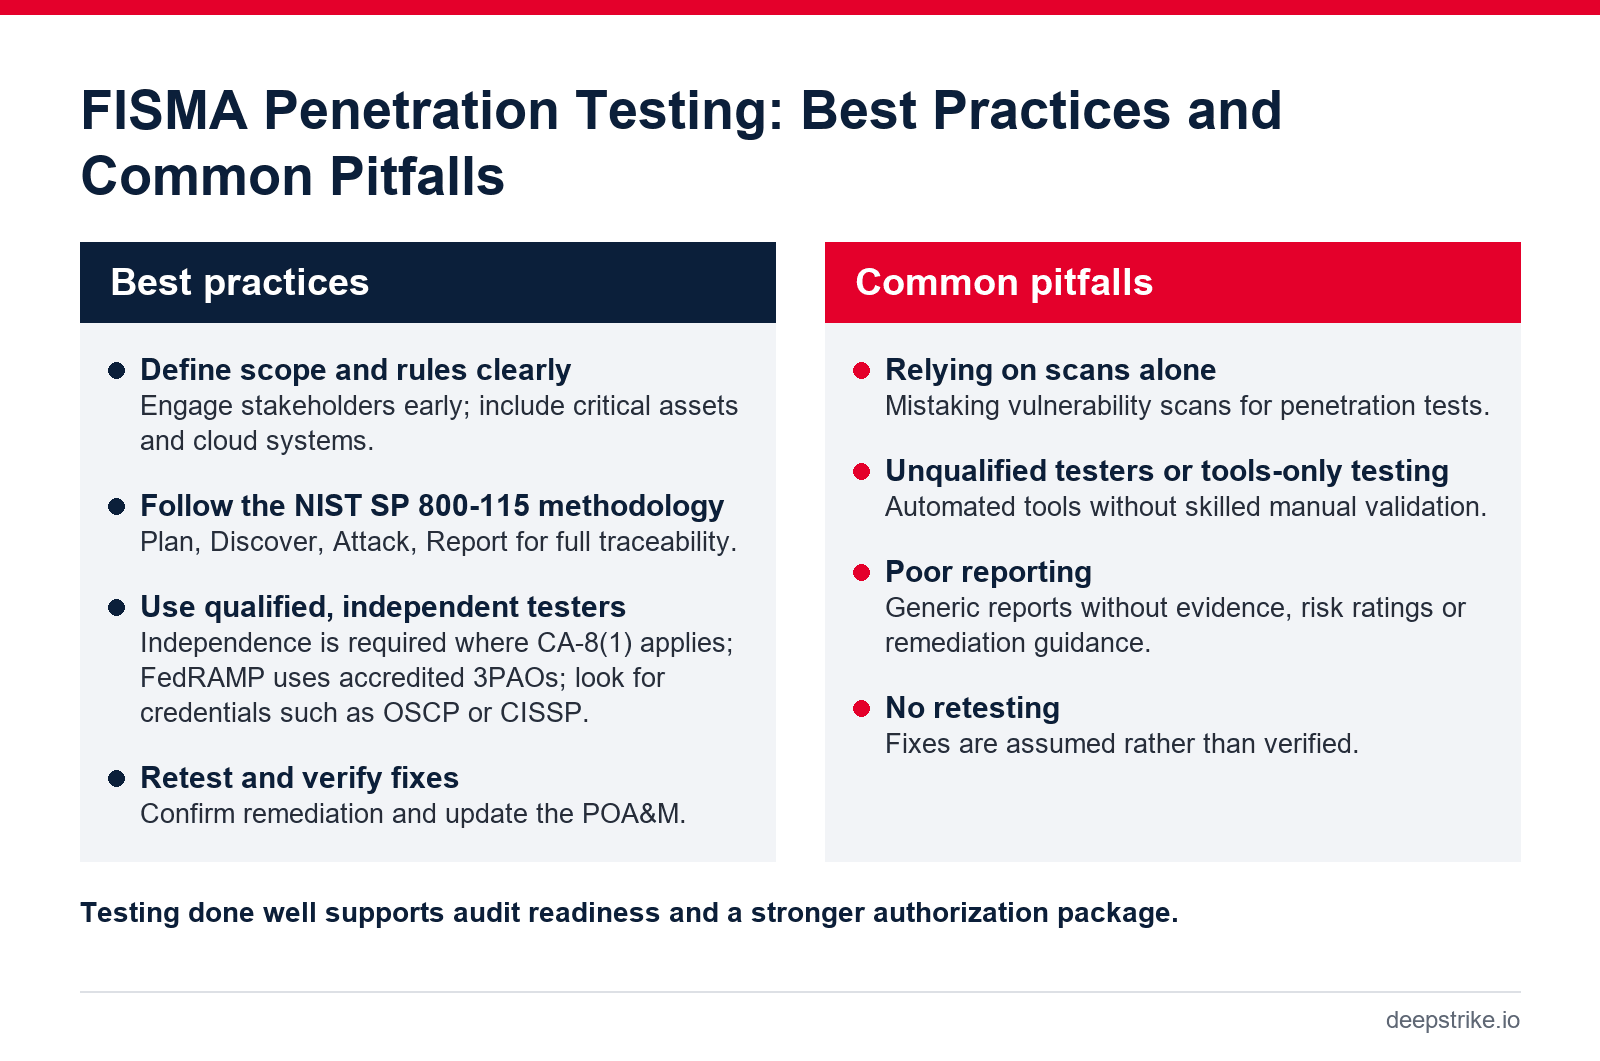
From experience, these guidelines help ensure effective FISMA pentesting:
Common mistakes include skipping scoping, missing critical systems and thinking automated tools alone satisfy FISMA. Remember: automated scans identify potential issues, but penetration tests confirm exploitable issues. In real assessments, testers often uncover critical chains of exploits that scanners missed.
FISMA penetration testing isn’t just a compliance checkbox, it's a proactive defense measure. By thoroughly testing your federal systems against NIST’s CA-8 control and following established methodologies, you reduce the risk of future breaches. The latest FISMA reports and FedRAMP rules make it clear regular, well-scoped pentests by qualified experts are expected for high-impact federal systems.
Ready to Strengthen Your Defenses? DeepStrike’s team is here to help. We can guide you through penetration test scoping, execution, and remediation.
Explore our penetration testing services to see how we can uncover vulnerabilities before attackers do. Drop us a line we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security. With certifications such as CISSP, OSCP, and OSWE, he has led numerous red team engagements. Mohammed focuses on cloud security, application vulnerabilities, and adversary emulation, helping clients in finance, healthcare, and technology sectors build resilient defenses.
It means performing penetration tests specifically to comply with FISMA/NIST requirements. Federal agencies use these tests to simulate real attacks on in-scope systems and validate security controls. Our government cybersecurity breach statistics show why: agencies reported 32,211 incidents in FY2023.
NIST leaves CA-8 frequency to the agency. Many agencies test High-impact systems and HVAs at least annually; GSA’s policy, for example, requires annual HVA pentests, and FedRAMP sets its own cadence for cloud services.
No. Automated vulnerability scans (NIST RA-5) are helpful, but the NIST CA-8 control specifically requires manual penetration tests. Scanners may find issues, but only pentests prove those issues can be exploited in sequence.
Qualified third-party security professionals or accredited 3PAOs should conduct the tests. NIST even recommends independent testers to avoid conflicts. Look for providers experienced with federal standards and certifications.
FISMA applies to all federal information systems, including cloud-hosted ones. FedRAMP is the government-wide program that standardizes how cloud services used by agencies are assessed and authorized, including its own penetration-testing requirements for 3PAOs.
Agencies document findings in the ATO package and track them in the Plan of Action & Milestones (POA&M). High-risk issues are remediated quickly and re-tested. In this way, the pentest drives continuous improvement of the security posture.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
