June 30, 2026
Updated: November 5, 2026
A buyer-focused guide to the best AWS penetration testing companies, covering IAM, S3, EC2, EKS, Lambda, VPC, API Gateway, PTaaS, reporting, retesting, and pricing.

Mohammed Khalil
The best AWS penetration testing companies in 2026 are the firms that can show how an attacker would move through your AWS accounts, not just list misconfigurations. This guide compares 15 providers: DeepStrike (the publisher, listed first), NetSPI, Bishop Fox, GuidePoint Security, Synack, Cobalt, IBM X-Force Red, Kroll, Mandiant, NCC Group, HackerOne, BreachLock, Packetlabs, LevelBlue SpiderLabs, and Rhino Security Labs. Shortlist on four things: IAM privilege escalation depth, Lambda, EKS, and API Gateway coverage, an audit-ready report, and written retest terms.
The best AWS penetration testing companies are the providers that can validate real AWS risk, not just list misconfigurations. The right choice depends on AWS account structure, AWS Organizations complexity, IAM design, EKS or ECS usage, Lambda and serverless scope, S3 and data exposure, API Gateway exposure, reporting quality, retesting terms, and whether the buyer needs one-time testing or PTaaS. DeepStrike publishes this list and lists itself first; list order is not a quality ranking. Enterprise buyers may also shortlist NetSPI, Bishop Fox, IBM Security X-Force Red, Mandiant, GuidePoint, Synack, Cobalt, NCC Group, Kroll, HackerOne, BreachLock, Packetlabs, LevelBlue SpiderLabs (formerly Trustwave), and Rhino Security Labs, depending on scope and operating model.
For a broader comparison across testing types and regions, see our list of the top penetration testing companies worldwide.
The table condenses each provider’s published AWS or cloud testing offer, as described on its own website and detailed in the provider sections below. “Confirm” means the provider does not publish a standing retest commitment for cloud work, so get it in writing. NetSPI and Synack completed their merger on October 5, 2026, and appear separately because their published delivery models still differ. DeepStrike publishes this list and lists itself first; list order is not a quality ranking. For Azure and Google Cloud providers, see our comparison of the best cloud penetration testing companies.
| Provider | Best fit | Delivery model | Retesting (published) | Check before buying |
|---|---|---|---|---|
| DeepStrike | SMB to mid-market teams that want human-led AWS validation | Manual testing with a collaboration platform; one-shot or continuous plans | Basic plan lists 12 months of remediation retesting | Not a fit if you only need posture scanning |
| NetSPI | Large enterprises with broad AWS estates | In-house team; AWS configuration review plus external and internal network testing | Confirm | Lambda, EKS, and cross-account scope are not detailed |
| Bishop Fox | Mature teams that want objective-driven attack paths | Scenario-based manual testing | Confirm | Which accounts and services the objective covers |
| GuidePoint Security | Enterprises tying testing to an AWS security program | Consulting-led testing | Confirm | Request the AWS methodology and a sample report |
| Synack | Large, fast-changing AWS estates | Vetted researcher pool on a PTaaS platform; 14-day to 365-day options | Patch verification included | Many researchers may access your accounts |
| Cobalt | SaaS and product teams | PTaaS with a community of vetted pentesters | Free retesting of findings for 6 or 12 months | AWS-specific and multi-account depth |
| IBM X-Force Red | Multinational enterprises | Expert-led and AI-driven testing managed in Red Portal | Confirm | Which findings come from autonomous testing |
| Kroll (Redscan) | Regulated organizations | Testing plus CIS benchmark configuration review | Post-test remediation support; confirm retest | How IAM escalation is tested |
| Mandiant | Threat-led enterprise programs | Threat-informed testing and red teaming | Confirm | AWS services are not named publicly |
| NCC Group | Enterprises that want configuration assurance | Configuration scanner plus read-only console review | Confirm | Read-only review is not exploitation |
| HackerOne | Product teams running applications on AWS | Human-led H1 Pentest on its platform | Retesting after fixes | AWS control-plane attack paths |
| BreachLock | Mid-market and compliance-driven teams | In-house pentesters plus autonomous testing | Confirm | The human and automated split |
| Packetlabs | Teams that want manual attack-path depth | Specialist manual testing | Not mentioned on its cloud page | Retest terms in writing |
| LevelBlue SpiderLabs | Existing LevelBlue managed-services buyers | Offensive testing inside a managed security portfolio | Confirm | No AWS-specific methodology is published |
| Rhino Security Labs | Teams that want AWS attack-research depth | Six-step AWS method ending in remediation testing | Remediation testing is a published step | Current scope, team, and report format |
Buyers searching for the best AWS penetration testing companies usually need five things at once: a provider shortlist, a way to distinguish human-led AWS testing from CSPM or scanner output, practical AWS scoping guidance, commercially realistic pricing expectations, and a procurement framework they can use with engineering, security, and sourcing stakeholders.
The need is especially acute in multi-account AWS environments where IAM trust relationships, role chaining, S3 exposure, EKS configuration, Lambda permissions, API Gateway authorization, and VPC segmentation cannot be safely reduced to a posture dashboard alone. A useful article must therefore compare companies while also explaining what serious AWS penetration testing services should cover.
That is why this page combines vendor comparison with buyer education. A list without methodology is too thin for procurement. A technical explainer without vendor fit does not solve the buying task. Serious buyers need both.
AWS penetration testing services are authorized security assessments of AWS-hosted environments and AWS-connected assets designed to validate whether real attackers could exploit weaknesses in the customer-controlled parts of the cloud stack under the AWS shared responsibility model. In practice, that can include IAM permissions and privilege escalation paths, S3 and data exposure, EC2 and VPC exposure, EKS and ECS security, Lambda and serverless components, RDS and data services, API Gateway and internet-facing APIs, CloudFront exposure, secrets handling, and logging or monitoring controls where detection validation is in scope. A credible AWS pentest goes beyond configuration review or scanner findings by using manual techniques to test exploitability, role chaining, cross-account trust, metadata-service abuse, lateral movement, exposed secrets, and AWS attack paths. The final deliverable should document evidence, impact, remediation steps, and retesting terms. AWS penetration testing supports risk validation, but it does not guarantee compliance, breach prevention, regulator approval, or AWS approval of the environment.
AWS-native tools and CSPM/CNAPP platforms are valuable, but they solve a different problem. Security Hub can centralize and prioritize security findings. GuardDuty can detect malicious activity. Inspector can surface vulnerability and exposure findings. IAM Access Analyzer can highlight access exposure and unused permissions. Macie can help identify sensitive data risk. Config can record resource configuration state, and CloudTrail can record control-plane activity. These capabilities matter for discovery, inventory, compliance monitoring, and prioritization.
What these tools generally do not do by themselves is validate exploitability, prove business impact, or safely chain weaknesses the way a human AWS penetration test should. A well-run AWS penetration test should validate IAM privilege escalation, STS AssumeRole abuse, cross-account attack paths, metadata-service abuse, lateral movement across VPCs, exposed secrets, S3 access paths, Lambda permission flaws, EKS RBAC and secret exposure, ECS risks where relevant, API Gateway abuse, and whether multiple lower-severity issues combine into a material cloud compromise path.
A CSPM, CNAPP, AWS-native security tool, or cloud scanner can support discovery and posture management, but it should not be treated as a full AWS penetration test unless human testers validate exploitability, attack paths, and business impact.
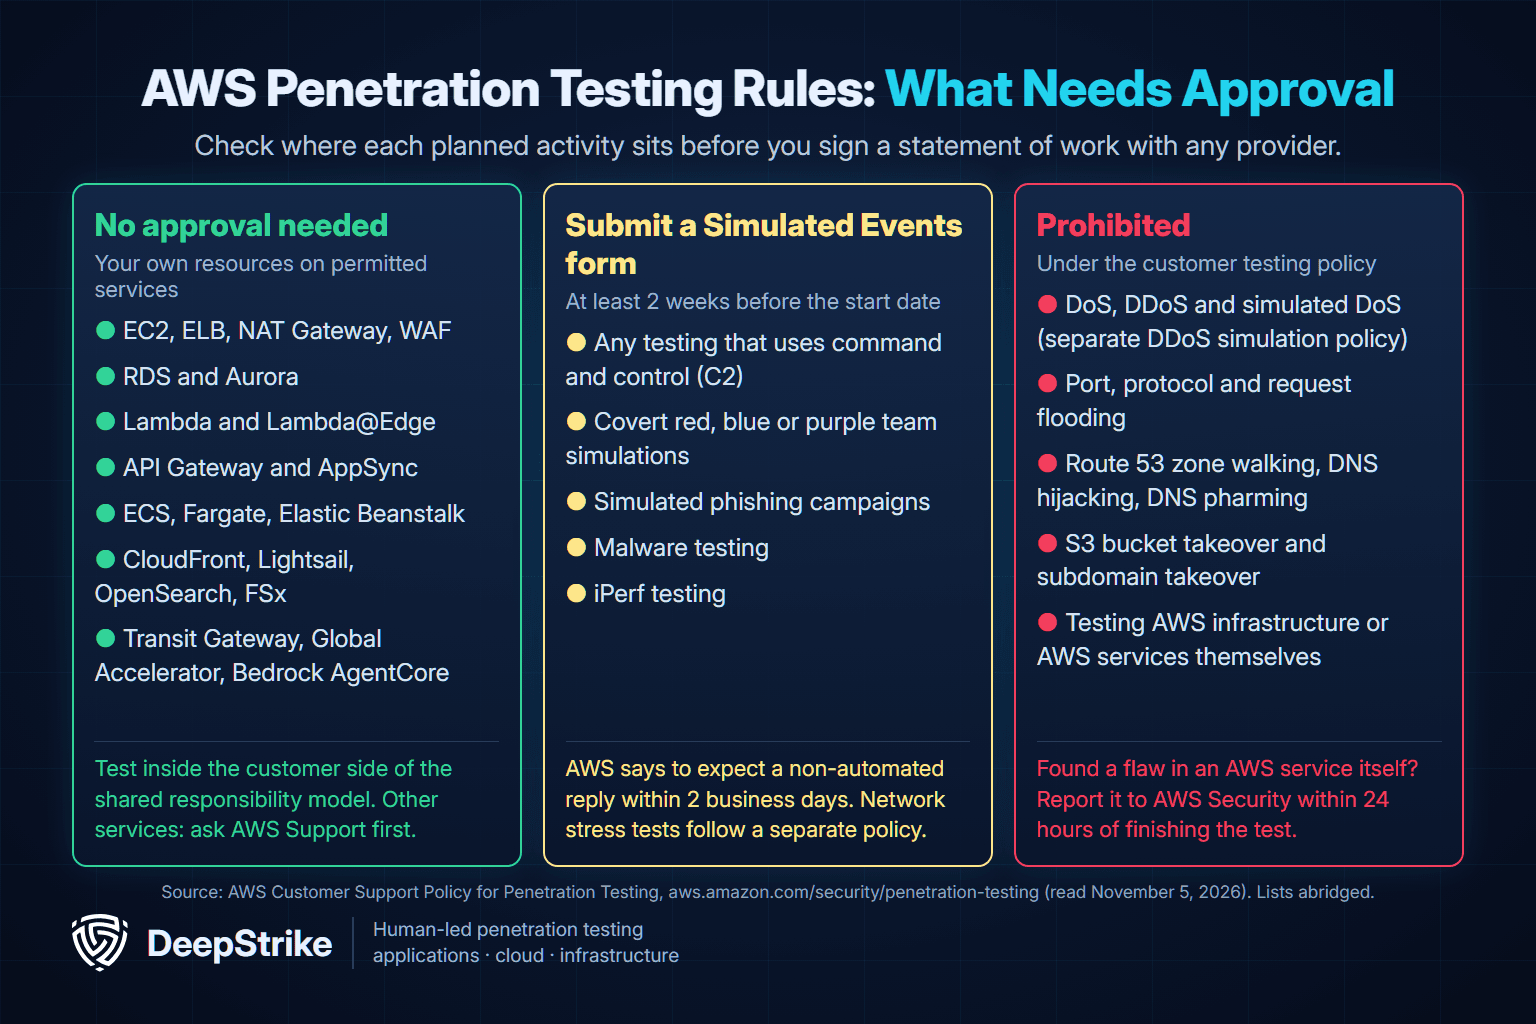
Yes. Under its customer support policy for penetration testing, AWS lets customers test their own resources on a list of permitted services without prior approval. The list includes EC2, RDS, Aurora, CloudFront, API Gateway, AppSync, Lambda, ECS, Fargate, Lightsail, Elastic Beanstalk, OpenSearch, FSx, Transit Gateway, Global Accelerator, and Bedrock AgentCore. Testing any other service means working with AWS Support or your account representative first.
A provider that cannot place each planned activity in one of these groups has not read the policy. Ask for the mapping in the rules of engagement.
This comparison uses AWS-specific selection criteria rather than simple brand familiarity. Providers were selected and described using these criteria, not scored against them: manual AWS exploitation depth, IAM and privilege escalation testing, AWS Organizations and cross-account experience, coverage across S3, EC2, VPC, RDS, Lambda, EKS, ECS, API Gateway, CloudFront, storage exposure, AWS attack-path chaining, PTaaS or continuous-testing capability, report quality, remediation guidance, retesting clarity, enterprise readiness, SMB accessibility, and whether the provider states limitations instead of flattening everything into generic cloud assessment language.
Disclosure: DeepStrike publishes this list and lists itself first; list order is not a quality ranking. The other providers are not ranked against each other, and the list should not be read as a paid third-party award or a claim that one provider is universally best for every organization.
No shortlist should replace buyer due diligence. Security teams should verify AWS scope, tester seniority, methodology, sample reports, account access model, AWS rules of engagement, retesting terms, and data-handling requirements before selecting a provider. AWS publishes customer testing policies and permitted-service boundaries, so production safety controls and rules of engagement should be confirmed before testing begins.
Summary cards for each provider. DeepStrike publishes this list and lists itself first; list order is not a quality ranking.
1. DeepStrike
2. NetSPI
3. Bishop Fox
4. GuidePoint Security
5. Synack
6. Cobalt
7. IBM Security X-Force Red
8. Kroll
9. Mandiant
10. NCC Group
11. HackerOne
12. BreachLock
13. Packetlabs
14. LevelBlue (Trustwave SpiderLabs)
15. Rhino Security Labs
AWS-native services can improve visibility and operating discipline. Security Hub, GuardDuty, Inspector, IAM Access Analyzer, Macie, Config, and CloudTrail can reduce blind spots, accelerate triage, and provide operational evidence for remediation and detection engineering.
Third-party platforms such as Wiz, Prisma Cloud (now Cortex Cloud), Orca Security, Tenable Cloud Security, Check Point CloudGuard, Aqua Security, Snyk Cloud, Sysdig, Prowler, and ScoutSuite may support CSPM, CNAPP, exposure management, identity risk, cloud workload security, and code-to-cloud context. These categories complement AWS penetration testing. They do not automatically prove that a human attacker can abuse an AWS identity path, serverless trust chain, Kubernetes exposure, or cross-account misconfiguration in practice.
The procurement rule is simple: use tools for continuous visibility and posture management, and use AWS penetration testing to validate exploitability, impact, and attack paths.
For applications, yes. AWS Security Agent on-demand penetration testing became generally available on March 31, 2026, and AWS now sells it as AWS Continuum for penetration testing. It runs autonomous AI agents against web applications and APIs, attempts to validate findings through attack chains, and reports CVSS scores with reproduction steps. AWS prices it at $50 per task-hour, metered per second; its launch post estimated about 24 task-hours, roughly $1,200, for an average application test.
It is a practical way to test applications more often. Its launch materials focus on the application layer, though, and do not describe testing IAM privilege escalation across accounts, AWS Organizations trust, or EKS and Lambda execution roles from the control plane, which is the work most buyers hire an AWS penetration testing company to do. Treat it like the other cloud penetration testing tools: run it between human-led tests and give your testers its findings as a starting point.
Start with scope, not vendor logos. Your shortlist should be driven by AWS account count, Organizations and OU structure, privileged IAM roles, SCPs, permission boundaries, federation paths, workload identities, S3 and data stores, VPC connectivity, EKS and ECS usage, Lambda and event-driven architecture, API Gateway exposure, Secrets Manager and Parameter Store usage, CI/CD paths, production constraints, and the access model you are willing to grant testers.
Then verify evidence quality. Ask for a sample report, proof-of-exploitation style, remediation guidance, retesting terms, secure evidence handling, communication cadence, executive reporting, and whether the provider understands AWS testing boundaries and customer-testing policy requirements.
Finally, separate pure platform subscriptions from consultant-led validation. Some providers are strongest when you want a portal and ongoing workflow. Others are strongest when you need a small team of senior operators to test specific AWS attack paths manually.
A mature AWS methodology (see our AWS penetration testing methodology guide) should cover scoping and rules of engagement, AWS customer-testing policy awareness, the AWS shared responsibility model, inventory and asset discovery, IAM privilege escalation, AWS Organizations and cross-account trust, S3 and data exposure, EC2 and VPC exposure, EKS and ECS testing, Lambda and serverless paths, API Gateway and cloud API security, secrets and CI/CD risk, CloudTrail and GuardDuty validation where detection testing is in scope, safe exploitation controls, reporting, remediation, and retesting.
Recognized references such as NIST SP 800-115, PTES, OWASP WSTG, OWASP API Security Top 10, MITRE ATT&CK Cloud, CIS AWS Foundations, CIS Kubernetes, and Cloud Security Alliance guidance are useful anchors. They do not replace scoping judgment, but they help buyers distinguish structured testing from vague cloud review language.
Buyers should be suspicious when providers discuss only CSPM findings or cloud configuration review but cannot explain how they validate exploitability under the shared responsibility model.
AWS penetration testing pricing varies by provider, number of AWS accounts, IAM complexity, EKS or container scope, Lambda or serverless scope, network exposure, S3 and data exposure, API Gateway complexity, documentation quality, reporting depth, retesting, and urgency. Public vendor pricing is rarely listed, so buyers should compare scoped deliverables rather than headline price.
The main commercial models are fixed-scope AWS pentests, time-and-materials engagements, PTaaS subscriptions, enterprise retainers, cloud red-team assessments, and platform-subscription models paired with manual validation. Enterprise buyers typically need more emphasis on multi-account scoping, executive deliverables, repeat testing, and procurement support. SMBs usually need tighter scope control, faster remediation guidance, and a provider that will not sell a broad cloud red-team program when the actual need is focused validation of IAM, S3, EC2, VPC, and API risk.
Enterprise buyers usually need multi-account AWS scoping, shared-services context, IAM path analysis across business units, EKS and container coverage, VPC segmentation testing, cross-account trust review, compliance mapping, retesting workflows, executive reporting, and vendor readiness for complex procurement. That favors providers with stronger program management, repeat testing, and broader offensive-service benches.
SMBs usually need clarity, speed, practical remediation, and a provider that can focus on the AWS assets that matter without forcing a larger managed program. For those buyers, a smaller manual-first provider or a practical PTaaS vendor can create better value than a large consultancy or a scan-led cloud platform marketed as a pentest replacement.
Many AWS tests are bought because someone outside the security team asked for evidence: a SOC 2 auditor, an enterprise customer’s security review, or Amazon itself. The provider you pick has to produce a document that reader will accept, so ask for a sample penetration testing report at the scoping stage.
DeepStrike’s cloud penetration testing deliverables include a report, fix recommendations, retesting, and an attestation letter confirming the test was completed. Compare that list against every provider’s proposal, including ours.
A defensible RFP should ask for:
DeepStrike publishes this list and lists itself first; list order is not a quality ranking. The numbers below are for reference only.
Public offering: DeepStrike's penetration testing services describe human-led testing across applications, cloud environments, and infrastructure, supported by a findings and collaboration platform. Its public process covers planning, reconnaissance, vulnerability discovery, controlled exploitation, reporting, and technical support. Published reports include reproduction steps, remediation guidance, and root-cause information; the proposal should define exact coverage and commercial terms.
AWS testing relevance: Founded in 2016, DeepStrike LLC is headquartered in Newark, Delaware, has 11–50 employees, and also publishes a business address in Dubai, UAE (IFZA Business Park). It delivers AWS testing remotely as part of its cloud penetration testing work; define tester locations, permitted subcontracting, and data-handling restrictions in the engagement agreement.
Team certifications: OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate, as shown on DeepStrike's services page.
Official sources: Pricing , Contact Us
Buyer fit: Engineering teams that need application, cloud, or infrastructure testing with direct remediation collaboration.
Buying through AWS: DeepStrike is listed on AWS Marketplace, so teams can buy its penetration testing and continuous testing through their AWS account, with charges billed by AWS. Eligible Marketplace purchases can count toward an AWS spend commitment, subject to the buyer’s agreement with AWS.
| Documented strengths | Limits and buying considerations |
|---|---|
| Human-led testing with reproduction evidence, root-cause information, and remediation guidance. | The service description is not an independently measured quality comparison. Assess the assigned team and a relevant sample report. |
| The published Basic plan lists Slack collaboration, customizable reports, and 12 months of remediation retesting. | No numeric price is displayed on the pricing page. Basic is a one-shot test; recurring coverage belongs to a different plan, with contract-specific terms. |
| Team certifications shown on the services page include OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate. | These are individual tester credentials, not a company-level accreditation; ask which certified testers will be assigned to your engagement. |
Public offering: NetSPI's AWS penetration testing combines a configuration review of AWS services and IAM policies, external AWS network testing, and internal testing of AWS virtual networks. Techniques include system and service discovery, automated vulnerability scanning with manual verification, manual web application and network protocol attacks, network pivoting, privilege escalation, and access to sensitive data, using both anonymous and credentialed users. Engagements produce reports with prioritized vulnerabilities and remediation guidance.
AWS testing relevance: The AWS page names IAM policies and internet-exposed S3 buckets but does not detail Lambda or EKS testing, so confirm serverless, container, and cross-account scope. CREST's public marketplace lists NetSPI with penetration testing accreditation; confirm tester locations and data handling in the agreement. NetSPI and Synack completed their merger on October 5, 2026; NetSPI states that existing customers continue working under their current agreements, services, and platforms.
Official sources: https://www.netspi.com/netspi-ptaas/cloud-penetration-testing/aws/; https://www.netspi.com/contact/
Buyer fit: Large enterprises that want AWS testing inside a broader testing program run by an in-house team.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published AWS scope pairs IAM and service configuration review with external and internal network testing. | Lambda, EKS, and cross-account testing are not detailed; define them explicitly in scope. |
| Anonymous and credentialed testing with manual verification and privilege escalation. | The AWS page does not mention retesting; confirm fix verification terms. |
Public offering: Bishop Fox's cloud penetration testing combines configuration review with penetration testing across AWS, Google Cloud, Azure, and hybrid environments. Engagements are objective-driven: the client defines a target scenario, such as a compromised application or a malicious user, and assessors emulate attacker tactics to abuse misconfigurations, escalate privileges, and reach targets through over-privileged access, unintended entry points, and internal pathways. Deliverables include contextual attack insights, exploit likelihood analysis, impact severity scoring, executive and technical reports, and prioritized recommendations.
AWS testing relevance: The cloud page states that the methodology applies to AWS but does not list AWS-specific services or techniques, so confirm IAM, EKS, Lambda, and multi-account coverage. Bishop Fox lists its headquarters in Tempe, Arizona; confirm tester locations, data access, and retest terms in the agreement.
Official sources: https://bishopfox.com/services/cloud-penetration-testing; https://bishopfox.com/contact
Buyer fit: Mature security teams that want scenario-based AWS testing focused on attack paths rather than configuration checklists.
| Documented strengths | Limits and buying considerations |
|---|---|
| Objective-driven testing that emulates attacker tactics beyond configuration review. | Objective-based engagements may not cover every AWS account or service; agree coverage expectations up front. |
| Deliverables include attack-path insights, exploit likelihood analysis, and executive and technical reports. | The cloud page does not mention retesting; confirm fix verification terms. |
Public offering: GuidePoint Security lists cloud penetration testing aimed at current and emerging cloud-specific threats, alongside general penetration testing, penetration testing as a service, red and purple teaming, and application security assessments. It also lists AWS security program services among its services by platform.
AWS testing relevance: GuidePoint Security LLC lists its address at 1900 Reston Metro Plaza, Reston, Virginia. Request the AWS methodology, covered services, a sample report, and retest terms before buying.
Official sources: https://www.guidepointsecurity.com/cloud-penetration-testing/; https://www.guidepointsecurity.com/penetration-testing/
Buyer fit: Enterprises that want AWS testing aligned with a wider AWS security program and advisory work.
| Documented strengths | Limits and buying considerations |
|---|---|
| Cloud penetration testing sits alongside PTaaS, red and purple teaming, and AWS security program services. | Public AWS testing detail is limited; request the methodology and a sample cloud report. |
| Listed on federal contract vehicles such as GSA MAS and NASA SEWP VI. | Contract vehicles are procurement routes, not technical accreditations; assess the assigned testers. |
Public offering: Synack offers penetration testing as a service delivered through its platform and the Synack Red Team, which it describes as 1,500 vetted security researchers. Its published coverage includes web, host, API, mobile, and AI applications and cloud testing across AWS, Azure, and GCP, with options from a 14-day test to continuous 365-day coverage. Deliverables include executive reporting with root-cause analysis, compliance documentation, and triage and patch verification.
AWS testing relevance: CREST's public marketplace lists Synack, Inc with penetration testing accreditation. Crowd-based delivery means several researchers may access your AWS accounts; agree access roles, logging, and data handling, and confirm whether control-plane IAM paths are in scope. Synack merged with NetSPI on October 5, 2026; NetSPI states that Synack's FedRAMP Moderate authorization covers the Synack platform only.
Official sources: https://www.synack.com/penetration-testing/; https://www.synack.com/contact/
Buyer fit: Large organizations with changing AWS estates that want continuous or time-boxed testing from a vetted researcher pool.
| Documented strengths | Limits and buying considerations |
|---|---|
| Cloud testing across AWS, Azure, and GCP with continuous or time-boxed options. | Many researchers may access your accounts; agree least-privilege test roles and logging. |
| Triage and patch verification, plus executive reporting with root-cause analysis. | Confirm how much testing targets the AWS control plane versus hosted applications. |
Public offering: Cobalt's cloud pentest simulates attacks on AWS, Azure, and GCP environments in a four-phase assessment aligned with the shared responsibility model: external attack simulation, manual exploitation and chaining beyond configuration checks, assessment of the cloud network perimeter and segmentation, and testing of IAM, storage, networking, and compute against the OWASP Cloud-Native Top 10. A separate cloud configuration review is also offered, and findings are reported in real time.
AWS testing relevance: Testing is delivered by the Cobalt Core, which Cobalt describes as a community of vetted pentesters matched to the customer's stack, and every pentest includes free retesting of individual findings for 6 or 12 months. CREST's public marketplace lists Cobalt Labs with penetration testing accreditation; confirm tester locations and AWS access controls in the agreement.
Official sources: https://www.cobalt.io/services/cloud-pentest-service; https://www.cobalt.io/contact-us
Buyer fit: SaaS and product teams that want AWS testing alongside web and API pentests on one platform.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published four-phase method covering IAM, storage, networking, and compute against the OWASP Cloud-Native Top 10. | The page does not describe AWS-specific services or multi-account coverage; confirm both for large estates. |
| Free retesting of individual findings for 6 or 12 months, with real-time reporting. | Testers come from a community model; ask how cloud specialists are assigned. |
Public offering: IBM's offensive security services, delivered by X-Force Red, describe penetration testing of applications, networks, cloud environments, hardware, and AI systems, with practitioners who validate findings and chain weaknesses together. Service lines include continuous AI-driven testing with expert review, expert-led AI-augmented penetration testing, and adversary simulation, plus compliance and threat-led testing and social engineering. Testing, findings, and remediation are managed in its Red Portal, which integrates with vulnerability management and ticketing systems.
AWS testing relevance: The offensive security page covers cloud environments but does not name AWS services, so confirm AWS scope and methodology. CREST's public marketplace lists IBM with penetration testing accreditation; confirm which team and country will deliver your test and how data is handled.
Official sources: https://www.ibm.com/services/offensive-security
Buyer fit: Multinational enterprises that want AWS and cloud testing from a global provider alongside adversary simulation and compliance-aligned testing.
| Documented strengths | Limits and buying considerations |
|---|---|
| Expert-led testing, continuous AI-driven testing, and adversary simulation managed in Red Portal. | Confirm which findings come from autonomous testing and which from expert-led work. |
| Threat-led and compliance-aligned testing for frameworks such as PCI DSS, SOC 2, FedRAMP, and DORA. | Enterprise contracting can add procurement steps; agree scope, named testers, and retest terms in the proposal. |
Public offering: Redscan, a Kroll business, offers custom cloud penetration testing that combines traditional internal and external testing with cloud configuration review against best practice and CIS benchmarks, covering Amazon Web Services, Microsoft Azure and Azure AD, and Microsoft 365. Assessed issues include authentication flaws, poor privilege management, unpatched vulnerabilities, misconfigurations, and insufficient log management, and the service includes walkthroughs and post-test remediation support.
AWS testing relevance: Redscan states that testers follow each cloud provider's rules of engagement, and it links to a separate AWS page. Confirm IAM, container, serverless, and multi-account coverage, the contracting entity, and tester locations in the agreement.
Certifications: Redscan states that it is a CREST member and that its testers hold CREST, CEH, OSCP, Tiger Scheme QSTM, and CISA/CISM qualifications.
Official sources: https://www.redscan.com/services/penetration-testing/cloud-penetration-testing/; https://www.kroll.com/en/contactus
Buyer fit: Regulated organizations that want AWS testing linked to configuration benchmarking and Kroll's detection and response services.
| Documented strengths | Limits and buying considerations |
|---|---|
| Combines testing with CIS benchmark configuration review across AWS, Azure, and Microsoft 365. | The cloud page does not describe AWS-specific attack-path techniques; ask how IAM escalation is tested. |
| Walkthroughs during the assessment and post-test remediation support. | Report contents are not specified on the cloud page; request a sample cloud report. |
Public offering: Mandiant's penetration testing simulates real-world attacker tactics against networks, applications, cloud-hosted resources, devices, ICS/SCADA systems, and people through social engineering, following a four-step approach from reconnaissance to exploitation and internal access. Its cloud option assesses existing cloud security defenses and controls across popular cloud platforms. Deliverables include technical documentation to recreate findings, risk analysis, and tactical and strategic recommendations, and a separate red team assessment tests detection and response.
AWS testing relevance: Mandiant is part of Google Cloud, and its cloud testing description refers to popular cloud platforms rather than naming AWS. Confirm AWS-specific scope and methodology, tester locations, and data handling in the agreement.
Official sources: https://cloud.google.com/security/consulting/mandiant-penetration-testing; https://cloud.google.com/security/consulting/mandiant-red-team
Buyer fit: Enterprises that want AWS testing or red teaming informed by incident response and threat intelligence.
| Documented strengths | Limits and buying considerations |
|---|---|
| Testing draws on attacker tactics, with a separate red team assessment based on incident response TTPs. | The pages do not name AWS services; confirm IAM, container, and serverless coverage. |
| Deliverables include technical documentation to recreate findings plus tactical and strategic recommendations. | Retesting is not described; confirm fix verification terms. |
Public offering: NCC Group's cloud security assessment covers cloud-native and hybrid environments, using a proprietary configuration scanner that incorporates cloud-provider benchmarks and manual review with read-only console access, and includes container and orchestration reviews. Its wider penetration testing catalogue covers applications, networks, hardware, AI/ML, and red, purple, and black team attack simulation, and reports are available through its Cyber Services Portal.
AWS testing relevance: The penetration testing page does not name AWS, and its cloud assessment emphasizes configuration review, so confirm whether your scope includes exploitation of IAM paths and cross-account trust. CREST's public marketplace lists NCC Group with penetration testing and threat-led penetration testing accreditations; confirm the delivering practice and tester locations.
Certifications: NCC Group's site displays CREST membership and NCSC CHECK penetration testing marks.
Official sources: https://www.nccgroup.com/penetration-testing-services/; https://www.nccgroup.com/contact-us/
Buyer fit: Large organizations that want AWS configuration assurance alongside other specialist testing from one provider.
| Documented strengths | Limits and buying considerations |
|---|---|
| Configuration scanner with cloud-provider benchmarks plus manual read-only console review, including containers. | Read-only configuration review is not exploitation; specify any attack-path testing you need. |
| Reports and vulnerability-management integration through the Cyber Services Portal. | The service page does not state retest terms; confirm fix verification in the proposal. |
Public offering: HackerOne Pentest covers cloud environments alongside web applications, APIs, networks, mobile, desktop, and PCI segmentation; for cloud it assesses infrastructure for misconfigurations, insecure access controls, improper resource segregation, and exposed storage or policies. Cloud testing is delivered through the human-led H1 Pentest rather than H1 Agentic Pentest. Findings are delivered live in the platform, followed by a final report with proofs of concept and retesting after fixes.
AWS testing relevance: The pentest page does not detail AWS-specific techniques, so confirm whether IAM privilege escalation, role assumption, and multi-account paths are in scope. CREST's public marketplace lists HackerOne with penetration testing accreditation; confirm pentester vetting and data handling in the agreement.
Official sources: https://www.hackerone.com/product/pentest; https://www.hackerone.com/contact/pentest
Buyer fit: Product teams that run applications on AWS and want cloud and application testing on the same platform as a bug bounty.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published cloud scope covers misconfigurations, access controls, resource segregation, and exposed storage or policies. | AWS control-plane attack paths are not described; confirm them explicitly. |
| Live findings, a final report with proofs of concept, and retesting after fixes. | The page does not describe pentester vetting; ask who will test your AWS accounts. |
Public offering: BreachLock's cloud penetration testing lists AWS areas including S3 bucket misconfigurations, IAM misconfigurations, insecure EC2 instances, security group and network ACL issues, serverless function vulnerabilities, database security, and identity federation, alongside Azure, GCP, containers, Kubernetes, and the control plane. It states that its AWS testing follows a framework built around AWS penetration testing policies, and its platform combines in-house pentesters with autonomous testing.
AWS testing relevance: BreachLock lists BreachLock Inc. in New York and BreachLock NL B.V. in Amsterdam, and CREST's public marketplace lists Breachlock Ltd with penetration testing accreditation. The cloud page does not describe the human and automated split, report contents, or retests; confirm them in the proposal.
Certifications: BreachLock lists CREST, ISO 27001, and SOC 2 on its site.
Official sources: https://www.breachlock.com/products/cloud-penetration-testing/; https://www.breachlock.com/about/contact/
Buyer fit: Mid-market and compliance-driven teams that want AWS testing with platform-based tracking.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published AWS issue types span S3, IAM, EC2, serverless, databases, and identity federation. | Confirm how much testing is human-led and how cross-account paths are covered. |
| Cloud testing also covers containers, Kubernetes, and the control plane. | Report contents and retest terms are not on the cloud page; request a sample report. |
Public offering: Packetlabs' cloud penetration testing covers AWS, Azure, and GCP, including abuse of IAM roles, trust policies, and token assumptions; public buckets, snapshot leakage, and backup access; container breakout and Kubernetes control weaknesses; CI/CD pipeline injection and secrets exposure; serverless functions; and hybrid paths such as VPN, Direct Connect, and peering. It states that it focuses on exploitability rather than checklist reviews and uses credentialed and white-box testing where appropriate. Reports tie findings to attack paths, impact, and prioritized remediation, with executive summaries.
AWS testing relevance: Packetlabs lists its headquarters in Toronto with offices in San Francisco and Sydney, and publishes a cloud sample report. The cloud page does not mention retesting; confirm retest terms, tester locations, and data handling.
Certifications: Packetlabs states that it is CREST-accredited and SOC 2 Type II attested, and that its testers are OSCP-certified at minimum.
Official sources: https://packetlabs.net/services/cloud-penetration-testing/; https://www.packetlabs.net/services/
Buyer fit: Mid-market and enterprise teams that want manual AWS attack-path testing from a specialist firm.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published cloud scope covers IAM trust abuse, storage exposure, containers, CI/CD, serverless, and hybrid connectivity. | The cloud page does not mention retesting; confirm fix verification. |
| Credentialed and white-box testing, plus a public cloud sample report. | A specialist firm may have less capacity for very large multi-region programs; agree staffing early. |
Public offering: LevelBlue's offensive security services, supported by its SpiderLabs consultants and researchers, include end-to-end penetration testing, expert-led red teaming, threat hunting, threat intelligence, vulnerability management, and data security for on-premises and cloud databases. Findings are integrated into its Fusion platform alongside other LevelBlue services.
AWS testing relevance: The offensive security page does not describe AWS penetration testing specifically, so confirm AWS scope, methodology, and a sample cloud report before buying. The page states that it uses onshore, offshore, and federally cleared staff; define tester locations, subcontracting, and data handling in the agreement.
Official sources: https://www.levelblue.com/solutions/offensive-security-solutions; https://www.levelblue.com/company/contact
Buyer fit: Organizations that want AWS testing from the provider that runs, or could run, their managed security services.
| Documented strengths | Limits and buying considerations |
|---|---|
| Penetration testing, red teaming, threat hunting, and vulnerability management in one offensive security line. | No AWS-specific methodology is published; request one and a sample report. |
| Findings integrate into the Fusion platform with managed security data. | When the same provider monitors your environment, agree how testing independence and escalation will work. |
Public offering: Rhino Security Labs’ AWS penetration testing page sets out a six-step structure for each engagement: AWS service reconnaissance, enumeration and configuration scanning, attack and penetration, post-exploitation, reporting and documentation, and remediation testing. Its AWS service sheet lists IAM privilege escalation paths, EC2 user data and Systems Manager abuse, VPC routes for lateral movement, S3 access, Lambda role escalation, RDS backup access, and attempts to evade CloudTrail and GuardDuty.
AWS testing relevance: Rhino created Pacu, an open-source AWS exploitation framework released in 2018, and published research describing 21 AWS IAM privilege escalation methods. That research is public evidence of AWS depth, but the service sheet dates from 2018, so ask for the current methodology, team, tester locations, and a sample AWS report.
Official sources: https://rhinosecuritylabs.com/penetration-testing/aws-penetration-testing/; https://rhinosecuritylabs.com/aws/pacu-open-source-aws-exploitation-framework/
Buyer fit: Security teams that want AWS privilege escalation and post-exploitation testing from a firm that publishes AWS attack research.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published six-step AWS method that ends with remediation testing. | The AWS service page is brief; request the current scope and a sample report. |
| Created the open-source Pacu framework and published 21 IAM privilege escalation methods. | Public research shows expertise but does not measure the team assigned to you. |
The strongest shortlist in 2026 includes DeepStrike, NetSPI, Bishop Fox, GuidePoint Security, Synack, Cobalt, IBM Security X-Force Red, Kroll, Mandiant, NCC Group, HackerOne, BreachLock, Packetlabs, LevelBlue SpiderLabs (formerly Trustwave), and Rhino Security Labs. NetSPI and Synack merged in October 2026. The right choice depends on whether you need manual AWS exploitation depth, PTaaS, enterprise coordination, red-team support, or a narrower product/security assessment.
DeepStrike publishes this list and lists itself first; list order is not a quality ranking. DeepStrike offers human-led cloud, application, and infrastructure testing with exploit evidence, remediation guidance, and retesting. Evaluate it with the same scoping questions you ask other providers and perform your own due diligence.
AWS penetration testing is an authorized assessment of the customer-controlled parts of an AWS environment under the shared responsibility model. It may include IAM abuse, storage exposure, VPC and compute exposure, API abuse, serverless flaws, container risk, and cloud attack-path chaining. It goes beyond scanner output by validating exploitability, documenting impact, and recommending remediation and retesting.
Choose based on AWS scope and methodology, not brand alone. Confirm how the provider handles IAM privilege escalation, cross-account trust, EKS, Lambda, storage exposure, API Gateway, reporting, and retesting. Review a sample deliverable, ask about production-safety controls, and verify whether the engagement is manual, automated, or hybrid.
There is no reliable universal AWS pentest price because scope drives cost. AWS account count, IAM complexity, Kubernetes and container usage, serverless scope, VPC exposure, public APIs, compliance reporting, urgency, and retesting materially affect effort. Most vendors use quote-based models, so buyers should compare deliverables and evidence depth rather than a single number.
CSPM helps identify posture issues, configuration drift, and policy gaps. AWS penetration testing validates whether those weaknesses are exploitable and what business impact they create when chained together. Security Hub, GuardDuty, Inspector, IAM Access Analyzer, Macie, Config, and CloudTrail are useful, but they do not replace a human-led test of IAM paths, storage exposure, cross-account trust, or cloud attack chains.
A credible AWS pentest should consider IAM privilege escalation, insecure role trust, over-permissioned identities, exposed S3 paths, EC2 and VPC exposure, insecure security groups and routing, metadata-service abuse, secrets exposure, API Gateway authorization flaws, Lambda permission issues, EKS RBAC and secret exposure, ECS task-role issues, and cross-account attack paths where present.
It should. IAM privilege escalation is one of the most important AWS risk areas because cloud compromise is often identity-led. Providers that cannot explain how they test role chaining, AssumeRole trust, permission boundaries, SCP effects, temporary credentials, or cloud API abuse are unlikely to deliver a strong AWS assessment.
It can, but only if scoped. EKS requires dedicated validation of RBAC, secret exposure, pod security assumptions, network policy, service accounts, and the interaction between Kubernetes identities and AWS IAM. If EKS matters, ask for an explicit EKS methodology before purchase.
It can, but many proposals under-scope it. Lambda and other serverless components require testing of execution-role permissions, trigger sources, API integrations, secrets handling, logging, and excessive permissions. Buyers should verify how much of the service is application testing versus cloud-control testing involving Lambda permissions and event flows.
A useful AWS report should contain an executive summary, technical findings, safe proof-of-exploitation, business impact, affected accounts and assets, attack-path context, severity rationale, remediation guidance, and retest results or retest terms. It should separate configuration observations from validated exploit chains.
Frequency depends on change rate and risk. Testing should occur after major architectural changes, before significant launches, and on a recurring cadence for high-risk environments. Fast-changing AWS estates often benefit from PTaaS or recurring validation rather than annual-only testing.
No, not for your own resources on AWS’s list of permitted services, such as EC2, RDS, Lambda, API Gateway, and ECS. You must submit a Simulated Events form at least two weeks ahead for command-and-control, covert red team, phishing, or malware testing. DoS, flooding, Route 53 zone walking, and S3 bucket takeover are prohibited.
Yes, for applications. AWS Security Agent on-demand penetration testing, now sold as AWS Continuum for penetration testing, became generally available on March 31, 2026, and costs $50 per task-hour. Its published scope is the application layer, so it does not replace a human-led test of IAM privilege escalation and cross-account attack paths.
Yes, for Selling Partner API solution providers that handle personally identifiable information. Amazon’s Data Protection Policy requires a penetration test at least every 365 days using an industry-recognized methodology, covering cloud environments, applications, APIs, and storage that process Amazon data. Critical findings must be fixed within 7 days and high-risk findings within 30.
The best AWS penetration testing companies are not interchangeable. The right choice depends on AWS scope, IAM complexity, cloud attack-path risk, reporting quality, retesting, and whether the buyer needs a one-time engagement, a recurring PTaaS model, or a broader red-team-oriented assessment. The strongest providers are the ones that can explain their methodology in AWS terms, separate manual validation from posture tooling, document exploit evidence clearly, and fit your account structure, engineering workflow, and procurement constraints.
DeepStrike publishes this list and lists itself first; list order is not a quality ranking. DeepStrike offers human-led AWS and cloud testing with reproduction evidence, remediation guidance, and direct collaboration. Apply the same selection criteria to every provider, including DeepStrike, against your own AWS scope.
DeepStrike helps organizations validate AWS exposure through manual AWS penetration testing, AWS IAM and privilege escalation testing, S3 and storage exposure testing, EKS and container security testing, Lambda and serverless security testing, AWS/API attack-path validation, continuous penetration testing, remediation tracking, and retesting support.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
