October 4, 2025
Updated: November 5, 2026
Act LXIX/2024 (NIS2) raises the bar: compare Hungarian pentest firms, scopes, cost factors, and compliance tips.

Mohammed Khalil
Penetration testing (pentesting, also known as ethical hacking) simulates real cyberattacks to find and validate exploitable vulnerabilities in systems, networks, and applications. In Hungary it matters in 2026 because Act LXIX of 2024 requires in-scope organizations to manage cyber risk and pass an audit by an SZTFH-registered auditor, and pentest results are practical evidence that security controls work. The main drivers:
For nearby Central European markets, see Austria and Slovenia.
Regulatory Pressure (NIS2, GDPR, ISO 27001):
Cyber Threat Surge:
Compliance and Insurance Needs:
Leading pentesters here follow industry standards like OWASP and NIST e.g. NIST SP 800‑115 and use a mix of black box, gray box, and white box methods. They simulate advanced attack scenarios including social engineering, API attacks, cloud misconfigurations to reveal hidden vulnerabilities.
Hungary's NIS2 law is Act LXIX of 2024 on Cybersecurity, applicable since 1 January 2025 and implemented by Government Decree 418/2024 (XII. 23.). The Supervisory Authority for Regulatory Affairs (SZTFH) registers in-scope organizations and oversees the mandatory cybersecurity audit, which only an auditor on its register may perform. Organizations operating before 2025 had to complete their first audit by 30 June 2026; organizations registered later have two years from registration (SZTFH, checked 3 November 2026). None of the four other providers in this list appears on SZTFH's register of NIS2 auditors (last updated 16 September 2026, checked 3 November 2026), so use them for testing that supplies audit evidence and contract the audit itself with a registered auditor.
The audit procedure is set by Decree 1/2025 (I. 31.) SZTFH. It lists testing as an audit method alongside document review and interviews, names earlier vulnerability-assessment results among the documents auditors examine, and includes penetration testing by an independent expert or team (Behatolásvizsgálat – Független szakértő vagy csapat) in its control list. A pentest report is useful audit evidence, but the audit itself must come from a registered auditor.
Other bodies affect scoping and reporting. According to ENISA's overview of incident reporting, the Special Service for National Security is Hungary's national incident-handling centre (operating as NCSC Hungary), financial entities report major ICT incidents to the Magyar Nemzeti Bank (MNB) under DORA, and personal-data breaches go to the data protection authority NAIH. Financial entities identified by their competent authority must also run threat-led penetration testing at least every three years under DORA Article 26.
Public-sector buyers procure under Act CXLIII of 2015 on Public Procurement, normally through the government's electronic procurement system (EKR), so foreign or remote providers should confirm they can bid and contract that way. We found no Hungarian state accreditation scheme for penetration testers comparable to the UK's CHECK scheme; ask for the assigned testers' certifications and check any CREST claim on CREST's own directory.
Several firms stand out in Hungary’s cybersecurity market, ranging from Hungarian boutiques and managed security providers to remote providers. DeepStrike publishes this list and lists itself first; list order is not a quality ranking. Its customers page shows organizations it publicly references.
We started from providers that publicly offer penetration testing to organizations in Hungary: firms with a Budapest office or a Hungarian-language service, plus remote providers that market VAPT internationally. On 3 November 2026 we checked each provider's own website for service scope, published testing process, retesting, stated company and tester certifications, office locations, and Hungary-specific services such as support for Act LXIX of 2024. This is desk research: we did not run test engagements with these firms, and we did not use prices or client reviews. Each entry states what the provider is best suited for and what to confirm before you sign.
Public offering: DeepStrike's penetration testing services describe human-led testing across applications, cloud environments, and infrastructure, supported by a findings and collaboration platform. Its public process covers planning, reconnaissance, vulnerability discovery, controlled exploitation, reporting, and technical support. Published reports include reproduction steps, remediation guidance, and root-cause information; the proposal should define exact coverage and commercial terms.
Hungary relevance: Founded in 2016, DeepStrike LLC is headquartered in Newark, Delaware, has 11–50 employees, and also publishes a business address in Dubai, UAE (IFZA Business Park). It delivers testing remotely for Hungarian clients; define tester locations, permitted subcontracting, and data-handling restrictions in the engagement agreement.
Team certifications: OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate, as shown on DeepStrike's services page.
Official sources: Pricing , Contact Us
Buyer fit: Engineering teams that need application, cloud, or infrastructure testing with direct remediation collaboration.
| Documented strengths | Limits and buying considerations |
|---|---|
| Human-led testing with reproduction evidence, root-cause information, and remediation guidance. | The service description is not an independently measured quality comparison. Assess the assigned team and a relevant sample report. |
| The published Basic plan lists Slack collaboration, customizable reports, and 12 months of remediation retesting. | No numeric price is displayed on the pricing page. Basic is a one-shot test; recurring coverage belongs to a different plan, with contract-specific terms. |
| Team certifications shown on the services page include OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate. | These are individual tester credentials, not a company-level accreditation; ask which certified testers will be assigned to your engagement. |
Public offering: Hacktify runs a bug bounty platform on which a community of ethical hackers continuously tests client systems, and states that clients pay only for vulnerabilities found. Its penetration testing service covers networks, web and mobile applications, wireless networks, and social engineering in black, grey, or white box form, following planning, automated reconnaissance, manual testing, and reporting steps. It also helps set up vulnerability disclosure policies and offers consulting for NIS2, ISO/IEC 27001, and Hungarian Act LXIX of 2024, including training and assessments.
Hungary relevance: Hacktify International Kft. is a Hungarian company with a Hungarian-language website and a Hungarian phone contact; its site does not publish a street address. Confirm the contracting entity, how platform researchers are vetted, where testers are located, and how findings data is handled in the agreement.
Certifications: Hacktify's site displays Certop ISO/IEC 27001 and ISO 9001 certification logos and a National Security Authority logo; ask for the current certificates and their scope.
Official sources: https://www.hacktify.eu/behatolasteszt/; https://www.hacktify.eu/kapcsolat/
Best fit: Hungarian organisations that want continuous crowd-sourced testing combined with penetration tests and help with NIS2 compliance.
What sets it apart in Hungary: Of the providers listed, Hacktify is the only one that pairs a Hungarian-language bug bounty platform with penetration testing and consulting that names Act LXIX of 2024, which suits organizations that want ongoing researcher coverage after a point-in-time test.
Limitation / what to confirm: Its pentest page does not mention retesting or name tester certifications, and Hacktify does not appear on SZTFH's NIS2 auditor register (checked 3 November 2026). Confirm retesting, the assigned testers, and the contracting entity, and keep any NIS2 audit separate from the testing engagement.
| Documented strengths | Limits and buying considerations |
|---|---|
| Bug bounty, penetration testing, and vulnerability disclosure services are offered alongside NIS2 and ISO 27001 consulting. | Crowd-sourced findings depend on researcher participation; agree scope rules, payout terms, and how duplicates are handled. |
| Published pentest process covers planning, reconnaissance, manual testing, and a severity-ranked report with remediation recommendations. | The pentest page does not mention retesting or tester certifications; ask for both and request a sample report. |
Public offering: Cyberintelsys offers vulnerability assessment and penetration testing of web, mobile, and API applications, networks, cloud, Active Directory, OT, IoT, and medical devices, plus source code review and LLM testing. Its offensive line includes red, blue, and purple teaming, social engineering, and phishing simulation, and it also sells managed security and compliance consulting for frameworks such as ISO 27001, SOC 2, PCI DSS, GDPR, and DORA. Its VAPT page describes reports with reproduction steps and remediation guidance, followed by retesting.
Hungary relevance: Cyberintelsys lists entities in Bengaluru, India, and Singapore and does not publish a Hungarian or other European office, so delivery to Hungarian clients is remote. Its website displays CREST and ISO 27001 imagery; confirm current CREST status on CREST's public register and define tester locations, reporting language, and data handling in the agreement.
Official sources: https://cyberintelsys.com/services-and-solutions/vapt/; https://cyberintelsys.com/contact-us/
Best fit: Organisations comfortable with remote, English-language delivery that want a broad VAPT and compliance catalogue under one contract.
What sets it apart in Hungary: It is the only listed provider without a European office; its case rests on the breadth of published test types, including OT, IoT, medical devices, and LLM applications, and an explicit re-testing step in its VAPT process.
Limitation / what to confirm: Its VAPT page does not mention Hungary or Hungarian-language reporting, and we could not confirm its CREST status from a public CREST source. Confirm that English-only reports are acceptable to your auditor, check CREST status directly with CREST, and set GDPR-compliant data-transfer terms.
| Documented strengths | Limits and buying considerations |
|---|---|
| Broad published scope from web, API, and mobile apps to OT, IoT, medical devices, and LLM testing. | Breadth across many test types does not show depth in each; request a sample report for your asset class. |
| The published VAPT process includes reproduction steps, remediation guidance, and retesting. | No Hungarian office is published; agree time zones, onsite needs, and data residency upfront. |
Public offering: White Hat IT Security offers penetration testing and vulnerability assessment that combines automated scanning with manual testing guided by OWASP and MITRE ATT&CK, covering API, mobile, web, and desktop applications, hardware and IoT, internal and external infrastructure, and phishing simulation, with reports that include remediation steps. Adversary simulation, red, blue, and purple teaming, and threat-led penetration testing (TLPT) are listed alongside. The company also runs a 24/7 SOC and managed detection and response, incident response, cyber threat intelligence, and GRC advisory for NIS2, ISO 27001, TISAX, and DORA.
Hungary relevance: White Hat IT Security lists its Budapest office at Ötvös János u. 3, 1021, with further offices in Munich and Dubai. As a multi-country provider, confirm which office's testers perform the work and where test data is stored in the agreement.
Certifications: Its certifications page displays ISO 27001 and Cybersecurity Made in Europe badges, a Microsoft Partner of the Year 2024 badge (Microsoft listed White Hat IT Security as a 2024 Hungary country winner), and individual tester badges such as OSCP, OSWE, OSCE, CISSP, and CISA. Ask for the current ISO 27001 certificate and its scope.
Official sources: https://whitehat.eu/cybersecurity-services/; https://whitehat.eu/
Best fit: Organisations that want pentest findings to feed directly into managed detection, incident response, and compliance work.
What sets it apart in Hungary: White Hat combines a Budapest office with a Microsoft-verified MXDR service and lists threat-led penetration testing (TLPT), which is relevant to financial entities that may face DORA TLPT.
Limitation / what to confirm: Its services page offers ISO 27001, NIS2, and TISAX audit preparation, but White Hat does not appear on SZTFH's NIS2 auditor register (checked 3 November 2026), so the statutory audit needs a separate registered auditor. Agree how testing stays independent from any SOC it runs for you.
| Documented strengths | Limits and buying considerations |
|---|---|
| Testing sits alongside an in-house 24/7 SOC, MDR, and incident response. | If White Hat also monitors your environment, agree how testing independence and findings escalation will work. |
| Published scope includes TLPT and red, blue, and purple teaming, plus GRC support for NIS2, TISAX, and DORA. | Managed security is the core of the portfolio; ask about the testing team's experience and request a sample report. |
Public offering: Silent Signal has an ethical hacking department that performs technical security assessments of infrastructure, applications, networks, and organisations, from code analysis to vulnerability testing and social engineering, and an information security consulting department covering risk assessment, regulatory compliance, business continuity, and security awareness. It also runs a dedicated IBM i security practice that offers assumed-breach penetration testing, configuration assessments, and a vulnerability feed. The company says it follows methodologies including OSSTMM, ISSAF, NIST SP 800-115, and OWASP.
Hungary relevance: Silent Signal Kft. lists its office at Nagymező utca 54-56, H-1065 Budapest, and says it has performed IT security assessments since 2009. Agree the reporting language, assigned testers, and data handling in the agreement.
Certifications: Silent Signal states that it is ISO 9001 and ISO 27001 certified and that its experts hold certifications including CISSP, OSCP, OSCE, OSWP, GPEN, GWAPT, CISA, and CISM.
Official sources: https://silentsignal.eu/services; https://silentsignal.eu/contact
Best fit: Hungarian enterprises that want research-driven manual testing, including IBM i environments, from a local boutique.
What sets it apart in Hungary: Silent Signal is a Budapest boutique that has performed security assessments since 2009 and runs a dedicated IBM i security practice, which suits organizations whose core systems run on IBM i midrange platforms.
Limitation / what to confirm: Its services page does not mention NIS2 or Act LXIX of 2024 and gives limited scope detail. Ask how its reports can support your SZTFH audit evidence, which language reports are delivered in, and who the assigned testers are.
| Documented strengths | Limits and buying considerations |
|---|---|
| Its experts report vulnerability research in products from vendors such as Cisco, Oracle, IBM, and Symantec. | A boutique team may have limited capacity for large parallel engagements; agree dates and named testers early. |
| A dedicated IBM i practice covers assumed-breach testing and configuration assessment of midrange systems. | The main services page gives limited scope detail; request the methodology and a sample report. |
Beyond the specialist firms above, buyers in Hungary can also consider larger consultancies:
Hungary’s penetration testing ecosystem blends boutique ethical hacking firms and specialized local providers with global consultancies. While multinational firms deliver scale and compliance breadth, local specialists can offer Hungarian-language delivery and on-site availability. Compare named testers, manual effort and retesting terms either way.
Pentest firms in Hungary typically offer these core services:
These services address common vulnerability classes. For example, providers check for unpatched servers, weak credentials, SQL injection, broken auth, SSRF/path traversal in APIs, and more. See OWASP guidance and common network vulnerabilities for details. Many firms highlight adherence to OWASP and CWE standards.
Ask each provider which standards its web testing follows, such as the OWASP Top 10, CWE Top 25, or NIST SP 800‑115.
Hungary's cybersecurity law, Act LXIX of 2024 (applicable since January 2025), requires in-scope entities to apply appropriate security measures and undergo cybersecurity audits. It aligns with GDPR's Article 32, which mandates technical security measures and a process for regularly testing their effectiveness.
In practice, auditors expect pentest reports to serve as evidence that controls work: for example, PCI DSS requires periodic penetration tests, and ISO 27001 expects technical vulnerabilities to be identified and managed.
DeepStrike and peers often emphasize these frameworks. DeepStrike’s services page lists team certifications such as OSCP, OSWE, GXPN, GWAPT, and CREST CPSA; ask any provider which certified testers will be assigned.
When you hire a Hungarian pentest firm, verify they know NIS2 obligations and GDPR requirements for instance, their report should document fixes for appropriate technical measures under GDPR.
To illustrate why security testing is crucial, recall the 2022 breach of Hungary's KRÉTA school administration system. Attackers used a spear-phishing email in September 2022 to compromise a developer's project manager account and later published KRÉTA source code; police stated that students' personal data was not retrieved. Because KRÉTA is mandatory in Hungarian schools, the incident showed how one supplier compromise can expose a nationwide government platform.
Regular pentesting and phishing simulations of critical suppliers and applications help catch such weaknesses beforehand. Though that incident predates Hungary's NIS2 law, it underscores the importance of ongoing security assessments.
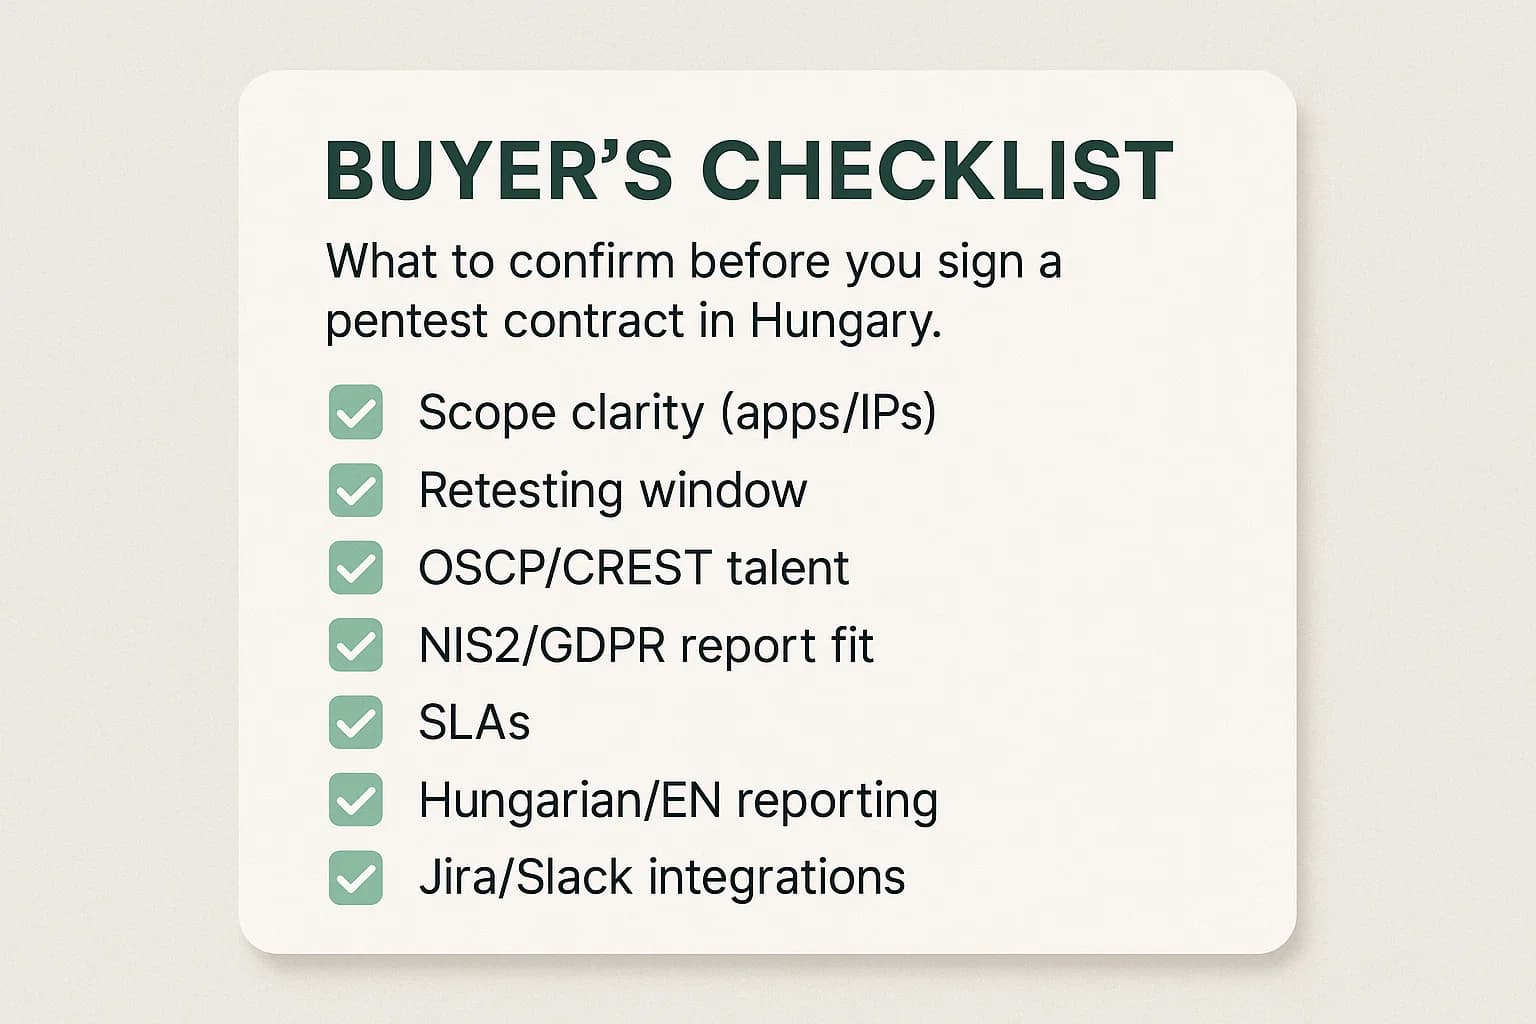
Choose a penetration testing partner in Hungary by matching its published scope to your assets, checking the assigned testers' certifications and a sample report, confirming retesting terms and reporting language, and asking how its reports will serve as evidence in your NIS2 audit by an SZTFH-registered auditor. Key factors:
Experience & Certifications:
Scope of Services:
Methodology:
Reporting & Remediation:
Continuous Testing PTaaS:
Pricing and Value:
Local Presence & Language:
A handy checklist is our penetration testing RFP writing guide, which covers all the above points when you request proposals. Remember: penetration testing isn’t a one time checkbox. The best partnerships involve periodic or continuous testing, knowledge transfer, and a focus on building your security program.
In today’s Hungary, robust cyber defenses demand regular validation. Pentesting helps you uncover hidden risks, fix them proactively, and produce evidence for auditors and regulators. Experienced providers bring knowledge of NIS2/GDPR, industry frameworks, and hands on skills to find the weaknesses automated scans miss.
The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our Penetration Testing Services to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
Besides DeepStrike (the publisher of this guide; human-led application, cloud, and infrastructure testing delivered remotely), options include Hacktify (Hungarian bug bounty platform, penetration testing, and NIS2 consulting), Cyberintelsys (India- and Singapore-based VAPT provider delivering remotely), White Hat IT Security (Budapest; SOC-backed pentesting and incident response), and Silent Signal (Budapest; ethical hacking, security consulting, and IBM i security).
Each has its niche. See our Top Penetration Testing Companies comparison for details.
Costs vary by scope: the number of applications, user roles, API endpoints, hosts and cloud accounts, plus testing depth, reporting and retesting terms. Ask providers to quote the same defined scope.
PTaaS subscriptions run monthly. Factors include target complexity, number of assets, and compliance requirements. Remember, quality pentests reduce the risk of expensive breaches.
Web pentests examine a web app’s security. Testers will probe for SQL injection, cross site scripting XSS, broken auth/IDOR, CSRF, SSRF, and other OWASP Top 10 flaws. They may also test APIs/GraphQL endpoints and business logic.
Reports include exploited examples and fixes. For a general definition, see our web application penetration testing services page.
A vulnerability scan is automated and finds known issues. Penetration testing is manual and goes deeper: testers exploit vulnerabilities to demonstrate risk. It can chain exploits (e.g., XSS → session hijack → data exfiltration) to show real impact.
Think of pentesting as the ethical hacker’s simulated attack that goes beyond what tools alone can do. See our comparison in vulnerability assessment vs penetration testing.
Neither law explicitly says do pen testing, but they require adequate security controls and regular reviews. GDPR Article 32 calls for appropriate technical measures and a process for regularly testing their effectiveness.
Hungary's NIS2 law, Act LXIX of 2024, requires in-scope entities to implement risk-management measures and undergo a cybersecurity audit by an SZTFH-registered auditor (the first audit was due by 30 June 2026 for organizations operating before 2025). In practice, pentesting is one of the best ways to produce evidence that controls work.
PTaaS is a subscription model where pentesting is ongoing rather than one off. It typically includes a platform with live dashboards, continuous testing, and retests after fixes. PTaaS is ideal for DevOps environments that change often.
DeepStrike offers a continuous penetration testing platform alongside manual reviews. PTaaS means you get security feedback year round, not just annually.
Pentesting and red teaming are both offensive (red-side) exercises. A pentest aims to find and validate as many vulnerabilities as possible in a defined scope; a red team exercise pursues specific objectives to test detection and response. A blue team defends, and in some engagements red and blue teams work together to improve security.
For more, see red team vs blue team explained. A full red team exercise may also include physical and social attacks; both are proactive security measures.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
