October 8, 2025
Updated: November 6, 2026
Layered controls, fast VPN patching, and clear BYOD policies to curb phishing, exploit and ransomware risks in hybrid work.

Mohammed Khalil
Viewed alongside broader cybersecurity statistics, remote work isn't just a trend; it is the new normal. The U.S. Bureau of Labor Statistics reports that 22.6% of employed people teleworked or worked at home for pay in March 2026, which keeps an organization's attack surface far wider than the office network. Home routers and personal devices often lack corporate-grade security, so remote workers can be easy targets.
Attackers follow that footprint. Verizon's 2026 Data Breach Investigations Report found that exploitation of vulnerabilities is now the most common initial access vector at 31%, while phishing attacks, scams that trick users into giving up passwords or installing malware, still opened 16% of breaches. In the 2025 DBIR, edge devices and VPNs made up 22% of exploitation targets, up from 3% a year earlier. This article breaks down the key remote work security risks and how to mitigate them.

Remote work security means applying enterprise grade protections to distributed employees. In other words, it’s the policies, tools and practices that protect sensitive data, communications, and system access when staff are off site. This includes things like requiring VPNs and endpoint protection on home devices, encrypting remote connections, and enforcing strict data handling rules. As more workers stay remote or hybrid, these controls must extend beyond the office to keep cyber threats at bay.
Remote and hybrid work are now a permanent part of how companies operate, which keeps the attack surface wide. Attackers are taking notice: in November 2024, New York regulators (NYDFS) warned regulated companies about remote technology workers with ties to North Korea getting hired under false identities.
In June 2025, the U.S. Justice Department announced searches of 29 suspected "laptop farms" across 16 states tied to North Korean remote IT workers who had obtained jobs at more than 100 U.S. companies. With distributed teams, even small security lapses like a weak Wi-Fi password or outdated software can lead to breaches and widespread damage.
Remote work also shows up in breach costs. IBM's Cost of a Data Breach Report 2025 lists a remote workforce among the factors that raise costs, adding about $131,212 to the average breach, and the 2026 edition puts the global average at a record $4.99M.
In short, 2026's cyber risk profile is defined by where work happens, and home offices are no exception.
These are the newest primary-source figures that matter for remote and hybrid teams. Most are cross-industry benchmarks rather than remote-only measurements, so read them as the risk context a distributed workforce operates in.
| Statistic | Figure | Year and scope | Source |
|---|---|---|---|
| U.S. workers who teleworked or worked at home for pay | 22.6% | March 2026, employed people | U.S. Bureau of Labor Statistics |
| Breaches with a human element | 62% (60% a year earlier) | 2026 DBIR, all breaches | Verizon 2026 DBIR |
| Breaches that began with credential abuse | 13% (exploitation now leads at 31%) | 2026 DBIR, known initial access vectors | Verizon 2026 DBIR |
| Breaches that began with pretexting | 6% | 2026 DBIR, all breaches | Verizon 2026 DBIR |
| Business email compromise reported to the FBI | 24,768 complaints and $3.05 billion in losses | 2025, U.S. complaints | FBI IC3 2025 Internet Crime Report |
| All cybercrime losses reported to the FBI | $20.877 billion, up 26% from 2024 | 2025, U.S. complaints | FBI IC3 2025 Internet Crime Report |
| Users who accept a simple approve/deny MFA push on the first try | About 1% | Microsoft studies, published 2022 | Microsoft Entra blog |
Sources: Verizon 2026 DBIR, FBI IC3 2025 Internet Crime Report, Microsoft Entra blog on MFA fatigue (2022) and the U.S. Bureau of Labor Statistics. For the full loss breakdowns, see our cybercrime statistics and business email compromise statistics.
Two patterns stand out. Attackers still reach remote teams through people and identities: phishing (16%), credential abuse (13%) and pretexting (6%) remain major ways in, even as exploited VPN and edge devices take the top spot. And because business email compromise costs U.S. victims billions of dollars a year, the payment and approval workflows that remote staff handle by email are a direct target.
Remote setups introduce several unique security challenges. The most critical risks include:
Unsecured Wi Fi & Home Networks:
Unmanaged Personal Devices BYOD:
Data Leakage & Shadow IT:
Phishing & Malware:
Collaboration & Cloud App Risks:
Insider Threats & Reduced Visibility:
Vulnerable VPNs & Edge Devices:
For a distributed team, identity is the control plane. One compromised account can unlock email, SaaS apps, cloud consoles, source code and the VPN at once, without the attacker ever touching an office network. Verizon's 2026 DBIR found credential abuse at the start of 13% of breaches and a human element in 62% of them. MFA is essential, but attackers now target the MFA process itself.
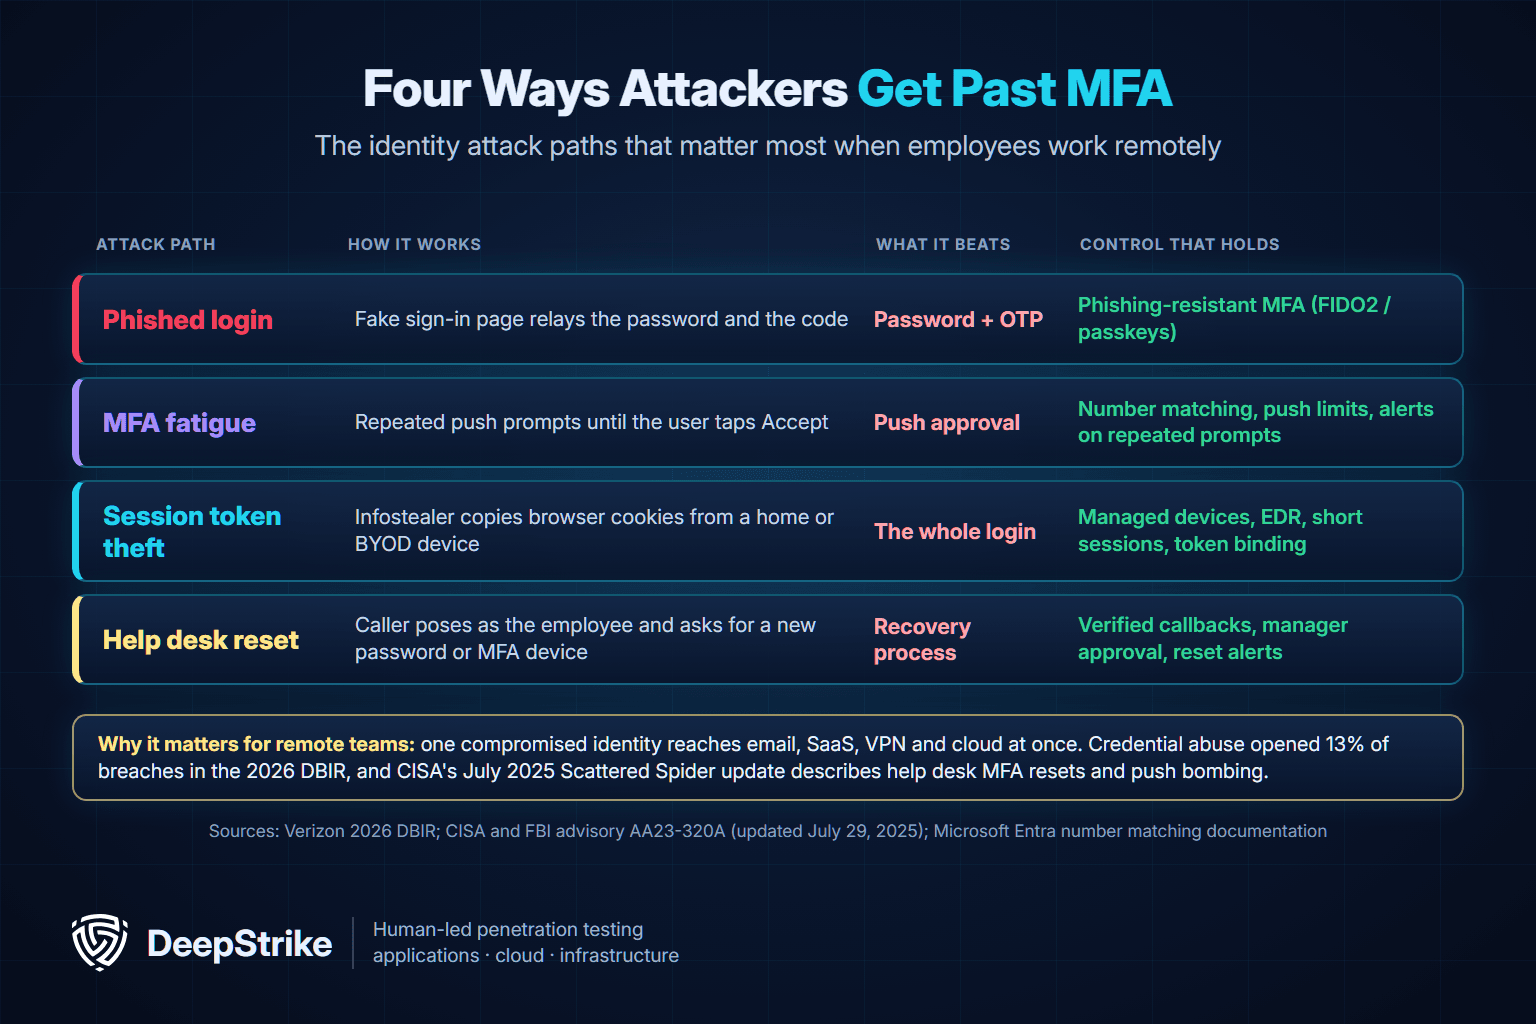
After stealing a password, an attacker sends repeated push prompts until the user taps Accept to make them stop. Microsoft reported in 2022 that about 1% of users accept a simple approve/deny request on the first try, which is enough when an attacker can try many accounts. Microsoft Authenticator now uses number matching for all push notifications, so the user must type the number shown on the sign-in screen. Check that every other push-based MFA tool in your stack does the same, cap repeated prompts, and alert on bursts of denied requests. Our guide to MFA fatigue attacks covers detection in more depth.
Infostealer malware on a home laptop or BYOD device copies saved passwords and browser session cookies. A stolen session token lets the attacker reuse a login that has already passed MFA, so no prompt ever appears. That is why the BYOD figure above matters: in the 2025 DBIR, 46% of infostealer-infected systems holding corporate logins were non-managed devices. Shorter session lifetimes, re-authentication for sensitive actions, device-bound sessions where your platform supports them, and EDR on every device that reaches corporate apps all shrink the window. Our account takeover statistics show how often stolen credentials and sessions turn into takeovers.
Remote employees rarely walk up to the IT desk, so a phone call asking for a password or MFA reset sounds normal. Attackers exploit that. The CISA and FBI advisory on Scattered Spider, updated on July 29, 2025, describes actors posing as employees to convince help desk staff to reset passwords and transfer MFA to a device the attacker controls, alongside push bombing and SIM swapping. Verizon's 2026 DBIR also found pretexting at the start of 6% of breaches. Verify identity with something an attacker cannot look up online, such as a callback to a number already on file or manager approval, and alert both the user and the security team on every MFA reset. A social engineering penetration test shows whether your help desk process holds up.
Remote teams work inside SaaS apps, and an app a user connects through an OAuth consent screen can keep access to mail, files or chat even after a password change. Public file links, guest accounts and dormant contractor accounts add more exposure. Limit user consent to verified apps, send high-risk permissions to admin approval, review connected apps and external sharing on a schedule, and remove accounts as part of offboarding. Our OAuth security guide explains how consent grants work, and our shadow IT statistics show how much SaaS use sits outside IT's view.
The table below maps each identity risk to its business impact and the control to validate.
| Identity risk | How it happens | Business impact | Control to validate |
|---|---|---|---|
| Phished credentials | Fake login pages or adversary-in-the-middle phishing relay the password and code. | Email, SaaS, VPN and cloud compromise. | Phishing-resistant MFA, email security, phishing simulations. |
| MFA fatigue | Repeated push prompts are sent until the user approves one. | Account takeover even with MFA enabled. | Number matching, FIDO2 security keys, push limits, risk-based prompts. |
| Session hijacking | Cookies or tokens are stolen from browsers or endpoints. | MFA bypass and direct access to SaaS sessions. | Device binding, shorter token lifetimes, session anomaly monitoring. |
| OAuth abuse | A malicious or risky app receives persistent SaaS permissions. | Long-lived access to email, files, chat, CRM or code. | OAuth app audit, admin consent workflow, permission review. |
| Help desk reset abuse | An attacker talks support into resetting MFA or a password. | Account takeover, including privileged accounts. | Identity verification testing, callback rules, support playbooks. |
| Privilege creep | Users keep access after role changes, or accounts stay active after offboarding. | Larger blast radius after any compromise. | Access reviews, just-in-time access, offboarding checks. |
VPNs still matter for legacy applications, but a compromised VPN account can reach far more than the user needs if the network behind it is flat. Zero Trust Network Access (ZTNA) grants access per application after checking the user and the device, which shrinks the blast radius. NIST SP 800-207 describes this shift from the network perimeter to individual resources. Neither model is safe by default: ZTNA policies can still be too broad or skip device checks. If you keep a VPN, decide whether split tunneling is allowed, since it changes which security controls see remote traffic.
| Access model | Strength | Weakness | What to test |
|---|---|---|---|
| Traditional VPN | Works for legacy apps and broad remote connectivity. | Large blast radius if one user account is compromised. | MFA, segmentation, exposed services, patching, impossible-travel alerts. |
| ZTNA | Application-level access and better segmentation. | Misconfiguration can grant too much access or skip device checks. | Policy enforcement, device posture, app scope, contractor access. |
| SSO + SaaS access | Central identity and user lifecycle management. | One account compromise can expose many apps. | MFA, session controls, OAuth grants, access reviews. |
| Privileged access | Controls admin workflows and sensitive actions. | High-value target for attackers. | PAM, just-in-time access, logging, separate admin accounts. |
Measure remote access risk by blast radius, not only by whether the login is secure: ask what one stolen account could reach. For adoption and maturity data, see our zero trust statistics.
Contractors and very small teams without a corporate gateway sometimes fall back on consumer VPN services. If you are comparing them, Cybernews has a useful comparison of NordVPN and Surfshark covering security, privacy, protocols and performance. A consumer VPN encrypts traffic on untrusted Wi-Fi, but it does not replace the identity and device checks described above.
To mitigate the above risks, adopt a defense in depth strategy. Key steps include:
Combining these controls creates multiple hurdles for attackers. For example, even if a phishing email captures a password, MFA and endpoint security can stop the breach in its tracks. Layering secure remote access, MFA and endpoint protection means no single failure hands an attacker the keys.
Some industries face extra scrutiny. Financial firms (GLBA and PCI regulated) are constantly targeted, and in November 2024 New York regulators specifically warned them about North Korea-linked operatives posing as remote tech hires.
Healthcare is similarly at risk: AHA noted 386 health care cyberattacks reported in 2024 as of early October, and calls ransomware a threat-to-life crime given its potential to shut down hospitals. IBM's 2026 Cost of a Data Breach Report puts the average healthcare breach at $6.64M.
In these sectors, strong remote controls, encrypted telehealth tools, and dual control on critical transactions are used alongside strict monitoring and compliance measures.
Policies describe how controls should work; testing shows whether they hold. Before you expand remote hiring, onboard contractors, move to new SaaS apps or close an office, validate the controls most likely to fail under real attack pressure:
If you hire across borders, an employer of record can handle verified onboarding, in-country payroll and offboarding, which narrows several of the identity and access gaps in this checklist. Test the handoff anyway, because the accounts it creates and removes still land in your SSO and SaaS tools.
Retest after fixes, because identity, SaaS and endpoint settings change constantly in distributed teams. DeepStrike's red team assessments chain these paths together the way a real attacker would, cloud penetration testing covers the SaaS and cloud side, and continuous penetration testing keeps validation running as configurations change.
Remote working dramatically expands the cyber attack surface, unsecured home routers, personal devices, and lack of office oversight all invite threats.
The key takeaway for 2026: awareness alone is not enough. Businesses must enforce layered controls (MFA, VPN or Zero Trust access, endpoint security, encryption, and fast patching of remote-access devices) for every remote connection.
Keep your software and policies up to date, and make sure every remote employee is trained. With a defense in depth strategy, you can let teams stay flexible without gambling with your security.
Ready to Strengthen Your Defenses? The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture or uncover hidden risks, DeepStrike, one of the top penetration testing companies, is here to help.

Our experts provide clear, actionable guidance to protect your business wherever work happens. Explore our penetration testing services to see how we can uncover vulnerabilities before attackers do. Drop us a line we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
The top risks include insecure home Wi-Fi, outdated personal devices, phishing and social engineering, vulnerable VPN gateways, and shadow IT (unsanctioned apps and file sharing). In Verizon's 2026 DBIR, exploited vulnerabilities opened 31% of breaches and phishing opened 16%. Prevent these with VPN+MFA for connectivity, prompt patching of remote-access devices, strong endpoint protection, and clear data policies.
Require that all remote access goes through a corporate VPN or a Zero Trust network solution. Protect those logins with multi-factor authentication so stolen passwords aren’t enough. Keep VPN software and configurations updated, and monitor for unusual access.
It should mandate security measures on personal devices: latest OS and antivirus/EDR installed, full disk encryption, and strong passcodes. Companies often use MDM/UEM to enforce these requirements and enable remote wipe. The policy should also forbid moving sensitive corporate data to personal apps.
Combine user training with technical controls. Regularly train employees to recognize phishing and run simulated tests. Use email filtering/anti-phishing tools. Most importantly, enforce multi-factor authentication on all accounts: this way, a phished password alone is not enough to log in. Use phishing-resistant MFA (FIDO2/WebAuthn passkeys or security keys) where possible, because some phishing kits relay one-time codes and push approvals, and push bombing can wear users down.
Zero Trust is a security model built on never trust, always verify. Every access request even on the internal network is authenticated and authorized. For remote work, it means continuously validating user identity and device security for each session, and limiting permissions. It minimizes what attackers can reach even if they obtain valid credentials.
No. A VPN encrypts the connection, but a stolen VPN login can still reach large parts of the network if segmentation is weak, and VPN gateways are themselves a top exploitation target. Pair VPN or ZTNA access with phishing-resistant MFA, device posture checks, least-privilege access, fast patching of the gateway and monitoring of remote sessions.
MFA fatigue, also called push bombing, is when an attacker who already has a password sends repeated push prompts until the user approves one. Microsoft reported in 2022 that about 1% of users accept a simple approve/deny prompt on the first try. Number matching, limits on repeated prompts, alerts on bursts of denials and phishing-resistant MFA reduce the risk.
The common routes are adversary-in-the-middle phishing pages that relay the code, MFA fatigue, session cookies stolen by infostealer malware, and social engineering of the help desk to reset MFA. CISA's July 2025 update on Scattered Spider describes help desk resets and push bombing. Phishing-resistant MFA, short sessions, managed devices and verified reset procedures close most of these gaps.
Test critical remote access, identity, SaaS and cloud controls at least once a year and after major changes, such as a new VPN or ZTNA rollout, an identity provider migration or a large contractor onboarding. PCI DSS, for example, requires penetration testing at least once every 12 months and after significant changes. Higher-risk environments benefit from more frequent or continuous testing.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
