June 21, 2026
Updated: November 5, 2026
Recent law firm data breaches in 2026, legal-sector breach statistics, how the attacks worked, what they cost, and the security testing that reduces client data risk.

Mohammed Khalil
Quick answer: Law firm data breaches are rising. BakerHostetler handled more than 30 law-firm incidents in 2024 and nearly double that in 2025, and at least 10 Big Law firms disclosed breaches between Memorial Day and Labor Day 2026, according to Law.com. Recent victims include Jones Day, Quinn Emanuel, McDermott Will & Schulte, Greenberg Traurig and Seyfarth Shaw. Most began with phishing or social engineering of one employee, often by a fake IT support contact, then a theft of a few client files and an extortion threat. In surveys, 39% of legal tech leaders reported a breach in the past year.
2026 law firm data breach statistics highlight how legal-sector cyber risk is driven by concentrated client data, ransomware, email compromise, remote access flaws, cloud/SaaS use, document management systems (DMS), client portals, third-party services, and insufficient proof of security testing. Surveys and incident data show law firms face frequent breaches and a high likelihood of client data exposure: 39% of legal technology decision-makers in an Arctic Wolf and Above the Law survey said their firm had a breach in the past year, and BakerHostetler's 2026 incident report says law-firm incidents nearly doubled in 2025. These incidents often go beyond IT downtime: attacks can leak privileged communications, litigation strategy, M&A documents, discovery files, billing records and regulated client data. Such breaches can create confidentiality, professional responsibility, contractual, regulatory, operational, and client-trust concerns, depending on jurisdiction, matter type, and affected data.
This article compiles publicly available 2021–2026 data and annotates each statistic by its source (law-firm-specific, legal-sector benchmark, ransomware benchmark, etc.) to avoid conflating general breach stats with law firm evidence. We explain which figures specifically involve law firms versus broader benchmarks. Throughout, we connect these statistics to actionable security priorities: for example, enforcing multi-factor authentication (MFA), securing cloud document sharing, auditing DMS permissions, testing backups, vetting vendors, conducting penetration tests, and running incident response tabletop exercises. The goal is to show that law firm cybersecurity is fundamentally a client-data risk management issue, not just an IT checklist. By focusing on evidence of control effectiveness (e.g. through penetration testing and verification), firms can meet client and regulatory demands for proven security, not just promises on paper.
This 2026 guide combines law-firm-specific breach reports, legal industry security surveys, ABA ethics guidance, ransomware and breach benchmarks, government data (FBI and CISA), threat-intel reports, and public case studies. Each statistic is clearly labeled by type (e.g. “law-firm survey,” “legal-sector benchmark,” “ransomware benchmark,” “case study,” etc.) so readers know whether it reflects law firms specifically or broader trends. Only verified numbers are used; broad breach or ransomware figures are given as context unless a source explicitly cites legal organizations. Source links point to official reports or reputable publications where available.
| Statistic | Data Type | What It Shows | Law Firm Implication | Source |
|---|---|---|---|---|
| 29% of lawyers said their firm had experienced a security breach (ever) | Law-firm survey | More than a quarter of respondents report at least one breach; 19% did not know. | Breaches are a common legal-sector risk, and many lawyers lack visibility into incidents. | ABA 2023 Cybersecurity TechReport |
| 46% of 50–99-attorney firms (about 35% of 100+ firms) reported a breach | Law-firm segment | Mid-size firms reported the highest breach rate in the ABA's latest size breakdown (2021 survey). | Mid-size firms hold large-firm data with smaller security teams. | ABA Legal Technology Survey 2021 (figures from secondary summaries; not confirmed against the ABA report, which is not publicly accessible) |
| 39% of firms had a breach in the last year | Law-firm survey (160+ legal tech decision-makers, published Jan 2024) | A large minority of firms report a recent security breach. | Roughly 2 in 5 firms note a recent breach, so the threat is active. | Arctic Wolf / Above the Law |
| 56% of breached firms lost client data | Law-firm survey | More than half of breaches involved confidential client data loss. | Any breach is likely to expose client files or communications. | Arctic Wolf / Above the Law |
| 26% of firms feel “very prepared” for incidents | Law-firm survey | Only about 1 in 4 firms feel highly prepared. | Most firms lack confidence in their response readiness. | Arctic Wolf / Above the Law |
| 60% cite attack sophistication as top challenge | Law-firm survey | Six in ten point to attack sophistication as their biggest challenge. | Firms see advanced, tailored attacks as their main hurdle. | Arctic Wolf |
| ~20% of firms experienced a cyberattack in the past year | Law-firm survey (500 US legal professionals, 2025) | 1 in 5 surveyed firms reported an attack. | Attacks on firms of all sizes are routine. | Proton |
| 39% of attacked firms lost or exposed data (about 8% of all respondents) | Law-firm survey (2025) | Many attacks led to actual data loss or exposure. | Detection and containment speed decide whether an attack becomes a breach. | Proton |
| Law-firm incidents nearly doubled in 2025 | Incident-response data | BakerHostetler handled roughly twice as many law-firm incidents as in 2024, partly due to Silent Ransom Group. | Law firms are an increasingly specific target. | BakerHostetler 2026 DSIR |
| $682,702 average ransom paid in 2025 (+36%); $4.2M average initial demand | Ransomware benchmark (all industries) | Ransom payments rose again in 2025 after falling in 2024 ($501,338). | Extortion pressure is rising; tested backups and IR plans matter. | BakerHostetler 2026 DSIR |
| $1M median initial ransom demand, Legal & Government (2023) | Ransomware benchmark | Legal and government victims faced higher median demands than the $600K all-industry median. | Attackers price law-firm data at a premium. | Arctic Wolf Labs 2024 Threat Report |
| $1.88M average ransom payment in Q2 2026 | Ransomware benchmark | Coveware says the average was skewed by Silent Ransom Group's campaign against law firms. | Data-theft extortion of law firms is driving large payments. | Coveware Q2 2026 |
| 18.9% of ransomware cases hit Professional Services (Q4 2025) | Ransomware benchmark | Professional services (including law firms) was the top sector in Q4 2025; 13.1% in Q2 2026. | Law firms sit in a consistently targeted sector. | Coveware |
| 36 confirmed ransomware attacks on US law firms and legal companies in 2025 | Law-firm incident count | 318,676 people were notified across these attacks. | Ransomware against US legal organizations is frequent and public. | Comparitech |
| ~$820M ransomware payments in 2025 (2024 revised to $892M) | Ransomware industry stat | Total payouts across industries dipped about 8%. | Ransomware remains a large criminal business. | Chainalysis |
| $3.05B BEC losses in 2025 ($2.77B in 2024) | Fraud benchmark (all industries) | Business email compromise losses keep rising. | Payment redirection through law-firm email is a major fraud vector. | FBI IC3 2025 |
| 191,561 phishing/spoofing complaints in 2025 (193,407 in 2024) | Fraud benchmark (all industries) | Phishing remains one of the most reported cybercrimes. | Law firms must guard email and credentials. | FBI IC3 2025 |
| 3,611 ransomware complaints in 2025 (3,156 in 2024) | Fraud benchmark (all industries) | Reported ransomware complaints rose year over year. | Assume ransomware is a clear threat requiring backups and an IR plan. | FBI IC3 2025 |
| 22% of respondents' firms were asked by a client to complete a security questionnaire; 50% of 100+ lawyer firms received client security-requirements documents | Law-firm survey | Client vetting is common for large firms but rare for smaller ones. | Expect client demands for proof of security to grow. | ABA 2023 Cybersecurity TechReport |
Table: Key 2023–2026 law firm and legal-sector breach statistics, with data type and source. Each stat is labeled as law-firm-specific, legal/professional benchmark, or industry report. For example, the “39% had a breach” stat is from a law-firm survey, whereas the FBI IC3 figures are industry-wide crime report data. The professional services share of ransomware comes from Coveware incident data, and the business email compromise (BEC) losses are from FBI IC3. Law firms should focus on actionable gaps reflected by these stats: for instance, if only 26% feel very prepared, then improving incident response readiness is a priority. Likewise, because credential abuse was the most common initial access vector (22%) in Verizon's 2025 DBIR and stolen credentials appeared in about 88% of basic web application breaches, enforcing MFA and monitoring is critical.
These figures show that law firm breach risk isn’t just the number of incidents: it’s about what sensitive data is exposed and how quickly attacks escalate. Broad breach or ransomware stats are useful context but should be interpreted with care (e.g. the Coveware and IC3 data cover all industries, not law firms alone; see our all-industry data breach statistics for that baseline). The most instructive benchmarks are those labeled as law-firm or legal-sector. For example, when 56% of breached firms lose client data, it signals that any breach can compromise privilege, not just corporate secrets. Similarly, Professional Services topping Coveware's Q4 2025 sector list tells us law firms are prominent targets. Crucially, the stats point to fixable gaps: rising ransom payments in 2025 and FBI warnings about Silent Ransom Group show extortion pressure on law firms is increasing, while high phishing counts and limited client security vetting (22% of firms receive questionnaires) show where defenses remain weak. The key takeaway is that law firm breach statistics must be translated into tangible risk metrics (MFA coverage, DMS permission reviews, tabletop testing, etc.) so firms can prove they’ve actually closed these gaps.
Search for "law firm data breach" in 2026 and most results are news, because the year brought an unusual run of public disclosures from large US firms. The table lists incidents that firms confirmed publicly or reported to state attorneys general, using what the firms themselves said. Attribution to a threat group appears only where a named source made it, and most firms have not confirmed who attacked them.
| Date (2026) | Law firm | What the firm disclosed | Data involved |
|---|---|---|---|
| Mar 30 to Apr 6 | Jones Day | A "phishing" incident; Silent Ransom Group posted the data on its leak site on March 30 | A limited number of dated files for 10 clients |
| Early 2026 | Orrick, Herrington & Sutcliffe | A limited phishing incident the firm says it stopped quickly | Data of a small number of clients |
| July | WilmerHale | Named in a proposed class action over a breach affecting the firm | Not detailed in the cited report |
| August | Goodwin Procter; Herbert Smith Freehills Kramer | Breaches disclosed to US state regulators | Personal data reported to regulators |
| Aug 14 | Quinn Emanuel | Social engineering; one temporarily compromised user account reached stored files for a single application | A limited number of client documents |
| Aug 28 | McDermott Will & Schulte | An "isolated social engineering incident involving a single user," reported to state attorneys general | Files with Social Security numbers and health data |
| Early September | Holland & Knight | Social engineering gave an attacker unauthorized remote access to a firm computer | A small number of files affecting 14 clients |
| Early September | Katten | Social engineering; attackers obtained files but, the firm says, no system access | A very small number of files with client information |
| Sep 10 | Greenberg Traurig; Eckert Seamans | Greenberg Traurig says an unauthorized actor posted a limited number of documents on the dark web; both firms now face proposed class actions | Documents of a small number of clients |
| Sep 22 | Seyfarth Shaw | A person posing as the IT help desk deceived an employee into emailing client documents to an outside account | Names and Social Security numbers of at least 300 people |
| October | Squire Patton Boggs; Holland & Knight | Breach disclosures filed with state regulators | Sensitive personal information, per the filings |
Sources: Reuters on Jones Day, Quinn Emanuel and McDermott, Greenberg Traurig and Eckert Seamans and Seyfarth Shaw; the ABA Journal on Orrick; Non-Billable on Holland & Knight and Katten; Law360 on Seyfarth's notice count, the October filings and the Eckert Seamans lawsuits; Above the Law on the Greenberg Traurig class actions.
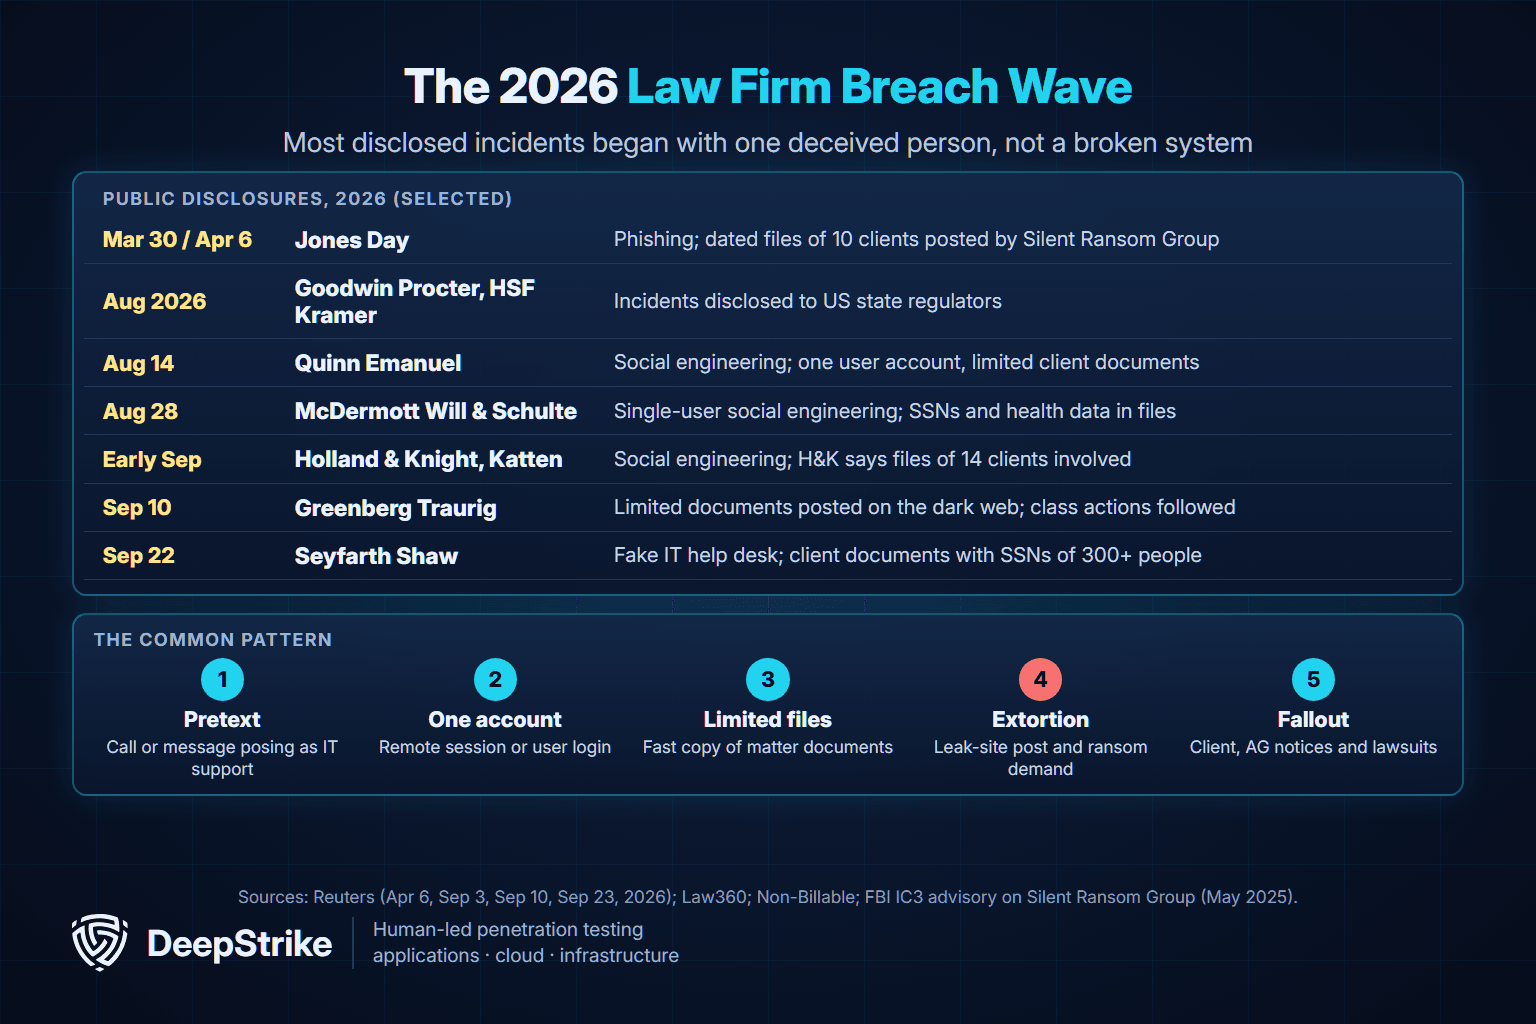
Three patterns stand out. First, the entry point was a person, not a firewall. Firms described phishing, a fake IT help desk, or a social engineering contact that led to remote access. That matches the FBI warning that Silent Ransom Group, also known as Luna Moth and Chatty Spider, contacts staff while posing as IT support, copies data and then demands payment. It also matches BakerHostetler's finding that phishing caused 30% of the 1,250+ incidents it handled in 2025. Our vishing statistics show how common these phone pretexts have become across industries.
Second, the files taken were few but sensitive. Most firms said only a "limited number" of documents were involved, yet those documents held Social Security numbers, health data or client matter files. A small theft is still a reportable breach, and for a law firm it can mean notifying clients, state regulators and sometimes courts.
Third, litigation now follows within weeks. Greenberg Traurig and Eckert Seamans both faced proposed class actions soon after their disclosures. That fits BakerHostetler's 2026 incident data: class actions were filed after 14% of the incidents it handled in 2025, up from 9% in 2024.
For defenders, the lesson is to test the help desk and the people around it, not only the perimeter. Verify caller identity before any password or MFA reset, block unapproved remote-access tools, and limit what one account can reach in the DMS. A social engineering penetration test shows whether a fake IT call would work at your firm before an extortion group tries it.
No public dataset gives an average cost for law firm breaches specifically, so treat any single figure with care. The best law-firm data points are settlements and ransoms. Orrick's 2023 breach, which exposed data of 637,620 people, ended in an $8 million class settlement. Arctic Wolf put the median initial ransom demand for legal and government victims at $1 million in 2023. Coveware said its Q2 2026 average ransom payment of $1.88 million was skewed by Silent Ransom Group's campaign against law firms.
Those figures leave out forensic work, notification, outside counsel, lost billable time and clients who leave after a breach. For cross-industry benchmarks of those costs, see our cost of a data breach analysis.
A law firm data breach is any security incident where unauthorized parties access, exfiltrate, encrypt, destroy, or otherwise compromise data belonging to a law firm or its clients. Because law firms handle highly sensitive client information, breaches include many scenarios:
Ransomware attacks with data theft – Files encrypted or stolen by ransomware gangs (often double-extortion events).
Email account compromise – Attackers get into attorney or staff email (often via phishing or credential stuffing).
Business Email Compromise (BEC) – Phishing or other methods cause employees to reroute funds or send data (e.g. fake wire instructions or fraudulent invoices).
Phishing-based credential theft – Email or web phishing leading to stolen usernames/passwords.
Cloud storage exposure – Accidental public sharing or misconfigured cloud repositories (e.g. unsecured AWS, OneDrive, Google Drive or SharePoint files).
Document Management System (DMS) exposure – Weak permissions or bugs in systems like iManage or NetDocuments exposing client files.
Case-management platform breach – Unauthorized access to tools (e.g. Clio, Relativity, or iManage projects) holding case records.
Client portal compromise – Flaws in or misuse of portals where clients upload or download documents.
eDiscovery data leak – Discovery evidence or litigation document sets leaked from storage or tools like Relativity.
Remote access compromise – VPN, RDP, or VDI accounts hacked, giving outsiders a foothold in the network.
Third-party legal vendor breach – A provider (e.g. eDiscovery firm, IT consultant, billing service) is hacked, exposing the law firm’s data.
Insider misuse – Employees or contractors leak or steal client data maliciously or negligently.
Misdirected email – Sensitive information sent to the wrong recipient (e.g. family law files or social security numbers sent to unintended address).
Lost/stolen device – Unencrypted laptops, phones, or backups containing client data are lost or stolen.
Exposed backups – Backup media or cloud backups left unprotected.
API or web portal vulnerability – Flaws in custom or SaaS APIs that grant unintended access to documents or case data.
Vendor support account compromise – Attackers obtain high-level access by compromising a law firm’s external IT support account or a connected service.
Each of these incidents may differ in impact: some primarily cause data confidentiality loss (e.g. data exfiltration), others cause operational disruption (e.g. encryption of files, email systems down), and many combine both. In legal contexts, breaches also raise professional issues: loss of attorney-client privilege, professional responsibility concerns (ABA Model Rule 1.6), regulatory exposure (HIPAA, GLBA, state privacy laws), and damage to client relationships. When client data (medical records, trade secrets, litigation strategy, etc.) is stolen, the harm can be far greater than typical corporate breaches. The following sections explore the main attack vectors and risks specifically affecting law firms, along with controls to validate that these vectors are secured.
Law firm cybersecurity today is as much about maintaining client trust and compliance as it is about IT. Law firms store confidential information that is often more valuable than their own financial data: M&A and IPO documents, patent filings, court strategies, healthcare data, trade secrets, and millions in financial transactions. Attackers target law firms to reach this data, either for direct theft/extortion or as leverage against clients (e.g. leaking a deal’s contents or suing a firm for privilege waiver). This makes law firms prime targets not because they have weaker IT, but because they hold goldmines of sensitive information.
Effective security programs in law firms must therefore cover people, process, and technology – with an emphasis on proof of control, not just policy. Small and midsize firms can face risks comparable to large firms but often have smaller security teams. Meanwhile, enterprise clients (banks, healthcare, government) increasingly require their outside counsel to demonstrate strong controls (via questionnaires, SOC reports, cyber insurance requirements, etc.).
The table below summarizes common law-firm risk areas, why each matters to legal data, typical weaknesses, and how to validate it:
| Law firm risk area | Why it matters | Common weakness | Validation method |
|---|---|---|---|
| Client Files (DMS) | Central repository of matter data (case files, contracts) | Overly broad permissions, lack of matter segmentation | DMS access audit (who can see what), permission reviews |
| Primary client/court communication channel | Phishing, credential compromise, lack of MFA | Email security review (MFA checks, inbox rule/OAuth audits) | |
| Remote Access (VPN/RDP) | Attorneys work from varied locations (home, court, travel) | Weak or no MFA, device policy gaps | Remote access pentest, MFA enforcement check |
| Cloud/SaaS | M365, Google Workspace, iManage, Clio, eDiscovery platforms | Misconfiguration (excess sharing, weak admin roles) | Cloud app review (Azure/AWS/CASB configurations), SaaS audit |
| Ransomware | File encryption + potential data theft | Untested backups, no IR plan, delayed detection | Ransomware readiness test (backup restore, IR tabletop) |
| Third-party vendors | eDiscovery, IT support, billing, client portal providers | Unrestricted vendor access, insufficient vetting | Vendor access review, contractual security questionnaire |
| Client Portals/API | External file exchange sites for clients/counsel | Broken auth, improper access controls | Web application/API penetration test |
| Email/Identity | Mailboxes contain privileged data and PII | Single-factor auth, session hijacking | Identity review (OAuth app audit, session management) |
| Mobile Devices | Laptops and smartphones out in the field | No mobile device management (MDM), no encryption | Endpoint security audit, MDM policy check |
| Incident Response (IR) | Breach containment and communication | Untested IR plan, no tabletop exercises | Tabletop exercise report, breach drill documentation |
Each row above maps a risk to its typical law-firm context. For example, firms often store all client case files in a DMS. If permissions are not reviewed regularly, an outsider could access multiple clients’ files. A DMS access audit can validate matter-level controls. Likewise, email is the lifeline of legal work. Weak email security (missing MFA or overlooked inbox rules) is a top vector; an email/identity security review (MFA enforcement, mailbox rule audit) helps catch those gaps. Remote desktop or VPN without strong MFA is another high-risk gap: testing remote access paths will reveal if ransomware gangs can slip in. For each critical area (cloud, DMS, email, remote access, vendors, etc.), law firms should require verification (pentests, audits, backups, drills) – not just checkbox compliance – to reduce breach risk.
Law firms hold highly sensitive client data that can be far more damaging if exposed than typical corporate data. Types of client data at risk include: privileged legal communications (attorney-client emails, memos), litigation and arbitration strategy, settlement negotiations, M&A acquisition files, due diligence documents, intellectual property (patents, trade secrets), employment and personnel files, health or HIPAA-protected information (in healthcare cases), financial records (bank statements, tax returns), real estate closing papers, personal identity documents (SSNs, driver’s licenses), contracts, and large sets of discovery evidence.
Even if the firm’s own assets (cash, IP) are not heavily impacted, exposure of client data can have severe consequences:
Attorney-client privilege breach (client lawsuits or loss of privilege protections).
Regulatory fines if protected data (PHI, financial data) was leaked.
Client loss of trust and reputational harm.
Market harm from leaking M&A or IPO details.
Litigation disadvantage if strategy or evidence is revealed to opposing parties.
Controls needed: Firms should enforce least-privilege and segmentation (e.g. matter-level access in DMS), encryption (at rest and in transit), robust logging of file access, and strict data retention policies (to avoid “too much old data” exposure). In incident response, privilege review becomes key: affected data may trigger different obligations (notifying only some clients vs. many).
The table below outlines key client data types, why they’re sensitive, breach impact, and how to validate their protection:
| Client data type | Why it’s sensitive | Breach impact | Control to validate |
|---|---|---|---|
| Privileged communications | Attorney-client confidentiality | Loss of privilege, malpractice risk | DMS and mailbox access log review |
| M&A documents | Market-moving corporate strategy | Insider trading risk, deal disruption | Matter-level permission audit |
| Litigation strategy | Case plans and evidence | Gives opponent advantage | Access logging, compartmentalization |
| eDiscovery files | Vast sets of documents (often PII) | Mass data breach (billions of pages) | Repository permissions review |
| Healthcare client data | Protected health information (PHI) | HIPAA breaches, regulatory action | Data handling and classification audit |
| Financial records | Bank accounts, transactions | Fraud risk, privacy breach | Encryption-at-rest, audit trails |
| Identity documents | Social security, licenses | Identity theft, privacy violation | Secure storage policies, retention review |
| IP/patents | Trade secrets, patents | Competitive disadvantage | Document classification, NDA controls |
| Employee/legal staff data | Payroll, criminal background checks | Employment law issues, identity theft | Access controls, anonymization |
| Criminal defense records | Sensitive details of accused clients | Fair trial concerns, defamation risk | Encrypted storage, limited access |
Table: Examples of client data types and their breach implications. Protecting each type requires tailored controls (and testing those controls). For instance, privileged emails should be secured and monitored since their exposure can completely undermine legal representation. Matter-level access audits and DMS permission reviews can validate that such data is only accessible to the right staff. EDiscovery repositories should be scanned for misconfigurations because leaked eDiscovery data can involve millions of pages of sensitive info.
In summary, all client data is high risk, but breaches involving privileged or regulated data carry an extra layer of professional and legal consequences. Law firms should inventory data by sensitivity (e.g. a data map by matter type) and ensure the highest-risk categories are locked down and audited.
Ransomware poses a dual threat to law firms: encryption downtime and data theft/extortion. Legal firms face growing “double extortion” and pure data-theft campaigns that steal client-related data. Coveware data shows Professional Services (including law firms) was the single most targeted sector (18.9%) in Q4 2025, and the FBI warns that Silent Ransom Group has consistently targeted US law firms since 2023, using phone-based IT-support impersonation to steal data and extort firms. Coveware's Q3 2026 report goes as far as forecasting that most of the Am Law 100 will be affected by this campaign.
Ransomware impact on law firms:
File encryption – Attorneys lose access to case files, billing systems, and internal records, threatening court deadlines and client deliverables. Lost productivity and emergency IT costs mount.
Data theft – Confidential client files or privileged communications may be exfiltrated and threatened with publication or sale. This creates notification duties and client harm even if files are recovered.
Extortion pressure – Cybercriminals may threaten to leak client-related data (case details, personal info) if ransom isn’t paid, further damaging firm reputation.
Email or DMS outage – Ransomware may down email servers or document systems, blocking communication and collaboration.
Third-party vendor outages – If a vendor (e.g. cloud provider or eDiscovery service) is hit, a law firm’s data or workflows can be disrupted.
Client notification/legal fallout – Any stolen PHI, financial, or personal data can trigger breach notification laws (HIPAA, state privacy) and potential client lawsuits.
Firms with untested backups face catastrophic downtime. Even with backups, the choice to restore or negotiate depends on confidence in data recovery (hence the need for practice runs). Law firms must also navigate post-ransomware response considerations: clients must be informed promptly if client files were exposed, and client communications and disclosure decisions should be handled carefully with appropriate legal review.
| Ransomware impact | Law firm example | Why it matters | Validation method |
|---|---|---|---|
| Encrypted files | Attorneys locked out of cases | Case delays, missed deadlines, billable hours lost | Backup restore drill (test recovery) |
| Data theft | Client contracts and strategy stolen | Confidentiality breach, breach notifications, malpractice | Endpoint logging/EDR review |
| Extortion threats | Hackers threaten to publish client data | Reputational damage, client loss, legal liability | IR tabletop exercise |
| Email outage | Encrypted mail server | Critical client/partner communication halted | Email continuity simulation |
| Document system outage | DMS (NetDocuments/iManage) locked | All case files inaccessible, cripples work | DMS resilience test (switchover) |
| Third-party outage | Cloud hosting or vendor services down | Loss of practice support (eDiscovery, billing, court e-filing) | Vendor response tabletop |
Table: Ransomware extortion impacts on law firms with validation methods. For example, a backup restore test (restoring a DMS from backup) verifies whether encrypted files can be recovered. Incident response tabletop exercises should simulate scenarios with stolen client data to ensure the team knows how to communicate with clients and authorities.
Noteworthy: Orrick, Herrington & Sutcliffe suffered a network intrusion in 2023 that exposed data of 637,620 people and ended in an $8M class settlement. ALPHV/BlackCat exfiltrated about 4TB (roughly 2.2 million files) from Australia’s HWL Ebsworth in 2023, according to the Australian government, and published part of it. In 2025, Williams & Connolly disclosed that a nation-state actor accessed a small number of attorneys' email accounts. These cases show attackers targeting legal intelligence. Firms need tested incident response plans, including legal review of privilege issues and coordination with law enforcement, because ransomware and extortion are as much a legal problem as a technical one.
Email is the backbone of legal practice and one of the most common entry points for attackers. Law firm email accounts often hold years of sensitive correspondence, client documents, and privileged strategy. Attackers exploit this centrality via:
Phishing – Fake emails (from clients, courts, bar associations) trick attorneys into revealing credentials or clicking malware links. A single clicked link can seed account takeover or network intrusion. The FBI’s IC3 received 191,561 phishing/spoofing complaints in 2025 (193,407 in 2024), indicating how common this threat is.
Stolen credentials – Password reuse or undetected breaches can allow attackers to buy or guess passwords. (Verizon’s 2025 DBIR found credential abuse was the most common initial access vector, at 22% of breaches, highlighting the risk if MFA is not enforced.)
MFA fatigue/consent attacks – Social engineering to trick a user into approving an MFA push, or malicious OAuth app authorization compromising email.
Inbox rule abuse – After takeover, attackers set forwarding or hiding rules to steal or silo ongoing communications.
Business Email Compromise (BEC) – Sophisticated fraud where attackers impersonate a partner or client to reroute funds or steal data. For example, an accountant’s wire instructions are changed in email, costing the firm/clients money. FBI IC3 reported $2.77B in BEC losses in 2024 and $3.05B in 2025, so even a single redirected settlement payment can have major impact.
Vendor or client impersonation – Attackers pose as trusted parties. Lawyers, staff, or clients unknowingly send files, data, or payments to the fraudsters.
Client impersonation/invoice fraud – Fake invoices for litigation support or ghost client, leading to misdirected payments or disclosure of matter info.
Even without mass data exfiltration, email-based attacks are costly. A clever phishing email can siphon off six-figure escrow funds, or silently compromise a partner’s account and undermine an entire multi-year case. Title and escrow firms face the same pattern; see our real estate wire fraud statistics. The table below highlights how these email risks play out:
| Email risk | How it appears | Law firm impact | Validation method |
|---|---|---|---|
| Phishing | Attorney clicks malicious link | Credential theft, mailbox compromise | Phishing simulation tests, MFA enforcement check |
| BEC (invoice fraud) | Fake email alters payment instructions | Financial loss (stolen client funds) | Payment process review (dual-approval) |
| OAuth abuse | Malicious app granted mailbox access | Persistent hidden access, data exfiltration | OAuth/app permission audit |
| Inbox rule abuse | Email forwards or moves initiated by attacker | Delayed breach detection, missed alerts | Mailbox rule/script audit |
| Client impersonation | Fake client requests documents or transfers | Data leak, financial fraud | Out-of-band verification (phone check) |
| Account takeover | Attacker sends phishing from the attorney’s real mailbox | Follow-on phishing, reputation damage | Identity session review (logs, unusual access) |
Table: Email compromise and account takeover scenarios at law firms. For instance, phishing simulations (and mandatory MFA) can greatly reduce credential theft. Inbox rule audits might find malicious forwarding a firm didn’t know about. Dummy payment orders tested in the payment workflow (e.g. forcing an HR person to call the partner to confirm wire transfers) can prevent BEC fraud.
Given email’s critical role, every law firm should protect and test its email systems. This includes enforcing phishing-resistant MFA on all mailboxes, monitoring unusual login locations, scanning for suspicious inbox rules, and training users on verifying payment requests. Regularly reviewing third-party mail integrations (OAuth) is also crucial. Since email compromises can go undetected for months, continuous monitoring and rapid incident investigation (e.g. via EDR alerts on credential misuse) are key to mitigating this top risk vector.
Modern law firms rely heavily on cloud and SaaS platforms: Microsoft 365 or Google Workspace for email/docs; NetDocuments or iManage as DMS; Clio or PracticePanther for case management; Relativity or Zapproved for eDiscovery; client portals (ShareFile, CP Secure); and more. While these tools improve collaboration, they introduce exposure if misconfigured. Common issues include:
Over-permissioned data – Cloud drives, SharePoint sites or DMS folders often accumulate “Anyone with link” shares or guest accounts. An audit may find thousands of files shared outside the firm.
Excessive admin roles – Unchecked admin privileges in M365/Azure or DMS can let a compromised admin account expose data or create backdoors.
Cloud OAuth trust – Third-party apps connected to mail or documents (e.g. eSignature services, Slack, ChatGPT, CRM) may have more access than intended. A malicious or vulnerable app can siphon data.
Missing encryption – Some SaaS solutions store data encrypted only on the vendor side (e.g. OneDrive’s default encryption). Without client-side keys, a breach of the vendor or account can expose plaintext data.
Versioning and retention – Inadequate version control or retention policies mean a brief breach could lose data permanently, or violate regulations by not preserving required records.
Shadow IT – Use of unsanctioned tools (private Dropbox, personal email, etc.) creates unmonitored risks.
In law-firm contexts, these problems matter because client files need strict access controls. The table below lists common systems and typical exposure paths:
| System/Platform | Common exposure | Breach path | Validation method |
|---|---|---|---|
| Microsoft 365 / Google Workspace | Broad sharing in OneDrive/Drive/SharePoint/Teams | Phishing, OAuth abuse, misconfigurations | Cloud security review (permissions, MFA, conditional access) |
| Document Management System (DMS) | All matter documents | Over-permissioned folders | DMS permission audit (ensure least privilege) |
| eDiscovery platforms (Relativity, etc.) | Large evidence sets | Accidental guest links or mis-collection | Repository access review, user activity logs |
| Case-management system | Client/matter records (names, details) | Exploited web/API vulnerabilities | Application pentesting (auth, access control) |
| Client portals (Citrix, Clinked, etc.) | External file exchanges (court filings, invoices) | Broken authentication or token theft | Web app/API penetration test |
| Billing and finance systems | Client billing info, trust account data | Credential compromise | Access and transaction audit |
| Legal SaaS integrations (APIs, SSO) | API keys and SSO tokens | Compromised service account | SaaS/OAuth token review, API key rotation |
Table: Cloud, DMS, and legal SaaS exposures. For example, a review of M365 might uncover SharePoint sites open to “Anyone with the link”, or Gmail accounts without MFA. Testing could include cloud configuration audits (CIS benchmarks for Azure/GCP), DMS permission simulations, and penetration tests of any public-facing law firm web apps or client portals.
In practice, law firms should treat their cloud and SaaS environment as an extension of their perimeter. Regular audits of Teams/SharePoint sharing, strict MFA for all cloud admins, and token management (avoiding excessive OAuth consents) are crucial. When using third-party hosted services (like SaaS DMS or eDiscovery), the firm’s security team must ensure those vendors have robust controls too – and ask for SOC 2/ISO27001 reports. However, ultimate responsibility lies with the firm’s own configurations and user behavior. Validating these systems often means running specialized pentests or configuration reviews specifically on each platform, rather than assuming a cloud provider or vendor fully secures them.
While this article is not legal advice, law firms operate under heightened duties that directly tie to cybersecurity:
Confidentiality duties (ABA Model Rule 1.6) – Lawyers must protect client information. ABA ethics opinions (e.g. Formal Opinion 483) interpret this to include reasonable cybersecurity. A breach can raise professional responsibility concerns if controls were inadequate.
Technology competence (ABA Rule 1.1) – Attorneys must stay reasonably informed about technology risks affecting client representation. Failing to understand basic cyber hygiene can breach this duty.
Data privacy laws – Law firms handling healthcare (HIPAA), financial (GLBA), or personal data (state privacy laws, GDPR for foreign clients) must comply with breach notification and security rules. Breaching these can trigger regulatory exposure separate from malpractice liability.
Contractual and client requirements – Corporate or government clients often include security clauses in engagement letters or require annual questionnaires. Ignoring these can lead to contract defaults or lost business.
Cyber insurance – Policies typically mandate controls (MFA, EDR, backups, testing). If a firm claims coverage but lacks proof of controls, insurers can deny claims after a breach.
The gap in legal practice is often evidence, not just policy. It’s common to have written policies on backups or incident response, but without testing and logs to show they work in practice, client auditors and regulators may not be satisfied.
| Compliance / duty area | Why it matters | Common gap | Evidence to prepare |
|---|---|---|---|
| Attorney-client confidentiality | Ethical duty + client trust | Broad access to privileged data | Access reviews, encryption/EDR logs |
| Tech competence (ABA 1.1) | Must be aware of cyber risks | No security training/test plan | Security assessment report, training records |
| Incident response readiness | Ethics require prompt action (ABA 1.6) | Untested or incomplete IR plan | Tabletop exercise report, IR plan document |
| Engagement agreements | Clients may require security standards | No documented controls or audits | Pentest summary, compliance reports |
| Regulated client data | HIPAA/GLBA/CCPA demand safeguards | Untracked PHI/PII flows | Data inventory, classification maps |
| Cyber insurance underwriting | Controls required for coverage | Unsupported claims (e.g. “we have MFA”) | MFA enforcement evidence, EDR logs, backup tests |
Table: Compliance and professional responsibility areas for law firms. For instance, ABA Formal Opinion 483 discusses safeguards such as encryption and access controls in the context of reasonable efforts to protect client information. Having a written IR plan isn’t enough; a live tabletop exercise provides tangible evidence of preparedness. Many firms discover that what matters to regulators or insurers is whether you can show controls and testing outcomes, not just having policies.
Notably, professional-client confidentiality means that any breach could also trigger malpractice or bar discipline, even if no laws were explicitly broken, if the firm did not make reasonable efforts to protect client information. For example, the American Bar Association’s Technology Survey indicates a significant fraction of firms have already been breached, yet less than 35% of legal professionals are familiar with their legal obligations for handling cyberattacks (Proton's 2025 survey). Formal Opinion 483 (2018) and Formal Opinion 477R (2017) stress that encryption and reasonable safeguards are expected. In short, compliance for law firms is becoming demonstrable security: it’s about actually testing MFA, monitoring logs, proving backups work, and documenting those results so you can show due diligence to clients, auditors, or courts.
Any law firm looking to gauge its cybersecurity posture should cover multiple domains. Below is a practical checklist of key questions and evidence to gather in a comprehensive assessment. This is not exhaustive but covers the most critical areas for client data protection and incident readiness:
| Area | Assessment question | Evidence to collect |
|---|---|---|
| Client data inventory | What client data is stored, where (on premises, cloud, SaaS)? | Data map or database inventory, matter catalog |
| Data sensitivity classification | Which clients/matters involve regulated data or high-risk info? | Data classification policy, list of PHI/PII assets |
| Access controls | Who can access each type of sensitive matter? | DMS and case system permission lists, admin reports |
| Identity & Email | Are mailboxes protected by MFA? Are mail rules/OAuth apps reviewed? | MFA enrollment reports, mailbox rule/OAuth audit logs |
| Cloud security | Are sharing settings (OneDrive/Drive/SharePoint) locked down? | Cloud permissions review, conditional access configs |
| Document Management | Are matter permissions enforced and audited? | DMS permission reports, audit logs |
| Remote work / endpoints | Are VPN/RDP and devices secured? Is EDR deployed? | VPN/MFA policies, device encryption status, EDR logs |
| Backups & recovery | Are systems and data backed up and recoverable? | Backup architecture diagram, recent restore test results |
| Email filtering | Is phishing filtered/monitored? Are exceptions handled? | Email gateway/phishing report, allowed sender lists |
| Vendor risk | Which vendors have access to client data? Any SSO/API connections? | Vendor list with access level, third-party risk assessments |
| Incident Response | Is there a documented response plan? Has it been tested? | IR plan document, tabletop exercise report |
| Security Policies | Are security policies updated and enforced (MFA, password, etc.)? | Policy documents, enforcement logs |
| Monitoring & Logging | Are systems and accounts monitored for anomalies? | SIEM alerts history, login anomaly logs |
| Security awareness | Is there regular training for staff on phishing and compliance? | Training program schedule, phishing simulation results |
| Testing & Audits | Is there a schedule for pen-testing, vulnerability scans, compliance audits? | Pentest reports, vulnerability scan summaries, audit reports |
| Remediation tracking | Are identified issues tracked to closure with retesting? | Remediation ticket lists, retest validation reports |
Table: Law firm security assessment checklist. Each row highlights a domain and the kind of evidence or deliverable that should be collected or reviewed. For example, verifying that all privileged accounts have MFA might involve an audit report from the identity provider. Ensuring backups are effective means actually performing and documenting restore tests. The key is not just having these items, but collecting objective proof (logs, reports, test results) that controls are working.
This checklist should be customized for the firm’s size, practice areas, and risk tolerance. Solo/small firms may combine roles (e.g. IT person running multiple tasks), while larger firms should have designated CISOs or security teams tackling each domain. It’s often helpful to engage a third-party assessor to run through this checklist methodically, producing a clear summary of gaps and evidence.
Given the high stakes, law firms should have a phased approach to strengthening security controls and proving them. The roadmap below suggests priorities in the first 30 days, 90 days, and the first year:
Identify where critical client data resides (DMS, cloud drives, eDiscovery platforms, local servers, backups).
Audit MFA coverage: enforce MFA for all attorneys, partners, administrative staff, and system admins across email, VPN, cloud admin portals, etc.
Review email security: check for unauthorized forwarding rules or stale OAuth apps on all accounts.
Inspect major cloud services (Microsoft 365 / Google Workspace): list all external sharing links and guest accounts, remove unnecessary ones.
Inventory all key systems (DMS like iManage/NetDocuments, case-mgmt, eDiscovery, billing, client portals, CRM). Determine owners and last audit dates.
Evaluate remote access paths (VPN/RDP/VDI): ensure strong authentication and device checks.
Confirm backup ownership and testing: know who manages backups and when they were last restored in a test.
Identify high-risk third-party vendors (cloud providers, IT support, eDiscovery, etc.) and request security attestations or surveys.
Assign an owner for incident response and ensure the firm has a clear breach reporting process (who calls whom, client notification templates, etc.).
Conduct an email security and identity review: test for compromised credentials (via dark web scans or password auditing), and ensure MFA and secure configuration.
Perform web application penetration testing on any public-facing firm assets (law-firm websites, client portals, public APIs) to find auth and access bugs.
Carry out API and integration tests if the firm uses custom client portals or connects SaaS apps via APIs.
Run a cloud security review of Microsoft 365/Google Workspace (shared drives, Exchange, Teams), checking for misconfigurations (using automated tools or professional review); for AWS, Azure or GCP environments, commission a cloud penetration test.
Audit DMS and matter access: verify that only appropriate people have access to each matter’s files; remediate any broad permissions.
Test ransomware readiness: perform a backup restore drill on critical systems (ensuring data recovery works) and execute an incident response tabletop scenario focusing on ransomware.
Review vendor access: ensure each high-risk vendor account uses MFA and principle of least privilege, and that contracts require incident notification.
Build a remediation tracking system to assign fixes for any identified issues, and start tracking their closure.
For any critical gaps found (e.g. missing MFA, weak passwords, open sharing), remediate immediately.
Transition all high-risk users (partners, executive, IT admins) to phishing-resistant MFA (hardware keys or passkeys) and enforce it firm-wide.
Schedule annual penetration tests for any new or updated applications (client portals, custom tools).
Institute quarterly access reviews for the most sensitive areas (e.g. DMS matter lists, cloud admin accounts) to ensure old access is revoked.
Quarterly review of OAuth apps and external sharing in cloud services.
Test incident response end-to-end at least annually (reset from scratch after a year, or simulate a major breach).
Reassess vendors after any contract renewals or major incidents.
Maintain a security evidence binder for clients/insurers (MFA reports, pentest summaries, IR plans).
Begin reporting basic metrics to leadership (see next section).
| Priority | Control/Action | Risk reduced | Validation method |
|---|---|---|---|
| Critical | Enforce MFA on all partner/attorney/admin accounts | Compromised accounts | Identity review, conditional access policies |
| Critical | Inventory and classify client data | Unknown sensitive data | Data mapping, sensitivity labeling |
| High | DMS access review and cleanup | Overexposed client files | DMS permissions audit |
| High | Email/M365 security review (rules, OAuth) | Mailbox compromise | Security audit, OAuth app review |
| High | Test backups & restore capability | Data loss from ransomware | Documented restore test results |
| High | Test client portal and web apps (pentest) | Data leakage via portals | Web/API pentest report |
| High | Vendor access review | Third-party data exposure | Vendor access audit |
| Medium | Ransomware tabletop exercise | Inefficient breach response | Tabletop exercise report |
| Medium | Remediation retesting (critical fixes) | Old vulnerabilities persisting | Follow-up pen-test or scan |
Table: Example milestones for a law firm’s security roadmap. “Validation method” shows how to prove a control works (e.g. restoring backups, completing a pentest, etc.). Priorities are firm-specific, but as an example, enforcing MFA and mapping client data are critical first steps, while scheduled testing and quarterly reviews are medium-term steps.
This roadmap illustrates that law firm security must be continuously validated. Importantly, the last column stresses retesting: it’s not enough to fix an issue; verifying the fix (retesting) is essential to ensure the problem is truly resolved.
Penetration testing (pen-test) is a key tool in the firm’s security validation arsenal. It does not replace policies, training, or incident planning, but it verifies how well technical controls actually work. For law firms, recommended testing focuses on the exposures typical in legal workflows:
Web application pentest – Tests external sites like client portals, firm websites, or case-management login pages for flaws (injection, auth bypass, insecure direct object references).
API pentest – For any APIs used by client apps or SaaS integrations, ensuring no broken object-level security (BOLA) or weak auth that could leak matter data.
Cloud security review – Assess Microsoft 365/Azure or Google Workspace settings: ineffective MFA policies, excessive app permissions, public storage.
Microsoft 365 / Google Workspace security review – Specific audit of Exchange, OneDrive/Drive, Teams/Groups, SharePoint. Checks for insecure sharing and compliance misconfigurations.
Email security review – Checks on MFA enforcement, external forwarding rules, compromised email rules, and mailbox audit logs for anomalies.
DMS access review – Audit the iManage/NetDocuments environment: find any admin-level permissions mistakes or missing segmentation between matters.
Remote access testing – Attacks against VPN, RDP, Citrix (through internet or compromised accounts) to verify strong authentication and intrusion detection.
External network vulnerability assessment – Scanning external IPs and domains to find unpatched servers or open services that could be attacked (e.g. public RDP, SQL).
Ransomware tabletop – Simulated ransomware outbreak to test decision-making, communications, and backup restore process.
Backup restore test – Attempt to restore critical systems and data from backups (often done by IT but formalizing the test provides evidence).
Continuous penetration testing – Human-led testing triggered as applications and APIs change, so new exposures are found between annual tests.
The table below shows how different tests validate controls:
| Testing type | Best for | What it validates |
|---|---|---|
| Web app penetration test | Client/case portals, firm web apps | Authentication, session management, access control, data leakage |
| API penetration test | Document exchange APIs, integrations | BOLA, endpoint auth, excessive data exposure |
| Cloud security review | M365/Azure, Google Cloud, AWS | Sharing settings, IAM roles, logging, conditional access |
| Email security review | Mail servers, mail rules, identity | MFA, OAuth apps, mailbox rules, unusual login detection |
| DMS access review | iManage, NetDocuments, SharePoint | Matter permissions, admin access, audit trails |
| Remote access testing | VPN, RDP, Citrix, SSH | Multi-factor enforcement, exposed RDP ports |
| Ransomware tabletop | Incident response capability | Decision processes, communication paths, backup acceptance |
| Backup restore test | Data recovery | Technical ability to recover data completely |
| Remediation retesting | Previously identified vulnerabilities | Confirms the specific fixes work |
Table: Example penetration and security tests for law firms and their purposes. For example, a web application pentest of a client portal can uncover an authentication bypass, proving or disproving the efficacy of access controls. A continuous pen-test or vulnerability scan helps detect new flaws (or ones thought fixed that reopen) after system changes.
Retesting is critical. A common scenario: an audit finds a misconfiguration (say, an open S3 bucket or missing MFA). If the IT team fixes it, a subsequent penetration test or automated scan must verify the fix. Only then can the firm be confident the risk is mitigated. Continual testing, from phishing simulations to network scans, is what turns static “compliance” into dynamic security.
To quantify security posture, law firms should track key metrics that reflect client-data risk. Examples include:
| Metric | What it measures | Why it matters |
|---|---|---|
| MFA coverage (attorneys/admins) | Percentage of staff with MFA enabled | Strong MFA reduces account takeover risk |
| Access review exceptions | # of users with high-sensitivity access | Limits unnecessary client file exposure |
| DMS permission review completion | % of matters audited for correct access | Ensures confidentiality in document handling |
| Mailbox rule anomalies | Number of suspect inbox rules | Early warning of account compromise |
| External sharing findings | # of shared links or guest users | Reduces inadvertent data leaks via cloud share |
| Suspicious OAuth apps | # of third-party apps with org access | Identifies persistent access risks |
| Backup restore success rate | % of systems successfully restored | Direct measure of ransomware recovery readiness |
| Response plan age/frequency | Last date IR plan tested in X months | Older plans risk outdated assumptions |
| Critical finding age | Avg days high-risk issue open | Highlights exposure window |
| Remediation verification rate | % of fixes confirmed by retest | Prevents undetected residual risks |
| Vendor security assessment completion | % of vendors with recent security review | Reduces third-party breach risk |
| Incident response exercise completion | # of tabletop/full tests per year | Improves readiness and identifies gaps |
Table: Sample risk metrics to track at executive level. These metrics connect directly to breach vectors: for example, if MFA coverage is 80%, then 20% of accounts are easy targets. If backup restores fail 10% of the time, ransomware downtime risk is significant. Tracking how long high-severity vulnerabilities remain unpatched (finding age) gives leadership visibility into exposure windows. Such metrics translate technical assessments into business risk indicators.
Executive dashboards might include some of these numbers (e.g. “95% of key mailboxes have MFA”, “200 client matters reviewed this quarter for excessive access”, “annual backup restore success: 100%”). The goal is to move beyond compliance checkboxes to quantifiable assurance. These metrics also help answer client or regulator questions (e.g. “What percentage of partners use phishing-resistant MFA?”). Over time, seeing trends (e.g. shrinking time to close critical issues) demonstrates a maturing security program.
Law firm breach risk is client trust risk, not only IT risk. Exposed client files and privileged communications can damage careers, client relationships, and even eliminate privilege protections. Security work should focus on protecting client data, not just servers.
Client data concentration makes law firms targets. Firms often aggregate decades of client secrets – M&A plans, legal strategies, health records – across matters. Attacks like the 2023 Orrick breach (data of 637,620 people stolen) show attackers want this “megabase” of intelligence.
Ransomware hits law firms doubly hard. Besides typical downtime and lost productivity, law firms risk having confidential client documents stolen. Attackers increasingly promise to leak client data unless paid. Even with backups, firms need tested IR plans to recover quickly without conceding privilege.
Email compromise remains a top threat. Attorneys’ inboxes carry sensitive case discussions and billing details. A single phishing email or BEC scam can hijack millions in trust funds or slip fake legal advice. Given the FBI’s count of more than 191,000 phishing and spoofing complaints in 2025, firms must assume they’re targeted continually.
Cloud, DMS and SaaS improve efficiency but increase sharing risk. Files in Microsoft 365, iManage, or Clio simplify collaboration, but missteps (like over-shared OneDrive links or broad NetDocuments permissions) can open data floodgates. Periodic permissions audits and hardening (e.g. enforcing organization-only sharing) are essential.
Compliance gaps are often evidence gaps. Most firms have policies on paper, but regulators and clients increasingly want proof (logs, test results, reports). Being SOC 2 certified or having cyber insurance matters less if you can’t show MFA was on or an IR drill was done. Firms should treat compliance as proof of control.
Retesting is what turns remediation into real risk reduction. Fixing a vulnerability isn’t done when you click “patch applied.” A retest or monitoring check is needed to verify the flaw is closed. This practice prevents “ghost” vulnerabilities from lingering and assures stakeholders the fix truly worked.
Third parties are an extension of your own network. Vendors (e.g. eDiscovery providers, IT support, cloud services) often have access to your data. Treat them like any other system: review their controls, use vendor SOC reports, and limit their access rights.
Metrics drive accountability. Track metrics that reflect real security – e.g. MFA usage rates, pending critical issues, incident drill outcomes. Sharing these with leadership makes cybersecurity a boardroom topic and shows where to invest (personnel, tools, or testing).
Preparedness breeds resilience. Knowing what to do when a breach happens is as important as prevention. Regular incident response exercises, backed by tested backups and communication plans, let a firm respond calmly rather than scramble.
Key stats include: 29% of lawyers say their firm has experienced at least one breach (ABA 2023); 39% of legal tech decision-makers reported a breach in the past year, and among those breached, 56% lost client data (Arctic Wolf/Above the Law). BakerHostetler says law-firm incidents nearly doubled in 2025, and professional services was the most targeted ransomware sector in Q4 2025 at 18.9% (Coveware). Phishing remains rampant (FBI IC3: 191,561 phishing/spoofing complaints in 2025), and business email compromise cost $3.05B in 2025. These emphasize that law firms face both common cyber threats and sector-specific risks.
Law firms hold highly sensitive, confidential information – client contracts, M&A deals, litigation strategy, health or financial records – making them attractive targets. Attackers seek this data to extort firms or leverage it against clients. Unlike many businesses, law firms must protect privileged communications by law, so a breach can also lead to ethical and legal consequences. Specialized threat actors (sometimes nation-states) have actively targeted the legal sector recently (e.g. the 2025 Williams & Connolly email breach). In short, clients’ valuable data and legal privilege make firms lucrative and high-impact targets.
Everything from communication and case files to regulatory data. High-risk categories include privileged attorney-client communications and strategy (breach destroys privilege), corporate secrets like M&A or patent information (trading or competitive risk), personal data like social security numbers or health records (identity theft/HIPAA issues), and financial documents (fraud risk). EDiscovery datasets (thousands of pages) are also at risk of mass exposure. Firms must treat any client matter as potentially sensitive and enforce strict access controls (e.g. matter-based DMS permissions, encryption).
Ransomware can be devastating. It typically encrypts key systems (taking email, DMS, and case software offline) while often simultaneously stealing data. Law firms lose billable hours as staff can’t work, risk missing court deadlines, and face the moral dilemma of paying to retrieve encrypted client files. Even if backups allow restoration, any stolen client data triggers notification duties. Ransom notes may threaten to leak client documents, amplifying damage. In practice, firms suffer both operational shutdown and a breach of client confidentiality, which is the double-extortion pattern seen across sectors, made more damaging for law firms because the stolen data is often privileged client material.
Surveys and incidents show common gaps include: lack of (or non-enforced) multi-factor authentication on email and cloud accounts; overly broad access permissions in DMS or file shares; insufficient monitoring of privileged/admin accounts; unsecured remote access (e.g. VPN without MFA); poor email filtering and untested incident response plans. Many small firms also under-invest in security staff and awareness training. Essentially, firms often have critical controls on paper, but they’re not fully applied or tested in practice.
Email compromise (via phishing or stolen credentials) can be a gateway to entire firm compromise. A hacked attorney mailbox not only exposes confidential conversations and attachments, it can be used to phish colleagues or clients from within. Business Email Compromise (BEC) specifically can alter payment instructions on settlements or invoices; FBI IC3 reports billions lost to BEC each year. In a law firm, such fraud often involves client escrow or trust funds. Even if only one lawyer’s account is breached, it can erode client trust and potentially expose privileged information.
There’s no single federal law mandating specific security measures for all law firms. However, lawyers have a professional duty to protect client data (ABA Model Rule 1.6) and must be “reasonably” competent with technology (ABA Rule 1.1). Firms handling regulated data must follow those regulations (e.g. HIPAA, GLBA, state privacy laws). Additionally, many clients (corporate, government) now require evidence of security (security questionnaires, SOC 2 reports, cyber insurance) as a condition of engagement. So while not spelled out in one law, law firms effectively face growing obligations from professional ethics, client contracts, and industry regulations.
A thorough assessment covers people, process, and technology. It should include: inventory of client data and where it’s stored; review of access controls (who can access what matters?); audit of email and identity (MFA enforcement, phishing tests, inbox rules/OAuth apps); examination of cloud/SaaS settings (sharing permissions, admin roles); DMS permission audit; remote work protections (VPN policies, device encryption); backup and recovery capability tests; vendor and third-party access audit; and incident response readiness (a tested plan and tabletop exercises). The checklist table above outlines these areas and the specific evidence to collect (pentest reports, restore logs, IR plan, etc.).
Yes. Penetration testing identifies vulnerabilities in real-world settings (e.g. public web apps, cloud configurations, network). For law firms, targeted pentests (web portals, DMS access, cloud tenants, email systems, VPN) can reveal if attackers could break in. Importantly, pen testing verifies that existing controls actually work – it’s one thing to say “we have MFA,” but testing shows if there are any bypasses or misconfigurations. After fixes are applied, a retest ensures those risks are closed. In short, pentesting turns theoretical security measures into proven defenses, closing gaps before attackers find them.
At least annually for major tests, with some checks more frequent. For example, penetration tests of public-facing systems and cloud configuration audits should be done yearly (or after any major update). Vulnerability scans and patch checks should be monthly/quarterly. Email phishing simulations and any security awareness training could be quarterly. Critically, backup restore exercises and incident response tabletop simulations should happen at least once a year. High-risk controls (like MFA for new employees or after major changes) need ongoing verification (e.g. automated reports). In summary, law firms should embed testing into their routine schedule so that risk reduction is continuous, not one-off.
Common requests include: confirmation of MFA on all accounts (especially email and privileged accounts); proof of security monitoring (EDR or SIEM logs); summaries of vulnerability assessments or penetration test results; backup and disaster recovery plans and test results; cyber insurance details; incident response plans; and data classification/inventory documentation. Insurers often require a minimum “hygiene” (patching, training, MFA). Enterprise clients may send security questionnaires or demand SOC 2/ISO 27001 certificates. Essentially, they look for artifacts that controls were implemented (not just claimed). Having pentest reports, recent tabletop exercise summaries, and configuration review findings can significantly streamline these due diligence processes.
In 2026, law firms that publicly confirmed breaches include Jones Day (March to April); Quinn Emanuel, McDermott Will & Schulte, Goodwin Procter and Herbert Smith Freehills Kramer (August); Holland & Knight, Katten, Greenberg Traurig, Eckert Seamans and Seyfarth Shaw (September); and Squire Patton Boggs (October). Law.com counted at least 10 Big Law firms reporting breaches between Memorial Day and Labor Day 2026. Most firms said only a limited number of files were taken.
Phishing and social engineering. BakerHostetler found phishing caused 30% of the 1,250+ incidents it handled in 2025, and most 2026 law firm breaches started with a phishing message or a caller posing as IT support. Data-theft extortion follows: the FBI warns that Silent Ransom Group has targeted US law firms since 2023.
Costs vary widely, and no public source gives a law-firm average. Known data points include Orrick's $8 million class settlement after a 2023 breach affecting 637,620 people, a $1 million median initial ransom demand for legal and government victims in 2023 (Arctic Wolf), and Coveware's $1.88 million average ransom payment in Q2 2026, which it tied to attacks on law firms. Notification, forensics, lawsuits and lost clients add to the total.
In 2026, law firm breach risk centers on securing the entire client-data chain: from email and identity to cloud storage, document management and case systems, through client portals and third-party integrations. The statistics show that threats like ransomware, phishing, and credential theft are not theoretical – they are actively targeting law practices and putting privileged, confidential information at risk. But the solution isn’t generic IT advice; it’s validation that each point of exposure is tested and remediated. Firms must verify that MFA truly protects partners’ inboxes, that offboarding properly removes access to cloud drives, that backups restore whole data sets, and that incident response plans have been practiced. In other words, success lies in proving controls work through security testing (web/API pentests, cloud reviews, email audits) and iterative improvement.
DeepStrike helps law firms do exactly that. It supports that work with human-led penetration testing of client portals, web applications, APIs, cloud environments and external infrastructure, red team engagements, continuous testing that re-tests applications and APIs as releases ship, and retesting of fixed findings, giving firms the independent evidence they need. This isn’t just about meeting a checklist – it’s about safeguarding clients’ matters and fulfilling the trust and confidentiality that underpin legal practice. By rigorously testing and fixing these areas, firms can confidently demonstrate to clients, regulators, and insurers that their data protections are real and effective.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
This article prioritizes law-firm-specific surveys, legal-sector research, official government reports, professional responsibility guidance, ransomware benchmarks, breach-cost reports, threat intelligence, and public incident reporting. Each statistic is labeled by data type to distinguish law-firm-specific data from broader ransomware, breach, professional-services, email, or cloud benchmarks. Where a source is not law-firm-specific, it is used as context rather than as a direct proxy for legal-sector breach risk.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
