September 16, 2025
Updated: November 11, 2026
Compare Brazil’s top penetration testing providers for 2026 DeepStrike, Blaze, eSecurity, DM11, and Resh. Learn about services, cost factors, LGPD compliance, and how to choose the right partner.

Mohammed Khalil
In 2026, Brazilian organizations are moving from occasional audits to continuous, compliance aligned penetration testing and red team validation as a core element of enterprise risk management under LGPD pressure, insurance requirements, and AI accelerated threat activity.
Comparing providers beyond Brazil? Our global list of top penetration testing companies covers firms that deliver testing across regions.
For pricing factors, see our Portuguese-language guide to penetration testing cost (custo do teste de intrusão).
Related Latin American guides: Colombia, Chile, Mexico and Costa Rica.
For a broader comparison of cybersecurity providers beyond penetration testing, see Top Cybersecurity Companies in Brazil.
The average global data breach cost reached a record $4.99M USD in IBM's Cost of a Data Breach 2026, and the same study put the average Brazilian breach at a record R$7.44 million, up 3.5% from R$7.19 million in 2025 (see our data breach statistics for global context). Those averages capture forensic investigations, legal expenses, regulatory notification, operational downtime, customer churn, and long‑term brand erosion. For publicly traded companies and players in Brazil's fast-growing financial sector, breach disclosures also influence stock volatility and investor confidence, adding an additional financial dimension beyond direct remediation costs.
Boardrooms, audit committees, and executive risk councils across Brazil now treat penetration testing as a governance matter rather than a discretionary IT activity. AI‑assisted attack tooling, credential marketplaces, automated exploit kits, and commoditized ransomware frameworks have lowered attacker barriers while simultaneously increasing the speed, automation, and scale of potential compromise. Simultaneously, regulatory enforcement under the Lei Geral de Proteção de Dados LGPD has tightened, cross‑border data transfer scrutiny has increased, and some cyber‑insurance underwriters ask for recent penetration test reports or remediation evidence. The LGPD requires appropriate security measures (Art. 46) but does not prescribe penetration testing. The conversation has shifted from “Should we test?” to “How frequently and how deeply should we validate our defenses?”
DeepStrike publishes this guide and includes itself in the list; competitor profiles are based on their official websites, not sponsorships, affiliate arrangements, or paid placements. The objective is to support procurement teams, CISOs, compliance leaders, CTOs, and digital transformation executives in making informed vendor shortlisting decisions grounded in technical capability, regulatory alignment, delivery maturity, reporting clarity, and real‑world engagement depth rather than marketing narratives or surface‑level tool comparisons. The emphasis throughout this guide is on procurement clarity, measurable outcomes, audit defensibility, and sustainable long‑term security posture improvement rather than one‑off compliance checkbox fulfillment.
For Brazilian buyers, the main 2026 changes are AI-assisted discovery with manual validation still decisive, more advanced red teaming across multi-cloud and supply-chain paths, growth of PTaaS and continuous testing, more cloud and API scope, and stricter documentation expectations driven by LGPD enforcement and Banco Central rules. In more detail:
For financial institutions, the clearest testing rule is CMN Resolution 4,893 of 26 February 2021. Institutions authorised by the Banco Central do Brasil must keep a cybersecurity policy whose controls include, at minimum, periodic tests and scans to detect vulnerabilities, and the resolution also sets requirements for contracting data processing, storage, and cloud services in Brazil or abroad. BACEN-regulated buyers therefore usually want test evidence that maps to their policy, and need to know where a provider stores findings.
Outside finance, the LGPD (Law 13,709/2018) requires appropriate security measures (Art. 46) without prescribing penetration testing, and the ANPD's Resolution CD/ANPD 19/2024 governs international data transfers, which matters when testers outside Brazil can see personal data. Public bodies contract under the Public Procurement Law (Law 14,133/2021), so confirm that a shortlisted provider can take part in Brazilian public tenders. CERT.br, run by NIC.br, handles incident response for networks connected to the Internet in Brazil. Facts in this section were checked on 3 November 2026.
Companies were evaluated holistically across multiple dimensions rather than a single numeric score, reflecting real‑world buyer decision processes where risk tolerance, compliance exposure, digital maturity, and internal security capabilities vary significantly between organizations. The numbers in the provider headings are for navigation only and are not a ranking; DeepStrike publishes this guide and lists itself first. Assessment criteria included:
No company was included or excluded based on sponsorship, advertising or affiliate relationships. DeepStrike publishes this list and lists itself first; list order is not a quality ranking.
How we built this Brazil list: we started from penetration-testing providers with a Brazilian office or Brazilian roots that publish their services in Portuguese or English (São Paulo boutiques, a Recife-founded firm with European offices, and compliance-led consultancies), plus DeepStrike as publisher. We kept firms whose own sites describe penetration testing in detail and recorded addresses, methodology, credentials, retest terms, and limits from those sites, last checked in November 2026. This is desk research; we did not commission tests or score the providers.
Public offering: DeepStrike's penetration testing services describe human-led testing across applications, cloud environments, and infrastructure, supported by a findings and collaboration platform. Its public process covers planning, reconnaissance, vulnerability discovery, controlled exploitation, reporting, and technical support. Published reports include reproduction steps, remediation guidance, and root-cause information; the proposal should define exact coverage and commercial terms.
Brazil relevance: Founded in 2016, DeepStrike LLC is headquartered in Newark, Delaware, has 11–50 employees, and also publishes a business address in Dubai, UAE (IFZA Business Park). It delivers testing remotely for Brazilian clients; define tester locations, permitted subcontracting, and data-handling restrictions in the engagement agreement.
Team certifications: OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate, as shown on DeepStrike's services page.
Official sources: Pricing , Contact Us
Buyer fit: Engineering teams that need application, cloud, or infrastructure testing with direct remediation collaboration.
| Documented strengths | Limits and buying considerations |
|---|---|
| Human-led testing with reproduction evidence, root-cause information, and remediation guidance. | The service description is not an independently measured quality comparison. Assess the assigned team and a relevant sample report. |
| The published Basic plan lists Slack collaboration, customizable reports, and 12 months of remediation retesting. | No numeric price is displayed on the pricing page. Basic is a one-shot test; recurring coverage belongs to a different plan, with contract-specific terms. |
| Team certifications shown on the services page include OSCP, OSWE, OSEP, OSWP, GXPN, GWAPT, eCPPT, eMAPT, eWPT, CREST CPSA, CRTP, CRTE, and Microsoft Azure Security Engineer Associate. | These are individual tester credentials, not a company-level accreditation; ask which certified testers will be assigned to your engagement. |
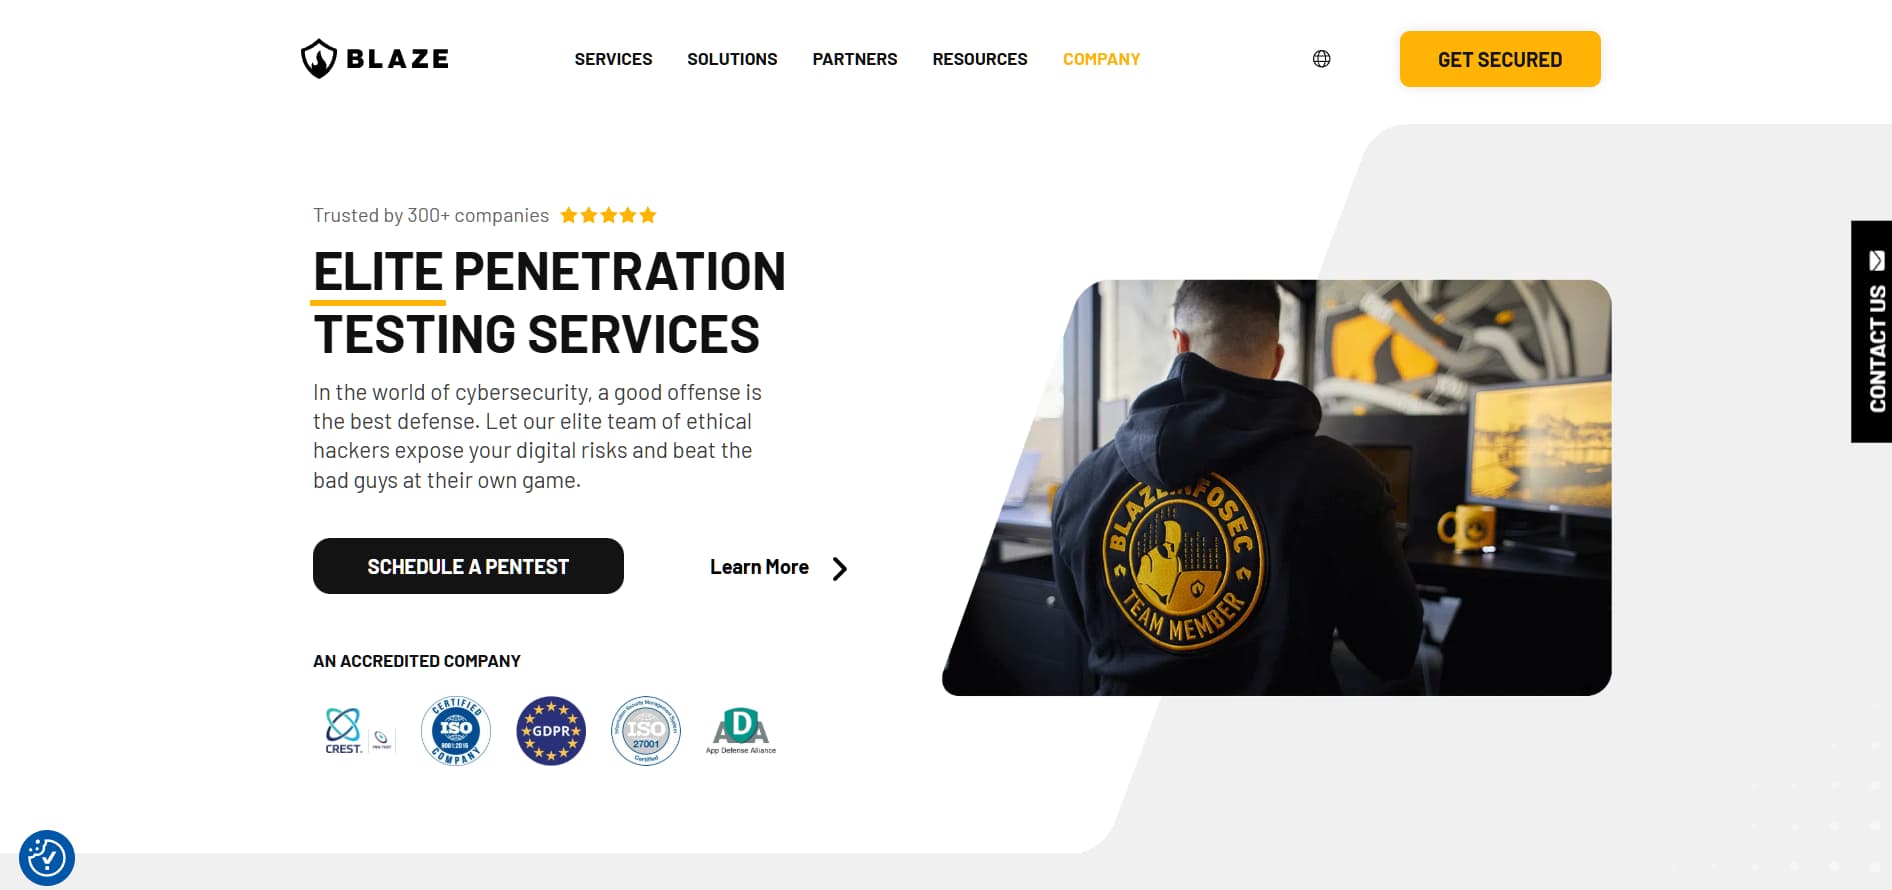
Public offering: Blaze Information Security offers penetration testing of web applications, REST, GraphQL, gRPC, and WebSocket APIs, iOS and Android apps, AWS, Azure, and GCP cloud environments, external, internal, and wireless networks, and AI/LLM applications. It also lists red and purple teaming, Microsoft 365 and Entra ID security assessments, product security assessments, and vCISO advisory. Findings are manually validated and shown live in the Blaze Portal, and retesting of agreed findings can be included in the engagement.
Brazil relevance: Blaze lists offices at Cais do Apolo 222, Recife, Pernambuco, as well as in Berlin and Porto. It is the option in this list rooted in Recife rather than São Paulo, with European offices and live findings in the Blaze Portal. Agree which office's team performs the work, the reporting language, and where findings data is stored in the agreement.
Official sources: https://www.blazeinfosec.com/services/penetration-testing; https://www.blazeinfosec.com/contact-us
Buyer fit: Brazilian and cross-border SaaS, fintech, and technology companies that want application and cloud testing with portal-based delivery.
| Documented strengths | Limits and buying considerations |
|---|---|
| Broad published scope including APIs, cloud, AI/LLM applications, and Microsoft 365, with live findings in a portal. | Retesting is included only when agreed; confirm it is in the quoted scope. |
| Findings can be mapped to SOC 2, ISO 27001, PCI DSS, HIPAA, and other frameworks. | Its homepage displays a CREST Security Testing badge; confirm current status on CREST's public register. |
Public offering: eSecurity offers penetration tests of web applications, REST, SOAP, and GraphQL APIs, Android and iOS apps, and IT infrastructure, in white-, grey-, or black-box form, alongside a cyber defense service backed by a 24/7 SOC. It cites OWASP, PTES, NIST SP 800-115, and MITRE ATT&CK, and its published seven-phase process includes a second round of testing to validate fixes and a final report that can be shared with third parties.
Brazil relevance: eSecurity lists its office at Avenida Paulista 1439, São Paulo, and states that it has operated since 2012. It stands out for Portuguese-language delivery with a built-in second test round and a 24/7 SOC for organisations that want monitoring after the test. Confirm the assigned testers, reporting language, and data handling in the agreement.
Certifications: eSecurity's pentest page says its specialists hold OSCP, eWPT, and CEH certifications.
Official sources: https://esecurity.com.br/pentest; https://esecurity.com.br/contato
Buyer fit: Brazilian SMBs and mid-sized organisations that want Portuguese-language pentesting with a retest round and optional SOC monitoring.
| Documented strengths | Limits and buying considerations |
|---|---|
| Published process includes a second test round to validate fixes and a shareable final report. | Red team or cloud-specific testing is not described on the pentest page; confirm coverage for those needs. |
| Pentest and 24/7 SOC services are available from one provider. | If the same provider also monitors your environment, agree how testing independence is kept. |
Public offering: DM11 offers penetration testing, vulnerability analysis, AI pentest and red team, SAST/DAST, phishing simulation, cloud security, and digital forensics, alongside governance, risk, and compliance programmes for PCI DSS, ISO 27001, SOC 2, BACEN resolutions, LGPD, and TISAX. Its Ethical Hacker as a Service (EHaaS) provides a testing team available throughout the year without a new contract for each test, and its oitenta20 IT risk assessment produces prioritised investment guidance.
Brazil relevance: DM11 lists its office at Av. Eng. Luís Carlos Berrini 1140, Brooklin, São Paulo, and cites 17 years of operation. Its distinguishing point is testing tied to BACEN, PCI DSS, and LGPD compliance programmes, plus a year-round Ethical Hacker as a Service model. Confirm the testers assigned, report language, and data handling in the agreement.
Certifications: DM11's homepage lists team credentials including CISA, CEH, ISO 27001 Lead Auditor, EXIN DPO, CGEIT, COBIT 5, and PMP.
Official sources: https://www.dm11.com.br/pt/servicos; https://www.dm11.com.br/pt/contato
Buyer fit: Payment, financial, and regulated organisations that want pentesting tied to PCI DSS, ISO 27001, SOC 2, or BACEN compliance work.
| Documented strengths | Limits and buying considerations |
|---|---|
| Pentesting sits alongside PCI DSS, ISO 27001, SOC 2, and BACEN compliance programmes. | If DM11 both implements controls and tests them, agree how independence is maintained. |
| Year-round testing through the EHaaS subscription model. | Subscription scope and retest terms are contract-specific; confirm them in the proposal. |
Public offering: Resh offers web, network, API, mobile, AI, IoT, wireless, physical, and blockchain penetration tests, phishing and stress tests, Red Team as a Service, continuous red teaming, vulnerability monitoring, and AWS cloud diagnostics. Its web testing covers the OWASP Top 10 and business-logic testing, and it offers annual contracts with recurring retests. Clients follow tests and reports through Resh's own platform, which uses EPSS exploit-probability data to prioritise findings.
Brazil relevance: Resh lists its office at Rua Pais Leme 215, São Paulo, with a further office in Leiria, Portugal. It is distinguished by a very broad published catalogue, including physical and blockchain tests, and EPSS-based prioritisation in its own platform. Confirm which office's testers perform the work and how data is handled in the agreement.
Official sources: https://resh.com.br/pentest-web/; https://resh.com.br/contatos/
Buyer fit: Brazilian SMBs and growing companies that want a broad pentest catalogue with platform-based reporting.
| Documented strengths | Limits and buying considerations |
|---|---|
| Very broad catalogue, from web and API to IoT, physical, and blockchain testing. | Breadth across many test types does not show depth in each; request a sample report for your asset class. |
| Annual contracts with recurring retests and an online reporting platform. | Tester certifications are not listed on the service pages reviewed; ask which credentials the assigned testers hold. |
| Company | Specialization | Best For | Region | Compliance focus | Ideal Size |
|---|---|---|---|---|---|
| DeepStrike | Human-led application, cloud, and infrastructure testing | Engineering teams needing remediation collaboration | Remote (HQ Newark, Delaware) | Reports prepared for PCI DSS, SOC 2, ISO 27001 and similar audits; confirm LGPD evidence needs in the proposal | SMB → Enterprise |
| Blaze InfoSec | Web, API, cloud, red team, PTaaS portal | SaaS, fintech and tech companies | Brazil (Recife) + Germany, Portugal | CREST badge shown; SOC 2, ISO 27001, PCI DSS mapping | Mid → Enterprise |
| eSecurity | Web, API, mobile, infrastructure pentests + 24/7 SOC | SMBs & Startups | Brazil | Not stated; confirm | SMB |
| DM11 | Compliance, PCI DSS, subscription pentest | Enterprises | Brazil | PCI DSS, ISO 27001, SOC 2, BACEN | Enterprise |
| Resh Cyber Defense | Broad pentest catalog, Red Team as a Service | SMBs | Brazil + Portugal | Not stated; confirm | SMB |
Pricing structures have shifted toward hybrid subscription and continuous validation models rather than purely one‑off engagements. Pricing depends on scope and is quoted per engagement; request itemised quotes based on the same scope document. Costs vary based on scope, complexity, application architecture, reporting depth expectations, executive presentation requirements, and regulatory documentation needs. See our guide to penetration testing cost. Typical effort drivers by engagement type:
SMB Tier: effort depends on application size, infrastructure complexity, and reporting scope.
Mid‑Market: effort grows with multi‑application testing, cloud scope, structured remediation workshops, and retest validation.
Enterprise: effort grows with multi‑vector testing, red team elements, executive presentations, compliance mapping documentation, and engineering collaboration cycles.
Red Team / Adversary Simulation: cost depends on engagement duration, stealth requirements, organizational size, and detection‑response benchmarking objectives.
Additional considerations:
Organizations comparing cloud penetration testing, red team, PCI DSS pentest, or PTaaS services in Brazil should align vendor strengths with risk exposure, digital architecture complexity, and compliance obligations rather than headline pricing alone. DeepStrike's own service pages cover web application penetration testing, mobile application penetration testing, cloud penetration testing, and continuous penetration testing. For compliance and threat context, see our guides to PCI DSS penetration testing, data privacy fines under GDPR, CCPA, and CPRA, and cybersecurity statistics.
AI accelerates reconnaissance, anomaly detection, and pattern recognition, but human expertise remains essential for exploit validation, contextual risk analysis, and business‑impact interpretation. AI acts as an accelerator, not a replacement for skilled ethical hackers.
For many SaaS, fintech, and digital‑first organizations, quarterly or continuous PTaaS models are supplementing not entirely replacing annual compliance audits. Continuous validation enhances rather than eliminates formal audit cycles.
Some do. Some cyber‑insurance underwriters ask for recent penetration test reports or remediation evidence before issuing or renewing policies; check your policy's questionnaire.
OSCP, CISSP, OSWE, and CREST remain widely recognized, particularly when combined with demonstrated real‑world engagement experience, exploit chaining capability, and documented remediation collaboration.
At minimum annually, but high‑growth SaaS, fintech, and cloud‑native organizations increasingly adopt quarterly or continuous validation cycles aligned with deployment frequency, compliance exposure, and business risk tolerance.
Ready to Strengthen Your Defenses? The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business. Explore our Penetration Testing Services to see how we can uncover vulnerabilities before attackers do. Drop us a line, we’re always ready to dive in.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, adversary emulation, and complex attack‑chain analysis. His work involves dissecting multi‑stage intrusion scenarios, advising executive leadership on cyber‑risk mitigation strategies, mentoring security teams, and developing resilient defense architectures for clients in the finance, healthcare, technology, and digital commerce sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
