Data privacy enforcement has matured. Supervisory authorities in the EU and California now pursue not only headline cases against tech giants, but also steady, sector wide actions that turn privacy from a legal checkbox into a material financial risk. If you manage compliance, security, product, or marketing, you need to know two things, what an “average” penalty looks like in practice, and what drives fines above or below that baseline.
This guide explains the average fines and typical ranges for the GDPR, CCPA, and CPRA, how regulators calculate penalties, and which behaviors escalate exposure. You will see dated figures from leading trackers and enforcement bodies, examples of real cases, and a practical plan to reduce risk before the next audit or complaint arrives, including where penetration testing for compliance can help validate technical safeguards. We also link to deeper reading and tools, so your team can move from policy on paper to measurable controls.
We use “average” two ways. For GDPR, there is a published cross country average of about €2.28 million per fine over 2018 to early 2026 (CMS Enforcement Tracker Report 2026, cut-off 1 March 2026). For CCPA and CPRA, statutes specify per violation amounts, so we discuss typical settlement sizes and how per person counting multiplies cost.
How GDPR Fines Work, Tiers, Caps, and Realistic Averages
The legal framework at a glance
- Two tiers of caps under Article 83.
Tier 1, up to €10 million or 2 percent of worldwide annual turnover, whichever is higher.
Tier 2, up to €20 million or 4 percent of worldwide annual turnover, whichever is higher. GDPR+1 - Authorities consider factors like nature, gravity, duration, intent, mitigation, prior infringements, and cooperation when setting amounts. GDPR
The real world average
Independent trackers aggregate public decisions. The CMS Enforcement Tracker Report 2026 (7th edition, cut-off 1 March 2026) records 2,685 fines totaling about €6.11 billion, an average fine of €2,277,122. This is not evenly distributed, since a handful of mega fines skew totals, yet the average still signals that seven figure penalties are common for sizeable organizations.
Trend insights you can brief to leadership
- Cumulative fines from 25 May 2018 to 10 January 2026 reach about €7.1 billion, per DLA Piper’s January 2026 GDPR fines survey, which puts fines imposed in 2025 at about €1.2 billion. Cumulative totals keep rising; annual totals swing with a few very large fines (see our GDPR fines statistics for the biggest fines and the Article 83 maximums).
- Sector exposure concentrates in media, telecom, and industry and commerce, with Ireland’s DPC often issuing the largest individual sanctions.
Examples to anchor expectations
- €1.2B against Meta in 2023 for international transfer violations.
- €746M against Amazon in 2021 for consent and data processing issues.
These outliers explain why median values would be lower than the average, yet they also show how quickly exposure scales for global companies.
CCPA and CPRA Penalties, How California Calculates Fines
Statutory amounts and inflation adjustments
California uses per violation amounts. Historically $2,500 per violation, or $7,500 for intentional violations or those involving minors. The California Privacy Protection Agency updates inflation adjusted figures. As of late 2024, the CPPA cites $2,663 and $7,988 respectively for administrative fines, with civil penalties carrying the same adjusted values. cppa.ca.gov
Key point: CPRA ended the old CCPA 30 day cure period in most cases, created a dedicated enforcement agency, and did not cap total exposure. The practical risk comes from how violations are counted, often per consumer, per incident, which can multiply totals rapidly. cppa.ca.gov
What “average” looks like in practice
California penalties tend to resolve in the six to low seven figure range for large retailers and ad tech cases, depending on consumer counts and injunctive terms. For example, Sephora settled for $1.2 million in 2022 for selling personal information without proper disclosure and opt outs, paired with strong injunctive relief. More recent CPPA actions have approved mid six figure to low seven figure penalties. These illustrate realistic order of magnitude for brand name companies.
What raises or lowers the final number
California statutes and guidance highlight intent, cooperation, remediation speed, and minors’ data as multipliers. Enforcement bodies can consider good faith and scale penalties for smaller entities. This makes documentation of compliance efforts valuable not just for audits, but as leverage in any resolution.
Headline Numbers vs. Everyday Risk, A Comparison Table
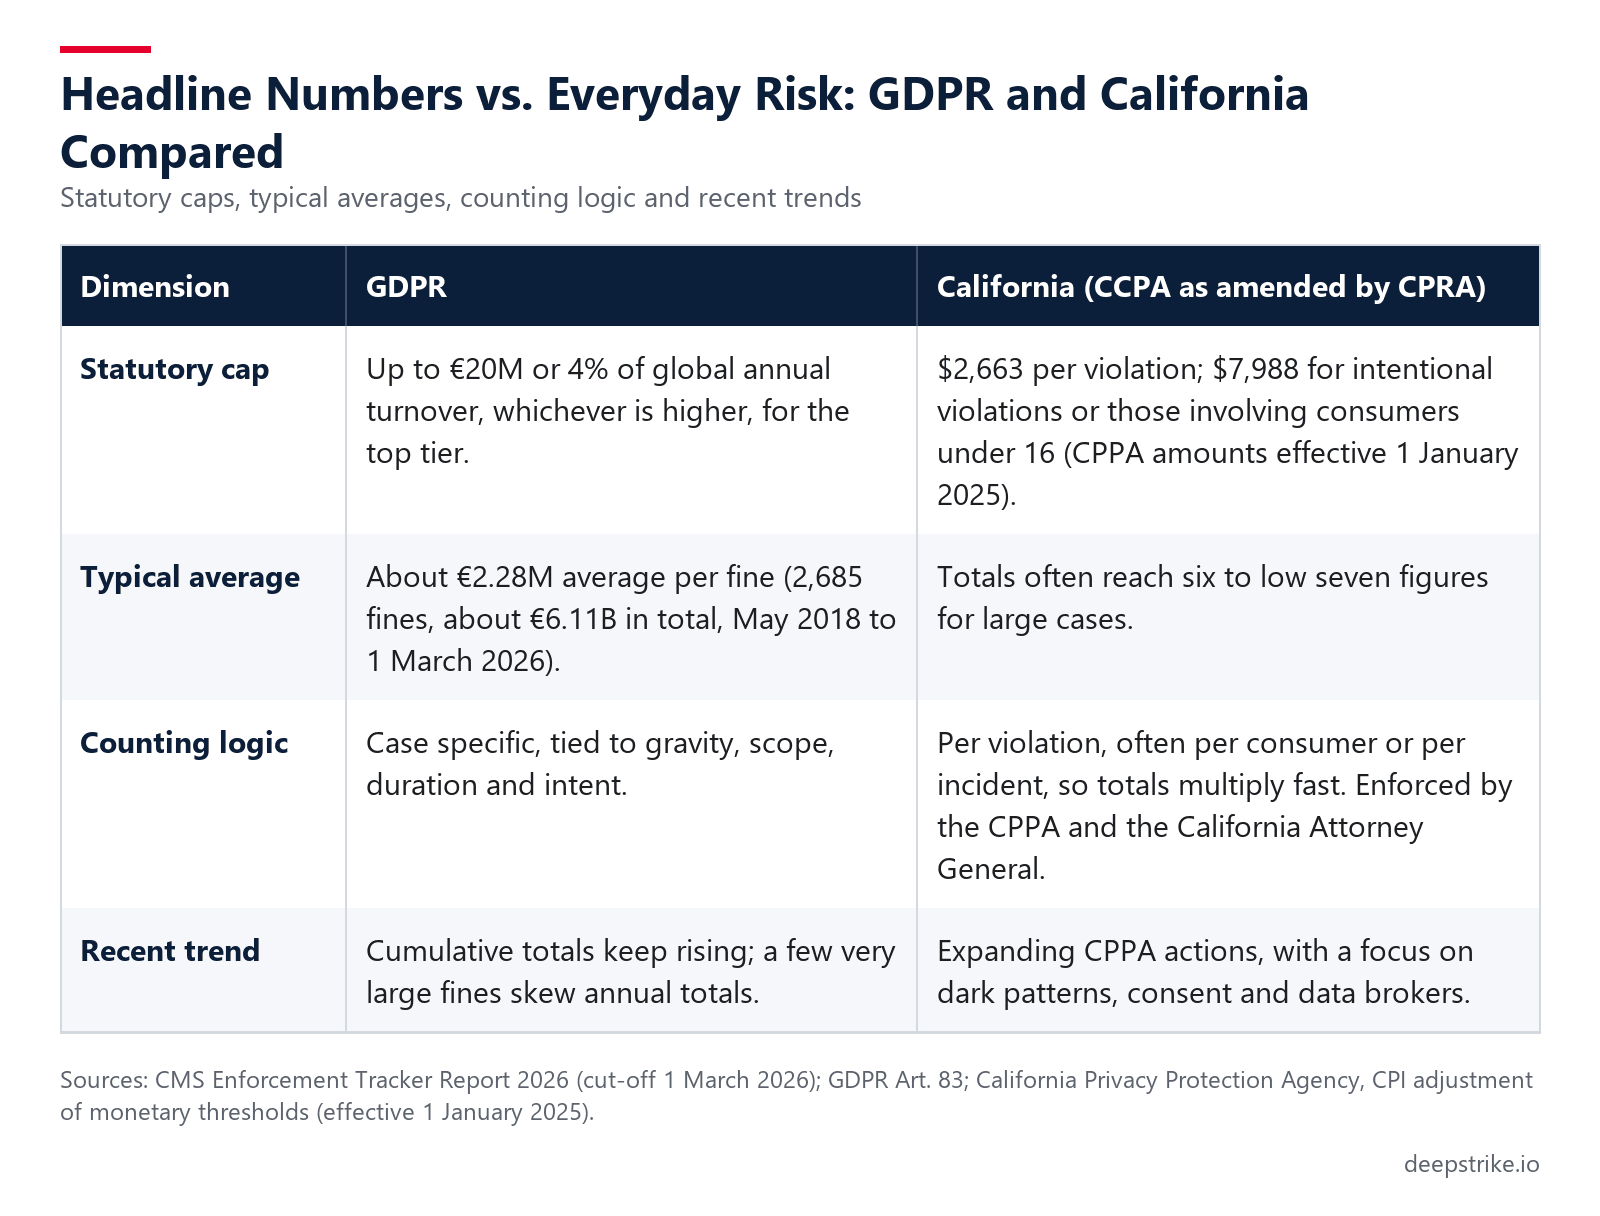
Headline Numbers vs. Everyday Risk: GDPR and California Compared
Sources for figures and trends: CMS Enforcement Tracker Report 2026 (cut-off 1 March 2026), DLA Piper’s January 2026 survey (data to 10 January 2026), CPPA announcements and inflation tables.
How Regulators Calculate Fines, The Factors That Matter Most
Common levers in the EU
- Scope and scale. Volume of people affected, categories of data, and cross border elements.
- Intent and negligence. Whether an infringement was intentional or negligent affects the amount within the applicable cap (Art. 83(2)(b)). Which cap applies depends on the provision infringed (Art. 83(4) and 83(5)): for example, breaches of the processing principles, lawful basis, data subject rights or transfer rules fall under the higher €20M or 4 percent maximum.
- Security controls. Insufficient technical and organizational measures add weight.
- Cooperation and remediation. Fast fixes and candor lower amounts. GDPR
California’s practical calculus
- Violation counting. Whether incidents are counted per person or per event.
- Minors. Higher ceiling for cases with actual knowledge that a consumer is under 16.
- Dark patterns. CPPA advisories stress user experience that frustrates rights, and design patterns can draw attention even before a breach occurs.
Case Snapshots, What “Average” Looks Like When Your Brand Is Involved
- Sephora, $1.2M under CCPA. Settlement with injunctive terms to honor opt outs and Global Privacy Control signals. This example is a clean illustration of how per violation statutes translate into a low seven figure outcome once consumer scale and injunctive commitments are included. California Attorney General
- Sector fines in the EU. For UK organizations with GDPR exposure, the largest GDPR penalties target cross-border processing and transparency failures. Even outside big tech, authorities have issued six and seven figure fines to utilities, healthcare, and commerce organizations when consent, transparency, or security measures fell short. See enforcement trends summarized by CMS.
What This Means For Your Budget, A Simple Forecast Model
Use this quick mental model to set reserves and prioritize controls.
- Countable population. Estimate the number of affected consumers or records.
- Violation multiplier. For California, consider per consumer, per incident logic. For the EU, consider the tier and potential percentage of turnover.
- Aggravators and mitigators. For U.S. organizations subject to CCPA/CPRA, minor’s data, prior incidents, dark patterns, and slow remediation raise exposure; fast fixes, documented DPIAs, and tested controls reduce it.
- Benchmark. Use about €2.28M (CMS all-fines average, cut-off 1 March 2026) only as a directional anchor; it is pulled up by a few very large fines, and most fines are far smaller. Use six to low seven figures for California actions involving well known brands. Adjust down if you are smaller, or up if your processing is cross border and high risk.
The Fastest Ways To Lower Fine Exposure This Quarter
Security and governance moves
- Close consent and cookie gaps. Honor Global Privacy Control, make opt outs and deletion easy, avoid dark patterns. CPPA has targeted these issues in guidance and actions. CPPA Enforcement Advisory 2024-02
- DPIA and RoPA hygiene. Keep Data Protection Impact Assessments current for high risk processing. Map records of processing and vendors.
- Data minimization. Delete stale data and shorten retention windows.
Documentation that pays off during investigations
- Testing evidence. Keep screenshots and logs showing consent UX, preference updates, and Global Privacy Control detection.
- Vendor contracts. Standard clauses that constrain ad tech and analytics data use, plus kill switches for misbehavior.
- Incident playbooks. Time boxed runbooks for consumer rights requests, breach notifications, and regulator contact.
Top Privacy Controls That Lower Fines
You can use this as a one page checklist to cut GDPR, CCPA, and CPRA exposure fast. Check each item and keep screenshots or logs as evidence. Where technical safeguards are in scope, professional penetration testing can independently validate whether exploitable weaknesses remain.
Data Mapping and Minimization
- Current Record of Processing Activities, systems and vendors mapped
- Data minimization enforced, stale data deleted on a rolling schedule
- Purpose limitation documented for each dataset
- Retention schedules applied in storage and backups
- High risk processing tagged for extra controls
DPIAs and Risk Reviews
- Data Protection Impact Assessments completed for high risk features
- Legitimate interest assessments where applicable
- Ad tech, analytics, and tracking risks reviewed with legal and security
- Third country transfer mechanisms documented, SCCs or alternatives in place
- Annual revalidation of DPIAs and risk registers
Consent, Cookies, and UX
- Consent flows are clear, specific, and granular
- Global Privacy Control honored for opt out
- Cookie banner matches actual tags, no non essential cookies before consent
- Opt out and delete paths reachable in three clicks or fewer
- No dark patterns, language and design do not trick or confuse
Consumer Rights Requests
- DSAR intake live and tested, identity verified in a privacy safe way
- Response workflow timed to statutory deadlines
- Redaction process for third party data in exports
- Deletion covers production, analytics, data warehouse, and backups per policy
- Audit trail kept for each request, timestamps and decisions included
Vendor and Contract Controls
- Processor and subprocessor list public and current
- DPA clauses signed and stored, breach notice windows defined
- Data use restrictions for ads and analytics written and enforced
- Termination and data return or deletion language verified
- Continuous vendor risk checks scheduled, evidence retained
Incident Readiness
- Breach playbooks tested with table top exercises
- Contact list for regulators and counsel maintained
- Notification decision matrix approved by legal and security
- Forensics ready logging, time sync, and data capture in place
- Press and customer communications templates prepared
Training and Accountability
- Annual privacy training for all staff, role based training for engineers and marketers
- Secure coding and privacy by design embedded in SDLC checklists
- Named DPO or privacy lead with authority and budget
- Quarterly metrics reported to leadership, risks and mitigations included
- Incentives aligned to reduce privacy risk, not only growth metrics
Evidence You Should Keep
- Screenshots and HAR files for consent and preference changes
- DSAR logs and response packets
- DPIAs, LIAs, RoPA exports, dated and signed
- Vendor DPAs and transfer assessments
- Patch and MFA compliance reports, SIEM retention proofs
Conclusion, The One Page Takeaway
The average GDPR fine sits around €2.28 million (CMS Enforcement Tracker Report 2026, cut-off 1 March 2026), a number that reflects steady EU enforcement across many sectors. California’s CCPA and CPRA use per violation amounts that escalate to six or seven figures once consumer counts or minors’ data are involved, and the CPPA’s design focused oversight means UX is now a compliance surface. Close consent and dark pattern gaps, keep DPIAs and vendor contracts tight, and document cooperation and remediation. Do these well and you lower both the probability and the price of your next enforcement event
Frequently Asked Questions
What is the average GDPR fine right now?
The average GDPR fine is about €2.28 million across 2018 to early 2026, based on the CMS Enforcement Tracker Report 2026 (cut-off 1 March 2026). Outliers are large, but seven figure results are common for medium to large organizations. CMS Law
How does California calculate CPRA fines?
California applies per violation amounts. As of recent CPPA updates, $2,663 for non intentional, $7,988 for intentional or minors’ data. The total depends on how many violations the agency counts, often per consumer. cppa.ca.gov
Do regulators consider cooperation and fixes?
Yes. Both GDPR and California decisions can reflect cooperation and remediation speed, which often lower the final penalty while shaping injunctive terms. GDPR
Are dark patterns a fine risk if there is no breach?
Yes. The CPPA has issued advisories against dark patterns that frustrate rights. Poor UX for opt outs and deletion requests can trigger enforcement. CPPA Enforcement Advisory 2024-02
Should we budget to the cap, or to the average?
Budget against a scenario range. Use the average as a directional anchor, then adjust for scale, intent, minors, and cross border processing. Outliers are rare, but prepare governance for worst case caps in contracts and insurance. CMS Law
Where can I see current EU fines and reasons?
The GDPR Enforcement Tracker lists fines by country, sector, and violation type, with filters and charts for trends.




