November 7, 2025
Updated: November 5, 2026
Two tests, two questions: can attackers breach your perimeter, and how far can they reach once they do.

Mohammed Khalil

Internal vs external penetration testing comes down to where the simulated attacker starts. An external test starts on the internet with no access and asks "can attackers get in?" through web apps, VPNs, email and exposed cloud services. An internal test starts inside the network, as a phished employee, stolen account or rogue insider, and asks "how far can they go?" through Active Directory, file shares and lateral movement. Most organizations run external first, then add internal; PCI DSS requires both, and mature penetration testing programs run both.
Updated: November 2026. Reflects current PCI DSS v4.0.1 requirements (which mandate both internal and external testing for the cardholder data environment) and initial-access data from Verizon's 2026 Data Breach Investigations Report.

| External penetration test | Internal penetration test | |
|---|---|---|
| Vantage point | The public internet (outside in) | Already inside the network (assumed breach) |
| Simulates | An anonymous attacker breaking in | A phished user, stolen creds, or malicious insider |
| Core question | "Can attackers get in?" | "How far can they go once inside?" |
| Typical targets | Web apps, VPNs, email, firewalls, exposed cloud | Active Directory, file shares, servers, lateral movement |
| Measures | Perimeter strength | Blast radius and internal segmentation |
| Relative cost | Usually lower (smaller, defined scope) | Often higher (larger internal estate) |
The one line to remember: external testing checks whether the front door is locked; internal testing checks what a burglar could reach once they're inside.
Looking for one test rather than the comparison? Our external penetration testing guide covers perimeter scope, process and a checklist, and our internal penetration testing guide covers assumed-breach methodology and Active Directory attack paths. This page compares the two and helps you decide which to run first.

An external penetration test targets your internet-facing perimeter, everything an anonymous attacker can see and reach from outside: web applications, APIs, VPN and remote-access gateways, email servers, firewalls, and exposed cloud services. The tester starts with no internal access, exactly as a real external attacker would, and tries to find a way in.
External testing answers the most fundamental question in security: is our perimeter actually holding? It finds exposed services, unpatched internet-facing systems, weak authentication, and misconfigurations. That matters because vulnerability exploitation was the most common initial access vector in Verizon's 2026 Data Breach Investigations Report, at 31% of breaches. Because the internet-facing surface changes constantly, external testing pairs naturally with ongoing attack surface management.

An internal penetration test starts from the assumption that the perimeter has already been breached. The tester is given a foothold inside the network, a standard employee's access, a connected device, or a set of low-privilege credentials, and then tries to do what a real intruder would: move laterally, escalate privileges, crack Active Directory, reach sensitive data, and evade detection, the core of a network penetration test. A common internal finding is a local administrator password shared across machines, which lets one captured hash unlock many hosts through pass-the-hash attacks.
Internal testing answers a different, equally important question: when (not if) someone gets in, how much damage can they do? It exposes flat networks with no segmentation, over-privileged accounts, weak internal credentials, and unmonitored lateral movement, the conditions that turn a single phished laptop into a full domain compromise. In the same Verizon dataset, phishing (16%) and credential abuse (13%) remained common ways in alongside exploitation (31%), so it is realistic to assume a foothold is achievable and test what an attacker can reach afterward.
For the full methodology, attack paths and a checklist, see our guide to internal penetration testing.

Beyond the vantage point, several practical differences shape how you scope each test.
| Dimension | External | Internal |
|---|---|---|
| Starting access | None (anonymous) | A foothold inside |
| Threat modeled | Outside attacker | Insider, phished user, post-breach attacker |
| Primary findings | Exposed services, unpatched perimeter, weak auth | Lateral movement, privilege escalation, weak segmentation, AD flaws |
| Typical tools/focus | Recon, web/app exploitation, credential attacks on gateways | Active Directory attacks, pivoting, credential harvesting |
| Scope size | Smaller, well-defined (the perimeter) | Larger (the internal estate) |
| Detection tested | Perimeter and edge alerting | Internal monitoring, EDR, SIEM, segmentation |
The most useful way to hold the distinction: external testing reduces the chance of a breach; internal testing reduces the impact of one. Neither substitutes for the other.
The same core toolkit can appear in both engagements, but the emphasis changes with the starting position. Wireless environments need a dedicated wireless penetration testing engagement beyond internal and external scopes.
| Area | External testing | Internal testing |
|---|---|---|
| Reconnaissance | DNS, public IPs, certificates, exposed services | Host, domain, share, trust, and identity enumeration |
| Network testing | Nmap-style port/service discovery, gateway testing | Internal service discovery, segmentation and pivot testing |
| Application testing | Web/API proxies such as Burp Suite; authentication and business-logic testing | Internal web apps, admin interfaces, databases and service-to-service trust |
| Identity testing | Password policy and exposed authentication gateways | Active Directory/Entra ID paths, credential exposure, privilege escalation |
| Common specialist tools | Nmap, Burp Suite, vulnerability scanners, controlled exploit frameworks | BloodHound, credential-audit tooling, Responder-style name-resolution testing, plus network and exploit tooling |
Tools do not define test quality, and recognized methodologies such as NIST SP 800-115 apply to both. The important difference is the hypothesis being tested: an external tester looks for a path from the internet to meaningful access, while an internal tester starts with limited access and tries to expand privilege, reach, and impact.
Findings vary by environment, but the same categories recur. The examples below are common, non-exhaustive patterns, described at the level a scoping or remediation discussion needs.
Treat these as hypotheses for scoping, not a checklist. A useful report shows which weaknesses actually chain together in your environment and what an attacker could reach as a result.
Accurate inputs keep quotes comparable and keep testing inside authorized boundaries. Expect a provider to ask for the following.
An external tester needs nothing from you except written authorization and a scope. An internal tester needs a starting point inside the network, and how you provide it shapes cost, logistics and what the test proves. Three delivery models are common:
The knowledge level is a separate choice. Internal tests are usually gray box, with credentials and a network map, because that reflects what an attacker learns quickly after landing; external tests are often black box from the internet, sometimes with test accounts for authenticated applications. Our guide to black box vs white box testing explains the trade-offs.
Most organizations should start with an external penetration test, because it shows whether attackers can get in through internet-facing web apps, portals and remote access. Choose internal testing when insider threat, ransomware blast radius or a flat network is the main concern, and choose both for a complete picture of initial access and post-breach impact.

This is the question most teams are really asking. Use this decision guide.
A practical rule of thumb: prioritize the test that matches your highest-risk attack path. For many organizations with a large public attack surface, that means starting external; for organizations with a complex internal estate, Active Directory exposure, or a strong assumed-breach concern, internal testing may be the higher priority. When your environment changes constantly, a continuous penetration testing model can cover both on an ongoing basis.

Sometimes the most useful assessment is not two disconnected tests but one layered attack path. The tester begins externally, establishes a controlled foothold if one exists, and then continues into the internal environment under pre-agreed rules of engagement.
This model answers a third question beyond "can they get in?" and "how far can they go?": what is the realistic end-to-end impact of one successful initial compromise?
A layered test is especially useful when you want to validate segmentation, identity controls, EDR/SIEM visibility, and incident-response detection across the full attack chain. It requires tighter scoping and safety controls than a standalone external or internal test, so the transition from perimeter testing to internal activity should be explicitly authorized in the statement of work.
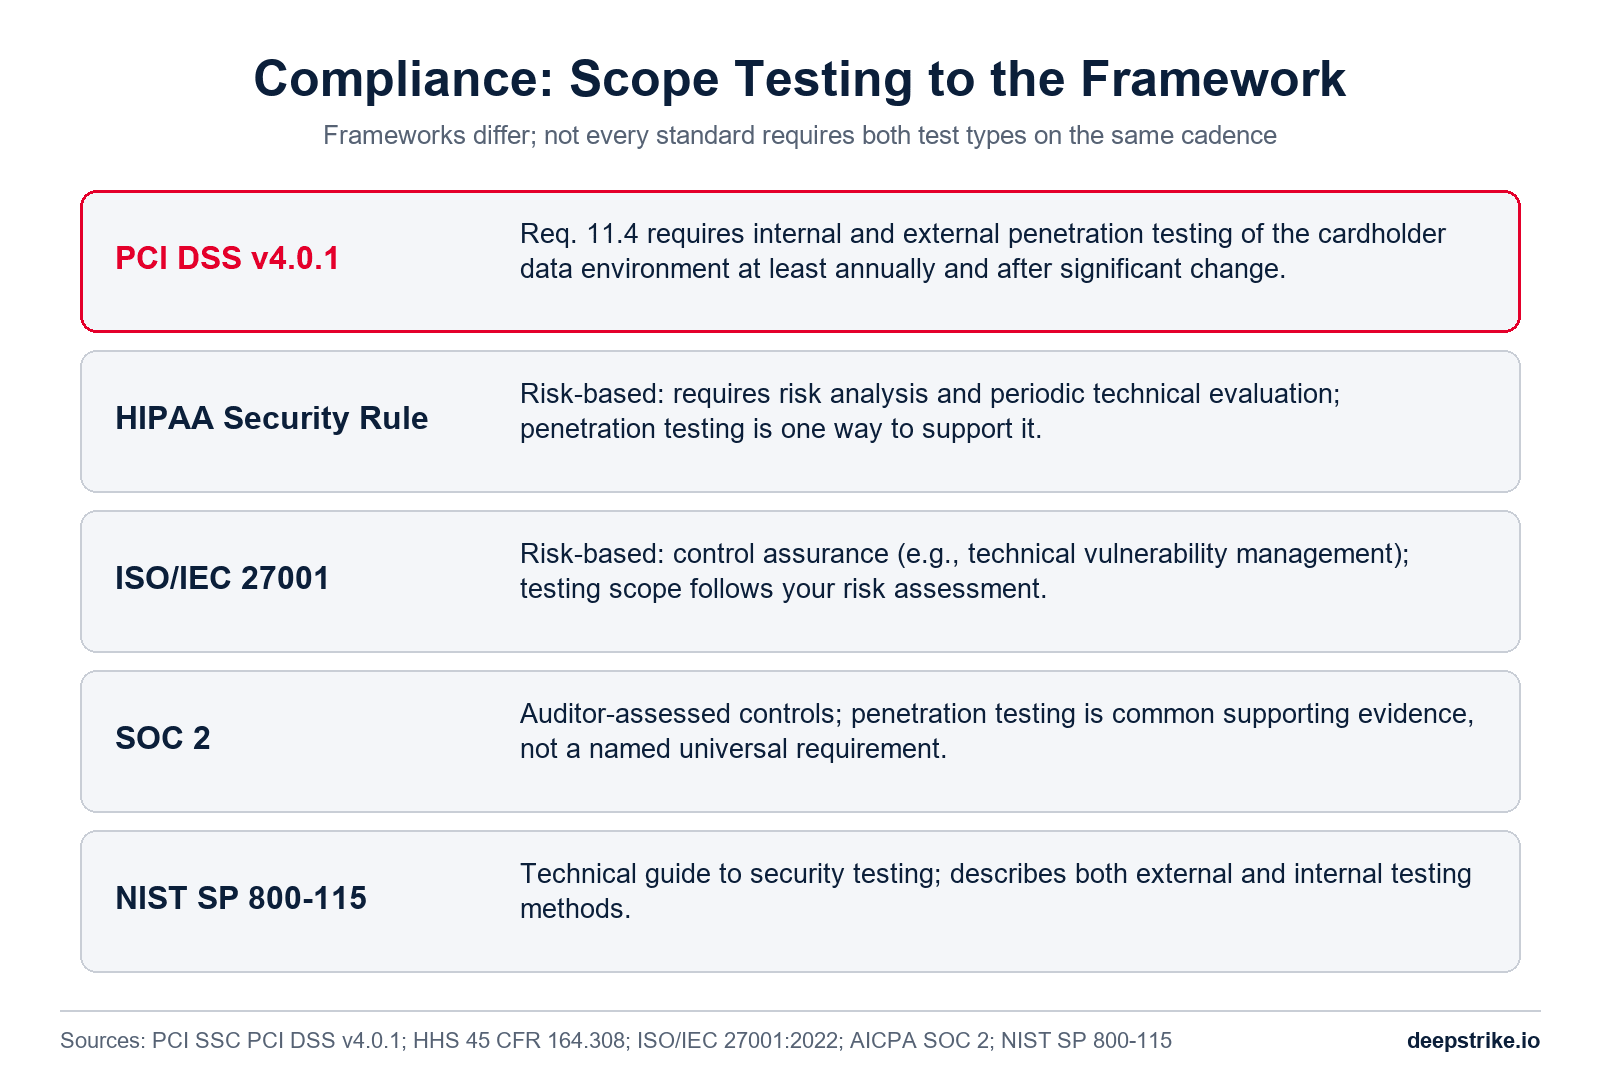
If a regulation is driving your test, scope to the framework rather than assuming every standard requires the same thing. PCI DSS v4.0.1 Requirement 11.4 explicitly requires internal and external penetration testing for the applicable cardholder-data environment at least annually and after significant change, as published by the PCI Security Standards Council and broken down in our PCI DSS penetration testing guide. Other frameworks and regulations, including SOC 2, ISO 27001, HIPAA, FedRAMP, and DORA, use different risk, control-assurance, or testing models and should not be summarized as universally requiring both types on the same cadence. Our penetration testing for compliance guide maps the differences.
"Internal vs external" sometimes means something else: who runs the test, not where it starts. An in-house security team is an internal tester; a contracted firm is an external tester. Either can run an internal or an external network test, so the two questions are independent.
Standards care more about qualification and independence than about employment. PCI DSS v4.0.1 Requirement 11.4.1 lets a qualified internal resource or a qualified external third party perform penetration testing, as long as the tester is organizationally independent of what is being tested, and it does not require a QSA or ASV. In practice, in-house teams are strong for frequent, targeted retesting because they know the environment. Third parties bring a fresh attacker's view, specialist depth, and the independent report that customers, auditors and insurers usually ask for.
A common split is in-house testing for releases and fixes, with a third-party internal and external test each year or after major change. If you are choosing a provider, our guide on how to choose a penetration testing company lists the questions to ask.
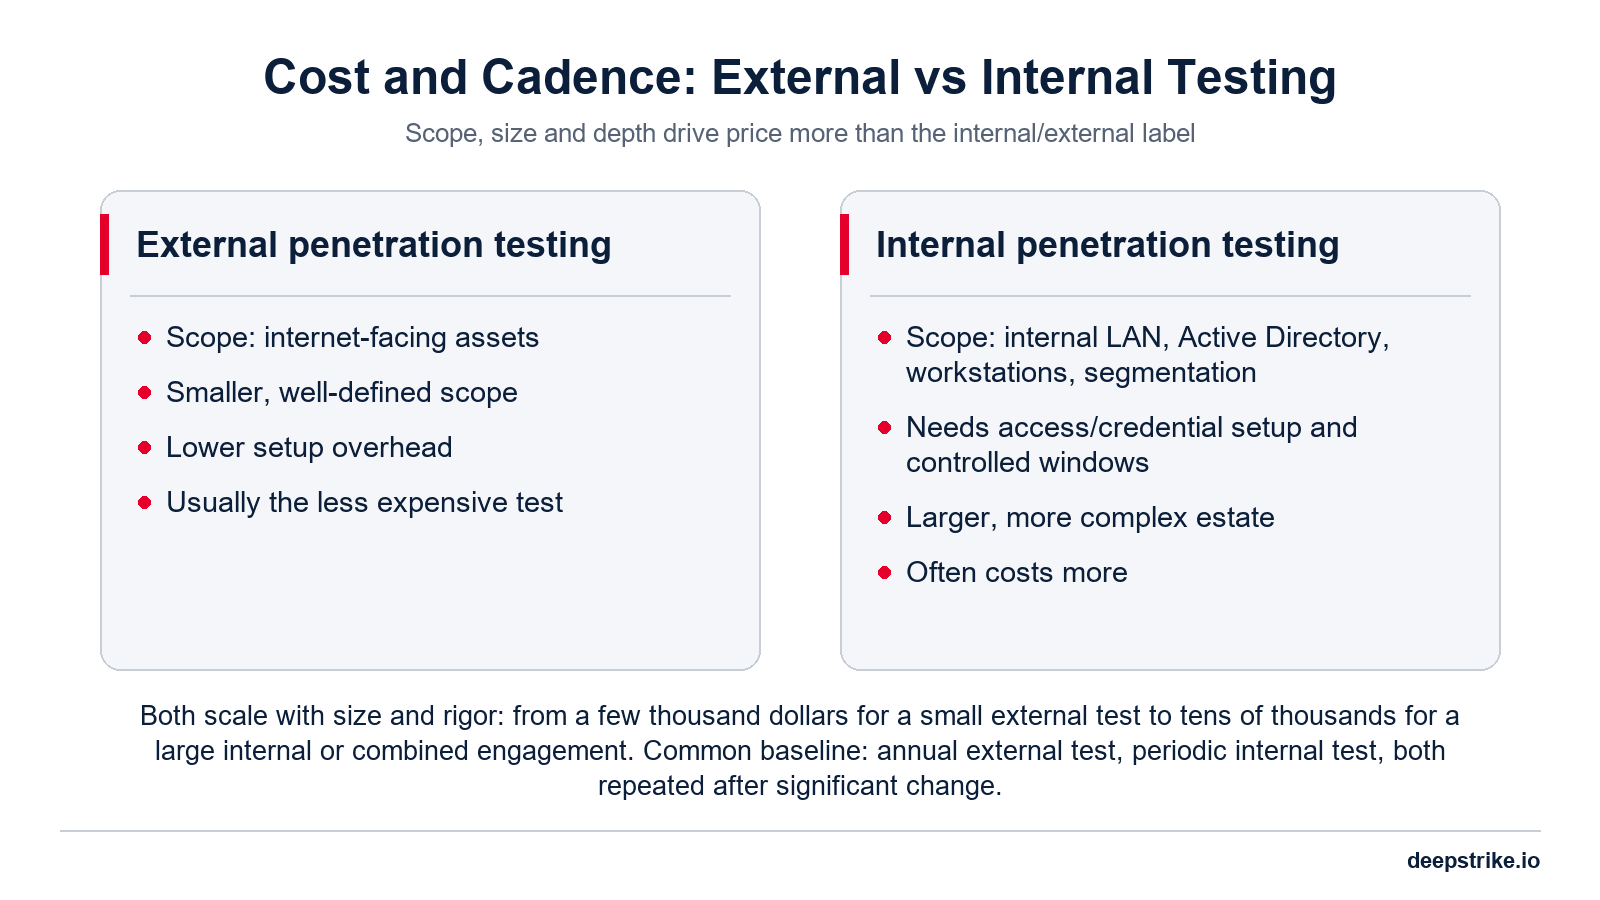
Cost depends far more on scope, size, and depth than on the internal-versus-external label, but a few patterns hold:
For real figures and what drives them, see our penetration testing cost guide. On cadence, the common baseline is an annual external test and a periodic internal test, with both repeated after significant changes, and more frequently for high-risk or heavily regulated environments.
Duration follows scope, not the label. As a planning estimate, a small external perimeter can often be tested within a week of active testing, while an internal test across several sites and Active Directory domains usually takes longer because there is more to enumerate and more attack paths to follow. Add time for access setup on internal tests (shipping a device or provisioning accounts), for reporting, and for a retest once fixes land. Ask each provider to break its estimate down by phase so you can compare like with like.


Internal versus external penetration testing is not a competition, it is two halves of the same picture. External testing tells you whether attackers can breach your perimeter; internal testing tells you how much they can reach once they do. In a world where the initial foothold is often easy, both questions matter, which is why the best answer for most organizations is "both," sequenced sensibly and repeated as your environment changes.
DeepStrike's penetration testing covers both external and internal perspectives, manual, adversary-realistic, and mapped to your compliance needs, so you know both whether attackers can get in and how far they could go. To scope an engagement, see our penetration testing services.
External penetration testing simulates an attacker trying to break in from the internet, testing your perimeter (web apps, VPNs, firewalls, exposed services). Internal penetration testing assumes the attacker is already inside and tests how far they can move, escalate privileges, and reach sensitive data. External asks "can they get in?"; internal asks "how bad is it once they do?"
For most organizations, yes. They answer different questions, external reduces the chance of a breach, internal reduces its impact, and major compliance frameworks like PCI DSS v4.0.1 explicitly require both. If you can only run one first, an external test is the usual starting point, but plan for internal testing, since assuming breach is the realistic modern threat model.
Internal tests are often more expensive because the internal environment, hosts, Active Directory, and applications, is usually larger and more complex than the defined internet-facing perimeter an external test covers. That said, cost depends far more on scope, size, and depth than on the internal-versus-external distinction itself.
Yes. PCI DSS v4.0.1 Requirement 11.4 explicitly requires both internal and external penetration testing at least once every 12 months and after any significant change to the cardholder data environment, plus segmentation testing (every six months for service providers). Scoping only one perspective typically leaves a compliance gap.
The common baseline is an annual external test plus a periodic internal test, with both repeated after significant changes such as a new application, infrastructure migration, or merger. High-risk and heavily regulated environments often test more frequently, and continuous or PTaaS models cover both on an ongoing basis.
External testing alone tells you whether attackers can breach your perimeter, but not what happens after they do, and in modern breaches the initial foothold is often the easy part. Relying only on external testing leaves the internal blast radius, flat networks, over-privileged accounts, weak segmentation, untested, which is exactly where ransomware does its damage.
You can use an in-house team if it is qualified and independent of the systems it tests. PCI DSS v4.0.1 Requirement 11.4.1 accepts a qualified internal resource or a qualified external third party, provided organizational independence exists. Many organizations still hire a third party for annual or audit-driven tests, because customers and auditors often expect independent evidence and outside testers bring a fresh view.
It is an internal test run without a tester on site. The provider ships a small testing device or supplies a virtual machine that you place on the internal network, or connects through VPN, and the tester works through that controlled foothold. The findings are the same as an on-site internal test, as long as the device sits on the network segments you want tested.
Usually on the external-facing application, because anyone on the internet can reach it without first gaining access. An internal SQL injection is still serious: any phished laptop or insider can reach it, internal apps often hold sensitive data, and they tend to get less monitoring. Rate both by exploitability and data impact, not by location alone.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
