August 18, 2025
Updated: November 5, 2026
Education is still the most attacked sector in 2026, averaging 4,696 weekly attacks per organization. Learn the causes, costs, case studies, and defense strategies for schools.

Mohammed Khalil
A data breach in education occurs when unauthorized parties steal or expose sensitive school data including student records, staff information, and proprietary research. In 2026, this is no longer a rare event; it's a daily crisis demanding urgent attention.
Here’s the deal: Recent intelligence confirms that schools and universities now face more cyberattacks than any other sector. And this isn't by accident. Attackers have made a strategic choice, viewing educational institutions as “target rich, cyber poor” a term used by CISA’s K–12 Cybersecurity Initiative to describe organizations that hold vast amounts of sensitive data but often lack the resources for robust protection.
The numbers are staggering. Between January and July 2026, the education sector endured an average of 4,696 cyberattacks per organization every week, according to Check Point Research. This means that while you're reading this, criminals are actively trying to access student names, grades, Social Security numbers, and more. A breach can violate privacy laws like the Family Educational Rights and Privacy Act (FERPA), leading to identity theft for minors and lasting financial and emotional harm for families. In short, educational institutions are under siege, and protecting student and staff data has never been more critical.
Education-specific data and broader cybersecurity statistics paint a clear and alarming picture of a sector under relentless attack. The trend is not just increasing; it's accelerating, solidifying education's position as a top target for cybercriminals worldwide.
Did you know? The education sector endured an average of 4,696 cyberattacks per organization every week from January to July 2026, more than double the global average of 2,150.
According to the 2026 Verizon Data Breach Investigations Report (DBIR), the Educational Services sector recorded 1,302 security incidents, with 1,252 confirmed data disclosures. The primary attack patterns were System Intrusion (hacking), Social Engineering (phishing), and Miscellaneous Errors (accidental exposure), together accounting for 83% of breaches in the industry. External actors were behind 78% of education breaches, and 78% were financially motivated.
Global threat intelligence from Check Point Research further quantifies this siege:
This constant barrage comes with a significant financial toll. The IBM X Force 2025 Cost of a Data Breach Report found that while the global average cost of a breach saw its first decline in five years, education was one of the few industries where costs increased. In IBM's 2026 Cost of a Data Breach Report, the global average rose to a record $4.99 million, and the average U.S. breach now costs $11.5 million, so the financial risk for unprepared schools is immense. Ransomware adds to the bill: the Sophos State of Ransomware in Education 2026 report puts the median ransom payment in education at $515,000, and EDUCAUSE tracks the long tail of legal, notification, and recovery work that follows a higher education breach.
Learning from real world incidents makes abstract threats tangible. These recent high profile breaches reveal a systemic, interconnected chain of failure in the educational cybersecurity ecosystem.
PowerSchool, a major education technology provider serving over 60 million students, suffered a devastating breach that perfectly illustrates third party risk. According to federal charging documents, the attacker used credentials assigned to a PowerSchool contractor to access the company's network on September 4, 2024, moved student and teacher data to a server he had leased in Ukraine on December 20, 2024, and sent a ransom demand on December 28, 2024, the day PowerSchool says it discovered the incident. The access ran through PowerSchool's PowerSource customer support portal.
The Chicago Public Schools (CPS) breach highlights how a vulnerability in a single piece of software can have far reaching consequences. According to CPS, the incident began late in 2024 when attackers compromised Cleo, a file transfer vendor the district uses to share data with other agencies. As Chalkbeat reported, the Russia linked "Clop" ransomware gang exploited this flaw to steal data not just from CPS but from dozens of other organizations nationwide.
Major universities are also prime targets, as shown by the breach at Columbia University that affected 868,969 individuals, according to the university's filing with the Maine Attorney General. An unauthorized actor gained access to the university's network and exfiltrated files for several weeks before a June 2025 systems outage exposed the intrusion.
These incidents reveal a deeply interconnected system where a school's security is defined by the weakest link in its entire digital supply chain. The 2026 Verizon DBIR found third party involvement in 48% of all breaches, up 60% year over year, and in 40% of breaches in the education sector.
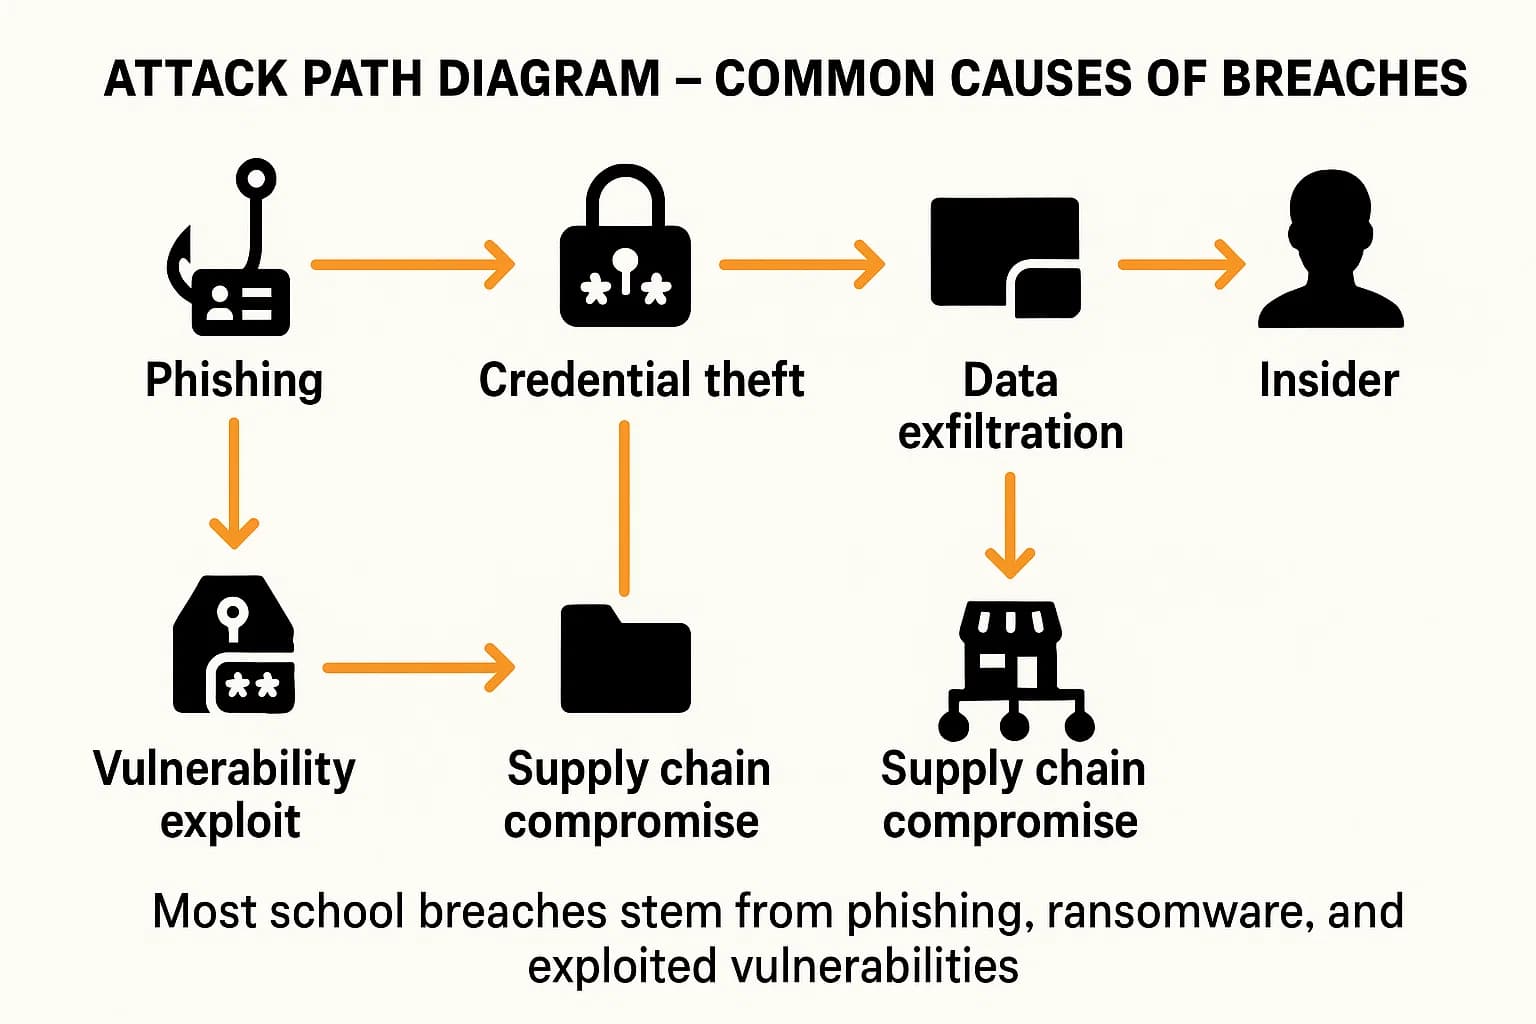
Attackers follow a predictable playbook, exploiting a handful of recurring weaknesses. Understanding these methods is the first step toward building an effective defense.
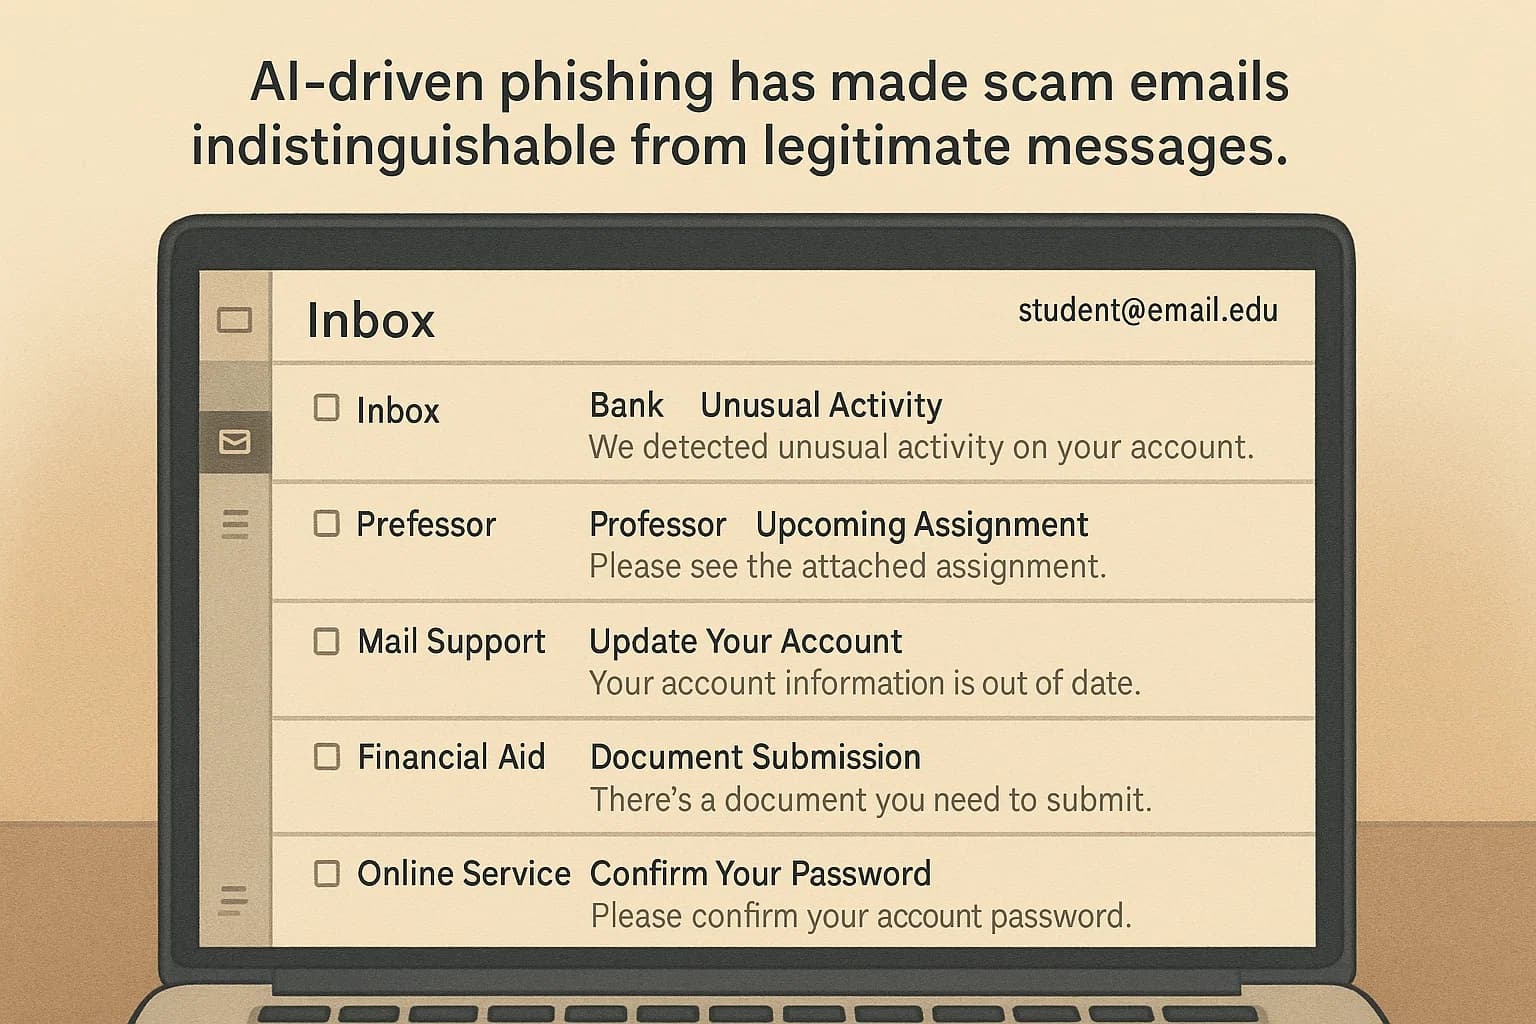
A major emerging threat in 2026 is the rise of AI driven phishing. Attackers are now using generative AI to create hyper personalized and highly convincing scam emails at a massive scale. These are not the typo ridden emails of the past; AI can mimic corporate writing styles, reference recent events, and even generate deepfake voice and video to impersonate executives. SlashNext reported a 1,265% increase in malicious phishing emails in the year after ChatGPT launched, and IBM's 2026 research found that 1 in 4 malicious breaches were AI-enabled. In education, Sophos found that identity-based techniques such as malicious email, phishing, and compromised credentials were behind 85% of ransomware attacks.
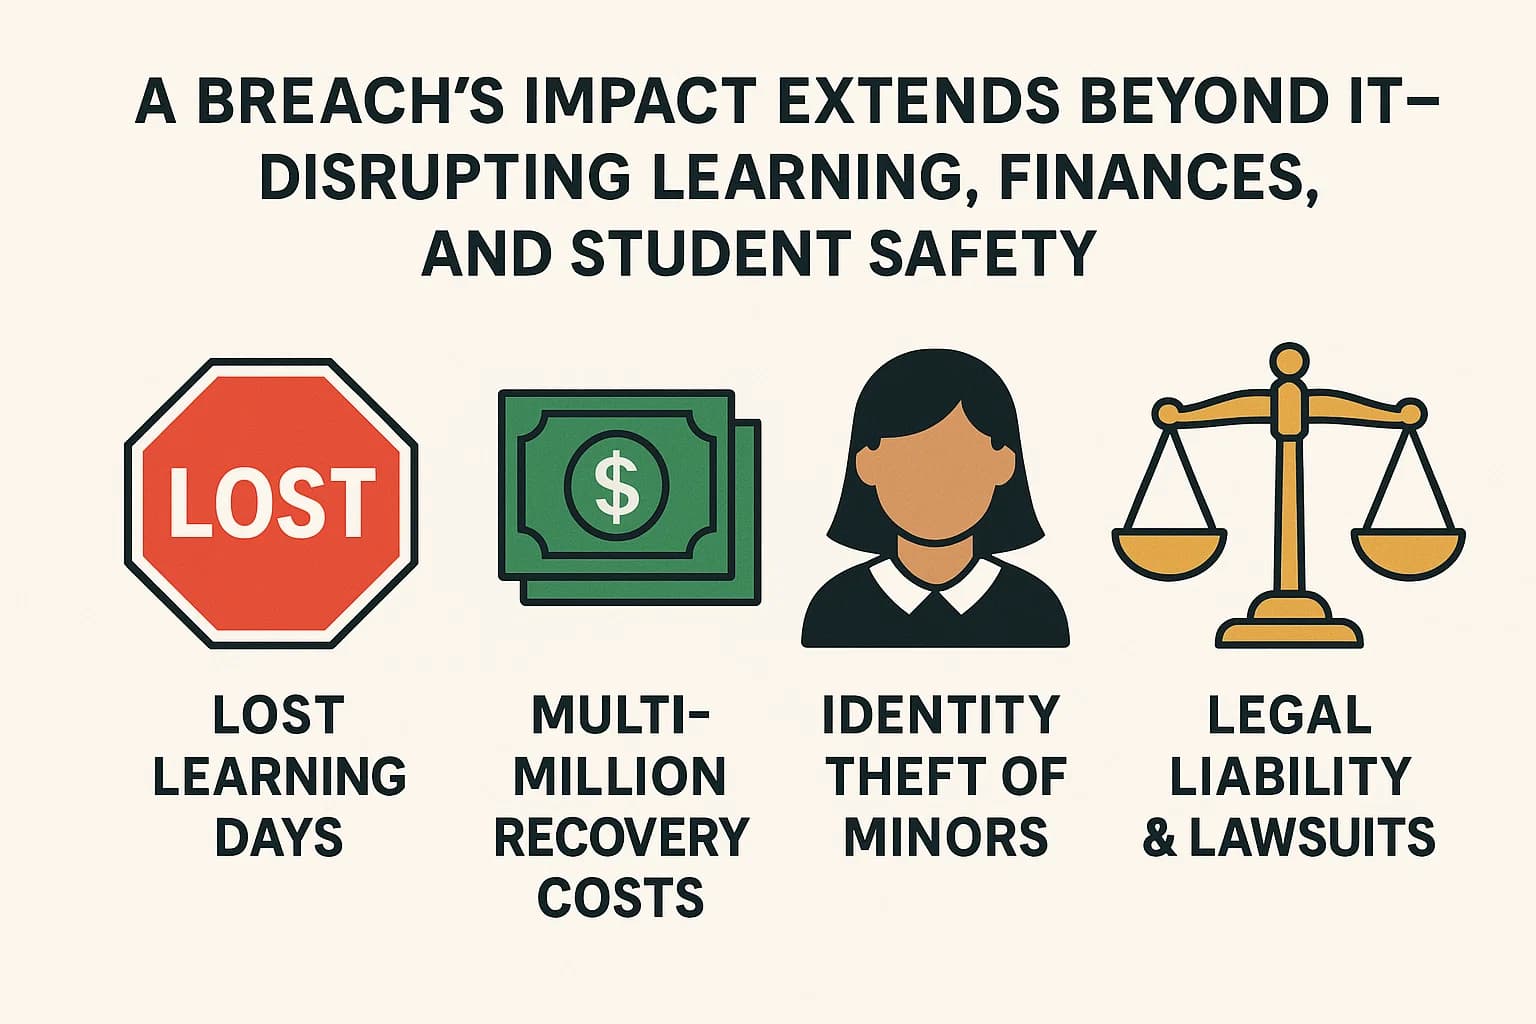
When a school suffers a data breach, the fallout extends far beyond the IT department, inflicting deep and lasting damage on the entire community.
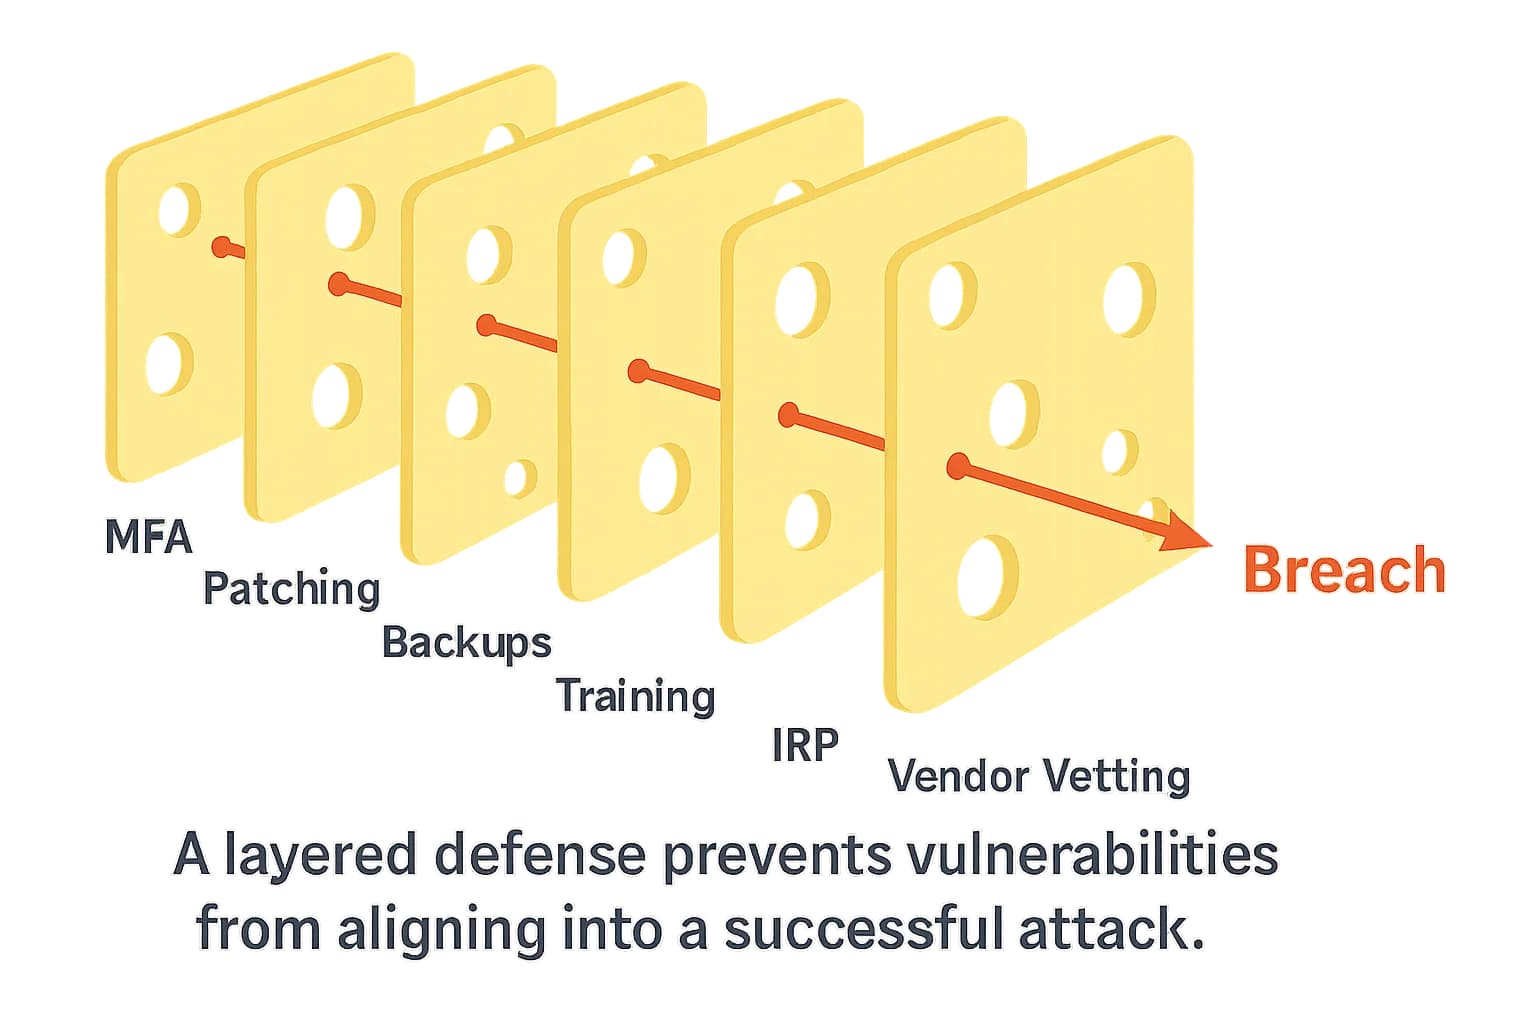
While the threats are daunting, the situation is far from hopeless. A proactive, layered defense strategy often compared to the "Swiss cheese model" of risk management can dramatically reduce risk. In this model, each security control is a slice of cheese with holes (weaknesses). No single slice is perfect, but by layering multiple slices (MFA, patching, training, etc.), you make it highly unlikely that the holes will align to allow a threat to pass through.
MFA, patching, and backups are among the measures prioritized by CISA’s “Protecting Our Future” K–12 Cybersecurity Initiative. EDR and network segmentation are additional widely used controls.
Technology alone isn't enough. As K12 SIX steering committee member Richard Thomas (Linn Benton Lincoln ESD) said when the group announced its 2025-26 steering committee in August 2025, "Cybersecurity in K-12 is just too big and too underfunded for any one district to handle on its own... What makes K12 SIX so valuable is that it gives us a way to come together sharing knowledge, support, and threat intelligence so we can all do a better job protecting our schools".
A strong security posture requires a strategic approach grounded in established frameworks.
A proactive security audit can be a great first step. Learn how our penetration testing services can help you test these controls.
As attacks escalate, many educational institutions are turning to cyber insurance to mitigate the financial fallout of a breach. This insurance can cover costs related to breach response, business interruption, data restoration, and legal liabilities.
However, getting coverage isn't a simple checkbox. Insurers are now demanding that schools demonstrate strong security hygiene to qualify for a policy and to keep premiums affordable. Key factors that affect premiums include:
In 2026, cyber insurance is becoming less of a safety net and more of a forcing function for better security practices across the education sector.
Navigating the legal landscape of data privacy is complex but essential.
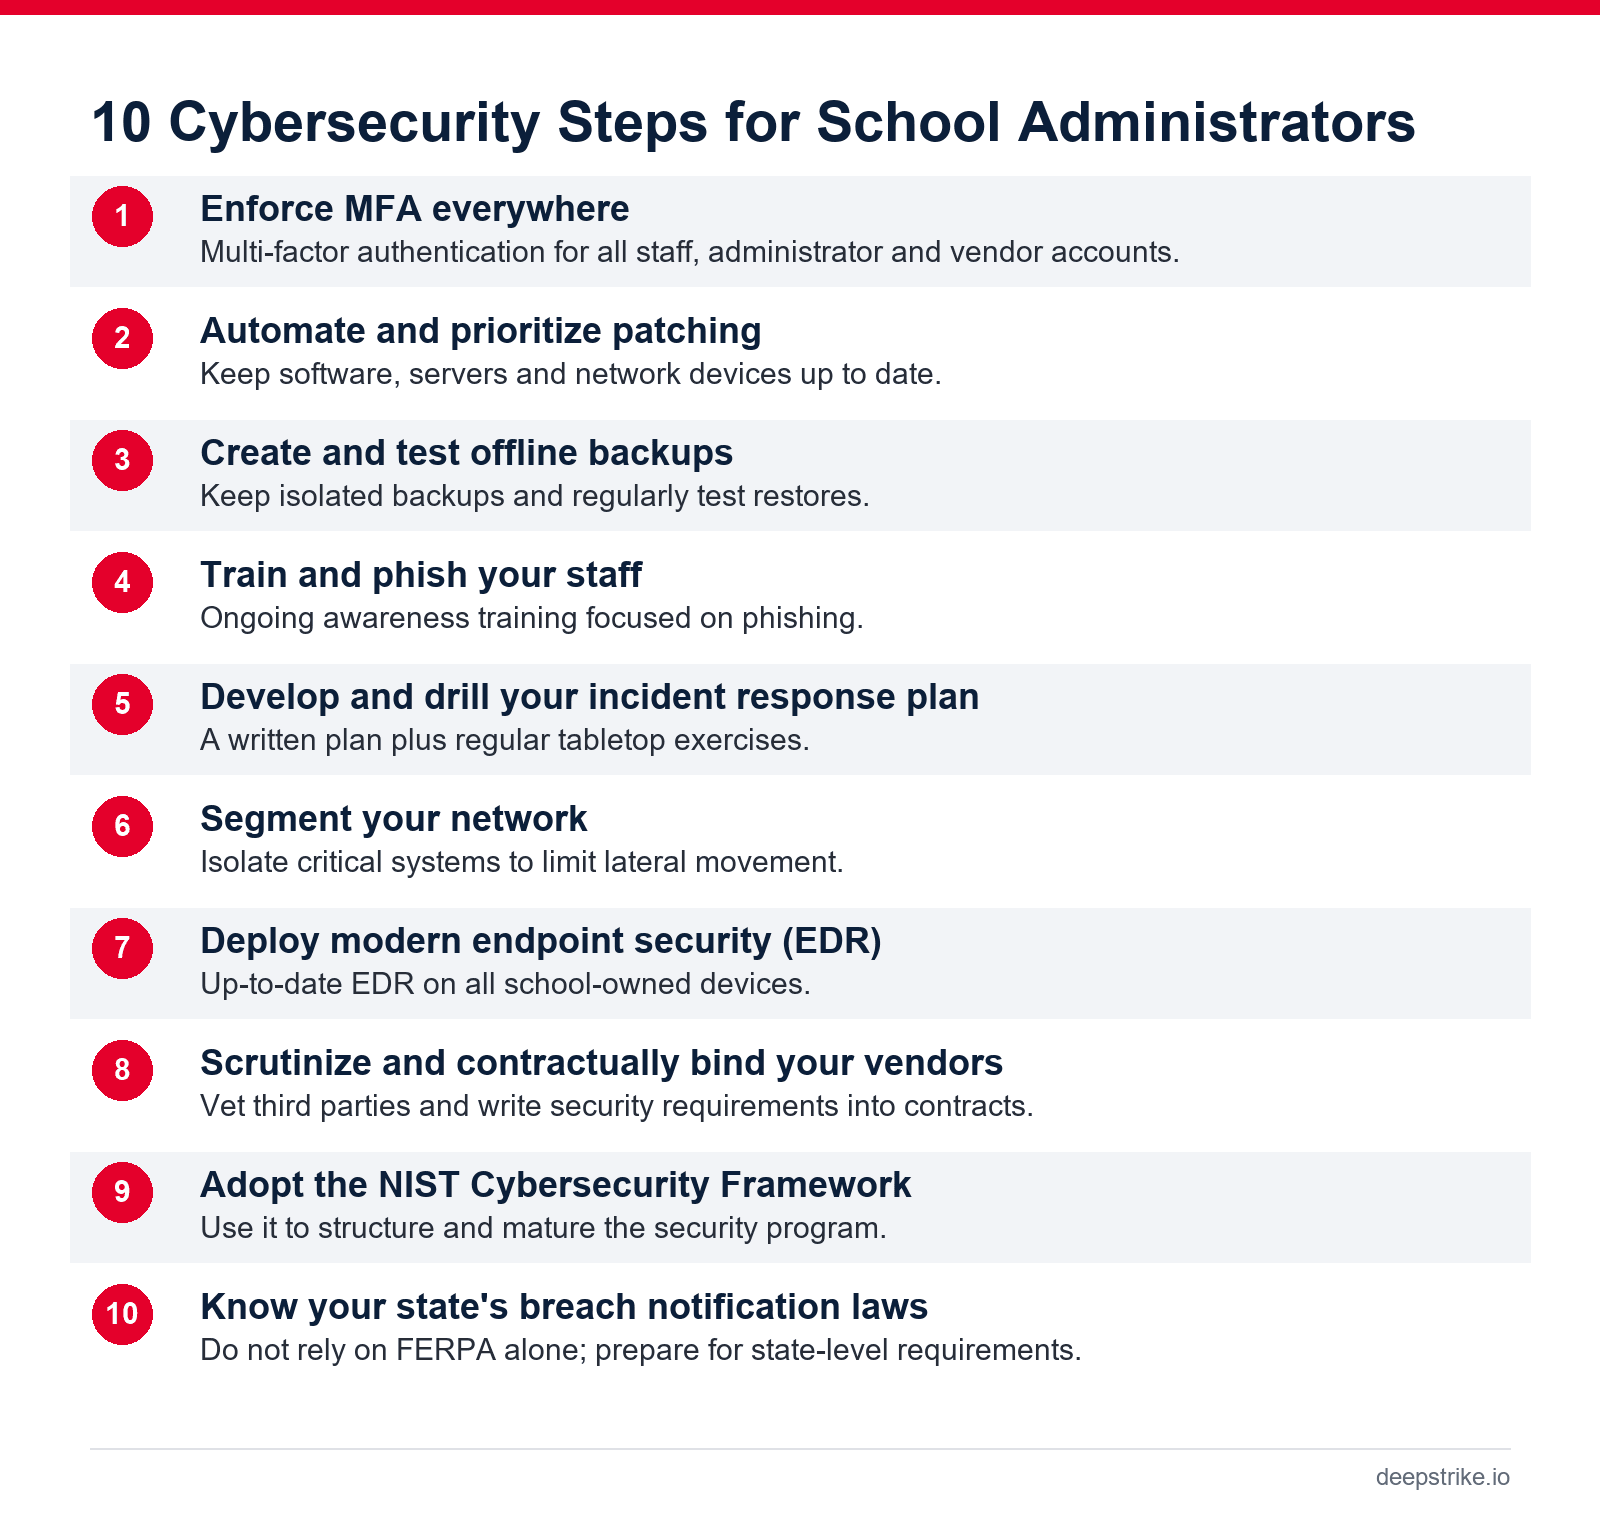
Here are the top 10 actionable steps for school cybersecurity best practices:
What is a data breach in education?
A data breach in education is any incident where sensitive school data such as student records, staff details, or health information is accessed or stolen by unauthorized parties. This can happen through hacking, phishing, ransomware, or insecure third party services.
Why are K 12 and universities such common targets for hackers?
A: Schools are prime targets because they hold massive amounts of valuable personal data but often have limited budgets and less mature security defenses. The open nature of campus networks and the critical need to maintain operations make them vulnerable to social engineering and ransomware demands.
How can schools protect against data breaches?
The most effective protections include deploying multi factor authentication (MFA), applying security patches promptly, maintaining and testing offline backups, and providing regular staff training on phishing. CISA's K 12 cybersecurity guidance highlights these as top priorities. Proactive security assessments, like those from a continuous penetration testing platform, also help uncover risks.
What should a school do if a breach occurs?
Immediately activate your incident response plan. The first steps are to contain the breach (e.g., isolate infected systems), preserve evidence, and engage cybersecurity experts. You must then notify affected individuals and regulatory bodies according to your state's laws and report the incident to law enforcement.
Does FERPA require schools to report data breaches? A: No, this is a common misconception. FERPA itself does not require schools to notify parents of a data breach. It only requires that the unauthorized disclosure be recorded. However, every state has its own data breach notification law; whether and how it applies to a school or district varies, so check your state's law and student-privacy statutes.
Are student information systems (SIS) secure?
The security of SIS platforms varies widely. As the PowerSchool incident demonstrated, even major platforms can be vulnerable if they lack basic controls like MFA. Schools must demand strong security from their vendors, including encryption, regular penetration testing, and clear contractual obligations for breach notification.
How do AI driven phishing trends affect schools?
AI is making phishing attacks far more sophisticated and harder to detect. Attackers use AI to create personalized, error free emails that can convincingly impersonate trusted sources. IBM's 2026 Cost of a Data Breach research found that 1 in 4 malicious breaches were AI-enabled, and Sophos found identity-based techniques such as phishing and stolen credentials behind 85% of ransomware attacks on education, which makes user training and advanced email security filters more critical than ever.
Data breaches in education are no longer a hypothetical risk; they are a clear and present danger. The stakes involve not just financial loss, but the fundamental privacy and safety of students. The evidence shows that schools face relentless threats, from ransomware gangs that cripple entire districts to supply chain attacks that expose millions of records at once.
But the situation isn't hopeless. By taking proactive and decisive steps enforcing MFA, patching systems diligently, maintaining tested backups, and relentlessly training staff educational institutions can build a resilient defense. The threats are complex, but the most effective solutions are foundational. Moving from a reactive posture to one of proactive readiness is the only way to safeguard our schools.
Ready to Strengthen Your Defenses?
The threats of 2026 demand more than just awareness; they require readiness. If you're looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
These measures are foundational, but many schools struggle to validate whether they’re actually working. That’s where expert testing comes in. Learn how we can test your MFA & patching readiness with DeepStrike’s penetration testing services.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
