October 14, 2025
Updated: November 5, 2026
As of November 2026, CMMC does not explicitly require pentesting at Level 1 or 2, while the Level 3 model does. Here is how the Phase II suspension affects scope, evidence, scanning, timing, and readiness decisions.

Mohammed Khalil
As of November 2026, CMMC penetration testing is not an explicit requirement at Level 1 or Level 2. Level 2 requires periodic vulnerability scanning and security-control assessment under NIST SP 800-171 Revision 2; a well-scoped pentest can support those activities but does not replace the CMMC assessment. The CMMC Level 3 model explicitly requires penetration testing at least annually and after significant system changes under CA.L3-3.12.1e. However, the Department has paused Phase II and currently permits only Level 1 and Level 2 self-assessment requirements in solicitations and contracts. US defense contractors can shortlist providers from the top US cybersecurity companies.
2026 implementation update: On July 13, 2026, the Department of War suspended CMMC Phase II and future milestones. Phase I self-assessments remain in place. The official CMMC program page should be treated as the source of truth for further implementation changes. As of November 4, 2026, that page still describes Phase II as suspended, and the Department had not announced the outcome of its CMMC Reform Task Force review or a new Phase II date.
That distinction matters. The underlying CMMC model still defines three levels, but the assessment level that a contracting officer may currently place in a solicitation or contract is narrower during the suspension. Older regulations and contract materials may still use “Department of Defense” or “DoD,” while the current program site uses “Department of War” or “DoW.”
Two rules make CMMC enforceable. The program rule, 32 CFR Part 170, was published on October 15, 2024 and took effect on December 16, 2024. It defines the three levels, the assessment types, scoring, POA&M limits and four implementation phases. The acquisition rule, the 48 CFR DFARS CMMC rule (DFARS Case 2019-D041), was published on September 10, 2025 and took effect on November 10, 2025. That date started Phase 1, because 32 CFR § 170.3(e) ties Phase 1 to the DFARS rule and starts each later phase one calendar year after the one before it.
| Date | Milestone | Status on November 4, 2026 |
|---|---|---|
| Oct 15, 2024 | 32 CFR Part 170 final rule published (89 FR 83092) | Final rule |
| Dec 16, 2024 | 32 CFR Part 170 takes effect | In force |
| Sep 10, 2025 | 48 CFR DFARS final rule published (90 FR 43560) | Final rule |
| Nov 10, 2025 | DFARS rule takes effect and Phase 1 begins: Level 1 (Self) or Level 2 (Self) as a condition of award, with Level 2 (C3PAO) at DoD discretion | Phase 1 remains in place |
| Jul 13, 2026 | DoW CIO suspends the Phase 2 transition and pending and future milestones; an Under Secretary memo implements it the same day | Suspension in effect |
| Sep 3, 2026 | Class Deviation 2026-O0025, Revision 3 tells contracting officers to remove or revise suspended CMMC requirements | In effect |
| Nov 10, 2026 | Planned Phase 2: Level 2 (C3PAO) as a condition of award for applicable contracts; Level 3 (DIBCAC) at DoD discretion | Suspended; no new date |
| Nov 10, 2027 | Planned Phase 3: Level 2 (C3PAO) also before option periods; Level 3 (DIBCAC) for applicable contracts | Suspended future milestone |
| Nov 10, 2028 | Planned Phase 4: CMMC in all applicable solicitations and contracts, including options on older contracts | Suspended future milestone |
The 2027 and 2028 dates come from the one-year rule in § 170.3(e). The Department's July 13, 2026 announcement suspended "pending and future" implementation milestones along with Phase 2, so none of those later dates is currently scheduled. The same announcement set up a CMMC Reform Task Force with a 60-day review. As of November 4, 2026, the Department had not published the review's results or a new Phase 2 date.
Trade press has reported options under discussion, such as restarting Phase 2 for a narrower group of contractors, but none is an official decision. Treat any restart date as unconfirmed until it appears on the DoW CIO CMMC page or in the Federal Register.
The September 3 class deviation matters for contract language. Class Deviation 2026-O0025, Revision 3 tells contracting officers to use a revised DFARS Part 240 in place of the codified text and to remove or revise CMMC requirements in line with the July 13 memorandum. It keeps baseline NIST SP 800-171 Rev 2 compliance under DFARS 252.204-7012, and it keeps the SPRS check before award and before an option is exercised when a contract requires a CMMC level.
Only at Level 3. CMMC Level 1 and Level 2 contain no explicit penetration-testing requirement, although a pentest can support Level 2 evidence, while Level 3 requires a pentest at least annually and after significant security changes. Level by level:
A pentest and a CMMC assessment answer different questions. A pentest asks whether an authorized tester can exploit weaknesses in a defined scope. A CMMC assessment asks whether the organization has implemented every applicable practice and can demonstrate that implementation through sufficient evidence. One activity can inform the other, but they are not interchangeable.
For organizations deciding whether testing is appropriate, it helps to begin with the difference between a vulnerability assessment and a penetration test. A scanner identifies potential weaknesses at scale; a pentest uses controlled human analysis to validate exploitability, attack paths, and business impact.
| CMMC level | Underlying model | Assessment designation allowed during the Phase II suspension | Explicit pentest requirement? |
|---|---|---|---|
| Level 1 | 15 FAR 52.204-21 requirements | Annual self-assessment and annual affirmation | No |
| Level 2 | 110 NIST SP 800-171 Rev. 2 requirements | Self-assessment every three years and annual affirmation | No |
| Level 3 | Level 2 requirements plus 24 selected NIST SP 800-172 requirements | Level 3 DIBCAC designation is suspended | Yes, in the underlying model |
The current model language appears in 32 CFR § 170.14. It identifies the Level 3 requirement as CA.L3-3.12.1e: conduct penetration testing at least annually or when significant security changes are made, using automated scanning tools and ad hoc tests performed by subject-matter experts.
The Level 3 requirement remains in the regulation even though Level 3 assessment designation is currently suspended. Organizations pursuing high-value programs should therefore separate near-term contract obligations from longer-term architecture and readiness planning.
CMMC Level 2 requires all 110 security requirements in NIST SP 800-171 Revision 2, grouped into 14 families. CMMC gives each one a family code, the level and the NIST number, so NIST requirement 3.11.2 becomes RA.L2-3.11.2. Assessors judge each requirement against its assessment objectives in NIST SP 800-171A, 320 objectives in all, and a requirement is MET only when every applicable objective is satisfied.
| Family | Code | Practices | What it covers | Where pentest evidence can help |
|---|---|---|---|---|
| Access Control | AC | 22 | Who and what can reach CUI; remote, wireless and mobile access; CUI on public systems | Tests least privilege, session controls and remote access paths |
| Awareness and Training | AT | 3 | Security awareness, role-based training, insider-threat awareness | Little; an authorized phishing exercise can inform training, but training records are the evidence |
| Audit and Accountability | AU | 9 | Creating, protecting, reviewing and correlating audit logs | Shows whether test activity was logged and noticed |
| Configuration Management | CM | 9 | Baselines, inventories, change control, least functionality, software restrictions | Finds unneeded services, weak settings and unapproved software |
| Identification and Authentication | IA | 11 | Identifying and authenticating users and devices, MFA, password protection | Tests MFA coverage, credential storage and replay resistance |
| Incident Response | IR | 3 | Incident handling, reporting, testing the response capability | A coordinated test can exercise detection and escalation; plans and records stay the evidence |
| Maintenance | MA | 6 | Controlled maintenance, maintenance tools, nonlocal maintenance sessions | Can check nonlocal maintenance paths and their MFA |
| Media Protection | MP | 9 | Marking, storing, sanitizing and transporting media with CUI | Little; mostly process and physical evidence |
| Personnel Security | PS | 2 | Screening people and protecting CUI during personnel actions | None; HR process evidence |
| Physical Protection | PE | 6 | Physical access, visitors, access logs, alternate work sites | Only if physical testing is separately authorized |
| Risk Assessment | RA | 3 | Risk assessments, vulnerability scanning, remediation | Validates scan results and covers custom applications (RA.L2-3.11.2, RA.L2-3.11.3) |
| Security Assessment | CA | 4 | Control assessments, plans of action, monitoring, system security plan | Direct input to CA.L2-3.12.1 through CA.L2-3.12.3 |
| System and Communications Protection | SC | 16 | Boundary protection, segmentation, encryption in transit and at rest, split tunneling | Tests boundaries, segmentation and exposed services |
| System and Information Integrity | SI | 7 | Flaw remediation, malware protection, security alerts, monitoring for attacks | Retests fixes and shows whether monitoring detects attack activity |
| Total | 14 families | 110 | Assessed against 320 NIST SP 800-171A objectives | Supporting evidence only, never a certificate |
Level 1 is much smaller: 15 basic safeguarding requirements from FAR 52.204-21 for systems that handle Federal Contract Information only. Level 3 keeps the full Level 2 set and adds 24 selected requirements from NIST SP 800-172, including the penetration-testing requirement CA.L3-3.12.1e.
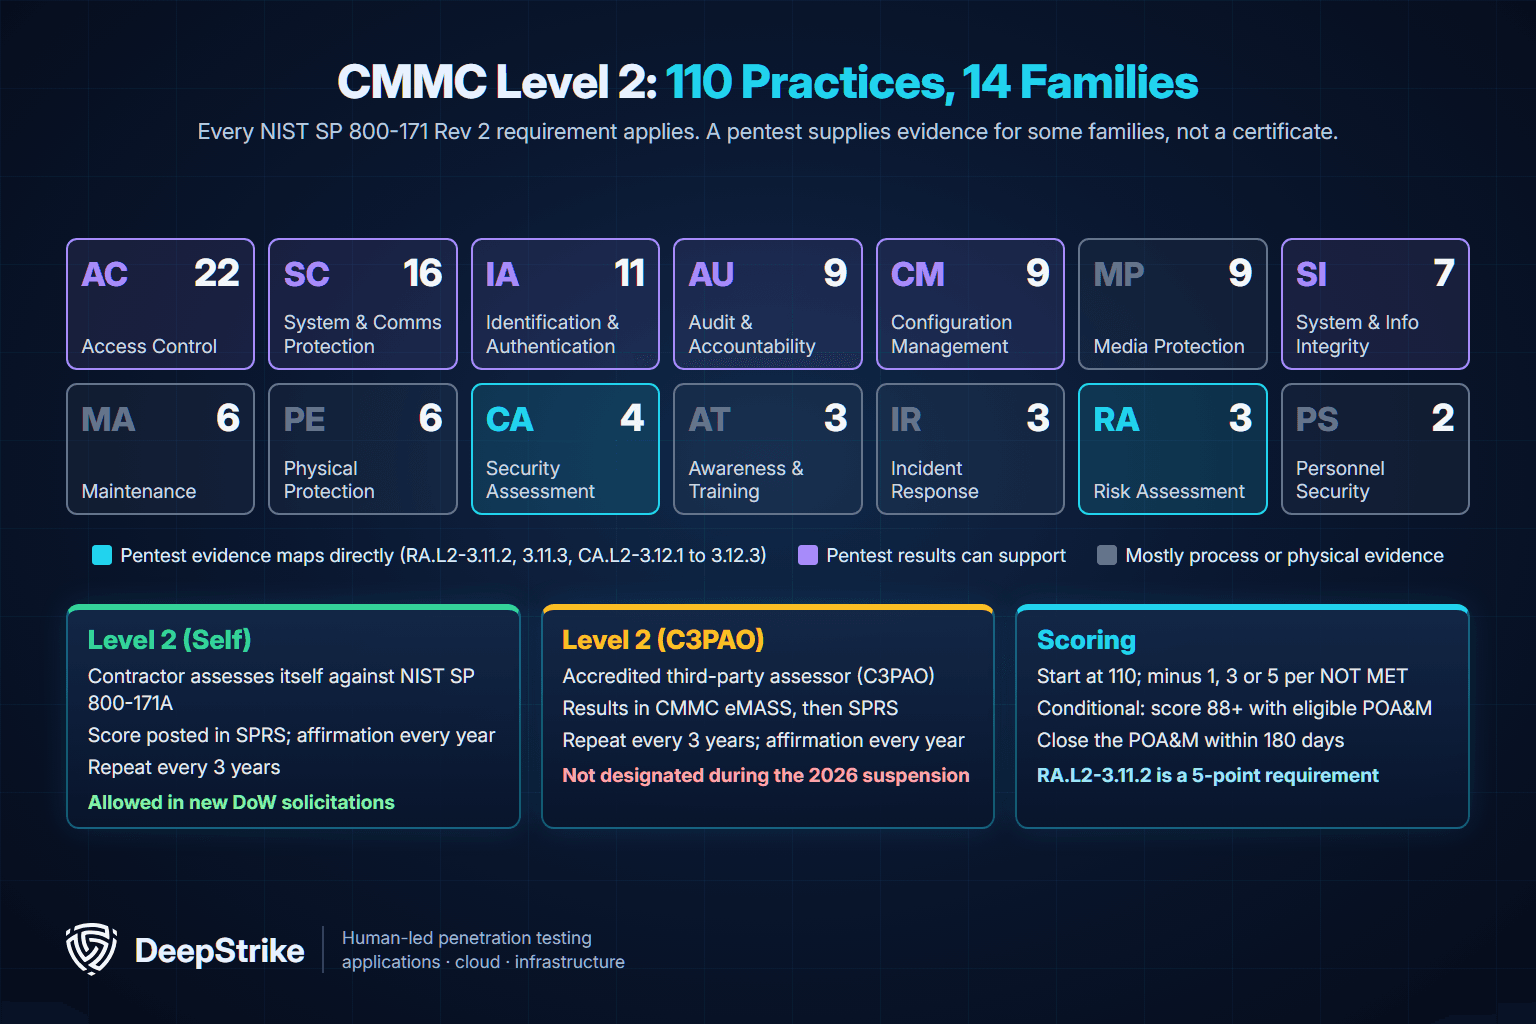
A Level 2 requirement in a contract names an assessment type as well as a level. The rule defines two Level 2 paths, and the current suspension allows only one of them in new DoW solicitations.
| Level 2 (Self) | Level 2 (C3PAO) | |
|---|---|---|
| Who assesses | The contractor itself | An authorized or accredited C3PAO |
| Method | NIST SP 800-171A objectives, scored under 32 CFR § 170.24 | Same |
| Where results go | SPRS | CMMC eMASS, which feeds SPRS |
| How often | Every three years | Every three years |
| Affirmation | At each assessment and every year after | At each assessment and every year after |
| Conditional status | Score of 88 or more with an eligible POA&M, closed within 180 days | Same; a C3PAO performs the closeout assessment |
| DoD verification | DCMA DIBCAC may assess under DFARS 252.204-7020 | Same |
| New DoW solicitations, November 2026 | Allowed | May not be designated during the suspension |
Scoring starts at 110. Each NOT MET requirement subtracts 1, 3 or 5 points under 32 CFR § 170.24. RA.L2-3.11.2, CA.L2-3.12.1 and CA.L2-3.12.3 are 5-point requirements, CA.L2-3.12.2 is worth 3 and RA.L2-3.11.3 is worth 1. Under 32 CFR § 170.21, Conditional status needs a score of at least 88 (0.8 × 110), POA&M items worth no more than 1 point (encryption that is in place but not FIPS-validated is the one 3-point exception), and none of six excluded requirements on the POA&M. One of the six is the system security plan, CA.L2-3.12.4.
The July 2026 suspension is an implementation change, not a cancellation of CMMC or the defense industrial base’s security obligations.
During the suspension:
The Department’s implementation memorandum also makes clear that NIST SP 800-171 Revision 2 and DFARS 252.204-7012 obligations remain. Contractors should verify the actual language in each solicitation, contract, option, and amendment rather than assuming that a general announcement has already changed a particular instrument.
Self-assessment does not mean “no evidence.” Level 1 and Level 2 organizations still need an accurate scope, implemented requirements, defensible assessment results, and the required affirmation. A pentest can expose implementation weaknesses before those weaknesses undermine the organization’s own assessment, but it does not make the self-assessment complete by itself.
CMMC Level 2 contains no blanket instruction to hire a pentest provider. Its explicit technical requirement is vulnerability scanning under RA.L2-3.11.2: scan periodically and when new vulnerabilities affecting the system are identified. The Level 2 Assessment Guide also notes that analyzing custom-developed software may require a penetration tester to test or validate findings when automated scanners are insufficient.
That nuance is documented in the official CMMC Level 2 Assessment Guide. The guide is clarifying assessment guidance rather than a substitute for the regulation, but it is a useful source for understanding possible evidence and assessment methods.
| Level 2 requirement | What CMMC expects | How a pentest may help | What a pentest cannot prove alone |
|---|---|---|---|
| RA.L2-3.11.2 | Periodic and event-driven vulnerability scanning | Validate exploitability and test areas automated tools cannot adequately analyze | That required scanning occurs across the defined frequency and scope |
| RA.L2-3.11.3 | Remediate vulnerabilities according to risk assessments | Establish impact, prioritize fixes, and verify selected remediation | That the organization’s full remediation process operates consistently |
| CA.L2-3.12.1 | Periodically assess security controls for effectiveness | Exercise selected technical controls under realistic attack paths | Effectiveness of all 110 requirements and their assessment objectives |
| CA.L2-3.12.2 | Develop and implement plans to correct deficiencies | Supply actionable findings, owners, and validation data | Eligibility of an item for a CMMC assessment POA&M |
| CA.L2-3.12.3 | Monitor controls on an ongoing basis | Add periodic human validation to the monitoring program | Continuous or program-wide monitoring by itself |
| SI.L2-3.14.1 | Identify, report, and correct system flaws promptly | Retest selected fixes and identify exploitable combinations | That every flaw is tracked and corrected within the organization’s process |
A practical way to express the value is:
Useful Level 2 evidence = correct scope + authorized testing + attributable evidence + owned remediation + retest
Even when all five elements are present, the result is supporting evidence, not a CMMC certificate, a guaranteed score, or a substitute for evaluating every applicable objective.
For teams that need the testing work to be repeatable across remediation cycles, a structured penetration testing as a service program can help. The organization should still document how that service fits its vulnerability-management, control-assessment, and evidence-retention processes.
The table above gives the short version. This section goes one level deeper, objective by objective, because that is how an assessor reads the evidence.
The requirement reads: scan for vulnerabilities in organizational systems and applications periodically and when new vulnerabilities affecting those systems and applications are identified. NIST SP 800-171A splits it into five objectives, and all five must be met:
[a] The scanning frequency for systems and applications is defined.[b] Systems are scanned at that frequency.[c] Applications are scanned at that frequency.[d] Systems are scanned when new vulnerabilities are identified.[e] Applications are scanned when new vulnerabilities are identified.It is a 5-point requirement, so it cannot go on a Level 2 POA&M. The CMMC Level 2 Assessment Guide expects every in-scope asset to be scanned, including laptops that rarely connect to the network. It also says custom-developed software may need a penetration tester to test and validate findings, because automated scanners are less thorough on custom applications.
Where a pentest helps with RA.L2-3.11.2:
A pentest does not satisfy RA.L2-3.11.2 on its own. A yearly test is not scanning at a defined frequency, and it is not event-driven scanning when a new CVE affects your systems. Keep the scan schedule, the scan reports and the records of out-of-cycle scans as the primary evidence.
The Security Assessment family has four requirements. A pentest feeds the first three directly and depends on the fourth.
One rule in § 170.24 is easy to miss. A temporary deficiency that is addressed in an operational plan of action, with reviews and progress toward the fix, is assessed as MET. A requirement that was never implemented is NOT MET whether or not it appears on a POA&M. So a newly found flaw in a working control, tracked properly, is handled very differently from a control that does not exist. Agree with your assessor before the assessment how open pentest findings will be treated.
Map each artifact to the requirement it supports:
Under § 170.24, evidence must be in final form. Working papers, drafts and unapproved policies do not count, so hand over the final, signed report rather than a draft.
| Activity | Primary question | Typical methods | Typical output | CMMC role |
|---|---|---|---|---|
| Vulnerability scanning | What known weaknesses may be present? | Automated authenticated or unauthenticated checks | Potential vulnerabilities, missing patches, and configuration findings | Explicit Level 2 requirement when performed periodically and when relevant new vulnerabilities emerge |
| Penetration testing | Which weaknesses and attack paths can an authorized human tester validate? | Manual analysis, exploitation, chaining, and targeted tooling | Validated findings, impact evidence, attack paths, and remediation guidance | Explicit at Level 3; optional supporting activity at Levels 1 and 2 |
| CMMC assessment | Are all applicable practices implemented with sufficient evidence? | Examine, interview, and test against assessment objectives | MET, NOT MET, or NOT APPLICABLE determinations and an assessment result | The formal compliance activity; not replaced by scanning or pentesting |
Running a scanner and calling the output a pentest weakens both security and evidence quality. Conversely, asking a pentester to “test all of CMMC” creates an undefined engagement: many CMMC objectives concern governance, policy, training, physical protection, and repeatable processes that cannot be established through offensive testing.
The CMMC assessment scope and the pentest scope should inform each other, but they are not automatically identical. Start with the system security plan, asset inventory, network and data-flow diagrams, external service-provider responsibilities, and the paths through which CUI is stored, processed, or transmitted.
The regulation’s CMMC scoping requirements distinguish CUI assets, security protection assets, contractor risk-managed assets, specialized assets, and out-of-scope assets. Those categories affect assessment treatment. The pentest should prioritize CUI assets and security protection assets while also considering credible paths from other reachable systems into the CUI environment.
A useful scoping workshop should answer these questions:
DeepStrike’s penetration-testing scope guide explains how to turn objectives, boundaries, exclusions, and rules of engagement into a testable statement of work. For a CMMC-focused engagement, that scope should also map each major test path to the relevant system boundary and asset owner.
The test type should follow the attack surface. That may include internal or external network testing, identity and Active Directory paths, web applications and APIs, cloud control planes, remote access, segmentation, or a focused review of custom-developed software. It does not follow that every organization needs every test type.
If CUI-facing applications are central to the boundary, a web application penetration test may be more useful than a broad external network test.
If the enclave relies on cloud identity, storage, or managed services, a separately authorized cloud penetration test may be necessary because provider policies and shared-responsibility boundaries can limit techniques.
Only CMMC Level 3 sets a pentest cadence: at least annually and when significant security changes are made. CMMC does not specify a frequency for Levels 1 and 2 because they do not explicitly require penetration testing, so those organizations should set a risk-based cadence using their threat model, contract language, architecture, change rate, and findings.
For CMMC Level 3, the model supplies the cadence: at least annually and when significant security changes are made.
For Levels 1 and 2, CMMC does not specify a pentest cadence because it does not explicitly require the activity. The organization should set a risk-based frequency based on its threat model, contract language, customer commitments, architecture, change rate, and findings. An annual test may be a reasonable program choice, but it should not be presented as a universal Level 2 rule.
Consider an additional test after material changes such as:
Between larger tests, focused validation can reduce the time that important findings remain unresolved. A continuous penetration-testing service may fit fast-changing environments, but it still needs a defined scope, authorization, triage process, and evidence-retention plan.
A CMMC-focused pentest report should be useful to engineers, control owners, executives and, when appropriate, the assessment team. At minimum, retain:
The mapping should say “supports evidence for” rather than “proves compliance with.” An assessor may need only the portions relevant to a particular objective, while sensitive exploit detail may require controlled handling. Agree on evidence access and redaction before testing starts.
A clear penetration-testing contract should define authorization, confidentiality, data retention, third-party approvals, deliverables, and retesting. For CUI environments, those terms are part of risk management, not administrative boilerplate.
Not automatically.
CA.L2-3.12.2 expects an organization to develop and implement plans of action designed to correct deficiencies and reduce or eliminate vulnerabilities. A contractor can use an operational remediation plan to manage pentest findings under that practice.
A CMMC assessment POA&M is a separate mechanism governed by 32 CFR § 170.21. It applies to eligible NOT MET assessment requirements, is subject to scoring and eligibility constraints, and must be closed within the applicable period. Level 1 does not allow an assessment POA&M; Level 2 permits only a limited one under the rule.
Therefore, do not automatically label every pentest issue a “CMMC POA&M item.” First determine whether the finding indicates that a specific assessment objective is NOT MET. Then document and handle it through the appropriate operational or assessment process.
Most defense contractors meet CMMC in one of three audit settings: their own Level 2 self-assessment, a C3PAO certification assessment, or a DCMA DIBCAC assessment, which DoD can run under DFARS 252.204-7020 even for a contractor that self-assessed. All three use the NIST SP 800-171A objectives and the same three methods: examine documents and records, interview people, and test the controls.
A pentest is not an audit, but it is a useful rehearsal for the test part. Before any of the three, check that:
For a broader comparison of audits and tests, see our IT security audit guide and the overview of penetration testing for compliance.
Choose the provider for its ability to test the actual attack surface safely and produce defensible evidence, not because it promises to “make you CMMC compliant.” A pentest company does not award a CMMC status unless it is separately authorized for the relevant assessment role, and those roles should not be casually conflated.
Evaluate:
DeepStrike provides penetration-testing services, so this guide has a commercial connection to the subject. Its requirements analysis is based on the cited official sources. Buying any DeepStrike service does not create or guarantee CMMC status.
No. CMMC Level 2 explicitly requires periodic vulnerability scanning and scanning when new vulnerabilities affecting the system are identified, but it does not contain a blanket penetration-testing requirement. A pentest may support selected assessment objectives, particularly where manual validation is valuable, but it does not replace the Level 2 assessment.
No. Phase I self-assessments remain. During the suspension, new solicitations and contracts may designate Level 1 Self or Level 2 Self, but not Level 2 C3PAO or Level 3 DIBCAC. Other applicable safeguarding and DFARS obligations also remain.
Yes. CA.L3-3.12.1e remains in the CMMC model and requires penetration testing at least annually and after significant security changes. What changed is that Level 3 DIBCAC assessment designation is currently suspended during the Phase II pause.
No. Scanning is broad and repeatable, while a pentest uses authorized human analysis to validate exploitability and combine weaknesses into attack paths. Level 2 explicitly requires vulnerability scanning; adding a pentest does not remove that obligation.
CMMC does not prescribe a Level 2 pentest schedule. Set a defensible cadence based on risk, contractual commitments, architectural change, and exposure. Annual testing and testing after material changes may be reasonable choices, but they are not universal Level 2 requirements.
No CMMC rule says a C3PAO must provide an organization’s security pentest. A C3PAO performs authorized CMMC certification assessments when that assessment designation applies. Select a pentest provider based on authorization, technical fit, evidence quality, data handling, and contractual constraints.
Not necessarily. The assessment team needs adequate evidence for the objectives being evaluated, but the exact artifacts and access method should be coordinated with the assessor. Sensitive exploit details should be controlled, and selective evidence must still be sufficient and attributable.
Level 2 requires all 110 security requirements in NIST SP 800-171 Revision 2, across 14 families such as Access Control (22), System and Communications Protection (16) and Identification and Authentication (11). Contractors are assessed against the 320 objectives in NIST SP 800-171A, scored under 32 CFR § 170.24, and must affirm compliance every year. The assessment repeats every three years, either as a self-assessment or by a C3PAO.
It has no start date right now. Phase 2 was scheduled for November 10, 2026, but the Department of War suspended it on July 13, 2026 together with later milestones. As of November 4, 2026, no new date had been published. Phase 1, which began on November 10, 2025, remains in effect.
Final status requires every requirement to be MET, a score of 110. A score of 88 or higher can give Conditional status if the remaining gaps are eligible for a POA&M under 32 CFR § 170.21. Those gaps must be closed and confirmed within 180 days, or the Conditional status expires.
CMMC penetration testing is not a universal checklist item. It is an explicit Level 3 model requirement and an optional but potentially valuable security-validation activity at Level 2. In 2026, contractors also need to account for the Phase II suspension without assuming that self-assessment eliminates evidence or security obligations.
Need help defining a CUI-focused scope, validating exploitable attack paths, and producing remediation-ready evidence? DeepStrike can design and execute an authorized penetration test around your actual environment. Your contracting officer, legal counsel, and assessment team should confirm how the resulting evidence fits your specific obligations. Talk to our team about a CMMC-focused test.
This article is general technical information, not legal, procurement, or certification advice. Current official guidance and the terms of each solicitation and contract control.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
