December 25, 2025
Updated: November 3, 2026
A practical guide to NetFlow, how it works, and why it matters

Mohammed Khalil
What is NetFlow? It is a Cisco-created network telemetry protocol that summarizes IP traffic into flow records and exports them to a collector for analysis. A flow is a one-way stream of packets sharing the same key fields, typically the 5-tuple (source and destination IP, source and destination port, protocol). Instead of storing every packet, a NetFlow-enabled router, switch or firewall records who talked to whom, when and how much data moved. NetFlow v9 is documented in the informational RFC 3954; its standardized successor, IPFIX, is defined in RFC 7011.
Today flow telemetry is fundamental in both enterprise networks and cloud environments. On premises, it runs on core network gear to monitor bandwidth and security. In the cloud, the major providers offer flow logs that serve the same purpose: AWS VPC Flow Logs, Azure virtual network flow logs and Google Cloud VPC Flow Logs all capture metadata about VM-to-VM and internet traffic. That wide reach makes NetFlow-style telemetry a key source of visibility for performance tuning, anomaly detection, compliance evidence and incident response.
NetFlow uses three components: an exporter, one or more collectors and an analyzer.
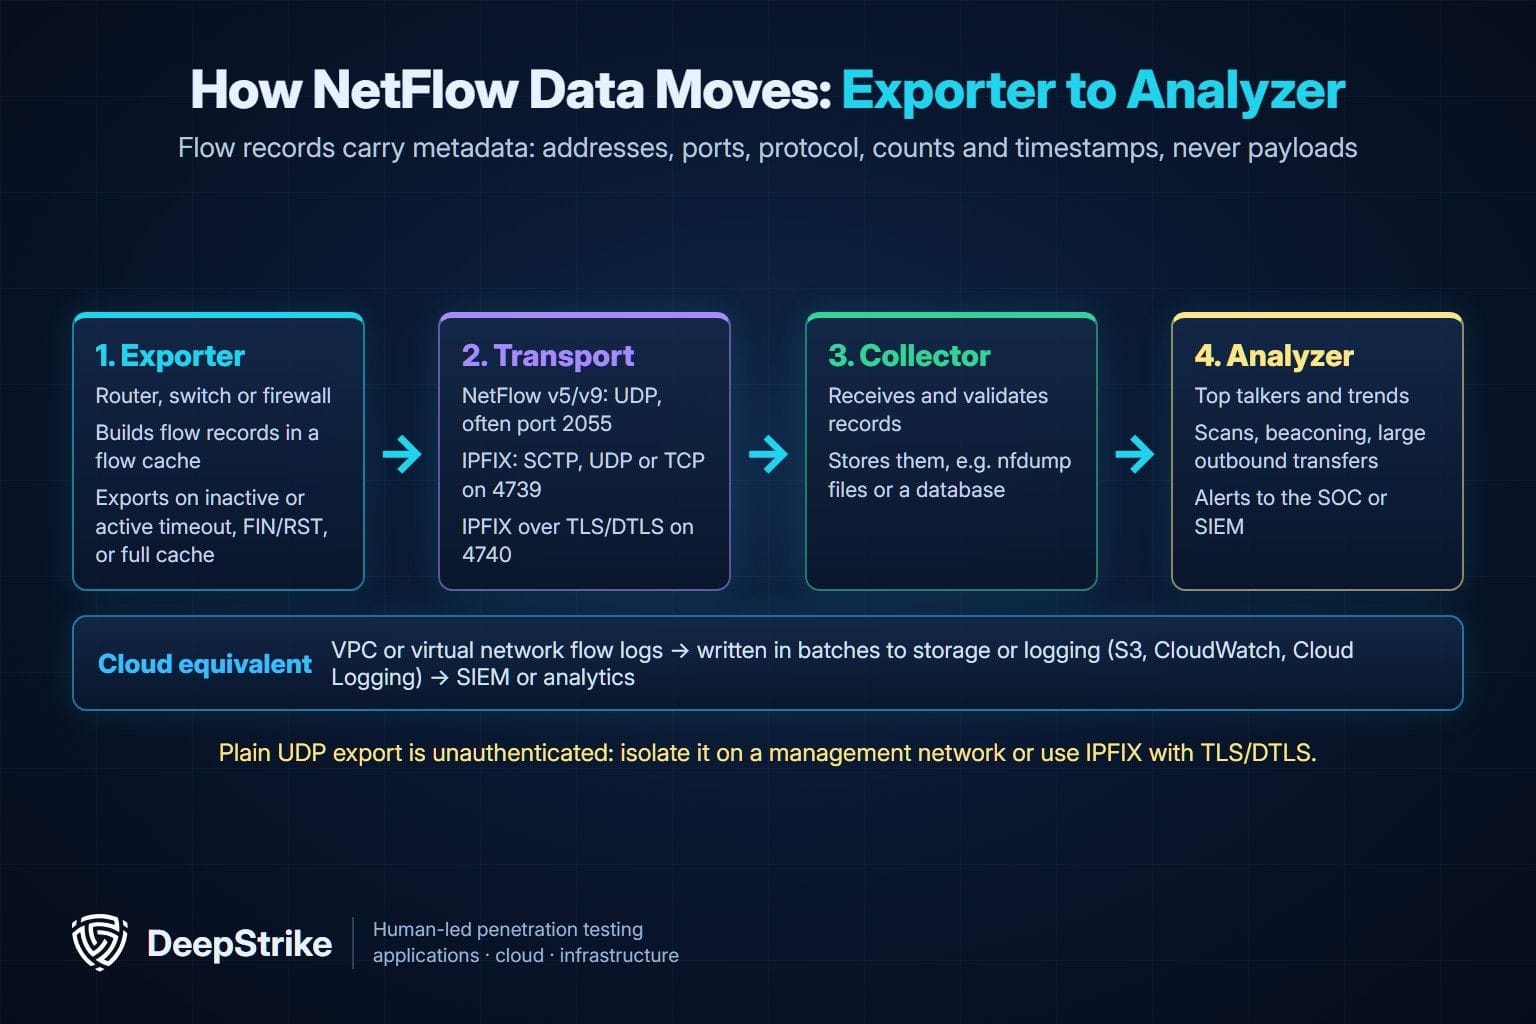
The exporter is usually a router, switch or firewall that observes traffic on its interfaces. As packets pass through, the device builds a flow record for each distinct traffic stream. Traditional Cisco NetFlow identifies a flow by seven key fields: source IP address, destination IP address, source port, destination port, IP protocol, Type of Service (ToS) and input interface. The record also carries non-key fields such as byte count, packet count, TCP flags, timestamps and, on many devices, BGP autonomous system numbers.
When a packet arrives, the exporter looks up its key fields in a flow cache. If a matching entry exists, the exporter increments that entry's packet and byte counters. If not, it creates a new entry. A flow is exported when one of these happens:
RFC 3954 says these timeouts should be configurable and sets no default values, so defaults vary by vendor and platform. Check your device documentation before comparing flow counts across vendors.
The exporter packages completed records and sends them to one or more collectors. NetFlow v5 and v9 export over UDP, and port 2055 is a common collector convention (9995 and 9996 also appear in vendor defaults). IPFIX is more flexible. RFC 7011 makes SCTP mandatory for compliant implementations and allows UDP and TCP, with IANA port 4739 for plain export and 4740 for secured export. For protection, IPFIX specifies TLS over TCP and DTLS over UDP or SCTP, which provide confidentiality, integrity and mutual authentication of exporters and collectors. Plain UDP export is unauthenticated, so many teams also isolate flow traffic on a management VLAN and restrict which hosts may send to the collector.
NetFlow v9 and IPFIX are template-based: the exporter first sends a template that describes which fields follow, then sends data records in that layout. NetFlow v5 uses a fixed record layout, which is why it cannot carry IPv6 addresses.
The collector, usually software on a server or an appliance, receives flow packets, validates them and stores them. The analyzer reads the stored records and produces human-readable output: reports, charts and alerts. Analysts use it to view top talkers and bandwidth trends or to surface unusual spikes. The result is a scalable view of who talked to whom, when, for how long and how much, without capturing packet contents.
Inspecting every packet on a fast link can overload the device and the collector, so many platforms support packet sampling. With 1-in-N sampling, the exporter meters only one packet out of every N. Most exporters report the sampled counts together with the sampling rate, and the collector or analyst multiplies by N to estimate totals; some platforms export counts already scaled, so check which your device sends.
Here is an illustrative calculation. A 10 Gbps internet link is sampled at 1:1000. Over five minutes the collector records 4,000 sampled packets from one internal host to an unfamiliar external address, with 5.6 MB of sampled bytes. Scaled estimates are about 4,000,000 packets and about 5.6 GB transferred. That estimate is good enough to flag possible exfiltration for investigation. The same sampling rate can miss a short session entirely: a 30-packet beacon has roughly a 3% chance of being seen at all (30 ÷ 1000). Sampling is reliable for volume trends and large transfers, and unreliable for small, low-and-slow activity.
| Version | Record format | IPv6 support | Transport | Standard status | Typical collector port |
|---|---|---|---|---|---|
| NetFlow v5 | Fixed layout, seven key fields | No | UDP | Cisco proprietary, undocumented by IETF | 2055 (convention) |
| NetFlow v9 | Template-based | Yes | UDP (transport independent by design) | Informational RFC 3954 (2004) | 2055 (convention) |
| IPFIX ("NetFlow v10") | Template-based, variable-length fields, enterprise elements | Yes | SCTP (mandatory), UDP, TCP; TLS/DTLS for security | IETF Standards Track, RFC 7011 (2013) | 4739; 4740 for TLS/DTLS |
| sFlow | Packet sampling plus interface counters | Yes | UDP | Industry specification by InMon (sflow.org), not an IETF standard | 6343 (convention) |
In practice v9 and IPFIX are close relatives, and many devices and vendors use the terms loosely. If you are choosing a format for a new deployment, IPFIX gives the widest field support and the only standardized security mechanism.
Each telemetry source answers a different question. The table below summarizes what flow data can and cannot tell you compared with the alternatives.
| Question you need answered | NetFlow / IPFIX | sFlow | SNMP | Packet capture (PCAP) |
|---|---|---|---|---|
| Who talked to whom, on which ports? | Yes, per flow | Yes, statistically | No | Yes |
| How much data moved per conversation? | Yes (exact or sampled) | Estimated from samples | Interface totals only | Yes, exact |
| Is the device or link healthy (CPU, errors, utilization)? | No | Interface counters | Yes | No |
| What was inside the traffic (files, commands, URLs)? | No | Only sampled header bytes | No | Yes, if not encrypted |
| Storage cost for months of history | Moderate | Low | Very low | Very high |
| Best use | Long-term traffic visibility, security analytics, forensics | Very high-speed switching fabrics | Device health and capacity alarms | Deep forensic analysis of specific traffic |
SNMP and NetFlow are commonly deployed together: SNMP tells you a link is congested, and NetFlow tells you which conversations are congesting it. Packet capture complements both by giving full detail for a narrow window when an investigation needs payload evidence.
NetFlow supports many practical scenarios in both network operations and security:
These examples show that NetFlow and its cloud equivalents support both daily operations and advanced security work, from bandwidth monitoring to hunting stealthy intruders.
All three major cloud providers offer flow logging that is conceptually equivalent to NetFlow:
Unlike on-premises NetFlow, which streams records over the network, cloud flow logs are usually written in batches to storage or a logging service. The content is similar: source and destination IP, ports, protocol, packet and byte counts, timestamps and, on most platforms, an accept or reject action. Note that cloud flow logs are often sampled or aggregated over an interval, so treat them as visibility data, not as a complete packet ledger. For a broader view of testing cloud network controls, see DeepStrike's cloud penetration testing services.
NetFlow's value comes from the visibility it provides into the traffic layer. By summarizing each conversation rather than every packet, it offers a comprehensive yet scalable view of IP communication.
NetFlow is passive telemetry, not an offensive technique. The real risk is in its blind spots and in how attackers try to avoid it:
Knowing these limits helps defenders tune flow monitoring and close the gaps with other controls.
To get value from NetFlow, organizations must collect and monitor flow data deliberately:
Flow monitoring is only as good as the detections built on it. DeepStrike's Red Teaming Services generate realistic attacker traffic across your network, showing what your flow telemetry catches and what it misses.
Because NetFlow is a monitoring technology, the goal is reliable visibility and a clear process for acting on it:
NetFlow belongs to a family of traffic-monitoring technologies:
Together with sFlow, SNMP and packet capture (compared in the table above), these technologies form a toolkit for network traffic analysis. Knowing when to use flows, packet capture or other logs is key to comprehensive visibility.
A NetFlow record includes the fields that identify the conversation (source IP, destination IP, source port, destination port and protocol) plus metrics such as packet count, byte count and flow start and end times. It often adds fields such as input and output interface, Type of Service, TCP flags and autonomous system numbers. NetFlow v5 uses seven fixed key fields and exports counters and timestamps with them.
Packet capture (PCAP) records every packet's full header and payload, which gives maximum detail but requires heavy storage and processing. NetFlow records only summary metadata for each flow, which greatly reduces data size and makes it practical on large networks. NetFlow cannot show payload or application-level details, so it cannot reveal the exact files transferred or the user behind the traffic.
NetFlow v5 is an older, fixed-format version built on seven key fields and no IPv6 support. NetFlow v9 introduced template-based export, which allows flexible field selection and supports IPv6 and MPLS; it is documented in the informational RFC 3954. IPFIX is the IETF standard derived from v9 (RFC 7011). It keeps templates, adds variable-length and enterprise-specific fields and defines SCTP, UDP and TCP transport with TLS or DTLS security.
Yes, through each provider's flow logs. AWS offers VPC Flow Logs, Azure offers virtual network flow logs (NSG flow logs retire on September 30, 2027) and Google Cloud offers VPC Flow Logs. They capture source and destination IP, ports, protocol, packet and byte counts, timestamps and usually an accept or reject action. Unlike on-premises NetFlow, which streams records over UDP or IPFIX transport, cloud flow logs are written in batches to storage or logging services such as S3, CloudWatch or Cloud Logging.
NetFlow logs provide a historical record of network connections. During an incident, defenders can query them for all communications involving a suspicious IP or compromised host, which helps map lateral movement and data exfiltration. If malware is found on a server, analysts can list every external IP that server contacted around the time of compromise. Months of retained flow logs are valuable for retrospective forensics.
An exporter is a network device, typically a router, switch or firewall, that monitors traffic on its interfaces, builds flow records and sends them out. A collector is usually a server application that receives those records, processes them and stores them in a database or flat files. The exporter pushes data on a timer or when flows end, and an analyzer reads the collector's storage to generate reports and alerts.
The main limits are data volume and lack of content. High-throughput networks can produce millions of flows per minute, so storage and analysis need capacity, and sampling to reduce load can miss small events. NetFlow does not capture payloads, so content-based detection such as a malware signature match is impossible. It logs IP addresses, so NAT and VPN concentrators can obscure the true source. It also records no user identity, so you need DHCP, DNS or identity logs for full context.
NetFlow is a foundational network telemetry protocol that summarizes who is talking to whom across a network. Exporters on routers and switches send flow records to collectors, giving continuous visibility into traffic patterns and volumes. That visibility supports performance monitoring and security alike: finding bottlenecks, checking segmentation and detecting suspicious behavior. Flow data and cloud flow logs come with trade-offs, mainly large volumes, sampling gaps and no payload, so teams combine them with IDS, endpoint and identity logs. For new deployments, IPFIX with TLS or DTLS is the standardized choice, and validating your detections against realistic attacker traffic shows whether your flow monitoring works when it matters.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements for Fortune 500 companies, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
