December 25, 2025
Updated: November 5, 2026
A clear explanation of ARP spoofing, how it works on LANs, real-world risks, and proven mitigation strategies.

Mohammed Khalil
ARP spoofing (also called ARP cache poisoning) is a local-network man-in-the-middle attack in which an attacker sends forged Address Resolution Protocol (ARP) replies so that other devices link the attacker's MAC address to someone else's IP address, usually the default gateway. Traffic meant for that IP then flows through the attacker, who can read, alter or drop it. It works because ARP has no authentication. Strictly, spoofing is the act of sending forged ARP replies; poisoning is the corrupted cache that results. Defenses include Dynamic ARP Inspection, segmentation and encryption.
ARP, defined in RFC 826, resolves IPv4 addresses to link-layer (MAC) addresses on a local subnet. A host that wants to reach an IP address broadcasts a request, the owner replies with its MAC address, and the requester stores that mapping in its ARP cache.
ARP spoofing abuses this process. A malicious host injects fake ARP messages into the subnet to re-map IP addresses to its own MAC address. In plain terms, the attacker tells other devices "I am the router" (or another host), and they start sending traffic through the attacker. This works because ARP has no built-in authentication: any device can reply to an ARP request, and hosts trust the reply. An attacker on the same Ethernet or Wi-Fi segment can therefore trick victims into sending packets to the attacker's machine. This lets the attacker intercept, inspect or alter network traffic, a classic man-in-the-middle attack.
ARP spoofing is still relevant because most enterprise networks still run IPv4, which relies on ARP. IPv6 replaces ARP with the Neighbor Discovery Protocol (NDP). NDP has an optional cryptographic extension, Secure Neighbor Discovery (SEND), but it is rarely deployed, so NDP spoofing is the IPv6 equivalent of this attack. Security teams see ARP spoofing in internal and campus networks where an insider or a compromised device gains local access. A malware-infected workstation or a rogue Wi-Fi client, for example, can poison ARP caches in its subnet to spy on other machines.
MITRE ATT&CK tracks the technique as Adversary-in-the-Middle: ARP Cache Poisoning (T1557.002) and lists real-world use: the Cleaver group has used custom tools to facilitate ARP cache poisoning, and LuminousMoth has used ARP spoofing to redirect a compromised machine to an attacker-controlled website.
Dynamic ARP Inspection can pass a configuration audit and still leave gaps in production, for example when it covers only some VLANs or trusts too many ports. Our Red Teaming Services test whether your Layer 2 controls actually hold.
Normally, when Host A wants to send a packet to IP X, it broadcasts "Who has IP X?" on the LAN. The true owner replies "IP X is at MAC M," and Host A caches that answer. The weakness is that any host can send a forged reply, and many operating systems accept it, even when they never sent a request. An attacker sends fake ARP replies that bind the attacker's MAC address to another IP, often the gateway's. Victims update their ARP caches and send traffic to the attacker's MAC instead of the legitimate device.
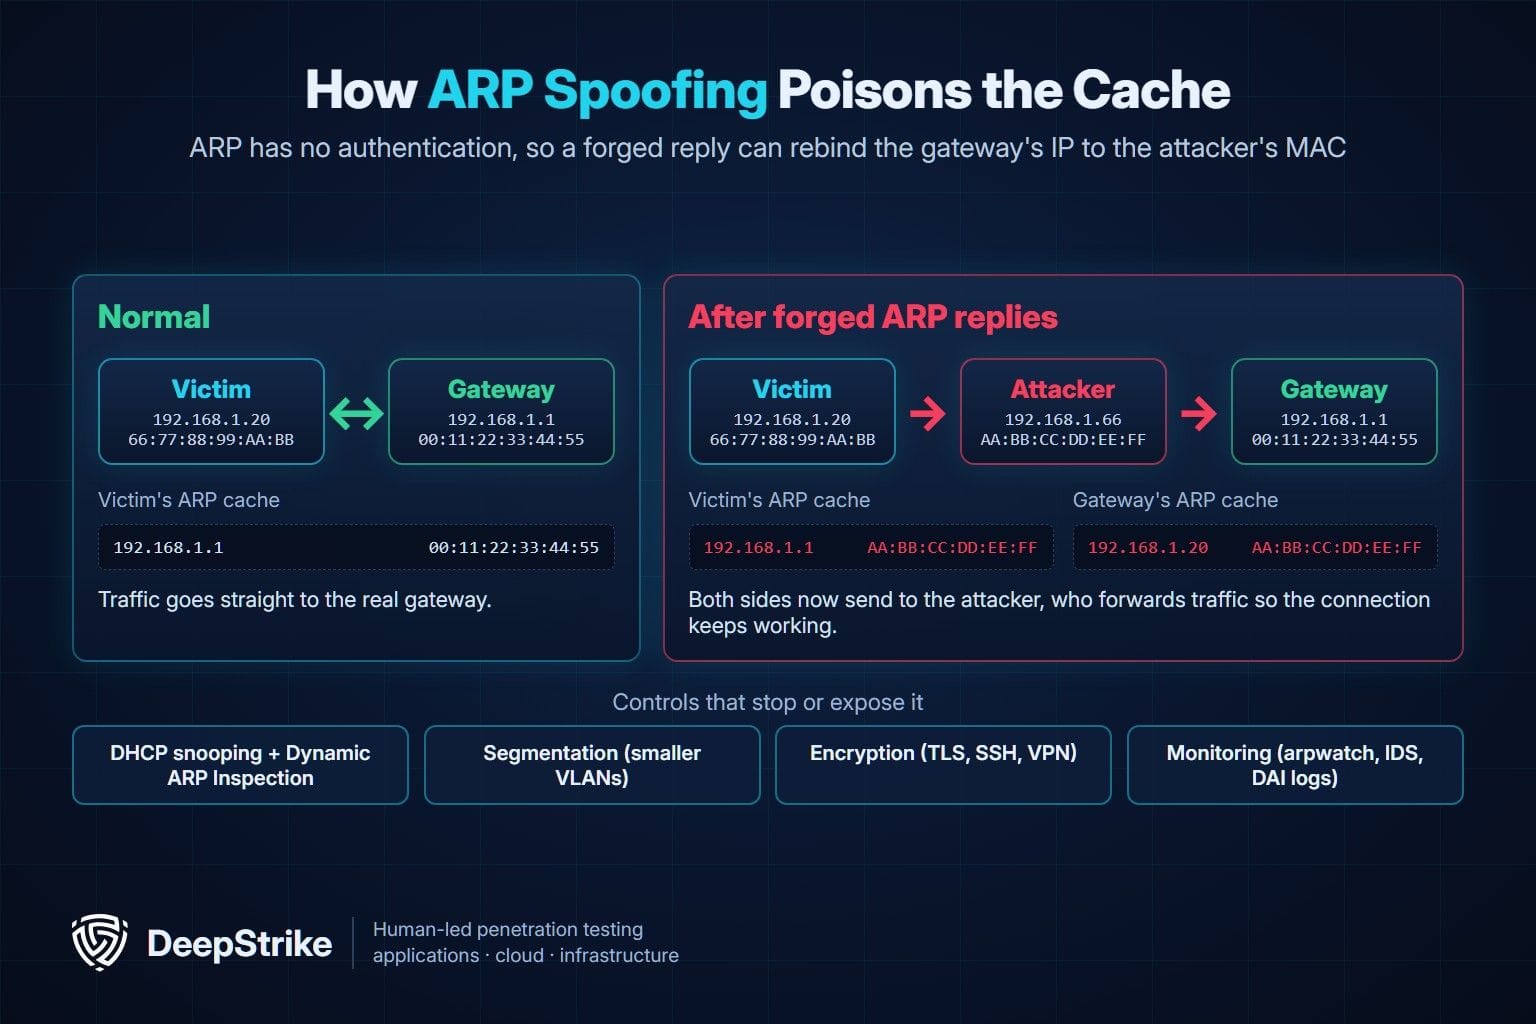
Many hosts accept unsolicited ARP replies at any time, and the protocol itself offers no guardrail. During authorized penetration tests, tools such as Bettercap, Ettercap or arpspoof automate step 2 and can link many IPs to the tester's MAC at once. The attacker effectively pretends to be both ends of the conversation and sits in the middle of it.
ARP spoofing is most commonly observed inside networks:
Legitimate uses: ARP-related techniques are also used defensively. Administrators set static ARP entries for critical devices, hard-coding the router's IP-to-MAC mapping to prevent poisoning. Engineers run ARP monitoring tools such as arpwatch to audit network changes. In penetration testing, ARP spoofing is simulated with permission to evaluate an organization's network defenses. ARP itself is fundamental to every IPv4 Ethernet network; ARP spoofing is the abuse of it to gain visibility into LAN traffic.
ARP spoofing can undermine a network's confidentiality and integrity. When it succeeds, attackers bypass perimeter defenses by working inside the LAN. They can silently capture sensitive corporate or personal data and inject harmful traffic. The impacts include stolen passwords and documents, malware delivered inside legitimate sessions, and denial of service when traffic is dropped or ARP traffic floods the segment.
The business consequences follow: a breach that starts with ARP poisoning can lead to regulatory penalties, loss of customer trust and expensive incident response. Many internal services still use unencrypted protocols, so an attacker who spoofs a gateway can capture everything from database queries to login attempts. Even when data is encrypted, ARP spoofing can disrupt sessions or steer devices toward rogue DNS servers. Because the attack is simple and the tools are freely available, any flat, poorly monitored LAN is at risk.
Attackers use ARP spoofing mainly as an internal technique. After gaining a foothold, for example through phishing or a compromised host, an adversary can use ARP spoofing during lateral movement to sniff traffic from other machines on the LAN and collect credentials. Tools are widely available: arpspoof (part of the dsniff suite), Ettercap and Bettercap all automate the attack. That low barrier makes ARP poisoning a common choice during internal reconnaissance or data collection.
The technique is effective because ARP has no challenge-response step, so hosts trust updates. Attackers can send unsolicited or gratuitous ARPs continuously to keep caches poisoned. Detecting a malicious ARP packet on its own is hard because ARP traffic is frequent and one spoofed packet looks like a routine update. An attacker can also throttle their packets to stay below rate-based alarms.
ARP spoofing is often paired with MAC address spoofing (changing the attacker's NIC MAC to impersonate another device) and can complement DNS or DHCP spoofing. Once active, it can be hard to spot without monitoring, because switches typically do not log ARP packets by default and many hosts do not alert when an ARP entry changes. This is why security teams emphasize proactive controls (see below) over reactive fixes. A related local-network attack is DHCP starvation, which exhausts a DHCP server's pool of available addresses.
Detecting ARP spoofing means looking for inconsistent ARP mappings or unusual ARP traffic. Key approaches:
In practice, defenders look for ARP irregularities across endpoints and the network: multiple IP addresses resolving to a single MAC, unexpected gateway MAC changes and unusual volumes of gratuitous ARPs. A combination of periodic ARP cache snapshots, arpwatch or IDS alerts, and switch DAI and DHCP snooping logs works best. Blind spots include unmonitored segments and devices that do not report. Legitimate events such as DHCP lease changes or gateway failover can be noisy, so organizations tune thresholds and keep known-good baselines, such as expected gateway MAC addresses.
Preventing ARP spoofing relies on network design and host controls together:
| Control | What it stops | Where it commonly fails |
|---|---|---|
| Dynamic ARP Inspection | Forged ARP replies that do not match DHCP snooping bindings | Enabled on some VLANs only; static-IP hosts without ARP ACLs; trunk or uplink ports trusted too broadly |
| DHCP snooping | Rogue DHCP servers and builds the binding table DAI relies on | Binding table incomplete after switch reboots or for statically addressed servers |
| Port security / 802.1X | Unknown devices joining the LAN | MAC-bypass exceptions for printers and IoT; a compromised authorized device is still trusted |
| Segmentation (VLANs, subnets) | Spread of poisoning beyond one broadcast domain | Large flat "user" VLANs; shared management networks |
| Static ARP entries | Poisoning of specific critical mappings | Not maintained when hardware changes; impractical at scale |
| Encryption (TLS, VPN, SSH) | Reading or silently modifying intercepted data | Legacy plaintext protocols; users clicking through certificate warnings |
| Monitoring (arpwatch, IDS, DAI logs) | Undetected, long-running poisoning | Alerts not routed to anyone; noisy baselines that get ignored |
No single measure is perfect, but together these controls make ARP poisoning far less effective and easier to detect, provided someone verifies they are actually enabled and enforced. That verification is where the red team and blue team division of labor matters, because DAI and port security can pass a configuration audit and still leave gaps in production. A network penetration test is the usual way to check.
ARP caching is a normal function in which a host remembers IP-to-MAC mappings. ARP spoofing (cache poisoning) is an attack that inserts false mappings into that cache. They differ in intent and in where the entries come from.
Yes. On Windows, run arp -a (or Get-NetNeighbor in PowerShell) and look for two IP addresses, especially the default gateway, sharing one MAC address. On Linux, use ip neigh. Sysmon does not log ARP cache changes (its Event ID 22 is a DNS query event), so for continuous detection use network-side tools such as arpwatch, an IDS ARP rule like Snort 3's arp_spoof inspector, or Dynamic ARP Inspection logs on your switches.
ARP spoofing requires Layer 2 access to the same segment. In typical public cloud networks such as AWS VPCs or Azure virtual networks, the provider's software-defined network handles address resolution, so customers generally cannot perform ARP spoofing there. On a private Wi-Fi or office LAN it works much as on Ethernet, because the access point bridges clients into the same subnet; WPA2 and WPA3 do not prevent it between authenticated clients. It fails when the network isolates clients (for example, with client isolation or per-host routing). IPv6-only segments face the equivalent NDP spoofing risk instead.
Yes. Widely used tools include Bettercap (actively maintained), Ettercap and arpspoof from the dsniff suite, all of which automate sending forged ARP replies. Older Windows tools such as Cain & Abel also had ARP spoofing modules but are no longer maintained. These tools are intended for authorized testing and auditing but are also misused by attackers.
Enable DHCP snooping and Dynamic ARP Inspection on switches, use static ARP entries for critical devices, segment the network into separate subnets, and enforce port security or 802.1X. Encrypt traffic (VPN, HTTPS, SSH) so intercepted data is unusable even if ARP is poisoned. Monitor with arpwatch, IDS rules and switch logs to detect attacks early.
ARP does not exist in IPv6; Neighbor Discovery replaces it, so the classic IPv4 ARP poisoning attack does not apply to IPv6-only networks. However, NDP is not authenticated by default, and the optional SEND extension is rarely deployed, so attackers can spoof neighbor and router advertisements instead. Protect IPv6 segments with RA Guard and ND inspection.
A gratuitous ARP is an unsolicited ARP announcement a device makes, for example when its IP changes or to detect address conflicts. It is normally legitimate. Attackers abuse gratuitous ARPs by sending fake ones repeatedly to poison other hosts' caches. Gratuitous ARP is not inherently malicious, but it is the mechanism most often used in ARP spoofing; MITRE suggests considering disabling ARP cache updates from gratuitous replies where operationally possible.
ARP spoofing exploits the trust-based design of ARP. It lets an attacker with local access impersonate other devices at Layer 2 and transparently capture or manipulate traffic. Because ARP lacks authentication, any IPv4 LAN is potentially vulnerable without proper controls. Defenders have strong options: DHCP snooping and DAI, port security and 802.1X, segmentation, static ARP for key machines and encryption, backed by monitoring. The practical next step is to confirm that these controls are enabled on every relevant VLAN and actually block a spoofing attempt, ideally through an authorized test, so a covert foothold cannot turn into a full compromise.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
