November 10, 2025
Updated: November 6, 2026
How threat intelligence, SOC and IR teams evaluate dark web search engines: use cases, coverage, filtering policy, status, risk and governance.

Mohammed Khalil
Dark web search engines, also called onion or Tor search engines, are specialized indexes of sites on Tor and similar anonymity networks that Google does not cover. This guide compares nine of them for authorized security work: threat intelligence, exposure monitoring, brand and credential monitoring, and incident response. It covers what a security team would use each one for, its coverage, filtering policy, status and risk. It is not a browsing guide, and it gives no addresses or access steps.
Security teams care about these indexes because the dark web remains a hub of criminal activity, with billions of stolen credentials circulating in underground forums: Flashpoint counted 3.3 billion compromised credentials and cloud tokens from more than 11.1 million infostealer-infected machines in 2025 alone. Tor Metrics estimates about 3 million people connect to Tor directly each day (July to October 2026 median), plus roughly 200,000 more through bridges. Those users include journalists and privacy-minded people as well as criminals, so the network itself says little; what matters to a defender is whether your organization’s data or name appears there.
Why this matters: UK cybersecurity teams now monitor the dark web to catch leaked data and threats before they hit. For example, finding employee passwords or customer records on a dark web site can tip off a company to a breach. A search engine can help answer a specific question about that exposure, but a result is only a lead: it can be stale, fake or dangerous to open. That is why this guide treats these tools as controlled research instruments with an owner, a scope and stop rules.
This article explains what dark web search engines are, why security teams use them in 2026, and how nine well-known engines compare on coverage, filtering policy, status and risk. It then sets out the governance a team needs, a legal notice on illegal content, and how to decide between manual search and a monitoring service. It is written for threat intelligence analysts, SOC and incident response teams, penetration testers, and the people who run brand and credential monitoring.
Dark web search engines are specialized search tools for the hidden internet. They index and catalog .onion websites that regular search engines like Google cannot see. By design, dark web sites aren’t indexed by Google: they live on the Tor network or similar anonymity networks. Think of the dark web as a sealed off library; dark web search engines are the custom catalogs that list some of its books, and each catalog is incomplete.
Unlike Google’s web crawlers that follow links all over the public internet, dark web search engines use Tor based crawlers and sometimes user submissions to discover hidden sites. The process is slower and less comprehensive because many onion sites are transient or not well interlinked. Each dark web search engine has its own approach:
Crucially, dark web search engines vary in filtering policy. On the surface web, Google will blacklist obviously harmful or illegal sites. On the dark web, some engines attempt something similar by filtering out known abuse material and known scam or malware sites. Others index whatever their crawlers reach and apply little or no moderation. For a security team, that policy shapes how much legal and malware risk a query carries and how easily the work can be justified to counsel, so the comparison below states it for each engine.
In 2026, the dark web remains a source of exposure data and early warning signals. Data breaches and cybercrime have fed a thriving underground economy. A few trends explain why security teams look there:
For cybersecurity professionals like penetration testers and threat intel analysts, dark web reconnaissance has become a standard part of the job. During a penetration test or security assessment, U.S. security teams often check dark web sources for leaked passwords, company mentions, or sales of exploits. This information can improve a pentest. For example, if a tester learns through a lawful source that your users’ passwords have leaked, and the rules of engagement explicitly allow it, the team can test whether those passwords still work on your network. It’s a way to simulate how a real attacker might use dark web intel.
This work has to be done carefully and legally. A search engine with a published filtering policy reduces the chance of an analyst landing on illegal material, but it does not make results trustworthy. Every query and every result still sits inside an authorization, an environment and a set of stop rules, which the governance section below covers.
In summary, dark web search matters to security teams because it can answer narrow, defensible questions about exposure. The comparison below shows which engine suits which question.
Below are nine tools that security teams evaluate, or still see cited in older reports, when they scope dark web research. The comparison is based on the engines’ own published policies and on threat intelligence and vendor reports, checked in November 2026. We did not run test searches through these engines for this update, and the order is not a ranking. Two entries are retained for reference because they are no longer available. DeepStrike publishes this guide and offers dark web monitoring as part of a paid plan, which is covered later.
The table shows what a team needs to know before approving each tool. The legal notice further down applies to all of them.
| Search Engine | Security Team Use | Coverage | Filtering Policy | Logging and Privacy | Status and Main Risk |
|---|---|---|---|---|---|
| Ahmia | First-pass brand and domain checks; research that must be documented | Public onion services; smaller index by design | Yes: blocks abuse material through a published blocklist | Open source; no IP addresses or cookies stored, but search terms logged without IPs for research (policy updated Sept 2026) | Active, checked Nov 2026; clones impersonate it and results are not verified |
| DuckDuckGo on Tor | Supporting clearnet lookups such as news and company mentions; not onion discovery | Regular web; no dark web index | Standard web search settings only; no onion filtering because there is no onion index | Strict no log policy; doesn’t store searches | Active; an empty result is not evidence of absence |
| Torch | Wider check on older forum threads and leak announcements when scope allows | Large but self-reported and unverified | None; no moderation or verification | Says it does not track searches; not audited; reports on ads conflict | Reported active (KELA, July 2026); clones are common; illegal or malicious results possible |
| Haystak | Investigations that need historical snapshots or keyword alerts from the paid tier | Claims 1.5 billion pages; unverified | Reports conflict; paid tier adds filter options | No tracking claimed; not audited | Availability inconsistent in 2026 reports; anonymous operators |
| Not Evil | None today; seen in older reports only | Offline | Formerly: community flagging; filtering claims vary by source | Formerly: no ads, no trackers | Offline since 2024 (Cyble, June 2026); treat name-alikes as impersonation |
| DarkSearch | None today; its API model shows how monitoring works | No longer public | Formerly: some community reported content removal | Formerly: no user logs; free API (discontinued) | Access ended January 2022; treat anything using the name as unverified |
| OnionLand | Comparing mentions across Tor, I2P and the regular web | Tor onion and I2P sites plus some regular web content | Partial: blocklists abuse material; otherwise broad, and reviewers report scam listings | Previously published policy allowed logging of IP, browser and clickstream data (policy page unavailable Nov 2026); sponsored ads | Reachable Nov 2026; logging, ads and JavaScript dependence |
| DeepSearch | Targeted keyword checks where precision matters more than volume | Smaller; may miss new sites | Reportedly filters spam and some harmful sites; not a full filter | Open source; transparent crawling | Listed in 2026 roundups; uptime not independently confirmed |
| DarkWebLinks | Spotting when tracked platforms go down, move or relaunch | Curated list, not a search index | Curated; operator says links are verified | Static list; no independent review | Listed as active (KELA, July 2026); look-alike sites; listings include criminal platforms |
As shown, Ahmia stands out for its published filtering and privacy policies, and OnionLand also blocklists abuse material, although its logging and ads weigh against it. Engines like Torch and Haystak offer breadth, which can help corroborate a lead, but they carry more legal and malware risk and need tighter controls. DuckDuckGo isn’t a dark web index at all. Two once-popular engines, Not Evil and DarkSearch, are no longer available as of November 2026. The profiles below set out what each is good for and what to watch.
Ahmia is usually the easiest engine for a security team to justify first, because its policies are public. It filters abuse material from its results: it publishes a blocklist of child sexual abuse sites and removes reported abuse content from its index. Ahmia grew through a 2014 Google Summer of Code project with the Tor Project, and as of November 2026 it is still free, open source and run by its founder, security researcher Juha Nurmi.
Security team use: Ahmia suits first-pass checks on a brand, domain or product name, and its privacy policy (updated September 2026) can go straight into a research approval. It says it stores no IP addresses, uses no cookies and builds no user profiles, although it does log search terms and clicked links, without IPs, for academic research and safety filtering. Queries should therefore stick to public identifiers, not passwords, customer data or incident details. Ahmia also runs a clearnet interface, so an analyst can check whether a company name appears in its index and pass any hits into the approved research process without opening them.
Coverage and limits: Because of its filtering, Ahmia’s index is smaller than those of engines that do not filter, and closed forums won’t appear unless someone submits them. A clean result therefore proves little. Ahmia itself warns about fake man-in-the-middle clones, so an address found elsewhere should not be trusted on its face. Status: active; its clearnet site and policy pages responded when checked in November 2026.
DuckDuckGo is not a dark web search engine, although it is often listed alongside them. It’s the default search box in the Tor Browser and known for its no tracking privacy policy; the Tor Project says it chose DuckDuckGo because it does not log or share personal information. DuckDuckGo is free to use and run by Duck Duck Go, Inc. It also operates an onion service, so queries made that way stay inside the Tor network.
Coverage: DuckDuckGo does not index .onion sites beyond maybe a few that have been linked on the clear web. It mostly returns surface web results, which makes it regular web search over Tor. Its SafeSearch setting applies to those ordinary web results and says nothing about onion content.
Security team use: Inside an approved research environment, it handles supporting lookups such as news about a breach, a product name or a threat actor’s public reporting, without mixing that work with a personal or corporate search account. KELA describes this kind of surface-web research as its main value, paired with a true onion index.
Limitations: Because it does not index the dark web, DuckDuckGo can’t show whether your data is exposed on onion services. An empty result says nothing about exposure, so it should never be recorded as evidence of absence. Results are mostly ordinary web pages, which lowers the risk compared with other entries, but the same authorization and evidence rules apply.
Torch is one of the oldest and largest dark web search engines, and threat intelligence firm KELA still described it as active in July 2026. Its operators are anonymous. It claims a very large index built up over the years, including older forum threads and leak announcements, though the size of that index is self-reported and unverified. Reports on advertising conflict: earlier reviews describe an ad-funded service, while Cyble described it as ad-free in June 2026.
Filtering policy: Torch applies no content filtering and verifies nothing it lists. Its results can include illegal, malicious or scam pages, and any ads should be treated the same way. One click on a bad link could expose an analyst to malware or to illegal material. That makes it a poor fit for unsupervised use and a hard tool to approve without the controls in the governance section.
Security team use: The argument for Torch is coverage. If a filtered index comes up empty and the scope allows a wider check, Torch may return more hits. For instance, a researcher looking for mentions of Acme Corp in older forum threads or leak announcements might use it to corroborate an existing lead. Expect a lot of noise, and treat every hit as unverified until it is confirmed through an approved source.
Status and risk: Torch’s address has changed over the years and phishing clones that copy its interface are widespread, so we do not print a Torch address here. A negative result proves nothing, and a positive result is only a lead. Teams with a recurring need are usually better served by a monitoring service than by repeated manual checks.
Haystak is aimed at investigators who need depth. Its own homepage claims it has indexed over 1.5 billion pages, one of the biggest indexes, and it runs on a freemium model. The free version offers basic keyword search and shows results with some ads. The premium version, Haystak Pro, offers advanced features: complex queries, filters and historical snapshots of sites. Its operators are anonymous, and we could not independently confirm its uptime or its index size.
Filtering policy: Reports conflict, so treat this as unverified. NordLayer’s review says it does not filter by default and adds safety flags to results, Cyble describes filtering as a paid-tier option, and other reviews say it excludes certain abuse categories. Haystak says it does not track users or serve personalized ads. A team should assume illegal or malicious results are possible.
Security team use: Historical snapshots are the feature most relevant to defenders, because they can show what a page held after it went offline, which matters when a lead disappears during an investigation. Date and type filters help when tracking a specific topic. Third-party reviews say the paid premium tier adds keyword alerts and an API, which would allow programmatic queries for certain keywords in a security operations center.
Status: Vendor roundups still listed Haystak as online in 2026, but Cyble noted reports of intermittent outages in June 2026, and Avira reported that same month that its free search did not appear to be working. A team should not build a process around its availability, and should review the operators’ anonymity before paying for or depending on the service.
In short, Haystak’s value is depth for a defined investigation, not routine checks. Because cloned and look-alike onion sites are common, we do not print its address here. As with any engine on this list, a missing result does not prove that data is absent.
Status as of November 2026: Not Evil is offline. Threat intelligence firm Cyble reports it has been down since 2024 and had not returned in a stable, verifiable form when Cyble last checked in June 2026, so any site using the name today should be treated as a possible impersonation. We keep this profile for reference. Not Evil, sometimes styled as NotEvil, was a dark web search engine with an interesting ethos: it relied on its user community to police the results. The name itself poked fun at Google’s old motto Don’t be evil, and it tried to live up to that by not engaging in any evil behavior itself: no ads, no tracking, no profiling of users. Just a search bar and results pulled from the Tor network.
Where Not Evil stood out was its moderation. Users could flag results that were misleading or malicious, and the system would remove or label them accordingly. Earlier reviews said it also blocked known abuse sites, although Cyble describes it as having positioned itself as an unfiltered alternative to Google, so its filtering was never consistent or verifiable.
Coverage while it ran: It was very minimalistic, often showing only a title and link for each result, with no snippets or previews. Its availability was always hit or miss, and the service has now been offline since 2024.
Risk today: Not Evil was Tor only, with no clear web site, and it has no maintained successor. With the original service gone, look-alike sites using its name may be phishing or malware traps, so a security team should not use them and should remove the name from any older playbooks.
Not Evil showed what crowd-sourced moderation could look like, but today Ahmia is the closest maintained option for a team that wants filtered results.
Status as of November 2026: DarkSearch is no longer publicly available. Its operators ended public access on January 13, 2022, the darksearch.io domain did not resolve when we checked in November 2026, and KELA notes the operators now point organisations to a commercial OSINT platform. We keep this profile because DarkSearch’s model is still how many monitoring tools work. DarkSearch was geared towards cybersecurity professionals and emphasized automation and integration. In practice, it offered a free API that let you plug dark web search into your own tools or scripts. That was a big deal for companies that want to continuously scan the dark web for their data without manually visiting sketchy sites every day.
Feature wise, DarkSearch combined automated crawling of onion sites with user reporting. If the community flagged something as illegal or malicious, DarkSearch would try to exclude it. It aimed for broad coverage with some checks to keep results high quality, and KELA notes that its index had freshness problems, with many results pointing to dead pages.
Privacy: DarkSearch stated that it did not store user queries. The API similarly didn’t require personal information beyond an API key.
The real value was for developers and analysts: a team could integrate DarkSearch with SIEM tools or use it to script alerts, such as an alert when a company name showed up in its results. That pattern still defines how dark web data reaches a SOC today.
Use cases: Say you run a continuous penetration testing platform or a threat intel team. Hooking a dark web search API into your alerting (DarkSearch’s free API once filled this role; today commercial dark web monitoring platforms do) lets you know quickly when a new database dump or credential leak mentioning your domain appears on the dark web. That speed is crucial: the Verizon 2025 DBIR found that 54% of ransomware victims it examined had their domains show up in infostealer logs or marketplace postings, and 40% had corporate email addresses among the compromised credentials. Finding that data quickly can buy you time to respond.
DarkSearch’s public site and its onion service are no longer available, and any site claiming to be DarkSearch today should be treated as unverified. Its role for organizations is now filled by commercial dark web monitoring services.
OnionLand searches more than one network. It indexes not just Tor .onion sites but I2P sites, another anonymity network, and even some regular web content, giving it an unusual scope. The interface includes search suggestions and category browsing.
Security team use: Its value is comparison. An analyst researching an impersonation campaign or a leaked document may want to see whether the same name appears on the regular web and on anonymity networks, and one index can show that faster than several. Any hit still needs validation: Cyble cites user reports of a higher-than-average share of scam listings.
Privacy and logging: OnionLand’s advanced features rely on JavaScript and other web technologies, which a hardened research environment normally restricts, so its design conflicts with typical controls. Its previously published privacy policy said its servers record IP addresses, ISP, browser and operating system details, timestamps and clickstream data, which it may use for purposes including marketing; the policy page was not available when checked in November 2026, and the site shows sponsored ads. A team should assume queries are logged and keep them to public identifiers.
Filtering policy and status: OnionLand blocklists abuse material and publishes hashes of the blocked sites and images, but beyond that it does not heavily filter content, and Cyble’s 2026 review lists it as not filtering content. As of November 2026 it remains online, on Tor and I2P and on the regular web.
OnionLand is a reasonable secondary source for cross-network checks, not a first stop. Given its logging, ads and JavaScript dependence, a team may prefer to get the same visibility from a monitoring provider.
DeepSearch is an open source dark web search engine focused on accuracy over quantity. Instead of bringing back hundreds of possibly relevant hits, it tries to return a smaller set of relevant results by filtering out spammy pages, link farms and obvious junk.
Because it’s open source, anyone can inspect how DeepSearch’s crawler and index work, which gives a security reviewer something concrete to assess. Researchers can also run their own instance and tune it, subject to the same authorization and legal review as any other collection.
Security team use: It suits targeted checks where an analyst already has a precise term. KELA points to it for finding niche, low-traffic forums where threat actors may discuss tactics. For instance, searching a software name might return a few relevant forum posts or breach data entries, where a larger engine would return many more mentions and scam pages. Less noise saves analyst time and means fewer unknown pages to triage.
Coverage and limits: DeepSearch’s index is smaller. It may miss new sites, and its filtering can hide useful material; NordLayer’s review warns that over-filtering can remove threat intelligence and that some results are broken. For thorough investigations, cross-check with another source.
Filtering policy: Reviews describe a filter that targets spam and, according to some, illegal and harmful sites, but no source presents it as a complete safety filter. Assume illegal or malicious results remain possible.
Status: DeepSearch runs on Tor; we could not confirm an official clearnet interface, so be wary of clearnet sites using the name. It is still covered in KELA’s July 2026 roundup of dark web search engines, which describes it as open source and focused on accuracy over quantity, but we could not independently confirm its uptime as of November 2026.
DarkWebLinks is not a traditional search engine but rather a curated directory. It is in the same family as the Hidden Wiki: a list of onion links organized by category, with an emphasis on current v3 onion addresses.
Security team use: The useful signal is availability, not discovery. KELA describes it as tracking the up or down status of cybercrime platforms, which can show when a platform exits, shifts domains or relaunches. Those moves can precede data trading or new exposure, so a threat intelligence team may record them as context.
Filtering policy: DarkWebLinks says it curates its listings and avoids abuse material, and some directories also try to flag scam sites. That is not independent review. Many listed services are illicit, so a directory entry never means a site is lawful, safe or appropriate for an analyst to open.
Coverage and limits: A directory covers only what its editors choose, and KELA notes limited depth beyond status tracking. It will not tell you whether your organization is mentioned anywhere, so it cannot replace an index or a monitoring feed.
Status and risk: KELA listed it as active in July 2026. Directories can become outdated or compromised, and several unrelated sites use similar names, so a team should not assume it has the genuine service and should not treat any listing as verified.
Overall, DarkWebLinks and similar directories are context sources for analysts who already have a scoped question. They offer no shortcut around the governance below.
These tools raise legal, safety and evidence questions that a consumer checklist does not answer. The controls below are conceptual and should be adapted with your counsel. Set them before the first query:
These controls need not be heavy. A short written standard, one approved environment and a clear escalation path cover most programs. If a team cannot put them in place, that is a strong signal to use a monitoring service instead.
If you encounter illegal content during this work, do not access it further and do not save, screenshot, download or share it. Leave the page, tell your case owner or counsel, and report it to the proper authority. For suspected child sexual abuse material, report to the NCMEC CyberTipline in the United States or the Internet Watch Foundation (IWF) in the United Kingdom. Elsewhere, use your national hotline or law enforcement. Give only the details the report asks for. A research authorization does not cover this material, and no engine’s filtering rules out encountering it.
Manual search is a good tool for a specific question with a named owner. It is a poor control for continuous visibility, since a single query shows only what one index held on one day and cannot reach closed sources. A practical test is whether the question has an end date. If it does, scoped search may fit. If it never ends, you need monitoring.
| Situation | Better Fit | Why |
|---|---|---|
| A specific lead needs corroboration during an incident | Scoped manual search | Narrow question, named owner and a short time window |
| One-time check of brand or domain mentions in public indexes | Scoped manual search | A filtered index can answer it with low effort, though a clean result proves little |
| Penetration test reconnaissance under agreed rules of engagement | Scoped manual search plus lawful breach-intelligence sources | The scope and authorization already exist, and the findings feed the test |
| Ongoing exposure of employee and customer credentials | Monitoring service | Continuous collection and alerting; repeated manual checks leave gaps |
| Brand impersonation or mentions across many sources | Monitoring service | Wider collection than public engines, with analyst triage |
| Data traded in closed forums or behind logins | Monitoring service or vetted intelligence provider | Public engines can’t see it, and analysts shouldn’t create accounts to look |
| No isolated environment, legal review or trained staff | Monitoring service | The risk of a manual program outweighs what it would find |
Monitoring moves the collection and much of the exposure to a provider whose job is to work with these sources, and your team receives alerts instead of opening unknown pages. It is not a complete answer: no provider sees everything, and alerts still need validation and a response plan. Compare options in our review of dark web monitoring tools.
If you also want this alongside ongoing testing, DeepStrike’s Premium plan includes Dark Web Monitoring, along with continuous security testing, weekly automated vulnerability scanning and attack surface management. As the publisher of this guide we have an interest here, so compare it against the alternatives for your needs.
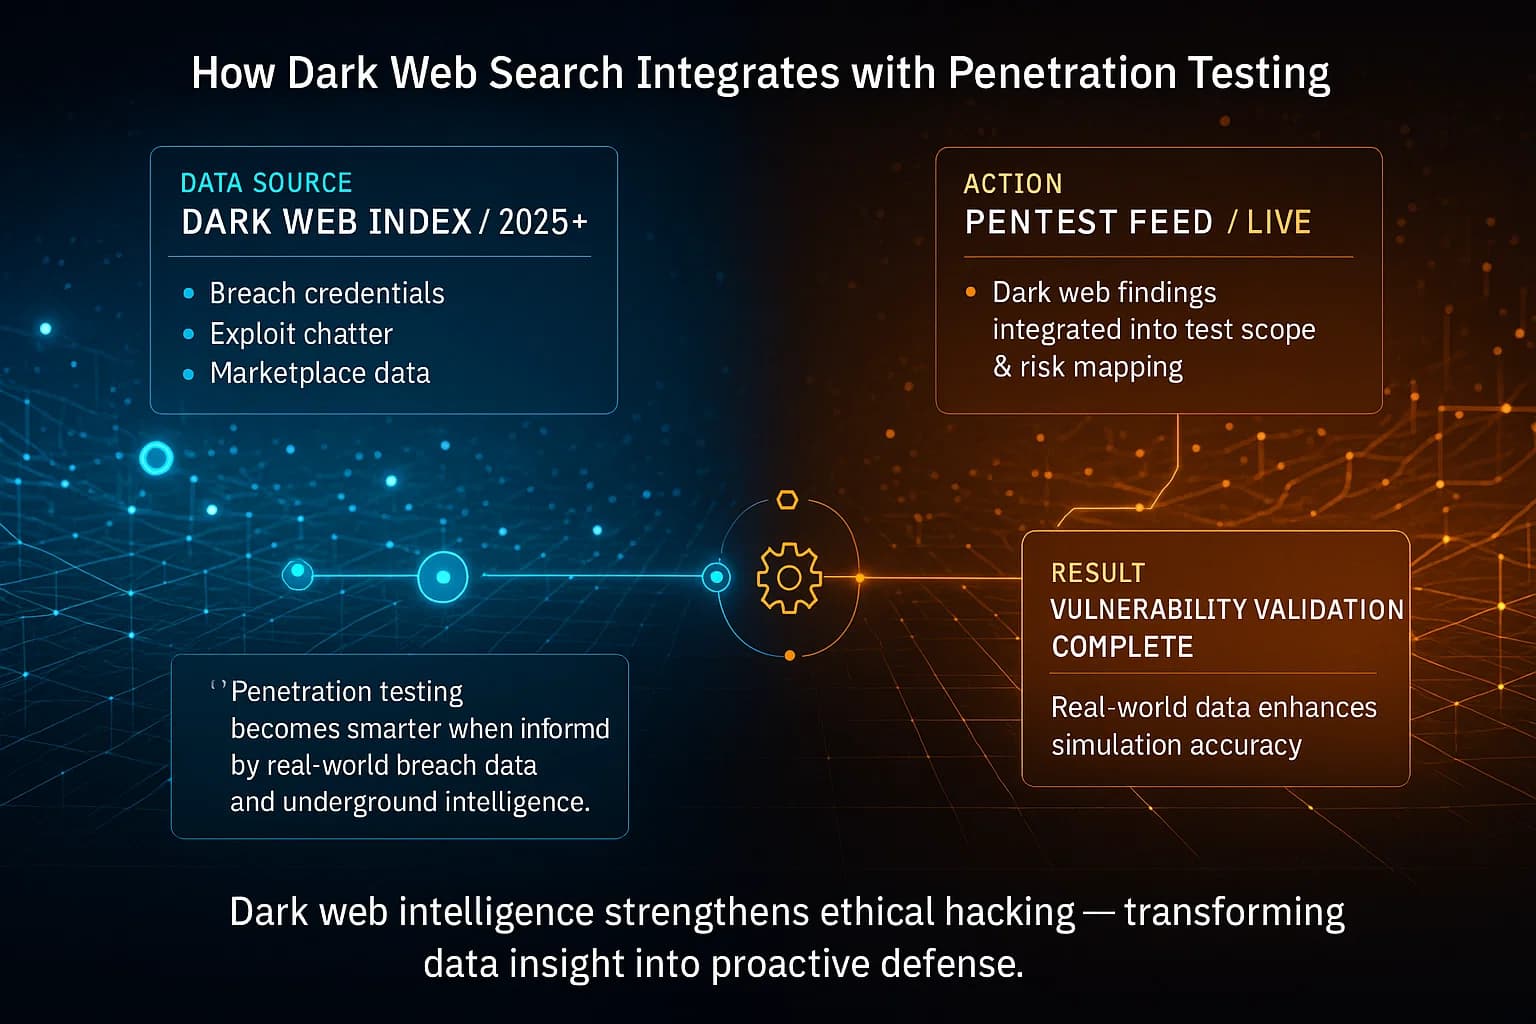
You might be wondering, why is a penetration testing firm like DeepStrike talking about dark web search engines? The answer is reconnaissance. In ethical hacking engagements pentests, one step is often to gather OSINT Open Source Intelligence about the target organization. This can include checking the dark web for any leaked passwords, confidential data, or chatter that could be used in an attack. Think of it as seeing your company from an attacker’s perspective if your admin’s password leaked on a forum, a hacker would find it and try it; so we want to find it first. Dark web search is one part of open-source intelligence; see what OSINT is and how security teams use it.
What these search engines can surface about your organization changes week to week as new dumps, pastes, and forum posts appear. Continuous penetration testing keeps re-checking your external attack surface and the leaked-credential paths an attacker would try, so new exposure gets tested as it changes rather than once a year.
Dark web search engines make this process more efficient. Rather than manually combing through forums, a pentester can use tools like Ahmia or a commercial dark web monitoring API to quickly spot mentions of the client’s domain or sensitive projects. For example, a consultant might discover API keys or network diagrams being shared on a dark web paste site, which would be an immediate red flag to report. Leaked password dumps can include an organization’s users. Where the engagement scope allows, testers check that exposure through lawful breach-intelligence sources rather than buying data from criminal markets.
Another area is account takeover simulation. If employees reuse passwords, their old breached credentials could let an attacker in. Testers check for that exposure through lawful breach-intelligence datasets, some of which let an authorized team query its own domain and see whether addresses appear in known dumps. That is useful for demonstrating risk to a client without touching criminal markets.
From a defense standpoint, many companies now invest in dark web monitoring services. These often are powered by the same principles as the search engines we discussed: crawling sites, indexing new dumps, alerting when something relevant pops up. Providers like Recorded Future, KELA, or Threat Intelligence platforms integrate dark web search capabilities to feed into organizations’ security dashboards. They’ll flag, say, We found your VPN credentials on a dark web pastebin. That early warning can prevent a breach.
A penetration test report can include a dark web exposure analysis section summarizing what an attacker could learn about you from underground sources. Used within scope and under the rules above, these search engines give testers a starting point for that intelligence.
To sum up, dark web search engines are one input to professional security testing. They connect what circulates underground to your organization. A professional red-team engagement can use this intelligence to test whether leaked credentials, exposed data, or underground threat activity can be chained into a realistic attack path. For companies, checking these sources through a monitoring service or scoped research now sits alongside patching and regular penetration testing as part of good security hygiene.
Dark web search engines are useful when a security team treats them as limited research instruments. Ahmia offers documented filtering, DuckDuckGo supports clearnet lookups, and Torch and Haystak offer breadth with more risk and less assurance. Whichever a team uses, the deciding factors are authorization, an isolated environment, legal review, evidence handling and clear stop rules. For anything continuous, a monitoring service is usually the better fit.
Ready to Strengthen Your Defenses? The threats of 2026 demand more than just awareness; they require readiness. If you’re looking to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike is here to help. Our team of practitioners provides clear, actionable guidance to protect your business.
Explore our penetration testing services to see how we can uncover vulnerabilities before attackers do. Where it fits the agreed scope, our assessments can include dark web reconnaissance to look for exposed credentials and data linked to your organization, and we’ll help you act on what we find. Drop us a line, we’re always ready to dive in.
About the Author Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
There isn’t a single best one; it depends on the question. Ahmia is often the best starting point for security teams because its filtering and privacy policies are published, which makes the work easier to document. It removes child sexual abuse material and reported abuse content from its index, which reduces, but does not eliminate, the chance of landing on harmful sites. Torch and Haystak offer more breadth, with more risk and unverified index sizes. DuckDuckGo’s onion service helps with supporting clearnet lookups, though it’s not dark web specific. Many researchers use more than one source to corroborate findings.
No, Google does not index dark web sites. Dark web pages use special .onion addresses that Google’s bots don’t crawl, so Google shows surface web results, including pages that discuss these sites. That is why a Google search cannot tell a security team whether its data is exposed on onion services. That question needs a scoped dark web search under authorization or a monitoring service.
In most places, using Tor or a search engine is not illegal by itself, but that does not settle the question for a company. Accessing illegal material can be a crime, and buying or handling stolen data can create legal exposure, even for research. Laws differ by jurisdiction. A security team should work under written authorization, have counsel review the program, and stop and report if it encounters illegal content.
No. DuckDuckGo is a privacy focused search engine that also operates a Tor onion service, but it mainly searches the normal web, not onion sites. It’s the default search in Tor Browser because it doesn’t track you. For a security team, it helps with supporting clearnet lookups, while something like Ahmia or Torch is a true onion search engine. An empty DuckDuckGo result is not evidence that data is absent from the dark web.
They shouldn’t. Tools, environments and network design should be approved centrally as part of the research program, and personal accounts, devices and software should stay out of it. VPNs are a common example of a choice that should not be left to individuals: the Tor Project’s support pages say it doesn’t recommend using a VPN with Tor unless you’re an advanced user. Set the standard once, with security architecture and legal review, and apply it to everyone doing this work.
The main risks come from the results and from how the work is run. Results can be illegal, malicious or fake, and filtering, such as Ahmia’s, reduces but never removes that risk. Engines with no moderation, such as Torch, return whatever they index. Queries can be logged, so they can reveal an investigation. Clones also impersonate engines, including defunct ones such as Not Evil and DarkSearch. Companies manage these risks through authorization, an isolated environment, query rules, no interaction with sellers and stop-and-report procedures, or by using a monitoring service.
Stop immediately. Do not access it further and do not save, screenshot, download or share it. Tell your case owner or counsel and report it to the proper authority: the NCMEC CyberTipline in the United States, the Internet Watch Foundation (IWF) in the United Kingdom, or your national hotline or law enforcement elsewhere.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
