October 18, 2025
Updated: November 5, 2026
A 2026 deep dive into Google's CASA security framework: assurance levels, costs, approved labs, and how to pass your audit for restricted scope API access.

Mohammed Khalil
Updated: November 2026. Reflects the CASA v2 specification (version 2.1.1, June 2026), Assurance Levels AL1 and AL2 in place of Tiers, the current ADA authorized lab list, and current published lab pricing.
| Question | Answer |
|---|---|
| What is it? | Google's required annual security assessment for apps that access restricted-scope data from or through a server |
| Based on | OWASP ASVS, as the foundation for the testable CASA v2 requirements (v2.1.1, June 2026) |
| Run by | The App Defense Alliance (ADA), under the Linux Foundation since November 2023 |
| Who needs it | Any app requesting restricted Google scopes (Gmail, Drive, and similar) that accesses that data from or through a server |
| Levels | AL1 (developer tested, lab reviewed) or AL2 (lab tested), assigned by Google |
| Pass certificate | A Letter of Validation (LOV), renewed at least every 12 months |
| Cost | Indicative market range: roughly $675 to $5,400 at published lab list prices (November 2026), depending on level and lab |
| Cadence | Every 12 months, a reassessment |
The one line to remember: CASA is not optional for restricted-scope apps, it is the price of continued access to Google user data, and it comes due every year.
Google's Cloud Application Security Assessment (CASA) is a standardized security review for cloud apps, created by the App Defense Alliance (ADA), an industry group founded by Google. In November 2023 the ADA moved under the Linux Foundation's Joint Development Foundation, with Google, Meta and Microsoft on its steering committee, making it a neutral, community-run standard rather than a single vendor's checklist. The requirements are now maintained as CASA v2 by ADA's Application Security Assessment Working Group (version 2.1.1 dated June 2026). In practice, CASA is a security audit framework that uses the OWASP ASVS (Application Security Verification Standard) as its foundation and turns it into testable requirements with clear acceptance criteria.
It defines a consistent set of baseline controls in six areas, authentication, session management, access control, communications (cryptography), data validation and sanitization, and configuration, that any Google integrated app must meet. CASA uses a risk based approach: apps are classified by user count, OAuth scopes, data sensitivity and other signals, and then verified accordingly.
Practically, CASA serves as a high assurance pentest for cloud apps. At AL2, an ADA-authorized lab performs a time limited, functional audit of your app's web application and web-accessible APIs. This means the lab will run DAST (dynamic analysis), review evidence or code snippets, and other checks, focused on the application layer and, where applicable, its deployment and user data storage rather than a full infrastructure test. At AL1, you run the tests and the lab reviews your evidence.
The goal is to show that your app handles Google data securely and can promptly delete it on request.
Figure: Google Workspace Marketplace shows an independent security verification badge on apps that passed CASA at Assurance Level 2 (the old Tier 3).
User trust and compliance Google requires CASA for apps that request restricted OAuth scopes, those that provide broad access to Gmail, Drive and other sensitive Google user data, and that access that data from or through a server.
In Google's words, apps "accessing restricted data from or through a third-party server must undergo an annual security assessment by a Google-approved third party" (restricted scope verification). For U.S. SaaS vendors handling Google user data at scale, CASA is mandatory.
The stakes are high. Apps validated at AL2 (formerly Tier 3) earn a coveted security verification badge in the Google Workspace Marketplace. This badge signals to customers that the app has been rigorously audited.
In contrast, apps failing CASA may be denied API access or removed from listings. With the ongoing tightening of data privacy rules and Google's OAuth policies, CASA compliance is now a go/no go for Google integrations. It's especially critical for enterprise or SaaS vendors who live and die by API trustworthiness.
Standardization and industry alignment CASA fills a big gap. Over the past decade, cloud infrastructure security has improved dramatically but application layer security still lags.
By aligning with OWASP ASVS and sponsoring a tiered framework, Google and the ADA are pushing the industry toward a common standard for app security.
Knowing CASA means you're on the forefront of app security best practices, not scrambling after a breach.
Key point: Don’t confuse CASA with generic pen testing. It’s specifically for Google bound applications. If you only use non Google cloud services AWS, Azure or have no restricted scopes, CASA doesn’t apply. But if Google APIs are involved, CASA is the official requirement.
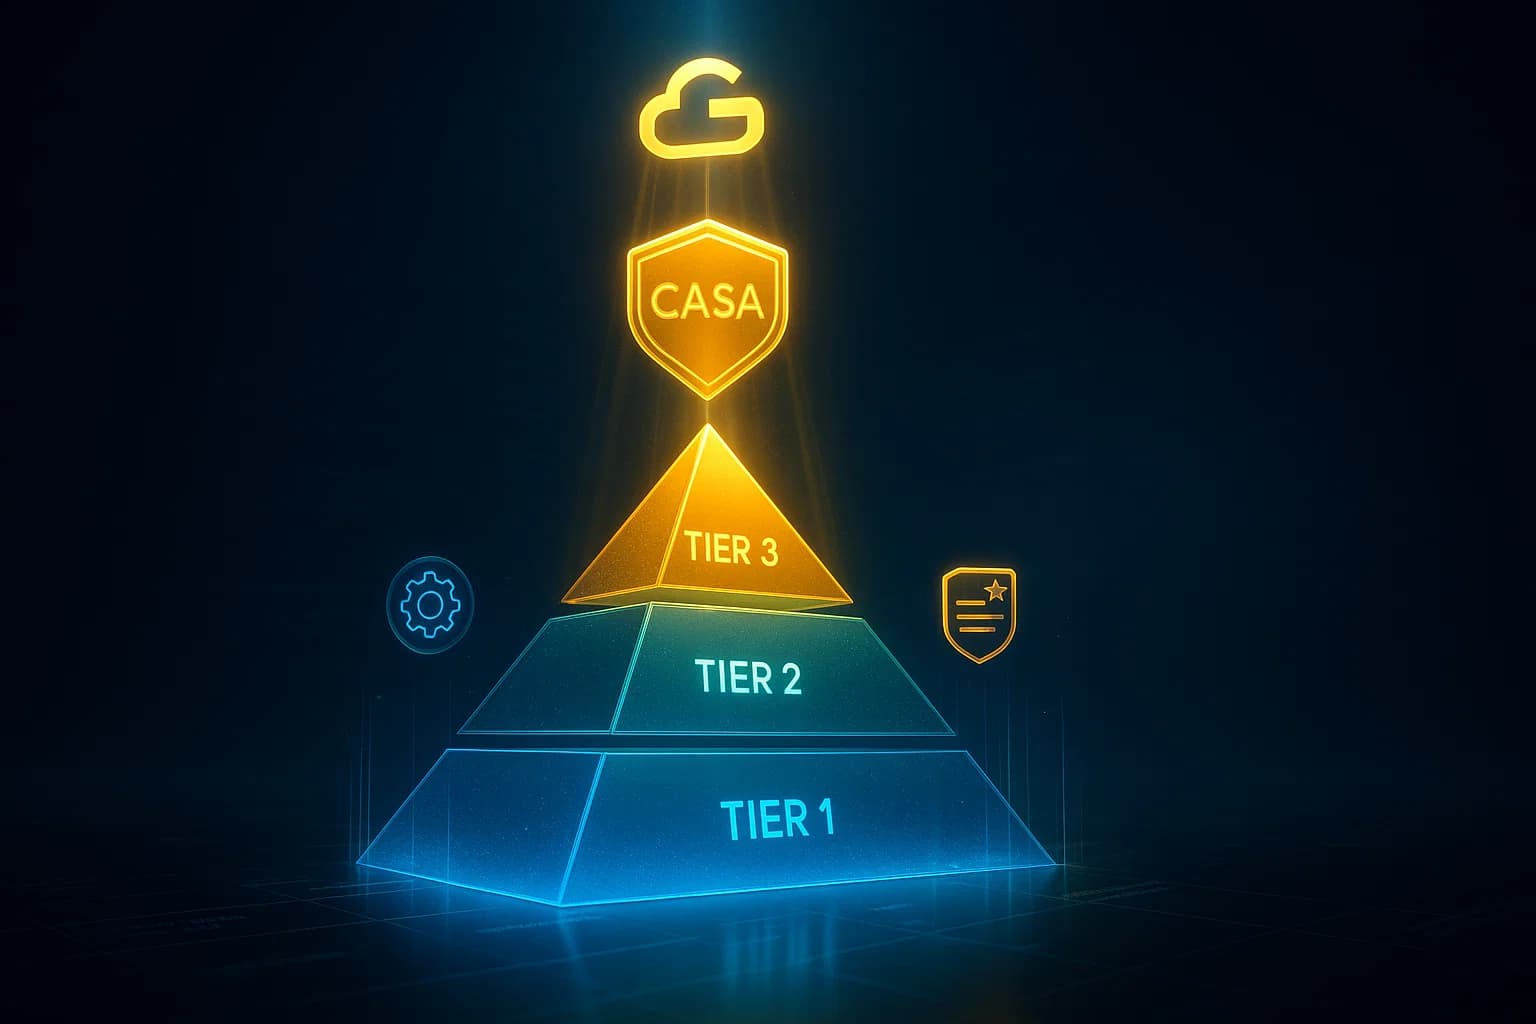
CASA originally used a three tier system to scale the assessment effort to the app's risk.
Important update: the Tier 1 to 3 naming is the legacy model. The App Defense Alliance now describes apps in terms of Assurance Levels, and for CASA, Google assigns your app to AL1 or AL2. The requirements themselves are identical at every level; the only thing that changes is the rigor of verification. If you read older guidance that talks about Tiers, this is the mapping:
| Assurance level | What it means | Roughly the old Tier |
|---|---|---|
| AL0 - Self Assessment | The developer assesses the product against the requirements. It does not result in formal certification by the ADA Certification Body. | Tier 1 |
| AL1 - Developer Tested, Lab Reviewed | You run the required test cases and submit evidence and attestations, including automated scan artifacts. An ADA-approved lab reviews that evidence for completeness and sufficiency but does not retest the app itself. | Tier 2 |
| AL2 - Lab Tested | An ADA-approved lab evaluates each test case directly against your running application. You supply limited supporting information or code snippets on request. | Tier 3 |
Two things matter here. First, you do not choose your level, Google does, based on the sensitivity of the data you touch, how many users you have, and its own risk signals. Second, the assignment tends to be sticky: once an app is validated at the lab-tested level it generally stays there in future years, which is the same behaviour the old Tier 3 had.
The pass criteria are also worth knowing before you start. In CASA v2, each requirement comes with specific audit test cases and acceptance criteria, listed in the CASA Test Guide. Several are verified with an authenticated DAST scan using the ADA's published Burp Suite audit scan configuration. The lab validates every applicable requirement before it issues an LOV, so the Test Guide is the list to work through first.
Figure: CASA originally used three risk based tiers for cloud apps; Google now assigns AL1 or AL2. Each level has defined ASVS based requirements and testing scope.
All tiers share some common rules: the assessment focuses on the app itself not the cloud infra, and results must be updated annually.
Google requires each approved app to revalidate every 12 months. That means even after you pass, plan for a yearly retest. Also, any time you add new restricted scopes, you might need an updated CASA review.
It’s worth noting how CASA differs from broader penetration testing for compliance. CASA is narrower in scope: it tests the application layer according to OWASP ASVS controls. It doesn’t include, for example, attacking the cloud network or physical data centers.
For AL2 (formerly Tier 3) assessments, labs focus on web and API endpoints and the data storage used by the app: authentication and OAuth integration, session handling, access control, cryptography in transit, input handling and configuration. Things like network sniffing or physical security are out of scope. In that sense, CASA is like a specialized web/API app pentest tailored for Google's data integration scenario.
| CASA assessment | Standard penetration test | |
|---|---|---|
| Goal | Prove CASA conformance to keep Google API access | Find and prove exploitable weaknesses |
| Basis | ASVS-based CASA v2 requirements and test cases | Adversarial testing of your specific app |
| Output | Letter of Validation (pass/fail) | A findings report with attack paths |
| Driven by | Google's OAuth requirement | Your own risk or compliance needs |
| Depth | Evidence review (AL1) to direct lab test (AL2) | Human-led exploitation and chaining |
| Scope | Web app and web-accessible APIs, per the CASA control set | Application, API, and often infrastructure |
For cloud apps, you should still use professional penetration testing services to assess infrastructure, networks, and other attack paths separately. CASA complements those efforts by covering key application controls. If you already have regular pentesting, you’ll find many overlaps. But don’t assume a generic pentest alone will satisfy Google: only a CASA report from an authorized lab gets you the official LOV.
Achieving CASA compliance is a multi step process. Here’s a high level how to for Google integrated apps:
Quick tip: Turnaround can be relatively fast. For example, TAC Security advertises assessment to LoV in about 1 to 3 weeks for AL1 packages and 2 to 4 weeks for AL2 (November 2026) once the lab has everything. However, delays in fixing issues can add time. Budget a couple of months to be safe.
The teams that sail through CASA do a few things deliberately, and each one removes a common reason submissions get rejected.
See our web application penetration testing services for deeper pentesting methodology insights on the application layer CASA covers.
Major data platforms have already gone through CASA.
For instance, Qlik Cloud achieved CASA Tier 3 certification for its integration with Google. Qlik's trust page confirms:
CASA Tier 3 is a security assessment framework based on OWASP ASVS that is mandated by Google Marketplace when cloud applications access sensitive scope data in Google Cloud.
In other words, Qlik proved its app security to Google’s standards and earned the independent security badge. This shows CASA is not just theory, it's a real requirement for enterprise cloud apps in production.
CASA compliance isn't optional, it's essential for Google integrated apps. By adopting the CASA framework as used by leaders like Qlik and mandated by Google, developers ensure their cloud applications are hardened against common threats and meet Google's strict OAuth requirements.
Google assigns the level, so you cannot simply start at a lower tier, but preparing against the full requirement set early means a move from AL1 to AL2 as your app grows is no surprise. AL2 remains the gold standard for maximum trust.
We hope this guide has clarified what CASA is, why it matters, and how to navigate its requirements. Remember: the goal is not just getting a badge, but truly securing your users’ data.
Ready to Strengthen Your Defenses? Today's security threats demand readiness. If you're integrating with Google APIs and need to validate your security posture, identify hidden risks, or build a resilient defense strategy, DeepStrike can help.
Our team of experienced practitioners provides clear, actionable guidance on penetration testing and security assessments.
Explore our penetration testing services to see how we uncover vulnerabilities before attackers do. Drop us a line we’re always ready to dive in.
About the AuthorMohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led numerous red team engagements, focusing on cloud security, application vulnerabilities, and adversary emulation. His work involves dissecting complex attack chains and developing resilient defense strategies for clients in the finance, healthcare, and technology sectors.
CASA historically used Tiers 1 to 3. The App Defense Alliance now uses Assurance Levels: AL0 is a developer self-assessment that does not produce formal certification, AL1 is developer-tested and lab-reviewed (the developer submits evidence and an approved lab checks it), and AL2 is a direct lab test of the running application. For CASA, Google assigns AL1 or AL2 based on your data sensitivity and user count. The requirements are the same at every level; only the rigor of verification changes.
At least every 12 months after your assessor's approval date. Google's Trust and Safety team contacts you when it is time. The required level can rise if your user base or data handling grew. Start before your current validation expires so your Google API access never lapses.
It is a CASA tool that maps your existing security certifications, such as ISO 27001, SOC 2, or PCI DSS, to CASA requirements so anything already covered needs fewer checks. Running it early is the single biggest time-saver for teams that already hold certifications.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
