June 8, 2026
Updated: November 5, 2026
The newest cloud security statistics for 2026, the top cloud security risks behind them, and the controls and testing priorities that address each one.

Mohammed Khalil
Cloud security statistics for 2026 show that cloud risk is driven less by “the cloud” itself and more by configuration, identity, access, APIs, SaaS integrations, Kubernetes, CI/CD pipelines, third-party cloud dependencies, and weak monitoring. Public cloud and cloud-native research shows recurring exposure in storage, compute, service accounts, secrets, and data paths. The practical issue is not whether a workload is hosted in AWS, Azure, Google Cloud, Kubernetes, or SaaS. The issue is whether the controls around that workload are correctly configured, monitored, tested, and retested after changes. AWS teams acting on these numbers can shortlist the best AWS penetration testing companies.
This guide uses publicly available 2019-2026 research and labels each statistic by data type. The main lesson is clear: cloud security cannot be proven by architecture diagrams, CSPM dashboards, or compliance checklists alone. It requires IAM review, configuration validation, API testing, logging review, segmentation validation, cloud penetration testing, and remediation retesting.
The twelve figures below are the newest primary-source cloud security statistics available in November 2026. Each one keeps its own population and date, so read them side by side rather than as one combined rate. Identity remains the most common way into cloud and SaaS environments, exploits now lead on cloud workloads, and data stored in public cloud produces the most expensive breaches.
| Statistic | Figure | Scope and date | Source |
|---|---|---|---|
| Cloud and SaaS incidents that began with an identity issue | 83% | Mandiant incident response and managed defense engagements, H2 2025 | Google Cloud Threat Horizons Report H1 2026 |
| Leading initial access vector in Google Cloud incidents | Software vulnerability, 44.5% (weak credentials 27.2%, misconfiguration 21%) | Incidents observed on Google Cloud, H2 2025 | Google Cloud Threat Horizons Report H1 2026 |
| Cloud-related incidents aimed at data theft | 73% | Mandiant cloud engagements, H2 2025 | Google Cloud Threat Horizons Report H1 2026 |
| Average cost of a breach of data stored in public cloud | USD 5.38 million (global average USD 4.99 million) | 602 breached organizations, March 2025 to February 2026 | IBM Cost of a Data Breach Report 2026 |
| Time to identify and contain a breach of data stored across environments | 256 days | Data spread across on-premises, private and public cloud; same IBM sample | IBM Cost of a Data Breach Report 2026 |
| Breaches with third-party involvement | 48%, up 60% year over year | More than 22,000 confirmed breaches | Verizon DBIR 2026 |
| Third parties that fully fixed missing or weak MFA on cloud accounts | 23% | Third-party cloud exposure findings (n=7,513) | Verizon DBIR 2026 |
| Breaches that involved ransomware | 48% (69% of victims did not pay) | Confirmed breaches, all environments | Verizon DBIR 2026 |
| Increase in destructive campaigns against Azure customer environments | 87% | Microsoft Defender for Cloud, first vs second 100 days of 2025 | Microsoft Digital Defense Report 2025 |
| Identity attacks that are password spray or brute force | More than 97% | Microsoft Entra ID telemetry, April to June 2025 | Microsoft Digital Defense Report 2025 |
| Global median dwell time | 14 days (11 days a year earlier) | Mandiant investigations in 2025, all environments | Mandiant M-Trends 2026 |
| Cloud-conscious intrusions | Up 37% year over year (vendor estimate) | CrowdStrike threat hunting data, 2025 | CrowdStrike 2026 Global Threat Report |
Sources: Google Cloud Threat Horizons Report H1 2026, IBM Cost of a Data Breach Report 2026, Verizon 2026 DBIR, Microsoft Digital Defense Report 2025 and Mandiant M-Trends 2026. The CrowdStrike figure is a vendor estimate from its 2026 Global Threat Report and is cited without a link.
This 2026 guide combines cloud-security-specific research, cloud-native security reports, cross-industry breach benchmarks, cloud compliance guidance, IAM and misconfiguration research, and cybersecurity vendor studies. Each statistic is labeled by data type so general breach statistics are not treated as cloud-only evidence. Where a statistic is not cloud-specific, it is used only as context for cloud risk. Source links point to official report pages or source hubs where available.
| Statistic | Data type | What it shows | Cloud security implication | Source |
|---|---|---|---|---|
| 54% of cloud environments have exposed VMs or serverless instances containing sensitive data. | Vendor benchmark (Wiz telemetry) | Sensitive data is often placed in reachable compute environments. | Public or weakly controlled compute exposure should be prioritized for review and retesting. | Wiz Cloud Data Security Snapshot 2025 |
| 72% of cloud environments have publicly exposed PaaS databases lacking sufficient access controls. | Vendor benchmark (Wiz telemetry) | Cloud data stores are frequently reachable or poorly restricted. | Database exposure should be reviewed through configuration testing, IAM review, and network validation. | Wiz Cloud Data Security Snapshot 2025 |
| 35% of cloud environments have VMs or serverless instances that both expose sensitive data and have high or critical severity vulnerabilities. | Vendor benchmark (Wiz telemetry) | The highest-risk cloud assets often combine data exposure and exploitable flaws. | Teams should prioritize toxic combinations, not isolated alerts. | Wiz Cloud Data Security Snapshot 2025 |
| 12% of cloud environments have publicly exposed containers exploitable via known vulnerabilities. | Vendor benchmark (Wiz telemetry) | Container exposure creates runtime compromise paths. | Container and Kubernetes review should cover exposure, image risk, RBAC, and network policy. | Wiz Cloud Data Security Snapshot 2025 |
| Roughly half of AWS EC2 instances still allow the older IMDSv1 metadata service. | Vendor benchmark (Datadog telemetry) | Legacy metadata access remains common. | IMDSv2 enforcement and SSRF-aware testing should be part of AWS security review. | Datadog State of Cloud Security 2025 |
| Threat actors exploited identity issues for initial access in 83% of incidents involving major cloud and SaaS environments (Mandiant engagements, H2 2025). | Cloud breach analysis | Identity compromise is the dominant cloud breach path. | IAM should be treated as the cloud perimeter, with MFA, least privilege, and privilege path analysis. | Google Cloud Threat Horizons Report H1 2026 |
| Credential abuse was the initial access vector in 13% of breaches (down from 22% in the 2025 DBIR), while exploitation of vulnerabilities led at 31%; credential abuse appeared at some point in 39% of breaches. | Cross-industry breach benchmark | Credentials remain a core intrusion path even as exploitation leads initial access. | Cloud identity controls should be tied to broader credential-defense strategy. | Verizon DBIR 2026 |
| Compromised cloud credentials were the second most common initial access vector (28%) in cloud-related incidents, behind phishing (33%). | Cloud-specific incident benchmark | Credential theft and phishing are leading cloud intrusion paths. | Cloud IAM review should cover credential exposure, MFA, session protection, and privilege paths. | IBM X-Force Cloud Threat Landscape Report 2024 |
| MFA blocks more than 99% of unauthorized access attempts. | IAM benchmark (vendor research) | Strong authentication materially reduces identity compromise. | Admin, developer, service, and SaaS accounts should be protected by MFA or phishing-resistant controls. | Microsoft Azure AD MFA research (2019), reconfirmed in Microsoft Digital Defense Report 2025 |
| 43% of cloud-infrastructure secrets exposed in public git repositories were Google Cloud API keys (441,780 exposed secrets analyzed). | Cloud / secrets benchmark | Cloud credentials often leak through developer and CI/CD workflows. | Secrets scanning, rotation, and CI/CD review should be part of cloud security validation. | Verizon DBIR 2025 |
| The median time to remediate leaked secrets found in a GitHub repository was 94 days. | Incident operations benchmark | Credential remediation is often slower than attackers need. | Secret rotation, detection, and retesting should be tracked as operational metrics. | Verizon DBIR 2025 |
| 96% of surveyed organizations are moderately or extremely concerned about cloud security. | Vendor survey (2024) | Cloud security remains a board and security-team priority. | Budget should be tied to practical validation, not only new tooling. | Fortinet Cloud Security Report 2024 |
| 61% of surveyed organizations planned to increase cloud security budget. | Vendor survey (2024) | Organizations recognize gaps in current cloud controls and staffing. | Investment should focus on IAM, misconfiguration, logging, API testing, and cloud-native validation. | Fortinet Cloud Security Report 2024 |
These statistics show that cloud breach risk is not only about infrastructure. It is about identity, configuration, data movement, runtime exposure, APIs, SaaS permissions, CI/CD pipelines, and monitoring. Cross-industry breach cost and credential statistics are useful context, but they should not be presented as cloud-specific unless the source explicitly segments cloud incidents.
The most actionable cloud statistics are tied to control gaps: exposed storage, overprivileged IAM, unmanaged service accounts, public services, excessive API permissions, weak logging, insecure Kubernetes, CI/CD secrets, and missing remediation retesting. Those are the areas where security leaders can convert statistics into measurable risk reduction.
For the controls behind the Kubernetes and container findings, see our guide to container security.
A cloud security incident occurs when cloud-hosted data, workloads, identities, services, applications, storage, APIs, SaaS environments, or management planes are exposed, abused, disrupted, or compromised.
A cloud breach is unauthorized access to cloud assets. A cloud misconfiguration is an insecure setup that may enable exposure. A cloud vulnerability is a software or service flaw. A SaaS security incident involves a cloud application provider or tenant configuration. A cloud compliance issue is an audit or control failure. These categories overlap, but they require different validation methods.
Cloud security risks in 2026 are concentrated around identity, configuration, data exposure, runtime complexity, SaaS sprawl, APIs, CI/CD, and monitoring. These risks become severe when they chain together: for example, a leaked CI/CD token can access an overprivileged role that can read public storage or modify production infrastructure.
| Cloud security risk | Why it matters | Common failure mode |
|---|---|---|
| Overprivileged IAM | Identity controls access to nearly everything in cloud. | Admin roles, wildcard permissions, stale access, unused privileges. |
| Public storage | Sensitive data can be exposed without exploiting a vulnerability. | Public buckets, exposed snapshots, open file shares, public databases. |
| SaaS sprawl | Business data moves into many cloud apps outside core cloud accounts. | Unknown OAuth apps, weak admin controls, broad export permissions. |
| API exposure | APIs expose cloud-hosted business logic and data. | BOLA, weak token validation, excessive data exposure, no rate limits. |
| Kubernetes risk | Container workloads can expose sensitive services and secrets. | Weak RBAC, exposed dashboard, insecure pods, no network policies. |
| CI/CD secrets | Pipelines often hold cloud credentials and deploy permissions. | Tokens in logs, repositories, environment variables, or build artifacts. |
| Cloud logging gaps | Teams cannot investigate or detect abuse without usable logs. | Disabled audit logs, short retention, missing alerts, unmonitored regions. |
| Multi-cloud complexity | Controls differ across AWS, Azure, Google Cloud, Kubernetes, and SaaS. | Inconsistent IAM, visibility, policy enforcement, and alerting. |
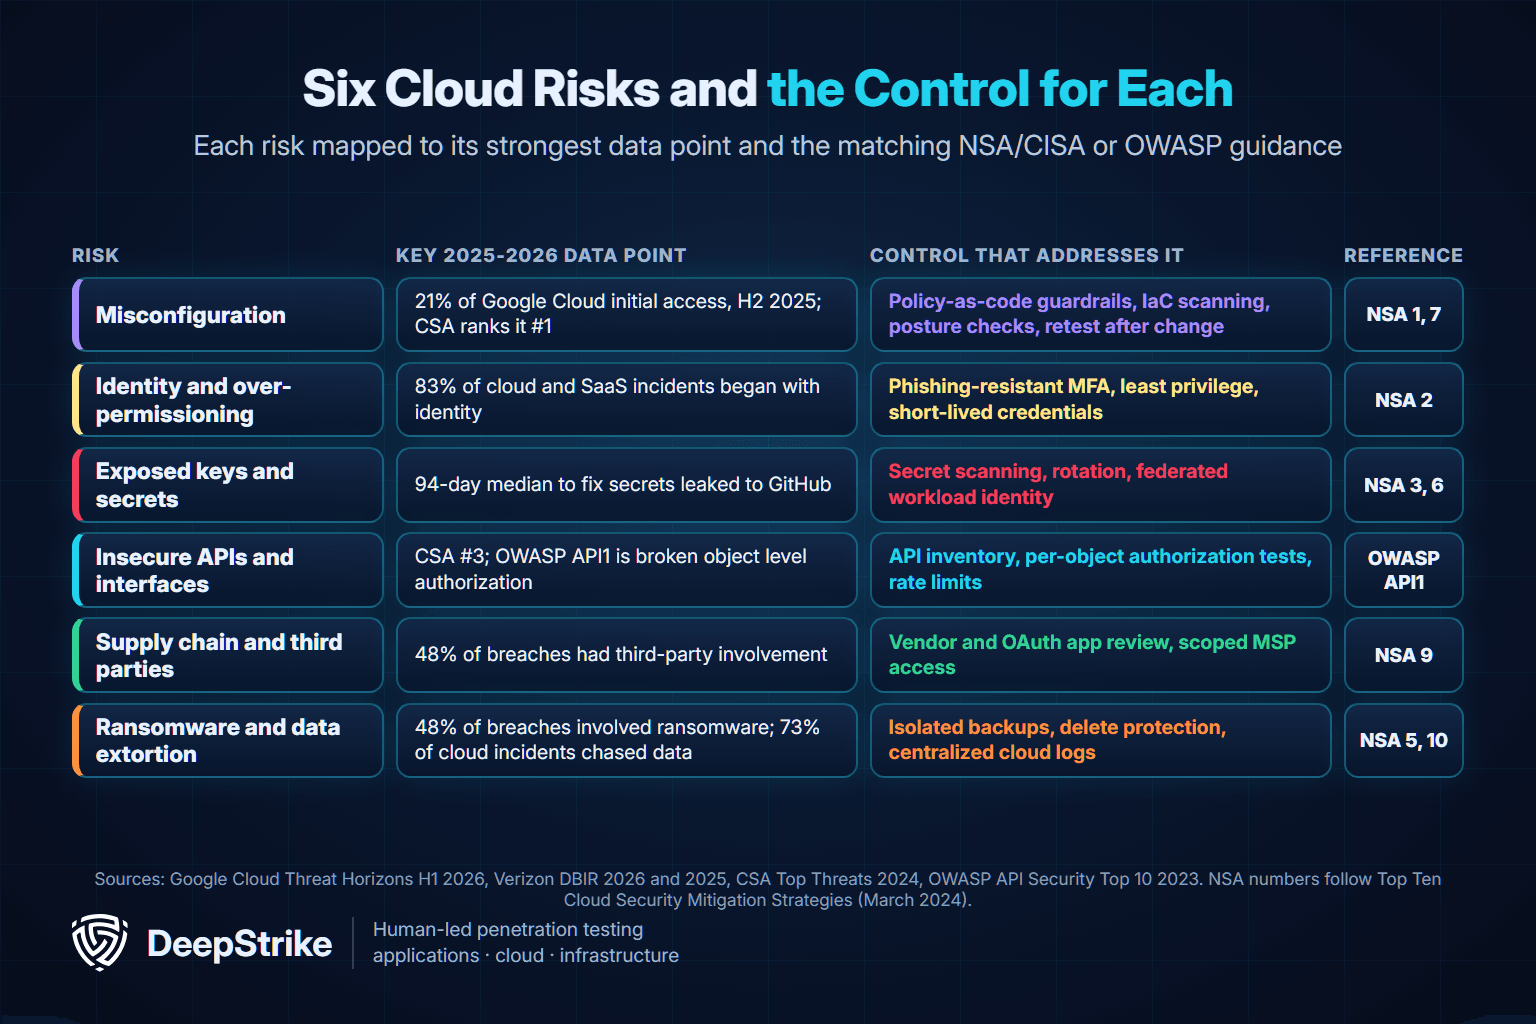
Six risks explain most of the cloud incident data published in 2025 and 2026. The Cloud Security Alliance's Top Threats to Cloud Computing 2024, based on a poll of more than 500 industry experts, ranks misconfiguration and inadequate change control first, identity and access management second, and insecure interfaces and APIs third. Incident data from Google Cloud, Mandiant, Verizon and Microsoft adds exposed secrets, third-party access and data extortion. Each risk below has its statistics and the control that most directly reduces it.
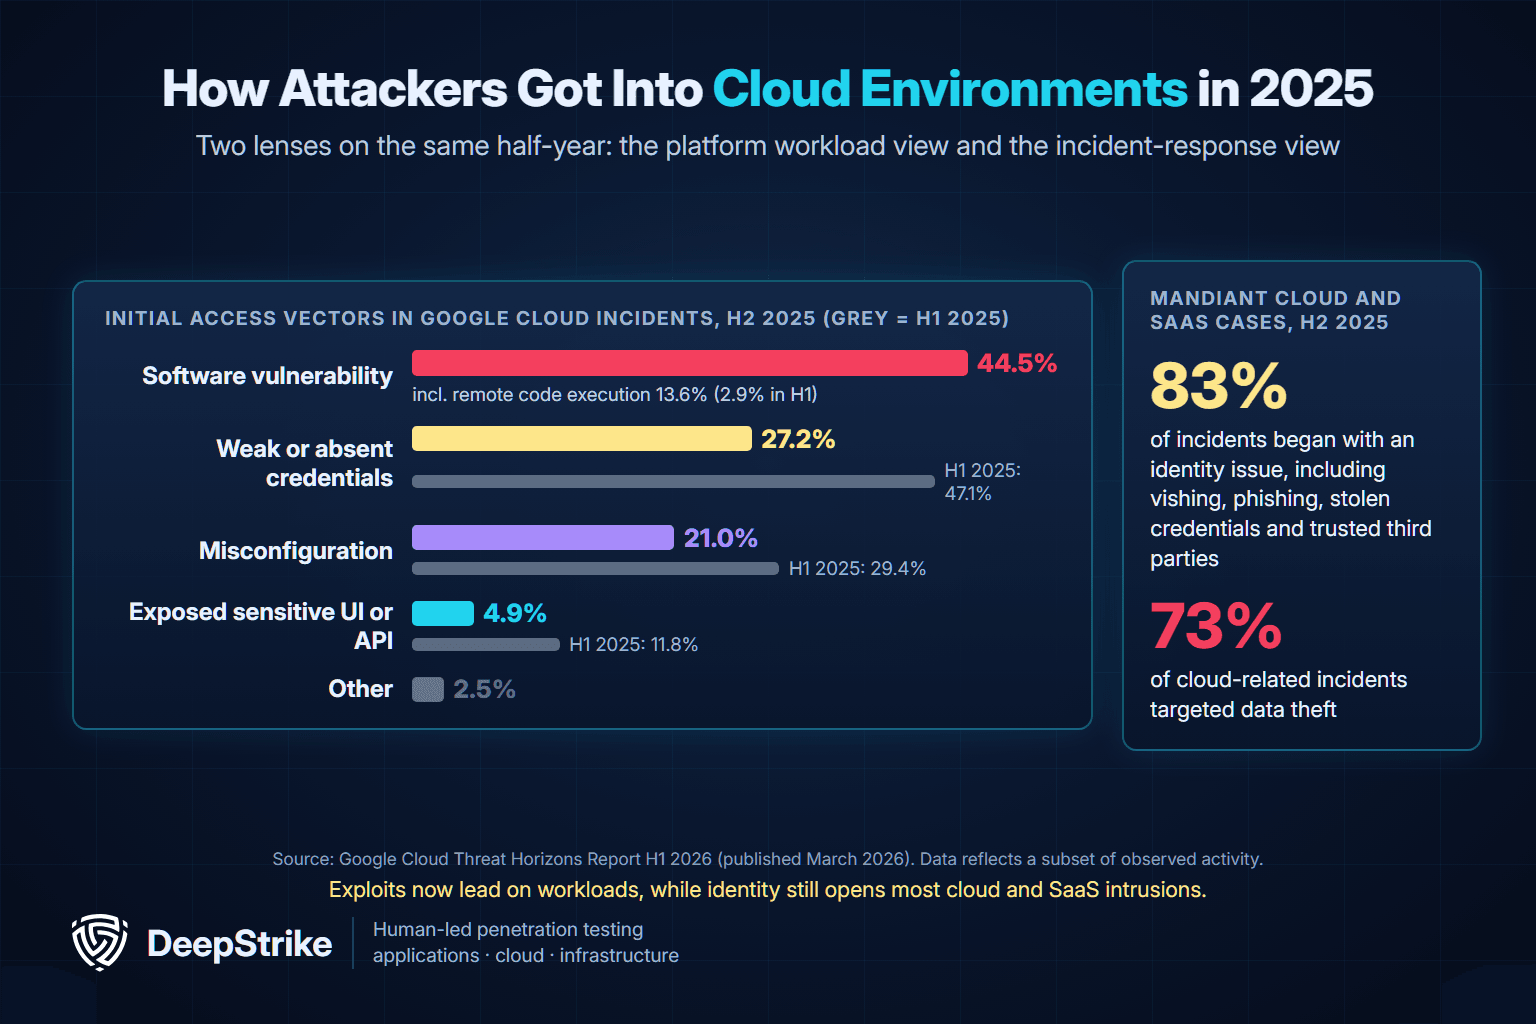
Misconfiguration was the initial access vector in 21% of the incidents Google Cloud observed on its platform in H2 2025, down from 29.4% in H1 2025, and in 7% of Mandiant's cloud and SaaS cases over the same period. Verizon's 2026 DBIR counts misconfiguration in 13% of error-related breaches (17% in EMEA) and calls it arguably the most worrying error type, because one unsecured cloud database can expose terabytes.
Fixes are slow: in Verizon's third-party cloud data, half of the weak-password and permission-misconfiguration findings were still open after almost eight months. Cloud-native workloads are exposed fast, too. Microsoft found that most compromised containers were attacked within 48 hours of deployment, with cryptomining the most common infection.
Control that addresses it: treat configuration as code. Enforce guardrails as policy at the organization level, scan infrastructure-as-code templates before deployment, run continuous posture checks against CIS Benchmarks and retest after every change window. NSA's Top Ten Cloud Security Mitigation Strategies start with the shared responsibility model and include secure infrastructure-as-code deployment. Our CSPM tools guide compares the tooling, and the Kubernetes penetration testing guide and container security guide cover RBAC, network policies and runtime hardening for clusters.
Identity is the most consistent signal across the 2026 datasets. Mandiant found identity issues behind 83% of initial access in incidents involving major cloud and SaaS environments in H2 2025: phishing (31%, including 17% voice phishing), compromised third-party relationships (21%), stolen human and non-human credentials (21%) and malicious insiders (7%). Microsoft's Digital Defense Report 2025 says more than 97% of the identity attacks it sees are password spray or brute force, and that credential and access-key theft attempts against Azure environments rose 23% between the first and second 100 days of 2025. Verizon's 2026 DBIR finds credential abuse at some stage in 39% of breaches.
Over-permissioning turns one stolen identity into a large blast radius. Microsoft reports attackers pivoting to workload identities (apps, services and scripts) because they often hold elevated privileges with weak controls, and IBM's 2026 study found fewer than half of breached organizations securing non-human identities.
Control that addresses it: phishing-resistant MFA for every human administrator (Microsoft says MFA still blocks over 99% of unauthorized access attempts), least privilege enforced with access analysis, short-lived credentials for workloads, conditional access, and regular removal of unused roles. These map to the NSA and CISA sheet on secure cloud identity and access management practices. For adoption data on the architecture behind these controls, see our zero trust statistics.
Static secrets turn a code leak into a cloud breach. In the Verizon 2025 DBIR analysis of 441,780 secrets exposed in public git repositories, 43% of the cloud-infrastructure secrets were Google Cloud API keys, and the median time to remediate leaked secrets found in a GitHub repository was 94 days. The 2026 DBIR lists secrets among the data compromised in 13% of breaches and records the March 2025 GitHub Actions compromise that exposed secrets for more than 23,000 repositories, which CISA tracked as CVE-2025-30066.
Google's Threat Horizons report describes an attacker using AWS access keys first exposed in a 2022 incident at a password management provider to enter a victim environment in late 2025, and a CI/CD intrusion that reached full cloud administration in under 72 hours by abusing OpenID Connect trust between a CI/CD provider and a cloud platform.
Control that addresses it: scan repositories, pipelines and build logs for secrets; rotate on detection; replace long-lived keys with federated workload identity whose trust conditions are scoped to specific repositories and branches; and enforce IMDSv2 on AWS instances. The NSA and CISA sheets on secure cloud key management and on defending CI/CD environments cover these controls, our secure SDLC guide places them in the build process, and the AWS penetration testing guide shows how testers check access keys and instance metadata exposure.
The Cloud Security Alliance ranks insecure interfaces and APIs third. In Google Cloud's H2 2025 data, exposed sensitive user interfaces or APIs fell to 4.9% of initial access from 11.8% in H1, which Google links to automated guardrails. The risk moves rather than disappears: among organizations that reported an AI-related breach, IBM's 2026 study found compromise of connected apps, APIs or plug-ins in 27%, and broken object level authorization is still first in the OWASP API Security Top 10 2023.
Control that addresses it: keep an inventory of every API, including shadow and deprecated versions; test authorization per object and per tenant; enforce rate limits and schema validation at the gateway; and log API calls centrally. Scanners rarely understand tenant boundaries, so authorization flaws usually need manual testing. Our guide to API penetration testing services explains what that testing covers.
Verizon's 2026 DBIR found third-party involvement in 48% of breaches, a 60% increase on the prior dataset, and only 23% of third-party organizations had fully remediated missing or improperly secured MFA on their cloud accounts. In Mandiant's H2 2025 cloud and SaaS cases, 21% began with a compromised trusted third party. IBM's 2026 study ranks supply chain compromise as the second most common initial attack vector after phishing, and the ENISA Threat Landscape 2025, covering July 2024 to June 2025, puts supply chain at 10.6% of the threat categories it recorded. M-Trends 2026 describes attackers who compromise SaaS vendors, steal hard-coded keys and personal access tokens, and use them to pivot into downstream customer environments.
Control that addresses it: inventory every third party with cloud or SaaS access, scope and time-limit vendor and managed service provider roles, review OAuth app consents, require MFA for vendor accounts and monitor their sessions. NSA and CISA cover this in their sheet on mitigating risks from managed service providers in cloud environments. Broader trend data sits in our supply chain attack statistics.
In cloud environments, attackers increasingly steal data rather than encrypt it. Mandiant's H2 2025 cloud cases show data theft in 73% of incidents: 45% silent exfiltration with no immediate extortion demand and 28% data theft with signs of extortion, while ransomware appeared in only 3%. Across all environments, Verizon's 2026 DBIR found ransomware in 48% of breaches (up from 44%), yet 69% of victims did not pay and the median payment fell to USD 139,875.
Microsoft recorded an 87% increase in campaigns aimed at disrupting Azure customer environments through ransomware, mass deletion or other destructive actions, and says more than 40% of ransomware attacks now involve hybrid components, up from less than 5% two years earlier. CrowdStrike's 2026 Global Threat Report, a vendor estimate, puts the rise in cloud-conscious intrusions at 37% year over year.
Control that addresses it: keep backups in a separate account or tenant with immutability and delete protection, alert on mass deletion and unusual storage reads, centralize cloud logs with retention that covers long dwell times (Mandiant's global median was 14 days in 2025, and espionage cases ran far longer), and rehearse rebuilding identity systems. Ransomware trends across all environments are tracked in our ransomware statistics.
The pattern across all six risks is the same: the control usually exists, but nobody has proven that it holds after the last change. A cloud penetration test checks whether an attacker could chain a misconfiguration, an over-permissioned identity, a leaked key or a third-party path into data access, and a retest confirms the fix.
The strongest cloud programs treat identity as the perimeter. Users, service accounts, workload identities, access keys, OAuth apps, and federated identities decide what attackers can reach after compromise. Least privilege, conditional access, MFA, short-lived credentials, and privilege path analysis are now baseline cloud controls.
Public storage, permissive security groups, broad IAM policies, exposed databases, unsafe Kubernetes defaults, and weak SaaS permissions continue to create preventable exposure. Guardrails help, but cloud environments still require review and retesting after changes.
SaaS platforms hold customer records, employee data, support logs, finance data, and collaboration content. OAuth consent, data export rights, admin roles, third-party apps, and SaaS-to-SaaS integrations should be reviewed alongside AWS, Azure, Google Cloud, and Kubernetes controls.
Containers, Kubernetes, serverless, ephemeral workloads, and infrastructure as code reduce delivery friction but increase configuration and runtime drift. Container image scanning, RBAC review, secrets handling, pod security, and network policy validation are now important security tasks.
Cloud applications expose data through APIs, partner integrations, mobile backends, microservices, and API gateways. Broken authorization and weak token handling often require manual API testing because scanners may not understand user roles, tenant boundaries, or business workflows.
Pipelines deploy infrastructure, hold secrets, build images, and publish artifacts. A compromised pipeline can become a cloud compromise. Secrets scanning, branch protection, least-privilege deployment roles, artifact signing, SBOMs, and IaC scanning should be part of cloud security.
SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR/CCPA, NIST, FedRAMP, CIS Benchmarks, and CSA CCM all influence cloud controls. Compliance evidence matters, but compliance does not prove exploit resistance. Technical validation is still required.
Cloud environments change too quickly for one annual review to be enough. Continuous control monitoring, recurring IAM review, API testing after major changes, retesting after fixes, and periodic cloud penetration testing reduce drift and prevent old weaknesses from reappearing.
| Root cause | How it happens | Example | Validation method |
|---|---|---|---|
| Overprivileged IAM | User or service role has excessive permissions. | Developer role can access production data. | IAM review and privilege path analysis. |
| Public storage | Cloud storage is exposed publicly. | Public bucket with customer exports. | Cloud configuration review. |
| Weak logging | Activity cannot be reconstructed. | Audit logs disabled, incomplete, or short-retention. | Logging and detection review. |
| Exposed management interface | Admin panel or dashboard is internet-facing. | Kubernetes dashboard, Grafana, or database console exposed. | External attack surface test. |
| API authorization flaw | API exposes another tenant’s records. | IDOR/BOLA in customer portal. | API penetration testing. |
| CI/CD secrets exposure | Cloud keys leak in repository or pipeline. | AWS, Azure, or GCP keys in build logs. | CI/CD security review. |
| Poor segmentation | Dev, staging, and production are too connected. | Staging compromise reaches production data. | Segmentation validation. |
| Weak SaaS permissions | OAuth app has broad data access. | Integration can export all CRM records. | SaaS permission review. |
| Unpatched workload | VM or container runs vulnerable software. | Exposed web service exploited. | Vulnerability assessment and retesting. |
| No remediation validation | Fix is assumed but not proven. | Public storage reappears after a change. | Remediation retest. |
Cloud breaches create costs beyond incident response. Evidence may be distributed across accounts, regions, SaaS tools, logs, ephemeral workloads, and CI/CD systems. Identity cleanup, token rotation, data discovery, regulatory review, and retesting can take longer than the initial containment work.
| Cost category | Cloud breach example | Why it matters |
|---|---|---|
| Forensics | Logs, identities, APIs, workloads, and cloud resources must be reviewed. | Cloud evidence can be distributed and short-lived. |
| Identity recovery | Keys, tokens, service accounts, OAuth apps, and passwords must be rotated. | Identity cleanup is often complex and time-sensitive. |
| Data discovery | Teams must identify which records were exposed. | Cloud data may be duplicated across storage, SaaS, analytics, and backups. |
| Ransomware recovery | Cloud backups or workloads are encrypted or deleted. | Recovery depends on backup isolation and privilege boundaries. |
| Compliance review | PCI, HIPAA, SOC 2, ISO 27001, or GDPR obligations may apply. | Audit evidence and notifications may be required. |
| Cloud spend abuse | Attackers abuse compute, storage, or cloud services. | Unexpected infrastructure costs can escalate quickly. |
| Customer notification | Exposed cloud data triggers disclosure duties. | Trust, legal, and customer-retention impact can exceed technical cost. |
| Remediation and retesting | IAM, storage, API, logging, and segmentation fixes are implemented. | Fixes must be validated to prevent false closure. |
Cloud identity includes users, service accounts, workload identities, API keys, OAuth apps, access keys, privileged roles, federated identities, break-glass accounts, and CI/CD deployment roles. One compromised identity can expose storage, workloads, databases, backups, and management planes.
| IAM risk | Why it matters | Cloud example | Validation method |
|---|---|---|---|
| Overprivileged roles | Excess permissions expand blast radius. | Developer can read production buckets. | IAM review. |
| Stale identities | Unused access remains exploitable. | Former contractor account is still active. | Access audit. |
| Long-lived keys | Static keys can be stolen and reused. | Access key was never rotated. | Secrets review. |
| Weak MFA | Password theft becomes cloud access. | Admin account lacks MFA. | Identity review. |
| Role chaining | Attackers escalate through allowed paths. | Low-privilege role assumes admin role. | Privilege path analysis. |
| OAuth abuse | SaaS app can access broad data. | CRM app exports all contacts. | SaaS permission review. |
| Poor service account governance | Machine identities are forgotten. | Workload identity has wildcard permissions. | Service account review. |
| No conditional access | Risky logins are allowed. | Admin login from unusual location succeeds. | Access policy review. |
Cloud compliance pressure is increasing, but compliance should be treated as evidence of control design, not proof that an attacker cannot exploit the environment. Cloud controls should be validated technically, especially where regulated data, payments, PHI, customer records, or government workloads are involved.
| Compliance area | Cloud relevance | Security implication | Validation method |
|---|---|---|---|
| SOC 2 | SaaS and cloud-hosted platforms. | Evidence for access, change, logging, vendor controls. | Control testing and cloud review. |
| ISO 27001 | Information security management. | Risk treatment, access control, supplier risk. | Audit evidence and control validation. |
| PCI DSS | Cardholder data in cloud or payment workflows. | CDE scope, segmentation, logging, vulnerability testing. | PCI-focused cloud testing. |
| HIPAA | PHI in cloud services. | Access, encryption, audit logs, BAAs. | HIPAA cloud configuration review. |
| GDPR/CCPA | Personal data in cloud environments. | Data mapping, access, breach response. | Data-flow and access review. |
| NIST / FedRAMP | Government or regulated cloud workloads. | Control baselines, evidence, continuous monitoring. | Control validation and assessment. |
| CIS Benchmarks | Cloud hardening guidance. | Baseline configuration security. | CIS benchmark review. |
| CSA CCM | Cloud control framework. | Cloud governance and shared responsibility. | Cloud control mapping. |
| Environment | Common risk | Main breach concern | Validation priority |
|---|---|---|---|
| AWS | IAM, S3, security groups, Lambda, EKS. | Public data, privilege escalation, exposed services. | IAM review, S3 review, EKS testing. |
| Azure | Entra ID, storage, role assignments, subscriptions. | Identity abuse, overprivileged roles, SaaS integration risk. | Identity review and RBAC review. |
| Google Cloud | IAM, service accounts, Cloud Storage, projects. | Service account abuse, public storage, logging gaps. | IAM and service account review. |
| Kubernetes | RBAC, network policies, images, secrets. | Cluster compromise and lateral movement. | Kubernetes security review. |
| SaaS platforms | OAuth apps, admin roles, export permissions. | Data export and account takeover. | SaaS permission review. |
| CI/CD cloud pipelines | GitHub, GitLab, Jenkins, Azure DevOps. | Secrets leakage and poisoned deployment. | CI/CD security assessment. |
| Multi-cloud | Inconsistent controls across providers. | Monitoring and policy gaps. | Cross-cloud control review. |
| Priority | Control | Risk reduced | Validation method |
|---|---|---|---|
| Critical | Cloud asset inventory | Unknown exposure. | Cloud discovery. |
| Critical | IAM least privilege review | Identity compromise. | IAM review. |
| Critical | Public storage review | Data exposure. | Configuration review. |
| High | API penetration testing | Cloud-hosted data leakage. | Manual API test. |
| High | Kubernetes security review | Runtime compromise. | Cluster assessment. |
| High | CI/CD security review | Build and deployment compromise. | Pipeline review. |
| High | Logging and detection review | Delayed incident response. | Cloud logging review. |
| Medium | Cloud ransomware tabletop | Slow recovery. | Incident exercise. |
| Medium | Continuous penetration testing | New exposure between annual tests. | Recurring validation. |
CSPM, CWPP, CIEM, and cloud-native security tools are useful, but they do not always prove exploitability or business impact. Cloud penetration testing validates whether an attacker can chain IAM, network, storage, API, SaaS, Kubernetes, and CI/CD weaknesses into meaningful exposure. Providers differ significantly in how deeply they test each of these layers — our comparison of the best cloud penetration testing companies breaks down what to check before scoping.
| Testing type | Best for | What it validates |
|---|---|---|
| Cloud configuration review | AWS, Azure, Google Cloud. | IAM, storage, logs, network exposure. |
| IAM review | Users, roles, service accounts. | Least privilege and privilege escalation paths. |
| API penetration testing | Cloud-hosted APIs. | BOLA, token handling, excessive data exposure. |
| Kubernetes review | EKS, AKS, GKE, self-managed clusters. | RBAC, secrets, network policies, image risk. |
| CI/CD security review | Cloud deployment pipelines. | Secrets, permissions, artifact trust. |
| SaaS permission review | Cloud business apps. | OAuth scopes, export rights, admin abuse. |
| Red team assessment | Mature cloud environments. | Real attack chains across identity, cloud, and apps. |
| Retesting | Post-remediation validation. | Whether fixes actually reduced risk. |
| Metric | What it measures | Why it matters |
|---|---|---|
| Public exposure count | Public buckets, open ports, exposed services. | Shows immediate internet-facing risk. |
| Overprivileged IAM roles | Excess permissions. | Measures cloud blast radius. |
| Long-lived key count | Static credentials. | Measures credential theft risk. |
| Logging coverage | Audit log visibility. | Determines investigation readiness. |
| MFA coverage for admins | Protected privileged accounts. | Shows identity-control maturity. |
| Critical misconfigurations | High-risk cloud control gaps. | Tracks immediate remediation workload. |
| API test coverage | Cloud-hosted API routes tested. | Measures data exposure validation. |
| Kubernetes policy violations | Cluster hardening gaps. | Shows runtime control weakness. |
| CI/CD secrets incidents | Exposed credentials in pipelines. | Measures DevSecOps hygiene. |
| Retest pass rate | Whether fixes worked. | Prevents false closure. |
| Compliance drift | Controls out of required state. | Shows audit and governance risk. |
The most important cloud security statistics are the ones tied to outcomes: exposed cloud data, overprivileged IAM, compromised identities, misconfigured storage, leaked secrets, API incidents, weak logging, and slow remediation. Tool adoption numbers are useful, but the stronger indicator is whether critical cloud exposures are found, fixed, and retested.
The biggest cloud security risks are overprivileged IAM, public storage, SaaS sprawl, insecure APIs, Kubernetes misconfiguration, CI/CD secrets, weak logging, stale service accounts, public management interfaces, and compliance drift. These risks become more serious when they chain together into a path from identity compromise to data access.
Cloud breaches usually happen because an attacker abuses identity, configuration, API, or monitoring gaps. Common causes include stolen credentials, leaked access keys, public storage, exposed APIs, permissive IAM, weak SaaS permissions, vulnerable workloads, and missing logs. The cloud provider may secure the platform, but customers still need to secure their configurations, identities, data, and applications.
Yes. Misconfigurations remain a major cloud exposure pattern because cloud environments change quickly and controls differ across providers. Public buckets, exposed databases, open security groups, weak Kubernetes RBAC, disabled logging, and overbroad IAM policies can expose data without requiring a sophisticated exploit.
IAM is important because identity controls access to cloud management planes, storage, workloads, databases, APIs, and SaaS platforms. A single compromised admin, service account, OAuth app, or deployment role can create broad exposure. Least privilege, MFA, conditional access, service account governance, and privilege path analysis are core cloud security controls.
SaaS platforms are part of the modern cloud attack surface because they store business data and often share identity, OAuth, and integration layers with cloud systems. CRM, HRIS, helpdesk, file-sharing, email, analytics, and collaboration platforms should be reviewed for admin roles, export permissions, OAuth scopes, and data-sharing settings.
The most relevant cloud compliance requirements depend on your data and industry. Common frameworks include SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR/CCPA, NIST, FedRAMP, CIS Benchmarks, and CSA CCM. These frameworks shape access, logging, encryption, vendor, segmentation, monitoring, and evidence requirements.
No. Cloud compliance can show that controls are designed and documented, but it does not prove those controls resist real attack paths. A compliant cloud environment can still have exposed APIs, overprivileged IAM, weak SaaS permissions, or missing logs. Technical validation and retesting are needed to prove risk reduction.
Critical cloud environments should be reviewed continuously or at least quarterly for IAM, public exposure, logging, SaaS permissions, and misconfiguration. Full cloud penetration testing is usually appropriate annually and after major architecture, authentication, API, Kubernetes, CI/CD, or compliance-scope changes.
Cloud penetration testing is a controlled security assessment of cloud-hosted infrastructure, identities, applications, APIs, Kubernetes clusters, SaaS permissions, CI/CD pipelines, and cloud configurations. The goal is to validate whether an attacker can exploit or chain weaknesses into data exposure, privilege escalation, lateral movement, or business disruption.
Useful testing includes IAM review, cloud configuration review, API penetration testing, Kubernetes review, CI/CD security assessment, SaaS permission review, external attack surface testing, segmentation validation, red team cloud scenarios, continuous penetration testing, and remediation retesting. Testing should be scoped around data sensitivity, identity paths, and business-critical workloads.
There is no single current figure. Misconfiguration was the initial access vector in 21% of incidents Google Cloud observed in H2 2025 and in 7% of Mandiant's cloud and SaaS cases, and it accounts for 13% of error-related breaches in Verizon's 2026 DBIR. Older claims that nearly all cloud failures will be the customer's fault were forecasts, not measurements.
IBM's Cost of a Data Breach Report 2026 puts the average cost of a breach of data stored in public cloud at USD 5.38 million, against a global average of USD 4.99 million across all breaches. Breaches of data spread across on-premises, private and public cloud cost USD 5.39 million and took 256 days to identify and contain.
Identity. Mandiant found identity issues, mainly phishing, vishing, stolen credentials and compromised third parties, behind 83% of initial access in cloud and SaaS incidents in H2 2025. On cloud workloads themselves, exploited software vulnerabilities led at 44.5% of initial access in Google Cloud's H2 2025 data.
Cloud security in 2026 is about validating identity, configuration, APIs, workloads, SaaS permissions, CI/CD pipelines, and cloud data paths before attackers chain them together. The strongest programs do not stop at CSPM alerts or compliance evidence. They verify whether cloud controls reduce real exposure and whether fixes remain closed after remediation.
DeepStrike helps organizations validate cloud exposure through cloud penetration testing, IAM and configuration review, API-focused security validation, Kubernetes security review, CI/CD security assessment, red team assessments, continuous penetration testing, and remediation retesting.
Mohammed Khalil is a Cybersecurity Architect at DeepStrike, specializing in advanced penetration testing and offensive security operations. With certifications including CISSP, OSCP, and OSWE, he has led red team and application security engagements for organizations in technology, finance, healthcare, and regulated environments. His work focuses on real-world attack path validation, cloud security, application vulnerabilities, PCI exposure, and adversary emulation.
All statistics in this article are drawn from public cloud security research, cloud-native reports, cross-industry breach reports, cloud compliance guidance, IAM research, API security guidance, and cybersecurity vendor studies. Cloud-specific benchmarks, cloud-native benchmarks, IAM benchmarks, API benchmarks, compliance benchmarks, and cross-industry breach benchmarks are labeled in the statistics table. Source names below link to official report pages or source hubs where available.

Stay secure with DeepStrike penetration testing services. Reach out for a quote or customized technical proposal today
Contact Us
